[](https://www.paloaltonetworks.com/)
[](https://unit42.paloaltonetworks.com/)
Menu
* [Tools](https://unit42.paloaltonetworks.com/tools/)
* [ATOMs](https://unit42.paloaltonetworks.com/atoms/)
* [Security Consulting](https://www.paloaltonetworks.com/unit42)
* [About Us](https://unit42.paloaltonetworks.com/about-unit-42/)
* [**Under Attack?**](https://start.paloaltonetworks.com/contact-unit42.html)
English
* [English](https://unit42.paloaltonetworks.com/i-soon-data-leaks/)
* [Japanese](https://unit42.paloaltonetworks.com/ja/i-soon-data-leaks/)
* [Threat Research Center](https://unit42.paloaltonetworks.com "Threat Research")
* [Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/ "Threat Research")
* [Nation-State Cyberattacks](https://unit42.paloaltonetworks.com/category/nation-state-cyberattacks/ "Nation-State Cyberattacks")
[Nation-State Cyberattacks](https://unit42.paloaltonetworks.com/category/nation-state-cyberattacks/)
# Data From Chinese Security Services Company i-Soon Linked to Previous Chinese APT Campaigns
 7 min read
Related Products
[Advanced URL Filtering](https://unit42.paloaltonetworks.com/product-category/advanced-url-filtering/ "Advanced URL Filtering")
* 
By:
* [Unit 42](https://unit42.paloaltonetworks.com/author/unit42/)
* 
Published:February 23, 2024
* 
Categories:
* [Malware](https://unit42.paloaltonetworks.com/category/malware/)
* [Nation-State Cyberattacks](https://unit42.paloaltonetworks.com/category/nation-state-cyberattacks/)
* [Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/)
* 
Tags:
* [China](https://unit42.paloaltonetworks.com/tag/china/)
* [GitHub](https://unit42.paloaltonetworks.com/tag/github/)
* [I-Soon leaks](https://unit42.paloaltonetworks.com/tag/i-soon-leaks/)
* [Linux](https://unit42.paloaltonetworks.com/tag/linux/)
* [Treadstone](https://unit42.paloaltonetworks.com/tag/treadstone/)
* [Windows](https://unit42.paloaltonetworks.com/tag/windows/)
* [Winnti](https://unit42.paloaltonetworks.com/tag/winnti/)
* [](https://unit42.paloaltonetworks.com/i-soon-data-leaks/?pdf=download&lg=en&_wpnonce=40dbae5d0f "Click here to download")
* [](https://unit42.paloaltonetworks.com/i-soon-data-leaks/?pdf=print&lg=en&_wpnonce=40dbae5d0f "Click here to print")
Share
* 
* [](mailto:?subject=Data%20From%20Chinese%20Security%20Services%20Company%20i-Soon%20Linked%20to%20Previous%20Chinese%20APT%20Campaigns&body=Check%20out%20this%20article%20https%3A%2F%2Funit42.paloaltonetworks.com%2Fi-soon-data-leaks%2F "Share in email")
* [](https://www.facebook.com/sharer/sharer.php?u=https%3A%2F%2Funit42.paloaltonetworks.com%2Fi-soon-data-leaks%2F "Share in Facebook")
* [](https://www.linkedin.com/sharing/share-offsite/?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Fi-soon-data-leaks%2F&title=Data%20From%20Chinese%20Security%20Services%20Company%20i-Soon%20Linked%20to%20Previous%20Chinese%20APT%20Campaigns "Share in LinkedIn")
* [](https://twitter.com/intent/tweet?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Fi-soon-data-leaks%2F&text=Data%20From%20Chinese%20Security%20Services%20Company%20i-Soon%20Linked%20to%20Previous%20Chinese%20APT%20Campaigns "Share in Twitter")
* [](https://www.paloaltonetworks.com//www.reddit.com/submit?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Fi-soon-data-leaks%2F&ts=markdown "Share in Reddit")
* [](https://mastodon.social/share?text=Data%20From%20Chinese%20Security%20Services%20Company%20i-Soon%20Linked%20to%20Previous%20Chinese%20APT%20Campaigns%20https%3A%2F%2Funit42.paloaltonetworks.com%2Fi-soon-data-leaks%2F "Share in Mastodon")
## Executive Summary
On Feb. 16, 2024, someone uploaded data to GitHub that included possible internal company communications, sales-related materials and product manuals belonging to the Chinese IT security services company i-Soon, also known as Anxun Information Technology. The leaked materials appear to show how a commercial entity developed and supported cyber espionage tools in support of Chinese-affiliated threat actors. As part of initial investigation into the leaked data, Unit 42 discovered links between information in the data leak and previous Chinese-affiliated advanced persistent threat (APT) campaigns. Unit 42 assesses with high confidence that the leaks are genuine.
For example, documents in the leak appear to show i-Soon was marketing the Treadstone malware controller software, which was attributed to Elemental Taurus (aka APT41) in the 2019 [U.S. grand jury indictment against three Chengdu 404 employees](https://www.justice.gov/opa/press-release/file/1317206/dl) \[PDF\].
Through analysis of the leaked data, Unit 42 has identified actor-owned infrastructure and potential malware related to historic reporting on Chinese threat actors. Given the scope of the data leak, this report will cover initial analysis and significant findings, with further reporting likely to come at a future time. (While the original GitHub repo where the leak was posted has now been taken down by GitHub staff, citing a violation of terms of service, researchers will continue to study what was initially shared.)
Based on our current understanding of the data leak, customers can be better protected through Palo Alto Networks security products against the tools and techniques used by the Chinese threat actors mentioned in this article.
| **Related Unit 42 Topics** | [**GitHub**](https://unit42.paloaltonetworks.com/tag/github/), **[China](https://unit42.paloaltonetworks.com/tag/china/)** |
|----------------------------|----------------------------------------------------------------------------------------------------------------------------|
## Technical Analysis
Text on the GitHub repository claims that i-Soon has targeted the governments of India, Thailand, Vietnam and South Korea, as well as the intergovernmental organization NATO. We continue to analyze the leaked data to verify these claims.
The GitHub repository contains a mixture of online chat conversations, screenshots and probable victim data, as well as sales- and support-related documents. The text conversations dated between November 2018 and January 2023, and they involve 37 unique usernames.
The conversations range from general conversation and workplace issues to talking about targets, software vulnerabilities and customers.
Figure 1 graphs the text communications observed between the members of i-Soon, showing relationships between employees and the volume of messages between them. (Specific user names and given names have been redacted.)
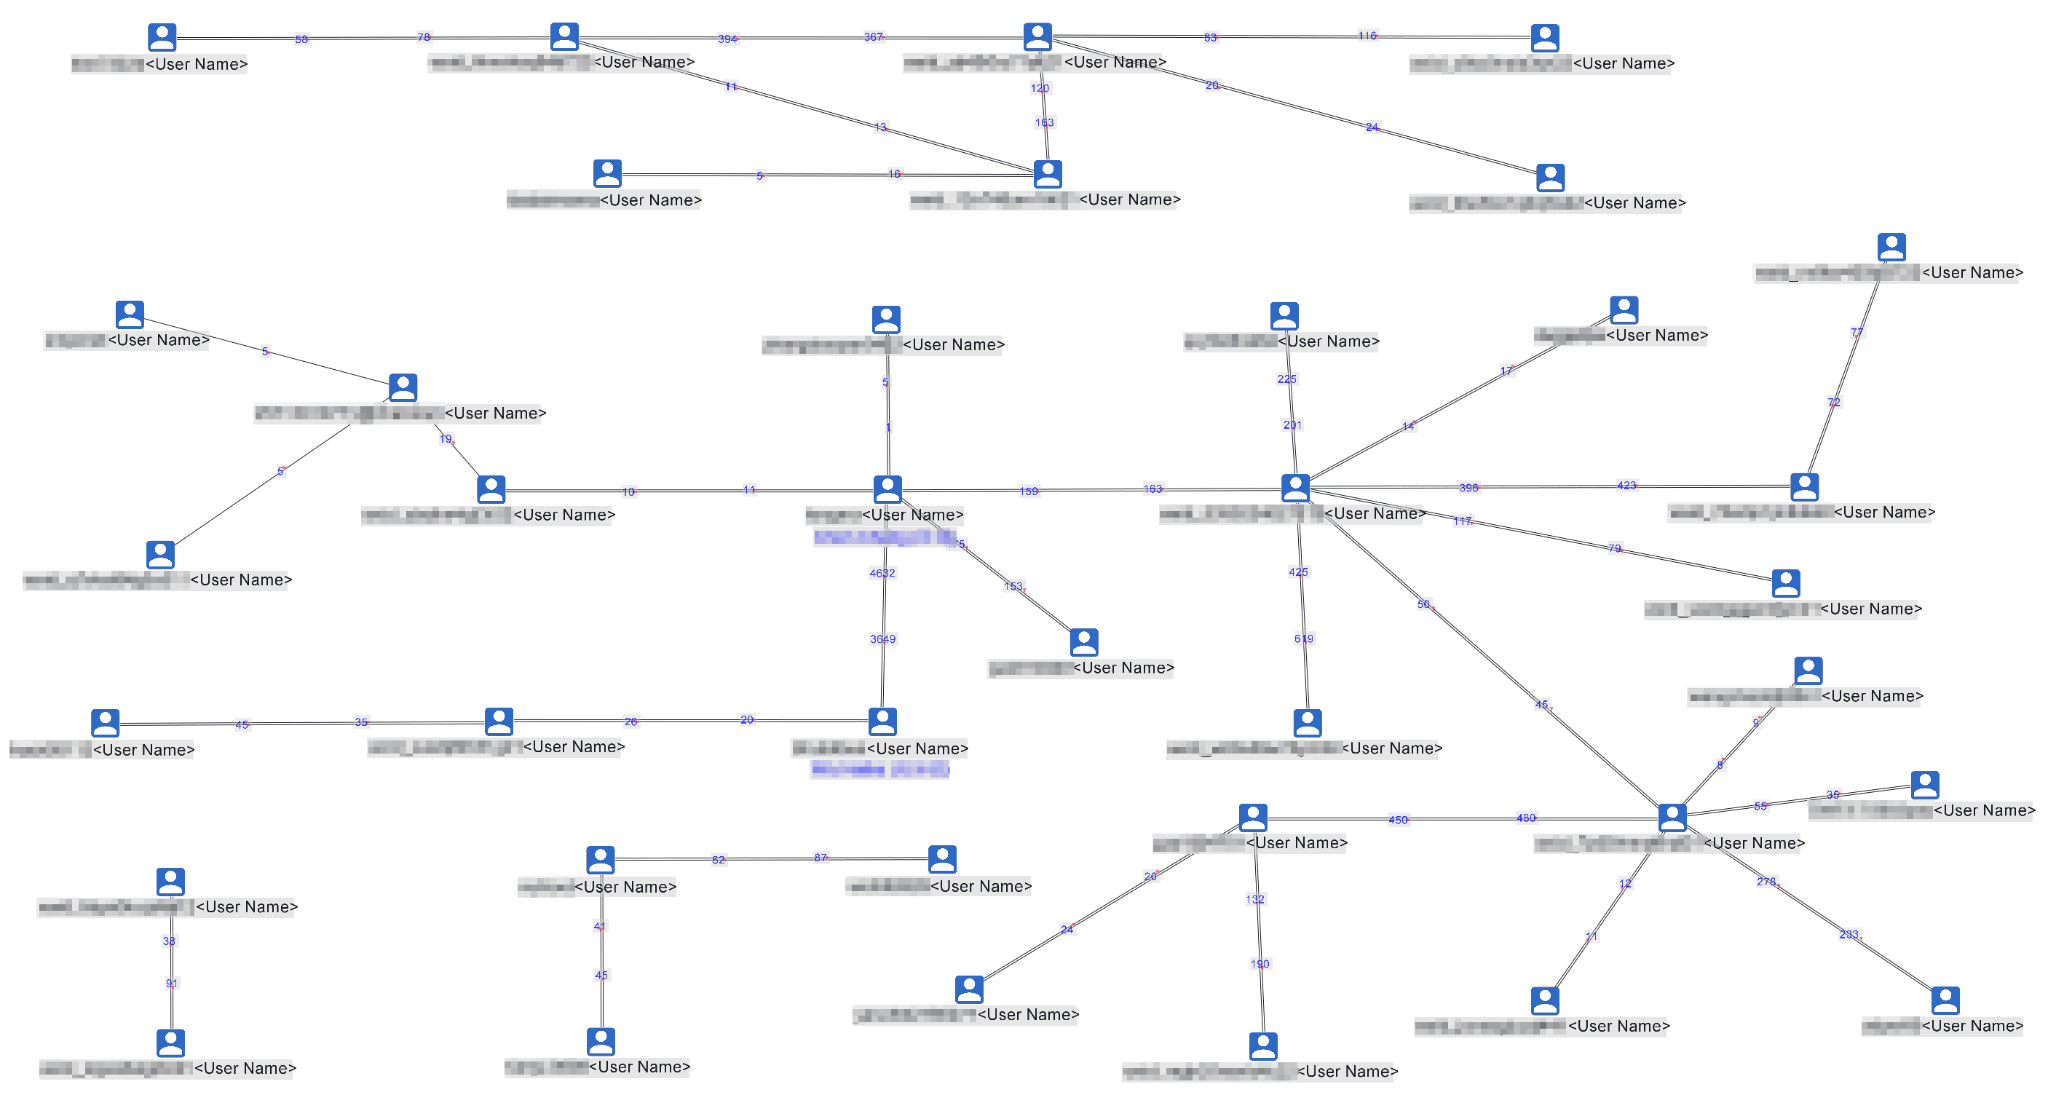 Figure 1. Visualization of i-Soon's leaked online chats (specific user names redacted).
### Links to Previous Threat Intelligence Reporting
Unit 42 has found links in the leaked i-Soon text message conversations to two previously reported campaigns attributed to Chinese advanced persistent threat (APT) groups.
#### Campaign 1: 2022 Supply Chain Attack
In September 2022, [Trend Micro reported](https://www.trendmicro.com/en_sg/research/22/l/probing-weaponized-chat-applications-abused-in-supply-chain-atta.html) about a supply chain attack on the Canadian software company Comm100. The attackers trojanized the installer for Comm100's chat-based customer engagement application hosted on their official website. When we looked through the i-Soon data leak, we found indications that i-Soon was involved in that attack.
Table 1 includes an excerpt taken from a conversation between two members of i-Soon where they claim IP address 8.218.67\[.\]52 is their server.
|--------------------|---------------------|---------------------|-------------------------------------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------|
| **Date** | **From** | **To** | **Message** | **Translated** |
| 2022-06-13 7:39:19 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | 扬州那边问个人pc的通道 | \[A person or organization from Yangzhou\] wants to ask for or request access to a PC channel that belongs to a specific individual. |
| 2022-06-13 7:39:21 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | \[捂脸\] | \[emoji suggesting embarrassment or sorry to bother you\] |
| 2022-06-13 7:39:23 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | 现在能给不 | Can you give it now? |
| 2022-06-13 7:40:26 | wxid\_zbxxxxxxxxxxxx | wxid\_c9xxxxxxxxxxxx | 【彩宝贝】 【代理】 8.218.67\[.\]52:27011 【TCP隧道】 8.218.67\[.\]52:17011 【账号】 admin 【密码】 88888888 | 【Gambling or lottery site】 【Proxy】 8.218.67\[.\]52:27011 【TCP Tunnel】 8.218.67\[.\]52:17011 【account】 admin 【password】 88888888 |
| 2022-06-13 7:40:34 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | 嗯嗯 | Uh-huh |
| 2022-06-13 7:40:37 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | 我日 | \[Expletive\] |
| 2022-06-13 7:40:54 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | 这个服务器在香港的 | This server is in Hong Kong |
| 2022-06-13 7:41:06 | wxid\_zbxxxxxxxxxxxx | wxid\_c9xxxxxxxxxxxx | 你不管 | You don't need to worry about it |
| 2022-06-13 7:41:07 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | \domain\_access\_r esult(1).csv\ | |
| 2022-06-13 7:41:11 | wxid\_c9xxxxxxxxxxxx | wxid\_zbxxxxxxxxxxxx | 嗯 | Um |
| 2022-06-13 7:41:14 | wxid\_zbxxxxxxxxxxxx | wxid\_c9xxxxxxxxxxxx | 这个服务器是我们的 | This server is ours |
*Table 1. Transcript of conversation between i-Soon members about IP address* 8.218.67\[.\]52\*.\*
On June 17, 2022, days after the above conversation occurred, the IP address 8.218.67\[.\]52 served a Linux ELF file with the SHA256 of db4497090a94d0189aa3c3f4fcee30d5381453ec5aa38962e2ca971074b74e8b. The file was served from the URL hxxp\[://\]8.218.67\[.\]52/js/xxx.jpg. When executed, the file attempts to contact the domain unix.s3amazonbucket\[.\]com (which is not a legitimate Amazon domain).
The Trend Micro report also mentioned that another subdomain of s3amazonbucket\[.\]com (analyaze.s3amazonbucket\[.\]com) was used as a command and control (C2) server for the trojanized installers.
Given the domain s3amazonbucket\[.\]com was likely under the control of i-Soon, Unit 42 assesses with moderate confidence that a group of hackers within i-Soon was involved in the supply chain attack on Comm100.
#### Campaign 2: 2019 Poison Carp Attack
In September 2019, [Citizen Lab reported](https://citizenlab.ca/2019/09/poison-carp-tibetan-groups-targeted-with-1-click-mobile-exploits/) on attackers targeting Tibetan groups via multiple iOS and Android exploits. Citizen Lab attributed the attack to the Chinese threat group they track as POISON CARP. The report references domains that were tied to an IP address that we found references to in this data leak.
The IP address 74.120.172\[.\]10 was associated with the domain mailteso\[.\]online between Sept. 22, 2020, and Feb. 20, 2024, and mailnotes\[.\]online between Aug. 7, 2021, and July 12, 2022.
Table 2 outlines the conversation between i-Soon employees about IP address 74.120.172\[.\]10.
|---------------------|---------------------|---------------------|--------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------|
| **Date** | **From** | **To** | **Message** | **Translated** |
| 2023-01-09 02:28:14 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | 等一下 平台有点问题 | Wait, there are some issues with the platform |
| 2023-01-09 02:28:18 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 好的 | OK |
| 2023-01-09 02:36:19 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | hxxps\[://\]74.120.172\[.\]10:100 92/home | |
| 2023-01-09 02:36:25 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | access OrFRXV LZtestUser lzqzmp@123 | |
| 2023-01-09 02:43:51 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 演示视屏发一个 | Send over a demo video |
| 2023-01-09 02:44:06 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 这个资料都不用给了 | No need to give this information |
| 2023-01-09 02:44:09 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | \[呲牙\] | \[Grinning emoji\] |
| 2023-01-09 02:44:20 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | 这是微软的试用版 | This is the trial version of the Microsoft \[tool\] |
| 2023-01-09 02:44:33 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 恩,我看到了 | I saw it |
| 2023-01-09 02:44:51 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 微软的演示视频有吗 | Do you have a demo video \[for Microsoft Windows tool\]? |
| 2023-01-09 02:44:58 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | 我问下 | Let me ask |
| 2023-01-09 02:48:54 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | \ 微软邮件密取平台.7z\ | \ Microsoft Mail Secret Platform .7z \ |
| 2023-01-09 02:52:01 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 是不是你们视频错了啊 | Is your video wrong? |
| 2023-01-09 02:52:03 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 我打不开 | I can not open it |
| 2023-01-09 02:55:53 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | 嗯? | Huh? |
| 2023-01-09 02:55:56 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | 解压就行了呀 | Just decompress it |
| 2023-01-09 02:56:36 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 估计是我没看视屏的 | I guess I didn't watch the video |
| 2023-01-09 03:01:26 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 还有安卓的远控 | Also the Android RAT |
| 2023-01-09 03:02:07 | wxid\_hlxxxxxxxxxxxx | wxid\_12xxxxxxxxxxxx | 安卓稍等一下 有点问题 | Wait, there's some issues with the Android one |
| 2023-01-09 03:02:26 | wxid\_12xxxxxxxxxxxx | wxid\_hlxxxxxxxxxxxx | 好 | ok |
*Table 2. Transcript of conversation between i-Soon employees about IP address 74.120.172\[.\]10.*
At the time of Citizen Lab publication, mailnotes\[.\]online was associated with IP address 207.246.101\[.\]169, which was concurrently associated with the domain gmail.isooncloud\[.\]com.
### Links to Known Chinese Intrusion Sets
The data leaks include manuals and whitepapers for various software tools. Of particular importance, these tools include software previously attributed to Chinese APT groups.
We do not currently know whether i-Soon were developers, resellers or even simply end users of these tools. However, the leaked documents help confirm previous reporting that multiple China-attributed threat actor groups often use the same, likely commercialized, malware tool sets.
One document contains a footer that translates to "Anxun Information Technology Co., Ltd." and appears to be a product manual for a range of software tools sold by i-Soon. These tools include remote control management systems for Windows, Mac, iOS, Android and Linux.
The Linux remote control management software shown in Figure 2 is notable because the screenshot provided in the document to help explain the tool's functionality shows the malware control panel is named "Treadstone." The 2019 U.S. grand jury indictment of three Chengdu 404 employees [directly references](https://www.justice.gov/media/1095686/dl) Treadstone.
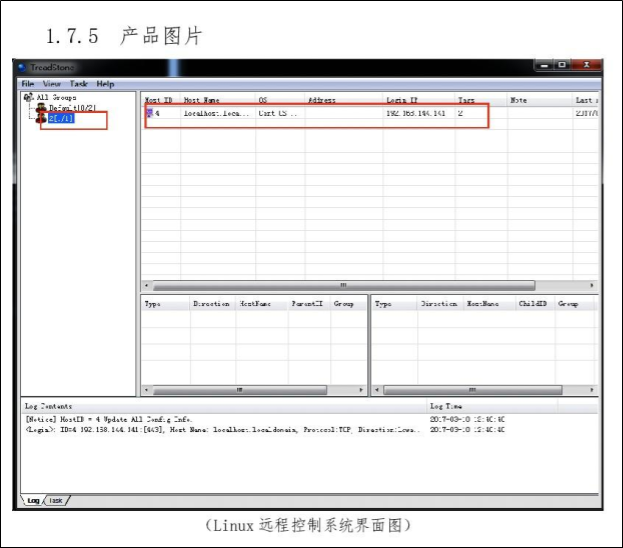 Figure 2. Screenshot of the Treadstone Linux malware control panel from a leaked product manual.
The indictment claims the Treadstone malware controller software "was designed to work with Winnti malware which, at the time, was used only by a small group of hackers." Given [reporting from October 2023](https://nattothoughts.substack.com/p/i-soon-another-company-in-the-apt41) of Chengdu 404 taking i-Soon to court for a software development contract dispute, i-Soon might have developed the Treadstone panel.
Another document relating to known Chinese APT tools is a whitepaper for a Windows remote control management system. This document covers the system and network architecture and the product's features. On one of the pages explaining management of the tool is a screenshot of what is likely the administrator panel, shown in Figure 3.
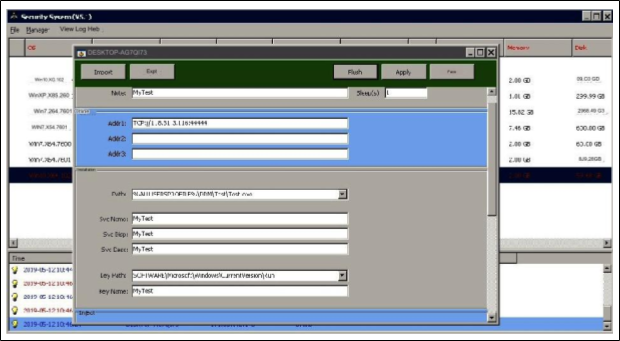 Figure 3. Administrator panel from Windows remote control management system related to known Chinese APT tool.
The screenshot shows the configured public IP address and port as TCP\[://\]118.31.3\[.\]116:44444. [SentinelLabs reported](https://www.sentinelone.com/labs/shadowpad-a-masterpiece-of-privately-sold-malware-in-chinese-espionage/) this IP address was used as a ShadowPad C2 server in August 2021 and attributed to the Winnti group. This second link to the Winnti group adds further evidence that i-Soon was involved in the development of known Winnti tool sets.
## Conclusion
This data leak provides unique insight into the Chinese private-sector hacking industry, which had previously only been seen through U.S. government indictments and reports. It also gives us a better understanding of the capabilities of Chinese threat actors, including how these groups are likely sharing or reselling the same tool sets. This dissemination of tools makes attribution more difficult for defenders and threat intelligence analysts.
Unit 42 will continue to analyze the leaked data, and we will update this post periodically, as we have more information to share.
Based on our understanding of the data leak, customers should be better protected through Palo Alto Networks security products against the tools and techniques used by the Chinese threat actors mentioned in this article. Malicious IPs related to the campaigns discussed have been blocked by [Advanced URL Filtering](https://docs.paloaltonetworks.com/advanced-url-filtering/administration).
If you think you might have been compromised or have an urgent matter, get in touch with the [Unit 42 Incident Response team](https://start.paloaltonetworks.com/contact-unit42.html) or call:
* North America Toll-Free: 866.486.4842 (866.4.UNIT42)
* EMEA: +31.20.299.3130
* APAC: +65.6983.8730
* Japan: +81.50.1790.0200
Palo Alto Networks has shared these findings with our fellow Cyber Threat Alliance (CTA) members. CTA members use this intelligence to rapidly deploy protections to their customers and to systematically disrupt malicious cyber actors. Learn more about the [Cyber Threat Alliance](https://www.cyberthreatalliance.org).
## Additional Resources
* [Probing Weaponized Chat Applications Abused in Supply-Chain Attacks](https://www.trendmicro.com/en_sg/research/22/l/probing-weaponized-chat-applications-abused-in-supply-chain-atta.html) -- Trend Micro
* [Missing Link: Tibetan Groups Targeted with 1-Click Mobile Exploits](https://citizenlab.ca/2019/09/poison-carp-tibetan-groups-targeted-with-1-click-mobile-exploits/) -- The Citizen Lab, Munk School of Global Affairs and Policy, University of Toronto
* [ShadowPad | A Masterpiece of Privately Sold Malware in Chinese Espionage](https://www.sentinelone.com/labs/shadowpad-a-masterpiece-of-privately-sold-malware-in-chinese-espionage/) -- SentinelLabs, SentinelOne
*Updated Feb. 27, 2024, at 8:03 a.m. PT to switch the images for figures 2 and 3.*
Back to top
### Tags
* [China](https://unit42.paloaltonetworks.com/tag/china/ "China")
* [GitHub](https://unit42.paloaltonetworks.com/tag/github/ "GitHub")
* [I-Soon leaks](https://unit42.paloaltonetworks.com/tag/i-soon-leaks/ "i-Soon leaks")
* [Linux](https://unit42.paloaltonetworks.com/tag/linux/ "Linux")
* [Treadstone](https://unit42.paloaltonetworks.com/tag/treadstone/ "Treadstone")
* [Windows](https://unit42.paloaltonetworks.com/tag/windows/ "Windows")
* [Winnti](https://unit42.paloaltonetworks.com/tag/winnti/ "Winnti")
[Threat Research Center](https://unit42.paloaltonetworks.com "Threat Research") [Next: Intruders in the Library: Exploring DLL Hijacking](https://unit42.paloaltonetworks.com/dll-hijacking-techniques/ "Intruders in the Library: Exploring DLL Hijacking")
### Table of Contents
*
### Related Articles
* [The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/ "article - table of contents")
* [Kimwolf v7: An Evolution of the Kimwolf Botnet](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/ "article - table of contents")
* [ChainDrop: Inside a Self-Propagating npm Worm](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/ "article - table of contents")
## Related Resources
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 10, 2026 [#### The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/)
* [API](https://unit42.paloaltonetworks.com/tag/api/ "API")
* [Cryptographic](https://unit42.paloaltonetworks.com/tag/cryptographic/ "cryptographic")
* [JSON](https://unit42.paloaltonetworks.com/tag/json/ "JSON")
[Read now ](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/ "The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 9, 2026 [#### Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure](https://unit42.paloaltonetworks.com/ppi-network-malware-campaign-analysis/)
* [ARKTunnel](https://unit42.paloaltonetworks.com/tag/arktunnel/ "ARKTunnel")
* [C2](https://unit42.paloaltonetworks.com/tag/c2/ "C2")
* [CL-CRI-1171](https://unit42.paloaltonetworks.com/tag/cl-cri-1171/ "CL-CRI-1171")
[Read now ](https://unit42.paloaltonetworks.com/ppi-network-malware-campaign-analysis/ "Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 3, 2026 [#### Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America](https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/)
* [Agentic AI](https://unit42.paloaltonetworks.com/tag/agentic-ai/ "Agentic AI")
* [ChatGPT](https://unit42.paloaltonetworks.com/tag/chatgpt/ "ChatGPT")
* [CL-CRI-1131](https://unit42.paloaltonetworks.com/tag/cl-cri-1131/ "CL-CRI-1131")
[Read now ](https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/ "Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 31, 2026 [#### Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams](https://unit42.paloaltonetworks.com/spring-ring-voice-phishing-campaigns/)
* [Cloaked Ursa](https://unit42.paloaltonetworks.com/tag/cloaked-ursa/ "Cloaked Ursa")
* [Entra ID](https://unit42.paloaltonetworks.com/tag/entra-id/ "Entra ID")
* [Microsoft Teams](https://unit42.paloaltonetworks.com/tag/microsoft-teams/ "Microsoft Teams")
[Read now ](https://unit42.paloaltonetworks.com/spring-ring-voice-phishing-campaigns/ "Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 25, 2026 [#### The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution](https://unit42.paloaltonetworks.com/ai-enabled-malware-analysis/)
* [Backdoor](https://unit42.paloaltonetworks.com/tag/backdoor/ "backdoor")
* [Bitcoin](https://unit42.paloaltonetworks.com/tag/bitcoin/ "Bitcoin")
* [DLL hijacking](https://unit42.paloaltonetworks.com/tag/dll-hijacking/ "DLL hijacking")
[Read now ](https://unit42.paloaltonetworks.com/ai-enabled-malware-analysis/ "The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 20, 2026 [#### Identity Abuse Through Trusted Communication Channels](https://unit42.paloaltonetworks.com/communication-channel-identity-risks/)
* [Authentication](https://unit42.paloaltonetworks.com/tag/authentication/ "authentication")
* [Identity theft](https://unit42.paloaltonetworks.com/tag/identity-theft/ "identity theft")
* [Malware](https://unit42.paloaltonetworks.com/tag/malware/ "malware")
[Read now ](https://unit42.paloaltonetworks.com/communication-channel-identity-risks/ "Identity Abuse Through Trusted Communication Channels")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 11, 2026 [#### Kimwolf v7: An Evolution of the Kimwolf Botnet](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/)
* [Android APK](https://unit42.paloaltonetworks.com/tag/android-apk/ "Android APK")
* [Ethereum](https://unit42.paloaltonetworks.com/tag/ethereum/ "Ethereum")
* [HTTP](https://unit42.paloaltonetworks.com/tag/http/ "HTTP")
[Read now ](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/ "Kimwolf v7: An Evolution of the Kimwolf Botnet")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 10, 2026 [#### The Permanent Threat: Analyzing Aeternum's Blockchain-Based C2 Operations and Communications](https://unit42.paloaltonetworks.com/aeternum-blockchain-c2-analysis/)
* [Aeternum](https://unit42.paloaltonetworks.com/tag/aeternum/ "Aeternum")
* [Infection chain](https://unit42.paloaltonetworks.com/tag/infection-chain/ "infection chain")
* [JSON](https://unit42.paloaltonetworks.com/tag/json/ "JSON")
[Read now ](https://unit42.paloaltonetworks.com/aeternum-blockchain-c2-analysis/ "The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications")
[High Profile Threats](https://unit42.paloaltonetworks.com/category/top-cyberthreats/) August 6, 2026 [#### ChainDrop: Inside a Self-Propagating npm Worm](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/)
* [Blockchain](https://unit42.paloaltonetworks.com/tag/blockchain/ "blockchain")
* [ChainDrop](https://unit42.paloaltonetworks.com/tag/chaindrop/ "ChainDrop")
* [Claude code](https://unit42.paloaltonetworks.com/tag/claude-code/ "Claude code")
[Read now ](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/ "ChainDrop: Inside a Self-Propagating npm Worm")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 6, 2026 [#### Token Jacking: Cybercriminals Could Be Stealing Your AI Resources](https://unit42.paloaltonetworks.com/ai-token-jacking/)
* [AI API](https://unit42.paloaltonetworks.com/tag/ai-api/ "AI API")
* [AI gateway](https://unit42.paloaltonetworks.com/tag/ai-gateway/ "AI gateway")
* [API keys](https://unit42.paloaltonetworks.com/tag/api-keys/ "API keys")
[Read now ](https://unit42.paloaltonetworks.com/ai-token-jacking/ "Token Jacking: Cybercriminals Could Be Stealing Your AI Resources")
* 
* 
 ![Enlarged Image]()
 Get updates from Unit 42
## Peace of mind comes from staying ahead of threats. Subscribe today.
Your Email
Subscribe for email updates to all Unit 42 threat research.
By submitting this form, you agree to our [Terms of Use](https://www.paloaltonetworks.com/legal-notices/terms-of-use "Terms of Use") and acknowledge our [Privacy Statement.](https://www.paloaltonetworks.com/legal-notices/privacy "Privacy Statement")
This site is protected by reCAPTCHA and the Google [Privacy Policy](https://policies.google.com/privacy) and [Terms of Service](https://policies.google.com/terms) apply.
Invalid captcha!
Subscribe  
{#footer} Products and Services
* [AI-Powered Network Security Platform](https://www.paloaltonetworks.com/network-security)
* [Secure AI by Design](https://www.paloaltonetworks.com/ai-security)
* [Prisma AIRS](https://www.paloaltonetworks.com/ai-security/prisma-airs)
* [AI Access Security](https://www.paloaltonetworks.com/sase/ai-access-security)
* [Cloud Delivered Security Services](https://www.paloaltonetworks.com/network-security/security-subscriptions)
* [Advanced Threat Prevention](https://www.paloaltonetworks.com/network-security/advanced-threat-prevention)
* [Advanced URL Filtering](https://www.paloaltonetworks.com/network-security/advanced-url-filtering)
* [Advanced WildFire](https://www.paloaltonetworks.com/network-security/advanced-wildfire)
* [Advanced DNS Security](https://www.paloaltonetworks.com/network-security/advanced-dns-security)
* [Enterprise Data Loss Prevention](https://www.paloaltonetworks.com/sase/enterprise-data-loss-prevention)
* [Enterprise IoT Security](https://www.paloaltonetworks.com/network-security/enterprise-device-security)
* [Medical IoT Security](https://www.paloaltonetworks.com/network-security/medical-device-security)
* [Industrial OT Security](https://www.paloaltonetworks.com/network-security/ot-security-solution)
* [SaaS Security](https://www.paloaltonetworks.com/sase/saas-security)
* [Next-Generation Firewalls](https://www.paloaltonetworks.com/network-security/next-generation-firewall)
* [Hardware Firewalls](https://www.paloaltonetworks.com/network-security/hardware-firewall-innovations)
* [Software Firewalls](https://www.paloaltonetworks.com/network-security/software-firewalls)
* [Strata Cloud Manager](https://www.paloaltonetworks.com/network-security/strata-cloud-manager)
* [SD-WAN for NGFW](https://www.paloaltonetworks.com/network-security/sd-wan-subscription)
* [PAN-OS](https://www.paloaltonetworks.com/network-security/pan-os)
* [Panorama](https://www.paloaltonetworks.com/network-security/panorama)
* [Secure Access Service Edge](https://www.paloaltonetworks.com/sase)
* [Prisma SASE](https://www.paloaltonetworks.com/sase)
* [Application Acceleration](https://www.paloaltonetworks.com/sase/app-acceleration)
* [Autonomous Digital Experience Management](https://www.paloaltonetworks.com/sase/adem)
* [Enterprise DLP](https://www.paloaltonetworks.com/sase/enterprise-data-loss-prevention)
* [Prisma Access](https://www.paloaltonetworks.com/sase/access)
* [Prisma Browser](https://www.paloaltonetworks.com/sase/prisma-browser)
* [Prisma SD-WAN](https://www.paloaltonetworks.com/sase/sd-wan)
* [Remote Browser Isolation](https://www.paloaltonetworks.com/sase/remote-browser-isolation)
* [SaaS Security](https://www.paloaltonetworks.com/sase/saas-security)
* [AI-Driven Security Operations Platform](https://www.paloaltonetworks.com/cortex)
* [Cloud Security](https://www.paloaltonetworks.com/cortex/cloud)
* [Cortex Cloud](https://www.paloaltonetworks.com/cortex/cloud)
* [Application Security](https://www.paloaltonetworks.com/cortex/cloud/application-security)
* [Cloud Posture Security](https://www.paloaltonetworks.com/cortex/cloud/cloud-posture-security)
* [Cloud Runtime Security](https://www.paloaltonetworks.com/cortex/cloud/runtime-security)
* [Prisma Cloud](https://www.paloaltonetworks.com/prisma/cloud)
* [AI-Driven SOC](https://www.paloaltonetworks.com/cortex)
* [Cortex XSIAM](https://www.paloaltonetworks.com/cortex/cortex-xsiam)
* [Cortex XDR](https://www.paloaltonetworks.com/cortex/cortex-xdr)
* [Cortex XSOAR](https://www.paloaltonetworks.com/cortex/cortex-xsoar)
* [Cortex Xpanse](https://www.paloaltonetworks.com/cortex/cortex-xpanse)
* [Unit 42 Managed Detection \& Response](https://www.paloaltonetworks.com/cortex/managed-detection-and-response)
* [Managed XSIAM](https://www.paloaltonetworks.com/cortex/managed-xsiam)
* [Next-Generation Identity Security](https://www.paloaltonetworks.com/idira)
* [Privileged Access Management](https://www.paloaltonetworks.com/idira/human/privileged-access-management)
* [Identity and Access Management](https://www.paloaltonetworks.com/idira/human/identity-and-access-management)
* [Endpoint Privilege Manager](https://www.paloaltonetworks.com/idira/human/endpoint-privilege-manager)
* [Identity Governance](https://www.paloaltonetworks.com/idira/human/identity-governance)
* [Workforce Password Management](https://www.paloaltonetworks.com/idira/human/workforce-password-management)
* [Agentic Identities](https://www.paloaltonetworks.com/idira/agentic)
* [Secrets Management](https://www.paloaltonetworks.com/idira/machine/secrets-management)
* [Unified Secrets Governance](https://www.paloaltonetworks.com/idira/machine/unified-secrets-governance)
* [Application Credentials Delivery](https://www.paloaltonetworks.com/idira/machine/application-credentials-delivery)
* [Vendor Privileged Access](https://www.paloaltonetworks.com/idira/human/vendor-privileged-access)
* [Threat Intel and Incident Response Services](https://www.paloaltonetworks.com/unit42)
* [Prepare for Emerging Risks](https://www.paloaltonetworks.com/unit42/frontier-ai-defense)
* [Strengthen Your Defenses](https://www.paloaltonetworks.com/unit42/strengthen-your-defenses)
* [Build Your Security Strategy](https://www.paloaltonetworks.com/unit42/build-your-security-strategy)
* [Understand the Adversary](https://www.paloaltonetworks.com/unit42/threat-intelligence)
* [Respond to a Cyber Attack](https://www.paloaltonetworks.com/unit42/respond)
Company
* [About Us](https://www.paloaltonetworks.com/about-us)
* [Careers](https://jobs.paloaltonetworks.com/en/)
* [Contact Us](https://www.paloaltonetworks.com/company/contact-sales)
* [Corporate Responsibility](https://www.paloaltonetworks.com/about-us/corporate-responsibility)
* [Customers](https://www.paloaltonetworks.com/customers)
* [Investor Relations](https://investors.paloaltonetworks.com/)
* [Location](https://www.paloaltonetworks.com/about-us/locations)
* [Newsroom](https://www.paloaltonetworks.com/company/newsroom)
Popular Links
* [Blog](https://www.paloaltonetworks.com/blog/)
* [Communities](https://www.paloaltonetworks.com/communities)
* [Content Library](https://www.paloaltonetworks.com/resources)
* [Cyberpedia](https://www.paloaltonetworks.com/cyberpedia)
* [Event Center](https://events.paloaltonetworks.com/)
* [Manage Email Preferences](https://start.paloaltonetworks.com/preference-center)
* [Products A-Z](https://www.paloaltonetworks.com/products/products-a-z)
* [Product Certifications](https://www.paloaltonetworks.com/legal-notices/trust-center/certifications)
* [Report a Vulnerability](https://www.paloaltonetworks.com/security-disclosure)
* [Sitemap](https://www.paloaltonetworks.com/sitemap)
* [Tech Docs](https://docs.paloaltonetworks.com/)
* [Unit 42](https://unit42.paloaltonetworks.com/)
* [Do Not Sell or Share My Personal Information](https://panwedd.exterro.net/portal/dsar.htm?target=panwedd)

* [Privacy](https://www.paloaltonetworks.com/legal-notices/privacy)
* [Trust Center](https://www.paloaltonetworks.com/legal-notices/trust-center)
* [Terms of Use](https://www.paloaltonetworks.com/legal-notices/terms-of-use)
* [Documents](https://www.paloaltonetworks.com/legal)
Copyright © 2026 Palo Alto Networks. All Rights Reserved
* [](https://www.youtube.com/user/paloaltonetworks)
* [](https://www.paloaltonetworks.com/podcasts/threat-vector)
* [](https://www.facebook.com/PaloAltoNetworks/)
* [](https://www.linkedin.com/company/palo-alto-networks)
* [](https://twitter.com/PaloAltoNtwks)
* EN
Select your language
   
### Default Heading
Read the article 
Seekbar
 

Volume
