Using IDAPython to Make Your Life Easier: Part 4

Earlier installments of this series (Part 1, Part 2 and Part 3) have examined how to use IDAPython to make life easier. Now let’s look at how reverse engineers can use the colors and the powerful scripting features of IDAPython.

Continue reading "Using IDAPython to Make Your Life Easier: Part 4"

Palo Alto Networks Researcher Discovers Critical Vulnerabilities in Adobe Flash

Palo Alto Networks was recently credited with discovery of two new vulnerabilities affecting Adobe Flash Player.

Researcher Hui Gao discovered critical vulnerabilities CVE-2015-8443 and CVE-2015-8444. Descriptions of each, as well as details on affected versions and products, are included in an Adobe Security Bulletin dated December 8, 2015. Adobe has released security updates for Adobe Flash Player. Continue reading "Palo Alto Networks Researcher Discovers Critical Vulnerabilities in Adobe Flash"

Using IDAPython to Make Your Life Easier: Part 3

In the first two posts of this series (Part 1 and Part 2), we discussed using IDAPython to make your life as a reverse engineer easier. Now let’s look at conditional breakpoints.

While debugging in IDA Pro, there are often situations where an analyst wishes to break on a specific address, but only when a certain condition occurs. An example of this might include breaking on a call to a particular function, but only when a specific argument is passed to it. Another instance I personally run into is breaking when a specific library is loaded into my analysis virtual machine. Today, I’m going to look at this specific problem and discuss ways to handle it with IDAPython. Continue reading "Using IDAPython to Make Your Life Easier: Part 3"

Using IDAPython to Make Your Life Easier: Part 2

Continuing our theme of using IDAPython to make your life as a reverse engineer easier, I’m going to tackle a very common issue: shellcode and malware that uses a hashing algorithm to obfuscate loaded functions and libraries. This technique is widely used and analysts come across it often. Using IDAPython, we will take this challenging problem and defeat it quite easily.

Background

Reverse engineers most often encounter obfuscated function names in shellcode. The process is quite simple overall. The code will initially load the kernel32.dll library at runtime. Then, it continues to use this loaded image to identify and store the LoadLibraryA function, which is used to load additional libraries and functions. This particular technique employs a hashing algorithm that is used to identify a function. The hashing algorithm is commonly CRC32, however, other variations, such as ROR13, are common as well.

While reverse engineering a piece of malware, I ran into the following technique: Continue reading "Using IDAPython to Make Your Life Easier: Part 2"
The Threat Intelligence Research That Mattered to You This Year

blog-title-unit42-500x68

Unit 42 did some incredible work in 2015 discovering, analyzing and disclosing malware – some new and others making a reappearance. Take a look below at some of their top threat intelligence research from this past year:

XcodeGhost

Unit 42 analyzed XcodeGhost, which modifies Xcode and infects Apple iOS Apps, and its behavior. The team found that many popular iOS apps were infected, including WeChat, one of the most popular messaging applications in the world, and that the XcodeGhost attacker can phish passwords and open URLs through these infected apps. Continue reading "The Threat Intelligence Research That Mattered to You This Year"

Using IDAPython to Make Your Life Easier: Part 1

As a malware reverse engineer, I often find myself using IDA Pro in my day-to-day activities. It should come as no surprise, seeing as IDA Pro is the industry standard (although alternatives such as radare2 and Hopper are gaining traction). One of the more powerful features of IDA that I implore all reverse engineers to make use of is the Python addition, aptly named ‘IDAPython’, which exposes a large number of IDA API calls. Of course, users also get the added benefit of using Python, which gives them access to the wealth of capabilities that the scripting language provides.

Unfortunately, there’s surprisingly little information in the way of tutorials when it comes to IDAPython. Some exceptions to this include the following:

In the hopes of increasing the amount of IDAPython tutorial material available to analysts, I’m providing examples of code I write as interesting use-cases arise. For Part 1 of this series, I’m going to walk through a situation where I was able to write a script to thwart multiple instances of string obfuscation witnessed in a malware sample. Continue reading "Using IDAPython to Make Your Life Easier: Part 1"

ProxyBack Malware Turns User Systems Into Proxies Without Consent

Anonymous proxies play an important role in protecting one’s privacy while on the Internet; however, when unsuspecting individuals have their systems turned into proxies without their consent, it can create a dangerous situation. Palo Alto Networks researchers recently discovered a family of malware, designated ProxyBack, and observed over 20 versions that have been used to infect systems as far back as March 2014.

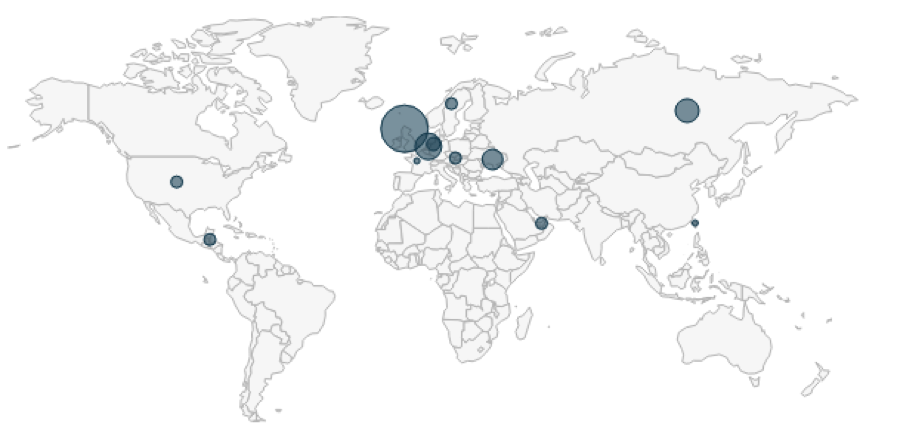
The primary distribution observed by Palo Alto Networks is focused heavily in Europe with most targets belonging to educational institutions.

proxyback1

Figure 1 – ProxyBack distribution shown in AutoFocus Continue reading "ProxyBack Malware Turns User Systems Into Proxies Without Consent"

BBSRAT Attacks Targeting Russian Organizations Linked to Roaming Tiger

In late 2014, ESET presented an attack campaign that had been observed over a period of time targeting Russia and other Russian speaking nations, dubbed “Roaming Tiger”. The attack was found to heavily rely on RTF exploits and at the time, thought to make use of the PlugX malware family.

ESET did not attribute the attacks to a particular attack group, but noted that the objective of the campaign was espionage and general information stealing. Based on data collected from Palo Alto Networks AutoFocus threat intelligence, we discovered continued operations of activity very similar to the Roaming Tiger attack campaign that began in the August 2015 timeframe, with a concentration of attacks in late October and continuing into December.

The adversaries behind these attacks continued to target Russia and other Russian speaking nations using similar exploits and attack vectors. However, while the malware used in these new attacks uses similar infection mechanisms to PlugX, it is a completely new tool with its own specific behavior patterns and architecture. We have named this tool “BBSRAT.” Continue reading "BBSRAT Attacks Targeting Russian Organizations Linked to Roaming Tiger"

#PANWchat Wrap-Up: The 2016 Threat Landscape

Last week we hosted the first ever Unit 42 Twitter chat with several of our Unit 42 experts, including Ryan Olson (@ireo), Jen Miller Osborn (@jadefh), Robert Falcone (@r0bf4lc), and Bryan Lee (@obiwanblee). The chat, “Sure Things and Long Shots, A Look at the 2016 Threat Landscape,” tackled questions from the biggest shifts in the threat landscape to the most effective measures to protect against those threats, and the best ways people can protect themselves in 2016.

The #PANWchat also served as the official launch of the new @Unit42_Intel Twitter handle, which moderated yesterday’s chat. Make sure to follow @Unit42_Intel for the latest from our Unit 42 team.

Take a look at some of the highlights from the chat below or catch up on the entire conversation through the #PANWchat hashtag. And be sure to check out our ongoing series of predictions for 2016! Continue reading "#PANWchat Wrap-Up: The 2016 Threat Landscape"

Attack on French Diplomat Linked to Operation Lotus Blossom

We observed a targeted attack in November directed at an individual working for the French Ministry of Foreign Affairs. The attack involved a spear-phishing email sent to a single French diplomat based in Taipei, Taiwan and contained an invitation to a Science and Technology support group event.

The actors attempted to exploit CVE-2014-6332 using a slightly modified version of the proof-of-concept (POC) code to install a Trojan called Emissary, which is related to the Operation Lotus Blossom campaign. The TTPs used in this attack also match those detailed in the paper. The targeting of this individual suggests the actors are interested in breaching the French Ministry of Foreign Affairs itself or gaining insights into relations between France and Taiwan.

We have created the Emissary tag for AutoFocus users to track this threat. Continue reading "Attack on French Diplomat Linked to Operation Lotus Blossom"

iOS Trojan “TinyV” Attacks Jailbroken Devices

In October 2015, we discovered a malicious payload file targeting Apple iOS devices. After investigating, we believe the payload belongs to a new iOS Trojan family that we’re calling “TinyV”. In December 2015, Chinese users reported they were infected by this malware. After further research, we found the malware has been repackaged into several pirated iOS apps that are available for download via multiple channels. In this blog, we will discuss how the TinyV Trojan spreads and how it works.

Repackaging and Spreading

TinyV was repackaged into some pirated iOS apps for jailbroken devices. Infected iOS apps include “Watermelon Player (西瓜播放器)”, “Youku (优酷)”, “iQiYi (爱奇艺)” and others. After repackaging, these apps were uploaded to websites for downloading. Continue reading "iOS Trojan “TinyV” Attacks Jailbroken Devices"

Palo Alto Networks Researchers Discover Critical Vulnerabilities in Internet Explorer and Microsoft Edge

Palo Alto Networks researchers Bo Qu and Hui Gao were credited with the discovery of three new critical Microsoft vulnerabilities affecting Internet Explorer (IE) versions 7, 8, 9, 10 and 11 and Microsoft Edge. These vulnerabilities are covered in Microsoft’s December 2015 Security Bulletin and documented in Microsoft Security Bulletins MS15-125 and MS15-124.  Continue reading "Palo Alto Networks Researchers Discover Critical Vulnerabilities in Internet Explorer and Microsoft Edge"

Palo Alto Networks Researchers Discover High Severity Vulnerability Impacting Apple’s Major Products

Palo Alto Networks researchers Tongbo Luo and Bo Qu are credited with discovering a new vulnerability (CVE-2015-7066) in OpenGL and Webkit that impacts all of Apple’s major products, including: Continue reading "Palo Alto Networks Researchers Discover High Severity Vulnerability Impacting Apple’s Major Products"

BackStab: Mobile Backup Data Under Attack from Malware

Today we are releasing a whitepaper describing how malicious actors are stealing private mobile device data by accessing local backup files stored on PC and Mac computers. We have identified 704 samples of six Trojan, adware and HackTool families for Windows® or Mac® OS X® systems that used this technique to steal data from iOS and BlackBerry® devices. These attacks have been in the wild for over five years, and we have observed them deployed in over 30 countries around the world.

Since these families use a common attack technique to access the backup files, we categorize all of them as using the “BackStab attack,” defined as “an attack approach that captures private mobile device data through the theft of local backup files stored on PC and Mac computers.”

The BackStab attack technique poses a risk to many mobile users for the following reasons: Continue reading "BackStab: Mobile Backup Data Under Attack from Malware"

Rootnik Android Trojan Abuses Commercial Rooting Tool and Steals Private Information

We recently analyzed a Trojan named "Rootnik" which uses a customized commercial root tool named “Root Assistant” to gain root access on Android devices. By reverse engineering and repackaging this tool, the creators of Rootnik successfully stole at least five exploits that give them root access to Android devices that are running Android 4.3 and earlier. Root Assistant was developed by a Chinese company to help individuals gain root access to their own devices. However, Rootnik uses this tool to attack phones all over the world. Based on the data we have collected, Android users in United States, Malaysia, Thailand, Lebanon and Taiwan have been affected by the Trojan thus far.

Rootnik was able to spread by being embedded in copies of legitimate applications: Continue reading "Rootnik Android Trojan Abuses Commercial Rooting Tool and Steals Private Information"