
In mid-July of this year, we noticed yet another legitimate website had been compromised by APT actors and was serving malware. In this case, it was a group commonly referred to as “Nitro,” which was coined by Symantec in its 2011 whitepaper.
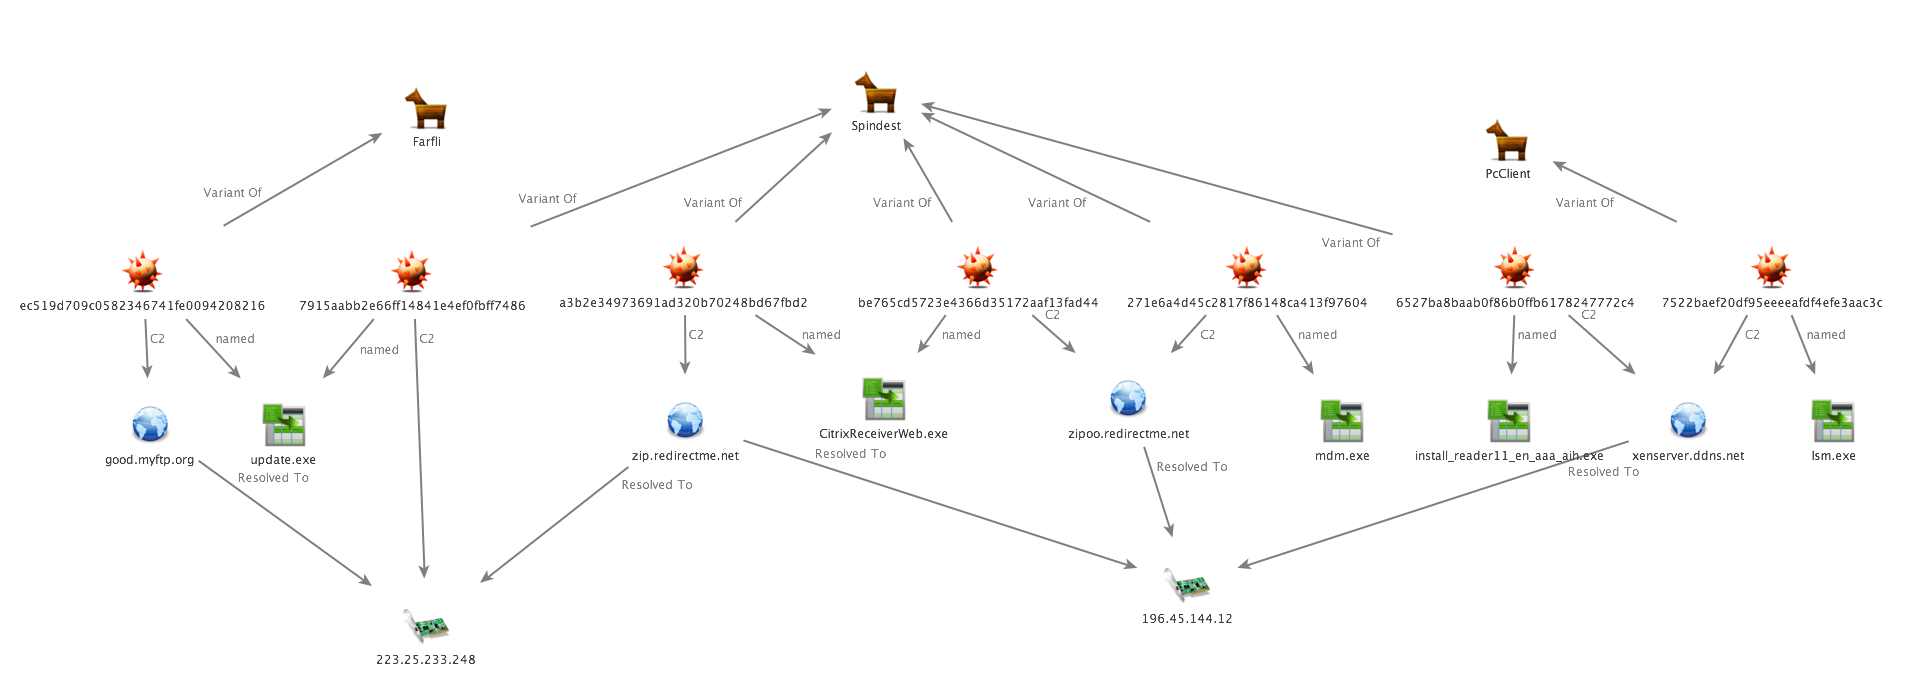
As we dug deeper, we found additional compromised legitimate websites and malware from the same group back through March of this year. In most instances, the malware is one commonly referred to as “Spindest,” though we also found “PCClient” and “Farfli” variants in use by the group. We don’t have enough data to say for certain that all of the malware in this blog was delivered via compromised legitimate websites.
Historically, Nitro is known for targeted spear phishing campaigns and using Poison Ivy malware, which was not seen in these attacks. Since at least 2013, Nitro appears to have somewhat modified their malware and delivery methods to include Spindest and legitimate compromised websites, as reported by Cyber Squared’s TCIRT. Our findings indicate they are continuing to evolve with the addition of PCClient and Farfli variants. The Maltego screenshot below shows the activity we describe in this blog.
 Continue reading "New Indicators of Compromise for APT Group Nitro Uncovered"
 Get updates from Unit 42
