Don’t Be an April Fool: Inside a Common Phone Scam

One of our team members on Unit 42 recently received a phone call from a scammer, and today being April Fool's Day we decided to write about how we played along with the scammer to learn about his operation.

Unit 42 analyst Robert received a phone call from a Tech Support scammer who told him his system was compromised and was seen performing illegal activities. The scam relied solely on social engineering, which is a technique to manipulate a victim into doing something or to give up information, but in this case was intended to get Robert to pay the scammer for unneeded system protection services. Social engineering is used in a majority of cyber crime and espionage attacks, albeit in this scam it was conducted over the phone and not via e-mail or social networking.

This blog, in Robert's voice, recounts the story of this unsolicited call and provides a glimpse into this scam operation. We intend this story to be light reading for security professionals, but hope that it provides awareness for less technical folks into the social engineering techniques used in these types of scams. Continue reading "Don’t Be an April Fool: Inside a Common Phone Scam"
How the EITest Campaign's Path to Angler EK Evolved Over Time

In October 2014, Malwarebytes identified a campaign based on thousands of compromised websites that kicked off an infection chain to Angler exploit kit (EK). It was named "EITest" campaign, because "EITest" was a variable consistently found in injected scripts across all of the compromised websites. Malwarebytes noted some changes in this campaign in 2015 and 2016.

Like others in the cybersecurity threat research community, we have been tracking the EITest campaign. This blog post focuses on network traffic and how indicators have changed over time. Continue reading "How the EITest Campaign's Path to Angler EK Evolved Over Time"

ProjectM: Link Found Between Pakistani Actor and Operation Transparent Tribe

Be the first to receive the latest news, cyber threat intelligence and research from Unit 42. Subscribe Now. 

Unit 42 is currently researching an attack campaign that targets government and military personnel of India. This attack appears to overlap with the Operation Transparent Tribe and Operation C-Major campaigns that targeted Indian embassies in Saudi Arabia and Kazakhstan, as well as the Indian military.

We are tracking the group of actors involved in this campaign as ‘ProjectM.’ During our research, we found a linkage between the infrastructure used by ProjectM and an individual from Pakistan. We cannot definitively confirm this individual is involved with this attack campaign, but the evidence that we will discuss in this blog post suggests that it is highly likely that this individual has some involvement with the threat group.

This blog post highlights the trail of evidence individuals leave on the Internet when they are not careful about disguising their identity. All of the information collected about this actor is public and accessible through open source research. Continue reading "ProjectM: Link Found Between Pakistani Actor and Operation Transparent Tribe"

Palo Alto Networks Researchers Discover Critical IE Vulnerabilities

Palo Alto Networks researchers Tongbo Luo and Hui Gao were credited with the discoveries of new critical Microsoft vulnerabilities affecting Internet Explorer (IE) versions 7, 8, 9, 10 and 11 on affected Windows clients. These vulnerabilities are documented in Microsoft Security Bulletin MS15-106 and MS15-112. Continue reading "Palo Alto Networks Researchers Discover Critical IE Vulnerabilities"

Evolution of SamSa Malware Suggests New Ransomware Tactics In Play

Ransomware is often in the headlines as new families are discovered on an almost weekly basis. Historically, these families have shared one similarity – they have all been deployed by attackers casting a wide net and largely being victim-agnostic. In most cases, the adversaries have used phishing emails and exploit kits in a ‘spray and pray’ style tactic.

However, in recent months, a new trend seems to be emerging: targeted attacks where ransomware is deployed by threat actors after successfully gaining unauthorized access to an organization’s network. One malware family seen in such attacks is known as ‘SamSa’, ‘Samas’, ‘samsam’, or most recently, ‘MOKOPONI’. Reports on this malware family have previously been published by both Intel Security and Microsoft.

Palo Alto Networks has collected over 20 samples of this particular malware family, and we have identified over $70,000 USD in Bitcoin payments to the attacker (Cisco Talos yesterday reported this figure to be closer to $115,000 USD). This blog details the evolution of this malware family, which was first witnessed in December 2015, as well as provides various indicators of compromise (IOCs) that can be used by the security community. Continue reading "Evolution of SamSa Malware Suggests New Ransomware Tactics In Play"

Campaign Evolution: Darkleech to Pseudo-Darkleech and Beyond

In 2015, Sucuri published two blog posts, one in March describing a pseudo-Darkleech campaign targeting WordPress sites, and another about its evolution the following December. Sites compromised by this campaign redirected unsuspecting users to an exploit kit (EK). The Sucuri posts describe patterns in the injected script related to this campaign. Since December 2015, patterns associated with pseudo-Darkleech have continued to evolve. Our blog post today will examine these changes.

However, before we look at the recent developments, we should understand how EKs fit into the overall picture and review the history of Darkleech.

Continue reading "Campaign Evolution: Darkleech to Pseudo-Darkleech and Beyond"

Locky Ransomware Installed Through Nuclear EK

In February 2016, Unit 42 published detailed analysis of Locky ransomware. We certainly weren’t the only ones who saw this malware, and many others have also reported on it. Since that time, Locky has been frequently noted in various campaigns using malicious spam (malspam) to spread this relatively new strain of ransomware.

When we initially reported on Locky, attackers were distributing the malware using Microsoft Office documents with malicious macros to download and execute the ransomware. Attackers quickly added another tactic, sending e-mails with zip attachments containing malicious Javascript files to accomplish the same goal. However, exploit kits (EKs) have also been used to infect users with Locky from casual web browsing. This activity suggests that there are effectively two paths to Locky: one through malspam and another through EK traffic.

Continue reading "Locky Ransomware Installed Through Nuclear EK"

AceDeceiver: First iOS Trojan Exploiting Apple DRM Design Flaws to Infect Any iOS Device

We’ve discovered a new family of iOS malware that successfully infected non-jailbroken devices we’ve named “AceDeceiver”.

What makes AceDeceiver different from previous iOS malware is that instead of abusing enterprise certificates as some iOS malware has over the past two years, AceDeceiver manages to install itself without any enterprise certificate at all. It does so by exploiting design flaws in Apple’s DRM mechanism, and even as Apple has removed AceDeceiver from App Store, it may still spread thanks to a novel attack vector.

AceDeceiver is the first iOS malware we’ve seen that abuses certain design flaws in Apple’s DRM protection mechanism -- namely FairPlay -- to install malicious apps on iOS devices regardless of whether they are jailbroken. This technique is called “FairPlay Man-In-The-Middle (MITM)” and has been used since 2013 to spread pirated iOS apps, but this is the first time we’ve seen it used to spread malware. (The FairPlay MITM attack technique was also presented at the USENIX Security Symposium in 2014; however, attacks using this technique are still occurring successfully.)

Continue reading "AceDeceiver: First iOS Trojan Exploiting Apple DRM Design Flaws to Infect Any iOS Device"

Digital Quartermaster Scenario Demonstrated in Attacks Against the Mongolian Government

Unit 42 has collected multiple spear phishing emails, weaponized document files, and payloads that targeted various offices of the Mongolian government during the time period of August 2015 and February 2016. The phishing emails and document files leveraged a variety of geopolitically sensitive subject matters as attractive lures, such as events in Beijing, the Dalai Lama, North Korea relations, the Zika virus, and various legitimate appearing announcements. As we began to analyze and tear down the various samples we collected, we found significant overlaps with previously reported and documented adversary groups, attack campaigns, and their toolsets, exemplifying the concept of the Digital Quartermaster.

Continue reading "Digital Quartermaster Scenario Demonstrated in Attacks Against the Mongolian Government"

PowerSniff Malware Used in Macro-based Attacks

Introduction

The concept of file-less malware is not a new one. Families like Poweliks, which abuse Microsoft’s PowerShell, have emerged in recent years and have garnered extensive attention due to their ability to compromise a system while leaving little or no trace of their presence to traditional forensic techniques.

System administrators have lauded the power and versatility of PowerShell since version 2.0’s integration into Windows 7. Unfortunately, with such versatility comes the opportunity for abuse, specifically surrounding the capability to write directly into memory of the host OS.

Typically, file-less malware has been observed in the context of Exploit Kits such as Angler. Palo Alto Networks has observed a recent high-threat spam campaign that is serving malicious macro documents used to execute PowerShell scripts which injects malware similar to the Ursnif family directly into memory. We call the malware PowerSniff. Continue reading "PowerSniff Malware Used in Macro-based Attacks"

Palo Alto Networks Researcher Discovers Critical IE Vulnerability

Palo Alto Networks researcher Hui Gao was credited with the discovery of a new critical Microsoft vulnerability affecting Internet Explorer (IE) versions 9, 10 and 11. This vulnerability is covered in Microsoft’s March 2016 Security Bulletin and documented in Microsoft Security Bulletin MS16-023. Continue reading "Palo Alto Networks Researcher Discovers Critical IE Vulnerability"

Banload Malware Affecting Brazil Exhibits Unusually Complex Infection Process

As previously discussed by Unit 42, banking Trojans have been targeting Brazilian systems for years given the popularity of online banking services in the country. Recently, we analyzed a handful of samples targeting Brazilian systems that exhibited a unique and complex multi-stage loading process. Antivirus detection names for this malware typically are detected as generic named families or “Banload”.

In this blog post, I’ll share details of the complexity of this Trojan’s installation process, which involves a series of archive downloads, process injections and executable installations, all orchestrated by an encrypted AutoIt script.

Please Note: This blog focuses specifically on the complexities of a malware infection process, but not on the impact of the malware or it’s other functionalities.

For those looking for a higher-level look at some of our recent research, please enjoy one of these options: Continue reading "Banload Malware Affecting Brazil Exhibits Unusually Complex Infection Process"

New OS X Ransomware KeRanger Infected Transmission BitTorrent Client Installer

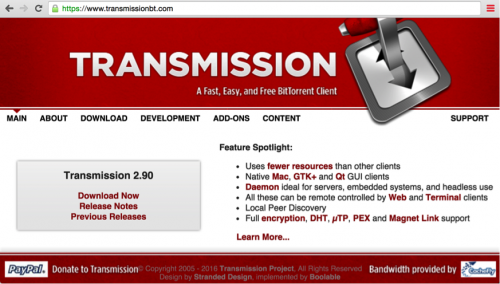
On March 4, we detected that the Transmission BitTorrent client installer for OS X was infected with ransomware, just a few hours after installers were initially posted. We have named this Ransomware “KeRanger.” The only previous ransomware for OS X we are aware of is FileCoder, discovered by Kaspersky Lab in 2014. As FileCoder was incomplete at the time of its discovery, we believe KeRanger is the first fully functional ransomware seen on the OS X platform.

Attackers infected two installers of Transmission version 2.90 with KeRanger on the morning of March 4. When we identified the issue, the infected DMG files were still available for downloading from the Transmission site (hxxps://download.transmissionbt.com/files/Transmission-2.90[.]dmg) Transmission is an open source project. It’s possible that Transmission’s official website was compromised and the files were replaced by re-compiled malicious versions, but we can’t confirm how this infection occurred.

fig1

Figure 1 KeRanger hosted in Transmission's official website

The KeRanger application was signed with a valid Mac app development certificate; therefore, it was able to bypass Apple’s Gatekeeper protection. If a user installs the infected apps, an embedded executable file is run on the system. KeRanger then waits for for three days before connecting with command and control (C2) servers over the Tor anonymizer network. The malware then begins encrypting certain types of document and data files on the system. After completing the encryption process, KeRanger demands that victims pay one bitcoin (about $400) to a specific address to retrieve their files. Additionally, KeRanger appears to still be under active development and it seems the malware is also attempting to encrypt Time Machine backup files to prevent victims from recovering their back-up data.

Palo Alto Networks reported the ransomware issue to the Transmission Project and to Apple on March 4. Apple has since revoked the abused certificate and updated XProtect antivirus signature, and Transmission Project has removed the malicious installers from its website. Palo Alto Networks has also updated URL filtering and Threat Prevention to stop KeRanger from impacting systems. Continue reading "New OS X Ransomware KeRanger Infected Transmission BitTorrent Client Installer"

New Malware 'Rover' Targets Indian Ambassador to Afghanistan

On December 24, 2015, Unit 42 identified a targeted attack, delivered via email, on a high profile Indian diplomat, an Ambassador to Afghanistan. The body and content of the email suggest that it was crafted and spoofed to look like it was sent by the current Defence Minister of India, Mr. Manohar Parrikar, commending the Ambassador on his contributions and success.

India has been a key nation in building and funding Afghanistan’s infrastructure and economic development, which includes setting up iron ore mines, steel plants, power plants and transportation systems, helping reconstruct the Salma Dam and constructing a new Parliament Complex for the Afghan Government.

Given India’s significant contributions to the development of Afghanistan, it is likely that there may be groups or nations who would be interested in tracking and spying on key individuals who officially represent India in Afghanistan. Continue reading "New Malware 'Rover' Targets Indian Ambassador to Afghanistan"

KeyBase Threat Grows Despite Public Takedown: A Picture is Worth a Thousand Words

Be the first to receive the latest news, cyber threat intelligence and research from Unit 42. Subscribe Now. 

In June 2015, Unit 42 reported on a keylogger malware family known as KeyBase, which had first appeared in February 2015. The author has since taken down its website and supposedly ceased selling the software, while also renouncing the tool’s use for any malicious purposes. However, as of this writing, the software is still readily available for download with minimal effort on multiple websites. What’s more, while development of KeyBase appears to have stopped, the usage of this malware has increased significantly since June. In our initial report, we identified approximately 1,500 sessions carrying KeyBase and approximately six months later we have seen over 4,900 different samples and 44,200 sessions within Palo Alto Networks AutoFocus. Continue reading "KeyBase Threat Grows Despite Public Takedown: A Picture is Worth a Thousand Words"