Palo Alto Networks Researchers Discover Critical Vulnerabilities in Internet Explorer and Adobe Shockwave Player

Palo Alto Networks researchers have been credited with discovery of new vulnerabilities affecting Adobe Shockwave Player and Microsoft Internet Explorer.

Palo Alto Networks researcher Tongbo Luo discovered a critical vulnerability in Adobe Shockwave Player affecting Shockwave versions 12.1.9.160 and earlier for Windows. The vulnerability and upgrade instructions are detailed by Adobe in a Security Bulletin dated September 8, 2015.  Continue reading "Palo Alto Networks Researchers Discover Critical Vulnerabilities in Internet Explorer and Adobe Shockwave Player"

Musical Chairs: Multi-Year Campaign Involving New Variant of Gh0st Malware

The Gh0st malware is a widely used remote administration tool (RAT) that originated in China in the early 2000s. It has been the subject of many analysis reports, including those describing targeted espionage campaigns like Operation Night Dragon and the GhostNet attacks on Tibet. Musical Chairs is a multi-year campaign which recently deployed a new variant Gh0st we’ve named “Piano Gh0st.”

Our evidence suggests the actors behind these attacks have been operating for over five years and have maintained a single command and control server for almost two. They use compromised e-mail accounts to distribute their malware widely and their targeting appears opportunistic rather than specific. Continue reading "Musical Chairs: Multi-Year Campaign Involving New Variant of Gh0st Malware"

KeyRaider iOS Malware: How to Keep Yourself Safe

Earlier this week we published an analysis of KeyRaider, which is an iOS malware family and a reminder of the risks users take when they choose to jailbreak their mobile devices.

Attackers used KeyRaider malware to steal more than 225,000 Apple accounts. KeyRaider targeted only jailbroken Apple devices, primarily through Chinese websites and apps that provide software for those jailbroken phones.

The best way to keep a mobile device safe is to keep it up to date with the latest software updates. That also means not jailbreaking your phone in the first place, as today there aren’t any Cydia repositories that perform strict security checks on apps or the tweaks used to change them.

But if your device is already jailbroken, what steps can you take to protect it against KeyRaider? Continue reading "KeyRaider iOS Malware: How to Keep Yourself Safe"

KeyRaider: iOS Malware Steals Over 225,000 Apple Accounts to Create Free App Utopia

Executive Summary

Recently, WeipTech was analyzing suspicious Apple iOS tweaks reported by users and found over 225,000 valid Apple accounts with passwords stored on a server.

In cooperation with WeipTech, we have identified 92 samples of a new iOS malware family in the wild. We have analyzed the samples to determine the author’s ultimate goal and have named this malware “KeyRaider”. We believe this to be the largest known Apple account theft caused by malware. Continue reading "KeyRaider: iOS Malware Steals Over 225,000 Apple Accounts to Create Free App Utopia"

Banking Trojan Escelar Infects Thousands In Brazil and the US

Unit 42 for the past three months has been tracking a banking Trojan targeting victims in Brazil and the United States. Escelar originally surfaced in January of this year, and has since had roughly 100,000 instances of attempted infections.

Attackers deliver the Trojan using generic Portuguese language phishing emails and are currently targeting seven Brazilian banks. Once delivered, Escelar has multiple installation stages where malware is downloaded using direct connections to multiple Microsoft SQL servers. These SQL servers are also used for command and control (C2) functionality. Continue reading "Banking Trojan Escelar Infects Thousands In Brazil and the US"

RTF Exploit Installs Italian RAT: uWarrior

Unit 42 researchers have observed a new Remote Access Tool (RAT) constructed by an unknown actor of Italian origin. This RAT, referred to as uWarrior because of embedded PDB strings, has been previously described by an independent researcher who noted a potentially unknown exploit being used against Microsoft Office. Continue reading "RTF Exploit Installs Italian RAT: uWarrior"

Retefe Banking Trojan Targets Sweden, Switzerland and Japan

Retefe is one of the most targeted banking Trojans currently in the wild. While other families such as Zeus and Citadel are widely adopted by attackers targeting banking websites around the world, Retefe is consistently used to target victims in Sweden, Switzerland and Japan.

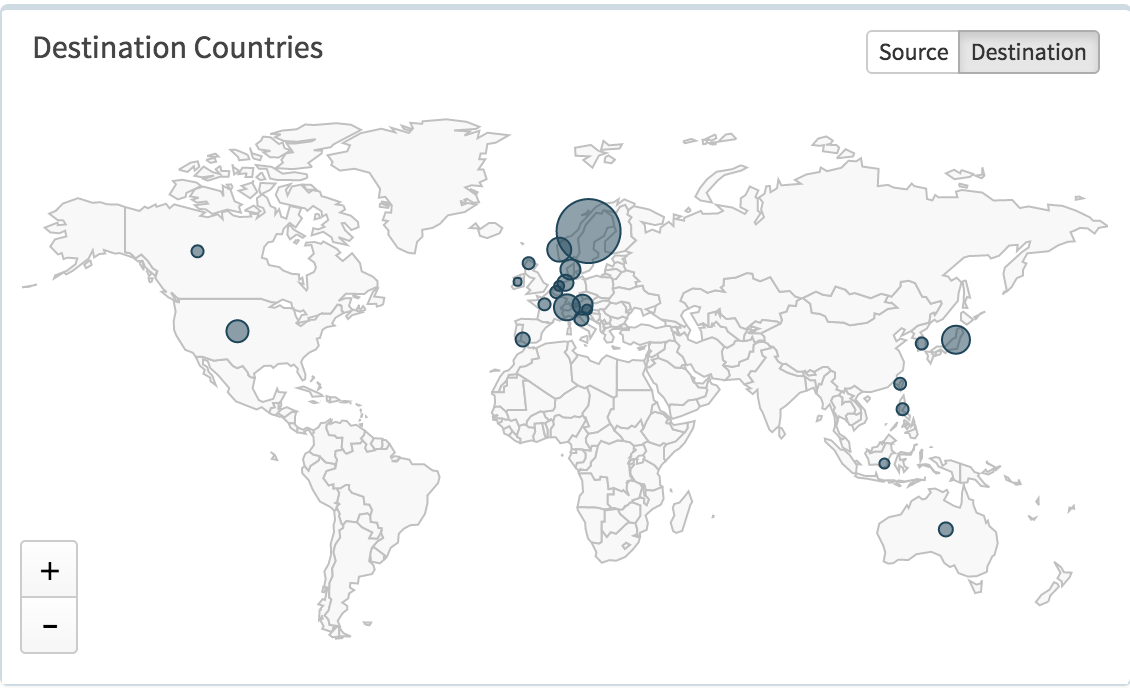
In the last two weeks we have detected a surge of e-mails using AutoFocus, each carrying the Retefe Trojan and targeting organizations in Western Europe and Japan.

retefe1

Figure 1: AutoFocus map of recent Retefe Trojan recipients Continue reading "Retefe Banking Trojan Targets Sweden, Switzerland and Japan"

What’s Next in Malware After Kuluoz?

Regular readers of this blog have heard all about the infamous Kuluoz malware. This family was the latest evolution of the Asprox malware and at its peak in 2014 it accounted for 80% of all malware sessions we observed in WildFire. When the team published our Threat Landscape Review in December of last year, we highlighted this family as a scourge that impacted nearly every company Palo Alto Networks protected in 2014. Kuluoz was primarily distributed through e-mail, which means we saw large numbers of SMTP sessions, but also downloads over a variety of webmail clients. Continue reading "What’s Next in Malware After Kuluoz?"

UPS: Observations on CVE-2015-3113, Prior Zero-Days and the Pirpi Payload

A June 23 FireEye blog post titled “Operation Clandestine Wolf” discussed a cyber espionage group, known as APT3, that had been exploiting a zero-day vulnerability in Adobe Flash. Unit 42 also tracks the APT3 group using the name UPS, which is an intrusion set with Chinese origins that is known for having early access to zero-day vulnerabilities and delivering a backdoor called Pirpi.

The UPS group has exploited several zero-day vulnerabilities, most recently using the zero-days released in the Hacking Team breach that we discussed in our July 10 blog post, “APT Group UPS Targets US Government with Hacking Team Flash Exploit”. However, the most recent original zero-day released by this group is tracked by CVE-2015-3113, which has similarities to the once zero-day vulnerabilities CVE-2014-1776 and CVE-2014-6332 exploited by UPS in May and November 2014, respectively. We’ll discuss here the similarities observed between the various components used to exploit these two vulnerabilities, specifically focusing on the malicious Flash files and the payloads delivered. Continue reading "UPS: Observations on CVE-2015-3113, Prior Zero-Days and the Pirpi Payload"

Watering Hole Attack on Aerospace Firm Exploits CVE-2015-5122 to Install IsSpace Backdoor

On July 16, 2015, the Palo Alto Networks Unit 42 threat intelligence team discovered a watering hole attack on the website of a well-known aerospace firm. The website was compromised to launch an apparent watering-hole attack against the company's customers. It was hosting an Adobe Flash exploit targeting one of the newly disclosed vulnerabilities from the Hacking Team data breach, CVE-2015-5122.

This attack yet again showcases the opportunistic tendencies of adversary groups and bad actors. The malware deployed by this exploit has been seen in a number of targeted attacks and provides attackers with a foothold on the victim’s machine and/or network.

The exploit file, movie.swf, was ZWS compressed, a tactic that has been observed to evade anti-virus programs. Once uncompressed, a binary was found to be embedded in the Flash file. Upon further analysis, this file was found to contain behavior consistent with a Trojan commonly called IsSpace. Based on its codebase and behavioral patterns, it appears that IsSpace could possibly be an evolution of the NFlog backdoor, which has previously been attributed to the adversary groups DragonOK and Moafee. Both groups are thought to be operating out of Southeast Asia, and Moafee in particular has been associated with attacks on the US defense industrial base. Continue reading "Watering Hole Attack on Aerospace Firm Exploits CVE-2015-5122 to Install IsSpace Backdoor"

Palo Alto Networks Researcher Discovers Two Critical Internet Explorer Vulnerabilities

Palo Alto Networks researcher Bo Qu discovered two new critical Internet Explorer (IE) vulnerabilities affecting IE versions 6, 7, 8, 9, 10, and 11. Both are included in Microsoft’s July 2015 Security Bulletin, and documented in Microsoft Security Bulletins MS15-065 and MS15-066. Continue reading "Palo Alto Networks Researcher Discovers Two Critical Internet Explorer Vulnerabilities"

Tracking MiniDionis: CozyCar’s New Ride Is Related to Seaduke

Executive Summary

Unit 42 has uncovered a new campaign from the CozyDuke threat actors, aka CozyCar [1], leveraging malware that appears to be related to the Seaduke malware described earlier this week by Symantec. [2]

This campaign, which began on July 7, 2015, appears to be targeted at government organizations and think-tanks located in democratic countries [3], and utilizes compromised, legitimate websites for spear phishing and command and control activity.

Unit 42 discovered the extent of this attack using the Palo Alto Networks AutoFocus service, which allows analysts to quickly find correlations among malware samples analyzed by WildFire. All files referenced throughout the analysis are contained in the IOC table at the end of this blog. Continue reading "Tracking MiniDionis: CozyCar’s New Ride Is Related to Seaduke"

Unit 42 Technical Analysis: Seaduke

Earlier this week Symantec released a blog post detailing a new Trojan used by the ‘Duke’ family of malware. Within this blog post, a payload containing a function named ‘forkmeiamfamous’ was mentioned. While performing some research online, Unit 42 was able to identify the following sample, which is being labeled as ‘Trojan.Win32.Seadask’ by a number of anti-virus companies.

MD5 A25EC7749B2DE12C2A86167AFA88A4DD
SHA1 BB71254FBD41855E8E70F05231CE77FEE6F00388
SHA256 3EB86B7B067C296EF53E4857A74E09F12C2B84B666FC130D1F58AEC18BC74B0D
Compile Timestamp 2013-03-23 22:26:55
File type PE32 executable (GUI) Intel 80386, for MS Windows, UPX compressed

Our analysis has turned up more technical details and indicators on the malware itself that aren’t mentioned in Symantec’s post. Here are some of our observations:

Continue reading "Unit 42 Technical Analysis: Seaduke"

APT Group UPS Targets US Government with Hacking Team Flash Exploit

On July 8, 2015, Unit 42 used the AutoFocus Threat Intelligence service to locate and investigate activity consistent with a spear-phishing attack targeting the US Government. The attack exploited an Adobe Flash vulnerability that stems from the zero-day vulnerabilities exposed from this month’s Hacking Team data breach.

The spear-phishing attack used a link to a Flash exploit hosted on two subdomains of a legitimate website, perrydale[.]com; rpt.perrydale[.]com and report.perrydale[.]com. Both domains resolve to the same Ukraine-based IP 194.44.130.179. Continue reading "APT Group UPS Targets US Government with Hacking Team Flash Exploit"

New Android Malware Family Evades Antivirus Detection by Using Popular Ad Libraries

NOTICE: We have updated this blog to clarify that Airpush is not responsible for Gunpoder. Airpush's platform was abused by the malware author to hide malicious activity.

Executive Summary

Unit 42 discovered a new family of Android malware that successfully evaded all antivirus products on the VirusTotal web service. We named this malware family “Gunpoder” based on the main malicious component name, and the Unit 42 team observed 49 unique samples across three different variants. This finding highlights the fine line between “adware,” which isn’t traditionally prevented by antivirus products, and malware, with its ability to cause harm.

Samples of Gunpoder have been uploaded to VirusTotal since November 2014, with all antivirus engines reporting either “benign” or “adware” verdicts, meaning legacy controls would not prevent installation of this malware. While researching the sample, we observed that while it contained many characteristics of adware, and indeed embeds a popular adware library within it, a number of overtly malicious activities were also discovered, which we believe characterizes this family as being malware, such as: Continue reading "New Android Malware Family Evades Antivirus Detection by Using Popular Ad Libraries"