Stolen Email Accounts of World’s Top Universities Selling on China’s Largest C2C Platform

Recently, we found email accounts from top universities across the world being sold on Taobao, the largest consumer-to-consumer (C2C) e-commerce platform in China. Advertised uses for these accounts included registering for special accounts under software developer programs, receiving student discounts or coupons from retailers, and obtaining access to academic databases.  This post describes the scope, associated risks, and implications of this activity.

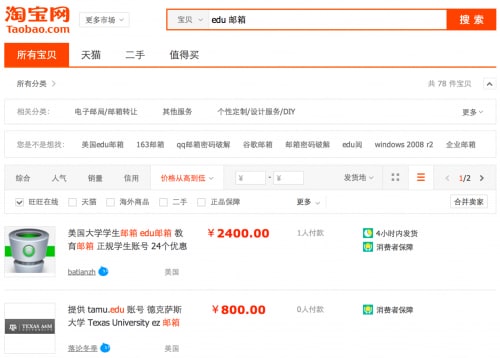
Our investigation began with a Chinese language search for "edu mailbox" in Taobao, which returned 99 results related to stolen university email accounts. The most expensive account was listed at ¥2400 RMB ($390.80 USD), while the cheapest was only ¥0.98 RMB ($0.16 USD).
taobao 1

Figure 1: Results for Chinese language "edu mailbox" search on Taobao.

These accounts, which include an education (EDU) top-level domain email address with valid password, represent 42 of the world’s top universities, across 10 countries: Continue reading "Stolen Email Accounts of World’s Top Universities Selling on China’s Largest C2C Platform"
Bad Certificate Management in Google Play Store

Following a recent study of apps in the Google Play Store, let’s discuss several security risks caused by the bad certificate management practiced in many Android apps, from social to mobile banking.

All Android apps must be digitally signed with a certificate from the developer. As described in Google’s official document, the app developer is required to create a keystore with a set of private keys, and then use the private key to generate a signed version of apps. This key has to be valid for at least 25 years. These certificates do not have to be generated by a certificate authority and can instead be self-signed. Because this is simpler and allows the author to retain the private key, the majority of Google store apps use self-signed certificates. This means it is the developer’s responsibility to keep the private key safe, whether that developer is a 13-year-old or a multi-national company. As this means the security protecting private keys varies widely, the security risks of bad certificate management cannot be ignored and must be identified, and where necessary, mitigated. Continue reading "Bad Certificate Management in Google Play Store"

Listen: How Evolved 419 Scammers Are Targeting the Enterprise

Unit 42, the Palo Alto Networks threat intelligence team, will be appearing on a live webcast and Q&A with Dark Reading tomorrow, Thursday, August 28 at 2:00 p.m. EDT.

DR-logo
Continue reading "Listen: How Evolved 419 Scammers Are Targeting the Enterprise"

NetWire and MITRE ChopShop

On August 4, Unit 42, the Palo Alto Networks threat intelligence team, released a tool to decrypt the traffic from a Remote Administration Tool (RAT) named NetWire (part of the NetWiredRC malware family).  For details of the encryption protocol used please see our earlier post here.

The previously released protocol decoder and parser was originally built as a stand-alone module. As part of Unit 42’s mission to contribute to the security community, we have developed, and are releasing today, a version of the NetWire decryption tool that works within ChopShop, a great open source tool from MITRE that provides a framework for protocol analysis.  To use the tool, simply grab the public_tools repo from the Unit 42 GitHub repository. Be sure to point your ChopShop command to that directory using the -M flag.

We hope that this integration of the decryptor tool with ChopShop will provide value to incident responders and security researchers.    Continue reading "NetWire and MITRE ChopShop"

Pivot on Google Code C2 Reveals Additional Malware

Last week, we reported on attacks observed against East Asia that used Google Code for command and control (C2). As follow-on to that work, we pivoted on the C2 indicators of compromise (IoCs) within our WildFire platform, looking for additional malicious activity.

One sample in particular caught our attention, downloaded on June 18 from 211.233.89.182 via FTP. While all of the other near-proximity samples downloaded from this Korean IP were flagged as malware by VirusTotal, this one was not at that time. Deeper inspection revealed what this malware was and how it evaded detection by antivirus programs.

The FTP download in question was for a resource innocuously named “p”. Continue reading "Pivot on Google Code C2 Reveals Additional Malware"

Examining the CHS Breach and Heartbleed Exploitation

Yesterday, TrustedSec, a security consultancy based on Ohio, wrote that the recent breach at Community Health Systems (CHS) was the result of exploitation of the Heartbleed OpenSSL vulnerability (CVE-2014-0160). CHS’s 8-K filing on Monday did not reveal how the attackers got into their network, only that the records of approximately 4.5 million patients were stolen in attacks in between April and June of 2014. TrustedSec reports on how attackers were apparently able to glean user credentials from a certain device via the Heartbleed vulnerability and use them to log in via a VPN.

Continue reading "Examining the CHS Breach and Heartbleed Exploitation"

Insecure Internal Storage in Android

Today, Palo Alto Networks researcher Claud Xiao is delivering a presentation titled “Insecure Internal Storage in Android” at the Hacks in Taiwan Conference (HITCON).

Claud is discussing techniques for accessing private data in Android’s internal storage system using the Android Debug Bridge (ADB) backup/restore functionality. While over 85% of active Android devices are vulnerable to this attack, Android includes multiple levels of protection to prevent unauthorized data access. In today’s presentation, Claud will have demonstrated how an attacker could bypass all of those protections to gain access to usernames, passwords and a treasure trove of other data.

To understand this attack, it’s critical to understand how applications use Android internal storage and why unauthorized access to this data is so problematic.

Continue reading "Insecure Internal Storage in Android"

Palo Alto Networks Discovers 3 Critical Internet Explorer Vulnerabilities

Palo Alto Networks researchers discovered 3 new critical Internet Explorer (IE) vulnerabilities covering IE versions 8, 9, 10 and 11.

Each of these discoveries allows full remote code execution using a memory corruption vulnerability in IE. They have been documented in Microsoft Security Bulletin MS14-051and part of the August 2014 Security Bulletin. Palo Alto Networks researcher Bo Qu is credited with all 3 vulnerabilities.

Palo Alto Networks customers are protected from these vulnerabilities through our regular Vulnerability Protection updates, and we recommend Internet Explorer users upgrade to the latest patch from Microsoft.

Continue reading "Palo Alto Networks Discovers 3 Critical Internet Explorer Vulnerabilities"

Attacks on East Asia using Google Code for Command and Control

Recently, FireEye published a blog titled “Operation Poisoned Hurricane” which detailed the use of PlugX malware variants signed with legitimate certificates that used Google Code project pages for command and control (C2). We were able to uncover multiple additional samples exploiting the same technique as well as an additional Google Code account with multiple projects containing encoded commands.

The attacks against Palo Alto Networks customers, which took place between early June to early July, also targeted users in East Asia; in this case an international law firm’s regional office and a major university. All of the attacks were detected by our WildFire platform.

Of note, three of the Google Code projects associated with the newly uncovered account were added during the past few days, indicating it is still in active use.

Continue reading "Attacks on East Asia using Google Code for Command and Control"

Hunting the Mutex

Summary

Mutex analysis is an often overlooked and useful tool for malware author fingerprinting, family classification, and even discovery. Far from the hypothesized "huge amount of variability" in mutex names, likely hypothesized due to the seemingly random appearance of them, practical mutex usage is embarrassingly consistent. In fact, over 15% of all collected worms share a single mutex [2gvwnqjz].

This blog was sourced from the data generated by the WildFire Analytics cloud, which processes thousands of samples a day and provides insights into various characteristics and behaviors of malware worldwide. But before we get into the details, here is a quick overview of mutexes and why they exist in the first place.

Mutex Overview Continue reading "Hunting the Mutex"

Check Out Scenes from Palo Alto Networks at Black Hat 2014

From a well-attended session on our advanced endpoint protection, to the buzz at the booth for Unit 42, our threat intelligence team, and a full slate of demonstrations and visualizations, there was plenty to take in at a very busy Black Hat USA.

Here's a look back at Palo Alto Networks at Black Hat: Continue reading "Check Out Scenes from Palo Alto Networks at Black Hat 2014"

Black Hat 2014: Threat Intelligence With an Emphasis On Context

A few weeks ago we formally introduced Unit 42, the new threat intelligence team at Palo Alto Networks. Following the release Unit 42's inaugural research paper, 419 Evolution, many of the team leads are on the scene here at Black Hat 2014 in Las Vegas.

blog-title-unit42

It's a chance for the security community at large to get to know Unit 42 and our intelligence gathering process, which endeavors not only to provide technical research and detailed analysis of threats, but also to provide context into an attacker's motivations and methods using data collected from the Palo Alto Networks security platform. The approach is intended to help security practitioners and business leaders make sense of trends and thus make better-informed decisions about their security posture.

Ryan Olson, Unit 42 Intelligence Director, joined us from the show floor at Black Hat today to talk about Unit 42, 419 Evolution and what's to come from this exciting new Palo Alto Networks team. Watch below: Continue reading "Black Hat 2014: Threat Intelligence With an Emphasis On Context"

Where To Find Palo Alto Networks At Black Hat 2014

Black Hat USA 2014 is taking place all this week in Las Vegas, and as the exhibit halls and many of the briefings open on Wednesday, we invite you to visit with Palo Alto Networks throughout the show.

Black Hat

Join us at Booth #227 on Wednesday and Thursday to: Continue reading "Where To Find Palo Alto Networks At Black Hat 2014"

Palo Alto Networks Provides a New Breed of Intelligence to Detect and Prevent

Back in June, Microsoft patched 59 Internet Explorer vulnerabilities and Palo Alto Networks discovered 21 of them, all rated critical. Then in July, we released findings about evolved Nigerian 419 scammers from Unit 42, the new Palo Alto Networks threat intelligence team.

The way we perform cybersecurity research is opening the door to a new breed of intelligence that I predict will reshape how organizations gather and share cyber intelligence while converting it to actionable indicators.

The reason is evasive applications. Continue reading "Palo Alto Networks Provides a New Breed of Intelligence to Detect and Prevent"

Backoff and Citadel Abuse Remote Access Tools

Recent events continue to highlight the abuse of remote access applications in the enterprise. Last Tuesday, Trusteer reported that a new variant of Citadel, which has long relied on VNC to give attackers remote control over systems, began adding new credentials to systems it infects and enabling the standard Windows remote desktop application (RDP). This allows the attacker to maintain control over the system even after the Citadel infection is removed. As the report indicates, using RDP this way also allows the attackers to “fly under the radar” as RDP is commonly used by administrators and often not treated as a threat. Continue reading "Backoff and Citadel Abuse Remote Access Tools"